mirror of
https://github.com/gobysec/GobyVuls.git
synced 2026-10-24 17:04:30 +00:00
14 lines
1.5 KiB
Markdown
14 lines
1.5 KiB
Markdown

|
**Updated document date: November 24, 2025**
|
|||
|
|
|
|||
|
|
## Oracle Identity Manager /iam/governance/applicationmanagement/api/v1/applications/groovyscriptstatus;.wadl Command Execution Vulnerability (CVE-2025-61757)
|
|||
|
|
| **Vulnerability** | Oracle Identity Manager /iam/governance/applicationmanagement/api/v1/applications/groovyscriptstatus;.wadl Command Execution Vulnerability (CVE-2025-61757)|
|
|||
|
|
| :----: | :-----|
|
|||
|
|
| **Chinese name** |Fortinet FortiWeb /api/v2.0/cmdb/system/admin%3f/../../../../../cgi-bin/fwbcgi 权限绕过漏洞(CVE-2025-64446) |
|
|||
|
|
| **CVSS core** | 8.5 |
|
|||
|
|
| **FOFA Query** (click to view the results directly)| [(title="Oracle Access Management" || (body="/oamcustompage/pages/css/login_page.css" && body="/oamcustompage/pages/login.jsp"))]
|
|||
|
|
| **Number of assets affected** | 1100+ |
|
|||
|
|
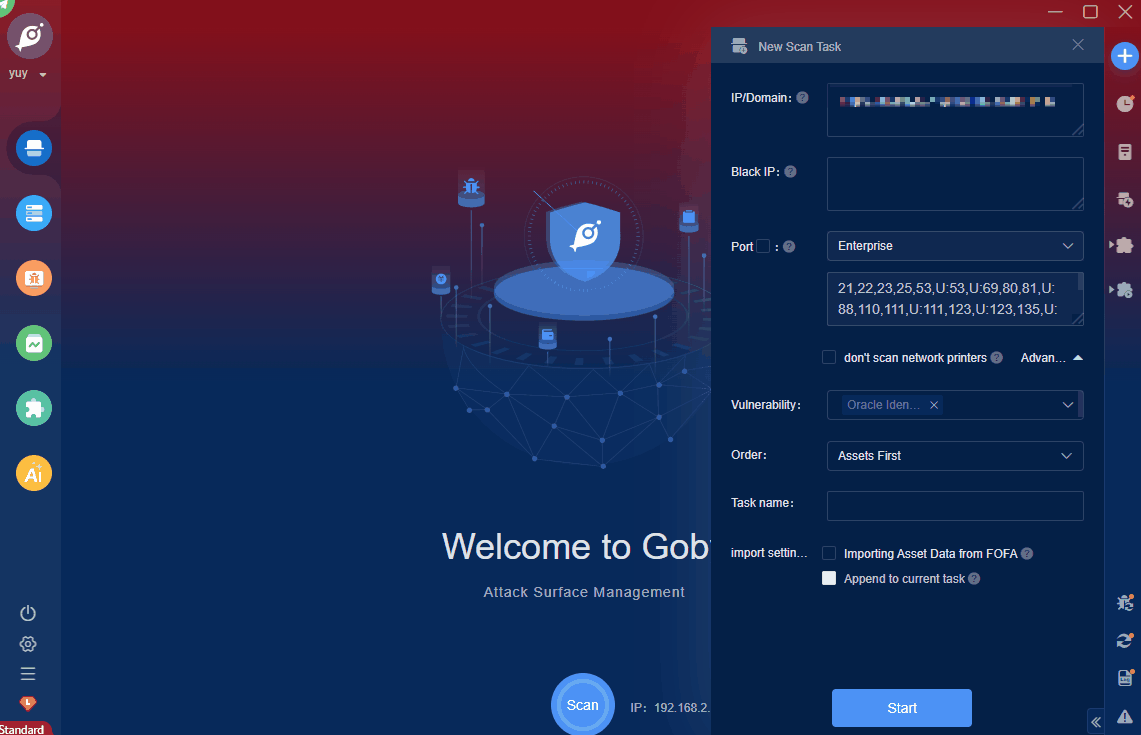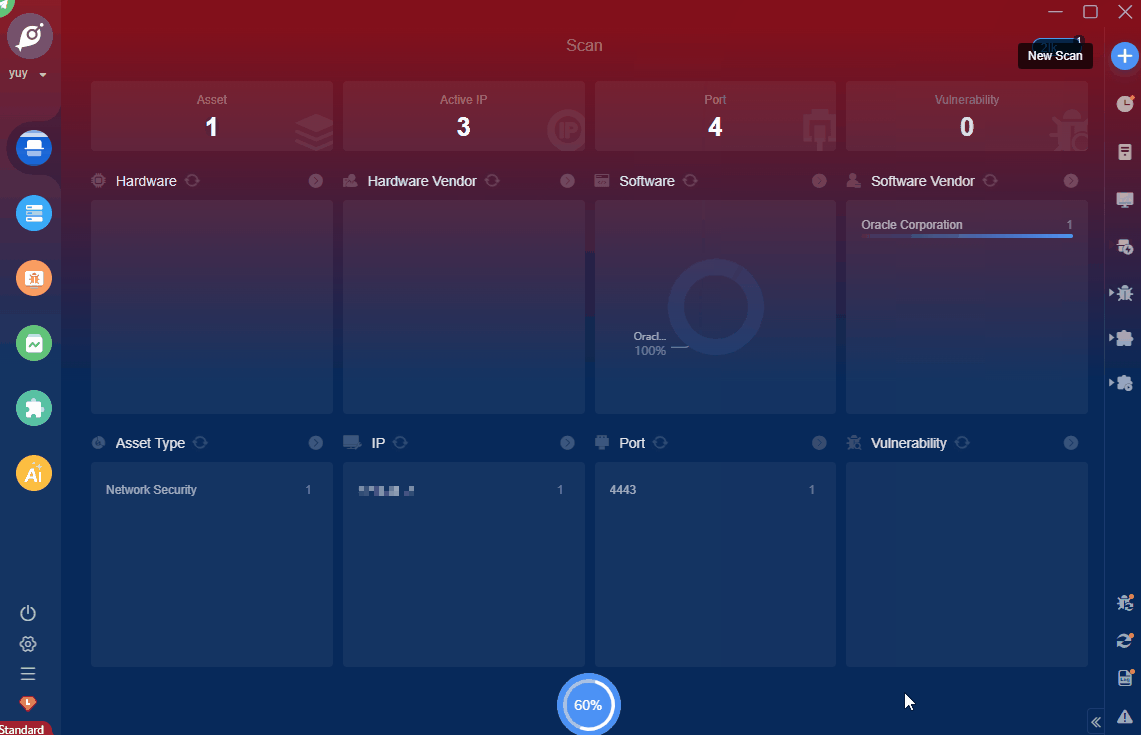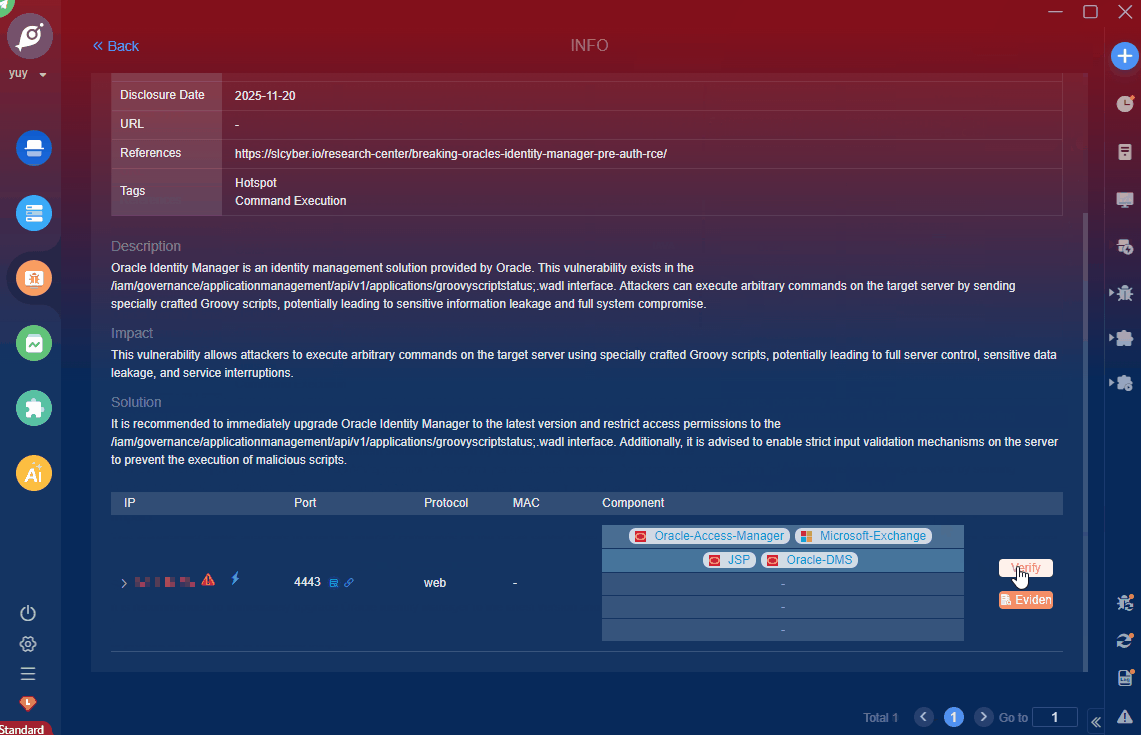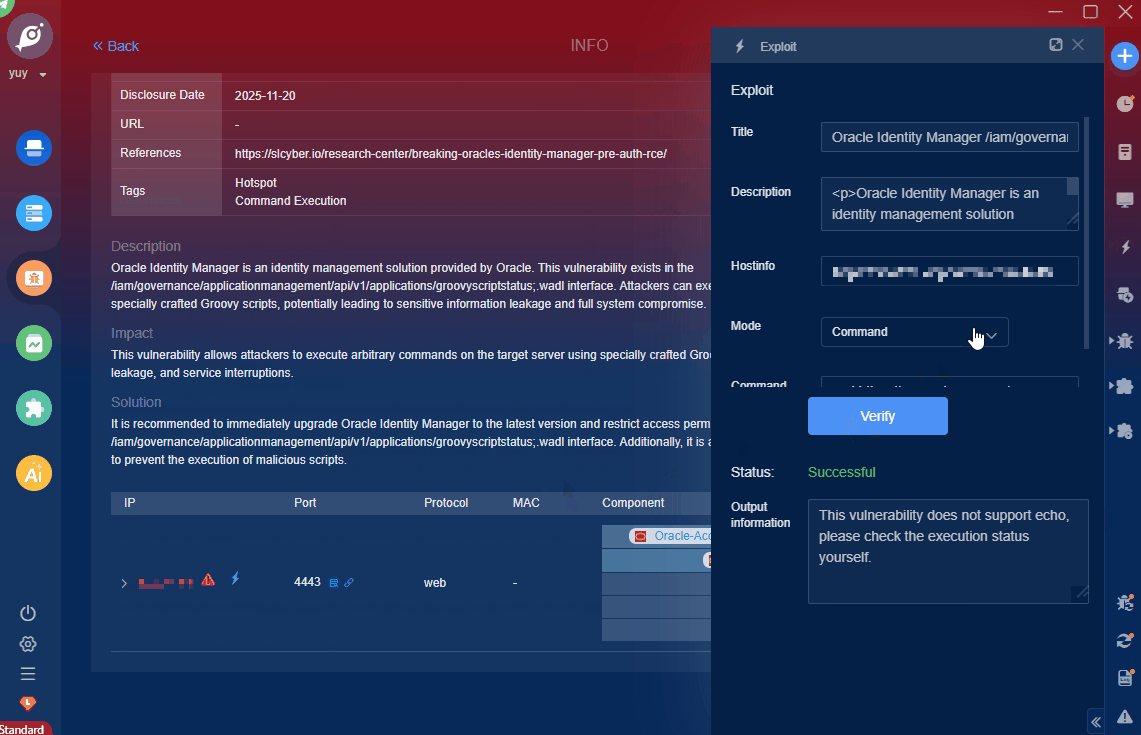
| **Description** |Oracle Identity Manager is an identity management solution provided by Oracle. This vulnerability exists in the /iam/governance/applicationmanagement/api/v1/applications/groovyscriptstatus;.wadl interface. Attackers can execute arbitrary commands on the target server by sending specially crafted Groovy scripts, potentially leading to sensitive information leakage and full system compromise. |
|
|||
|
|
| **Impact** | This vulnerability allows attackers to execute arbitrary commands on the target server using specially crafted Groovy scripts, potentially leading to full server control, sensitive data leakage, and service interruptions.|
|
|||
|
|
| **Affected versions** |12.2.1.4.0, 14.1.2.1.0|
|
|||
|
|
|
|||
|
|
|