mirror of
https://github.com/gobysec/GobyVuls.git
synced 2026-10-24 08:54:28 +00:00
Add CVE-2025-58360 vulnerability documentation
Document details the GeoServer /geoserver/wms GetMap XML External Entity Injection Vulnerability (CVE-2025-58360), including its impact, affected versions, and CVSS score.
This commit is contained in:

1 file changed
+14
@@ -0,0 +1,14 @@
|
|||||||
|
**Updated document date: November 26, 2025**
|
||||||
|
|
||||||
|
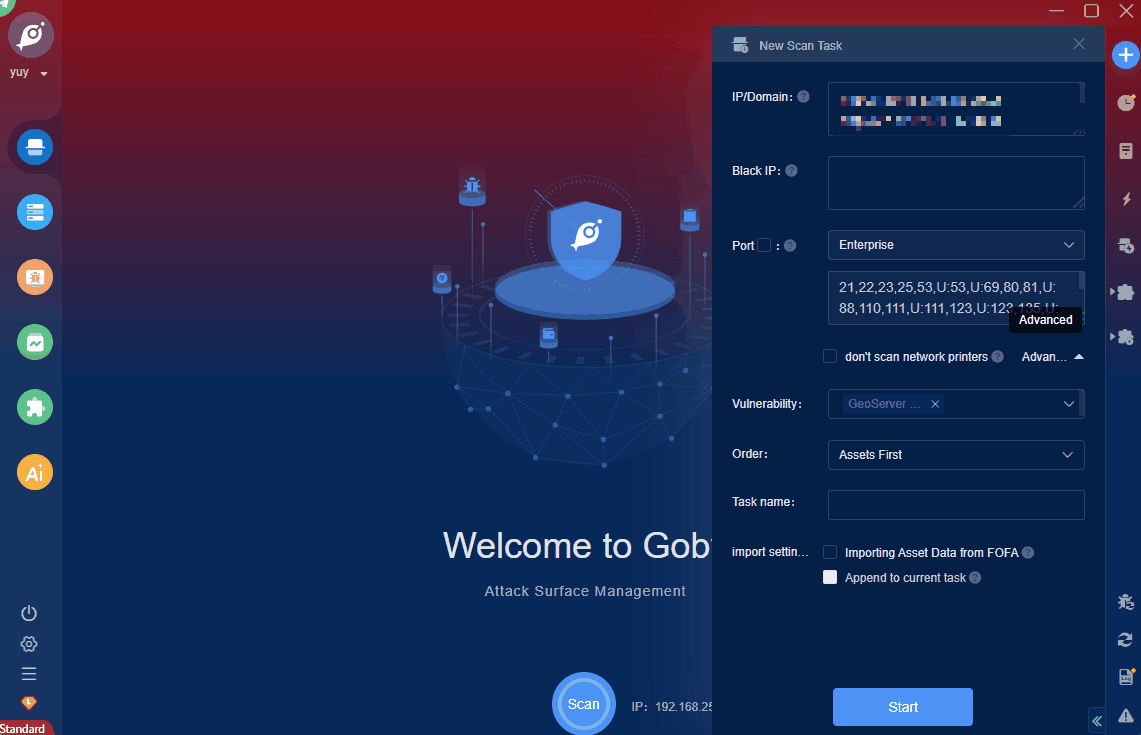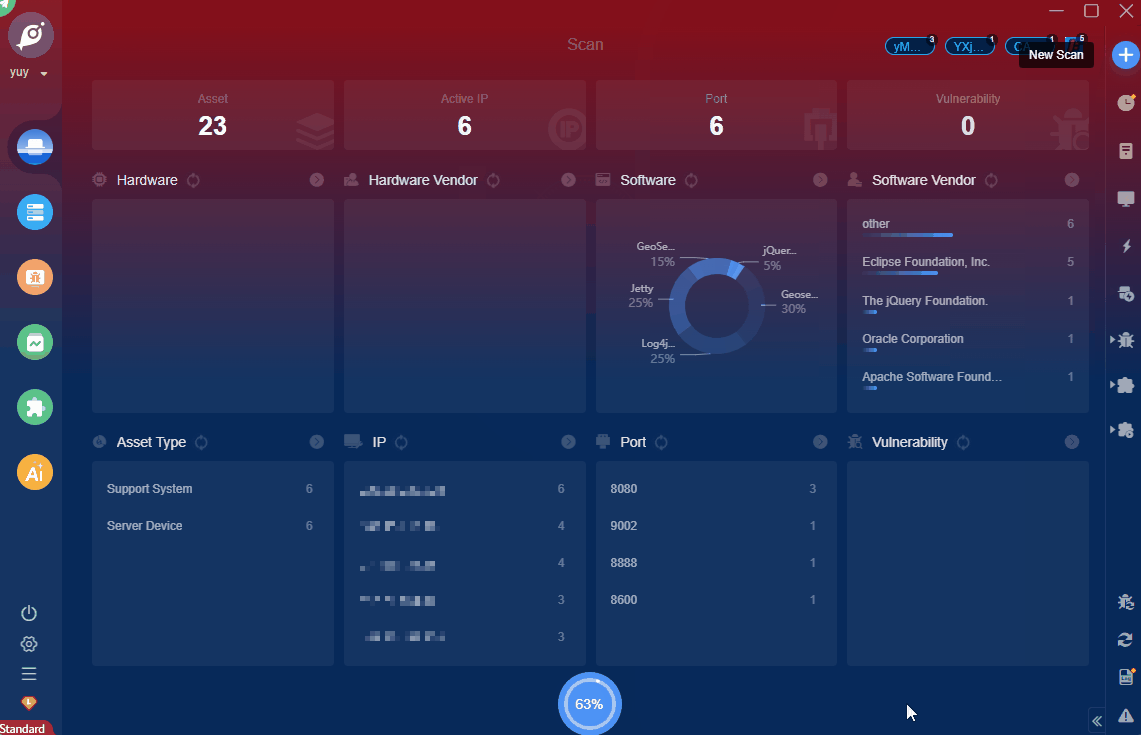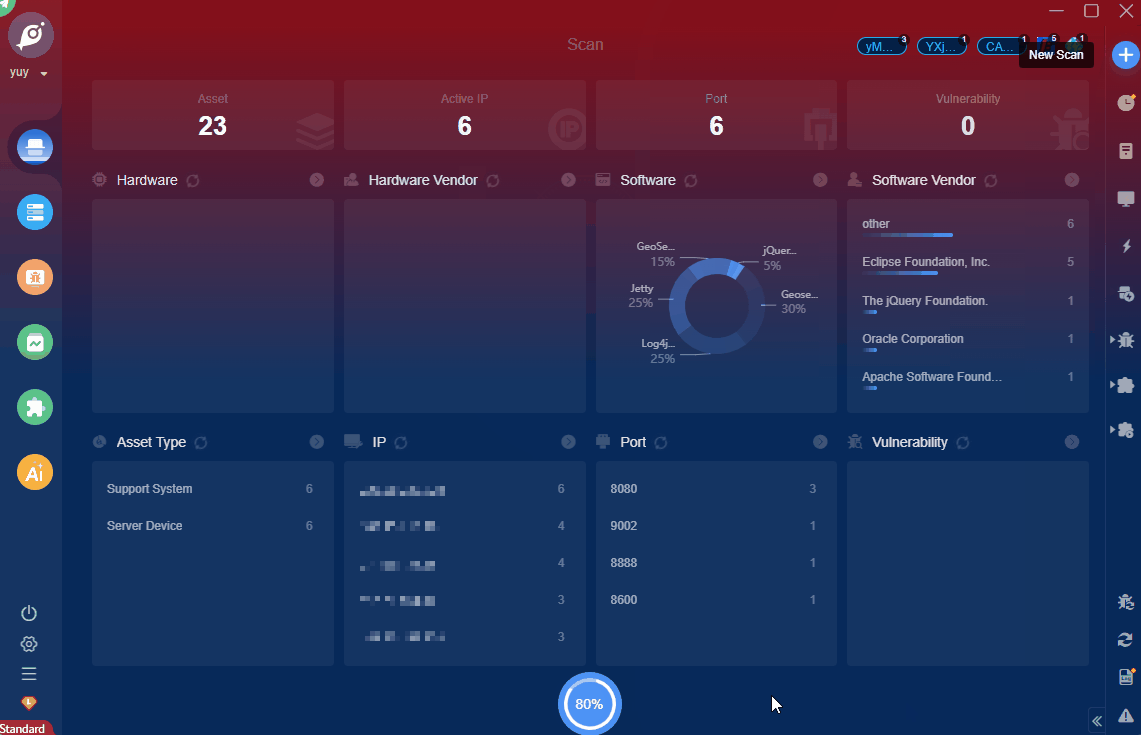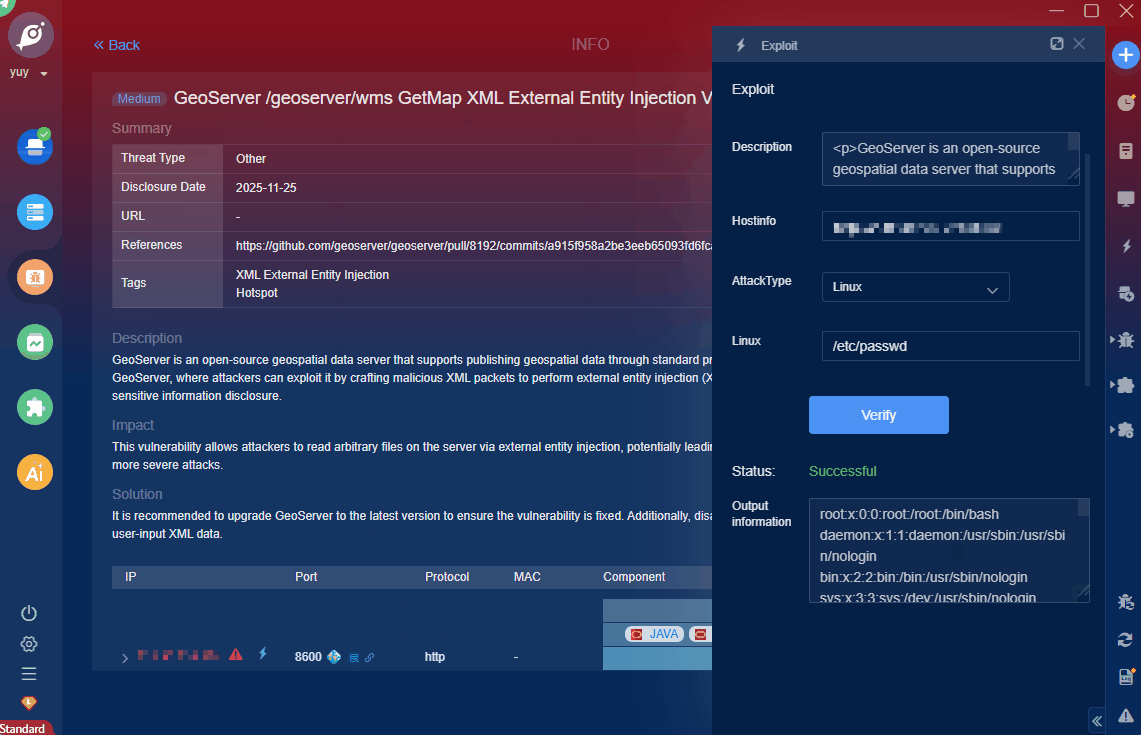
## GeoServer /geoserver/wms GetMap XML External Entity Injection Vulnerability (CVE-2025-58360)
|
||||||
|
| **Vulnerability** | GeoServer /geoserver/wms GetMap XML External Entity Injection Vulnerability (CVE-2025-58360)|
|
||||||
|
| :----: | :-----|
|
||||||
|
| **Chinese name** |GeoServer /geoserver/wms GetMap XML 外部实体注入漏洞(CVE-2025-58360)|
|
||||||
|
| **CVSS core** | 7.5 |
|
||||||
|
| **FOFA Query** (click to view the results directly)| [app="GeoServer"]
|
||||||
|
| **Number of assets affected** | 20k+ |
|
||||||
|
| **Description** |GeoServer is an open-source geospatial data server that supports publishing geospatial data through standard protocols. This vulnerability exists in the WMS interface of GeoServer, where attackers can exploit it by crafting malicious XML packets to perform external entity injection (XXE), potentially leading to arbitrary file reading on the server and sensitive information disclosure.|
|
||||||
|
| **Impact** | This vulnerability allows attackers to read arbitrary files on the server via external entity injection, potentially leading to sensitive information disclosure and further exploitation for more severe attacks.|
|
||||||
|
| **Affected versions** | GeoServer < 2.25.6、2.26.0 <= GeoServer < 2.26.2|
|
||||||
|
|
||||||
|
|
||||||
Reference in new issue
Block a user