mirror of
https://github.com/gobysec/GobyVuls.git
synced 2026-10-24 17:04:30 +00:00

1.1 KiB
1.1 KiB
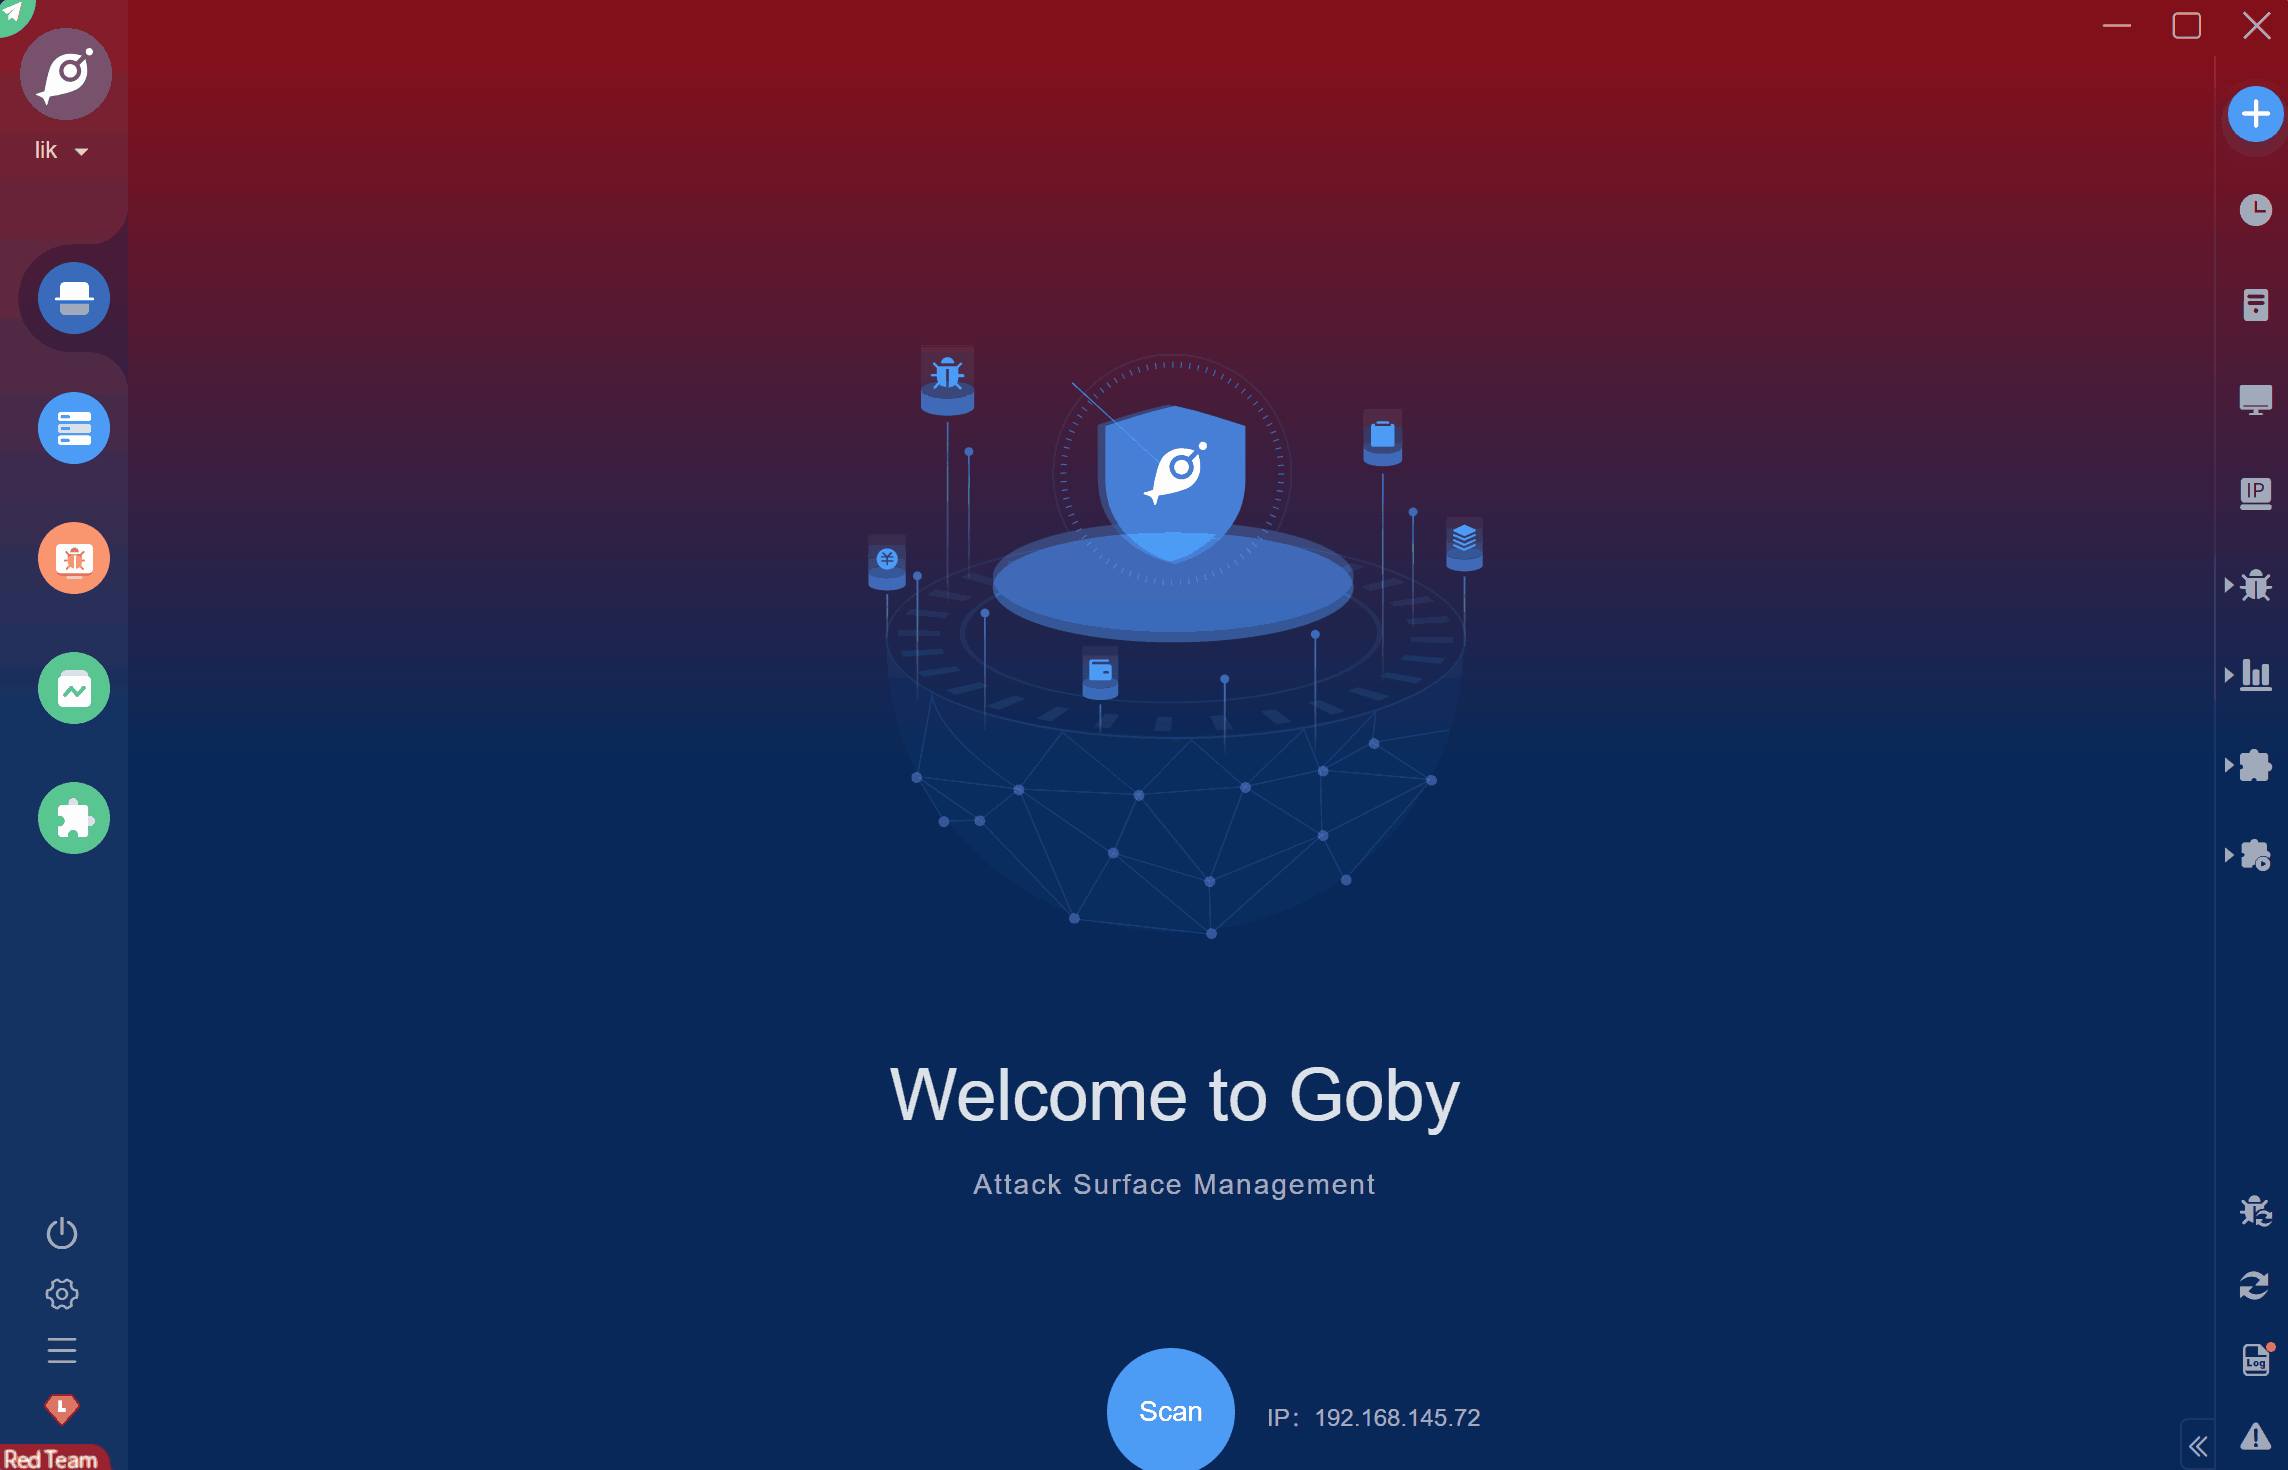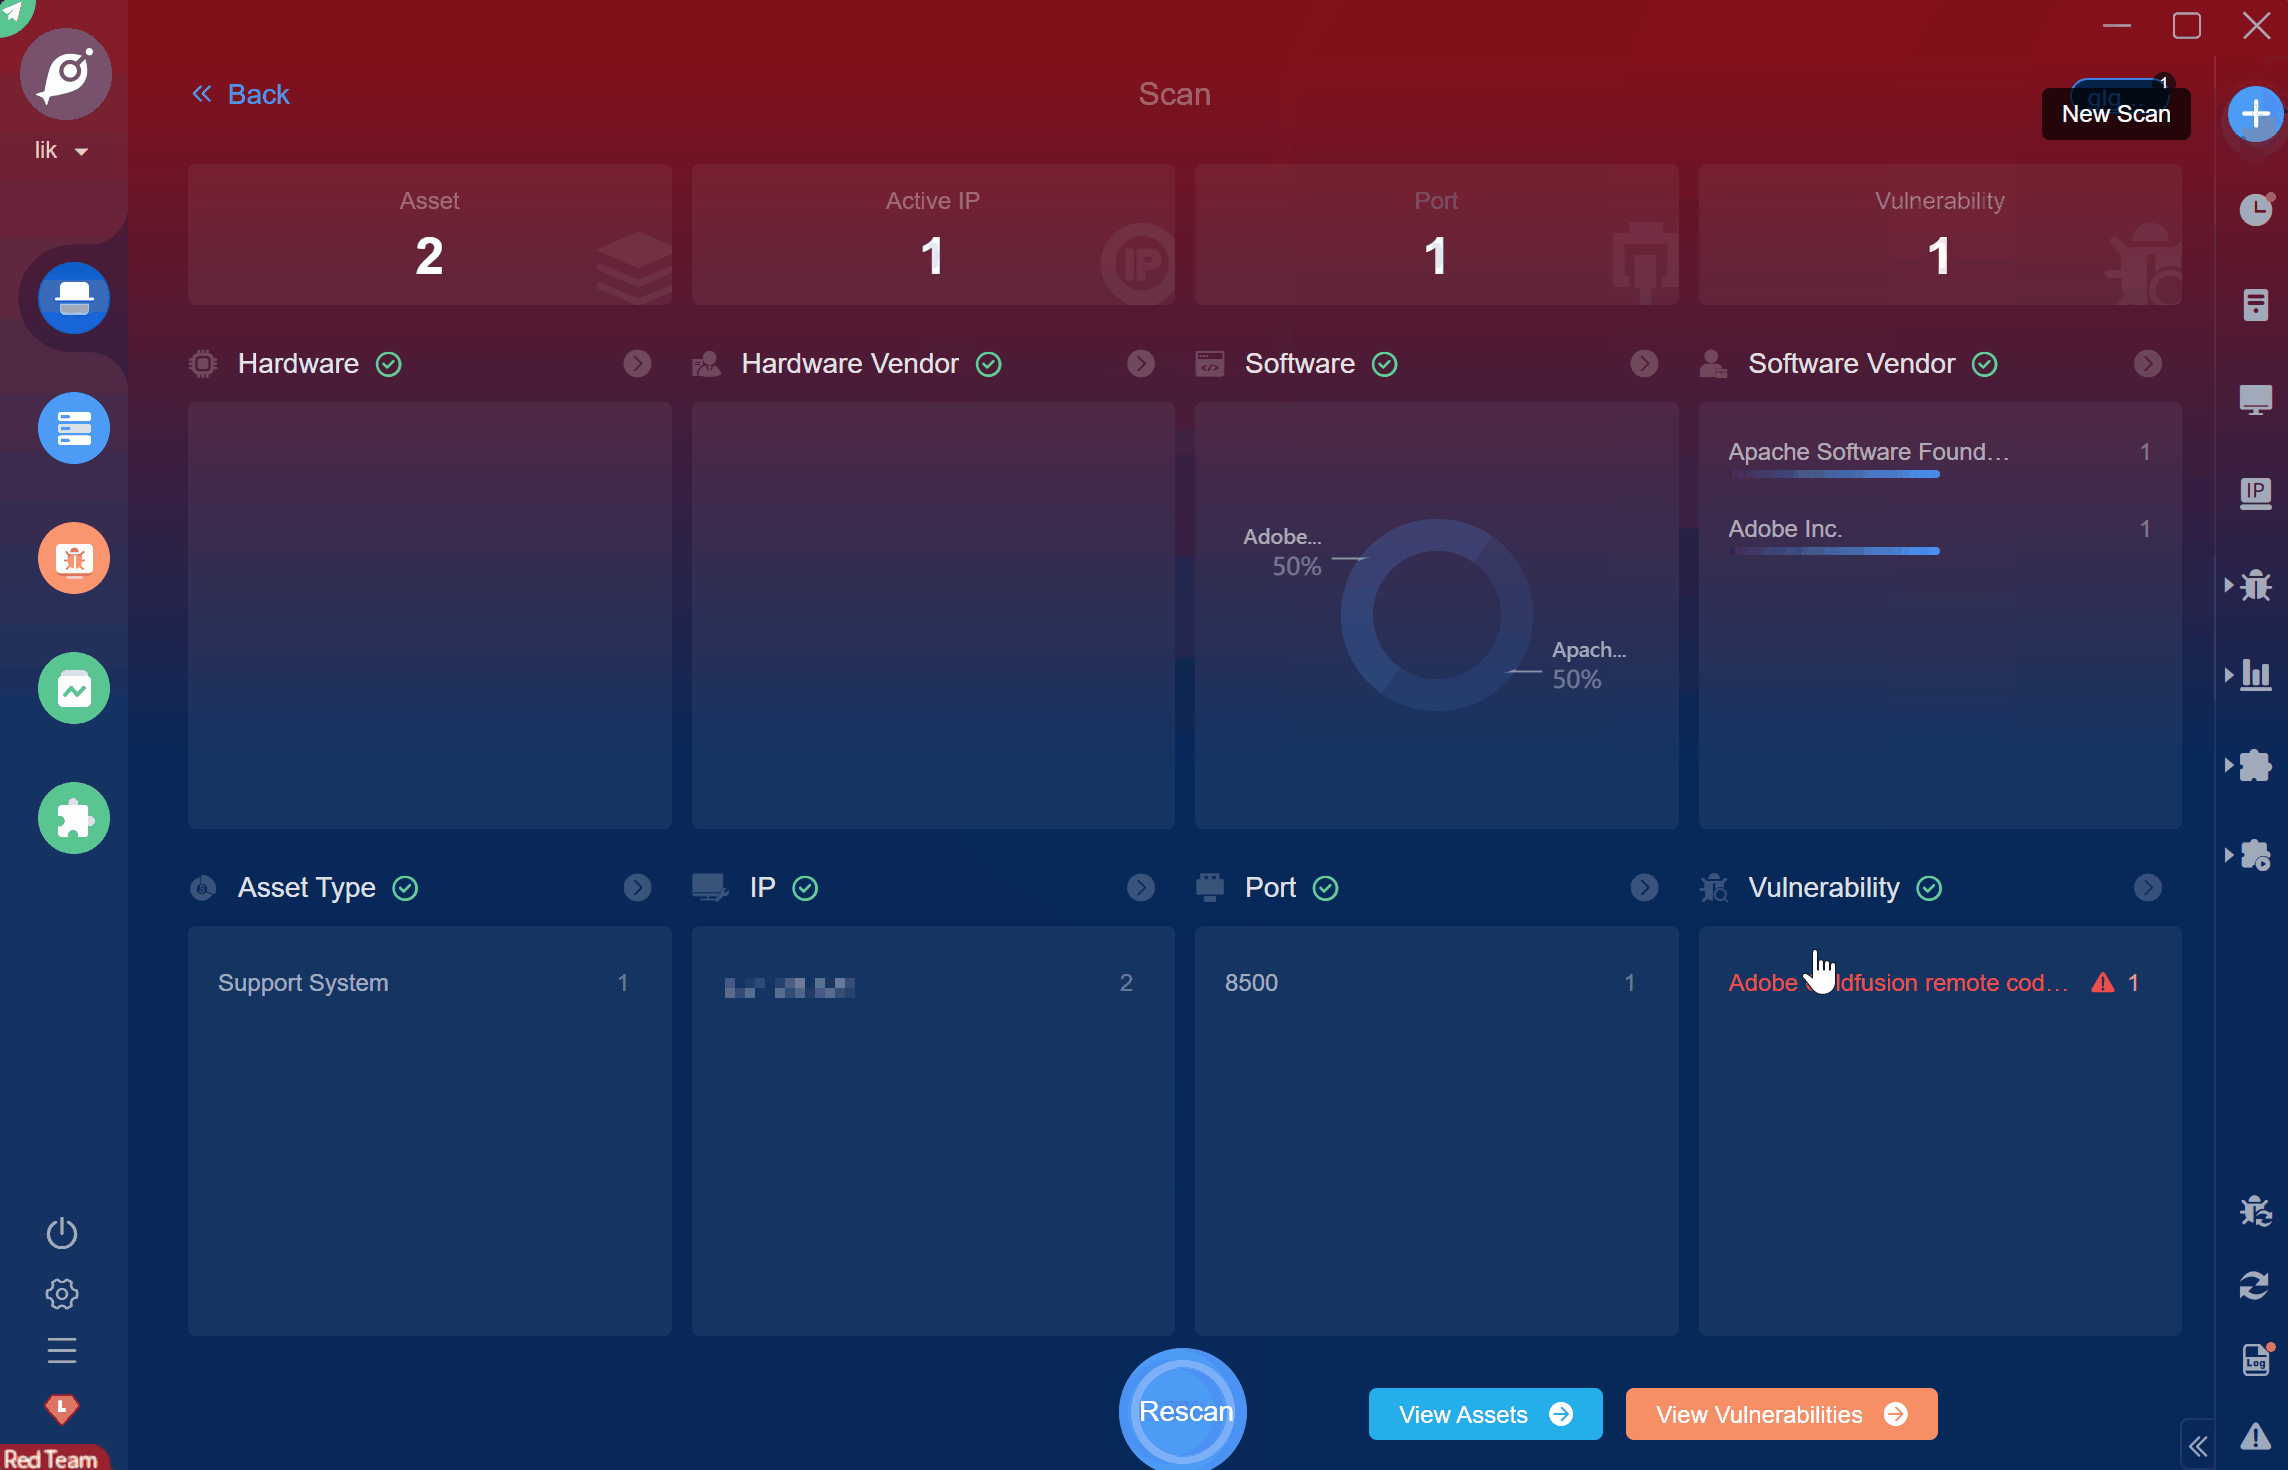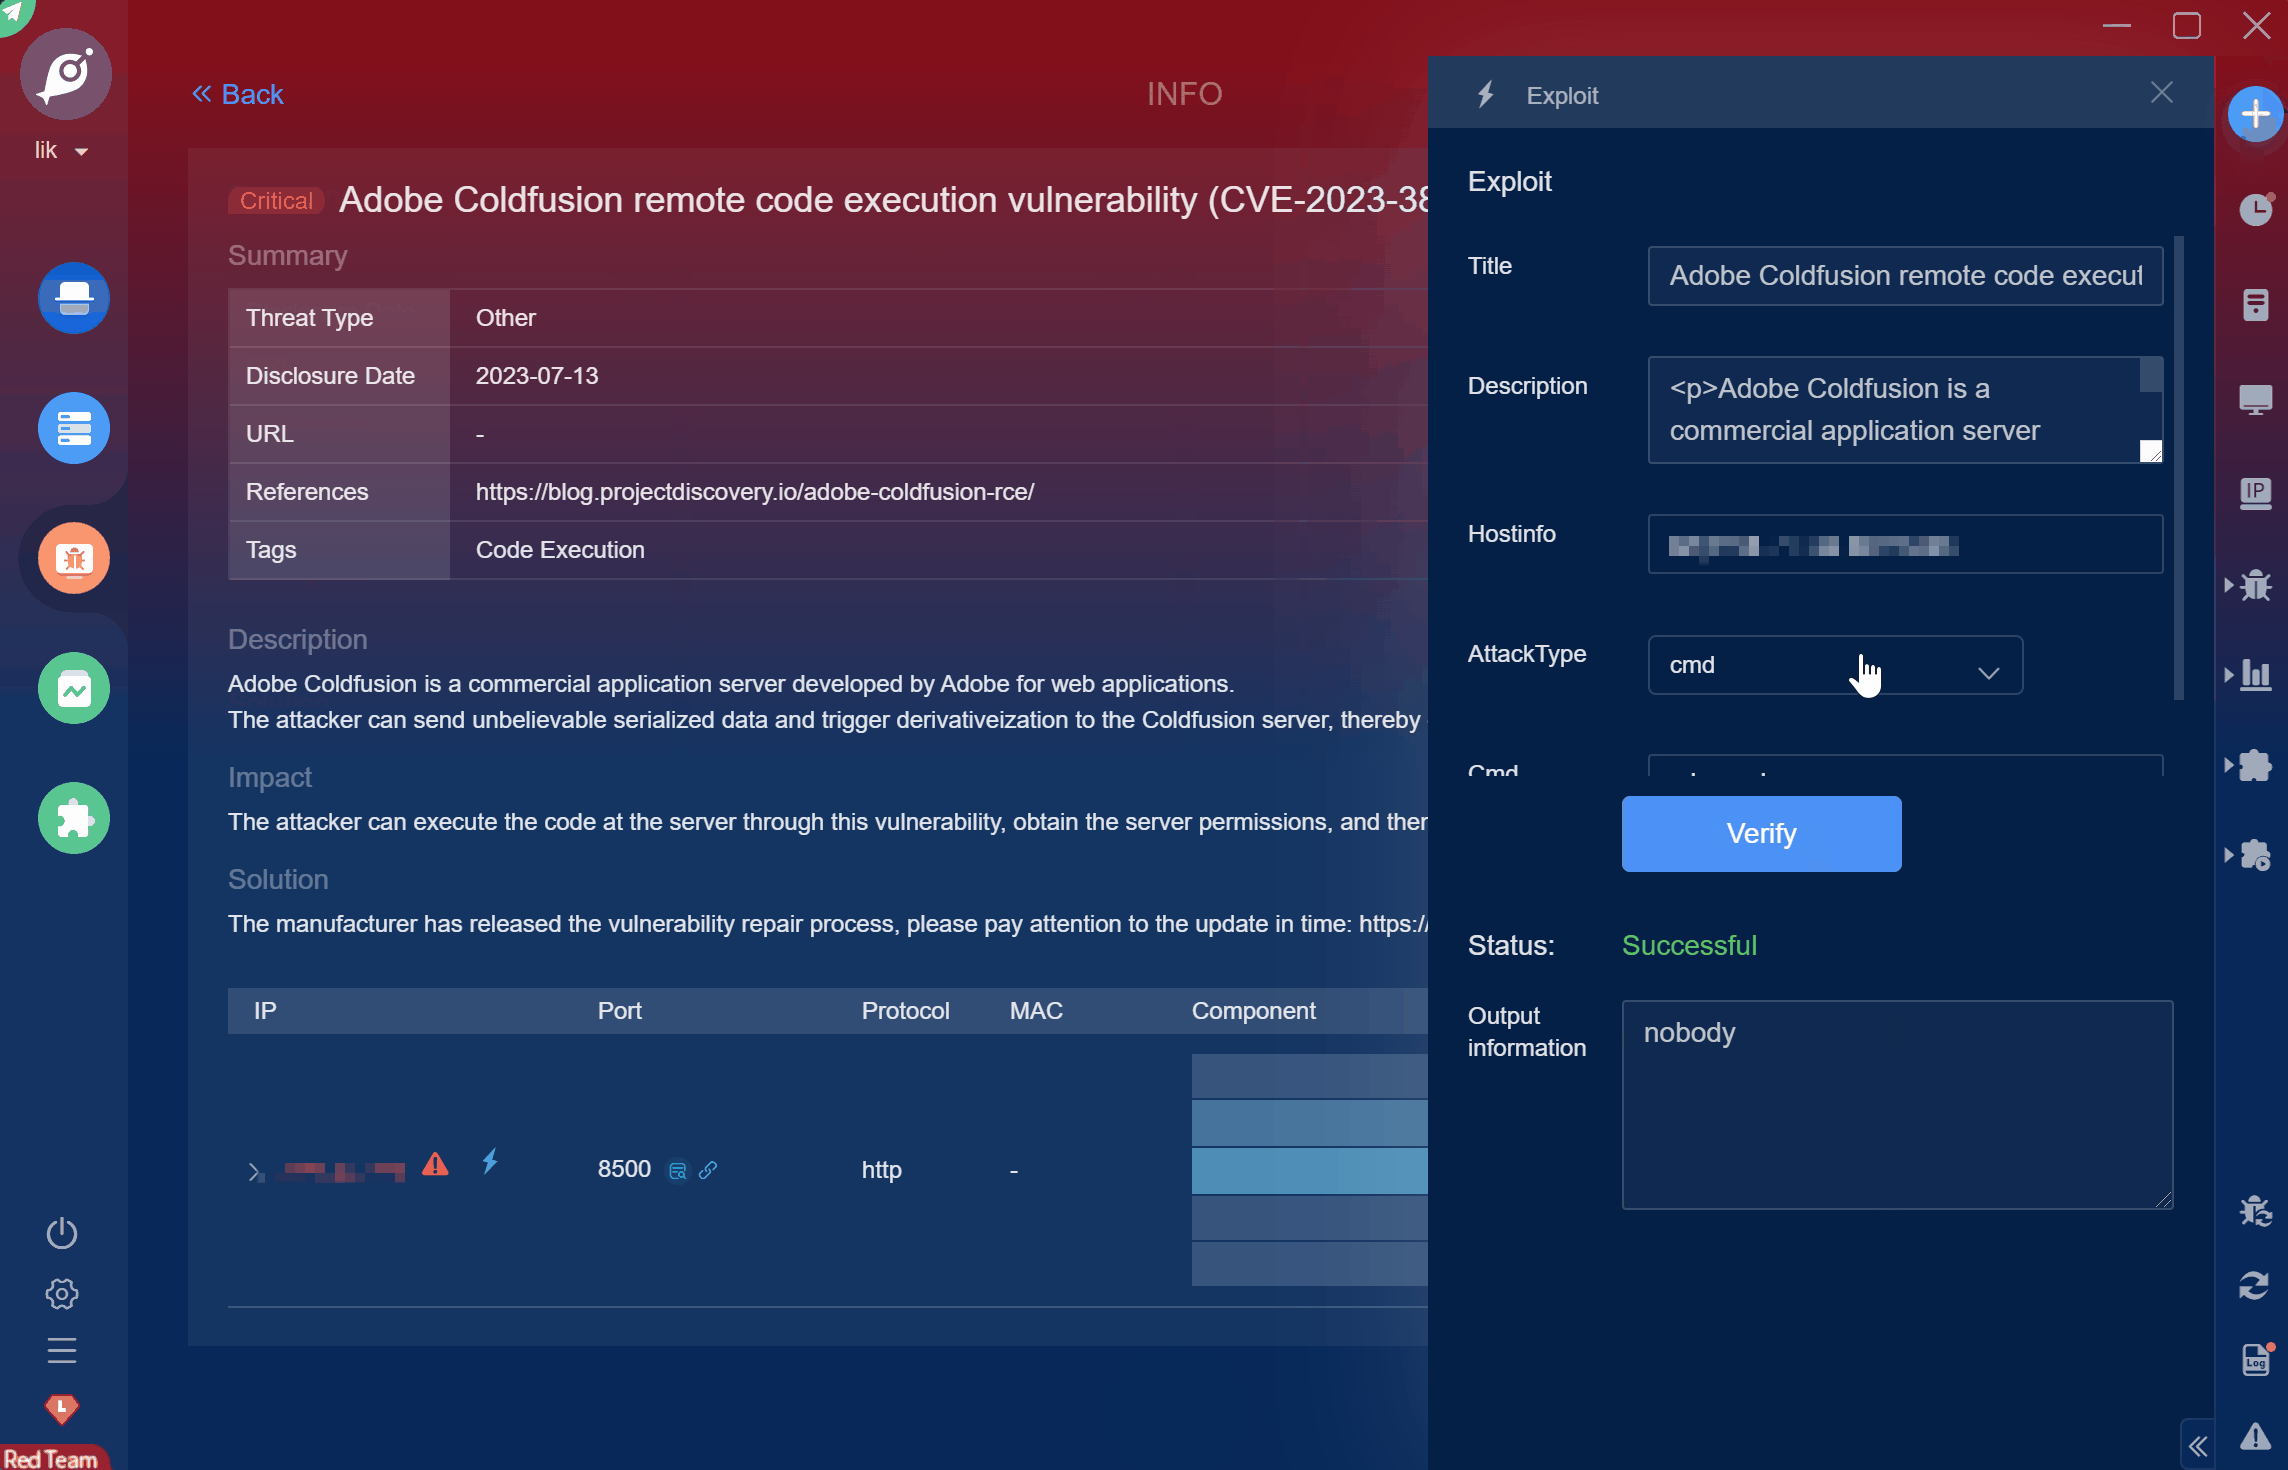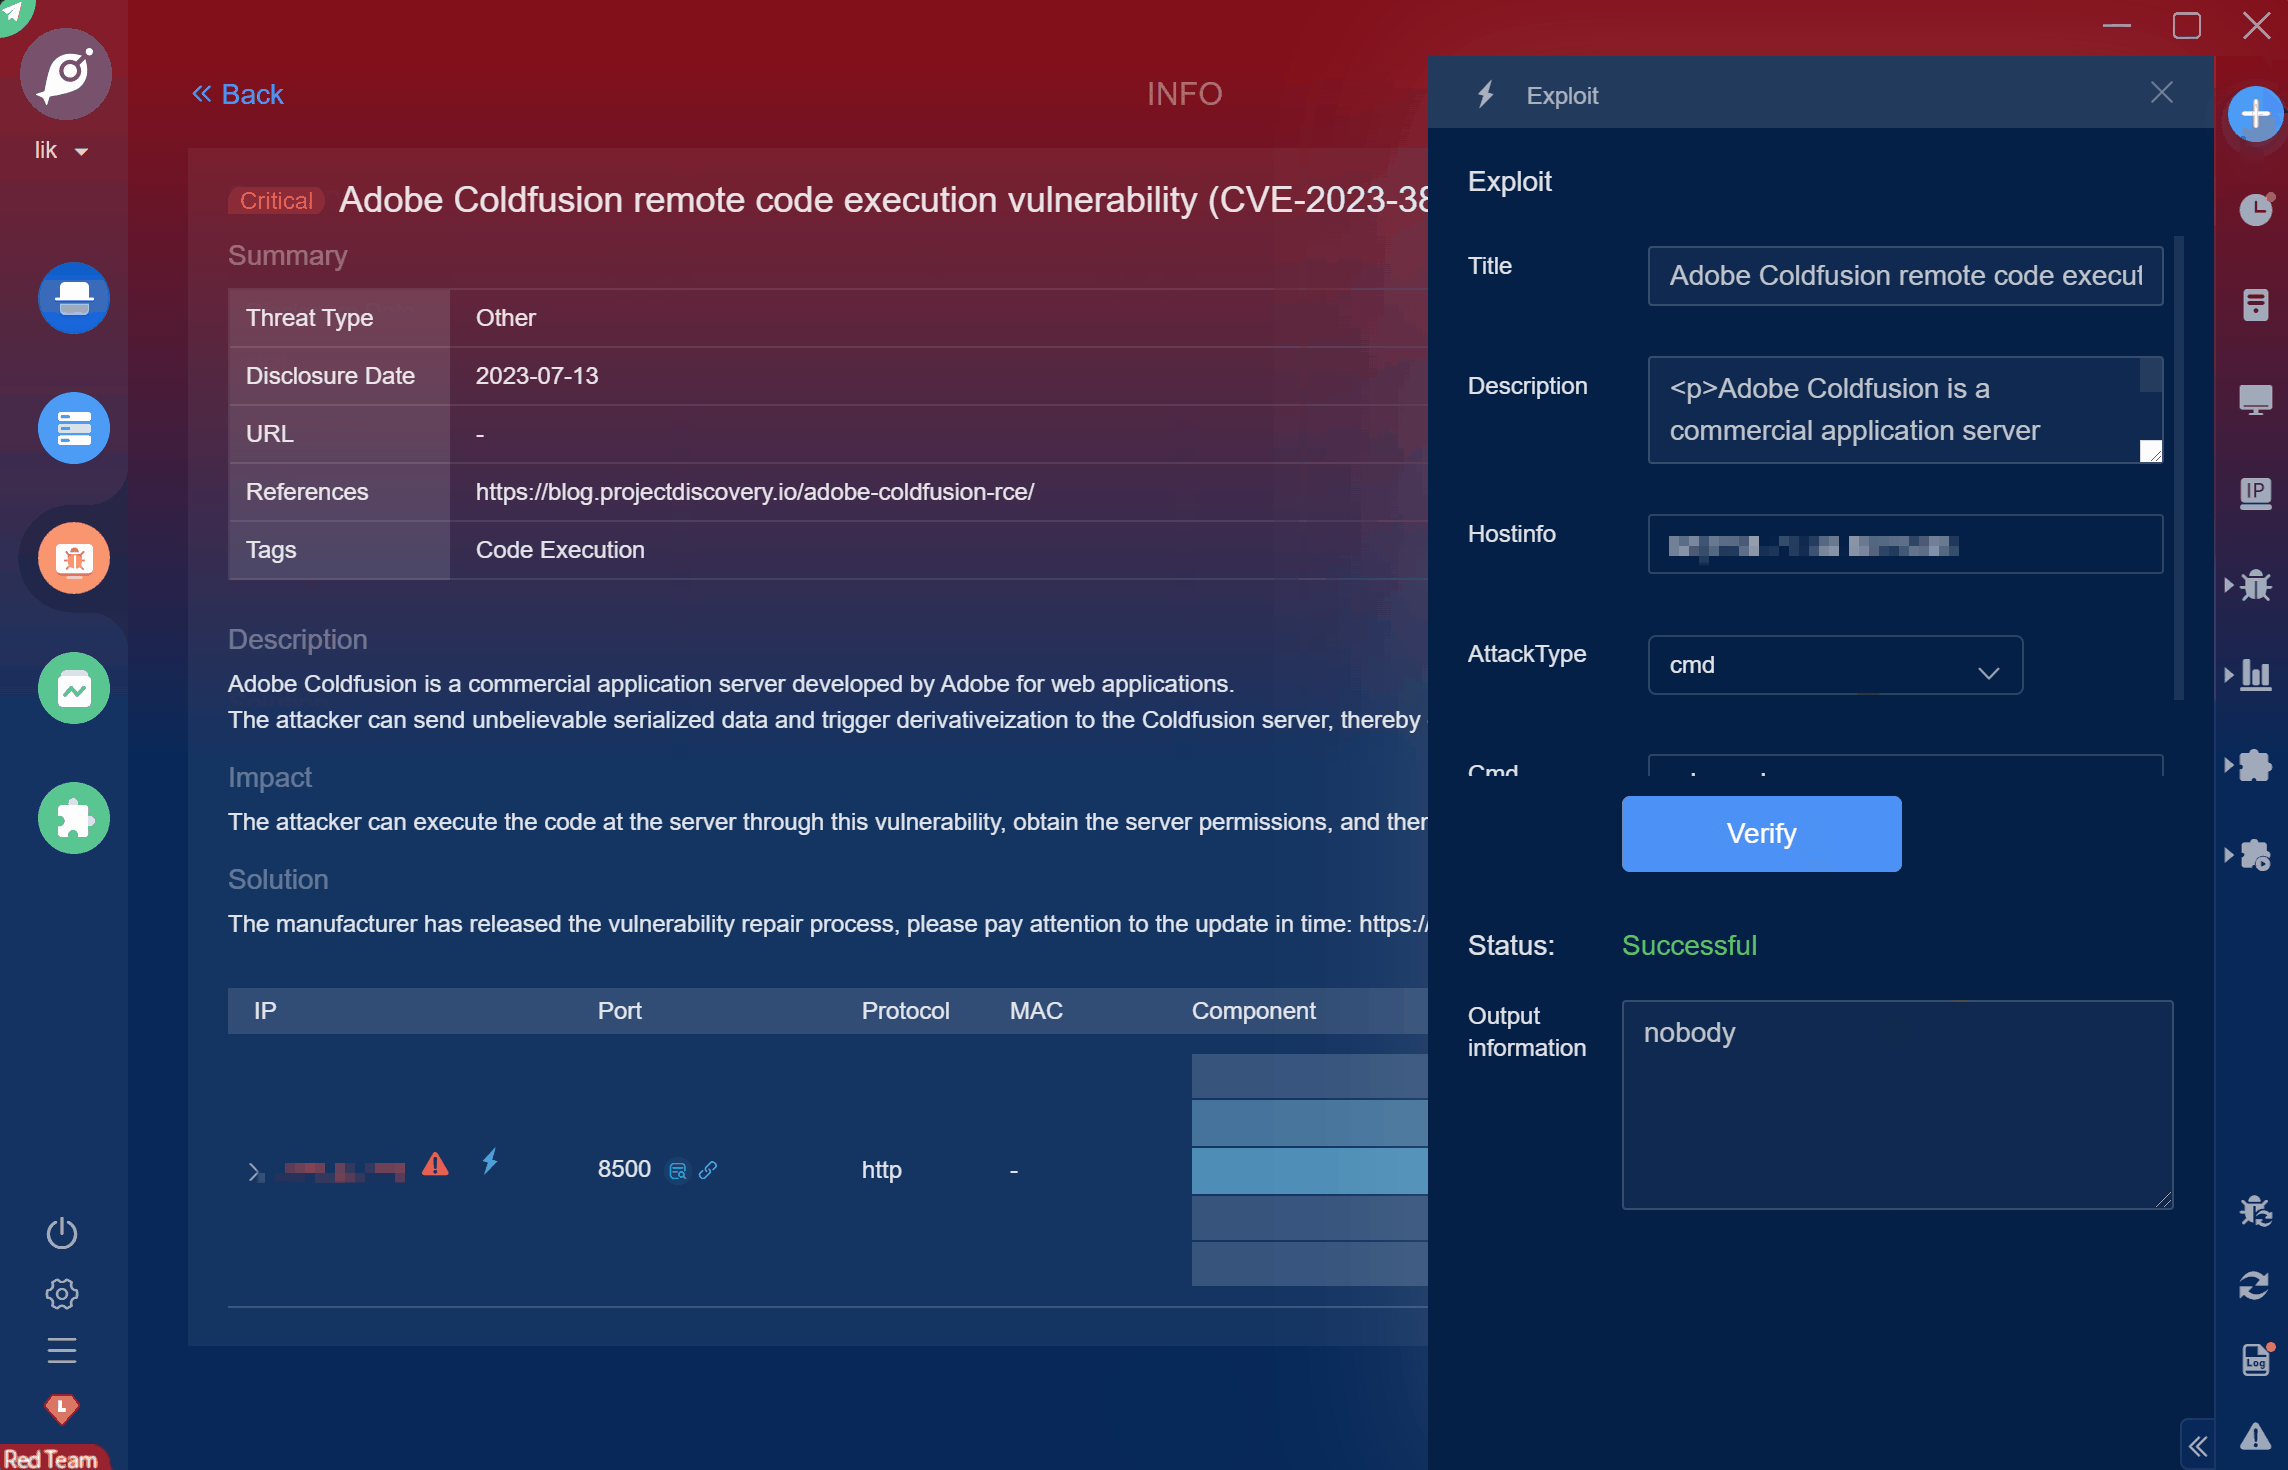
Adobe Coldfusion remote code execution vulnerability (CVE-2023-38203)
| Vulnerability | Adobe Coldfusion remote code execution vulnerability (CVE-2023-38203) |
|---|---|
| Chinese name | Adobe ColdFusion 远程代码执行漏洞(CVE-2023-38203) |
| CVSS core | 9.8 |
| FOFA Query (click to view the results directly) | (body="crossdomain.xml" && body="CFIDE") || (body="#000808" && body="#e7e7e7") |
| Number of assets affected | 3740 |
| Description | Adobe Coldfusion is a commercial application server developed by Adobe for web applications.The attacker can send unbelievable serialized data and trigger derivativeization to the Coldfusion server, thereby executing any code. |
| Impact | The attacker can execute the code at the server through this vulnerability, obtain the server permissions, and then control the entire web server. |