mirror of
https://github.com/gobysec/GobyVuls.git
synced 2026-10-24 17:04:30 +00:00
Update GobyVuls-Document.md
This commit is contained in:

1 file changed
+15
@@ -1,6 +1,21 @@
|
||||
# Goby History Update Vulnerability Total Document (Continuously Update)
|
||||
The following content is an updated vulnerability from Goby. Some of the vulnerabilities are recorded on the screen for easy viewing.
|
||||
|
||||
**Updated document date: July 1, 2025**
|
||||
|
||||
## Akamai CloudTest /concerto/services/RepositoryService XML External Entity Injection Vulnerability (CVE-2025-49493)
|
||||
| **Vulnerability** | Akamai CloudTest /concerto/services/RepositoryService XML External Entity Injection Vulnerability (CVE-2025-49493)|
|
||||
| :----: | :-----|
|
||||
| **Chinese name** |Akamai CloudTest /concerto/services/RepositoryService XML外部实体注入漏洞(CVE-2025-49493) |
|
||||
| **CVSS core** | 8.0 |
|
||||
| **FOFA Query** (click to view the results directly)| [(title="Akamai CloudTest" || body="/imageMaster.png") || (body="Akamai CloudTest build" && body="collector component version")]
|
||||
| **Number of assets affected** | 5600+ |
|
||||
| **Description** |Akamai CloudTest is a cloud service product used for testing and optimizing website performance. The SOAP endpoint in the product (e.g., /concerto/services/RepositoryService) contains an XML External Entity (XXE) injection vulnerability. Due to improper disabling of DTD processing, attackers can read sensitive files on the server (e.g., /etc/passwd) through carefully crafted XML requests. |
|
||||
| **Impact** | This vulnerability is low in exploitation difficulty but severe in impact, allowing attackers to steal sensitive system information. Enterprises are advised to immediately apply the latest patch provided by Akamai to mitigate the risk.|
|
||||
| **Affected versions** | version <12988
|
||||
|
||||
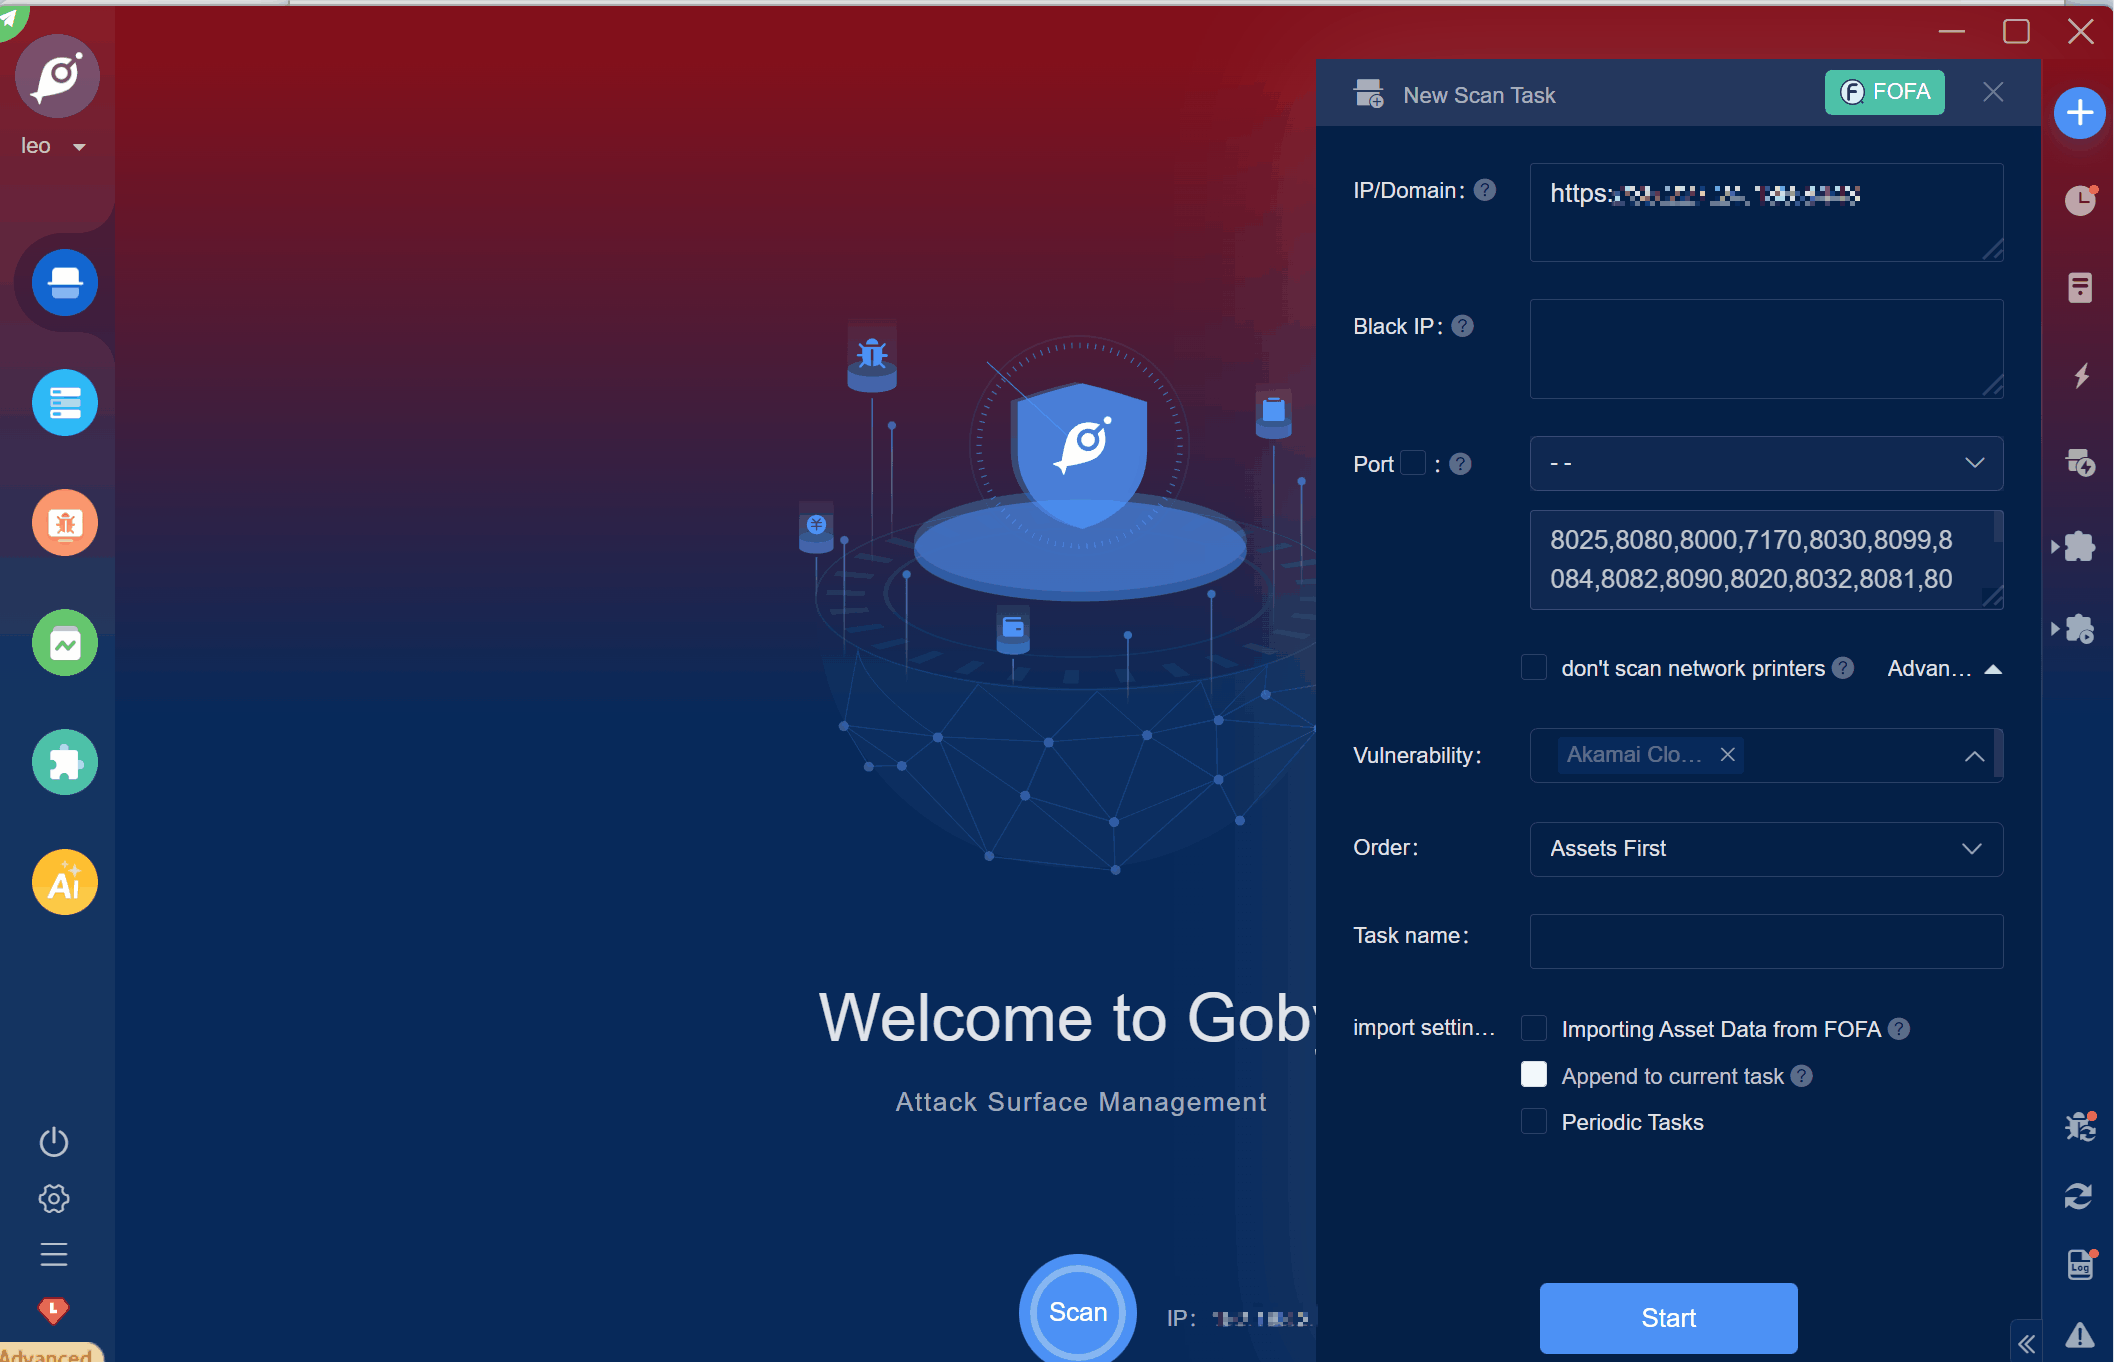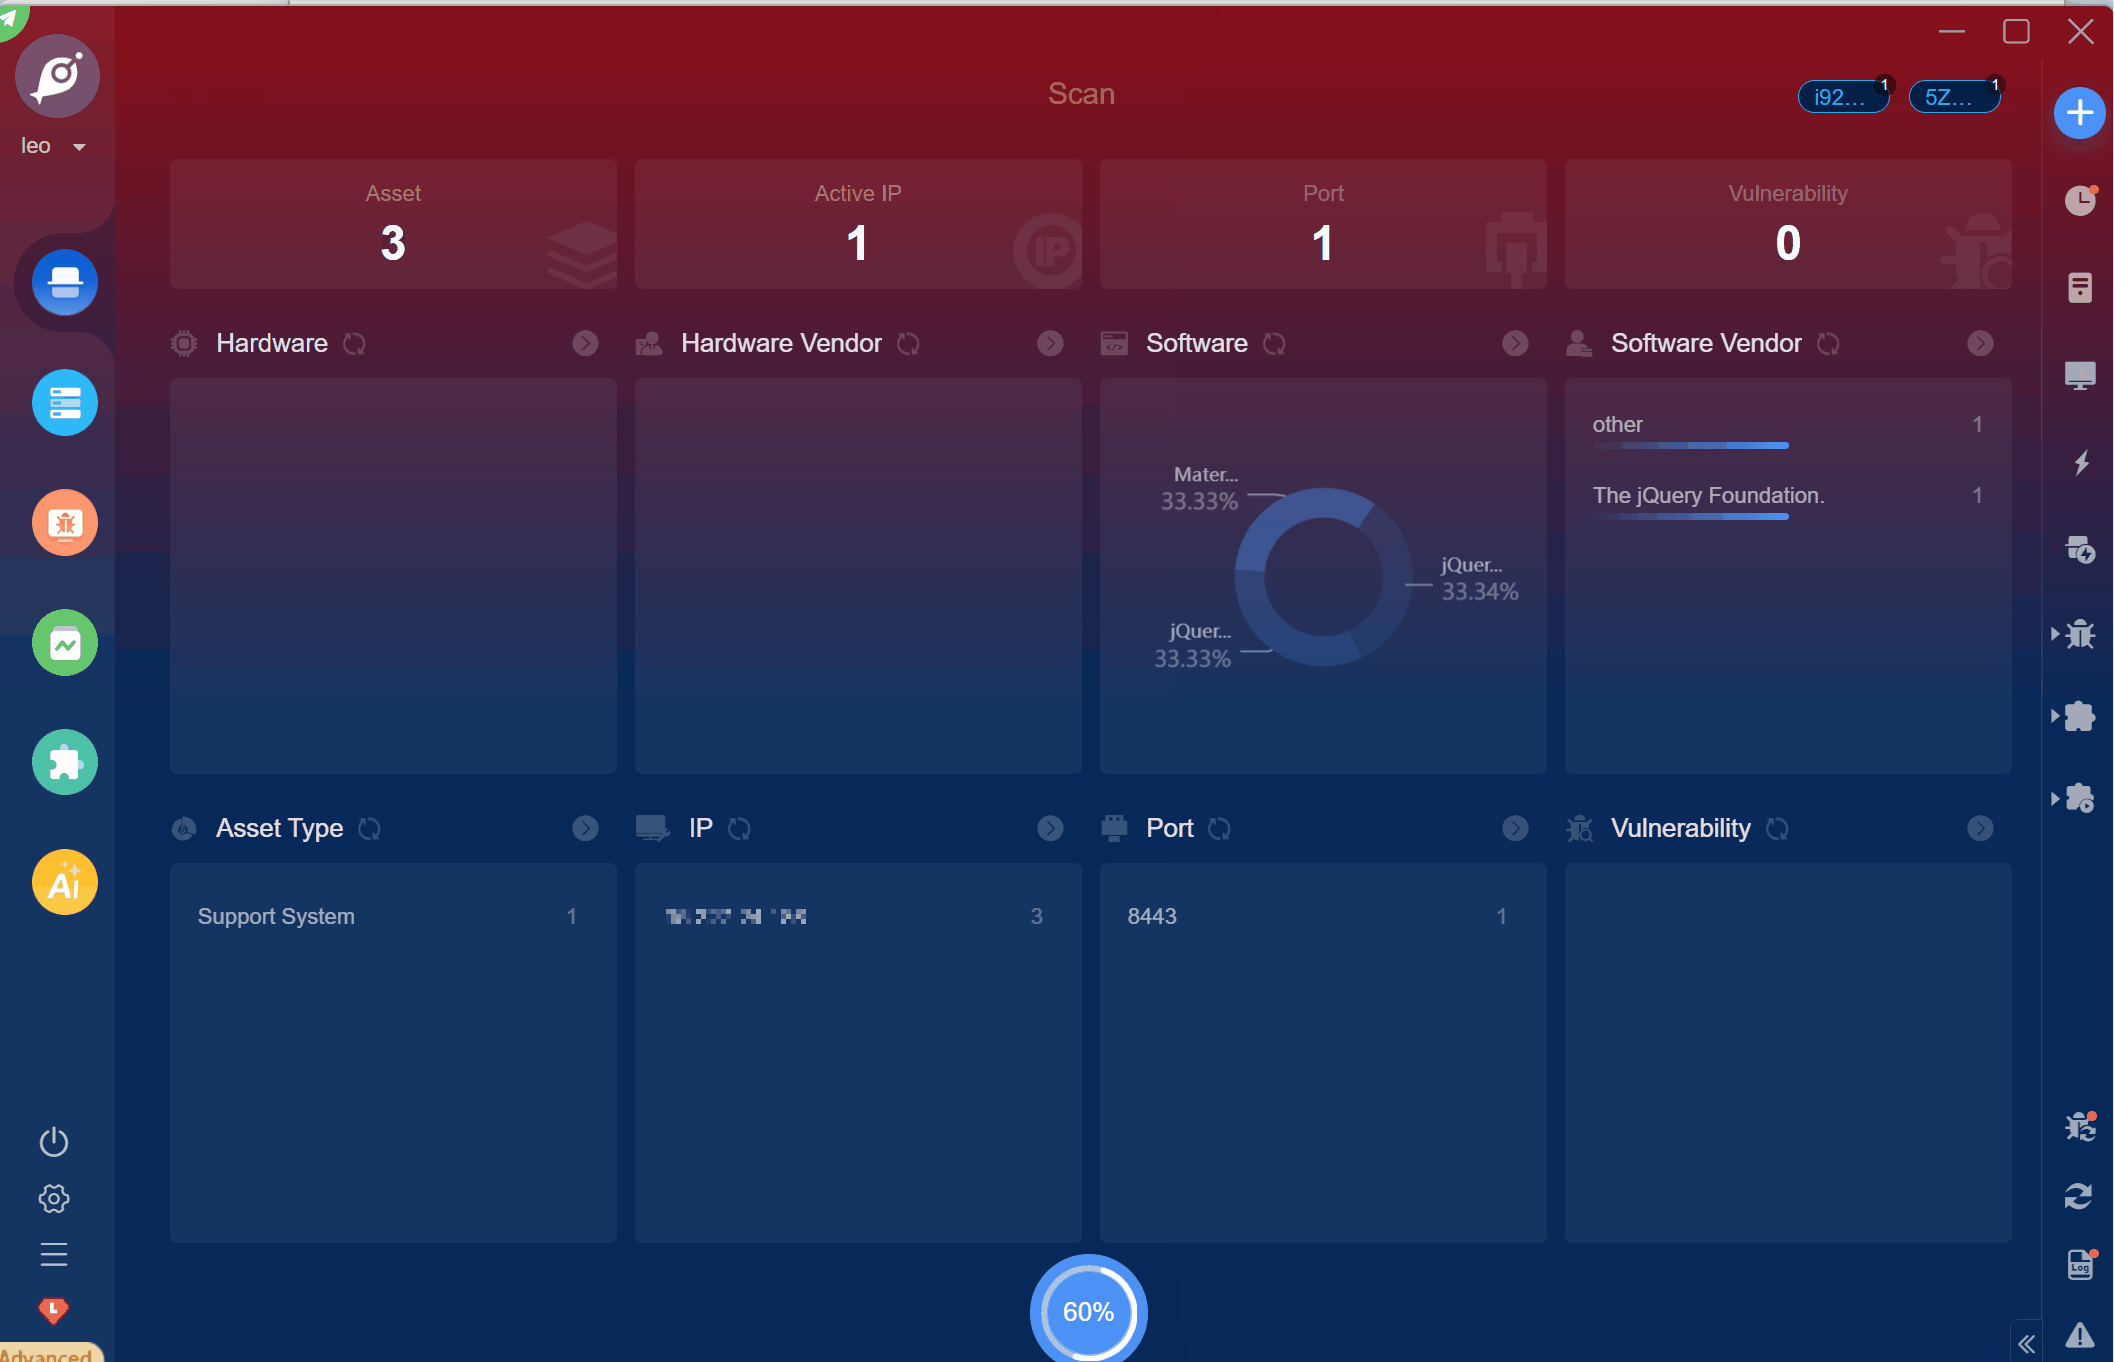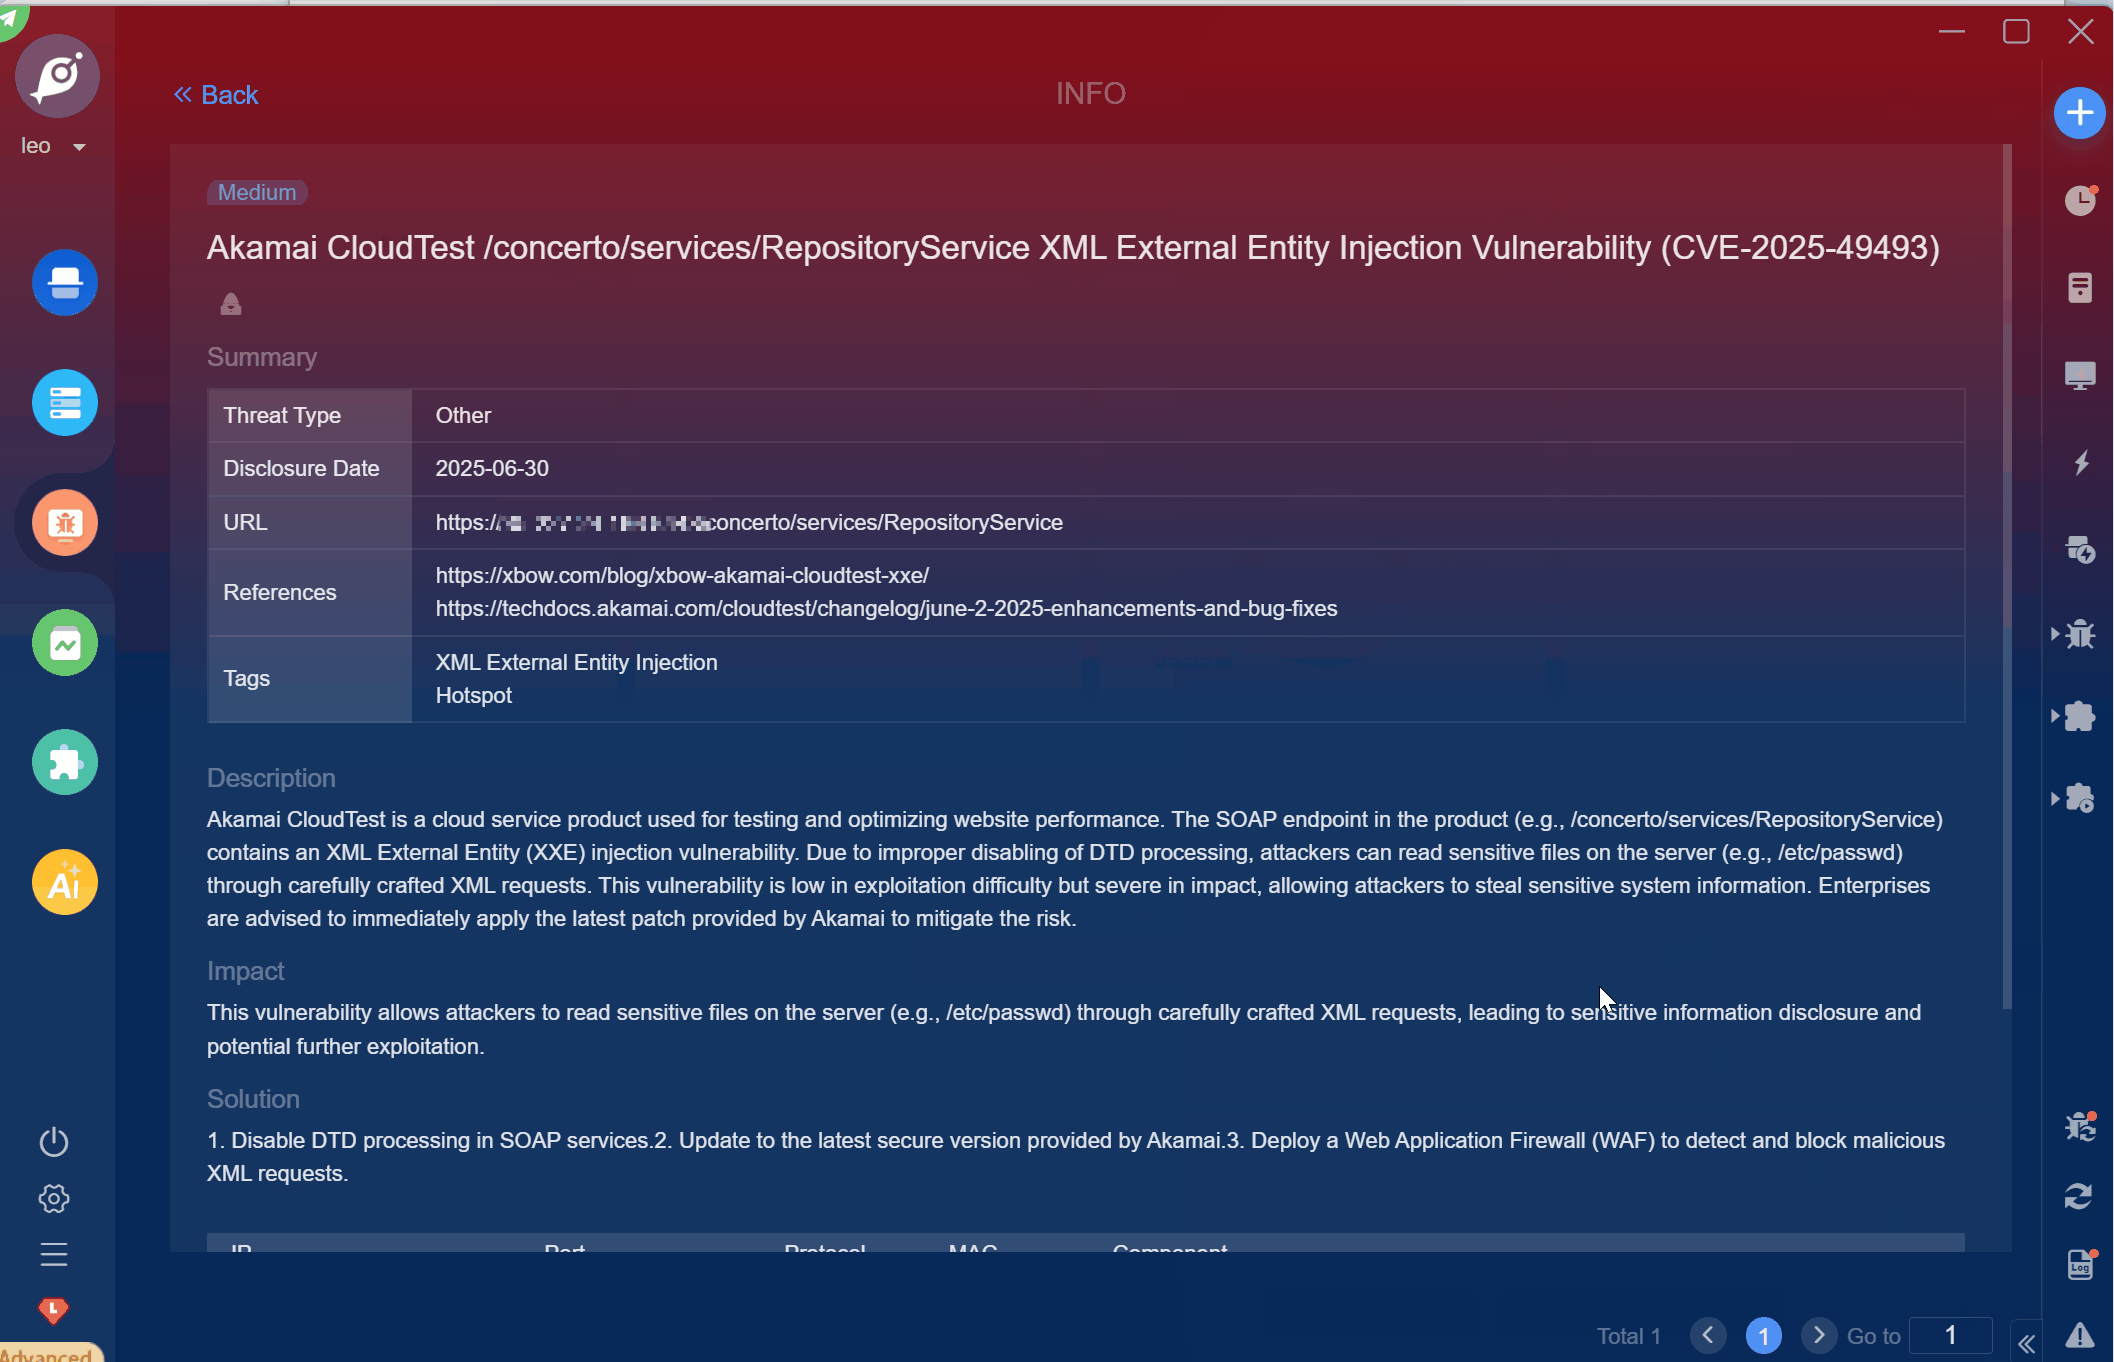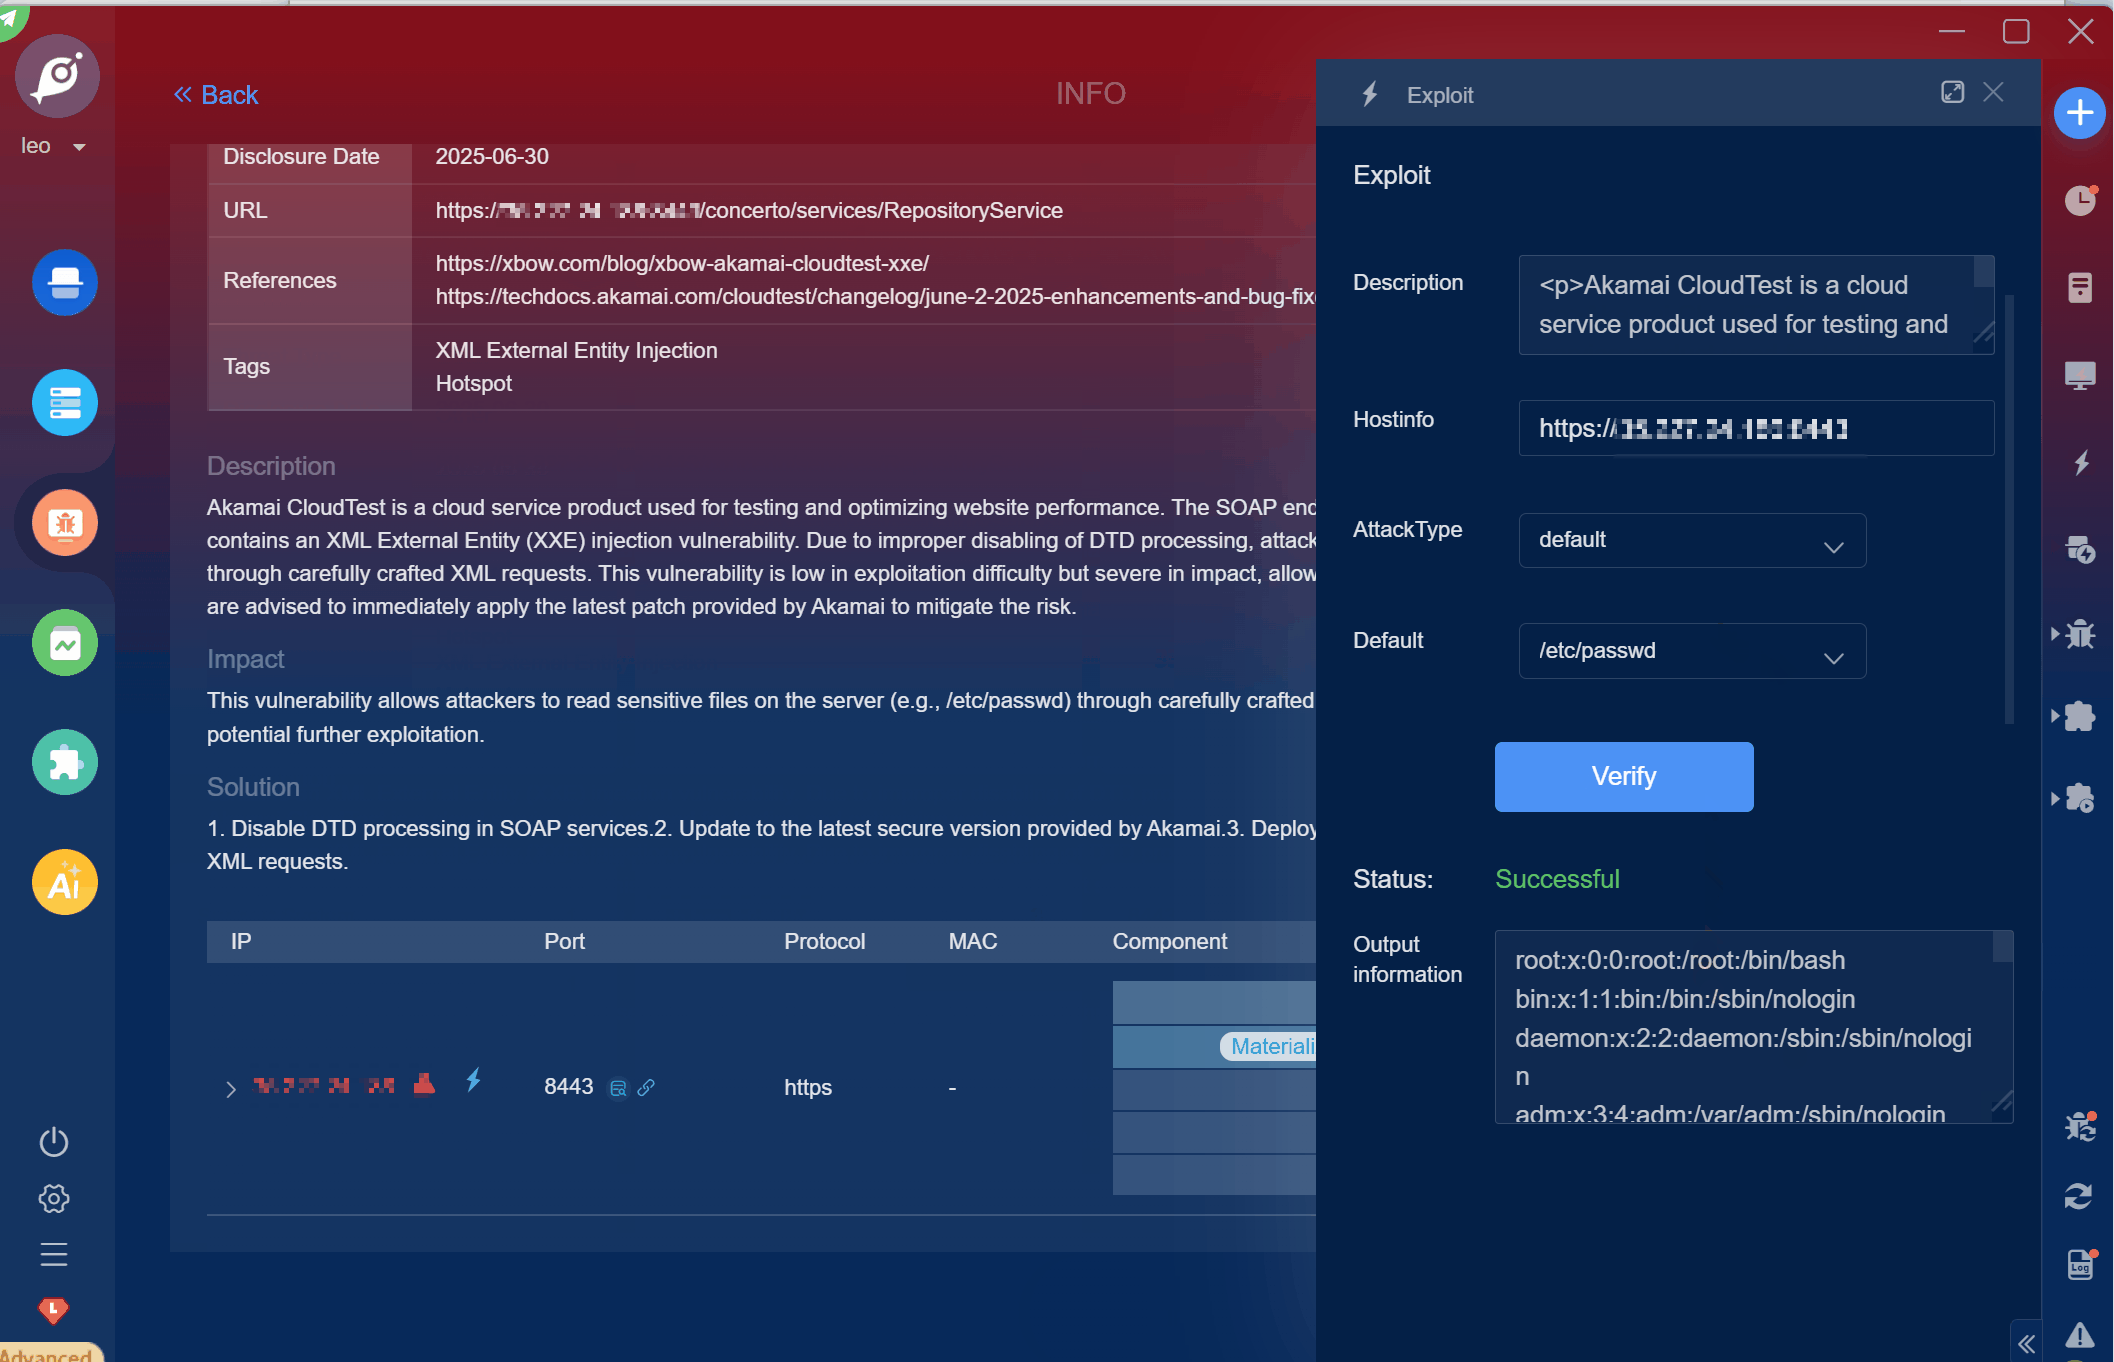
|
||||
|
||||
**Updated document date: April 25, 2025**
|
||||
|
||||
## Erlang/OTP SSH Server Code Execution Vulnerability (CVE-2025-32433)
|
||||
|
||||
Reference in new issue
Block a user