mirror of
https://github.com/gobysec/GobyVuls.git
synced 2026-10-24 08:54:28 +00:00
Add documentation for Next.js CVE-2025-55182
Document details the Next.js Code Execution Vulnerability (CVE-2025-55182), including its impact, affected versions, and security implications.
This commit is contained in:

1 file changed
+13
@@ -0,0 +1,13 @@
|
||||
**Updated document date: December 05, 2025**
|
||||
|
||||
## Next.js Code Execution Vulnerability(CVE-2025-55182)
|
||||
| **Vulnerability** | Next.js Code Execution Vulnerability(CVE-2025-55182)|
|
||||
| :----: | :-----|
|
||||
| **Chinese name** |Next.js 代码执行漏洞|
|
||||
| **CVSS core** | 10.0 |
|
||||
| **FOFA Query** (click to view the results directly)| [header="Next.js" && body="/_next/static"]
|
||||
| **Number of assets affected** | 800W+ |
|
||||
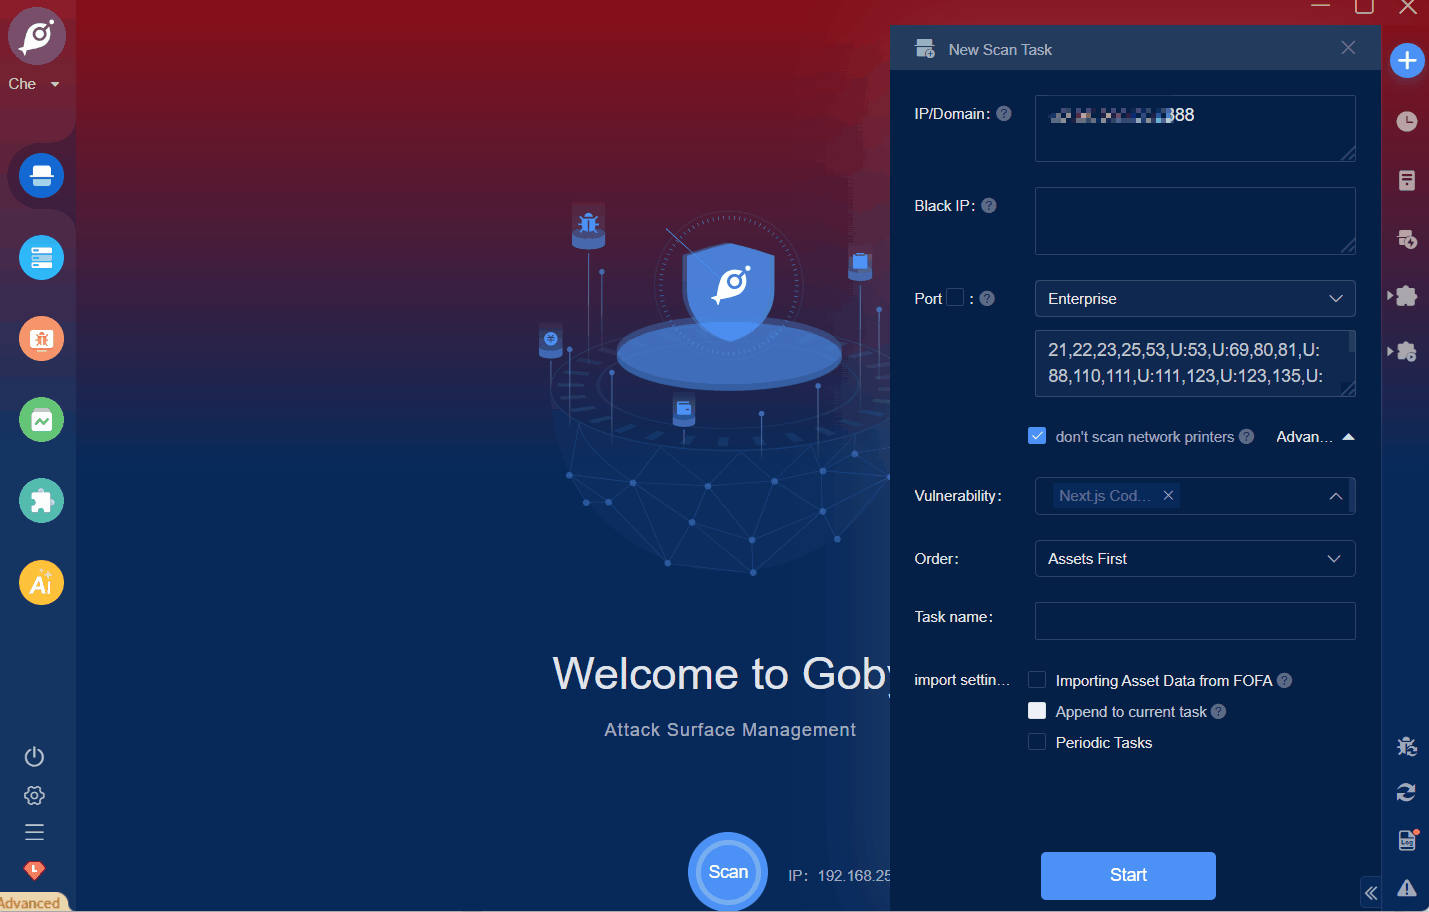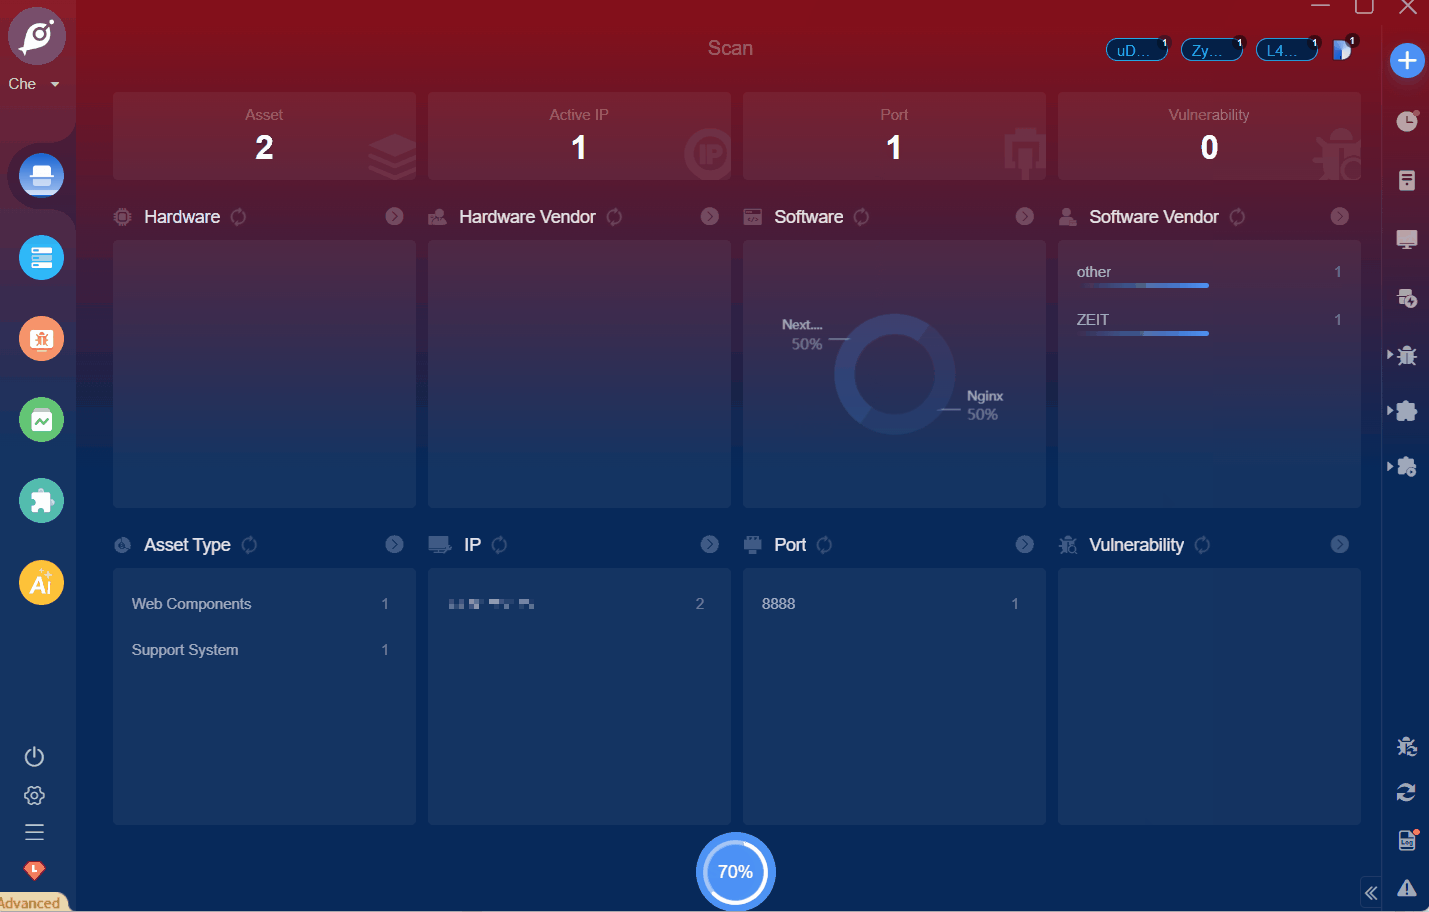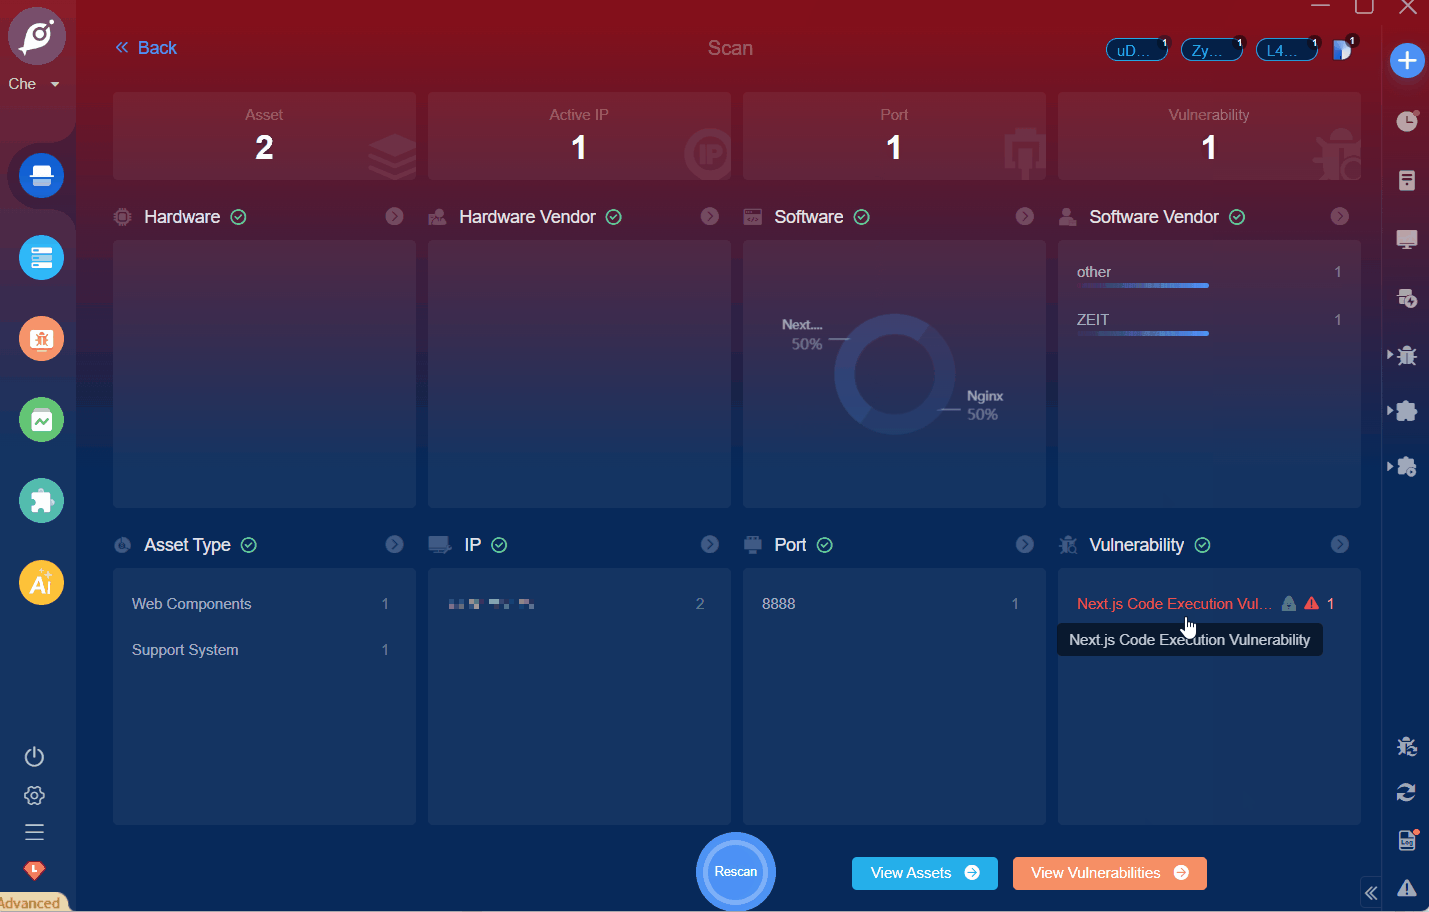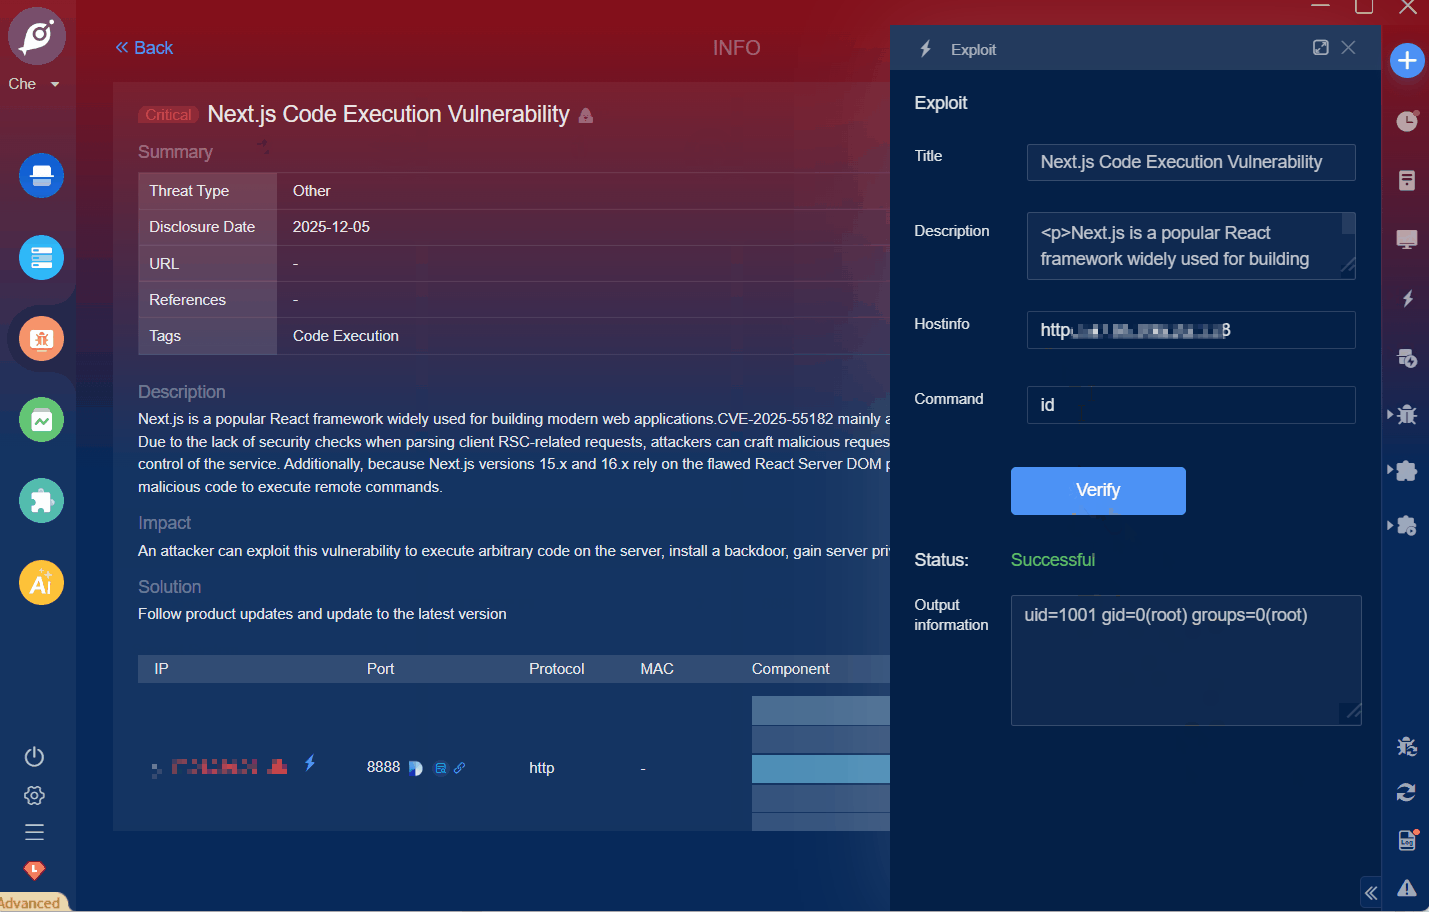
| **Description** |Next.js is a popular React framework widely used for building modern web applications.CVE-2025-55182 mainly affects the Server Actions feature of react-server-dom-webpack. Due to the lack of security checks when parsing client RSC-related requests, attackers can craft malicious requests to execute arbitrary code on the server and even take full control of the service. Additionally, because Next.js versions 15.x and 16.x rely on the flawed React Server DOM package when using the App Router, attackers can also inject malicious code to execute remote commands.|
|
||||
| **Impact** | An attacker can exploit this vulnerability to execute arbitrary code on the server, install a backdoor, gain server privileges, and ultimately take control of the entire web server.|
|
||||
|
||||
|
||||
Reference in new issue
Block a user