mirror of
https://github.com/gelusus/wxvl.git
synced 2026-10-28 19:30:54 +00:00
【已复现】n8n 前台远程代码执行漏洞(CVE-2026-21858)、【安全圈】安卓 ∕ Linux 内核高危漏洞 CVE-2025-38352 验证性利用代码已公开、【安全圈】GoBruteforcer 僵尸网络全球攻击 Linux 服务器,5 万台公网服务器面临风险、自动化平台n8n曝高危漏洞CVE-2026-21858,10万服务器面临接管风险、RuoYi-4.6.0代码审计之SQL注入漏洞、指纹识别+精准化 POC 攻击、2025年12月企业必修安全漏洞清单、n8n 满分漏洞 Ni8mare 可导致服务器遭劫持、Veeam 修复备份服务器中的RCE漏洞、【安全圈】三星 SSD 管理软件曝高危漏洞、2025年12月企业必修安全漏洞清单、【高危预警】Veeam备份软件曝出 CVSS 9.0 远程代码执行漏洞,勒索软件可利用其破坏备份数据、黑客利用0Day漏洞工具包在野攻击VMware ESXi实例、【已复现】ComfyUI-Manager存在远程代码执行(CVE-2025-67303)、高危漏洞威胁情报合集 (2026-01-08)、ByteSRC开年首测|火山引擎AI业务单个漏洞赏金10万元!、DLL 劫持复现记录(显式加载)、【接口漏洞第三章第四节】进阶实战:如何用 Burp Intruder “暴力推理”出隐藏的API端点?、【附POC及复现环境】n8n双CVE漏洞利用链可致远程代码执行漏洞(CVE-2026-21858+CVE-2025-68613)、【安全圈】黑客利用0Day漏洞工具包在野攻击VMware ESXi实例、【论文速读】| 用于软件供应链安全自主防御的Agentic AI:从溯源到漏洞缓解、【漏洞通告】n8n Webhook 请求处理不当导致未经身份验证的文件访问漏洞(CVE-2026-21858)、【已复现】ComfyUI-Manager 远程代码执行漏洞(CVE-2025-67303)、【已复现】n8n任意文件读取到沙箱逃逸 RCE(CVE-2026-21858)、【漏洞通告】n8n 远程代码执行漏洞(CVE-2026-21877)、
This commit is contained in:
 test committed
1 parent
eec6c2b2c2
commit
5ba4f5b851
25 files changed
+4397
-1
No files matched your search
@@ -16321,5 +16321,30 @@
|
||||
"https://mp.weixin.qq.com/s/E3pSbQBXpa7TVIZwhf-vfw": "网安实验干货每日分享Tomcat任意文件上传(CVE-2017-12615)-0108",
|
||||
"https://mp.weixin.qq.com/s/L64Q_Rf1ZC_vM4U6skeqng": "【扩充版】“任意用户漏洞”全景手册 20+ 实战案例",
|
||||
"https://mp.weixin.qq.com/s/ezMAgrMG82zFRfm1E-MO5Q": "【风险提示】MongoDB高危漏洞爆发!速查!!!",
|
||||
"https://mp.weixin.qq.com/s/Q2siDO0_xGYbvwPzbOaP_Q": "蓝凌OA漏洞利用总结"
|
||||
"https://mp.weixin.qq.com/s/Q2siDO0_xGYbvwPzbOaP_Q": "蓝凌OA漏洞利用总结",
|
||||
"https://mp.weixin.qq.com/s/OT_eiXOGfDf2l7D6fq-pIQ": "【已复现】n8n 前台远程代码执行漏洞(CVE-2026-21858)",
|
||||
"https://mp.weixin.qq.com/s/AU9RXBp44RhMTV904AcRKA": "【安全圈】安卓 ∕ Linux 内核高危漏洞 CVE-2025-38352 验证性利用代码已公开",
|
||||
"https://mp.weixin.qq.com/s/NBUe4Dd_wtmcqdx4WBnkJw": "【安全圈】GoBruteforcer 僵尸网络全球攻击 Linux 服务器,5 万台公网服务器面临风险",
|
||||
"https://mp.weixin.qq.com/s/SW0lK1tkMKy4kZp75QCOQg": "自动化平台n8n曝高危漏洞CVE-2026-21858,10万服务器面临接管风险",
|
||||
"https://mp.weixin.qq.com/s/c5B5ZoxefiBiXe508mJUig": "RuoYi-4.6.0代码审计之SQL注入漏洞",
|
||||
"https://mp.weixin.qq.com/s/pJUqfDpIlO2W_EjpsoS0FQ": "指纹识别+精准化 POC 攻击",
|
||||
"https://mp.weixin.qq.com/s/SDB4K0KqBlLAU9XKa45LJQ": "2025年12月企业必修安全漏洞清单",
|
||||
"https://mp.weixin.qq.com/s/Ad6eB5A_OqdHTb5lnI8yPQ": "n8n 满分漏洞 Ni8mare 可导致服务器遭劫持",
|
||||
"https://mp.weixin.qq.com/s/9cJkv84S0QsPngqElYpr3Q": "Veeam 修复备份服务器中的RCE漏洞",
|
||||
"https://mp.weixin.qq.com/s/-N1zflcEp9hrdPxEBk7oIA": "【安全圈】三星 SSD 管理软件曝高危漏洞",
|
||||
"https://mp.weixin.qq.com/s/ZH8WqVbJkrbJdGvD5E_rSQ": "2025年12月企业必修安全漏洞清单",
|
||||
"https://mp.weixin.qq.com/s/uc2NAhKIHqc5XHfcy4U5dg": "【高危预警】Veeam备份软件曝出 CVSS 9.0 远程代码执行漏洞,勒索软件可利用其破坏备份数据",
|
||||
"https://mp.weixin.qq.com/s/RkoaOPT2SHSLU1qLHgO-tg": "黑客利用0Day漏洞工具包在野攻击VMware ESXi实例",
|
||||
"https://mp.weixin.qq.com/s/4Y3mPSZ0hBmlLyni7xjVKQ": "【已复现】ComfyUI-Manager存在远程代码执行(CVE-2025-67303)",
|
||||
"https://mp.weixin.qq.com/s/cJ_wE479L1ASzLrW9ojZWA": "高危漏洞威胁情报合集 (2026-01-08)",
|
||||
"https://mp.weixin.qq.com/s/fXWXAQePehmW8wCHTWIjXA": "ByteSRC开年首测|火山引擎AI业务单个漏洞赏金10万元!",
|
||||
"https://mp.weixin.qq.com/s/xtGFMRLNafQ27jLNRRDPeA": "DLL 劫持复现记录(显式加载)",
|
||||
"https://mp.weixin.qq.com/s/sbqRMy26Ep11ToJpgVV4Ag": "【接口漏洞第三章第四节】进阶实战:如何用 Burp Intruder “暴力推理”出隐藏的API端点?",
|
||||
"https://mp.weixin.qq.com/s/bDfdME5ie6Nmwz2S7Ao_dg": "【附POC及复现环境】n8n双CVE漏洞利用链可致远程代码执行漏洞(CVE-2026-21858+CVE-2025-68613)",
|
||||
"https://mp.weixin.qq.com/s/8XdsB9mCjaoxjL9PtZzYag": "【安全圈】黑客利用0Day漏洞工具包在野攻击VMware ESXi实例",
|
||||
"https://mp.weixin.qq.com/s/5GRQbN_ZqpiiOGKib41FsA": "【论文速读】| 用于软件供应链安全自主防御的Agentic AI:从溯源到漏洞缓解",
|
||||
"https://mp.weixin.qq.com/s/M3euwAuL5jBaPTPTc8RBYg": "【漏洞通告】n8n Webhook 请求处理不当导致未经身份验证的文件访问漏洞(CVE-2026-21858)",
|
||||
"https://mp.weixin.qq.com/s/U8qYF4Y3SmTPARPEJjFSVA": "【已复现】ComfyUI-Manager 远程代码执行漏洞(CVE-2025-67303)",
|
||||
"https://mp.weixin.qq.com/s/jlBpcZBdlq_P_tQZZCQZDA": "【已复现】n8n任意文件读取到沙箱逃逸 RCE(CVE-2026-21858)",
|
||||
"https://mp.weixin.qq.com/s/u5lm3LJFVihrD5LjZy1ASw": "【漏洞通告】n8n 远程代码执行漏洞(CVE-2026-21877)"
|
||||
}
|
||||
File diff suppressed because it is too large.
Load diff
@@ -0,0 +1,192 @@
|
||||
# ByteSRC开年首测|火山引擎AI业务单个漏洞赏金10万元!
|
||||
字节跳动安全中心 2026-01-08 11:13
|
||||
|
||||
|
||||
|
||||
|
||||
**专测时间**
|
||||
|
||||
|
||||
1月9日-1月23日
|
||||
|
||||
报告标题请备注【火山AI专测】
|
||||
|
||||
需通过SRC平台“热门活动”模块提交
|
||||
|
||||
src.bytedance.com
|
||||
|
||||
专测范围
|
||||
|
||||
|
||||
- 大模型服务平台:
|
||||
|
||||
www.volcengine.com/product/ark
|
||||
|
||||
- 大模型生态广场:
|
||||
|
||||
www.volcengine.com/mcp-marketplace,火山引擎云原生 MCP Server
|
||||
|
||||
- 大模型应用开发:
|
||||
|
||||
Coze、知识库、VikingDB 向量数据库
|
||||
|
||||
- 大模型应用:
|
||||
|
||||
www.volcengine.com/product/ai-app-lab,应用广场上线的火山引擎自研AI Agent
|
||||
|
||||
- LUMI:
|
||||
|
||||
https://console.volcengine.com/lumi
|
||||
|
||||
- 虚拟数字人:
|
||||
|
||||
https://console.volcengine.com/avatar/
|
||||
|
||||
- 联网问答Agent:
|
||||
|
||||
https://console.volcengine.com/ask-echo
|
||||
|
||||
- AI特效平台(Ebox):
|
||||
|
||||
https://console.volcengine.com/ebox/home
|
||||
|
||||
- 智能创作云:
|
||||
|
||||
https://console.volcengine.com/muse/home/smartRecommend
|
||||
|
||||
- 智能推荐平台:
|
||||
|
||||
https://www.volcengine.com/product/rec
|
||||
|
||||
- agentkit:
|
||||
|
||||
https://www.volcengine.com/product/agentkit
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**专测奖励**
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
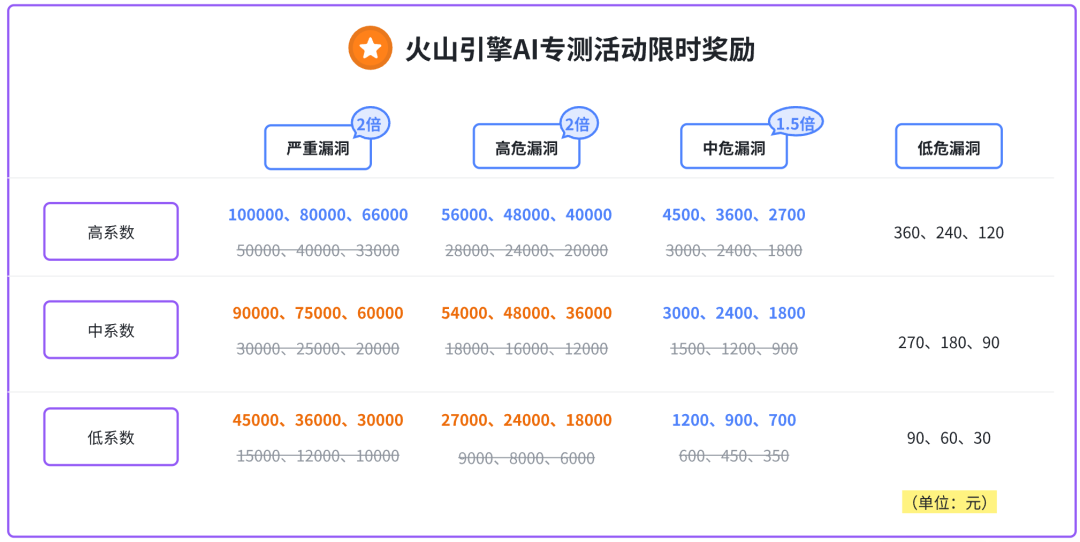
奖励一 单个漏洞可达100,000元!
|
||||
|
||||
严重/
|
||||
高危
|
||||
漏洞,享有
|
||||
**2倍**
|
||||
积分
|
||||
|
||||
中危漏洞,享有 **1.5倍**
|
||||
积分
|
||||
|
||||
|
||||
|
||||
|
||||
(🍗对利用思路巧妙、利用过程描述清晰的报告给予额外1-50分鸡腿分)
|
||||
|
||||
|
||||
|
||||
|
||||
奖励二 重点漏洞奖励
|
||||
|
||||
**重点漏洞类型(高危及以上)**
|
||||
|
||||
**在翻倍基础上额外奖励2000元/个:**
|
||||
|
||||
****
|
||||
1、容器逃逸(需证明影响其他用户)
|
||||
|
||||
2、
|
||||
全回显SSRF
|
||||
|
||||
3、批量获取登录后的用户会话数据/高敏AK等涉及核心敏感信息泄漏的漏洞
|
||||
|
||||
4、可获取MCP/Agent控制权限的漏洞
|
||||
|
||||
5、涉及任意账号接管/登录的漏洞
|
||||
|
||||
6、模型投毒、模型污染类可影响其他用户交互的漏洞
|
||||
|
||||
|
||||
|
||||
|
||||
奖励三 重点情报奖励
|
||||
|
||||
**重点情报类型(高危及以上)**
|
||||
|
||||
**在翻倍基础上额外奖励2000元/个:**
|
||||
|
||||
****
|
||||
1、对平台算力资源有重大影响的情报
|
||||
|
||||
2、涉及到大量平台用户数据的情报
|
||||
|
||||
****
|
||||
|
||||
**补充说明**
|
||||
|
||||
|
||||
|
||||
1、非信息安全漏洞导致的内容安全风险不收、与模型提示和响应内容相关的问题暂不收取。如这些问题对产品可造成额外的、可直接验证的安全影响(机密性、完整性、可用性),则正常收取。模型提示和响应内容的相关问题举例:
|
||||
|
||||
-模型提示:越狱/安全绕过(如 DAN 等相关提示词)
|
||||
|
||||
-模型响应内容:大模型输出恶意内容(如违规营销信息、恶意代码等,可向产品帮助中心反馈)
|
||||
|
||||
-模型幻觉:让大模型假装成计算机终端并执行命令等
|
||||
|
||||
2、非隐私数据泄露相关的AI服务风险暂不收取(jail break,prompt leak等)。
|
||||
|
||||
3、个人用户从Coze发布至豆包的智能体及插件所引发的安全漏洞不收取(如UGC 内容中用户自身行为导致的信息泄露不收取)。
|
||||
|
||||
4、沙箱环境中的代码执行/命令执行本身是预期的产品功能,如果能逃逸或影响到其他用户容器,则正常评分。(有效条件:逃逸到宿主机/物理机,获取有效敏感信息和权限,或证明通字节内网)
|
||||
|
||||
5、客户端漏洞均以最新版为准
|
||||
|
||||
6、
|
||||
正在专项排查中漏洞,如某系统**、****某类型漏洞内部展开统一的专项治理时暂不收取,具体情况以平台审核人员回复为准。**
|
||||
|
||||
|
||||
7、
|
||||
活动发奖:漏洞通过后,平台将会先下发基础积分,预计2月30日前下发活动额外奖励积分。请师傅们耐心等待❤️
|
||||
|
||||
****
|
||||
|
||||
**测试规范**
|
||||
|
||||
|
||||
**核心原则**
|
||||
|
||||
1、合法化原则:所有测试行为必须遵守《网络安全法》《数据安全法》《个人信息保护法》等法律法规要求。
|
||||
|
||||
2、无害化原则:禁止进行可能引起用户利益受损、业务异常运行的测试行为。
|
||||
|
||||
|
||||
**通用测试规则**
|
||||
|
||||
1、禁止使用可能造成业务影响的测试工具和手法。如:只允许手工低频测试,不允许手工高频发包、或使用自动化工具/插件测试,避免因过度测试导致业务告警、服务中断等问题。
|
||||
|
||||
2、禁止进行内网渗透测试行为和任何有害化的测试行为,包括但不限于:获取内网权限后在内网使用扫描器、或横向接触非对外开放系统目标、获取内网应用/主机权限/数据、上传 webshell、反弹 shell等。
|
||||
|
||||
3、禁止下载、保存、传播业务数据,包括但不限于业务服务器以及Github 等平台泄露的源代码、运营数据、用户资料、登录凭证等,若存在不知情的下载行为,需及时说明和删除;测试过程中获取的相关代码/数据,务必在SRC漏洞确认后立即删除,不得非法留存及使用(无论数据是否脱敏)。
|
||||
|
||||
4、禁止任何类型的网络拒绝服务(DoS 或DDoS)测试,或通过软件、工具自动扫描产生大量数据流量的行为。
|
||||
|
||||
5、禁止进行近源攻击或者黑客物理入侵、社会工程学测试或邮件钓鱼等非技术漏洞测试,尤其是禁止使用社工库等非法手段获取用户密码。
|
||||
|
||||
6、禁止使用任何违反平台规定或法律法规的文字、图片、视频作为测试素材。
|
||||
|
||||
7、禁止以证明漏洞危害为借口,对目标系统进行破坏性操作,如删改数据/配置、植入恶意程序等。
|
||||
|
||||
8、禁止用户打扰类测试。包括但不限于向真实用户邮箱、手机、社媒账号等渠道发送测试信息、发起群聊、推送push等干扰信息;或通过电话、即时通讯工具等方式直接联系真实用户进行测试。
|
||||
|
||||
9、禁止对未授权厂商/业务、超出测试范围列表进行漏洞挖掘,可与管理员联系确认是否属于资产范围后进行挖掘,否则未授权的法律风险将由漏洞挖掘者自己承担。
|
||||
|
||||
10、请将所有测试操作和行为及时、如实、完整上报,因故意瞒报、漏报等造成业务损害或潜在风险,ByteSRC保留追责权利。
|
||||
|
||||
|
||||
@@ -0,0 +1,224 @@
|
||||
# DLL 劫持复现记录(显式加载)
|
||||
原创 huan666 huan666 2026-01-08 11:01
|
||||
|
||||
相关代码来源于互联网,适用于新手小白,大佬绕行!!!
|
||||
|
||||
一、显式加载原理
|
||||
|
||||
程序在运行过程中,通过主动调用Windows API函数,比如LoadLibrary,来加载指定的DLL,再通过GetProcAddress获取 DLL 中函数的地址,最后手动调用函数FreeLibrary、释放 DLL。
|
||||
|
||||
二、环境搭建
|
||||
|
||||
编辑器:Visual Studio
|
||||
|
||||
进程查看工具:
|
||||
process-explorer
|
||||
|
||||
下载地址:
|
||||
|
||||
https://docs.microsoft.com/zh-cn/sysinternals/downloads/process-explorer
|
||||
|
||||
创建DLL1.dll:
|
||||
|
||||
1、新建动态链接库(DLL)项目-->下一步-->默认-->创建项目
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
2、修改dllmain.cpp文件
|
||||
```
|
||||
#include "pch.h"
|
||||
|
||||
// 定义原DLL的核心函数:DLL1已被成功加载!!!
|
||||
void dllmsg() {
|
||||
MessageBox(0, L"DLL1已被成功加载!!!", L"Good", 0);
|
||||
}
|
||||
|
||||
// DLL入口函数(默认生成,无需修改)
|
||||
BOOL APIENTRY DllMain(HMODULE hModule,
|
||||
DWORD ul_reason_for_call,
|
||||
LPVOID lpReserved
|
||||
)
|
||||
{
|
||||
switch (ul_reason_for_call)
|
||||
{
|
||||
case DLL_PROCESS_ATTACH:
|
||||
case DLL_THREAD_ATTACH:
|
||||
case DLL_THREAD_DETACH:
|
||||
case DLL_PROCESS_DETACH:
|
||||
break;
|
||||
}
|
||||
return TRUE;
|
||||
}
|
||||
```
|
||||
|
||||
3、修改framework.h文件
|
||||
|
||||
添加 Windows 头文件和函数导出声明(让外部 EXE 能调用dllmsg()
|
||||
函数)
|
||||
```
|
||||
#pragma once
|
||||
#define WIN32_LEAN_AND_MEAN // 从 Windows 头文件中排除极少使用的内容
|
||||
#include <windows.h> // 包含MessageBox所需的Windows API头文件
|
||||
|
||||
// 导出msg函数:extern "C"避免C++名字粉碎,__declspec(dllexport)标记为导出函数
|
||||
extern "C" __declspec(dllexport) void dllmsg(void);
|
||||
```
|
||||
|
||||
4、点击生成-生成解决方案,编译生成dll文件,先选择Release,再生成解决方案
|
||||
|
||||

|
||||
|
||||
|
||||

|
||||
|
||||
dll文件路径,在控制台日志中可查看。
|
||||
|
||||

|
||||
|
||||
|
||||
创建
|
||||
ConsoleApplication1.exe
|
||||
:
|
||||
|
||||
|
||||
1、创建新项目-->控制台应用-->下一步-->创建
|
||||
|
||||

|
||||
|
||||
2、编辑
|
||||
ConsoleApplication1.cpp文件
|
||||
```
|
||||
#include <iostream>
|
||||
#include <Windows.h>
|
||||
using namespace std;
|
||||
|
||||
int main()
|
||||
{
|
||||
// 定义函数指针类型,匹配msg()的参数和返回值
|
||||
typedef void(*DLLFUNC)(void);
|
||||
DLLFUNC GetDllfunc = NULL;
|
||||
|
||||
// 动态加载Dll1.dll(需确保EXE与DLL在同一目录)
|
||||
HINSTANCE hinst = LoadLibrary(L"Dll1.dll");
|
||||
if (hinst != NULL) {
|
||||
// 获取DLL中导出函数msg的地址
|
||||
GetDllfunc = (DLLFUNC)GetProcAddress(hinst, "dllmsg");
|
||||
}
|
||||
|
||||
// 调用dllmsg()函数(若获取地址成功)
|
||||
if (GetDllfunc != NULL) {
|
||||
(*GetDllfunc)();
|
||||
}
|
||||
|
||||
return 0;
|
||||
}
|
||||
```
|
||||
|
||||
3、点击生成-->生成解决方案
|
||||
|
||||

|
||||
|
||||
|
||||
将
|
||||
ConsoleApplication1.exe和
|
||||
Dll1.dll
|
||||
放在同一目录
|
||||
|
||||

|
||||
|
||||
运行
|
||||
ConsoleApplication1.exe,
|
||||
Dll1.dll已被加载
|
||||
|
||||

|
||||
|
||||
|
||||
三、劫持复现
|
||||
|
||||
|
||||
运行process-explorer,查看
|
||||
ConsoleApplication1.exe加载哪些DLL文件
|
||||
|
||||

|
||||
|
||||
点击View-->Show Lower Pane,可查看加载的DLL文件
|
||||
|
||||

|
||||
|
||||
|
||||
通过加载的DLL,发现
|
||||
C:\Users\huan666-pc\Desktop\test\Dll1.dll
|
||||
|
||||
|
||||
|
||||
被加载,并且在当前程序目录下,修改
|
||||
Dll1.dll文件为执行任意系统命令。
|
||||
|
||||
编写一个弹出计算器的DLL文件,文件名最后改为
|
||||
Dll1.dll
|
||||
```
|
||||
// dllmain.cpp : 定义 DLL 应用程序的入口点。
|
||||
#include "pch.h"
|
||||
// 包含Windows API头文件,用于调用系统函数
|
||||
#include <Windows.h>
|
||||
|
||||
// 定义弹出计算器的函数
|
||||
void OpenCalculator() {
|
||||
// 核心API:WinExec 执行系统命令,calc.exe是计算器程序
|
||||
// SW_SHOW:显示计算器窗口(不隐藏)
|
||||
// 注意:WinExec在新系统中仍可用,也可以用CreateProcess(更推荐,后面会补充)
|
||||
WinExec("calc.exe", SW_SHOW);
|
||||
|
||||
// 【可选】更健壮的写法(替代WinExec,推荐)
|
||||
/*
|
||||
STARTUPINFO si = { 0 };
|
||||
PROCESS_INFORMATION pi = { 0 };
|
||||
si.cb = sizeof(STARTUPINFO);
|
||||
// 创建新进程运行计算器
|
||||
CreateProcessA(NULL, "calc.exe", NULL, NULL, FALSE, 0, NULL, NULL, &si, &pi);
|
||||
// 关闭进程/线程句柄,释放资源
|
||||
CloseHandle(pi.hProcess);
|
||||
CloseHandle(pi.hThread);
|
||||
*/
|
||||
}
|
||||
|
||||
BOOL APIENTRY DllMain(HMODULE hModule,
|
||||
DWORD ul_reason_for_call,
|
||||
LPVOID lpReserved
|
||||
)
|
||||
{
|
||||
switch (ul_reason_for_call)
|
||||
{
|
||||
case DLL_PROCESS_ATTACH:
|
||||
// DLL被进程加载时,执行弹出计算器的函数
|
||||
OpenCalculator();
|
||||
break;
|
||||
case DLL_THREAD_ATTACH:
|
||||
case DLL_THREAD_DETACH:
|
||||
case DLL_PROCESS_DETACH:
|
||||
break;
|
||||
}
|
||||
return TRUE;
|
||||
}
|
||||
```
|
||||
|
||||
编译成DLL文件后,复制到劫持复现的目录下
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
|
||||
四、修复方案
|
||||
|
||||
注册表中修改,打开注册表:WIN+R-->regedit
|
||||
|
||||
\HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\Session Manager\KnownDLLs路径下定义加载的DLL,该目录下的
|
||||
DLL文件就会被禁止从EXE自身目录调用,而只能从系统目录加载。
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,104 @@
|
||||
# RuoYi-4.6.0代码审计之SQL注入漏洞
|
||||
安全艺术 安全艺术 2026-01-08 09:08
|
||||
|
||||
# 1. 环境搭建RuoYi-4.6.0
|
||||
|
||||
https://github.com/yangzongzhuan/RuoYi/releases
|
||||
|
||||
修改连接数据库的相关信息
|
||||
|
||||
RuoYi-4.6.0/ruoyi-admin/src/main/resources/application-druid.yml
|
||||
|
||||

|
||||
|
||||
将⽇志路径需改为相对路径 ./logs
|
||||
|
||||
RuoYi-4.6.0/ruoyi-admin/src/main/resources/logback.xml
|
||||
|
||||

|
||||
|
||||
将上传路径也修改为相对路径
|
||||
|
||||
RuoYi-4.6.0/ruoyi-admin/src/main/resources/application.xml
|
||||
|
||||

|
||||
|
||||
创建数据库
|
||||
```
|
||||
create database ry;
|
||||
source D:\@CodeAudit\Code\RuoYi-4.6.0\sql\ry_20201214.sql
|
||||
source D:\@CodeAudit\Code\RuoYi-4.6.0\sql\quartz.sql
|
||||
```
|
||||
|
||||

|
||||
|
||||
启动
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||

|
||||
# 2. SQL注入
|
||||
## 2.1. ${params.dataScope}
|
||||
|
||||
铲子一把梭
|
||||
|
||||

|
||||
|
||||
前端去抓数据包发现这个参数是隐藏的。
|
||||
```
|
||||
deptName=&status=
|
||||
```
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
闭合下
|
||||
|
||||

|
||||
|
||||
筛选下,有14个sink点
|
||||
|
||||

|
||||
|
||||

|
||||
### 2.1.1. /system/role/list
|
||||
|
||||

|
||||
### 2.1.2. /system/role/export
|
||||
|
||||

|
||||
### 2.1.3. /system/user/list
|
||||
|
||||

|
||||
### 2.1.4. /system/user/export
|
||||
|
||||

|
||||
### 2.1.5. /system/role/authUser/allocatedList
|
||||
|
||||

|
||||
### 2.1.6. /system/role/authUser/unallocatedList
|
||||
|
||||

|
||||
## 2.2. ${ancestors}
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
全局搜java文件
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
ancestors有长度限制
|
||||
|
||||

|
||||
|
||||
更多内容进群获取。
|
||||
|
||||

|
||||
|
||||
@@ -0,0 +1,122 @@
|
||||
# Veeam 修复备份服务器中的RCE漏洞
|
||||
Sergiu Gatlan 代码卫士 2026-01-08 10:03
|
||||
|
||||

|
||||
|
||||
聚焦源代码安全,网罗国内外最新资讯!
|
||||
|
||||
**编译:代码卫士**
|
||||
|
||||
**Veeam****发布安全更新,修复备份与复制软件中的多个安全漏洞,包括一个严重的远程代码执行漏洞CVE-2025-59470。该漏洞影响Veeam备份与复制软件13.0.1.180及所有更早的13.x版本。**
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
本周二,Veeam发布安全公告称:“该漏洞可导致拥有 Backup 或 Tape Operator权限的攻击者,通过发送恶意的时间间隔参数或排序参数,以postgres用户身份执行远程代码。” 不过Veeam 认为该漏洞仅能遭拥有Backup 或 Tape Operator权限的攻击者利用,因此将严重等级调整为“高危”。该公司在安全公告补充中指出:“Backup 或 Tape Operator角色被视为高权限角色,应受到相应级别的保护。遵循Veeam建议的安全指南可进一步降低漏洞被利用的可能性。”
|
||||
|
||||
Veeam已于1月6日发布版本13.0.1.1071,修复该RCE漏洞,并同时修复了另外两个漏洞:高危漏洞CVE-2025-55125和中危漏洞CVE-2025-59468。这两个漏洞分别可导致恶意备份或磁带操作员通过创建恶意的备份配置文件或发送恶意密码参数,获得远程代码执行权限。
|
||||
|
||||
Veeam备份与复制软件 (VBR) 是一款企业级数据备份与恢复解决方案,用于创建关键数据和应用程序的副本,以便在网络攻击、硬件故障或灾难发生后能够快速恢复。
|
||||
|
||||
|
||||
|
||||
|
||||
**Veeam 常遭勒索团伙利用**
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||
VBR软件在中大型企业及托管服务提供商中尤为普及,但也常成为勒索软件团伙的攻击目标。因为在受害者的网络环境中,VBR服务器可作为快速横向移动的跳板。
|
||||
|
||||
勒索软件团伙曾向BleepingComputer透露,他们总是以受害者的VBR服务器为目标,以此简化数据窃取过程,并便于在部署勒索软件 payload 前删除备份,从而阻止数据恢复。
|
||||
|
||||
古巴勒索软件团伙以及出于财务动机的FIN7威胁组织(该组织曾与Conti、REvil、Maze、Egregor和BlackBasta等勒索软件团伙合作)此前也曾被证实利用过VBR漏洞发起攻击。更近期的是Sophos X-Ops事件响应团队在2024年11月透露称,Frag勒索软件利用了两个月前披露的另一个VBR远程代码执行漏洞CVE-2024-40711。该漏洞也曾被Akira和Fog勒索软件利用,自2024年10月起针对存在漏洞的Veeam备份服务器发起攻击。
|
||||
|
||||
Veeam在全球拥有超过55万客户,其中包括74%的全球2000强企业和82%的财富500强公司。
|
||||
|
||||
****
|
||||
****
|
||||
|
||||
开源
|
||||
卫士试用地址:
|
||||
https://oss.qianxin.com/#/login
|
||||
|
||||
|
||||
代码卫士试用地址:https://sast.qianxin.com/#/login
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**推荐阅读**
|
||||
|
||||
[Veeam RCE漏洞导致域用户入侵备份服务器](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247523322&idx=2&sn=347204929358f8a4c82b2634e62774cd&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[Veeam 修复Backup & Replication 中的严重RCE漏洞](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247522555&idx=1&sn=46e012bb1770fd23ba35da839b60f669&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[Veeam 提醒注意VSPC中的严重RCE漏洞](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247521684&idx=1&sn=b5ba5835dc8937327b3ded698979f0f2&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[Veeam 修复5个严重漏洞](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247520714&idx=1&sn=df4e06a4fa7f19703c54eeb2ccf244d6&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[Veeam:Backup Enterprise Manager 中存在严重的认证绕过漏洞](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247519550&idx=2&sn=6b4de50a6ef98b37be097aae6daafa64&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**原文链接**
|
||||
|
||||
https://www.bleepingcomputer.com/news/security/new-veeam-vulnerabilities-expose-backup-servers-to-rce-attacks/
|
||||
|
||||
|
||||
题图:Pixa
|
||||
bay Licens
|
||||
e
|
||||
|
||||
|
||||
**本文由奇安信编译,不代表奇安信观点。转载请注明“转自奇安信代码卫士 https://codesafe.qianxin.com”。**
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
**奇安信代码卫士 (codesafe)**
|
||||
|
||||
国内首个专注于软件开发安全的产品线。
|
||||
|
||||

|
||||
|
||||
|
||||
觉得不错,就点个 “
|
||||
在看
|
||||
” 或 "
|
||||
赞
|
||||
” 吧~
|
||||
|
||||
@@ -0,0 +1,121 @@
|
||||
# n8n 满分漏洞 Ni8mare 可导致服务器遭劫持
|
||||
Bill Toulas 代码卫士 2026-01-08 10:03
|
||||
|
||||

|
||||
|
||||
聚焦源代码安全,网罗国内外最新资讯!
|
||||
|
||||
**编译:代码卫士**
|
||||
|
||||
**n8n****中存在一个CVSS满分、被称为 “Ni8mare” 的严重漏洞CVE-2026-21858,可导致未认证攻击者控制本地部署的工作流自动化平台n8n 实例。**
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
网络安全公司 Cyera 表示,目前存在超过10万台易受攻击的 n8n 服务器。n8n 是一款开源的工作流自动化工具,可使用户将应用、API和服务通过一款可视化编辑器连接到复杂的工作流。该工具主要用于自动化任务,支持与AI和LLM 服务的集成。N8n 在 npm 上的周下载量超过5万次,在 Docker Hub 上的拉取超过1亿次。该工具在AI 领域非常流行,用于协同 LLM 调用、构建 AI 智能体和 RAG 管道,并自动化数据的采集和检索。
|
||||
|
||||
|
||||

|
||||
|
||||
**漏洞详情**
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||
该漏洞可使攻击者通过执行特定的表单驱动工作流,访问底层服务器上的文件。n8n开发团队表示:“存在漏洞的工作流可能允许未经身份验证的远程攻击者进行访问。根据部署配置和工作流使用情况,该漏洞可能导致系统中存储的敏感信息遭泄露,并可能引发进一步的危害。”
|
||||
|
||||
Cyera公司研究人员于2025年11月9日发现了该漏洞并向n8n报送。他们指出,该安全问题源于n8n解析数据时存在的内容类型混淆问题。n8n通过监听特定消息来触发工作流的Webhook组件,会依据其配置的“content-type”头部,使用两种不同函数处理传入数据。当Webhook请求标记为multipart/form-data 时,n8n会将其视为文件上传,并调用专用的上传解析器。该解析器会将文件保存到随机生成的临时位置中,这意味着用户无法控制文件最终存储路径,从而防止了路径遍历攻击。然而,对于所有其它内容类型(如application/json),n8n则会改用其标准解析器进行处理。
|
||||
|
||||
研究人员发现,攻击者通过设置不同的内容类型(例如application/json),即可绕过上传解析器。在这种情况下,n8n仍会处理与文件相关的字段,但不会验证该请求是否实际包含有效的文件上传,从而导致攻击者能够完全控制文件元数据,包括文件路径,从而可能实现恶意文件写入或路径操纵。
|
||||
|
||||
研究人员解释道:“由于调用此函数时未验证内容类型是否为multipart/form-data,我们可完全控制req.body.files对象。这意味着我们能操纵filepath参数——无需复制上传的文件,而是复制系统中的任意本地文件。”
|
||||
|
||||
该漏洞可用于从n8n实例中读取任意文件,攻击者可通过将内部文件注入工作流知识库暴露敏感信息。研究人员指出,攻击者可借此窃取实例存储的密钥、向工作流注入敏感文件、伪造会话cookie绕过身份验证,甚至执行任意命令。
|
||||
|
||||
研究人员强调称,n8n作为核心自动化枢纽,常存储API密钥、OAuth令牌、数据库凭据、云存储访问权限、CI/CD机密及商业数据等关键信息。n8n开发团队表示,目前不存在官方临时解决方案,但可通过限制或禁用公开访问的Webhook和表单端点作为缓解措施。强烈建议用户升级至n8n 1.121.0或更高版本,彻底修复该漏洞。
|
||||
|
||||
|
||||
|
||||
开源
|
||||
卫士试用地址:
|
||||
https://oss.qianxin.com/#/login
|
||||
|
||||
|
||||
代码卫士试用地址:https://sast.qianxin.com/#/login
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**推荐阅读**
|
||||
|
||||
[n8n严重漏洞可导致任意代码执行](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247524734&idx=1&sn=7accfa41ad8e25a3c0a292eb451552af&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[欧洲空间局证实“外部服务器”遭攻陷](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247524774&idx=1&sn=b7f1ee58a6471570b261a95d96541d42&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[SmarterMail 严重漏洞可导致服务器遭完全接管](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247524768&idx=1&sn=9637d0eb4df20ac66e8c9fa5c1d84ddd&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[Red Hat服务器受陷,日产1.2万名客户数据遭泄露](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247524719&idx=2&sn=f5d89f84af3cc83b347bda7d39e298df&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[CISA和NSA分享如何保护微软 Exchange 服务器](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247524314&idx=1&sn=2ea2b06eca0631b008e170460b6c4c39&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**原文链接**
|
||||
|
||||
https://www.bleepingcomputer.com/news/security/max-severity-ni8mare-flaw-lets-hackers-hijack-n8n-servers/
|
||||
|
||||
|
||||
题图:Pixa
|
||||
bay Licens
|
||||
e
|
||||
|
||||
|
||||
**本文由奇安信编译,不代表奇安信观点。转载请注明“转自奇安信代码卫士 https://codesafe.qianxin.com”。**
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
**奇安信代码卫士 (codesafe)**
|
||||
|
||||
国内首个专注于软件开发安全的产品线。
|
||||
|
||||

|
||||
|
||||
|
||||
觉得不错,就点个 “
|
||||
在看
|
||||
” 或 "
|
||||
赞
|
||||
” 吧~
|
||||
|
||||
@@ -0,0 +1,120 @@
|
||||
# 【安全圈】GoBruteforcer 僵尸网络全球攻击 Linux 服务器,5 万台公网服务器面临风险
|
||||
安全圈 2026-01-08 11:00
|
||||
|
||||

|
||||
|
||||
|
||||
**关键词**
|
||||
|
||||
|
||||
|
||||
僵尸网络
|
||||
|
||||
|
||||
一款名为**GoBruteforcer**
|
||||
的高复杂度 Go 语言僵尸网络,正针对全球范围内的 Linux 服务器发起猛烈攻击,通过暴力破解手段尝试获取 FTP、MySQL、PostgreSQL 及 phpMyAdmin 等公网暴露服务的弱密码。
|
||||
|
||||
Check Point Research近期记录到该恶意软件的 2025 年变种版本,其技术水平较之前版本实现大幅升级,已成功攻陷数万台服务器。
|
||||
|
||||
该僵尸网络采用模块化感染链架构,核心组件包含网页后门、下载器、互联网中继聊天(IRC)僵尸程序以及暴力破解模块。
|
||||
|
||||
据切克波因特的分析数据显示,全球超**5 万台公网暴露服务器**
|
||||
或面临高布鲁特福瑟攻击风险,目前有近 570 万台 FTP 服务器、223 万台 MySQL 服务器及 56 万台 PostgreSQL 服务器在默认端口上暴露。
|
||||
#### 人工智能生成服务器配置成攻击推手
|
||||
|
||||
本轮GoBruteforcer攻击浪潮的爆发,**主要源于两大关键因素:一是大量运维人员直接复用人工智能生成的服务器部署示例,这类配置模板普遍存在通用用户名与弱默认密码问题;二是 XAMPP 等老旧网站集成环境仍被广泛使用,其搭载的各类服务缺乏基础加固措施。**
|
||||
|
||||
研究人员发现,该僵尸网络在暴力破解的凭证列表中,大量使用 “appuser”“myuser” 等通用运维用户名,而这些用户名恰好是大型语言模型在生成数据库配置示例时最常推荐的默认名称。
|
||||
|
||||
切克波因特的调查显示,高布鲁特福瑟使用的凭证列表,与一个包含 1000 万条泄露密码的数据库存在约**2.44% 的重合度**
|
||||
。
|
||||
|
||||
尽管这一匹配成功率看似较低,但庞大的暴露服务基数,使得暴力破解攻击对威胁行为体而言具备极高的经济效益。谷歌 2024 年《云威胁态势报告》指出,在遭攻陷的云环境中,**47.2% 的初始入侵路径均源于弱密码或缺失身份验证机制**
|
||||
,这也印证了此类攻击手段的可行性。
|
||||
|
||||
僵尸网络的命令与控制服务器会下发包含 200 组凭证的列表用于暴力破解任务,且攻击配置文件每周会更新数次。
|
||||
|
||||
密码列表的生成逻辑十分固定,仅基于 375-600 个常用弱密码构成基础库,再衍生出 “appuser1234”“operatoroperator” 等基于用户名变体的密码组合。
|
||||
|
||||
相较于 2023 年首次被记录的早期版本,2025 年变种版本实现多项重大技术升级:其 IRC 僵尸程序组件已完全基于 Go 语言重构,并使用加布勒混淆工具(Garbler)进行深度代码混淆,彻底取代了原先基于 C 语言的开发架构。
|
||||
|
||||
该恶意软件还新增进程伪装技术,通过调用prctl
|
||||
系统调用将自身进程名修改为 “init”,并对二进制文件进行覆盖处理,以此躲避安全检测。
|
||||
|
||||
研究人员还发现一个以加密货币敛财为目标的攻击活动,威胁行为体在攻陷服务器后,会部署额外的 Go 语言工具集,其中包含针对波场(TRON)及币安智能链的挖矿程序与钱包窃取工具。
|
||||
|
||||
在一台被攻陷的服务器上,调查人员提取到一个包含约 2.3 万个波场钱包地址的文件,并通过链上交易数据分析证实,这批攻击已成功实现经济收益。
|
||||
|
||||
该僵尸网络通过多重机制保障自身的抗打击能力:内置备用 C2 服务器地址、基于域名的故障恢复路径,以及将已感染主机升级为分发节点或 IRC 中继服务器的功能。
|
||||
|
||||
IRC 僵尸程序模块每日可完成两次更新,暴力破解组件则通过与系统架构匹配的 Shell 脚本下载,并在执行前校验文件的 MD5 哈希值,确保恶意程序未被篡改。
|
||||
#### 攻击兼具广谱性与针对性
|
||||
|
||||
GoBruteforcer的攻击活动同时具备**广谱扫射**
|
||||
与**定向行业打击**
|
||||
的双重特征。通用型攻击活动会组合使用通用运维用户名与标准弱密码发起试探;而专项攻击任务则会采用 “cryptouser”“appcrypto” 等加密货币相关用户名,或 “wpuser” 这类针对 WordPress 系统的专属凭证。
|
||||
|
||||
该恶意软件还会针对性攻击 XAMPP 集成环境 —— 这一热门开发工具通常默认启用 FTP 服务,并将 FTP 根目录映射到公网可访问的网页路径,存在严重安全隐患。
|
||||
|
||||
僵尸网络的架构设计具备高效攻击能力,受感染主机每秒可扫描约 20 个 IP 地址,且在 FTP 攻击任务执行期间,能将带宽消耗控制在较低水平:出站流量约 64 千比特 / 秒,入站流量约 32 千比特 / 秒。
|
||||
|
||||
攻击线程池的规模会根据目标服务器的 CPU 架构动态调整:64 位系统上会运行 95 个并发暴力破解线程,32 位系统则会适配为更少的线程数。
|
||||
|
||||
该恶意软件还具备智能目标筛选能力,会主动排除私有网络、云服务商网段及美国国防部 IP 地址范围,以此降低被安全监测系统发现的概率。
|
||||
#### 防护建议
|
||||
|
||||
企业可通过以下措施降低GoBruteforcer攻击风险:实施强密码策略、关闭不必要的公网暴露服务、部署多因素身份验证机制,以及持续监测异常登录尝试行为。
|
||||
|
||||
|
||||
END
|
||||
|
||||
|
||||
阅读推荐
|
||||
|
||||
|
||||
[【安全圈】美军进攻委内瑞拉前当地电信公司BGP路由发生异常 流量被引导至不安全的路线](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652073601&idx=1&sn=10d365f3aeaa11a32edd4b32ab718cbd&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】两款Chrome扩展窃取90万用户与ChatGPT的对话记录](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652073601&idx=2&sn=340af758cdc973198fef16ee90d05a49&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】0Day漏洞Chronomaly可获取Linux内核root权限](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652073601&idx=3&sn=dea95a9fbe14ba2f6a20a39754e7f77a&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】D-Link 多款老旧 DSL 网关路由器被曝命令注入 0day,已遭野外利用](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652073601&idx=4&sn=9c7154506dafe5b5720c6a61411d4662&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
**安全圈**
|
||||
|
||||

|
||||
|
||||
|
||||
←扫码关注我们
|
||||
|
||||
**网罗圈内热点 专注网络安全**
|
||||
|
||||
**实时资讯一手掌握!**
|
||||
|
||||
|
||||

|
||||
|
||||
**好看你就分享 有用就点个赞**
|
||||
|
||||
**支持「****安全圈」就点个三连吧!**
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,82 @@
|
||||
# 【安全圈】三星 SSD 管理软件曝高危漏洞
|
||||
安全圈 2026-01-08 11:00
|
||||
|
||||

|
||||
|
||||
|
||||
**关键词**
|
||||
|
||||
|
||||
|
||||
漏洞
|
||||
|
||||
|
||||
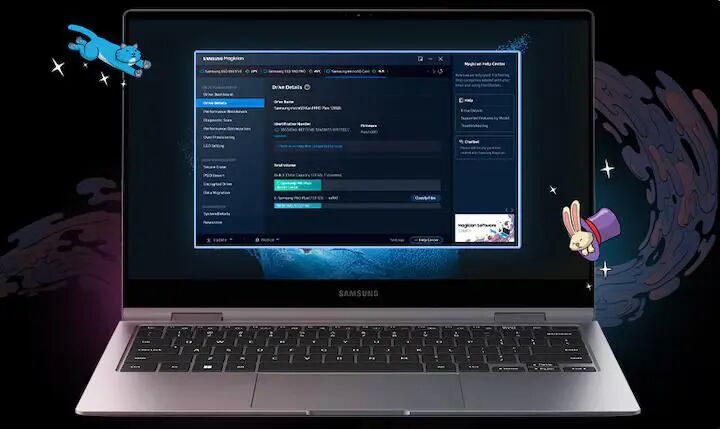
三星前天在其官网发布声明,确认旗下固态硬盘管理软件 " 三星魔术师 "6.3.0-8.3.2 版存在高危漏洞,**使用这些版本的用户应该立即更新**
|
||||
。
|
||||
|
||||
|
||||
|
||||
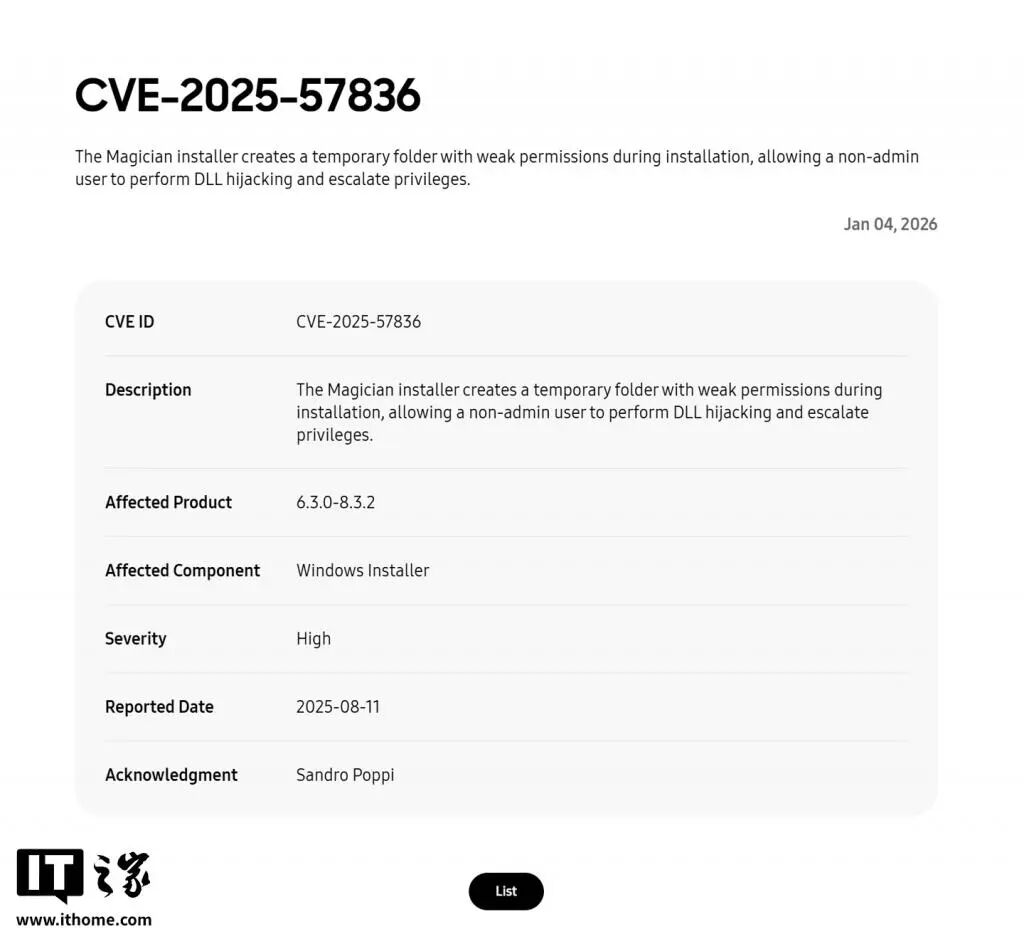
查询三星官网后发现,这些版本的三星魔术师存在 CVE-2025-57836 漏洞,可被黑客利用于提权、DLL 劫持,**进而获得管理员权限**
|
||||
,然后往应用程序目录中放置恶意代码,进而完全操控用户的电脑。
|
||||
|
||||
|
||||
|
||||
三星官方对此解释道,**这些版本的应用程序会在安装过程中创建一个权限过于宽松的临时文件夹**
|
||||
,进而允许非管理员用户进行 DLL 劫持并提权。
|
||||
|
||||
同时,三星已在 9.0 及更新版本的软件中修复了这一漏洞,**并且新版应用还带来了重构的 UI 界面**
|
||||
,可以自定义小组件。
|
||||
|
||||
|
||||
END
|
||||
|
||||
|
||||
阅读推荐
|
||||
|
||||
|
||||
[【安全圈】美军进攻委内瑞拉前当地电信公司BGP路由发生异常 流量被引导至不安全的路线](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652073601&idx=1&sn=10d365f3aeaa11a32edd4b32ab718cbd&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】两款Chrome扩展窃取90万用户与ChatGPT的对话记录](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652073601&idx=2&sn=340af758cdc973198fef16ee90d05a49&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】0Day漏洞Chronomaly可获取Linux内核root权限](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652073601&idx=3&sn=dea95a9fbe14ba2f6a20a39754e7f77a&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】D-Link 多款老旧 DSL 网关路由器被曝命令注入 0day,已遭野外利用](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652073601&idx=4&sn=9c7154506dafe5b5720c6a61411d4662&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
**安全圈**
|
||||
|
||||

|
||||
|
||||
|
||||
←扫码关注我们
|
||||
|
||||
**网罗圈内热点 专注网络安全**
|
||||
|
||||
**实时资讯一手掌握!**
|
||||
|
||||
|
||||

|
||||
|
||||
**好看你就分享 有用就点个赞**
|
||||
|
||||
**支持「****安全圈」就点个三连吧!**
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,108 @@
|
||||
# 【安全圈】安卓 / Linux 内核高危漏洞 CVE-2025-38352 验证性利用代码已公开
|
||||
安全圈 2026-01-08 11:00
|
||||
|
||||

|
||||
|
||||
|
||||
**关键词**
|
||||
|
||||
|
||||
|
||||
漏洞
|
||||
|
||||
|
||||
Linux 内核中存在一处高危竞争条件漏洞(漏洞编号CVE-2025-38352),其验证性利用代码已在GitHub 上公开发布。
|
||||
|
||||
该漏洞于今年年初被发现,攻击目标直指内核的**POSIX CPU 定时器**
|
||||
实现模块,此前曾被用于针对 32 位安卓设备的小规模定向攻击。
|
||||
|
||||
CVE-2025-38352 是 Linux 内核handle_posix_cpu_timers()
|
||||
函数中存在的**释放后使用**
|
||||
漏洞。
|
||||
|
||||
此漏洞的触发条件为内核配置项CONFIG_POSIX_CPU_TIMERS_TASK_WORK
|
||||
处于关闭状态 —— 该配置是大多数 32 位安卓内核的默认选项,但 64 位系统一般不会采用。
|
||||
|
||||
漏洞的成因是**僵尸进程触发 POSIX CPU 定时器时引发的竞争条件**
|
||||
:攻击者通过精准把控僵尸进程的创建、父进程对其的回收操作以及定时器的删除时机,可诱导内核访问已释放的内存区域,进而实现权限提升或内核代码执行。
|
||||
|
||||
区块链安全公司 Zellic 的研究员Faith发布了一款名为Chronomaly的全功能漏洞利用工具,专门针对 Linux 内核 5.10.x 版本发起攻击。
|
||||
|
||||
该研究员还同步发布了一个分为三部分的系列技术博客,详细拆解漏洞的发现过程、技术原理及利用手法,借此对外公布这款漏洞利用工具。
|
||||
|
||||
这款漏洞利用工具的一大显著优势是**无需依赖内核符号偏移量或特定内存地址**
|
||||
,因此可跨不同内核配置环境移植使用。
|
||||
|
||||
**工具中集成了两项核心技术:一是通过操控 CPU 定时器实现的竞争时间窗口延长技术,二是针对sigqueue结构体的跨缓存区分配策略。**
|
||||
|
||||
需要注意的是,该漏洞利用工具需在至少配备双核 CPU 的多核系统中运行,才能稳定触发竞争条件漏洞。
|
||||
|
||||
经测试验证,该工具可成功攻击运行 5.10.157 版本内核的 QEMU 虚拟化 Linux 系统,且其参数可根据不同运行环境灵活调整。
|
||||
|
||||
目前,该漏洞已被列入**CISA的已知被利用漏洞目录**
|
||||
,这意味着该漏洞已存在真实的在野攻击活动。
|
||||
|
||||
尽管漏洞威胁目前主要集中于 32 位安卓设备,但相关内核组件同样存在于其他基于 Linux 的 32 位操作系统中,这些系统也面临潜在风险。
|
||||
|
||||
GitHub 上的漏洞公告指出,用户应尽快将内核更新至已修复该漏洞的版本,或启用内核配置项CONFIG_POSIX_CPU_TIMERS_TASK_WORK
|
||||
以规避风险。
|
||||
|
||||
Linux 主线内核已通过编号为f90fff1e152dedf52b932240ebbd670d83330eca
|
||||
的提交记录完成漏洞修复,修复的核心逻辑为**禁止内核对僵尸进程执行定时器处理操作**
|
||||
。
|
||||
|
||||
设备制造商及系统管理员应将内核更新列为优先事项,以缓解这一高危漏洞带来的安全风险。
|
||||
|
||||
|
||||
END
|
||||
|
||||
|
||||
阅读推荐
|
||||
|
||||
|
||||
[【安全圈】美军进攻委内瑞拉前当地电信公司BGP路由发生异常 流量被引导至不安全的路线](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652073601&idx=1&sn=10d365f3aeaa11a32edd4b32ab718cbd&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】两款Chrome扩展窃取90万用户与ChatGPT的对话记录](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652073601&idx=2&sn=340af758cdc973198fef16ee90d05a49&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】0Day漏洞Chronomaly可获取Linux内核root权限](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652073601&idx=3&sn=dea95a9fbe14ba2f6a20a39754e7f77a&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】D-Link 多款老旧 DSL 网关路由器被曝命令注入 0day,已遭野外利用](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652073601&idx=4&sn=9c7154506dafe5b5720c6a61411d4662&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
**安全圈**
|
||||
|
||||

|
||||
|
||||
|
||||
←扫码关注我们
|
||||
|
||||
**网罗圈内热点 专注网络安全**
|
||||
|
||||
**实时资讯一手掌握!**
|
||||
|
||||
|
||||

|
||||
|
||||
**好看你就分享 有用就点个赞**
|
||||
|
||||
**支持「****安全圈」就点个三连吧!**
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,109 @@
|
||||
# 【安全圈】黑客利用0Day漏洞工具包在野攻击VMware ESXi实例
|
||||
安全圈 2026-01-08 11:00
|
||||
|
||||

|
||||
|
||||
|
||||
**关键词**
|
||||
|
||||
|
||||
|
||||
漏洞
|
||||
|
||||
|
||||
|
||||
|
||||
网络安全公司Huntress发现黑客正在利用一个0Day漏洞工具包攻击VMware ESXi实例,该工具包通过串联多个漏洞实现虚拟机逃逸。攻击者最初通过被入侵的SonicWall VPN获得初始访问权限。
|
||||
## 攻击过程分析
|
||||
|
||||
威胁行为者首先通过SonicWall VPN获得立足点,随后利用被入侵的域管理员账户进行横向移动,先后攻陷备份域控制器和主域控制器。在主域控制器上,攻击者部署了Advanced Port Scanner和ShareFinder等侦察工具,使用WinRAR暂存数据,并修改Windows防火墙规则以阻止外部出站流量,同时允许内部横向移动。
|
||||
|
||||
在部署漏洞工具包约20分钟后,攻击者开始执行ESXi漏洞利用程序,Huntress在勒索软件部署前成功阻止了攻击。
|
||||
## MAESTRO漏洞工具包技术细节
|
||||
|
||||
Huntress将该工具包命名为MAESTRO,其工作原理包括:
|
||||
- 使用devcon.exe禁用VMware VMCI驱动程序
|
||||
|
||||
- 通过KDU加载未签名驱动程序以绕过驱动程序签名强制(DSE)
|
||||
|
||||
- 执行核心逃逸操作
|
||||
|
||||
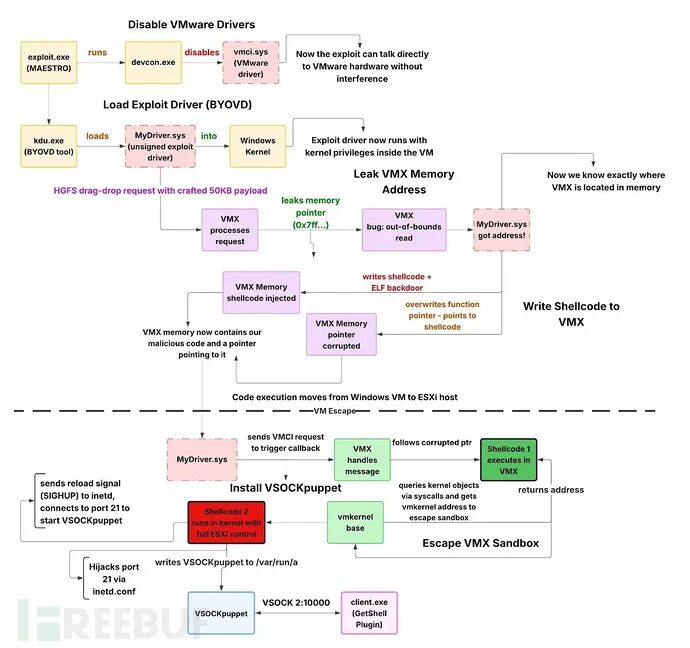
|
||||
|
||||
工具包截图(来源:Huntress)
|
||||
|
||||
MyDriver.sys驱动程序通过VMware Guest SDK查询ESXi版本,从支持ESXi 5.1至8.0共155个构建版本的数据表中选择偏移量,通过HGFS(CVE-2025-22226)泄露VMX基址,通过VMCI(CVE-2025-22224)破坏内存,并部署用于沙箱逃逸的shellcode(CVE-2025-22225)。
|
||||
<table><thead><tr style="box-sizing: border-box;margin: 0px;padding: 0px;border: 0px;text-decoration: none;font-style: inherit;font-variant: inherit;font-weight: inherit;font-stretch: inherit;font-size: inherit;line-height: inherit;vertical-align: baseline;font-family: 微软雅黑, "Microsoft YaHei", "WenQuanYi Micro Hei", PingFangSC;outline: none;"><th style="box-sizing: border-box;text-align: center;margin: 0px;padding: 0px;border-top: 1px solid rgb(204, 204, 204);border-right: 1px solid rgb(204, 204, 204);border-bottom: none;border-left: 1px solid rgb(204, 204, 204);border-image: initial;text-decoration: none;font-style: inherit;font-variant: inherit;font-weight: 550;font-stretch: inherit;font-size: inherit;line-height: inherit;vertical-align: baseline;font-family: 微软雅黑, "Microsoft YaHei", "WenQuanYi Micro Hei", PingFangSC;outline: none;background: rgb(245, 245, 245);"><section><span leaf=""><span textstyle="" style="font-size: 17px;">CVE编号</span></span></section></th><th style="box-sizing: border-box;text-align: center;margin: 0px;padding: 0px;border-top: 1px solid rgb(204, 204, 204);border-right: 1px solid rgb(204, 204, 204);border-bottom: none;border-left: 1px solid rgb(204, 204, 204);border-image: initial;text-decoration: none;font-style: inherit;font-variant: inherit;font-weight: 550;font-stretch: inherit;font-size: inherit;line-height: inherit;vertical-align: baseline;font-family: 微软雅黑, "Microsoft YaHei", "WenQuanYi Micro Hei", PingFangSC;outline: none;background: rgb(245, 245, 245);"><section><span leaf=""><span textstyle="" style="font-size: 17px;">CVSS评分</span></span></section></th><th style="box-sizing: border-box;text-align: center;margin: 0px;padding: 0px;border-top: 1px solid rgb(204, 204, 204);border-right: 1px solid rgb(204, 204, 204);border-bottom: none;border-left: 1px solid rgb(204, 204, 204);border-image: initial;text-decoration: none;font-style: inherit;font-variant: inherit;font-weight: 550;font-stretch: inherit;font-size: inherit;line-height: inherit;vertical-align: baseline;font-family: 微软雅黑, "Microsoft YaHei", "WenQuanYi Micro Hei", PingFangSC;outline: none;background: rgb(245, 245, 245);"><section><span leaf=""><span textstyle="" style="font-size: 17px;">漏洞描述</span></span></section></th></tr></thead><tbody><tr style="box-sizing: border-box;margin: 0px;padding: 0px;border: 0px;text-decoration: none;font-style: inherit;font-variant: inherit;font-weight: inherit;font-stretch: inherit;font-size: inherit;line-height: inherit;vertical-align: baseline;font-family: 微软雅黑, "Microsoft YaHei", "WenQuanYi Micro Hei", PingFangSC;outline: none;"><td style="box-sizing: border-box;margin: 0px;padding: 5px;border: 1px solid rgb(204, 204, 204);text-decoration: none;font-style: inherit;font-variant: inherit;font-weight: inherit;font-stretch: inherit;font-size: inherit;line-height: inherit;vertical-align: baseline;font-family: 微软雅黑, "Microsoft YaHei", "WenQuanYi Micro Hei", PingFangSC;outline: none;text-align: left;word-break: break-word;white-space: pre-wrap;"><section><span leaf=""><span textstyle="" style="font-size: 17px;">CVE-2025-22226</span></span></section></td><td style="box-sizing: border-box;margin: 0px;padding: 5px;border: 1px solid rgb(204, 204, 204);text-decoration: none;font-style: inherit;font-variant: inherit;font-weight: inherit;font-stretch: inherit;font-size: inherit;line-height: inherit;vertical-align: baseline;font-family: 微软雅黑, "Microsoft YaHei", "WenQuanYi Micro Hei", PingFangSC;outline: none;text-align: left;word-break: break-word;white-space: pre-wrap;"><section><span leaf=""><span textstyle="" style="font-size: 17px;">7.1</span></span></section></td><td style="box-sizing: border-box;margin: 0px;padding: 5px;border: 1px solid rgb(204, 204, 204);text-decoration: none;font-style: inherit;font-variant: inherit;font-weight: inherit;font-stretch: inherit;font-size: inherit;line-height: inherit;vertical-align: baseline;font-family: 微软雅黑, "Microsoft YaHei", "WenQuanYi Micro Hei", PingFangSC;outline: none;text-align: left;word-break: break-word;white-space: pre-wrap;"><section><span leaf=""><span textstyle="" style="font-size: 17px;">HGFS越界读取导致VMX内存泄露</span></span></section></td></tr><tr style="box-sizing: border-box;margin: 0px;padding: 0px;border: 0px;text-decoration: none;font-style: inherit;font-variant: inherit;font-weight: inherit;font-stretch: inherit;font-size: inherit;line-height: inherit;vertical-align: baseline;font-family: 微软雅黑, "Microsoft YaHei", "WenQuanYi Micro Hei", PingFangSC;outline: none;"><td style="box-sizing: border-box;margin: 0px;padding: 5px;border: 1px solid rgb(204, 204, 204);text-decoration: none;font-style: inherit;font-variant: inherit;font-weight: inherit;font-stretch: inherit;font-size: inherit;line-height: inLine truncated
|
||||
Shellcode会部署名为VSOCKpuppet的后门程序,该后门劫持ESXi的inetd服务(端口21)以获取root权限,并使用VSOCK进行隐蔽的虚拟机-宿主机通信,这种通信方式对网络监控工具不可见。
|
||||
## 攻击溯源与防御建议
|
||||
|
||||
PDB路径显示该工具包在简体中文环境中开发,如"全版本逃逸--交付"的路径名称,时间戳为2024年2月,比Broadcom在2025年3月4日发布的VMSA-2025-0004安全公告早了一年多。2023年11月的client.exe PDB表明该工具采用模块化设计,被篡改的VMware驱动程序引用了"XLab"。Huntress高度确信攻击者来自中文环境,基于资源文件和0Day漏洞获取能力。
|
||||
|
||||
防御建议:
|
||||
- 及时为ESXi打补丁,已停止支持的版本无法获得修复
|
||||
|
||||
- 使用"lsof -a"命令监控ESXi主机的VSOCK进程
|
||||
|
||||
- 警惕KDU等BYOD加载器
|
||||
|
||||
- 加强VPN安全防护
|
||||
|
||||
- 防火墙规则变更和未签名驱动程序都是系统被入侵的信号
|
||||
|
||||
- VSOCK后门可绕过入侵检测系统(IDS)
|
||||
|
||||
此次事件凸显了虚拟机监控程序面临的持续威胁,攻击者通过驱动程序恢复和配置清理保持隐蔽性。随着针对ESXi的勒索软件攻击增加,企业必须加强虚拟化环境的安全防护。
|
||||
|
||||
|
||||
END
|
||||
|
||||
|
||||
阅读推荐
|
||||
|
||||
|
||||
[【安全圈】美军进攻委内瑞拉前当地电信公司BGP路由发生异常 流量被引导至不安全的路线](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652073601&idx=1&sn=10d365f3aeaa11a32edd4b32ab718cbd&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】两款Chrome扩展窃取90万用户与ChatGPT的对话记录](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652073601&idx=2&sn=340af758cdc973198fef16ee90d05a49&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】0Day漏洞Chronomaly可获取Linux内核root权限](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652073601&idx=3&sn=dea95a9fbe14ba2f6a20a39754e7f77a&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】D-Link 多款老旧 DSL 网关路由器被曝命令注入 0day,已遭野外利用](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652073601&idx=4&sn=9c7154506dafe5b5720c6a61411d4662&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
**安全圈**
|
||||
|
||||

|
||||
|
||||
|
||||
←扫码关注我们
|
||||
|
||||
**网罗圈内热点 专注网络安全**
|
||||
|
||||
**实时资讯一手掌握!**
|
||||
|
||||
|
||||

|
||||
|
||||
**好看你就分享 有用就点个赞**
|
||||
|
||||
**支持「****安全圈」就点个三连吧!**
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,147 @@
|
||||
# 【已复现】ComfyUI-Manager 远程代码执行漏洞(CVE-2025-67303)
|
||||
长亭安全应急响应中心 2026-01-08 10:47
|
||||
|
||||
|
||||
|
||||
|
||||
ComfyUI 是一款流行的基于节点的 Stable Diffusion 图形用户界面,广泛应用于 AI 图像生成工作流的构建和执行。ComfyUI-Manager 是 ComfyUI 的扩展管理器插件,用于简化自定义节点、模型和依赖项的安装管理。
|
||||
|
||||
|
||||
2026年1月,长亭安全应急响应中心监测到 ComfyUI-Manager 存在配置文件未授权访问漏洞(CVE-2025-67303)。经分析,未经身份验证的攻击者可利用该漏洞访问并篡改应用程序的配置,配合 Git URL 安装功能实现远程代码执行,利用难度较低,建议受影响的用户尽快修复。
|
||||
|
||||
|
||||
**漏洞描述**
|
||||
|
||||
|
||||
Description
|
||||
|
||||
|
||||
|
||||
|
||||
**0****1**
|
||||
|
||||
**漏洞成因**
|
||||
|
||||
CVE-2025-67303 是 ComfyUI-Manager 配置文件存储位置不当导致的安全缺陷。在 V3.38 之前的版本中,Manager 将其配置文件、快照和关键数据存储在 user/default/ComfyUI-Manager/
|
||||
目录下。该目录属于 ComfyUI 的 default/
|
||||
用户数据目录,未受到系统级保护,可通过 Web API 直接访问。远程攻击者可通过 Web 接口直接访问和修改配置文件,篡改 security_level
|
||||
配置项,将安全级别从 normal
|
||||
降低至 weak
|
||||
,从而绕过安装限制,通过 Git URL
|
||||
安装功能实现远程代码执行
|
||||
。
|
||||
|
||||
|
||||
## 漏洞影响
|
||||
|
||||
攻击者可在服务器上执行任意代码,可能导致服务器被完全控制、数据泄露或业务系统沦陷。
|
||||
|
||||
|
||||
**处置优先级:高**
|
||||
|
||||
漏洞类型:
|
||||
远程代码执行
|
||||
|
||||
**漏洞危害等级:**
|
||||
高
|
||||
|
||||
**触发方式:**
|
||||
网络远程
|
||||
|
||||
**权限认证要求:**
|
||||
无需权限
|
||||
|
||||
**系统配置要求:**
|
||||
默认配置
|
||||
|
||||
**用户交互要求:**
|
||||
无需用户交互
|
||||
|
||||
**利用成熟度:**
|
||||
POC/EXP 已公开
|
||||
|
||||
**修复复杂度:**
|
||||
低,
|
||||
官方已提供修复方案
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**影响版本**
|
||||
|
||||
|
||||
Affects
|
||||
|
||||
|
||||
|
||||
|
||||
**02**
|
||||
```
|
||||
```
|
||||
|
||||
**解决方案**
|
||||
|
||||
|
||||
Solution
|
||||
|
||||
|
||||
|
||||
|
||||
**03**
|
||||
|
||||
##
|
||||
|
||||
## 升级修复方案
|
||||
|
||||
|
||||
1、升级 ComfyUI-Manager 至 V3.38 或更高版本
|
||||
|
||||
2、升级 ComfyUI 至 v0.3.76 或更高版本(需要 System User Protection API 支持)
|
||||
|
||||
安全迁移说明:
|
||||
|
||||
V3.38 版本将配置文件迁移至受保护的系统路径:
|
||||
- 旧路径:user/default/ComfyUI-Manager/
|
||||
(不安全,可被 Web API 访问)
|
||||
|
||||
- 新路径:user/__manager/
|
||||
(受 ComfyUI 系统保护,外部无法访问)
|
||||
|
||||
迁移过程:
|
||||
1. 仅 config.ini
|
||||
会自动迁移
|
||||
|
||||
1. 如安全级别低于 normal
|
||||
,将自动提升至 normal
|
||||
|
||||
1. 旧数据目录备份至 user/__manager/.legacy-manager-backup/
|
||||
|
||||
1. 快照数据(snapshots/
|
||||
)因可能已被篡改,需手动验证后复制
|
||||
|
||||
|
||||
|
||||
## 临时缓解方案避免使用 --listen 0.0.0.0等允许外部连接的参数启动 ComfyUI 手动检查 user/default/ComfyUI-Manager/config.ini,确认 security_level未被篡改 审查已安装的自定义节点,删除可疑的未知来源扩展 使用防火墙限制 ComfyUI Web 接口的访问来源安全级别说明级别允许操作strong仅允许更新 ComfyUI,阻止所有扩展安装normal允许安装/更新/删除已注册的自定义节点和模型(推荐)normal-在 normal基础上,允许通过 Git URL 或 pip 安装(仅限本地访问)weak允许所有操作,包括远程连接的 Git URL 安装(不推荐)漏洞复现Reproduction 04产品支持 Support 05云图:默认支持该产品的指纹识别,同时支持该漏洞的PoC检测洞鉴:默认支持该产品的指纹识别,预计2026.01.08支持该漏洞的自定义PoC无锋:默认支持该产品的指纹识别,预计2026.01.08支持该漏洞的PoC检测时间线 Timeline 062026年1月8日 长亭安全应急响应中心发布通告参考资料:[1].https://github.com/Comfy-Org/ComfyUI-Manager/blob/main/docs/en/v3.38-userdata-security-migration.md
|
||||
|
||||
|
||||
**长亭应急响应服务**
|
||||
|
||||
|
||||
|
||||
|
||||
全力进行产品升级
|
||||
|
||||
及时将风险提示预案发送给客户
|
||||
|
||||
检测业务是否受到此次漏洞影响
|
||||
|
||||
请联系长亭应急服务团队
|
||||
|
||||
7*24小时,守护您的安全
|
||||
|
||||
|
||||
第一时间找到我们:
|
||||
|
||||
邮箱:support@chaitin.com
|
||||
|
||||
@@ -0,0 +1,101 @@
|
||||
# 【已复现】ComfyUI-Manager存在远程代码执行(CVE-2025-67303)
|
||||
安恒研究院 安恒信息CERT 2026-01-08 10:06
|
||||
|
||||

|
||||
|
||||
<table><tbody><tr style="-webkit-tap-highlight-color:transparent;"><td colspan="4" data-colwidth="100.0000%" width="100.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;font-size:14px;color:rgb(255, 255, 255);box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;text-align:center;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">漏洞概述</span></strong></p></section></section></td></tr><tr style="-webkit-tap-highlight-color:transparent;"><td data-colwidth="25.0000%" width="25.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;text-align:left;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">漏洞名称</span></strong></p></section></section></td><td colspan="3" data-colwidth="75.0000%" width="75.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;font-size:14px;box-sizing:border-box;"><p><span style="letter-spacing:0.544px;"><span leaf="">ComfyUI-Manager存在远程代码执行(CVE-2025-67303)</span></span></p></section></section></td></tr><tr><td data-colwidth="25.0000%" width="25.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;text-align:left;"><strong><span leaf="">安恒CERT评级</span></strong></p></section></section></td><td data-colwidth="25.0000%" width="25.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><p style="-webkit-tap-highlight-color:transparent;"><span style="-webkit-tap-highlight-color:transparent;font-size:14px;letter-spacing:0.544px;"><span style="font-family:"PingFang SC", system-ui, -apple-system, "system-ui", "Helvetica Neue", "Hiragino Sans GB", "Microsoft YaHei UI", "Microsoft YaHei", Arial, sans-serif;font-size:14px;letter-spacing:0.544px;"><span leaf="">2级</span></span></span></p><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;font-size:14px;overflow:hidden;line-height:0;box-sizing:border-box;"><span leaf="" style="-webkit-tap-highlight-color:transparent;"><br/></span></section></section></td><td data-colwidth="25.0000%" width="25.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;text-align:left;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">CVSS3.1评分</span></strong></p></section></section></td><td data-colwidth="25.0000%" width="25.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;text-align:left;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">7.5</span></p></section></section></td></tr><tr style="-webkit-tap-highlight-color:transparent;"><td data-colwidth="25.0000%" width="25.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-colorLine truncated
|
||||
|
||||
**安恒研究院卫兵实验室已复现此漏洞。**
|
||||
|
||||
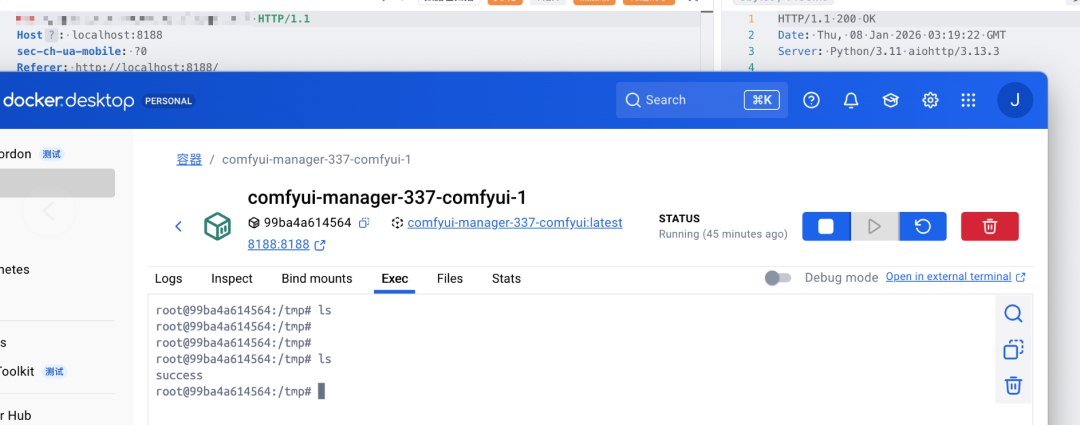
|
||||
|
||||
复现截图
|
||||
|
||||
|
||||
|
||||
**漏洞信息**
|
||||
|
||||
|
||||
|
||||
|
||||
ComfyUI-Manager是一款旨在增强ComfyUI易用性的扩展程序。它提供管理功能,用于安装、移除、禁用和启用ComfyUI的各种自定义节点。此外,该扩展程序还提供中心枢纽功能和便捷功能,方便用户访问ComfyUI中的各种信息。
|
||||
|
||||
|
||||
**漏洞描述**
|
||||
|
||||
**漏洞危害等级:**
|
||||
高危
|
||||
|
||||
**漏洞类型:**
|
||||
远程代码执行
|
||||
|
||||
|
||||
**影响范围**
|
||||
|
||||
**影响版本:**
|
||||
|
||||
ComfyUI-Manager < 3.38
|
||||
|
||||
**安全版本:**
|
||||
|
||||
ComfyUI-Manager 3.38
|
||||
|
||||
**CVSS向量**
|
||||
|
||||
访问途径(AV):网络
|
||||
|
||||
攻击复杂度(AC):低
|
||||
|
||||
所需权限(PR):无
|
||||
|
||||
用户交互(UI):无
|
||||
|
||||
影响范围 (S):不变
|
||||
|
||||
机密性影响 (C):无
|
||||
|
||||
完整性影响 (l):高
|
||||
|
||||
可用性影响 (A):无
|
||||
|
||||
|
||||
|
||||
|
||||
**修复方案**
|
||||
|
||||
|
||||
|
||||
|
||||
**官方修复方案:**
|
||||
|
||||
官方已发布修复方案,受影响的用户建议更新至安全版本。ComfyUI-Manager V3.38引入了一个安全补丁,将Manager的配置和数据迁移到受保护的系统路径。此更改利用了ComfyUI新的系统用户保护API来提供增强的安全隔离。
|
||||
|
||||
https://github.com/Comfy-Org/ComfyUI-Manager/blob/main/docs/en/v3.38-userdata-security-migration.md
|
||||
|
||||
**产品能力覆盖**
|
||||
|
||||
|
||||
|
||||
<table><tbody><tr style="-webkit-tap-highlight-color:#00000000;"><td style="-webkit-tap-highlight-color:#00000000;word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="-webkit-tap-highlight-color:#00000000;margin:5px 0px;"><section style="-webkit-tap-highlight-color:rgba(0, 0, 0, 0);margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;color:rgb(255, 255, 255);box-sizing:border-box;"><p style="-webkit-tap-highlight-color:#00000000;"><strong style="-webkit-tap-highlight-color:#00000000;"><span leaf="">产品名称</span></strong></p></section></section></td><td style="-webkit-tap-highlight-color:#00000000;word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="-webkit-tap-highlight-color:#00000000;margin:5px 0px;"><section style="-webkit-tap-highlight-color:rgba(0, 0, 0, 0);margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;color:rgb(255, 255, 255);box-sizing:border-box;"><p style="-webkit-tap-highlight-color:#00000000;"><strong style="-webkit-tap-highlight-color:#00000000;"><span leaf="">覆盖补丁包</span></strong></p></section></section></td></tr><tr style="-webkit-tap-highlight-color:#00000000;"><td style="-webkit-tap-highlight-color:#00000000;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:#00000000;margin:5px 0px;"><section style="-webkit-tap-highlight-color:rgba(0, 0, 0, 0);margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:#00000000;"><span leaf="">明鉴漏洞扫描系统</span></p></section></section></td><td style="-webkit-tap-highlight-color:#00000000;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:#00000000;margin:5px 0px;"><section style="-webkit-tap-highlight-color:rgba(0, 0, 0, 0);margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:#00000000;"><span leaf="">V1.3.2398.2025及以上版本</span></p></section></section></td></tr></tbody></table>
|
||||
|
||||
**参考资料**
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
https://github.com/Comfy-Org/ComfyUI-Manager/blob/main/docs/en/v3.38-userdata-security-migration.md
|
||||
|
||||
https://github.com/Comfy-Org/ComfyUI-Manager/pull/2338/commits/e44c5cef58fb4973670b86433b9d24d077b44a26
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**技术支持**
|
||||
|
||||
|
||||
|
||||
|
||||
如有漏洞相关需求支持请联系400-6059-110获取相关能力支撑。
|
||||
|
||||
@@ -0,0 +1,122 @@
|
||||
# 【已复现】n8n 前台远程代码执行漏洞(CVE-2026-21858)
|
||||
长亭安全应急响应中心 2026-01-08 10:47
|
||||
|
||||
|
||||
|
||||
|
||||
n8n 是一款开源的工作流自动化平台,广泛应用于企业和个人的自动化流程管理,提供节点式工作流编排、API 集成和数据处理等功能。
|
||||
|
||||
|
||||
2026年1月,长亭安全应急响应中心监测到 n8n 存在远程代码执行漏洞(CVE-2026-21858)。经分析,未经身份验证的攻击者可通过公开访问的表单节点远程访问服务器上的敏感文件,结合后台漏洞可实现远程代码执行,利用难度较低,建议受影响的用户尽快修复。
|
||||
|
||||
|
||||
**漏洞描述**
|
||||
|
||||
|
||||
Description
|
||||
|
||||
|
||||
|
||||
|
||||
**0****1**
|
||||
|
||||
**漏洞成因**
|
||||
|
||||
CVE-2026-21858 是 n8n 中一个由 Content-Type 混淆导致的文件处理缺陷。漏洞核心在于 parseRequestBody() 函数根据 Content-Type 头选择解析器:当值为 multipart/form-data 时调用文件上传解析器 parseFormData(),否则调用常规解析器 parseBody()。
|
||||
|
||||
然而,在表单提交处理函数 formWebhook() 中,调用 copyBinaryFile() 处理文件时,未验证请求的 Content-Type 是否为 multipart/form-data。攻击者可构造恶意请求,控制 req.body.files 对象,指定服务器上的任意文件路径,导致系统复制本地敏感文件而非上传的文件,造成信息泄露。
|
||||
|
||||
## 漏洞影响
|
||||
|
||||
敏感信息泄露
|
||||
:攻击者可远程读取 n8n 服务器上的任意文件,从而获取管理员凭证、加密密钥、API 密钥、OAuth 令牌等敏感数据。
|
||||
|
||||
身份验证绕过
|
||||
:攻击者利用泄露的用户信息和加密密钥可伪造管理员会话 Cookie,绕过身份验证获取管理员权限。
|
||||
|
||||
远程代码执行
|
||||
:获得管理员权限后,攻击者可创建包含"Execute Command"节点的恶意工作流,实现在服务器上执行任意命令,完全控制 n8n 实例。
|
||||
|
||||
|
||||
**处置优先级:高**
|
||||
|
||||
漏洞类型:
|
||||
远程代码执行
|
||||
|
||||
**漏洞危害等级:**
|
||||
高
|
||||
|
||||
**触发方式:**
|
||||
网络远程
|
||||
|
||||
**权限认证要求:**
|
||||
无需权限
|
||||
|
||||
**系统配置要求:存在公开访问的表单节点**
|
||||
|
||||
**用户交互要求:**
|
||||
无需用户交互
|
||||
|
||||
**利用成熟度:**
|
||||
POC/EXP 已公开
|
||||
|
||||
**修复复杂度:**
|
||||
低,
|
||||
官方已提供修复方案
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**影响版本**
|
||||
|
||||
|
||||
Affects
|
||||
|
||||
|
||||
|
||||
|
||||
**02**
|
||||
```
|
||||
```
|
||||
|
||||
**解决方案**
|
||||
|
||||
|
||||
Solution
|
||||
|
||||
|
||||
|
||||
|
||||
**03**
|
||||
|
||||
##
|
||||
|
||||
## 升级修复方案
|
||||
|
||||
|
||||
升级至 1.121.0 或更高版本,下载地址:https://github.com/n8n-io/n8n/releases
|
||||
|
||||
## 临时缓解方案如非必要,避免将该系统直接暴露在互联网漏洞复现Reproduction 04产品支持 Support 05云图:默认支持该产品的指纹识别,同时支持该漏洞的PoC检测洞鉴:默认支持该产品的指纹识别,同时支持该漏洞的自定义PoC检测雷池:默认支持部分敏感文件读取的检测,预计 2026.01.08 发布更新包支持 RCE 利用链的检测全悉:默认支持部分敏感文件读取的检测,预计 2026.01.08 发布更新包支持 RCE 利用链的检测无锋:默认支持该产品的指纹识别,预计 2026.01.08支持该漏洞的PoC原理检测时间线 Timeline 062026年1月8日 长亭安全应急响应中心发布通告参考资料:[1].https://github.com/advisories/GHSA-v4pr-fm98-w9pg
|
||||
|
||||
|
||||
**长亭应急响应服务**
|
||||
|
||||
|
||||
|
||||
|
||||
全力进行产品升级
|
||||
|
||||
及时将风险提示预案发送给客户
|
||||
|
||||
检测业务是否受到此次漏洞影响
|
||||
|
||||
请联系长亭应急服务团队
|
||||
|
||||
7*24小时,守护您的安全
|
||||
|
||||
|
||||
第一时间找到我们:
|
||||
|
||||
邮箱:support@chaitin.com
|
||||
|
||||
@@ -0,0 +1,100 @@
|
||||
# 【已复现】n8n任意文件读取到沙箱逃逸 RCE(CVE-2026-21858)
|
||||
安恒研究院 安恒信息CERT 2026-01-08 10:06
|
||||
|
||||

|
||||
|
||||
<table><tbody><tr style="-webkit-tap-highlight-color:transparent;"><td colspan="4" data-colwidth="100.0000%" width="100.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;font-size:14px;color:rgb(255, 255, 255);box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;text-align:center;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">漏洞概述</span></strong></p></section></section></td></tr><tr style="-webkit-tap-highlight-color:transparent;"><td data-colwidth="25.0000%" width="25.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;text-align:left;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">漏洞名称</span></strong></p></section></section></td><td colspan="3" data-colwidth="75.0000%" width="75.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;font-size:14px;box-sizing:border-box;"><p><span style="letter-spacing:0.544px;"><span leaf="">n8n任意文件读取到沙箱逃逸 RCE(CVE-2026-21858)</span></span></p></section></section></td></tr><tr><td data-colwidth="25.0000%" width="25.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;text-align:left;"><strong><span leaf="">安恒CERT评级</span></strong></p></section></section></td><td data-colwidth="25.0000%" width="25.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><p style="-webkit-tap-highlight-color:transparent;"><span style="-webkit-tap-highlight-color:transparent;font-size:14px;letter-spacing:0.544px;"><span style="font-family:"PingFang SC", system-ui, -apple-system, "system-ui", "Helvetica Neue", "Hiragino Sans GB", "Microsoft YaHei UI", "Microsoft YaHei", Arial, sans-serif;font-size:14px;letter-spacing:0.544px;"><span leaf="">1级</span></span></span></p><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;font-size:14px;overflow:hidden;line-height:0;box-sizing:border-box;"><span leaf="" style="-webkit-tap-highlight-color:transparent;"><br/></span></section></section></td><td data-colwidth="25.0000%" width="25.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;text-align:left;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">CVSS3.1评分</span></strong></p></section></section></td><td data-colwidth="25.0000%" width="25.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;text-align:left;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">10.0</span></p></section></section></td></tr><tr style="-webkit-tap-highlight-color:transparent;"><td data-colwidth="25.0000%" width="25.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-colLine truncated
|
||||
|
||||
安恒研究院卫兵实验室已复现此漏洞。
|
||||
|
||||
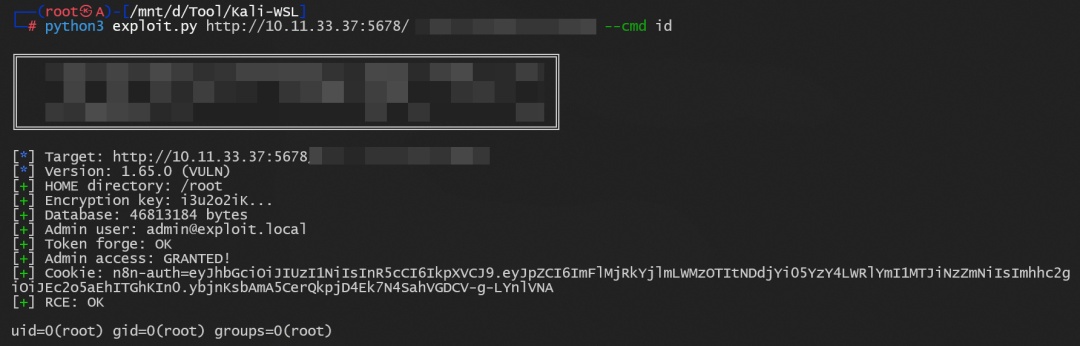
|
||||
|
||||
复现截图
|
||||
|
||||
|
||||
|
||||
**漏洞信息**
|
||||
|
||||
|
||||
|
||||
|
||||
n8n是一个开源的工作流自动化平台,提供了一个基于节点的可视化编辑器,用于与其他商业和专有应用程序集成,并支持自托管Web服务和托管云服务。
|
||||
|
||||
|
||||
**漏洞描述**
|
||||
|
||||
**漏洞危害等级:**
|
||||
严重
|
||||
|
||||
**漏洞类型:**
|
||||
远程代码执行
|
||||
|
||||
|
||||
**影响范围**
|
||||
|
||||
**影响版本:**
|
||||
|
||||
n8n < 1.121.0
|
||||
|
||||
**安全版本:**
|
||||
|
||||
n8n >= 1.121.0
|
||||
|
||||
**CVSS向量**
|
||||
|
||||
访问途径(AV):网络
|
||||
|
||||
攻击复杂度(AC):低
|
||||
|
||||
所需权限(PR):无
|
||||
|
||||
用户交互(UI):无
|
||||
|
||||
影响范围 (S):改变
|
||||
|
||||
机密性影响 (C):高
|
||||
|
||||
完整性影响 (l):高
|
||||
|
||||
可用性影响 (A):无
|
||||
|
||||
|
||||
|
||||
|
||||
**修复方案**
|
||||
|
||||
|
||||
|
||||
|
||||
**官方修复方案:**
|
||||
|
||||
官方已发布修复方案,受影响的用户建议更新至安全版本1.121.0。
|
||||
|
||||
https://github.com/n8n-io/n8n/releases
|
||||
|
||||
**产品能力覆盖**
|
||||
|
||||
|
||||
|
||||
<table><tbody><tr style="-webkit-tap-highlight-color:transparent;"><td data-colwidth="33.0000%" width="33.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;color:rgb(255, 255, 255);box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">产品名称</span></strong></p></section></section></td><td data-colwidth="67.0000%" width="67.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;color:rgb(255, 255, 255);box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">覆盖补丁包</span></strong></p></section></section></td></tr><tr style="-webkit-tap-highlight-color:transparent;"><td data-colwidth="33.0000%" width="33.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">AiLPHA大数据平台</span></p></section></section></td><td data-colwidth="67.0000%" width="67.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:#00000000;"><span style="-webkit-tap-highlight-color:#00000000;letter-spacing:0.544px;"><span leaf="">已支持</span></span></p></section></section></td></tr><tr style="-webkit-tap-highlight-color:transparent;"><td data-colwidth="33.0000%" width="33.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">APT攻击预警平台</span></p></section></section></td><td data-colwidth="67.0000%" width="67.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:#00000000;"><span leaf="" style="-webkit-tap-highlight-color:#00000000;">已支持</span></p></section></section></td></tr><tr style="-webkit-tap-highlight-color:#00000000;"><td data-colwidth="33.0000%" width="33.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">明鉴漏洞扫描系统</span></p></section></section></td><td data-colwidth="67.0000%" width="67.0000%" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:#00000000;"><span leaf="" style="-webkit-tap-higLine truncated
|
||||
|
||||
**参考资料**
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
https://github.com/n8n-io/n8n/security/advisories/GHSA-v4pr-fm98-w9pg
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**技术支持**
|
||||
|
||||
|
||||
|
||||
|
||||
如有漏洞相关需求支持请联系400-6059-110获取相关能力支撑。
|
||||
|
||||
|
||||
@@ -0,0 +1,154 @@
|
||||
# 【接口漏洞第三章第四节】进阶实战:如何用 Burp Intruder “暴力推理”出隐藏的API端点?
|
||||
原创 升斗安全XiuXiu 升斗安全 2026-01-08 10:56
|
||||
|
||||
**【文章说明】**
|
||||
- **目的**
|
||||
:本文内容仅为网络安全**技术研究与教育**
|
||||
目的而创作。
|
||||
|
||||
- **红线**
|
||||
:严禁将本文知识用于任何**未授权**
|
||||
的非法活动。使用者必须遵守《网络安全法》等相关法律。
|
||||
|
||||
- **责任**
|
||||
:任何对本文技术的滥用所引发的**后果自负**
|
||||
,与本公众号及作者无关。
|
||||
|
||||
- **免责**
|
||||
:内容仅供参考,作者不对其准确性、完整性作任何担保。
|
||||
|
||||
**阅读即代表您同意以上条款。**
|
||||
|
||||
****
|
||||
在识别出部分初始API端点后,我们还可通过Intruder工具探测隐藏端点。例如,假设已发现以下用于更新用户信息的API端点:
|
||||
|
||||
PUT /api/user/
|
||||
update
|
||||
|
||||
为发现隐藏端点,可使用
|
||||
Burp Intruder探测相同结构的其他资源。例如,可在路径的
|
||||
/update位置插入包含常见功能名称(如
|
||||
delete、add等)的字典列表进行遍历。
|
||||
|
||||
搜索隐藏端点时,建议使用基于常见
|
||||
API命名规范和行业术语的词汇表。同时,也要根据初步侦察结果,纳入与目标应用相关的特定词汇。
|
||||
|
||||
针对以上内容,我们从“概念原理、操作实践、防御视角”几个层面来深入展开。
|
||||
|
||||
1. 核心概念:为什么能“发现”隐藏端点?
|
||||
|
||||
这种方法本质上是一种 “智能化的
|
||||
暴力猜解”。
|
||||
|
||||
API的规律性:现代API(尤其是RESTful风格)的设计往往遵循一定的模式和命名规范。开发人员倾向于使用
|
||||
一致的、可读的动词和名词。
|
||||
|
||||
动词(
|
||||
HTTP方法
|
||||
):
|
||||
GET(获取)、
|
||||
POST(创建)、
|
||||
PUT(更新)、
|
||||
DELETE(删除)、
|
||||
PATCH(部分更新)。
|
||||
|
||||
名词(资源/对象):
|
||||
user、admin、product、order、profile、config。
|
||||
|
||||
基于已知推断未知:当我们发现 /api/user/
|
||||
update 时,这就像获得了一个“模板”。我们很自然地会猜想:
|
||||
|
||||
同一个
|
||||
user 资源,是否有 /api/user/
|
||||
delete、/api/user/
|
||||
add、/api/user/
|
||||
list?
|
||||
|
||||
除了 user,应用程序是否还有其他资源,如 /api/
|
||||
product/update、/api/
|
||||
admin/delete、/api/
|
||||
config/list?
|
||||
|
||||
2. 操作实践:如何更有效地使用
|
||||
Intruder
|
||||
?
|
||||
|
||||
我们提到的在 /
|
||||
update 位置进行替换是最常见的方法之一。我们可以系统化这个流程:
|
||||
|
||||
步骤分解:
|
||||
|
||||
(1).侦察与捕获:通过浏览应用、使用爬虫或分析前端JS文件,尽可能多地收集可见的端点(如 /api/user/
|
||||
update)。这是你的“种子”。
|
||||
|
||||
(2).构造攻击位置:在Burp Suite中,将请求发送到Intruder模块。
|
||||
|
||||
位置策略:
|
||||
- 路径爆破:将整个路径部分设为变量。例如,对于 /api/
|
||||
user/
|
||||
update,你可以将
|
||||
user 和
|
||||
update 都设为变量,形成 /<1>/<2> 的格式。
|
||||
|
||||
- 方法爆破:除了路径,也尝试更改HTTP方法。可能
|
||||
POST /api/user/update 不可用,但
|
||||
PATCH /api/user/update 却是有效的【这种我们在前面章节有说到过】。
|
||||
|
||||
- 参数爆破:有时端点是 /api/user,通过不同的参数来区分动作,如
|
||||
?action=update。这也可以作为爆破点。
|
||||
|
||||
|
||||
(3).准备高质量的字典:这是成功的关键。
|
||||
- 通用字典:使用像 SecLists 项目中的
|
||||
Discovery/Web-Content/api/ 目录下的字典,它包含了大量API相关的常见路径和参数名。
|
||||
|
||||

|
||||
|
||||
|
||||
- 行业特定术语:如果目标是金融应用,加入
|
||||
account, transfer, transaction;如果是社交应用,加入
|
||||
post, comment, friend。
|
||||
|
||||
- 基于应用的定制字典:从已收集的端点、响应信息、JavaScript文件中提取关键词。例如,发现了
|
||||
getUserProfile 函数,就可以将
|
||||
profile 加入字典。
|
||||
|
||||
- 变形与组合:使用工具生成大小写变体、单复数、添加前后缀(如
|
||||
/api/v1/user, /api/internal/user)。
|
||||
|
||||
|
||||
(4).执行与分析:
|
||||
|
||||
发起攻击后,不要只看状态码。404 是“不存在”,但 403(禁止访问)或 401(未授权)通常意味着
|
||||
端点存在,只是你没有权限,这是一个重大发现。
|
||||
|
||||
重点分析长度和响应内容与众不同的响应。一个返回
|
||||
{"error": "Invalid parameter"} 的 400 错误,可能比一个标准的 404 页面更有价值,因为它暗示
|
||||
服务器在处理这个路径。
|
||||
|
||||
注意 200 状态码但返回空内容或默认错误页的情况,这可能意味着端点存在但请求方式不对。
|
||||
|
||||
3. 防御视角:为什么会存在隐藏端点?
|
||||
- 遗留代码/调试端点:开发过程中留下的测试接口、管理后台入口,上线时未移除。
|
||||
|
||||
- 未文档化的功能:API文档更新不及时,或内部使用的接口未公开。
|
||||
|
||||
- 权限校验不完整:端点存在,但开发人员只在客户端菜单或按钮上做了权限控制,未在服务器端接口层进行校验。
|
||||
|
||||
- 架构分层:不同版本的API(如
|
||||
/api/v1/ 和
|
||||
/api/v2/)共存,旧版本被遗忘。
|
||||
|
||||
|
||||
防御建议:
|
||||
- 严格的访问控制:对所有端点实施“默认拒绝”策略,必须经过身份验证和授权检查。
|
||||
|
||||
- 定期审计与扫描:使用自动化工具和手动测试,定期对自身API进行模糊测试,发现隐藏或暴露的端点。
|
||||
|
||||
- 清理无用代码:建立上线前清理机制,移除调试代码和未使用的端点。
|
||||
|
||||
- 完善的日志与监控:对所有访问请求进行日志记录,并设置告警监控异常访问模式(如对大量不存在的路径进行探测)。
|
||||
|
||||
|
||||
关于如何挖掘、发现更多的api端点就介绍到这。接下来我们还会继续就api接口漏洞的更多细节进行内容输出,感兴趣的你,别忘了关注我。
|
||||
|
||||
@@ -0,0 +1,44 @@
|
||||
# 【漏洞通告】n8n Webhook 请求处理不当导致未经身份验证的文件访问漏洞(CVE-2026-21858)
|
||||
启明星辰安全简讯 2026-01-08 08:46
|
||||
|
||||
### 一、漏洞概述
|
||||
<table><tbody style="visibility: visible;"><tr style="height: 20.15pt; visibility: visible;"><td width="100" style="border-width: 2.25pt 1.5pt 1.5pt 2.25pt; border-color: windowtext; border-style: solid; background: rgb(222, 234, 246); padding: 0cm 5.4pt; visibility: visible;" height="20"><p style="text-align: center; line-height: 150%; margin-top: 0px; margin-bottom: 0px; visibility: visible;"><span style="font-family: 微软雅黑, "sans-serif"; color: rgb(51, 51, 51); font-size: 14px; visibility: visible;">漏洞名称<o:p style="visibility: visible;"></o:p></span></p></td><td width="100" colspan="3" valign="middle" style="width:91.0pt;background:#DEEAF6;border-top: 2.25pt solid windowtext; border-left: none; border-bottom: 1.5pt solid windowtext; border-right: 2.25pt solid windowtext;padding:0pt 5.4pt 0pt 5.4pt;height:20.15pt;"><p style="mso-margin-top-alt: auto;mso-margin-bottom-alt: auto;margin-left: 0.0pt;text-indent: 0.0pt;mso-pagination: widow-orphan;font-size: 12.0pt;font-family: 宋体;mso-fareast-font-family: 宋体;mso-bidi-font-family: 宋体;font-weight: normal;mso-bidi-font-weight: normal;text-align: center;line-height: 150%;"><span style="mso-bookmark:OLE_LINK4;"><span style="mso-bookmark:OLE_LINK1;"><span style="mso-bookmark:OLE_LINK2;"><span style="mso-bookmark:OLE_LINK6;"><span style="mso-bookmark:_Hlk121210716;"><span style="font-family:微软雅黑;mso-ascii-font-family:微软雅黑;mso-bidi-font-family:Arial;font-variant:normal;text-transform:none;color:#333333;">n8n Webhook 请求处理不当导致未经身份验证的文件访问漏洞</span></span></span></span></span></span></p></td></tr><tr style="height: 20.15pt; visibility: visible;"><td width="100" style="border-top: none; border-left: 2.25pt solid windowtext; border-bottom: 1.5pt solid windowtext; border-right: 1.5pt solid windowtext;background: rgb(222, 234, 246); padding: 0cm 5.4pt; visibility: visible;" height="20"><p style="text-align: center; line-height: 150%; margin-top: 0px; margin-bottom: 0px; visibility: visible;"><span style="font-family: 微软雅黑, "sans-serif"; color: rgb(51, 51, 51); font-size: 14px; visibility: visible;">CVE ID<o:p style="visibility: visible;"></o:p></span></p></td><td width="100" colspan="3" valign="middle" style="width:91.0pt;background:#DEEAF6;border-top:none;border-left:none;border-bottom: 1.5pt solid windowtext;border-right:2.25pt solid windowtext;padding:0pt 5.4pt 0pt 5.4pt;height:20.15pt;"><p style="mso-margin-top-alt: auto;mso-margin-bottom-alt: auto;margin-left: 0.0pt;text-indent: 0.0pt;mso-pagination: widow-orphan;font-size: 12.0pt;font-family: 宋体;mso-fareast-font-family: 宋体;mso-bidi-font-family: 宋体;font-weight: normal;mso-bidi-font-weight: normal;text-align: center;line-height: 150%;"><span style="mso-bookmark:OLE_LINK4;"><span style="mso-bookmark:OLE_LINK1;"><span style="mso-bookmark:OLE_LINK2;"><span style="mso-bookmark:OLE_LINK6;"><span style="mso-bookmark:_Hlk121210716;"><span style="font-family:微软雅黑;mso-ascii-font-family:微软雅黑;mso-bidi-font-family:Arial;font-variant:normal;text-transform:none;color:#333333;">CVE-2026-21858</span></span></span></span></span></span></p></td></tr><tr style="height: 20.15pt; visibility: visible;"><td width="100" style="border-top: none; border-left: 2.25pt solid windowtext; border-bottom: 1.5pt solid windowtext; border-right: 1.5pt solid windowtext;background: rgb(222, 234, 246); padding: 0cm 5.4pt; visibility: visible;" height="20"><p style="text-align: center; line-height: 150%; margin-top: 0px; margin-bottom: 0px; visibility: visible;"><span style="font-family: 微软雅黑, "sans-serif"; color: rgb(51, 51, 51); font-size: 14px; visibility: visible;">漏洞类型<o:p style="visibility: visible;"></o:p></span></p></td><td width="100" style="border-top: none; border-left: none; border-bottom: 1.5pt solid windowtext; border-right: 1.5pt solid windowtext;background: rgb(222, 234, 246); padding: 0cm 5.4pt; visibility: visible;" height="20"><p style="text-align: center; line-height: 150%; margin-top: 0px; margin-bottom: 0px; visibility: visible;"><span style="font-family: 微软雅黑, "sans-serif"; color: rgb(51, 51, 51); font-size: 14px; visibility: visible;">身份验证缺失<o:p style="visibility: visible;"></o:p></span></p></td><td width="100" style="border-top: none; border-left: none; border-bottom: 1.5pt solid windowtext; border-right: 1.5pt solid windowtext;background: rgb(222, 234, 246); padding: 0cm 5.4pt; visibility: visible;" height="20"><p style="text-align: center; line-height: 150%; margin-top: 0px; margin-bottom: 0px; visibility: visible;"><span style="font-family: 微软雅黑, "sans-serif"; color: rgb(51, 51, 51); font-size: 14px; visibility: visible;">发现时间<o:p style="visibility: visible;"></o:p></span></p></td><td width="100" style="border-top: none; border-left: none; border-bottom: 1.5pt solid windowtext; border-right: 2.25pt solid windowtext;backgroLine truncated
|
||||
n8n是一个开源的工作流自动化工具,旨在帮助用户通过图形化界面设计和自动化各种任务。它支持多种集成方式,可以与众多第三方服务和应用进行连接,例如数据库、API、云服务等。n8n提供丰富的节点和触发器,用户可以通过配置工作流来实现数据处理、任务调度、系统集成等功能。其可扩展性强,支持自定义节点,适用于开发者和企业用户,帮助提高工作效率和自动化水平。
|
||||
|
||||
2026年1月8日,启明星辰集团VSRC监测到n8n中存在一个未经身份验证的文件访问漏洞,攻击者通过特定的表单工作流请求可以访问服务器上的敏感文件。该漏洞由不当的webhook请求处理引起,攻击者利用这一漏洞能够在没有身份验证的情况下,远程访问文件,进而导致敏感信息泄露。漏洞的严重性取决于部署配置和使用的工作流。在某些情况下,攻击者可能进一步利用此漏洞对系统进行更深层次的入侵。漏洞评分10分,漏洞级别严重。
|
||||
### 二、影响范围
|
||||
|
||||
n8n <= 1.65.0
|
||||
### 三、安全措施
|
||||
|
||||
3.1 升级版本
|
||||
|
||||
官方已发布修复补丁,以修复该漏洞。
|
||||
|
||||
n8n >= 1.121.0
|
||||
|
||||
下载链接:
|
||||
|
||||
https://github.com/n8n-io/n8n/releases/
|
||||
|
||||
3.2 临时措施
|
||||
|
||||
暂无。
|
||||
|
||||
3.3 通用建议
|
||||
|
||||
定期更新系统补丁,减少系统漏洞,提升服务器的安全性。
|
||||
|
||||
加强系统和网络的访问控制,修改防火墙策略,关闭非必要的应用端口或服务,减少将危险服务(如SSH、RDP等)暴露到公网,减少攻击面。
|
||||
|
||||
使用企业级安全产品,提升企业的网络安全性能。
|
||||
|
||||
加强系统用户和权限管理,启用多因素认证机制和最小权限原则,用户和软件权限应保持在最低限度。
|
||||
|
||||
启用强密码策略并设置为定期修改。
|
||||
|
||||
3.4 参考链接
|
||||
|
||||
https://www.cyera.com/research-labs/ni8mare-unauthenticated-remote-code-execution-in-n8n-cve-2026-21858/
|
||||
|
||||
https://github.com/n8n-io/n8n/security/advisories/GHSA-v4pr-fm98-w9pg
|
||||
@@ -0,0 +1,42 @@
|
||||
# 【漏洞通告】n8n 远程代码执行漏洞(CVE-2026-21877)
|
||||
启明星辰安全简讯 2026-01-08 08:46
|
||||
|
||||
### 一、漏洞概述
|
||||
<table><tbody style="visibility: visible;"><tr style="height: 20.15pt; visibility: visible;"><td width="100" style="border-width: 2.25pt 1.5pt 1.5pt 2.25pt; border-color: windowtext; border-style: solid; background: rgb(222, 234, 246); padding: 0cm 5.4pt; visibility: visible;" height="20"><p style="text-align: center; line-height: 150%; margin-top: 0px; margin-bottom: 0px; visibility: visible;"><span style="font-family: 微软雅黑, "sans-serif"; color: rgb(51, 51, 51); font-size: 14px; visibility: visible;">漏洞名称<o:p style="visibility: visible;"></o:p></span></p></td><td width="100" colspan="3" valign="middle" style="width:91.0pt;background:#DEEAF6;border-top: 2.25pt solid windowtext; border-left: none; border-bottom: 1.5pt solid windowtext; border-right: 2.25pt solid windowtext;padding:0pt 5.4pt 0pt 5.4pt;height:20.15pt;"><p style="mso-margin-top-alt: auto;mso-margin-bottom-alt: auto;margin-left: 0.0pt;text-indent: 0.0pt;mso-pagination: widow-orphan;font-size: 12.0pt;font-family: 宋体;mso-fareast-font-family: 宋体;mso-bidi-font-family: 宋体;font-weight: normal;mso-bidi-font-weight: normal;text-align: center;line-height: 150%;"><span style="mso-bookmark:OLE_LINK4;"><span style="mso-bookmark:OLE_LINK1;"><span style="mso-bookmark:OLE_LINK2;"><span style="mso-bookmark:OLE_LINK6;"><span style="mso-bookmark:_Hlk121210716;"><span style="font-family:微软雅黑;mso-ascii-font-family:微软雅黑;mso-bidi-font-family:Arial;font-variant:normal;text-transform:none;color:#333333;">n8n 远程代码执行漏洞</span></span></span></span></span></span></p></td></tr><tr style="height: 20.15pt; visibility: visible;"><td width="100" style="border-top: none; border-left: 2.25pt solid windowtext; border-bottom: 1.5pt solid windowtext; border-right: 1.5pt solid windowtext;background: rgb(222, 234, 246); padding: 0cm 5.4pt; visibility: visible;" height="20"><p style="text-align: center; line-height: 150%; margin-top: 0px; margin-bottom: 0px; visibility: visible;"><span style="font-family: 微软雅黑, "sans-serif"; color: rgb(51, 51, 51); font-size: 14px; visibility: visible;">CVE ID<o:p style="visibility: visible;"></o:p></span></p></td><td width="100" colspan="3" valign="middle" style="width:91.0pt;background:#DEEAF6;border-top:none;border-left:none;border-bottom: 1.5pt solid windowtext;border-right:2.25pt solid windowtext;padding:0pt 5.4pt 0pt 5.4pt;height:20.15pt;"><p style="mso-margin-top-alt: auto;mso-margin-bottom-alt: auto;margin-left: 0.0pt;text-indent: 0.0pt;mso-pagination: widow-orphan;font-size: 12.0pt;font-family: 宋体;mso-fareast-font-family: 宋体;mso-bidi-font-family: 宋体;font-weight: normal;mso-bidi-font-weight: normal;text-align: center;line-height: 150%;"><span style="mso-bookmark:OLE_LINK4;"><span style="mso-bookmark:OLE_LINK1;"><span style="mso-bookmark:OLE_LINK2;"><span style="mso-bookmark:OLE_LINK6;"><span style="mso-bookmark:_Hlk121210716;"><span style="font-family:微软雅黑;mso-ascii-font-family:微软雅黑;mso-bidi-font-family:Arial;font-variant:normal;text-transform:none;color:#333333;">CVE-2026-21877</span></span></span></span></span></span></p></td></tr><tr style="height: 20.15pt; visibility: visible;"><td width="100" style="border-top: none; border-left: 2.25pt solid windowtext; border-bottom: 1.5pt solid windowtext; border-right: 1.5pt solid windowtext;background: rgb(222, 234, 246); padding: 0cm 5.4pt; visibility: visible;" height="20"><p style="text-align: center; line-height: 150%; margin-top: 0px; margin-bottom: 0px; visibility: visible;"><span style="font-family: 微软雅黑, "sans-serif"; color: rgb(51, 51, 51); font-size: 14px; visibility: visible;">漏洞类型<o:p style="visibility: visible;"></o:p></span></p></td><td width="100" style="border-top: none; border-left: none; border-bottom: 1.5pt solid windowtext; border-right: 1.5pt solid windowtext;background: rgb(222, 234, 246); padding: 0cm 5.4pt; visibility: visible;" height="20"><p style="text-align: center; line-height: 150%; margin-top: 0px; margin-bottom: 0px; visibility: visible;"><span style="font-family: 微软雅黑, "sans-serif"; color: rgb(51, 51, 51); font-size: 14px; visibility: visible;">RCE<o:p style="visibility: visible;"></o:p></span></p></td><td width="100" style="border-top: none; border-left: none; border-bottom: 1.5pt solid windowtext; border-right: 1.5pt solid windowtext;background: rgb(222, 234, 246); padding: 0cm 5.4pt; visibility: visible;" height="20"><p style="text-align: center; line-height: 150%; margin-top: 0px; margin-bottom: 0px; visibility: visible;"><span style="font-family: 微软雅黑, "sans-serif"; color: rgb(51, 51, 51); font-size: 14px; visibility: visible;">发现时间<o:p style="visibility: visible;"></o:p></span></p></td><td width="100" style="border-top: none; border-left: none; border-bottom: 1.5pt solid windowtext; border-right: 2.25pt solid windowtext;background: rgb(222, 234, 246); padding: 0cm 5.4pt; visibility: visibLine truncated
|
||||
n8n是一个开源的工作流自动化工具,旨在帮助用户通过图形化界面设计和自动化各种任务。它支持多种集成方式,可以与众多第三方服务和应用进行连接,例如数据库、API、云服务等。n8n提供丰富的节点和触发器,用户可以通过配置工作流来实现数据处理、任务调度、系统集成等功能。其可扩展性强,支持自定义节点,适用于开发者和企业用户,帮助提高工作效率和自动化水平。
|
||||
|
||||
2026年1月8日,启明星辰集团VSRC监测到n8n存在一个身份验证后远程代码执行(RCE)漏洞。在特定条件下,已验证用户可能通过构造恶意请求,导致n8n服务执行未经信任的代码,从而实现远程代码执行。这一漏洞的利用可能导致受影响实例的完全控制和泄露。该漏洞影响包括自托管和n8n云实例,攻击者能够通过恶意代码执行获取对系统的控制权。漏洞评分9.9分,漏洞级别严重。
|
||||
### 二、影响范围
|
||||
|
||||
0.123.0 <= n8n < 1.121.3
|
||||
### 三、安全措施
|
||||
|
||||
3.1 升级版本
|
||||
|
||||
官方已发布修复补丁,以修复该漏洞。
|
||||
|
||||
n8n >= 1.121.3
|
||||
|
||||
下载链接:
|
||||
|
||||
https://github.com/n8n-io/n8n/releases/
|
||||
|
||||
3.2 临时措施
|
||||
|
||||
暂无。
|
||||
|
||||
3.3 通用建议
|
||||
|
||||
定期更新系统补丁,减少系统漏洞,提升服务器的安全性。
|
||||
|
||||
加强系统和网络的访问控制,修改防火墙策略,关闭非必要的应用端口或服务,减少将危险服务(如SSH、RDP等)暴露到公网,减少攻击面。
|
||||
|
||||
使用企业级安全产品,提升企业的网络安全性能。
|
||||
|
||||
加强系统用户和权限管理,启用多因素认证机制和最小权限原则,用户和软件权限应保持在最低限度。
|
||||
|
||||
启用强密码策略并设置为定期修改。
|
||||
|
||||
3.4 参考链接
|
||||
|
||||
https://github.com/n8n-io/n8n/security/advisories/GHSA-v364-rw7m-3263/
|
||||
@@ -0,0 +1,169 @@
|
||||
# 【论文速读】| 用于软件供应链安全自主防御的Agentic AI:从溯源到漏洞缓解
|
||||
原创 知识分享者 安全极客 2026-01-08 09:35
|
||||
|
||||
|
||||
|
||||
**基本信息**
|
||||
|
||||
|
||||
原文标题:Agentic AI for Autonomous Defense in Software Supply Chain Security: Beyond Provenance to Vulnerability Mitigation
|
||||
|
||||
原文作者:Toqeer Ali Syed, Mohammad Riyaz Belgaum, Salman Jan, Asadullah Abdullah Khan, Saad Said Alqahtani
|
||||
|
||||
作者单位:伊斯兰大学(麦地那,沙特阿拉伯);阿拉伯开放大学巴林分校(A’Ali,巴林)
|
||||
|
||||
关键词:软件供应链安全,Agentic AI,多智能体,LLM推理,强化学习,区块链安全账本,持续集成/持续部署(CI/CD),主动防御
|
||||
|
||||
原文链接:https://arxiv.org/abs/2512.23480
|
||||
|
||||
开源代码:暂无
|
||||
|
||||
|
||||
**论文要点**
|
||||
|
||||
|
||||
论文简介:本论文聚焦于应对日益严重的软件供应链安全威胁,尤其是在可信开发与交付流程被攻击者利用的现实背景下,现有的传统溯源和完整性验证手段(如SLSA、SBOM、in-toto)主要事后追溯和溯源能力,缺乏主动、实时的漏洞发现与防御功能。作者提出了一种基于Agentic AI(智能体人工智能)的自主软件供应链安全防御框架,将大语言模型(LLM)推理、强化学习(RL)和多智能体协作相结合,设计专用安全Agent,并通过LangChain和LangGraph实现智能体编排与协同,使用Model Context Protocol(MCP)对接真实CI/CD环境,全程行动与观测记录于区块链安全账本以保证完整性与可审计性。在仿真和真实GitHub Actions与Jenkins环境中,框架能够有效检测和缓解注入攻击、不安全反序列化、访问控制失效、配置错误等主流威胁,实验结果显示其在检测准确率、缓解时延以及操作开销等方面优于传统的规则、溯源及强化学习单一基线,证明了Agentic AI推动自防御、主动的软件供应链安全体系的可行性和价值。
|
||||
|
||||
研究目的:当前软件供应链已成为数字生态系统中最关键却易受攻击的环节。近年来如SolarWinds、XZ Utils等著名事件显示,攻击者能够利用可信的开发与交付流程,向数千下游系统渗透恶意组件。这些攻击在软件生产(代码贡献、依赖集成、流水线执行等)过程中被引入,现有的溯源与透明度机制只能在事后进行验证,并不能主动阻断或缓解威胁。当前的主流工具大多反应迟缓,无法在构建前拦截异常,也难以在快速演化的攻击面前自适应调整。这一局限凸显了对能够在开发流程中自主感知、学习、推断和应对的新型智能防御机制的迫切需求。
|
||||
|
||||
Agentic AI 以其目标导向和自反性能力,为实现具备感知、认知、决策和行动闭环的主动型防御系统,提供了新的范式。本论文旨在跳出静态溯源和被动响应的框架,构建可持续学习和自适应决策的Agentic AI防御体系,实现对软件供应链全生命周期的实时风险管控与主动安全保障。
|
||||
|
||||
研究贡献:
|
||||
- 提出了Agentic AI驱动的自主软件供应链防御框架,将自适应的安全Agent体系引入整个供应链生命周期,突破传统溯源模型的被动局限,实现了对动态威胁(如注入、不安全配置等)的主动感知与即时缓解。
|
||||
|
||||
- 融合LLM语义推理与强化学习,实现安全决策的智能化与可解释性。大语言模型用于多阶段供应链语义关联分析和攻击模式溯源,强化学习赋予安全Agent自适应策略优化能力,在安全和业务连续性之间动态权衡。
|
||||
|
||||
- 多智能体协作机制与LangChain、LangGraph技术结合,支撑各Agent分工与决策流转,提升了系统的协作性、可扩展性与处理复杂场景的能力。
|
||||
|
||||
- 创新性地引入MCP协议与区块链安全账本实现标准化外部交互与操作透明审计,保证了溯源性和不可否认性,为安全事件回溯和治理提供强有力支撑。
|
||||
|
||||
- 在仿真及现实CI/CD环境(GitHub Actions和Jenkins)中进行系统性实验评估,全面证明了框架在检测率、响应时延、资源消耗等方面优于主流基线方法,推动了“自抗性供应链安全”的落地实践。
|
||||
|
||||
|
||||
|
||||
|
||||
**引言**
|
||||
|
||||
|
||||
随着现代数字生态日益复杂,软件供应链已成为其中最为重要却同时极易受攻击的薄弱环节。近期频发的重大安全事件(如SolarWinds供应链事件、XZ Utils后门攻击等)充分暴露了供应链攻击的高隐蔽性与大规模破坏潜力。攻击者能够借道受信任的开发和交付流程,将恶意代码、被篡改依赖、脆弱配置等注入到软件生命周期的早期,从而影响下游成千上万的系统。这些威胁已不限于已部署的软件,更多是在研发、构建或交付环节“种下”,使得传统依赖于事后完整性验证、人工代码审查或静态签名的防线变得越来越被动和脆弱。虽然SLSA、SBOM、in-toto等供应链安全框架能够提供一定程度的溯源、可追溯和工件验证能力,但在实际研发流水线面对异常依赖、恶意注入或配置漂移等动态风险时,这些机制的干预能力极为有限,往往要等到产物生成、交付甚至下游被攻击后才发现并追溯问题。现有工具普遍缺乏实时、前置、主动的异常检测与风险响应能力,难以满足现代敏捷开发和DevSecOps安全持续性的需求。
|
||||
|
||||
基于上述挑战,亟需新的安全范式,能够在“事前”甚至“事中”阶段持续学习、灵活适应复杂攻防环境,实现对整个开发—集成—交付链路的主动、智能、持续防护。Agentic AI(智能体人工智能)以其感知-认知-决策-行动闭环和目标导向自学习能力,为实现新一代自主供应链防御奠定了理论和方法基础。相较固定规则的传统自动化方案,Agentic AI能够在动态环境下探索新型威胁模式,优化策略、解释行动并自动调优安全策略。在本论文中,作者提出了一种基于Agentic AI的供应链安全防御框架,方案中融合了LLM驱动语义推理、强化学习赋能自适应决策、多智能体协作和区块链可信账本,为流水线中的不同环节(代码、依赖、配置、集成、部署)均配置专有安全Agent,实现实时威胁监控、异常隔离、修复和审计闭环。特别是在持续集成/持续部署(CI/CD)复杂流水线中,各Agent可自动互通、协作、感知与干预,推动安全从单点溯源进化到全链路自防御,并在实验层验证其在准确率、时延和可操作性等方面的优越性。这一创新实践为未来构建自抗性的、安全可信的软件生产与交付生态提供了重要理论基础与技术路线。
|
||||
|
||||
|
||||
**研究背景**
|
||||
|
||||
|
||||
软件供应链安全已成为近年学术界和产业界的研究热点,众多系统级威胁和事故推动了对供应链溯源、依赖验证、工件签名等基础设施的完善。最早的研究集中在依赖关系信任管理、工件完整性保护和元数据溯源,如SLSA、SBOM、in-toto等标准和机制广泛应用于产物验证和溯源追踪。这类方案普遍保障了工件的链路合法性与可追溯性,但往往停留在静态、被动、验收后追责的层面,缺乏对动态威胁环境的前瞻性响应能力。同时,部分研究关注软件供应链的安全设计原则,如透明性、有效性、分层隔离,提供了重要的理论支撑,但大多未能兼顾实时响应与智能化干预。
|
||||
|
||||
现有面向自动化的安全强化研究如ARGO-SLSA,初步实现了在Kubernetes等CI/CD流程下自动化合规与策略强制,但其本质仍为静态规则驱动,无法适应复杂威胁动态及新型攻击向量。在安全防御智能化方面,有学者尝试利用多智能体系统、协作型AI与强化学习等理论提升安全机制的自治性,但相关探索大多局限于物流、硬件、自动驾驶等领域,在软件开发与持续集成流中的实际落地实践有限,关于多Agent在软件供应链主动防御中协调协作与实时联动的模式仍缺乏系统性研究。
|
||||
|
||||
部分业界工作(如JFrog、Lineaje早期原型)试图通过AI Agent巡检与自愈修复实现AI化安全管控,但大多缺乏公开评测、可复现框架及同行验证,在方法的理论严谨性和适应复杂环境方面尚需突破。整体来看,既往方案在以下三个关键方面显著不足:一是强调事后产物完整性,多忽视风险前置干预;二是自动化手段未与智能化学习能力深度融合,难以识别与应对未知攻击模式;三是对注入攻击、配置漂移、访问控制失效等动态脆弱性的主动检测与自适应响应能力薄弱。该论文立足于此,首次系统性构建基于Agentic AI多智能体深度协作、可解释决策、有机学习的供应链安全体系,为领域迈向自抗性、主动性安全防御框架提供经验样板与理论支撑。
|
||||
|
||||
|
||||
**研究方法**
|
||||
|
||||
|
||||
论文提出的Agentic AI自主软件供应链防御框架,采用多层、多智能体体系结构渗透到整个供应链生命周期(从代码提交、依赖解析、CI/CD流水线到工件交付)。其核心体系包括智能体编排、语义安全推理、自适应决策优化、标准化外部交互和透明可信的安全账本,实现了全流程的持续感知、推理与主动干预。以下对主要关键技术与组成模块分层解析:
|
||||
|
||||
1. 框架总体架构
|
||||
|
||||
系统整体为多层次多智能体体系,每一安全Agent覆盖供应链的不同环节,包括代码分析、依赖安全、CI/CD监控、访问控制与配置审核。所有智能体通过LangChain的Agent编排能力和LangGraph的条件决策流构建,保障了Agent间的分工明确与协同高效。系统形成"监测→推理→决策→审计"的封闭反馈环,实现了全链路持续的安全压力测试与风险治理。
|
||||
|
||||
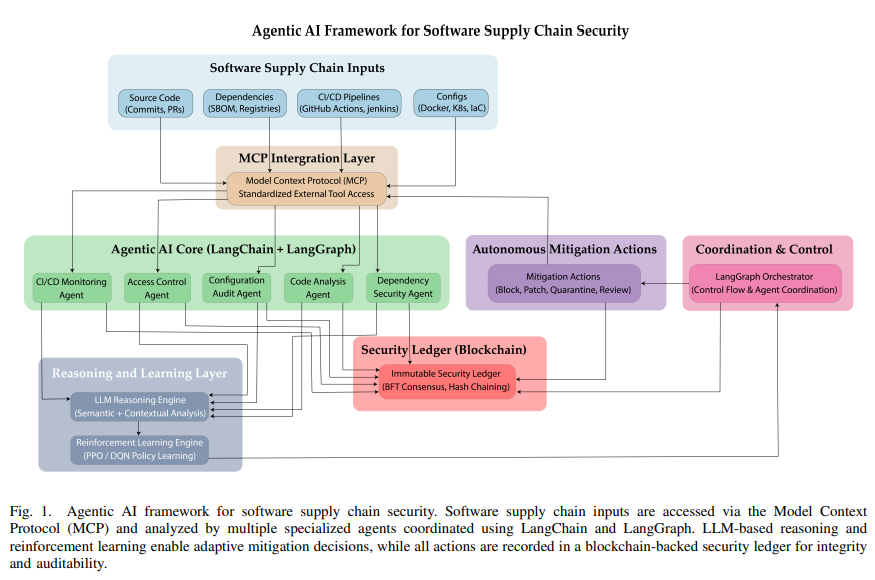
|
||||
|
||||
2. 多Agent协作与LangChain/LangGraph编排
|
||||
|
||||
具体Agent设计包括:代码分析Agent(聚焦代码提交和变更安全审查)、依赖智能Agent(分析第三方库和SBOM)、CI/CD监控Agent(管控流水线执行和配置)、访问控制Agent(分析权限与角色配置)以及配置审核Agent(核查容器、IaC配置等)。LangGraph实现了复杂的条件执行和流程分支,能够根据前置检测结果依次触发后续Agent补充验证或隔离流程。例如,代码分析Agent检测到疑似注入模式后,自动切换到CI/CD Agent进一步触发流程级验证并开展缓解措施。
|
||||
|
||||
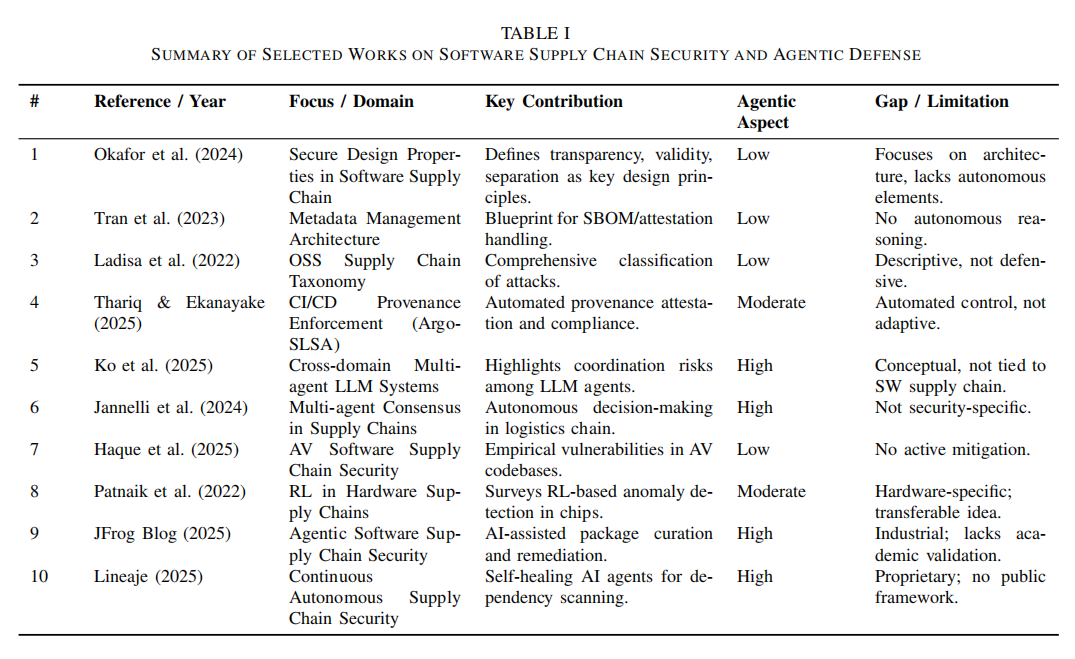
|
||||
|
||||
3. LLM推理与语义攻击建模
|
||||
|
||||
LLM作为框架的认知核心,不仅执行基础分类任务,更通过复杂提示模板实现跨阶段漏洞语义的聚合与推断。RAG(检索增强生成)机制将历史攻击轨迹、现行安全政策等上下文输入LLM推理链中,显著增强了面向注入、不安全反序列化、配置错误等语义类威胁的准确识别能力。同时,LLM可输出安全分析理由,实现各安全响应链条的可解释化。
|
||||
|
||||
4. 强化学习赋能决策自适应
|
||||
|
||||
为优化各Agent动作选择及策略调整,引入了以PPO算法为主的强化学习模型,每一智能体在模拟和真实流水线中按马尔可夫决策过程(MDP)优化自身策略。状态空间涵盖各环节上下文,动作空间为可执行安全缓解行为(如阻断构建、隔离依赖、请求人工复核),奖励函数按威胁缓解、误报、构建延迟和开发者采纳度综合制定,保障了安全效率与开发体验的动态均衡。
|
||||
|
||||
5. Model Context Protocol(MCP)及区块链安全账本
|
||||
|
||||
通过MCP协议,实现了智能体与外部(GitHub Actions、Jenkins等CI/CD工具链)的标准化消息传递与指令互操作,每一次检测、响应、缓解命令均独立记录并反馈。所有观察结果与安全行动被串联记录于基于BFT一致性和Merkle树完整性的权限型区块链,确保每一次安全决策的不可篡改、全程可追溯,为事后审计和威胁取证提供坚实支撑。
|
||||
|
||||
6. 容器化与可扩展实践
|
||||
|
||||
原型系统基于Python全模块化、服务化开发,所有Agent皆为独立服务,轻松通过容器调度扩展,支持Kubernetes等主流云原生环境批量部署。实验参数与配置模板均版本化管理,全面支撑未来复现与平滑升级改进。
|
||||
|
||||
通过上述多层次深度集成,形成了“以Agent为分工基础,以LLM+RL为认知与自适应核心,以区块链账本为可信底座”的新一代供应链自主防御基础设施,实现了覆盖全生命周期、多角度、多策略的持续智能抗风险能力。
|
||||
|
||||
|
||||
**实验实现**
|
||||
|
||||
|
||||
为全面评估所提Agentic AI防御框架的有效性,论文在模拟与真实CI/CD环境下开展了系统性实验设计,涵盖攻击检测能力、缓解时延、资源消耗与协同效果等全方位指标。具体设置与流程如下:
|
||||
|
||||
1. 实验环境构建
|
||||
|
||||
实验分别在自主仿真CI/CD流水线与真实GitHub Actions、Jenkins流水线部署场景下进行,所用源码仓库中注入了已知类型的威胁实例,包括典型的依赖投毒、脚本注入、不当配置(如K8S YAML错误)、访问控制隐患等。所有智能体通过MCP协议实时报文交互,各Agent同步监控流水线变更、日志、构建产物及环境配置。
|
||||
|
||||
2. 攻击场景与评测维度
|
||||
|
||||
主要覆盖四类中心威胁:注入攻击、不安全反序列化、访问控制失效和系统配置错误。对每类威胁,分别评估检测召回(precision/recall/F1)、缓解时延(MTTM)、应急响应覆盖率和自动化比率等指标。实际开发者可见性、提示解释性和流水线工时开销亦为关注维度。
|
||||
|
||||
3. 基线方法设置
|
||||
|
||||
选取了多种主流对比基线,包括静态规则驱动分析(如代码linter、策略引擎)、溯源/产物验证方案(如SLSA、in-toto)、仅用于强化学习Agent(无LLM推理)、以及商用AI代码安全扫描工具,通过统一数据集和实验流程确保基线对比公平、科学。
|
||||
|
||||
4. 消融实验与资源测量
|
||||
|
||||
通过模块级消融实验(分别关闭LLM、RL、账本等核心组件)分析每一技术点的独立增益与贡献;辅助统计流水线整体构建时延、CPU/内存消耗、开发者人工干预频度和安全事件回溯耗时,量化系统部署的运维负荷。
|
||||
|
||||
整个实验执行过程及参数均被版本化管理,并依托区块链账本完整记录,既保证了结果可靠复现,又为后续研究扩展和行业落地推广提供了范例支撑。
|
||||
|
||||
|
||||
**实验结果**
|
||||
|
||||
|
||||
实验结果显示,Agentic AI自主防御框架在检测准确率、威胁响应效率及资源开销等核心指标方面,均显著优于主流对比基线,并具备良好的主动防御和解释能力。具体分析如下:
|
||||
|
||||
1. 漏洞检测和缓解效果
|
||||
|
||||
在所有四类核心脆弱性检测场景(注入攻击、不安全反序列化、访问控制违例、配置失误),框架F1-score均高于静态规则和溯源基线,特别是在复杂语义型漏洞(如反序列化、访问控制)上优势更为突出。融合LLM的语义推理带来召回率(recall)大幅提升,而多Agent+RL协同有效降低了误报率和“误杀”概率,实现了精细化安全感知。
|
||||
|
||||
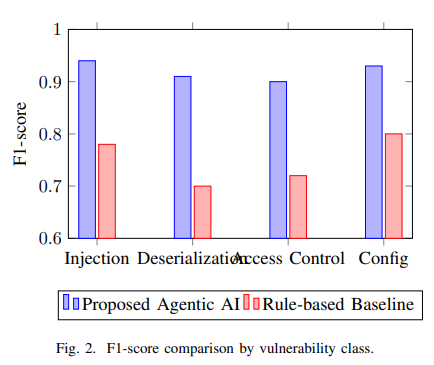
|
||||
|
||||
2. 缓解响应时延与自动化率
|
||||
|
||||
平均威胁缓解时延(从检测到实际修复/阻断)方面,Agentic AI系统可在无需人工干预下自动推出隔离、修复动作,大幅缩短解决时间,相较被动规则体系,响应时效提升最为显著。在真实流水线部署(GitHub Actions/Jenkins)中,逾90%的自动缓解操作均由Agent自主执行,仅有极少高度相关业务场景需人工确权二次确认。开发者反馈显示,由LLM自动生成的可解释“处置理由”,易于理解和采纳,且系统账本可信透明,便于后期溯源审计。
|
||||
|
||||
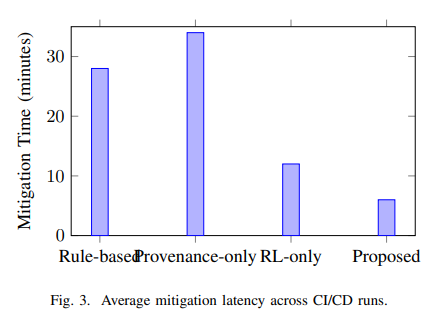
|
||||
|
||||
3. 系统开销与可扩展性
|
||||
|
||||
性能评测显示,Agentic AI体系对流水线的平均代码构建时延增加小于6%,主因在于并行分析和区块链写入带来小幅追加延迟;内存及CPU消耗则因容器化多条件优化,整体保持较低水平。消融实验进一步验证了LLM部分对检测复杂漏洞的关键贡献(召回提升15%以上),RL模块对缓解延迟和误报抑制明显(自动决策精度提升),安全账本在审计追踪和信任支撑方面不可替代,虽然对检测本身影响有限,但极大丰富了系统可用场景。
|
||||
|
||||
|
||||
|
||||
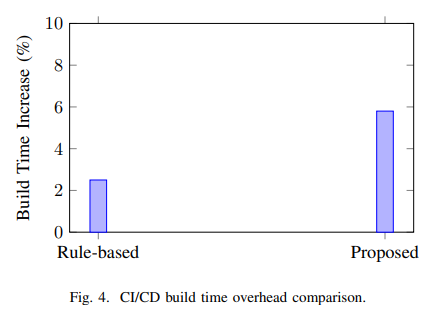
|
||||
|
||||
|
||||
4. 综合讨论与意义
|
||||
|
||||
整体上,本框架以多智能体协作和大模型认知为核心,推动软件供应链安全从“事后被动溯源”向“全流程主动能力”进化,不仅技术指标超越传统基线,更为开发与运维生态注入了持续安全自治的新范式。虽然新增的安全模块带来一定资源开销,但其系统性风险防控能力和变革性自治架构足以为关键领域支付“安全溢价”。此外,实验还验证了各技术组件的独立和协同价值,夯实了Agentic AI方案作为未来供应链安全主流基石的理论与实证基础。
|
||||
|
||||
|
||||
**论文结论**
|
||||
|
||||
|
||||
本论文系统提出并实践了Agentic AI赋能的自主软件供应链防御新框架,有效实现了从静态溯源走向动态主动防御的跨越。通过融合LLM驱动的语义分析、强化学习支撑的决策自适应、多智能体编排与区块链保障的可信审计,全方位地覆盖了供应链代码、依赖、配置、集成到交付全生命周期的安全风险监控与缓解。大规模仿真与真实CI/CD部署评测表明,所提框架无论在漏洞检测准确性、缓解效率还是操作可解释性和审计透明度上,均优于传统基线方法。与此同时,其模块化、标准化和可扩展性,也满足了云原生与DevSecOps等现代研发场景规模化落地与持续演进的需求。
|
||||
|
||||
尽管该方案在实际落地时仍面临操作开销、Agent协同复杂性、适应极端边界场景等现实挑战,但研究明确展示了利用Agentic AI推动供应链自防御机制的巨大潜力和实际价值。未来工作有望围绕更丰富攻击类别、跨团队协作问题、更加自适应的RL算法与可解释AI安全等领域开展深入拓展与优化,持续护航软件产业的安全可持续发展,为实现真正的“自抗性供应链”铺设坚实的理论与技术道路。
|
||||
|
||||
-End-
|
||||
|
||||
[](https://mp.weixin.qq.com/s?__biz=MzkzNDUxOTk2Mw==&mid=2247495405&idx=1&sn=67249648d5c312b5c178b23b077d28f3&scene=21#wechat_redirect)
|
||||
|
||||

|
||||
|
||||
|
||||

|
||||
|
||||
@@ -0,0 +1,86 @@
|
||||
# 【附POC及复现环境】n8n双CVE漏洞利用链可致远程代码执行漏洞(CVE-2026-21858+CVE-2025-68613)
|
||||
原创 a1batr0ss 天翁安全 2026-01-08 09:45
|
||||
|
||||
**免责声明:**
|
||||
本公众号所发布的全部内容,包括但不限于技术文章、POC脚本、漏洞利用工具及相关测试环境,均仅限于合法的网络安全学习、研究和教学用途。所有人在使用上述内容时,应严格遵守中华人民共和国相关法律法规以及道德伦理要求。未经明确的官方书面授权,严禁将公众号内的任何内容用于未经授权的渗透测试、漏洞利用或攻击行为。 所有人仅可在自己合法拥有或管理的系统环境中进行本地漏洞复现与安全测试,或用于具有明确授权的合法渗透测试项目。所有人不得以任何形式利用公众号内提供的内容从事非法、侵权或其他不当活动。 如因违反上述规定或不当使用本公众号提供的任何内容,造成的一切法律责任、经济损失、纠纷及其他任何形式的不利后果,均由相关成员自行承担,与本公众号无任何关联。
|
||||
## 不错过最新的漏洞POC
|
||||
|
||||
为保证您可以在第一时间接收到本公众号分享的**漏洞复现及POC**
|
||||
信息,建议您在公众号“天翁安全”主页界面将“天翁安全”设为**星标**
|
||||
。
|
||||
|
||||

|
||||
|
||||
## 漏洞介绍
|
||||
|
||||
n8n 是一款开源的工作流自动化与集成平台,主打可自托管和高度可定制的自动化能力,允许用户通过可视化节点和表达式将不同的应用、服务和内部系统连接起来,广泛用于 DevOps、数据同步、告警处理和业务流程自动化等场景;凭借对隐私友好的自部署模式、活跃的开源社区以及对数百种第三方服务的原生支持,n8n 在开发者和中小企业中具有较高影响力,已被大量公司用于生产环境,其工作流引擎往往直接接触内部系统、凭据和敏感数据,因此一旦出现安全漏洞,往往具有较大的实际风险和安全影响。
|
||||
|
||||
**CVE-2026-21858 与 CVE-2025-68613 可以组合形成一条完整的远程代码执行漏洞利用链**
|
||||
,其核心逻辑是“信息泄露导致信任边界崩塌,进而触发高权限代码执行漏洞”:攻击者首先利用 CVE-2026-21858 在未认证的情况下读取 n8n 服务器上的任意文件,从中获取配置文件、数据库内容或加密密钥等敏感信息,并据此伪造合法的管理员身份或会话;在成功冒充管理员后,攻击者即可访问 n8n 中仅对高权限用户开放的工作流和表达式功能,进一步利用 CVE-2025-68613 中表达式沙箱隔离不足的问题实现沙箱逃逸,最终在服务器上执行任意系统命令,从而将原本看似独立的文件读取和逻辑漏洞串联为一条高危的未授权 RCE 攻击链。
|
||||
|
||||

|
||||
## 漏洞影响版本
|
||||
|
||||
**CVE-2026-21858:**
|
||||
<table><thead><tr style="box-sizing: border-box;"><th style="box-sizing: border-box;margin: 0px;padding: 0.5rem 1rem;font-style: normal;font-weight: bold;text-align: left;border: 1px solid rgb(233, 235, 236);"><section><span leaf="">产品版本</span></section></th><th style="box-sizing: border-box;margin: 0px;padding: 0.5rem 1rem;font-style: normal;font-weight: bold;text-align: left;border: 1px solid rgb(233, 235, 236);"><section><span leaf="">版本</span></section></th></tr></thead><tbody><tr style="box-sizing: border-box;"><td style="box-sizing: border-box;margin: 0px;padding: 0.5rem 1rem;border: 1px solid rgb(233, 235, 236);"><section><span leaf="">n8n</span></section></td><td style="box-sizing: border-box;margin: 0px;padding: 0.5rem 1rem;border: 1px solid rgb(233, 235, 236);"><section><span leaf="">1.65.0 ≤ 版本 < 1.121.0</span></section></td></tr></tbody></table>
|
||||
**CVE-2025-68613:**
|
||||
<table><thead><tr style="box-sizing: border-box;"><th style="box-sizing: border-box;margin: 0px;padding: 0.5rem 1rem;font-style: normal;font-weight: bold;text-align: left;border: 1px solid rgb(233, 235, 236);"><section><span leaf="">产品版本</span></section></th><th style="box-sizing: border-box;margin: 0px;padding: 0.5rem 1rem;font-style: normal;font-weight: bold;text-align: left;border: 1px solid rgb(233, 235, 236);"><section><span leaf="">版本</span></section></th></tr></thead><tbody><tr style="box-sizing: border-box;"><td style="box-sizing: border-box;margin: 0px;padding: 0.5rem 1rem;border: 1px solid rgb(233, 235, 236);"><section><span leaf="">n8n 1.120.x</span></section></td><td style="box-sizing: border-box;margin: 0px;padding: 0.5rem 1rem;border: 1px solid rgb(233, 235, 236);"><section><span leaf="">0.211.0 ≤ 版本 < 1.120.4</span></section></td></tr><tr style="box-sizing: border-box;background-color: rgb(248, 248, 248);"><td style="box-sizing: border-box;margin: 0px;padding: 0.5rem 1rem;border: 1px solid rgb(233, 235, 236);"><section><span leaf="">n8n 1.121.x</span></section></td><td style="box-sizing: border-box;margin: 0px;padding: 0.5rem 1rem;border: 1px solid rgb(233, 235, 236);"><section><span leaf="">0.211.0 ≤ 版本 < 1.121.1</span></section></td></tr><tr style="box-sizing: border-box;"><td style="box-sizing: border-box;margin: 0px;padding: 0.5rem 1rem;border: 1px solid rgb(233, 235, 236);"><section><span leaf="">n8n 1.122.x</span></section></td><td style="box-sizing: border-box;margin: 0px;padding: 0.5rem 1rem;border: 1px solid rgb(233, 235, 236);"><section><span leaf="">0.211.0 ≤ 版本 < 1.122.0</span></section></td></tr></tbody></table>## 环境部署
|
||||
|
||||
在“n8n双CVE漏洞利用链复现环境” 中的执行以下命令部署漏洞复现环境
|
||||
> “n8n双CVE漏洞利用链复现环境”详见文末
|
||||
|
||||
```
|
||||
docker-compose up -d
|
||||
```
|
||||
|
||||

|
||||
|
||||
部署成功后访问 http://localhost:5678/
|
||||
可可看到如下界面
|
||||
|
||||

|
||||
## 漏洞复现
|
||||
> “n8n任意代码执行漏洞利用链POC”详见文末
|
||||
|
||||
|
||||
执行以下Python脚本:利用**CVE-2026-21858+CVE-2025-68613**
|
||||
漏洞利用链执行任意命令(这里执行id命令)
|
||||
```
|
||||
python n8n任意代码执行漏洞利用链POC.py http://localhost:5678 /form/vulnerable-form --cmd id
|
||||
```
|
||||
|
||||
执行Python脚本后会自动运行四个阶段**(任意文件读取 → 令牌伪造 → 沙箱绕过 → 执行命令)**
|
||||
|
||||
**第一阶段:任意文件读取**
|
||||
|
||||

|
||||
|
||||
**第二阶段:令牌伪造**
|
||||
|
||||

|
||||
|
||||
**第三阶段:沙箱绕过**
|
||||
|
||||

|
||||
|
||||
**第四阶段:执行命令**
|
||||
|
||||

|
||||
## 漏洞修复
|
||||
|
||||
目前n8n官方已发布新版本,建议用户立刻更新到**1.121.0及以上版本**
|
||||
。
|
||||
|
||||

|
||||
## 知识星球
|
||||
|
||||
**“n8n任意代码执行漏洞利用链POC”、“n8n双CVE漏洞利用链复现环境”、“n8n远程代码执行漏洞复现”**
|
||||
现已全部发布至知识星球,大家可在知识星球内获取,自行学习复现。
|
||||
|
||||

|
||||
> 星球加入方式见文章底部二维码,欢迎加入交流和学习
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
@@ -0,0 +1,165 @@
|
||||
# 【高危预警】Veeam备份软件曝出 CVSS 9.0 远程代码执行漏洞,勒索软件可利用其破坏备份数据
|
||||
原创 solarsec solar应急响应团队 2026-01-08 09:57
|
||||
|
||||

|
||||
|
||||
## 1.通告背景
|
||||
|
||||
在过去24小时,备份解决方案供应商 **Veeam**
|
||||
发布了安全更新(KB4738),修复了 Veeam Backup & Replication (VBR) 中的4个高危漏洞。其中,编号为 **CVE-2025-59470**
|
||||
的远程代码执行(RCE)漏洞 CVSS 评分高达 **9.0**
|
||||
。
|
||||
|
||||
备份系统是企业数据恢复的核心基础设施。一旦备份服务器遭攻击者控制,不仅意味着数据被窃取,更可能导致历史备份文件被彻底删除,从而使企业在遭受勒索病毒攻击时无法进行业务还原。
|
||||
|
||||
Solar 应急响应团队经过研判发现,该漏洞允许低权限用户获取服务器的最高控制权,极易被勒索软件组织用于破坏备份完整性。建议所有部署了 Veeam VBR 的客户立即开展自查与修补工作。
|
||||
## 2.漏洞技术分析
|
||||
|
||||
根据官方公告与补丁信息,此次受影响的版本为 **VBR 13.0.1.180 及更早版本**
|
||||
。漏洞的核心风险在于权限管理的逻辑缺陷,导致低权限账户可跨越边界执行任意代码。
|
||||
|
||||
**主要漏洞清单:**
|
||||
|
||||
<table><thead><tr><th style="color: rgb(89, 89, 89);font-size: 14px;line-height: 1.5em;letter-spacing: 0.02em;text-align: left;font-weight: bold;background: none 0% 0% / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">CVE 编号</span></section></th><th style="color: rgb(89, 89, 89);font-size: 14px;line-height: 1.5em;letter-spacing: 0.02em;text-align: left;font-weight: bold;background: none 0% 0% / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">漏洞类型</span></section></th><th style="color: rgb(89, 89, 89);font-size: 14px;line-height: 1.5em;letter-spacing: 0.02em;text-align: left;font-weight: bold;background: none 0% 0% / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">CVSS 评分</span></section></th><th style="color: rgb(89, 89, 89);font-size: 14px;line-height: 1.5em;letter-spacing: 0.02em;text-align: left;font-weight: bold;background: none 0% 0% / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">危害描述</span></section></th></tr></thead><tbody><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(255, 255, 255);background-image: none;background-origin: padding-box;background-position-x: 0%;background-position-y: 0%;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">CVE-2025-59470</span></section></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">远程代码执行 (RCE)</span></section></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">9.0 (高危)</span></section></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">允许具有“备份操作员”或“磁带操作员”权限的账户,通过构造恶意的内部参数,以 postgres 用户身份在服务器上执行任意系统命令。</span></section></td></tr><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(248, 248, 248);background-image: none;background-origin: paddiLine truncated
|
||||
|
||||

|
||||
|
||||
**图1:Veeam 官方发布 KB4738 安全更新公告(来源:Veeam官网)**
|
||||
|
||||
**Solar 团队研判:**
|
||||
虽然利用该漏洞需要攻击者拥有“备份操作员”等低级权限,但在实际的内网渗透场景中,攻击者往往通过爆破、钓鱼或凭证窃取(Credential Dumping)轻易获取此类普通账号。一旦获取,攻击者即可利用 **CVE-2025-59470**
|
||||
进行**本地权限提升(Local Privilege Escalation)**
|
||||
,从而完全接管备份服务器。
|
||||
## 3.勒索攻击场景研判
|
||||
|
||||
在 Solar 应急响应团队近期处置的勒索案件中,攻击者针对备份系统的破坏行为已成为标准攻击流程的一部分。
|
||||
# 3.1 攻击链路推演
|
||||
|
||||
结合我们掌握的 **Fog**
|
||||
、**Akira、LockBit等勒索家族的攻击手法,攻击者极有可能利用此漏洞构建以下攻击链路:**
|
||||
|
||||
**1.初始访问**
|
||||
:通过 RDP 爆破或 VPN 弱口令进入企业内网。
|
||||
|
||||
**2.横向探测**
|
||||
:扫描内网网段,定位安装了 Veeam VBR 的服务器端口(如 TCP 9392)。
|
||||
|
||||
**3.权限提升与破坏**
|
||||
:
|
||||
- 若服务器未修补漏洞,攻击者只需窃取或创建一个低权限的“操作员”账号。
|
||||
|
||||
- 利用 **CVE-2025-59470**
|
||||
执行恶意代码,直接获取服务器底层权限。
|
||||
|
||||
- **执行操作**
|
||||
:停止备份服务、格式化备份存储库、删除云端备份的不可变锁。
|
||||
|
||||
**4.全面加密**
|
||||
:在确认备份失效后,对生产环境服务器投放勒索病毒。
|
||||
# 3.2 实战警示:LockBit 案例中的数据恢复困境
|
||||
|
||||
在 Solar应急响应团队此前处理的一起非常经典的 **LockBit**
|
||||
勒索案件中,攻击者曾试图删除企业的数据库备份。虽然我们最终通过底层数据修复技术帮助客户挽回了损失,但该案例深刻揭示了备份服务器安全的重要性。
|
||||
|
||||
案例详情:[【成功案例】lockbit家族百万赎金不必付!技术手段修复被加密的数据库,附溯源分析报告](https://mp.weixin.qq.com/s?__biz=MzkyOTQ0MjE1NQ==&mid=2247493976&idx=1&sn=0471fb1022806483600fe259b7826972&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
如果黑客利用漏洞完全接管了备份服务器,删除了所有历史存档,那么即便拥有再强的数据修复技术,企业也将面临无法恢复的绝境。因此,修补备份软件漏洞,是保障数据恢复能力的重中之重。
|
||||
|
||||

|
||||
|
||||
**图2:黑客攻击路线图**
|
||||
## 4.处置建议与安全加固
|
||||
|
||||
针对此次高危漏洞,Solar 应急响应团队建议各单位立即执行以下防御措施:
|
||||
# A. 紧急补丁修复(优先级:P0)
|
||||
- **排查范围**
|
||||
:立即检查所有 Veeam Backup & Replication 服务器版本。
|
||||
|
||||
- **受影响版本**
|
||||
:**13.0.1.180 及以下**
|
||||
。
|
||||
|
||||
- **修复方案**
|
||||
:下载并安装 **Veeam KB4738**
|
||||
补丁。
|
||||
|
||||
- 补丁下载链接请参考 Veeam 官方支持门户:https://www.veeam.com/kb4738
|
||||
|
||||
# B. 攻击面收敛与加固
|
||||
|
||||
**1.网络隔离**
|
||||
:备份服务器不应直接暴露在普通办公内网,更严禁暴露在公网。建议将其部署在独立的**管理网段**
|
||||
,并配置严格的访问控制策略(ACL),仅允许特定运维 IP 访问。
|
||||
|
||||
**2.账号清理**
|
||||
:全面审查 Veeam 系统上的“备份操作员”和“磁带操作员”账号。移除所有不必要的账户,并强制开启 **MFA(多因素认证)**
|
||||
,防止账号被盗用。
|
||||
|
||||
**3.服务加固**
|
||||
:建议关闭备份服务器的 RDP 服务,改用带外管理(如 iDRAC/ILO)或通过堡垒机进行运维操作,阻断黑客利用 RDP 进行内网渗透的路径。
|
||||
# C. 备份策略升级
|
||||
- **落实“不可变备份”**
|
||||
:确保至少有一份备份存储在**Linux Hardened Repository**
|
||||
(Linux 加固存储库)或支持对象锁定的云存储(S3 Object Lock)中。这种存储方式能有效防止黑客即使获取了服务器权限也无法删除底层数据。
|
||||
|
||||

|
||||
|
||||
**图3:采用“不可变备份”架构阻断数据删除风险(来源:Veeam 官方架构图)**
|
||||
|
||||
以下是solar安全团队近期处理过的常见勒索病毒后缀:
|
||||
|
||||
<table><tbody><tr style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;"><td data-colwidth="168" width="168" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(255, 255, 255);max-width: 100%;box-sizing: border-box !important;background-color: rgb(165, 200, 255);"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(120, 120, 120);"><span style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(255, 255, 255);"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;"><span leaf="" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;">收录时间</span></strong></span></section></td><td data-colwidth="84" width="84" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(255, 255, 255);max-width: 100%;box-sizing: border-box !important;background-color: rgb(165, 200, 255);"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(120, 120, 120);"><p style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;clear: both;min-height: 1em;"><span style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(255, 255, 255);"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;"><span leaf="" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;">病毒家族</span></strong></span></p></section></td><td data-colwidth="49.0000%" width="49.0000%" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(255, 255, 255);max-width: 100%;box-sizing: border-box !important;background-color: rgb(165, 200, 255);"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(120, 120, 120);"><p style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;clear: both;min-height: 1em;"><span style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(255, 255, 255);"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;"><span leaf="" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;">相关文章</span></strong></span></p></section></td></tr><tr style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;"><td data-colwidth="168" width="168" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(255, 255, 255);max-width: 100%;box-sizing: border-box !important;background-color: rgb(237, 241, 253);"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;text-indent: 0em;"><span stLine truncated
|
||||
|
||||
|
||||
勒索攻击作为成熟的攻击手段,很多勒索家族已经形成了一套完整的商业体系,并且衍生了多个分支团队,导致勒索病毒迭代了多个版本。而每个家族擅用的攻击手法皆有不同,TellYouThePass勒索软件家族常常利用系统漏洞进行攻击;Phobos
|
||||
勒索软件家族通过RDP暴力破解进行勒索;Mallox勒索软件家族利用数据库漏洞,如(mssql命令执行)及暴力破解进行加密,攻击手法极多防不胜防。
|
||||
|
||||
<table><tbody><tr style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;"><td data-colwidth="30.0000%" width="30.0000%" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(255, 255, 255);max-width: 100%;box-sizing: border-box !important;background-color: rgb(165, 200, 255);visibility: visible;"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(120, 120, 120);visibility: visible;"><span style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(255, 255, 255);visibility: visible;"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;"><span leaf="" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;">收录时间</span></strong></span></section></td><td data-colwidth="49.0000%" width="49.0000%" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(255, 255, 255);max-width: 100%;box-sizing: border-box !important;background-color: rgb(165, 200, 255);visibility: visible;"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(120, 120, 120);visibility: visible;"><p style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;clear: both;min-height: 1em;visibility: visible;"><span style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(255, 255, 255);visibility: visible;"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;"><span leaf="" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;">相关文章</span></strong></span></p></section></td></tr><tr style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;"><td data-colwidth="30.0000%" width="30.0000%" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(255, 255, 255);max-width: 100%;box-sizing: border-box !important;background-color: rgb(237, 241, 253);visibility: visible;"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;text-indent: 0em;visibility: visible;"><span leaf="" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;">2024/12/12</span></section></section></td><td data-colwidth="49.0000%" width="49.0000%" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(255, 255, 255);max-width: 100%;box-sizing: border-box !important;background-color: rgb(237, 241, 253);visibility: visible;"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;"><span style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;"><span leaf="" style="-webkit-Line truncated
|
||||
|
||||
|
||||
有效的预防方法包括针对自身业务进行定期的基线加固、补丁更新及数据备份,在其基础上加强公司安全人员意识。
|
||||
|
||||
|
||||
<table><tbody><tr style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;"><td data-colwidth="30.0000%" width="30.0000%" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(255, 255, 255);max-width: 100%;box-sizing: border-box !important;background-color: rgb(165, 200, 255);visibility: visible;"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(120, 120, 120);visibility: visible;"><span style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(255, 255, 255);visibility: visible;"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;"><span leaf="" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;">收录时间</span></strong></span></section></td><td data-colwidth="49.0000%" width="49.0000%" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(255, 255, 255);max-width: 100%;box-sizing: border-box !important;background-color: rgb(165, 200, 255);visibility: visible;"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(120, 120, 120);visibility: visible;"><p style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;clear: both;min-height: 1em;visibility: visible;"><span style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(255, 255, 255);visibility: visible;"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;"><span leaf="" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;">相关文章</span></strong></span></p></section></td></tr><tr style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;"><td data-colwidth="30.0000%" width="30.0000%" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(255, 255, 255);max-width: 100%;box-sizing: border-box !important;background-color: rgb(237, 241, 253);visibility: visible;"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;text-indent: 0em;visibility: visible;"><span style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(0, 0, 0);visibility: visible;"><span leaf="" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;">2024/06/27</span></span></section></section></td><td data-colwidth="49.0000%" width="49.0000%" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(255, 255, 255);max-width: 100%;box-sizing: border-box !important;background-color: rgb(237, 241, 253);visibility: visible;"><span style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;"><spanLine truncated
|
||||
|
||||
**案例介绍篇**
|
||||
聚焦于真实的攻击事件,还原病毒家族的攻击路径和策略,为用户提供详细的溯源分析和防护启示;
|
||||
<table><tbody><tr style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;"><td data-colwidth="30.0000%" width="30.0000%" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(255, 255, 255);max-width: 100%;box-sizing: border-box !important;background-color: rgb(165, 200, 255);visibility: visible;"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(120, 120, 120);visibility: visible;"><span style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(255, 255, 255);visibility: visible;"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(255, 255, 255);font-family: Optima, PingFangSC-regular, serif;font-size: 16px;letter-spacing: normal;text-align: left;background-color: rgb(165, 200, 255);visibility: visible;"><span leaf="" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;">收录时间</span></strong></strong></span></section></td><td data-colwidth="49.0000%" width="49.0000%" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(255, 255, 255);max-width: 100%;box-sizing: border-box !important;background-color: rgb(165, 200, 255);visibility: visible;"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(120, 120, 120);visibility: visible;"><p style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;clear: both;min-height: 1em;visibility: visible;"><span style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(255, 255, 255);visibility: visible;"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(255, 255, 255);font-family: Optima, PingFangSC-regular, serif;font-size: 16px;letter-spacing: normal;text-align: left;background-color: rgb(165, 200, 255);visibility: visible;"><span leaf="" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;">相关文章</span></strong></strong></span></p></section></td></tr><tr style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;"><td data-colwidth="30.0000%" width="30.0000%" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(255, 255, 255);max-width: 100%;box-sizing: border-box !important;background-color: rgb(237, 241, 253);visibility: visible;"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;"><span leaf="" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;visibility: visible;">2024/06/27</span></section></section></td><td data-colwidth="49.0000%" width="49.0000%" Line truncated
|
||||
|
||||
**漏洞与预防篇**
|
||||
侧重于技术层面的防御手段,针对病毒利用的漏洞和安全弱点,提出操作性强的应对方案:
|
||||
|
||||
<table><tbody><tr style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;"><td data-colwidth="30.0000%" width="30.0000%" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(255, 255, 255);max-width: 100%;box-sizing: border-box !important;background-color: rgb(165, 200, 255);"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(120, 120, 120);"><span style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(255, 255, 255);"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(255, 255, 255);letter-spacing: 0.578px;background-color: rgb(165, 200, 255);"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;font-family: Optima, PingFangSC-regular, serif;font-size: 16px;letter-spacing: normal;text-align: left;"><span leaf="" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;">收录时间</span></strong></strong></strong></span></section></td><td data-colwidth="49.0000%" width="49.0000%" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(255, 255, 255);max-width: 100%;box-sizing: border-box !important;background-color: rgb(165, 200, 255);"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(120, 120, 120);"><p style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;clear: both;min-height: 1em;"><span style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(255, 255, 255);"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(255, 255, 255);font-family: Optima, PingFangSC-regular, serif;font-size: 16px;letter-spacing: normal;text-align: left;background-color: rgb(165, 200, 255);"><span leaf="" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;">相关文章</span></strong></strong></span></p></section></td></tr><tr style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;"><td data-colwidth="30.0000%" width="30.0000%" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(255, 255, 255);max-width: 100%;box-sizing: border-box !important;background-color: rgb(237, 241, 253);"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;text-indent: 0em;"><span leaf="" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;font-size: 16px;color: rgb(0, 0, 0);">2025/01/08</span></section></section></td><td data-colwidth="49.0000%" width="49.0000%" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-wordLine truncated
|
||||
|
||||
**应急响应工具教程篇**
|
||||
重点分享应急响应过程中常用工具的安装、配置与使用说明,旨在帮助读者快速掌握这些工具的操作流程与技巧,提高其在实际应急场景中的应用熟练度与效率。
|
||||
|
||||
<table><tbody><tr style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;"><td data-colwidth="30.0000%" width="30.0000%" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(255, 255, 255);max-width: 100%;box-sizing: border-box !important;background-color: rgb(165, 200, 255);"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(120, 120, 120);"><span style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(255, 255, 255);"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(255, 255, 255);font-family: Optima, PingFangSC-regular, serif;font-size: 16px;letter-spacing: normal;text-align: left;background-color: rgb(165, 200, 255);"><span leaf="" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;">收录时间</span></strong></strong></span></section></td><td data-colwidth="49.0000%" width="49.0000%" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(255, 255, 255);max-width: 100%;box-sizing: border-box !important;background-color: rgb(165, 200, 255);"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(120, 120, 120);"><p style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;clear: both;min-height: 1em;"><span style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(255, 255, 255);"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;color: rgb(255, 255, 255);font-family: Optima, PingFangSC-regular, serif;font-size: 16px;letter-spacing: normal;text-align: left;background-color: rgb(165, 200, 255);"><span leaf="" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;">相关文章</span></strong></strong></span></p></section></td></tr><tr style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;"><td data-colwidth="30.0000%" width="30.0000%" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(255, 255, 255);max-width: 100%;box-sizing: border-box !important;background-color: rgb(237, 241, 253);"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;text-indent: 0em;"><span leaf="" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;font-size: 16px;color: rgb(0, 0, 0);">2025/01/10</span></section></section></td><td data-colwidth="49.0000%" width="49.0000%" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 6px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(255, 255, 255);max-width: 100%;box-sizing: border-box !important;background-color: rgb(237, 241, 253);"><section style="-webkit-tap-highlight-coloLine truncated
|
||||
|
||||
如果您想了解有关勒索病毒的最新发展情况,或者需要获取相关帮助,请关注“Solar应急响应团队”。
|
||||
|
||||
**全国热线| 400-613-6816**
|
||||
|
||||
**更多资讯| 扫码加入群组交流**
|
||||
|
||||

|
||||
|
||||
|
||||
喜欢此内容的人还喜欢
|
||||
|
||||
|
||||
[【紧急警示】Weaxor最新变种“.wxx”来袭,批量入国内知名财务类管理系统发起勒索攻击!](https://mp.weixin.qq.com/s?__biz=MzkyOTQ0MjE1NQ==&mid=2247498941&idx=1&sn=bc6215afc52c9833b559b1385aca6ac6&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
Solar应急响应团队
|
||||
|
||||
|
||||
[【病毒分析】新版勒索病毒MEDUSA LOCKER 首发深度分析](https://mp.weixin.qq.com/s?__biz=MzkyOTQ0MjE1NQ==&mid=2247503856&idx=1&sn=c598583331355f663797d16674d27849&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
Solar应急响应团队
|
||||
|
||||
# 【成功案例】成功挫败 888 勒索家族历时半年的百万赎金勒索,应急处置全流程高效修复,避免千万损失并获客户赠送锦旗Solar应急响应团队
|
||||
|
||||
|
||||
@@ -0,0 +1,186 @@
|
||||
# 指纹识别+精准化 POC 攻击
|
||||
蚁景网安 2026-01-08 08:46
|
||||
|
||||
## 开发目的
|
||||
|
||||
解决漏洞扫描器的痛点
|
||||
|
||||
第一就是扫描量太大,对一个站点扫描了大量的无用 POC,浪费时间
|
||||
|
||||
指纹识别后还需要根据对应的指纹去进行 payload 扫描,非常的麻烦
|
||||
## 开发思路
|
||||
|
||||
我们的思路大体分为指纹+POC+扫描
|
||||
|
||||
所以思路大概从这几个方面入手
|
||||
|
||||
首先就是 POC,我们得寻找一直在更新的 POC,而且是实时更新的,因为自己写的话有点太费时间了
|
||||
|
||||
但是这 POC 的决定是根据我们扫描器来的,因为世面上已经有许多不错的扫描器了,目前打算使用的是 nuclei 扫描器
|
||||
|
||||
https://github.com/projectdiscovery/nuclei
|
||||
|
||||
Nuclei 是一种现代、高性能的漏洞扫描程序,它利用基于 YAML 的简单模板。它使您能够设计自定义漏洞检测场景,以模拟真实世界的条件,从而实现零误报。
|
||||
|
||||
目前也在不断维护更新,当然还有 Xray,Goby 等工具也是不错的选择
|
||||
|
||||
然后回到指纹识别技术,这个需要大量的指纹样本,但是世面上的各种工具已经可以做得很好了
|
||||
## 指纹识别
|
||||
|
||||
这里就的学习一下指纹识别的技术
|
||||
|
||||
首先我们需要知道收集指纹目前大概有哪些方法
|
||||
### 指纹识别方式
|
||||
#### 特定文件
|
||||
|
||||
比如举一个例子,我们通常是如何判断一个框架是 thinkphp 呢?
|
||||
|
||||
我们随便找几个 thinkphp 的网站
|
||||
|
||||
特征就是它的图标是非常明显的
|
||||
|
||||
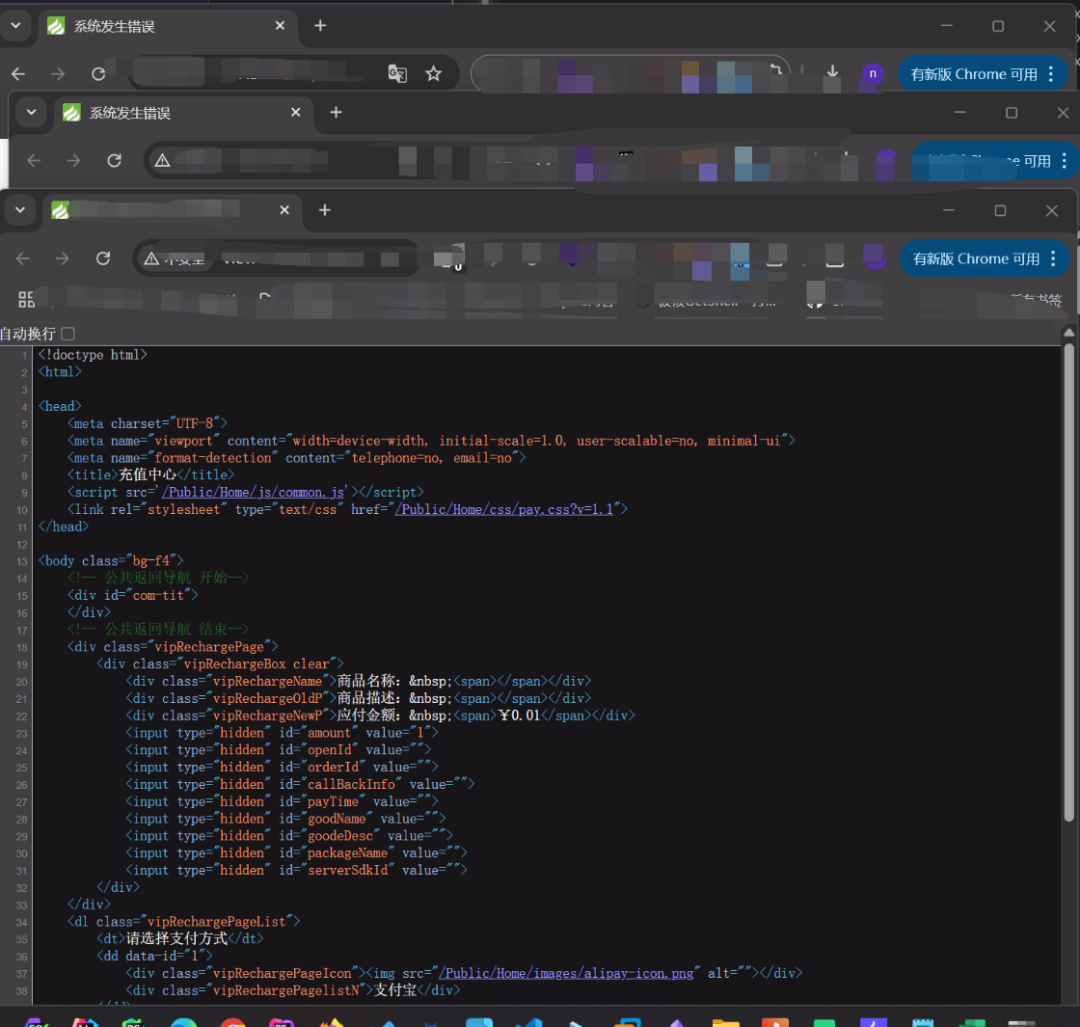
|
||||
|
||||
|
||||
可以看到图标都是一样的,目前 fofa 和 hunter 已经有这种查找的方法了,一般都是把我们的图标换算为我们的 hash 值
|
||||
|
||||
这个就是我们的 favicon.ico 图标
|
||||
|
||||
一般网站是通过在路径后加入 favicon.ico 比如
|
||||
|
||||
http://xxxxxx/favicon.ico
|
||||
|
||||
|
||||
|
||||
|
||||
然后就能获取这个图标了,而在 fofa 中可以直接拖动查询了,可以直接算出 hash 值
|
||||
|
||||
|
||||
|
||||
|
||||
比如 thinkphp 的
|
||||
|
||||
|
||||
|
||||
|
||||
然后再次查询
|
||||
|
||||
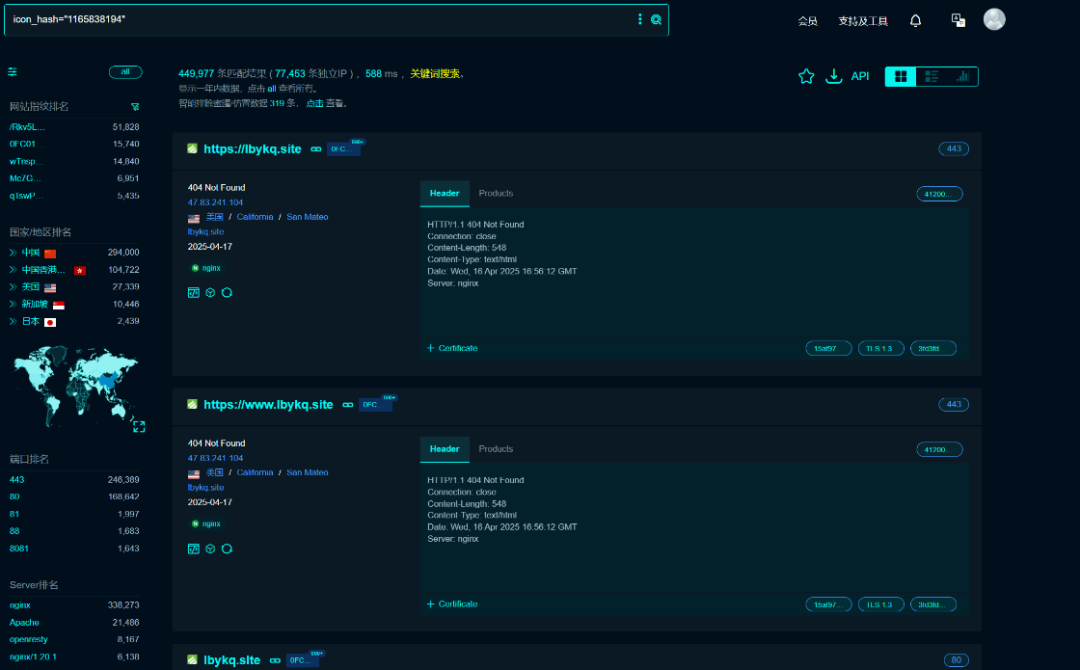
|
||||
|
||||
|
||||
全是 tp 的网站
|
||||
|
||||
参考https://github.com/TideSec/TideFinger/blob/master/Web%E6%8C%87%E7%BA%B9%E8%AF%86%E5%88%AB%E6%8A%80%E6%9C%AF%E7%A0%94%E7%A9%B6%E4%B8%8E%E4%BC%98%E5%8C%96%E5%AE%9E%E7%8E%B0.md
|
||||
|
||||
当然除了我们的 ico 文件,还有其他很多的文件
|
||||
|
||||
一些网站的特定图片文件、js 文件、CSS 等静态文件,如 favicon.ico、css、logo.ico、js 等文件一般不会修改,通过爬虫对这些文件进行抓取并比对 md5 值,如果和规则库中的 Md5 一致则说明是同一 CMS。这种方式速度比较快,误报率相对低一些,但也不排除有些二次开发的 CMS 会修改这些文件。
|
||||
|
||||
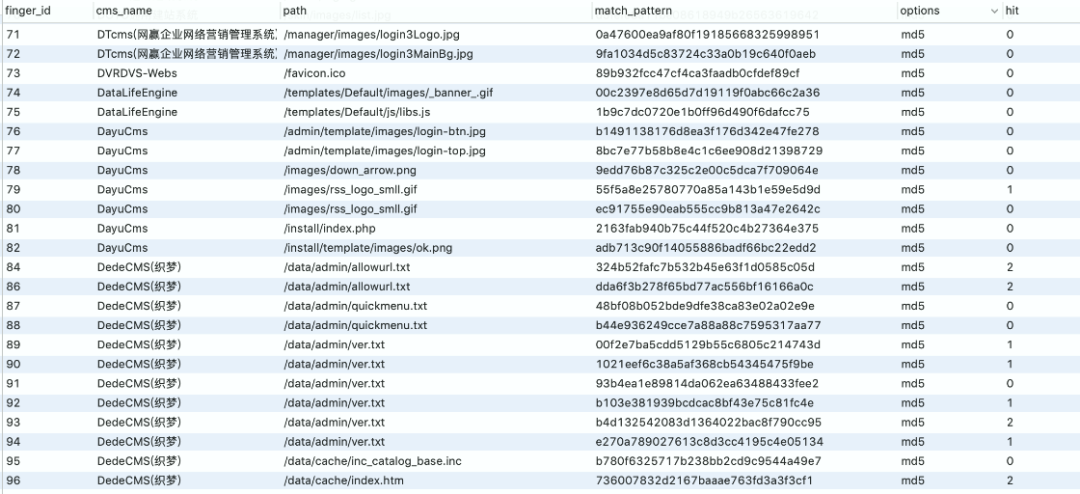
|
||||
|
||||
#### 页面关键字
|
||||
|
||||
比如 tp 的错误页面大多数都是
|
||||
|
||||
|
||||
|
||||
|
||||
我们 body 就可以包含这个关键字了
|
||||
|
||||
或者可以构造错误页面,根据报错信息来判断使用的 CMS 或者中间件信息,比较常见的如 tomcat 和 spring 的报错页面。
|
||||
|
||||
根据 response header 一般有以下几种识别方式:
|
||||
#### 请求头关键字
|
||||
|
||||
根据网站 response 返回头信息进行关键字匹配,这个一般是 ningx 这种
|
||||
|
||||
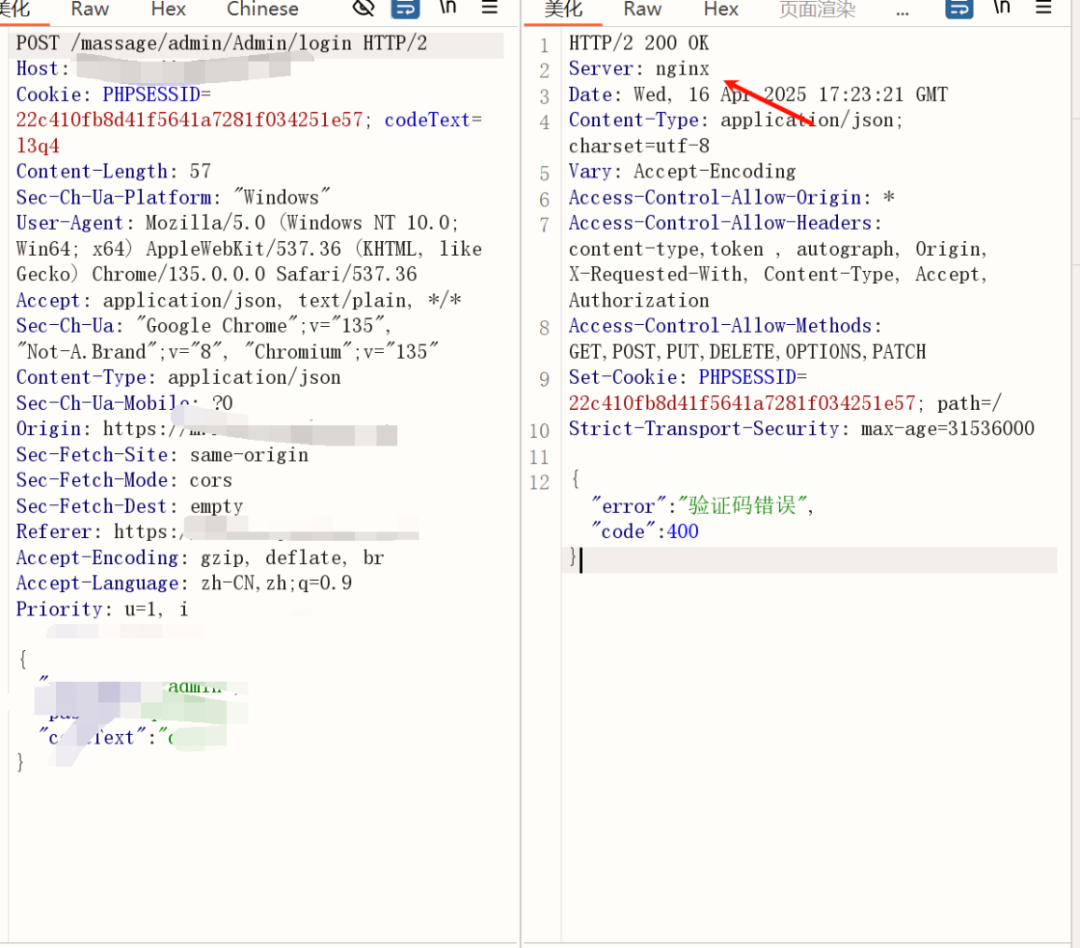
|
||||
|
||||
|
||||
能够识别我们的服务器
|
||||
#### URL 路径
|
||||
|
||||
根据总结
|
||||
|
||||
wordpress 默认存在 wp-includes 和 wp-admin 目录,织梦默认管理后台为 dede 目录,solr 平台可能使用/solr 目录,weblogic 可能使用 wls-wsat 目录等。
|
||||
|
||||
大部分还是根据我们的 body
|
||||
|
||||
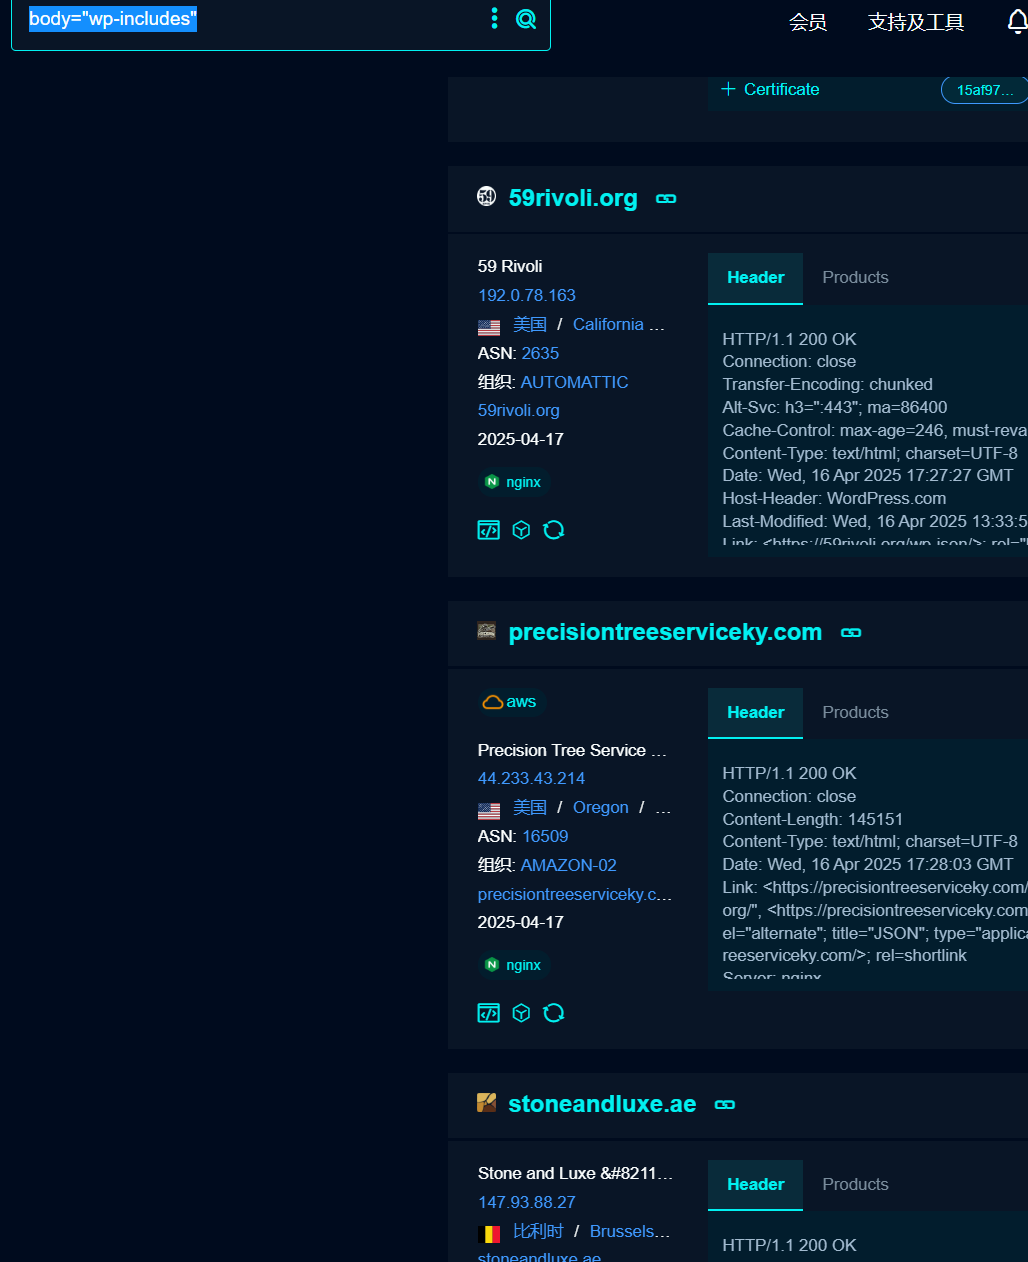
|
||||
|
||||
|
||||
然后点一个进去
|
||||
|
||||
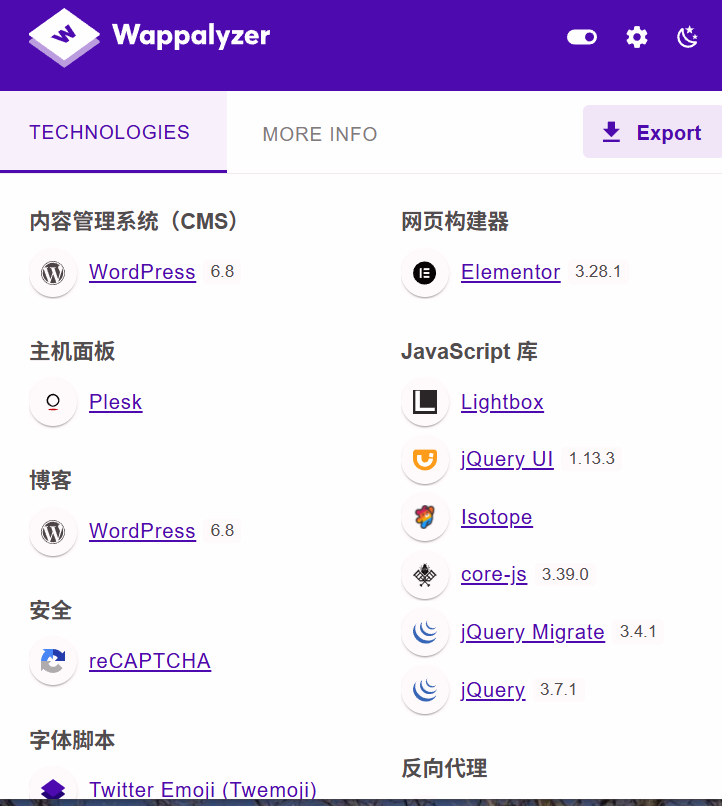
|
||||
|
||||
|
||||
可以看到都是我们的 wordPress 的站点
|
||||
### 指纹识别方法
|
||||
|
||||
有了我们上面的识别技术,那么我们大概是如何来识别一个指纹的呢
|
||||
|
||||
首先使用 python 简单举一个实现
|
||||
|
||||
首先就是需要一个配置文件,这个配置文件就需要包含我们的大体指纹和验证方法
|
||||
```
|
||||
- name: ThinkPHPmatchers: - type: header rule: X-Powered-By keyword: ThinkPHP - type: body keyword: "http://www.thinkphp.cn" - type: banner keyword: thinkphp - type: path path: /thinkphp/library/think/ keyword: class - type: favicon_hash hash: 1165838194
|
||||
```
|
||||
|
||||
然后就是我们的后端处理逻辑了
|
||||
```
|
||||
import yamlimport requestsimport socketimport base64import mmh3def get_http_response(url, path=""): try: full_url = url.rstrip("/") + path return requests.get(full_url, timeout=5) except: return Nonedef get_tcp_banner(ip, port=80): try: with socket.create_connection((ip, port), timeout=5) as s: banner = s.recv(1024).decode(errors="ignore") return banner except: return""def get_favicon_hash(url): try: res = requests.get(url.rstrip("/") + "/favicon.ico", timeout=5) favicon = base64.encodebytes(res.content) return mmh3.hash(favicon.decode('utf-8')) except: return Nonedef load_fingerprints(path="fingerprints.yaml"): with open(path, "r", encoding="utf-8") as f: return yaml.safe_load(f)def match_fingerprint(url, ip=None): fingerprints = load_fingerprints() results = [] res = get_http_response(url) banner = get_tcp_banner(ip or url.replace("http://", "").replace("https://", ""), 80) favicon_hash = get_favicon_hash(url) for fp in fingerprints: matched = False for matcher in fp["matchers"]: if matcher["type"] == "header"and res: if matcher["rule"] in res.headers and matcher["keyword"].lower() in res.headers[matcher["rule"]].lower(): matched = True elif matcher["type"] == "body"and res: if matcher["keyword"].lower() in res.text.lower(): matched = True elif matcher["type"] == "banner": if matcher["keyword"].lower() in banner.lower(): matched = True elif matcher["type"] == "path": res2 = get_http_response(url, matcher["path"]) if res2 and matcher["keyword"].lower() in res2.text.lower(): matched = True elif matcher["type"] == "favicon_hash": if favicon_hash == matcher["hash"]: matched = True if matched: results.append(fp["name"]) return results# 示例使用if __name__ == "__main__": target_url = "http://101.200.50.94:8009/" result = match_fingerprint(target_url) print("识别结果:", result)
|
||||
```
|
||||
|
||||
大体逻辑就是这样了
|
||||
|
||||
首先就是 yaml 文件为我们的判断依据,对应不同的判断方法我们都有对应的后端处理
|
||||
|
||||
一个是对 body 的处理,一个是对 hash 文件的处理
|
||||
|
||||
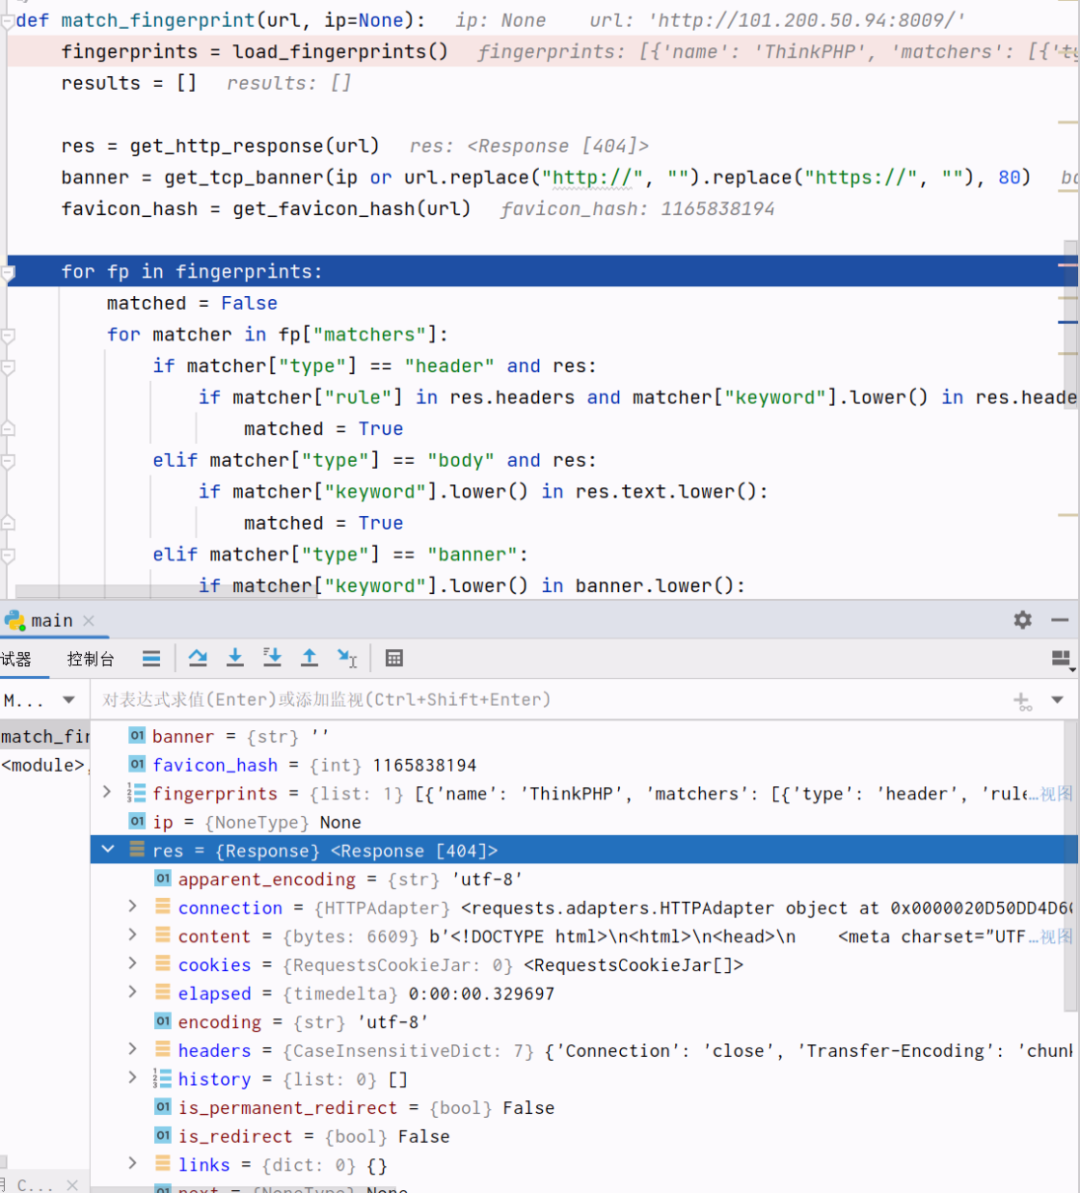
|
||||
|
||||
|
||||
然后再根据规则去匹配
|
||||
|
||||
匹配成功输出结果
|
||||
|
||||
当然这只是一个简单的逻辑,如果需要实现更高高效快捷第一就是指纹库,第二就是代码运行的速率,提高线程
|
||||
## 最终识别代码
|
||||
|
||||
首先就是指纹库的获取,这个的话我们就不直接获取了,使用的是 EHole 的指纹库
|
||||
|
||||
我们大概看看部分代码
|
||||
```
|
||||
{"fingerprint": [{ "cms": "seeyon", "method": "keyword", "location": "body", "keyword": ["/seeyon/USER-DATA/IMAGES/LOGIN/login.gif"]}, { "cms": "seeyon", "method": "keyword", "location": "body", "keyword": ["/seeyon/common/"]}, { "cms": "Spring env", "method": "keyword", "location": "body", "keyword": ["servletContextInitParams"]}, { "cms": "微三云管理系统", "method": "keyword", "location": "body", "keyword": ["WSY_logo","管理系统 MANAGEMENT SYSTEM"]}, { "cms": "Spring env", "method": "keyword", "location": "body", "keyword": ["logback"]}, { "cms": "Weblogic", "method": "keyword", "location": "body", "keyword": ["Error 404--Not Found"]}, { "cms": "Weblogic", "method": "keyword", "location": "body", "keyword": ["Error 403--"]}{ "cms": "Atlassian – JIRA", "method": "faviconhash", "location": "body", "keyword": ["981867722"]}, { "cms": "OpenStack", "method": "faviconhash", "location": "body", "keyword": ["-923088984"]}, { "cms": "Aplikasi", "method": "faviconhash", "location": "body", "keyword": ["494866796"]}, { "cms": "Ubiquiti Aircube", "method": "faviconhash", "location": "body", "keyword": ["1249285083"]}
|
||||
```
|
||||
|
||||
简单看了一下逻辑可以发现和我们的指定方法应该差不多,逻辑就是首先根据 method 去选择方法,一个是 keyword 方法,一个是 faviconhash 方法,是一个大的判断,然乎下面就是根据具体的比如 body,title 等去识别了
|
||||
|
||||
代码如下
|
||||
```
|
||||
import jsonimport requestsimport hashlibimport base64from bs4 import BeautifulSoupfrom urllib.parse import urljoinfrom concurrent.futures import ThreadPoolExecutor, as_completedimport argparse# 加载指纹def load_fingerprints(file='finger.json'): with open(file, 'r', encoding='utf-8') as f: data = json.load(f) if"fingerprint" in data: return data["fingerprint"] raise ValueError("指纹文件格式不正确,应包含 'fingerprint' 字段。")# 获取 HTTP 响应def get_http_response(url): try: headers = { "User-Agent": "Mozilla/5.0" } return requests.get(url, headers=headers, timeout=8, verify=False) except: return None# 计算 favicon hashdef get_favicon_hash(url): try: favicon_url = urljoin(url, '/favicon.ico') res = requests.get(favicon_url, timeout=5, verify=False) if res.status_code == 200: m = hashlib.md5() b64 = base64.b64encode(res.content) m.update(b64) returnint(m.hexdigest(), 16) except: return None# 匹配单条指纹def match_one(fpr, res, fav_hash): method = fpr["method"] loc = fpr.get("location", "body").lower() kws = fpr["keyword"] if method == 'keyword': text_body = res.text or"" text_head = "\n".join(f"{k}: {v}"for k, v in res.headers.items()) # 处理 title 和 header 等 if loc == 'header': spaces = [text_head, text_body] elif loc == 'title': soup = BeautifulSoup(text_body, "html.parser") title = soup.title.stringif soup.title and soup.title.stringelse"" spaces = [title, text_body] elif loc == 'body': spaces = [text_body] else: spaces = [text_body] for space in spaces: for kw in kws: if kw.lower() in space.lower(): return True if method == 'faviconhash'and fav_hash is not None: for kw in kws: try: if fav_hash == int(kw): return True except: continue return False# 识别单个 URL 指纹def match_fingerprint(url, fps=None): fps = fps orload_fingerprints() res = get_http_response(url) fav_hash = get_favicon_hash(url) matched = [] for fpr in fps: if'cms' not in fpr or'method' not in fpr or'keyword' not in fpr: continue ifmatch_one(fpr, res, fav_hash): matched.append(fpr['cms']) print(f"[✓] {url} 指纹识别结果:{list(set(matched))}") return {url: list(set(matched))}# 多线程执行def run_multithread(urls, threads): fps = load_fingerprints() results = [] with ThreadPoolExecutor(max_workers=threads) as executor: future_to_url = {executor.submit(match_fingerprint, url, fps): url for url in urls} for future in as_completed(future_to_url): results.append(future.result()) return results# 主程序入口def main(): parser = argparse.ArgumentParser(description="指纹识别脚本 - 支持多线程") group = parser.add_mutually_exclusive_group(required=True) group.add_argument("-u", "--url", help="单个目标 URL") group.add_argument("-f", "--file", help="包含多个 URL 的文件") parser.add_argument("-t", "--threads", type=int, default=10, help="线程数(默认10)") args = parser.parse_args() if args.url: match_fingerprint(args.url) elif args.file: with open(args.file, 'r', encoding='utf-8') as f: urls = [line.strip() for line in f if line.strip()] results = run_multithread(urls, args.threads)if __name__ == '__main__': main()
|
||||
```
|
||||
|
||||
加入了支持多线程和支持多目标的思路
|
||||
## 结合漏洞扫描
|
||||
|
||||
我们光目标识别后,还需要实现精准化打击,正好 Nuclei 引擎支持根据 tag 去寻找我们的目标,完美了
|
||||
|
||||
实现思路就是首先寻找我们的 tag,然后在漏洞库里面查询,把有 tag 的和没有 tag 的分别分开放好,然后根据有 tag 的去精准化识别运行,完成最后的精准化 POC 攻击
|
||||
|
||||
初步的代码如下
|
||||
```
|
||||
import jsonimport osimport threadingimport timeimport base64import hashlibimport requestsimport argparsefrom bs4 import BeautifulSoupfrom urllib.parse import urljoinfrom concurrent.futures import ThreadPoolExecutor, as_completedfrom queue import Queuerequests.packages.urllib3.disable_warnings()# ---------- 指纹识别部分 ----------def load_fingerprints(file='finger.json'): with open(file, 'r', encoding='utf-8') as f: data = json.load(f) return data["fingerprint"]def get_http_response(url): try: headers = {"User-Agent": "Mozilla/5.0"} return requests.get(url, headers=headers, timeout=8, verify=False) except: return Nonedef get_favicon_hash(url): try: favicon_url = urljoin(url, '/favicon.ico') res = requests.get(favicon_url, timeout=5, verify=False) if res.status_code == 200: m = hashlib.md5() b64 = base64.b64encode(res.content) m.update(b64) returnint(m.hexdigest(), 16) except: return Nonedef match_one(fpr, res, fav_hash): method = fpr["method"] loc = fpr.get("location", "body").lower() kws = fpr["keyword"] if method == 'keyword': text_body = res.text or"" text_head = "\n".join(f"{k}: {v}"for k, v in res.headers.items()) if loc == 'header': spaces = [text_head] elif loc == 'title': soup = BeautifulSoup(text_body, "html.parser") title = soup.title.stringif soup.title and soup.title.stringelse"" spaces = [title] else: spaces = [text_body] for space in spaces: for kw in kws: if kw.lower() in space.lower(): return True elif method == 'faviconhash'and fav_hash is not None: for kw in kws: try: if fav_hash == int(kw): return True except: continue return Falsedef match_fingerprint(url, fps): res = get_http_response(url) fav_hash = get_favicon_hash(url) matched = [] for fpr in fps: if'cms' not in fpr or'method' not in fpr or'keyword' not in fpr: continue ifmatch_one(fpr, res, fav_hash): matched.append(fpr['cms']) print(f"[✓] {url} 指纹识别结果:{list(set(matched))}") return {"url": url, "cms": list(set(matched))[0] if matched else""}def run_fingerprint_scan(urls, threads, output='res.json'): fps = load_fingerprints() results = [] with ThreadPoolExecutor(max_workers=threads) as executor: future_to_url = {executor.submit(match_fingerprint, url, fps): url for url in urls} for future in as_completed(future_to_url): results.append(future.result()) with open(output, 'w', encoding='utf-8') as f: json.dump(results, f, ensure_ascii=False, indent=2)# ---------- Nuclei 扫描部分 ----------class AutoNuclei: def __init__(self, res_file='res.json', tag_file='C:\\Users\\86135\\nuclei-templates\\TEMPLATES-STATS.json', thread_count=5): self.res_file = res_file self.tag_file = tag_file self.havetag_file = 'havetag.txt' self.notag_file = 'notag.txt' self.result_dir = 'result' self.thread_count = thread_count self.cms_targets = {} # {cms: [url1, url2]} self.nuclei_tags = set() self.tagged_targets = {} # {tag: [url1, url2]} self.untagged_targets = [] self.task_queue = Queue() self.load_res_json() self.load_tags() self.classify_targets() self.save_targets() self.start_scan_threads() def load_res_json(self): with open(self.res_file, 'r', encoding='utf-8') as f: data = json.load(f) for entry in data: cms = entry.get("cms", "").lower() url = entry.get("url") if cms and url: self.cms_targets.setdefault(cms, []).append(url) def load_tags(self): with open(self.tag_file, 'r', encoding='utf-8') as f: tags_data = json.load(f) for item in tags_data.get("tags", []): if item["name"]: self.nuclei_tags.add(item["name"].lower()) def classify_targets(self): for cms, urls in self.cms_targets.items(): if cms in self.nuclei_tags: self.tagged_targets.setdefault(cms, []).extend(urls) else: Line truncated
|
||||
```
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
学
|
||||
习
|
||||
网安实战技术课程
|
||||
,戳
|
||||
“阅读原文”
|
||||
|
||||
@@ -0,0 +1,67 @@
|
||||
# 自动化平台n8n曝高危漏洞CVE-2026-21858,10万服务器面临接管风险
|
||||
看雪学苑 看雪学苑 2026-01-08 10:05
|
||||
|
||||
近日,流行工作流自动化平台n8n曝出一个严重安全漏洞(CVE-2026-21858),威胁着全球约10万台服务器。该漏洞允许未经身份验证的攻击者完全控制服务器,其CVSS评分高达10.0,属于最高危级别。更令人担忧的是,完整的攻击链概念验证(PoC)已在网上公开。
|
||||
|
||||
|
||||
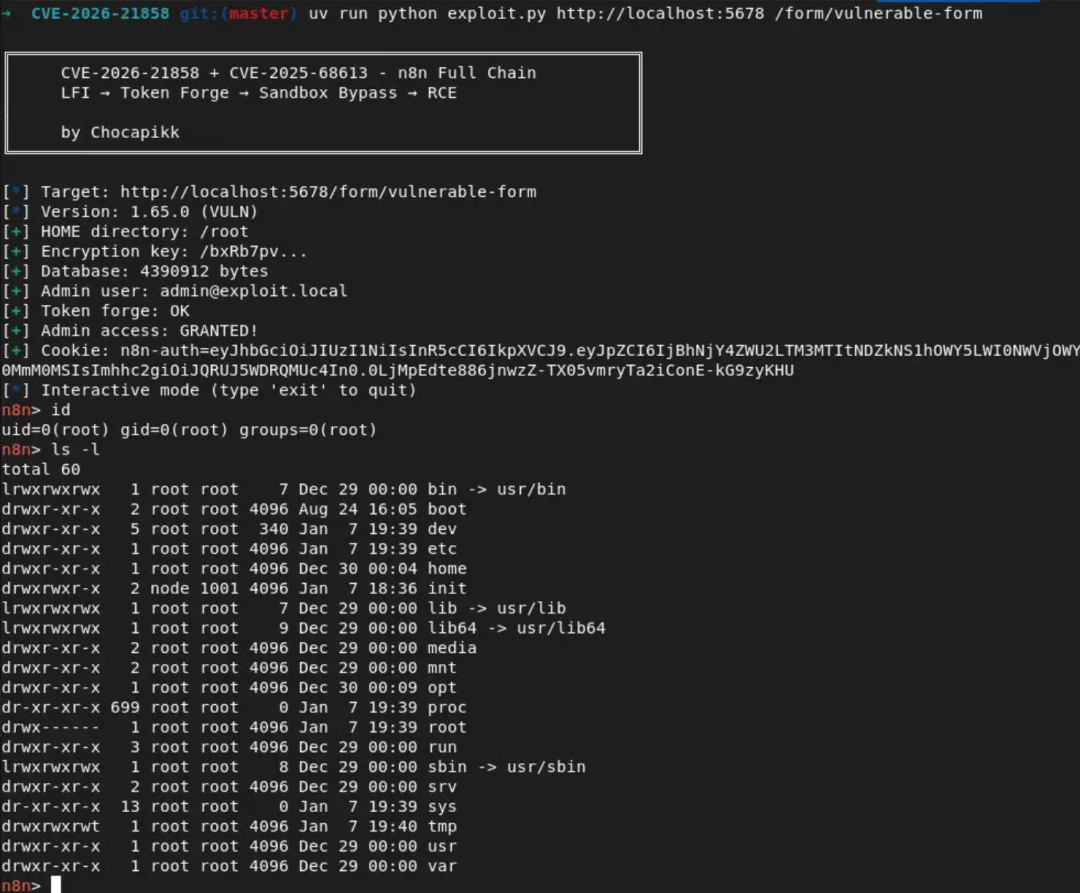
|
||||
|
||||
|
||||
根据安全公司Cyera发布的报告,该漏洞源于n8n处理HTTP请求时存在一个“Content-Type混淆”的逻辑错误。平台在处理传入数据时,若请求头为`multipart/form-data`,会使用安全的文件解析器(Formidable)填充`req.body.files`;若为`application/json`,则会用标准解析器解析JSON载荷至`req.body`。
|
||||
|
||||
|
||||
关键在于,用于处理文件上传的“表单Webhook节点”中的`prepareFormReturnItem`函数,盲目信任`req.body.files`的内容,却未验证请求是否确实为`multipart/form-data`类型。这导致攻击者可以进行一个致命操作:
|
||||
|
||||
|
||||
发送一个`Content-Type`标头为`application/json`的请求,但在JSON正文中恶意构造一个`files`对象,并指定`filepath`参数指向服务器上的任意文件(例如`/etc/passwd`)。由于程序信任此输入,便会将服务器内部文件“复制”并返回给攻击者,从而实现任意文件读取。
|
||||
|
||||
|
||||
然而,危险不止于此。Cyera报告详细描述了如何将此漏洞武器化,逐步实现完整的服务器接管:
|
||||
- 第一步:窃取凭据。
|
||||
攻击者利用文件读取漏洞,获取n8n数据库(如`/home/node/.n8n/database.sqlite`)和配置文件(`/home/node/.n8n/config`)。
|
||||
|
||||
- 第二步:伪造会话。
|
||||
数据库中存有用户详情(邮箱和哈希密码),配置文件则包含加密密钥。结合这两者,攻击者可以数字签名自己的会话Cookie(`n8n-auth`),从而以管理员身份成功登录系统。
|
||||
|
||||
- 第三步:执行代码。
|
||||
一旦获得管理员权限,攻击者只需创建一个新工作流,添加“执行命令”节点,便可运行任意shell命令,完全掌控服务器。
|
||||
|
||||
安全研究员Chocapikk已公开了一个PoC,将该漏洞与另一个漏洞(CVE-2025-68613)串联,实现了未经身份验证的远程代码执行(RCE)。
|
||||
|
||||
|
||||
此次漏洞的“爆炸半径”极大。由于n8n被设计用于连接各类系统,一个被攻陷的实例相当于将攻击者引入了它所触及的所有关键资产:“企业的Google Drive、OpenAI API密钥、Salesforce数据、IAM系统、支付处理器”等等。
|
||||
|
||||
|
||||
目前,官方并未提供针对此漏洞的临时缓解措施。管理员必须立即将n8n升级至1.121.0或更高版本以修复此问题。同时,安全团队应确保除非绝对必要,否则不要将n8n实例暴露在公网,并确保所有表单功能都已启用强制身份验证。
|
||||
|
||||
|
||||
|
||||
资讯来源
|
||||
:
|
||||
cybersecuritynews
|
||||
|
||||
转载请注明出处和本文链接
|
||||
|
||||
|
||||
|
||||
﹀
|
||||
|
||||
﹀
|
||||
|
||||
﹀
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
**球分享**
|
||||
|
||||

|
||||
|
||||
**球点赞**
|
||||
|
||||

|
||||
|
||||
**球在看**
|
||||
|
||||
@@ -0,0 +1,106 @@
|
||||
# 高危漏洞威胁情报合集 (2026-01-08)
|
||||
0xSecDebug 2026-01-08 09:38
|
||||
|
||||
|
||||
|
||||
****
|
||||
请勿利用文章内的相关技术从事非法测试,由于传播、利用此文所提供的信息而造成的任何直接或者间接的后果及损失,均由使用者本人负责,作者不为此承担任何责任。工具和内容均来自网络,仅做学习和记录使用,安全性自测,
|
||||
如有侵权请联系删除。
|
||||
****
|
||||
|
||||
如果师傅们想要第一时间获取到
|
||||
最新的威胁情报
|
||||
,可以添加下面我创建的钉钉漏洞威胁情报群,便于
|
||||
师傅们
|
||||
可以及时获取最新的
|
||||
IOC
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
HPE OneView 远程代码执行漏洞(CVE-2025-37164)
|
||||
|
||||
- CVE编号:
|
||||
**CVE-2025-37164**
|
||||
|
||||
- 危害定级:
|
||||
**严重**
|
||||
|
||||
- 漏洞标签:
|
||||
**在野利用**
|
||||
|
||||
**CISA KEV**
|
||||
|
||||
**POC公开**
|
||||
|
||||
**关键漏洞**
|
||||
|
||||
- 披露日期:
|
||||
**2025-12-16**
|
||||
|
||||
- 推送原因: 漏洞创建
|
||||
|
||||
- 信息来源:
|
||||
https://ti.qianxin.com/vulnerability/detail/433649
|
||||
|
||||
漏洞描述
|
||||
|
||||
HPE OneView是HPE公司提供的一款数据中心基础设施管理软件,用于整合和管理数据中心内的物理IT资源。该软件存在一个远程代码执行问题,攻击者可以利用该问题在未授权的情况下远程执行代码,控制服务器。
|
||||
|
||||
|
||||
开源检索
|
||||
|
||||
暂未找到
|
||||
|
||||
|
||||
|
||||
**HPE OneView 远程代码执行漏洞(CVE-2025-37164)**
|
||||
|
||||
- CVE编号:
|
||||
**CVE-2025-37164**
|
||||
|
||||
- 危害定级:
|
||||
**严重**
|
||||
|
||||
- 漏洞标签:
|
||||
**在野利用**
|
||||
|
||||
**CISA KEV**
|
||||
|
||||
**POC公开**
|
||||
|
||||
**关键漏洞**
|
||||
|
||||
- 披露日期:
|
||||
**2025-12-16**
|
||||
|
||||
- 推送原因: 漏洞创建
|
||||
|
||||
- 信息来源:
|
||||
https://ti.qianxin.com/vulnerability/detail/433649
|
||||
|
||||
漏洞描述
|
||||
|
||||
HPE OneView是HPE公司提供的一款数据中心基础设施管理软件,用于整合和管理数据
|
||||
中心内的物理IT资源。该软件存在一个远程代码执行问题,攻击者可以利用该问题在未授权的情况下远程执行代码,控制服务器。
|
||||
|
||||
|
||||
开源检索
|
||||
|
||||
暂未找到
|
||||
|
||||
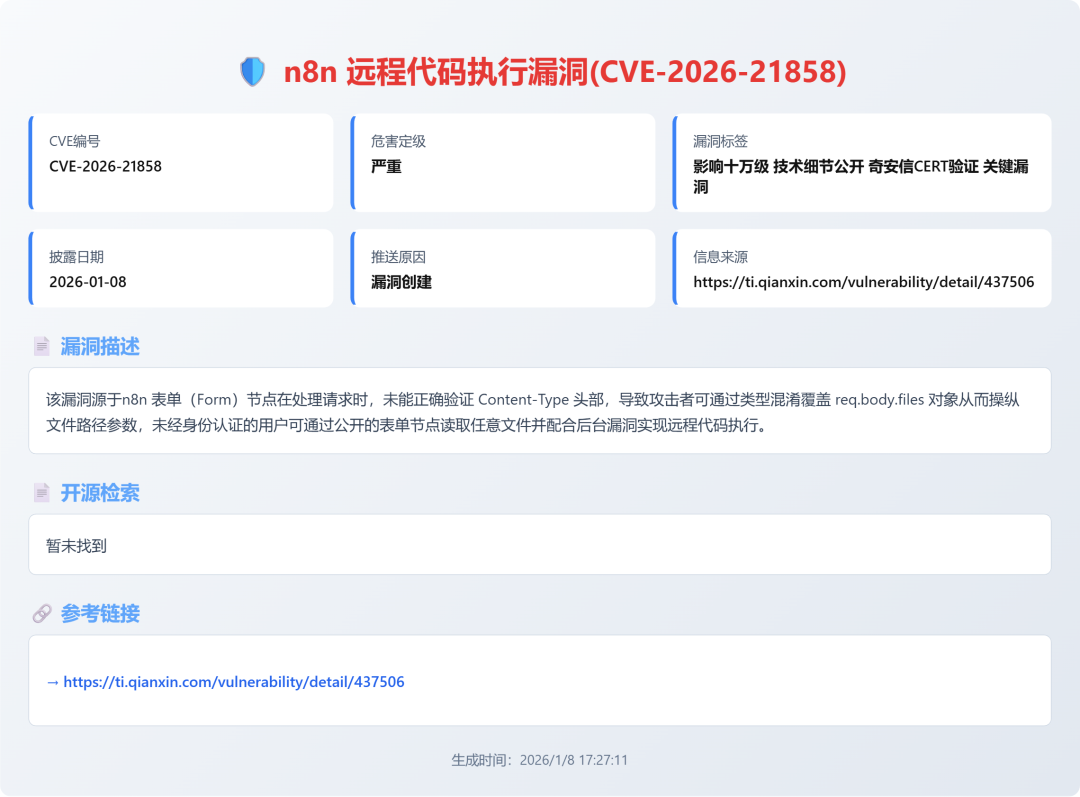
|
||||
|
||||
|
||||
绿盟漏洞情报(2026-01-08)
|
||||
|
||||
📊 数据来源:绿盟 www.nsfocus.net | 有效漏洞:1 条
|
||||
|
||||
Tenda AC23缓冲区溢出漏洞(CVE-2025-10803)
|
||||
|
||||
https://www.nsfocus.net/vulndb/132055
|
||||
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,102 @@
|
||||
# 黑客利用0Day漏洞工具包在野攻击VMware ESXi实例
|
||||
FreeBuf 2026-01-08 10:31
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
网络安全公司Huntress发现黑客正在利用一个0Day漏洞工具包攻击VMware ESXi实例,该工具包通过串联多个漏洞实现虚拟机逃逸。攻击者最初通过被入侵的SonicWall VPN获得初始访问权限。
|
||||
|
||||
|
||||
**Part01**
|
||||
## 攻击过程分析
|
||||
|
||||
|
||||
威胁行为者首先通过SonicWall VPN获得立足点,随后利用被入侵的域管理员账户进行横向移动,先后攻陷备份域控制器和主域控制器。在主域控制器上,攻击者部署了Advanced Port Scanner和ShareFinder等侦察工具,使用WinRAR暂存数据,并修改Windows防火墙规则以阻止外部出站流量,同时允许内部横向移动。
|
||||
|
||||
|
||||
在部署漏洞工具包约20分钟后,攻击者开始执行ESXi漏洞利用程序,Huntress在勒索软件部署前成功阻止了攻击。
|
||||
|
||||
|
||||
**Part02**
|
||||
## MAESTRO漏洞工具包技术细节
|
||||
```
|
||||
|
||||
```
|
||||
|
||||
Huntress将该工具包命名为MAESTRO,其工作原理包括:
|
||||
|
||||
- 使用devcon.exe禁用VMware VMCI驱动程序
|
||||
|
||||
- 通过KDU加载未签名驱动程序以绕过驱动程序签名强制(DSE)
|
||||
|
||||
- 执行核心逃逸操作
|
||||
|
||||
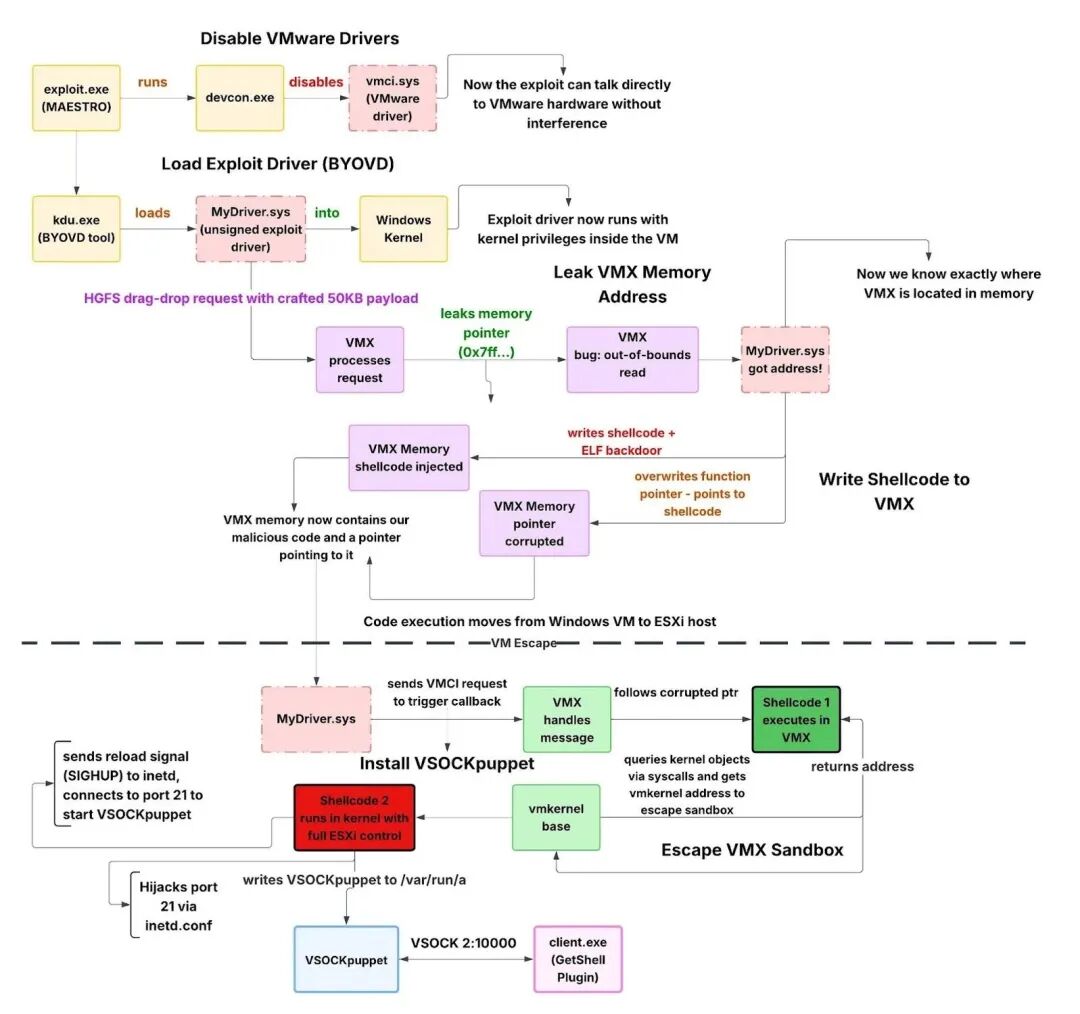
|
||||
|
||||
工具包截图(来源:Huntress)
|
||||
|
||||
|
||||
MyDriver.sys驱动程序通过VMware Guest SDK查询ESXi版本,从支持ESXi 5.1至8.0共155个构建版本的数据表中选择偏移量,通过HGFS(CVE-2025-22226)泄露VMX基址,通过VMCI(CVE-2025-22224)破坏内存,并部署用于沙箱逃逸的shellcode(CVE-2025-22225)。
|
||||
|
||||
|
||||
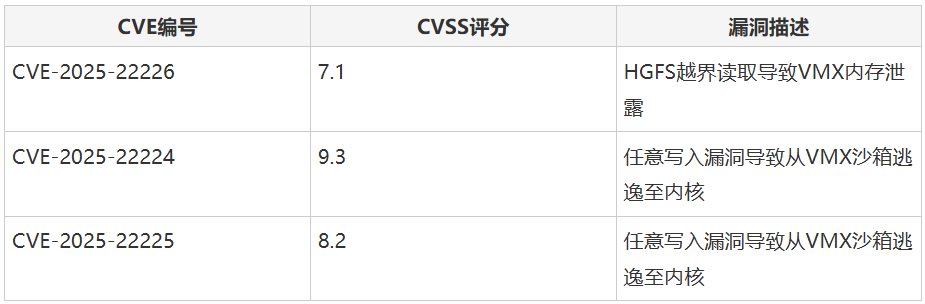
|
||||
|
||||
|
||||
Shellcode会部署名为VSOCKpuppet的后门程序,该后门劫持ESXi的inetd服务(端口21)以获取root权限,并使用VSOCK进行隐蔽的虚拟机-宿主机通信,这种通信方式对网络监控工具不可见。
|
||||
|
||||
|
||||
**Part03**
|
||||
## 攻击溯源与防御建议
|
||||
```
|
||||
|
||||
```
|
||||
|
||||
PDB路径显示该工具包在简体中文环境中开发,如"全版本逃逸--交付"的路径名称,时间戳为2024年2月,比Broadcom在2025年3月4日发布的VMSA-2025-0004安全公告早了一年多。2023年11月的client.exe PDB表明该工具采用模块化设计,被篡改的VMware驱动程序引用了"XLab"。Huntress高度确信攻击者来自中文环境,基于资源文件和0Day漏洞获取能力。
|
||||
|
||||
|
||||
防御建议:
|
||||
|
||||
- 及时为ESXi打补丁,已停止支持的版本无法获得修复
|
||||
|
||||
- 使用"lsof -a"命令监控ESXi主机的VSOCK进程
|
||||
|
||||
- 警惕KDU等BYOD加载器
|
||||
|
||||
- 加强VPN安全防护
|
||||
|
||||
- 防火墙规则变更和未签名驱动程序都是系统被入侵的信号
|
||||
|
||||
- VSOCK后门可绕过入侵检测系统(IDS)
|
||||
|
||||
此次事件凸显了虚拟机监控程序面临的持续威胁,攻击者通过驱动程序恢复和配置清理保持隐蔽性。随着针对ESXi的勒索软件攻击增加,企业必须加强虚拟化环境的安全防护。
|
||||
|
||||
|
||||
**参考来源:**
|
||||
|
||||
Hackers Exploiting VMware ESXi Instances in the Wild Using zero-day Exploit Toolkit
|
||||
|
||||
https://cybersecuritynews.com/vmware-esxi-exploited-toolkit/
|
||||
|
||||
|
||||
###
|
||||
###
|
||||
###
|
||||
|
||||
**推荐阅读**
|
||||
|
||||
[](https://mp.weixin.qq.com/s?__biz=MjM5NjA0NjgyMA==&mid=2651333596&idx=1&sn=a5f1d8decaf400a24f3b9e74a3a357e1&scene=21#wechat_redirect)
|
||||
###
|
||||
### 电台讨论
|
||||
|
||||
****
|
||||

|
||||
|
||||
****
|
||||
|
||||
|
||||
|
||||
|
||||
Reference in new issue
Block a user